

Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
apatchy — Fuzzing Framework for Modules in Apache HTTPD Server | Kitploit

Tools/GitHubGitHub/0xbigshaq/apatchy
Vulnerability AnalysisCode AnalysisDynamic Code Analysis (DAST)Web SecurityFuzzing
GitHub0xbigshaq/apatchy

apatchy

Fuzzing Framework for Modules in Apache HTTPD Server
View Repository
225535 months agoReviewed by Kitploit
Website
Share
apatchy

    apatchy

    An in-process fuzzing framework for Apache HTTPD

apatchy lets you fuzz Apache's full HTTP request processing pipeline - parsing, hooks, filters, handlers - without any network I/O. It replaces Apache's socket layer with custom I/O filters, feeding raw bytes directly into the same code paths that handle real HTTP traffic.
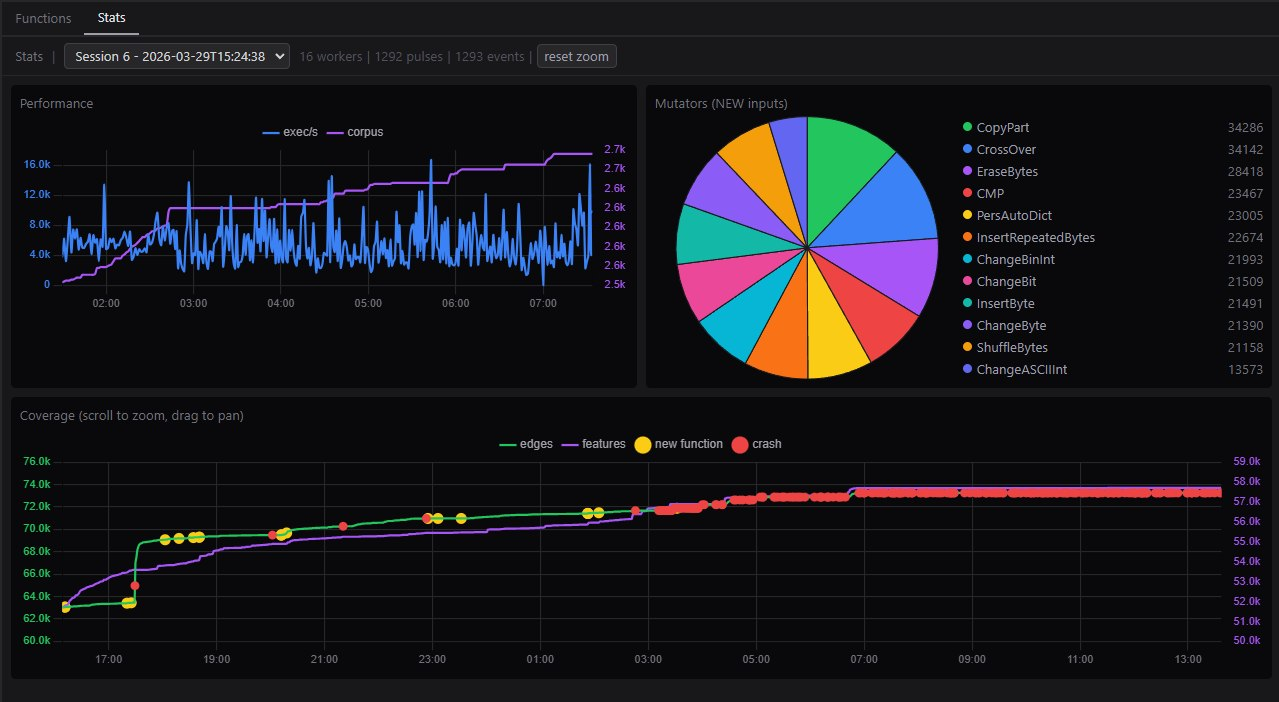
Features

  • Manage different build-trees & configurations
  • Coverage reports generation
  • Custom Introspection: LLVM Call-tree Analysis
  • Manager for: Harness, Proto Mutators
  • Triage bugs / re-play payloads
  • Profiling (kcachegrind/qcachegrind) to analyze bottlenecks in your harness logic to get better perf.
  • Custom toolchain to verify depndencies
  • Compatability with older Apache versions
  • 1day re-production system
  • and more :D

main-view

Quick Start

Recommended to run this on WSL2 and/or docker container

docker build --build-arg UID=$(id -u) -t apatchy-dev .
docker run -it --rm -p 9000:9000 -v $(pwd):/repo apatchy-dev

then run these commands in this order:

# 1. activate environment
cd framework/
uv venv .venv
uv pip install --python .venv -e ".[all]"
source .venv/bin/activate

# 2. init setup (one-time setup)
apatchy setup check                            # verify dependencies
apatchy setup --force llvm --llvm-version 18   # install LLVM tools locally

# 3. download
apatchy download --version 2.4.65

# 4. configure (vanilla root tree)
apatchy configure --asan --ubsan --ubsan-ignorelist ./configs/ubsan.ignorelist

# 5. build vanilla tree (`--bear` for IDE navigation)
apatchy make --tree vanilla --bear

# 6. build libfuzzer branch (inherits sanitizers from root)
apatchy make --tree lf

# 7. setup for protobuf
apatchy setup lpm

# 8. list avail. harnesses
apatchy link --list-harnesses

# 9. link target harness
apatchy link --harness mod_fuzzy_proto_session --bear

# 10. fuzz
apatchy fuzz \
    --config configs/session-coverage.conf \
    --seed-dir fuzz-seeds/session/ \


# 11. build coverage branch and generate HTML cov report
apatchy make --tree cov
apatchy coverage report \
    --with-introspect \
    --config configs/session-coverage.conf \
    --harness mod_fuzzy_proto_session \
    --suppress configs/ubsan.supp

# 12. launch interactive gui w/ call-tree analysis
apatchy introspect \
    --entry session_crypto_decode,session_crypto_encode,session_crypto_init

Documentation

Note: This is still in progress/not complete. I know the CLI needs more attention.

  • The documentation is live at https://pwner.gg/apatchy/
  • You can generate it locally via apatchy docs --serve

License

See LICENSE.

Download Tool

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    786
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    506
  • 3

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    429
  • 4

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    345
  • 5

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation improves the next.

    262
  • 6

    looking-glass

    anonghosty/looking-glass

    CSIRT platform that ingests Shadowserver reports into MongoDB and replays them as interactive maps, analysis, findings, advisories and executive dashboards.

    256

Explore all tools

Browse our collection of tools

View all tools →






