

akca
 akha-security/akca
Evidence-oriented DAST scanner in Go that crawls web apps and APIs, then runs adaptive SQLi, XSS, RCE, SSRF, and auth checks with replayable proof.
api-security-testingdefensive-toolsdynamic-analysis-sandboxing+9
243
akha-security/akcaEvidence-oriented DAST scanner in Go that crawls web apps and APIs, then runs adaptive SQLi, XSS, RCE, SSRF, and auth checks with replayable proof.
 vladko312/sstimap
Automatic SSTI detection tool with interactive interface
 vighnesh91/-logicsentry-ai
Offline SAST/DAST triage engine that parses source code and replays HAR traffic to detect business-logic flaws, BOLA, race conditions, and privilege…

 whwlsfb/burpcrypto
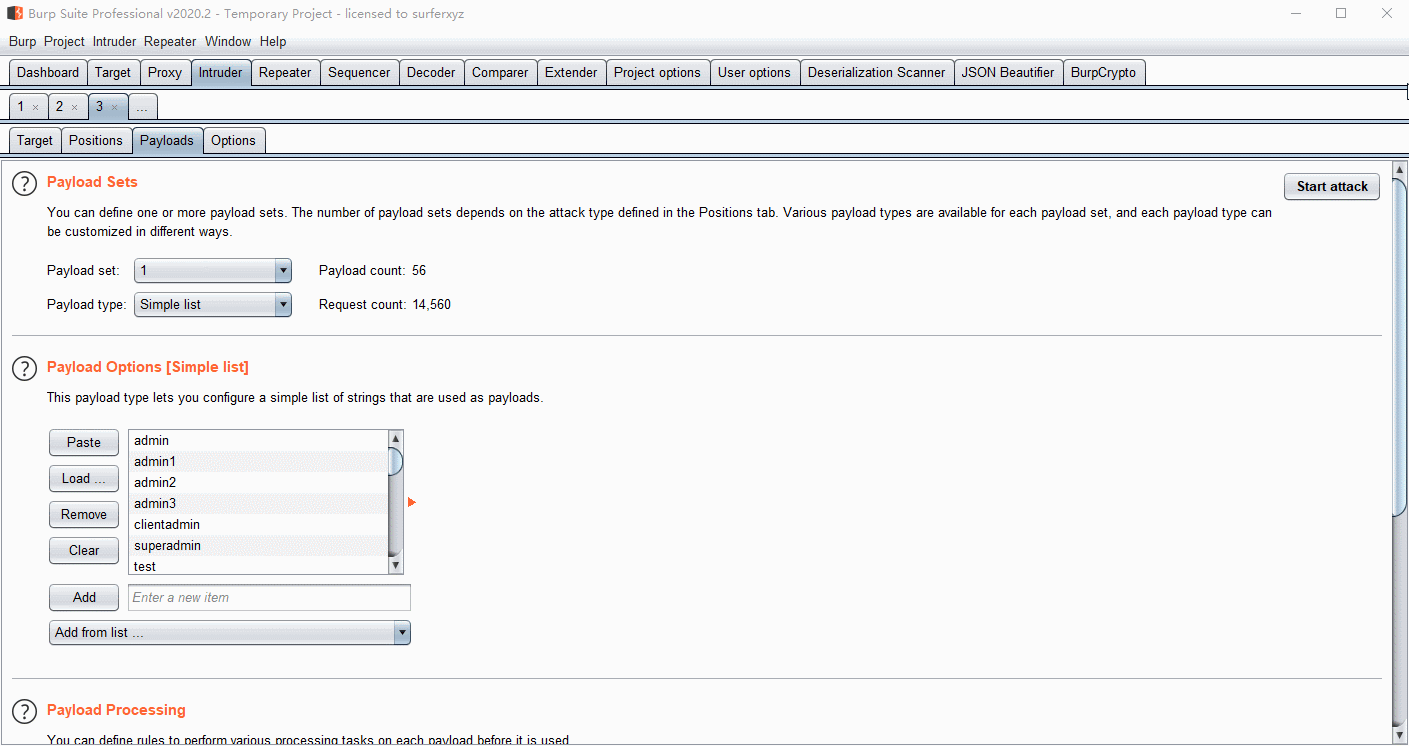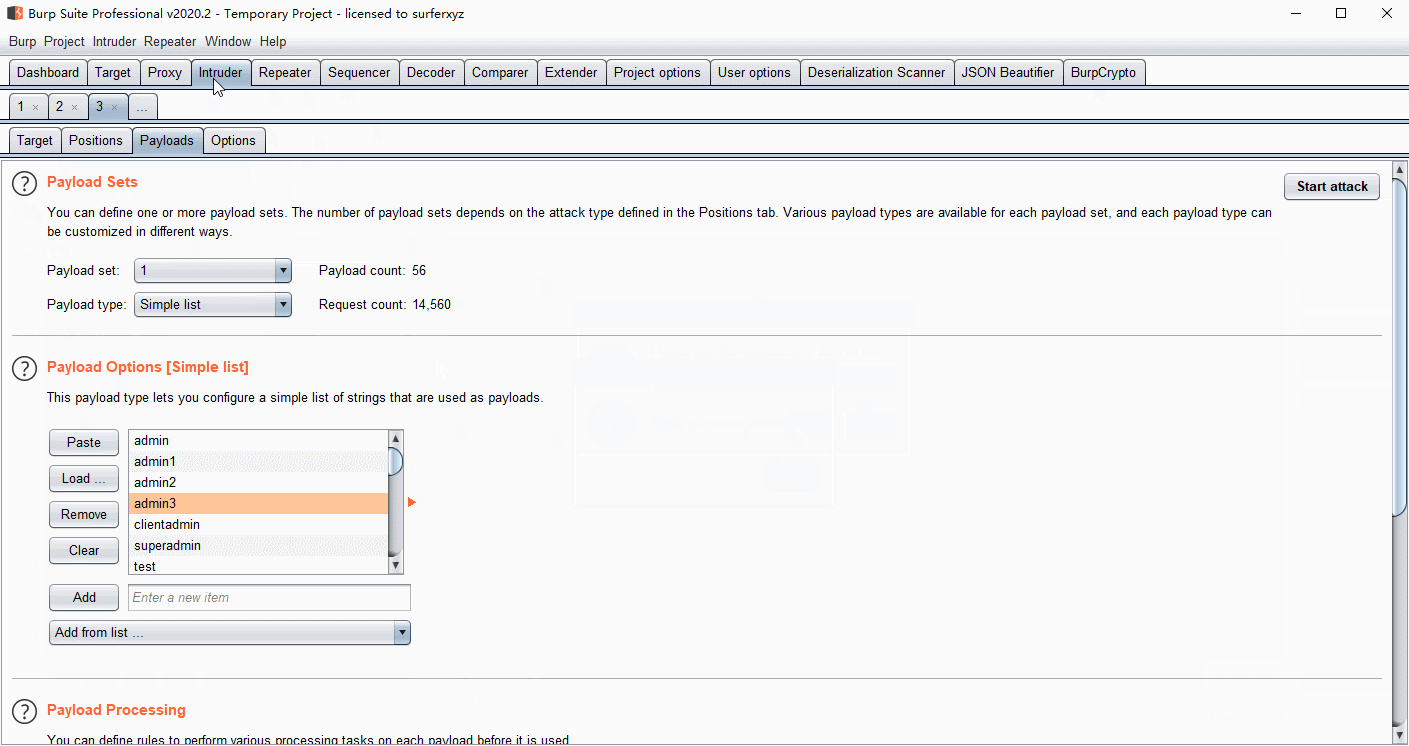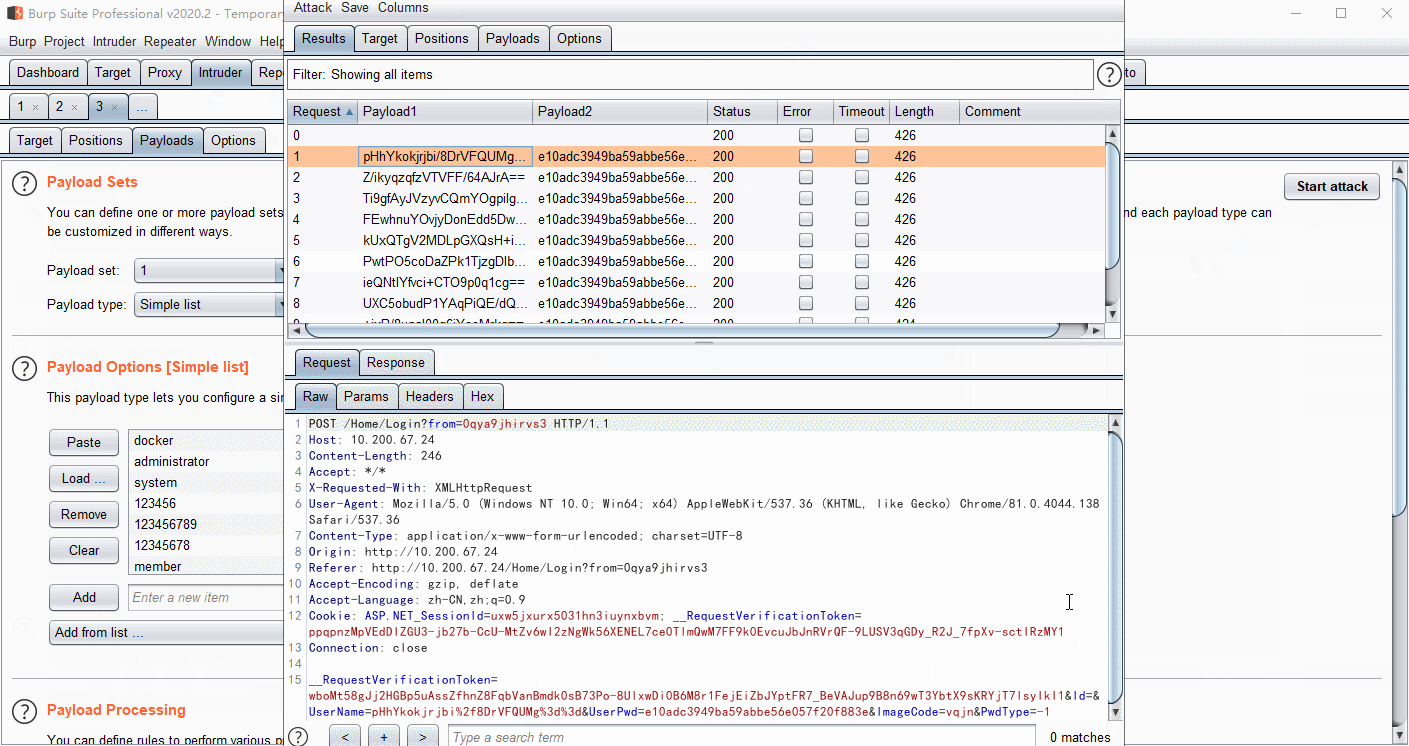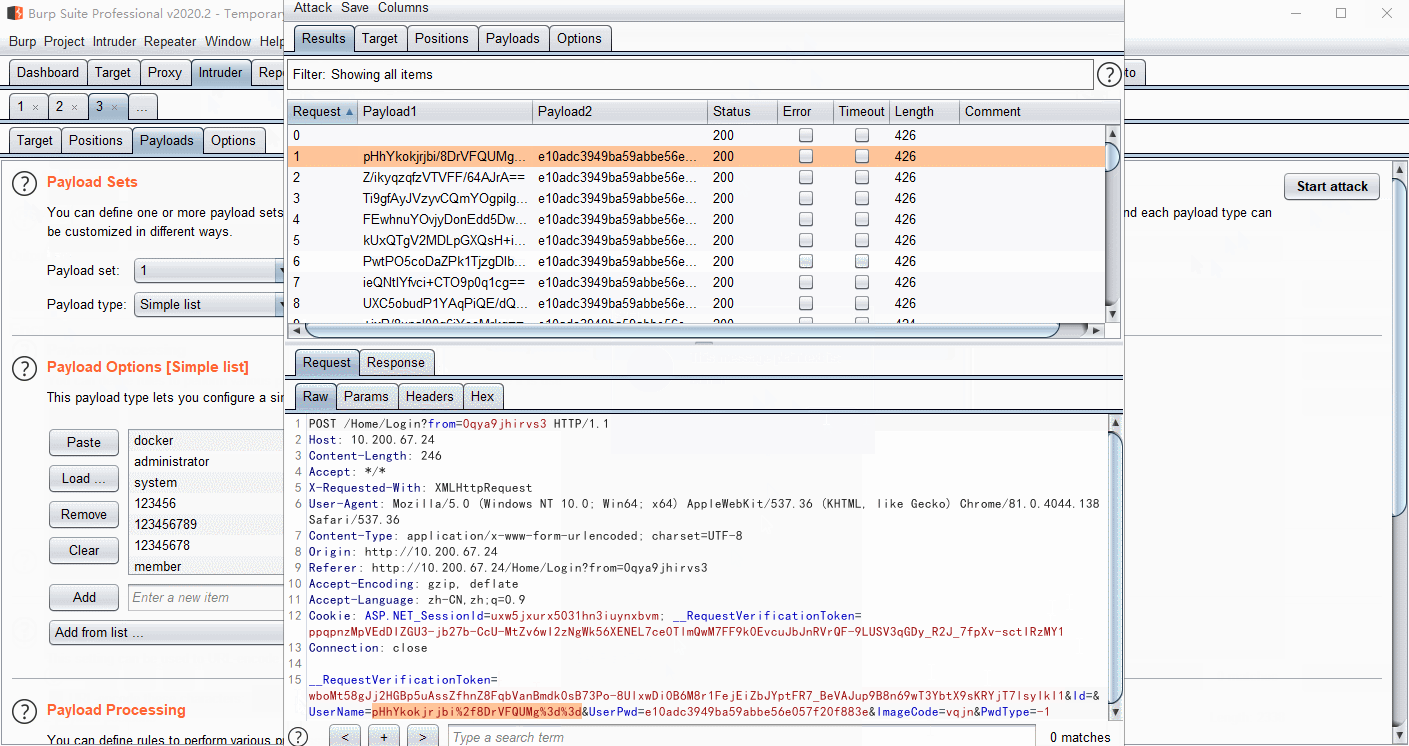
BurpSuite plugin for encrypting payloads with AES, RSA, DES, or custom JS code, enabling automated decryption of front-end encrypted traffic during…
 google/honggfuzz
Security oriented software fuzzer. Supports evolutionary, feedback-driven fuzzing based on code coverage (SW and HW based)
 danmcinerney/xsscrapy
XSS spider - 66/66 wavsep XSS detected
 trailofbits/polytracker
An LLVM-based instrumentation tool for universal taint tracking, dataflow analysis, and tracing.
 vigiloss/vigil
AI harness for long-running code audits, web pentests, and bug bounty hunting, built around how real investigations fail: anchored hypotheses, false…
 anonmoty/xxstrike
XSStrike based XSS scanner with custom features. Detects XSS vulnerabilities in web applications.
 spinkham/skipfish
Web application security scanner created by lcamtuf for google - Unofficial Mirror
 angorafuzzer/angora
Coverage-guided fuzzer that uses taint tracking and scalar optimization to solve path constraints without symbolic execution, improving branch…
 google/oss-fuzz-gen
LLM powered fuzzing via OSS-Fuzz.
 nccgroup/wssip
Application for capturing, modifying and sending custom WebSocket data from client to server and vice versa.
 michenriksen/jdam
A structure-aware JSON fuzzer
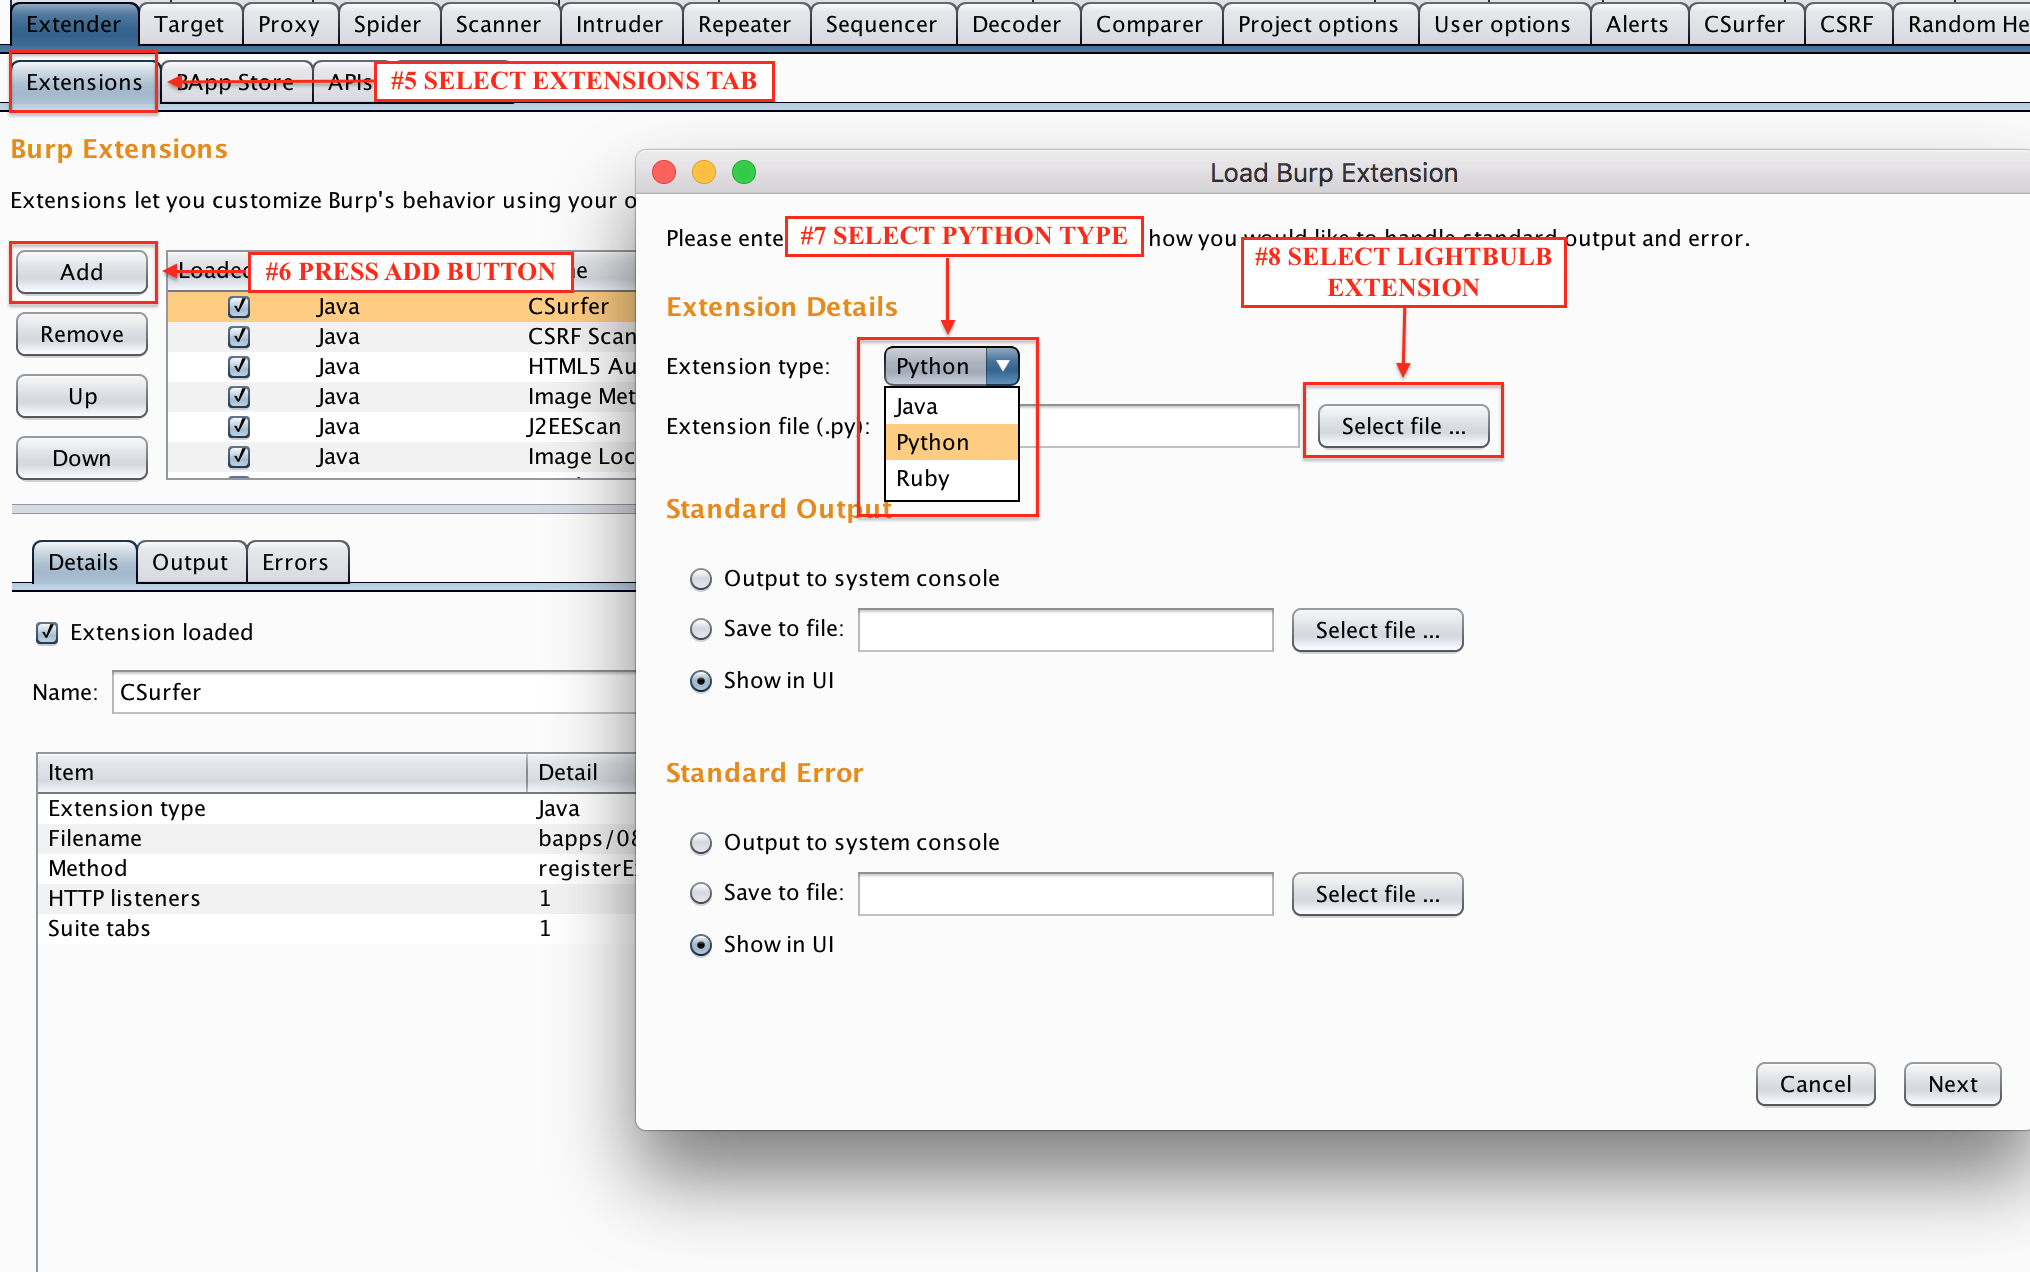 lightbulb-framework/lightbulb-framework
Tools for auditing WAFS
 jakabakos/cve-2017-9096-itext-xxe
Proof-of-concept exploit for CVE-2017-9096 demonstrating XML External Entity (XXE) injection in iText PDF library via malicious XMP metadata and form…
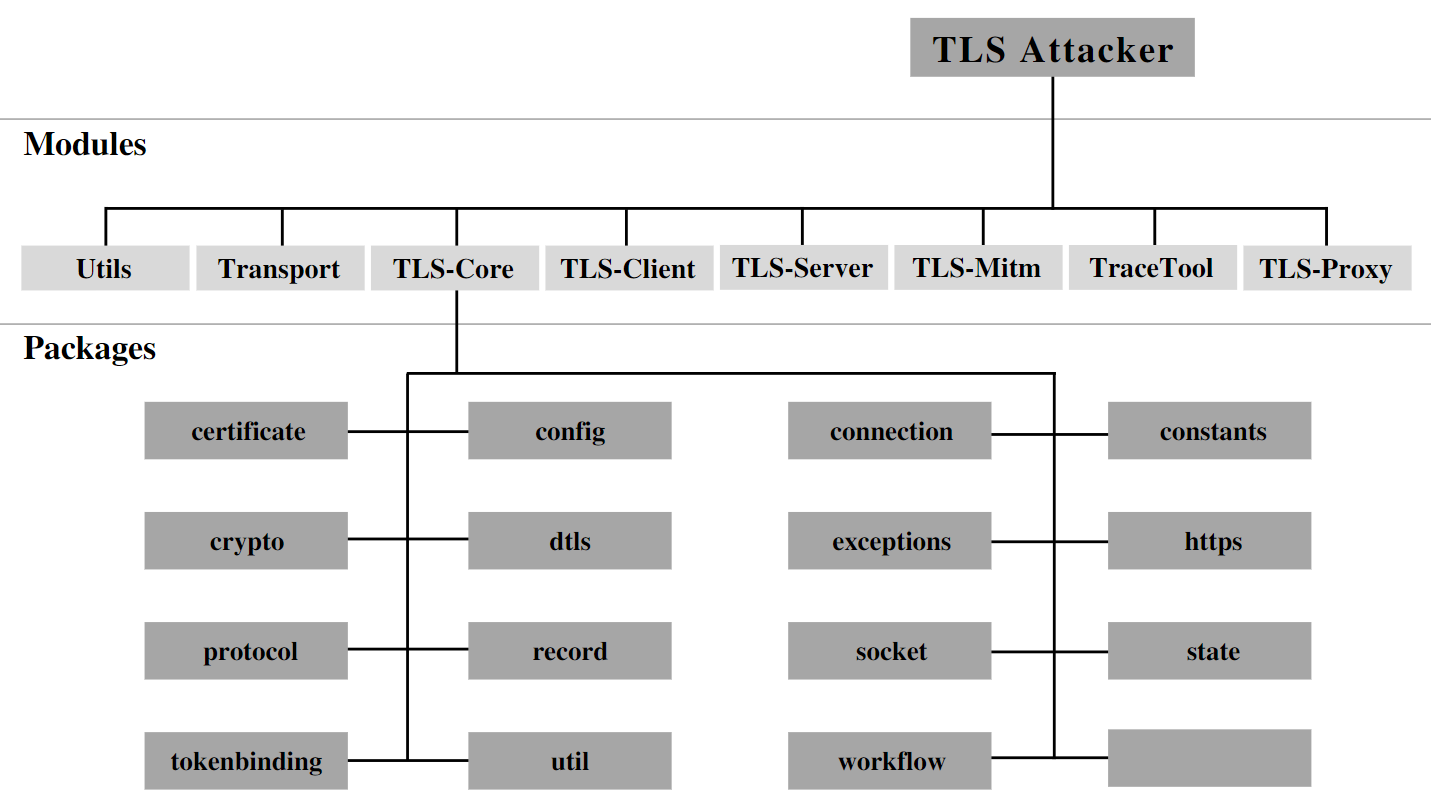 tls-attacker/tls-attacker
Java-based framework for systematic fuzzing and analysis of TLS libraries. Enables arbitrary protocol message crafting, modification, and testing of…