

scripts
 clausing/scripts
Collection of Python and Perl scripts for digital forensics, incident response, and network analysis, including hash signature tooling and packet…
digital-forensicsforensicsincident-response+5
84
clausing/scriptsCollection of Python and Perl scripts for digital forensics, incident response, and network analysis, including hash signature tooling and packet…
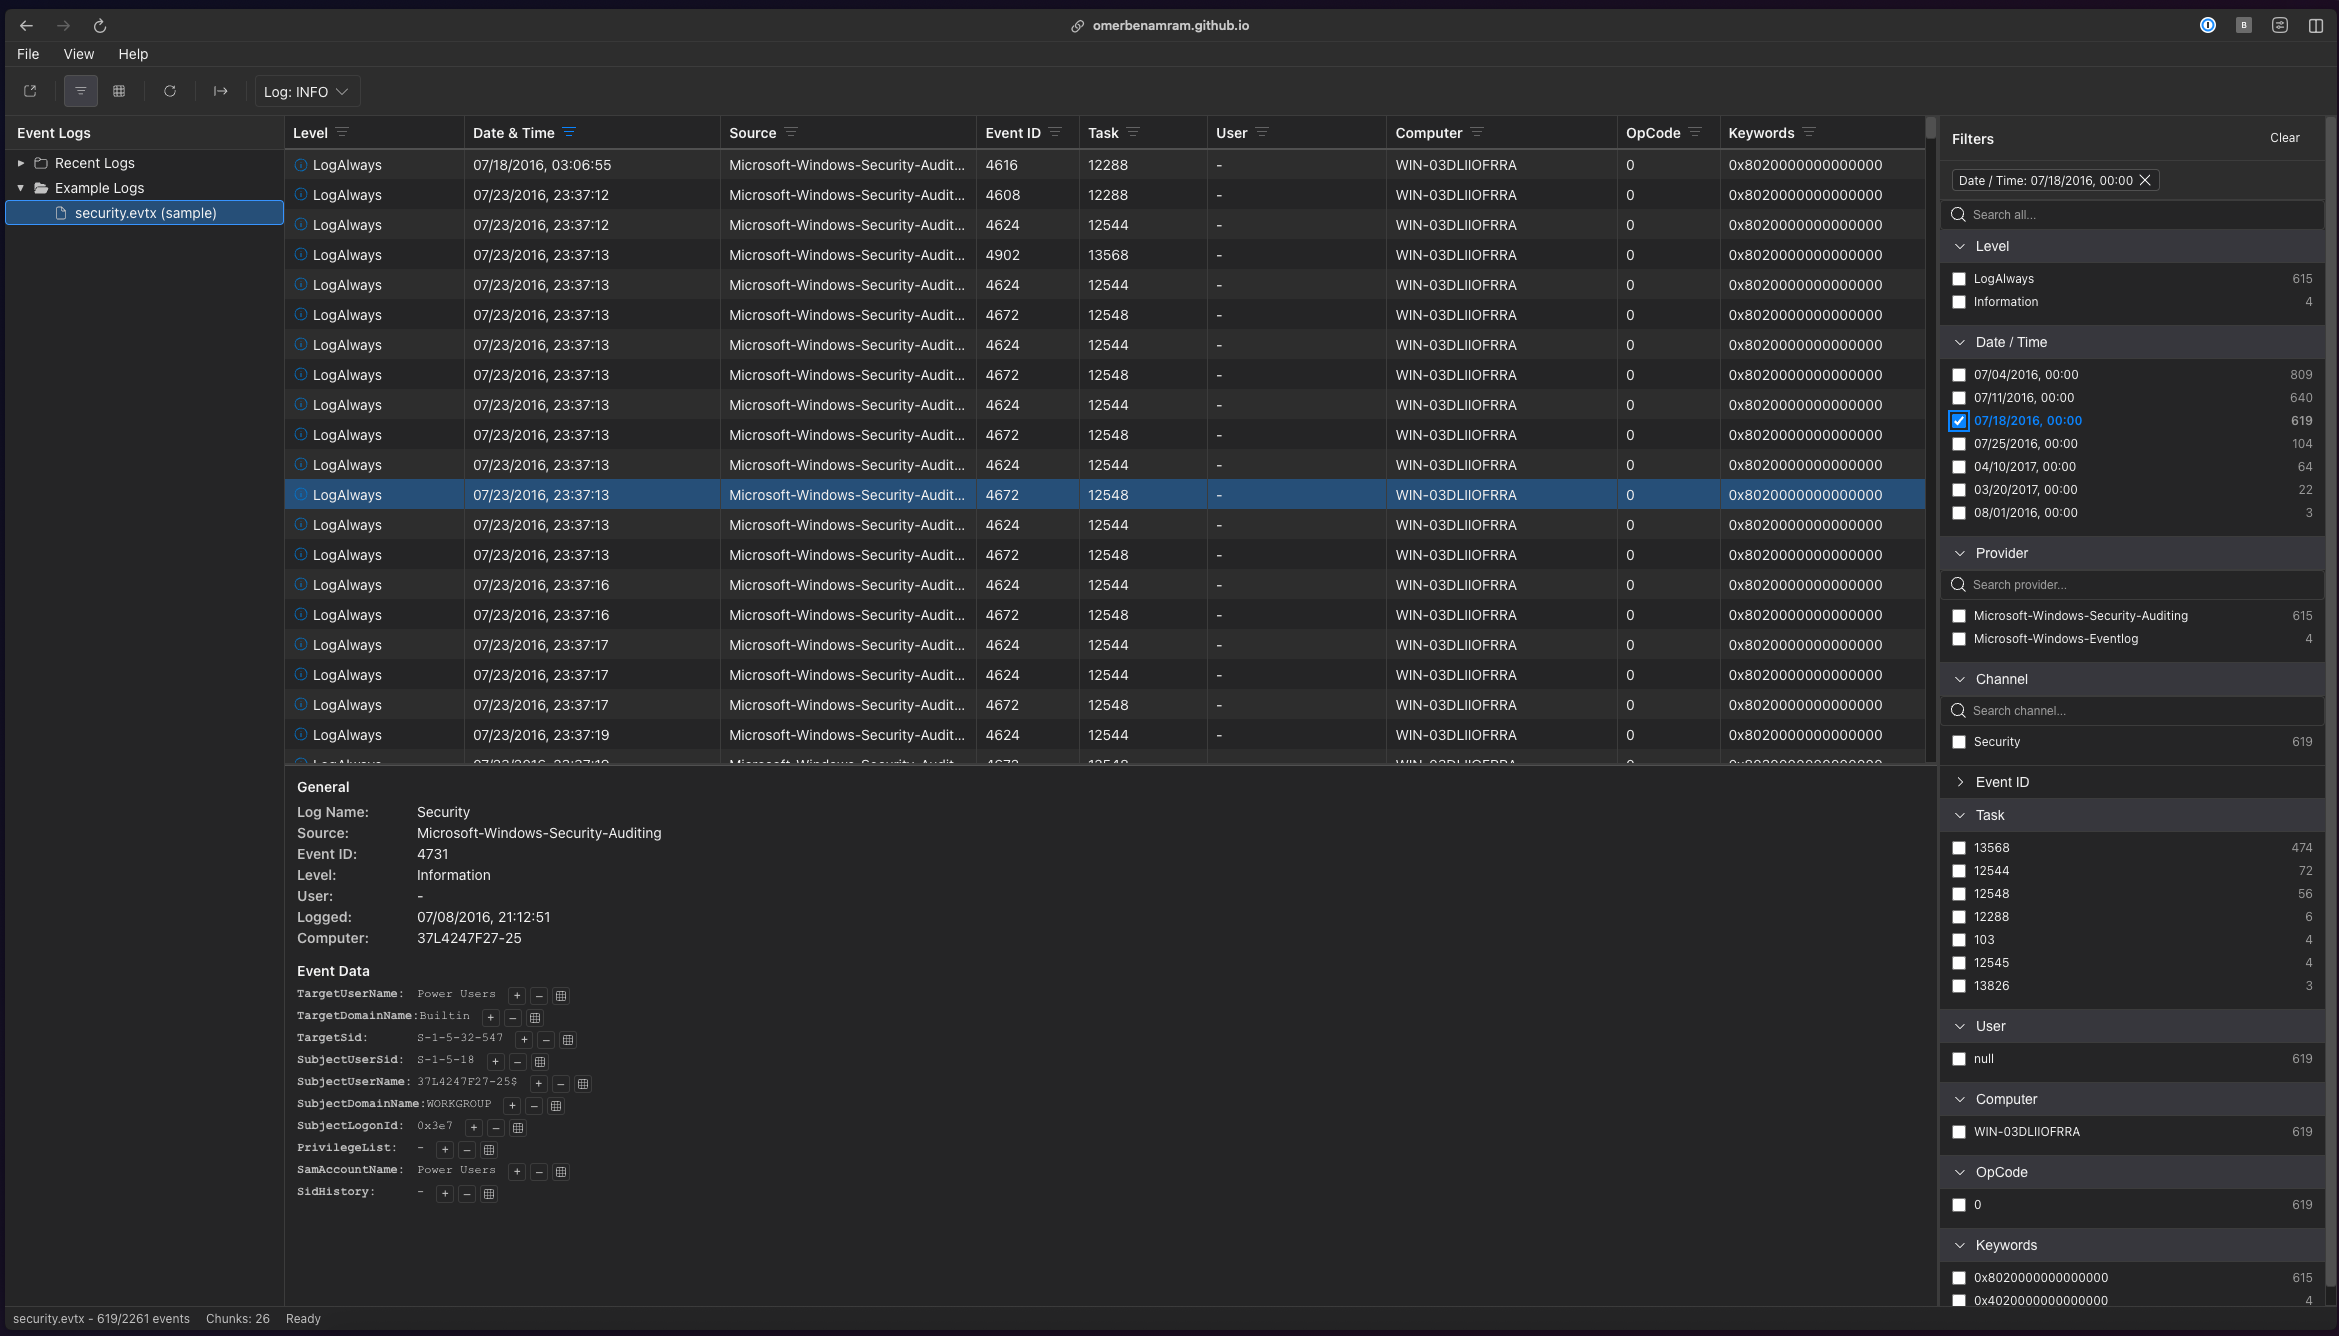 omerbenamram/evtx
A Fast (and safe) parser for the Windows XML Event Log (EVTX) format
 dougburks/so-crates
SO-CRATES: Security Onion Containerized Rapid Analysis of Threats, Evil, and Sus!
 yamato-security/hayabusa
Multi-threaded Windows event log forensics timeline generator and threat hunting tool with full Sigma rule support, producing CSV/JSON timelines for…
 wagga40/zircolite
A standalone SIGMA-based detection tool for EVTX, Auditd and Sysmon for Linux logs
 mandiant/macos-unifiedlogs
A cross platform parser for Apple UnifiedLogs!

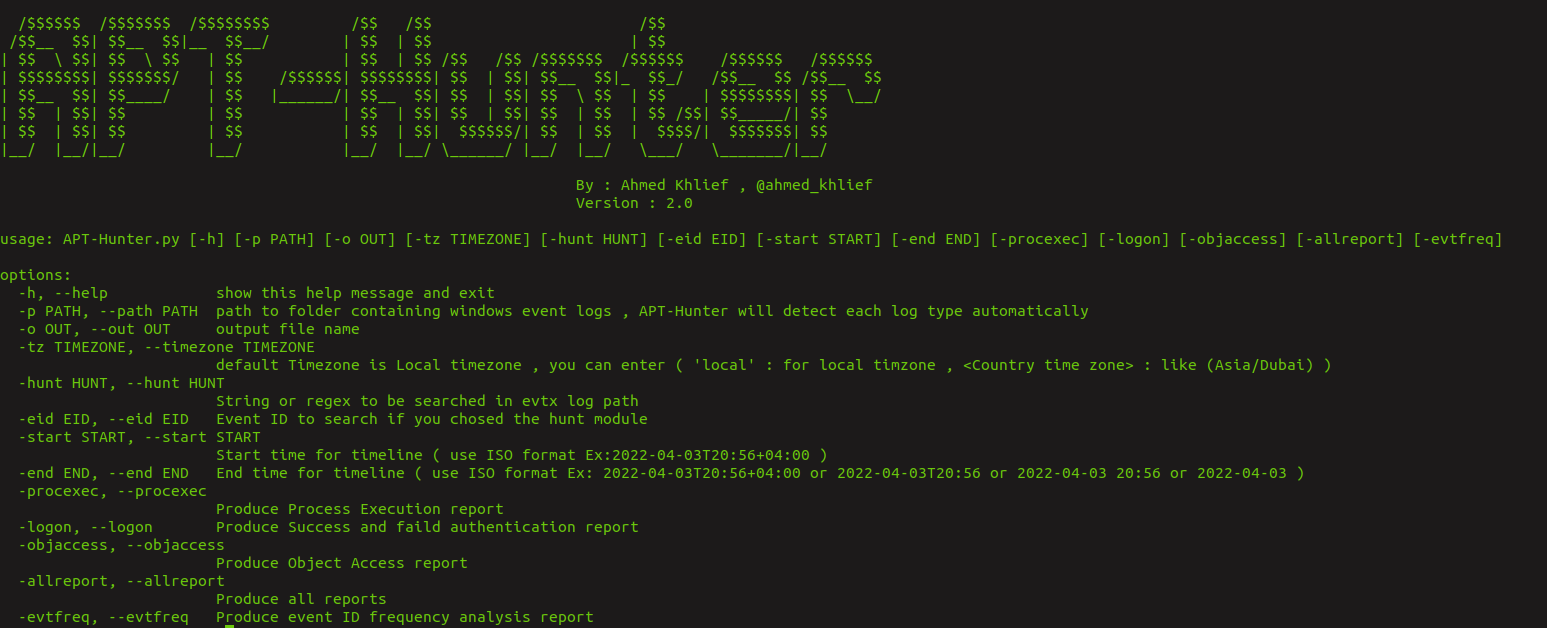 ahmedkhlief/apt-hunter
APT-Hunter is Threat Hunting tool for windows event logs which made by purple team mindset to provide detect APT movements hidden in the sea of…
 spieglt/whatfiles
Log what files are accessed by any Linux process
 lethal-forensics/macos-collector
macos-collector - Automated Collection of macOS Forensic Artifacts for DFIR
 invictus-ir/alfa
Automated forensic analysis tool for Google Workspace audit logs. Acquires all log types, maps events to MITRE ATT&CK Cloud Framework, and identifies…
 nu11secur1ty/pastokrapacefleciks
Analyzes .pcapng files to generate HTML reports for network traffic inspection and forensic review.
 thakur2309/pagasus-pro
Python ADB-based Android device management and security audit toolkit with an interactive menu for root detection, permission dumps, debuggable app…
 mrrawbit/sonicwall-sma1000-zero-day-ioc-check
Unofficial Bash IoC checker for SonicWall SMA1000 appliances affected by actively exploited CVE-2026-15409 and CVE-2026-15410.
 meirwah/awesome-incident-response
Curated index of incident response and DFIR tools, including memory and disk forensics, evidence collection, log analysis, playbooks, and educational…
 abc1230940/soc336-windows-ole-zero-click-rce-exploitation-detected-cve-2025-21298
SOC336 - Windows OLE Zero-Click RCE Exploitation Detected (CVE-2025-21298) Walkthrough
 airbus-cert/etl-parser
Event Trace Log file parser in pure Python
 mithileshan/soc-investigation-lab
End-to-end SOC investigation: CVE-2011-2523 kill chain, multi-source log correlation, incident report — MITRE ATT&CK T1190