

spidump
 wrongbaud/spidump
Tool for reconstructing SPI flash images via logic analyzer captures
digital-forensicsembedded-systems-securityfirmware-analysis+7
48 days ago
wrongbaud/spidumpTool for reconstructing SPI flash images via logic analyzer captures
 qsecure-labs/deadmatter
Offset Independent Credential Extraction Tool
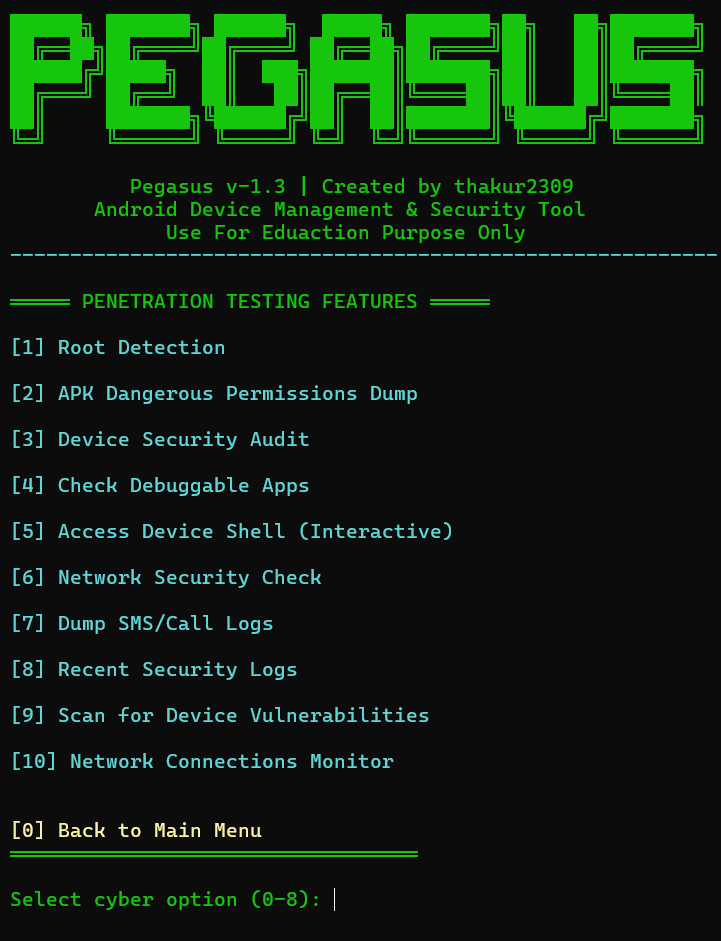 thakur2309/pagasus-pro
Python ADB-based Android device management and security audit toolkit with an interactive menu for root detection, permission dumps, debuggable app…
 fkie-cad/sandroid_dexray-intercept
A Android malware analysis tool that creates comprehensive runtime profiles by hooking into application behavior across cryptography, file systems,…
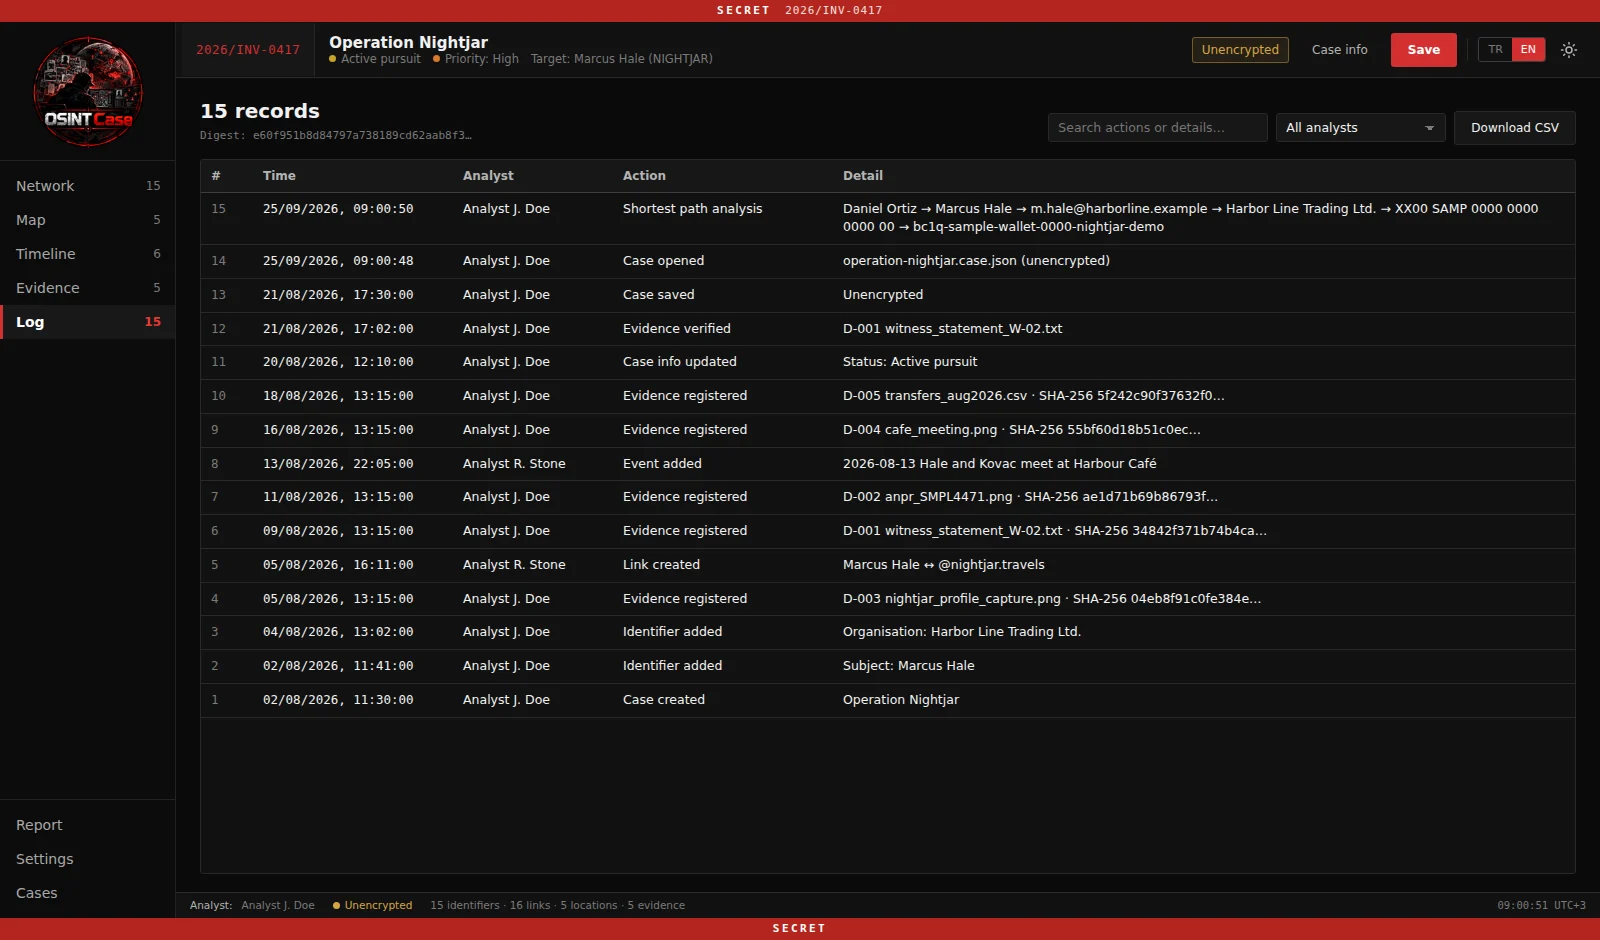 emrekybs/osintcase
An OSINT investigation case mapping tool for organizing entities, relationships, evidence, and intelligence.
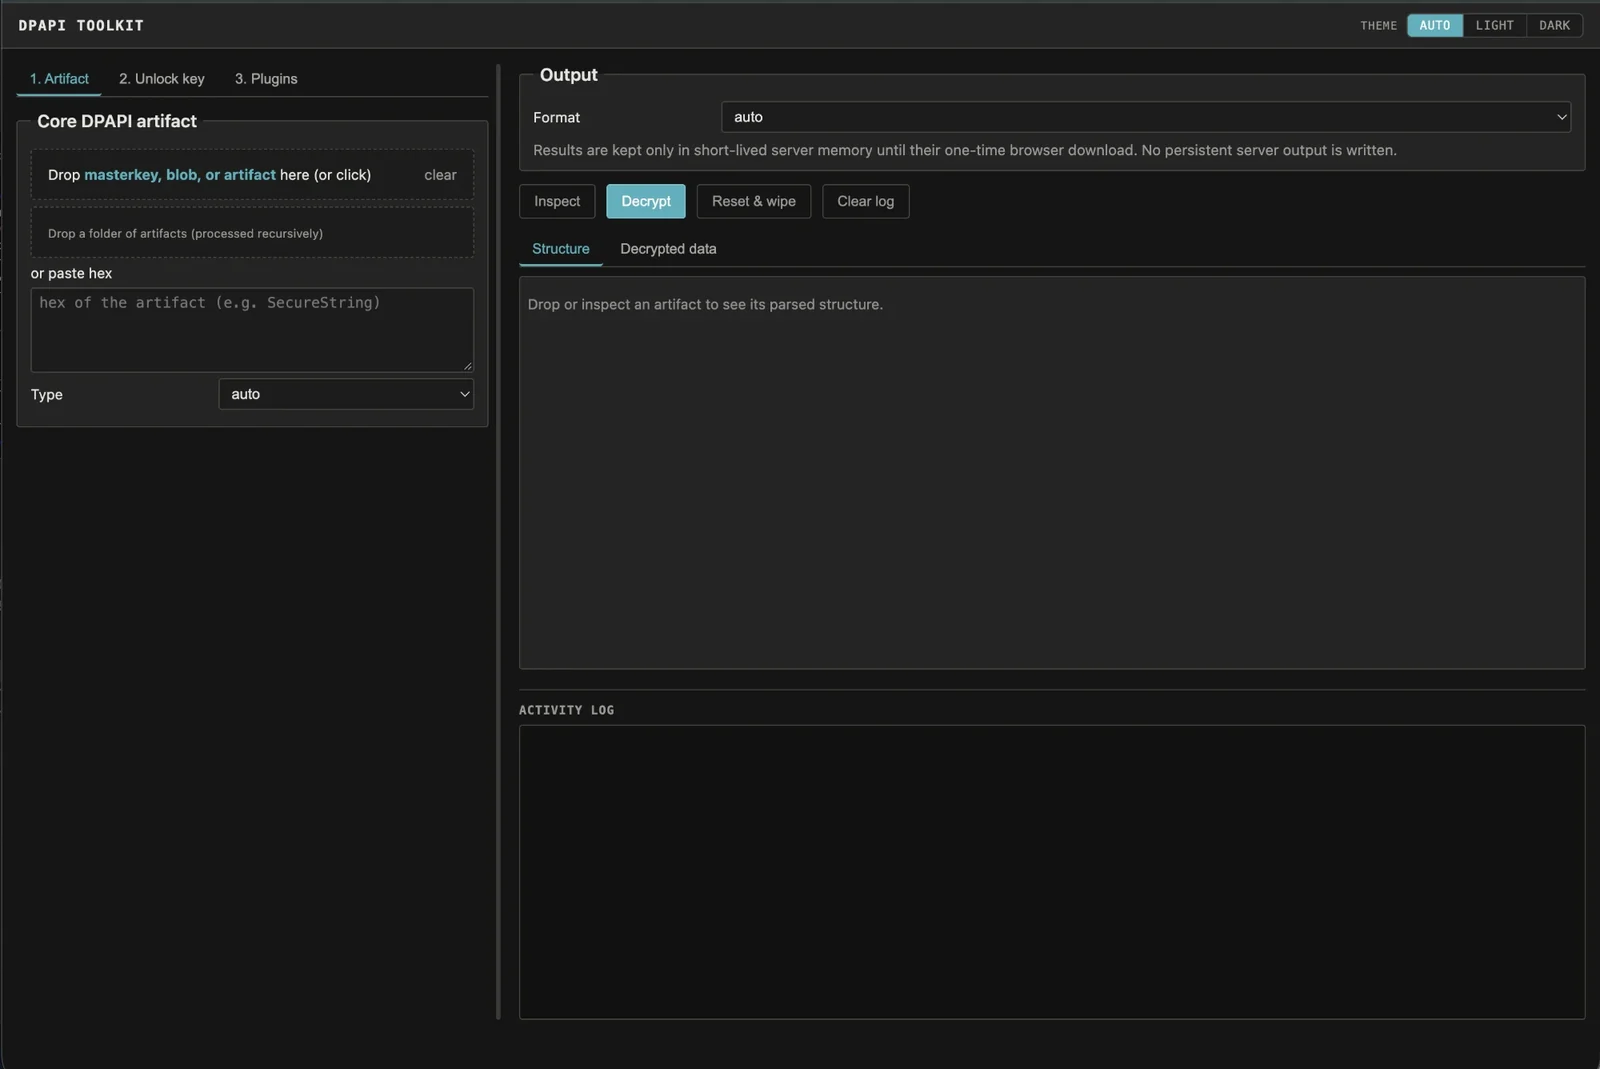 crypt0p3g/dpapi-toolkit
Drop any Windows DPAPI artifact and it identifies the format and the exact master key it needs, then decrypts once you supply the key. Offline, CLI +…
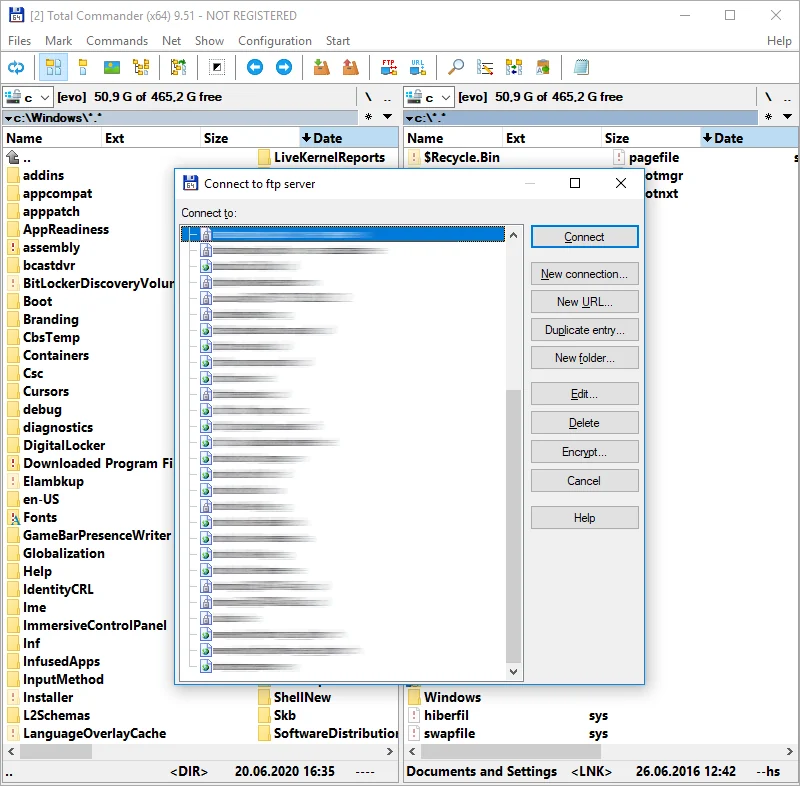 pelock/total-commander-ftp-password-recovery-tool-python
Total Commander FTP Password Recovery Tool for Python allows you to decrypt the FTP account password information for all Total Commander versions…
 withsecurelabs/esfang
ESF modular ingestion tool for development and research.
 qg5casz/walletool
Extracts cryptocurrency private keys and addresses from wallet.dat files for Bitcoin and Litecoin, enabling wallet recovery and forensic analysis.
 s4larie/walletool
A utility for extracting cryptocurrency wallet data from wallet.dat files.
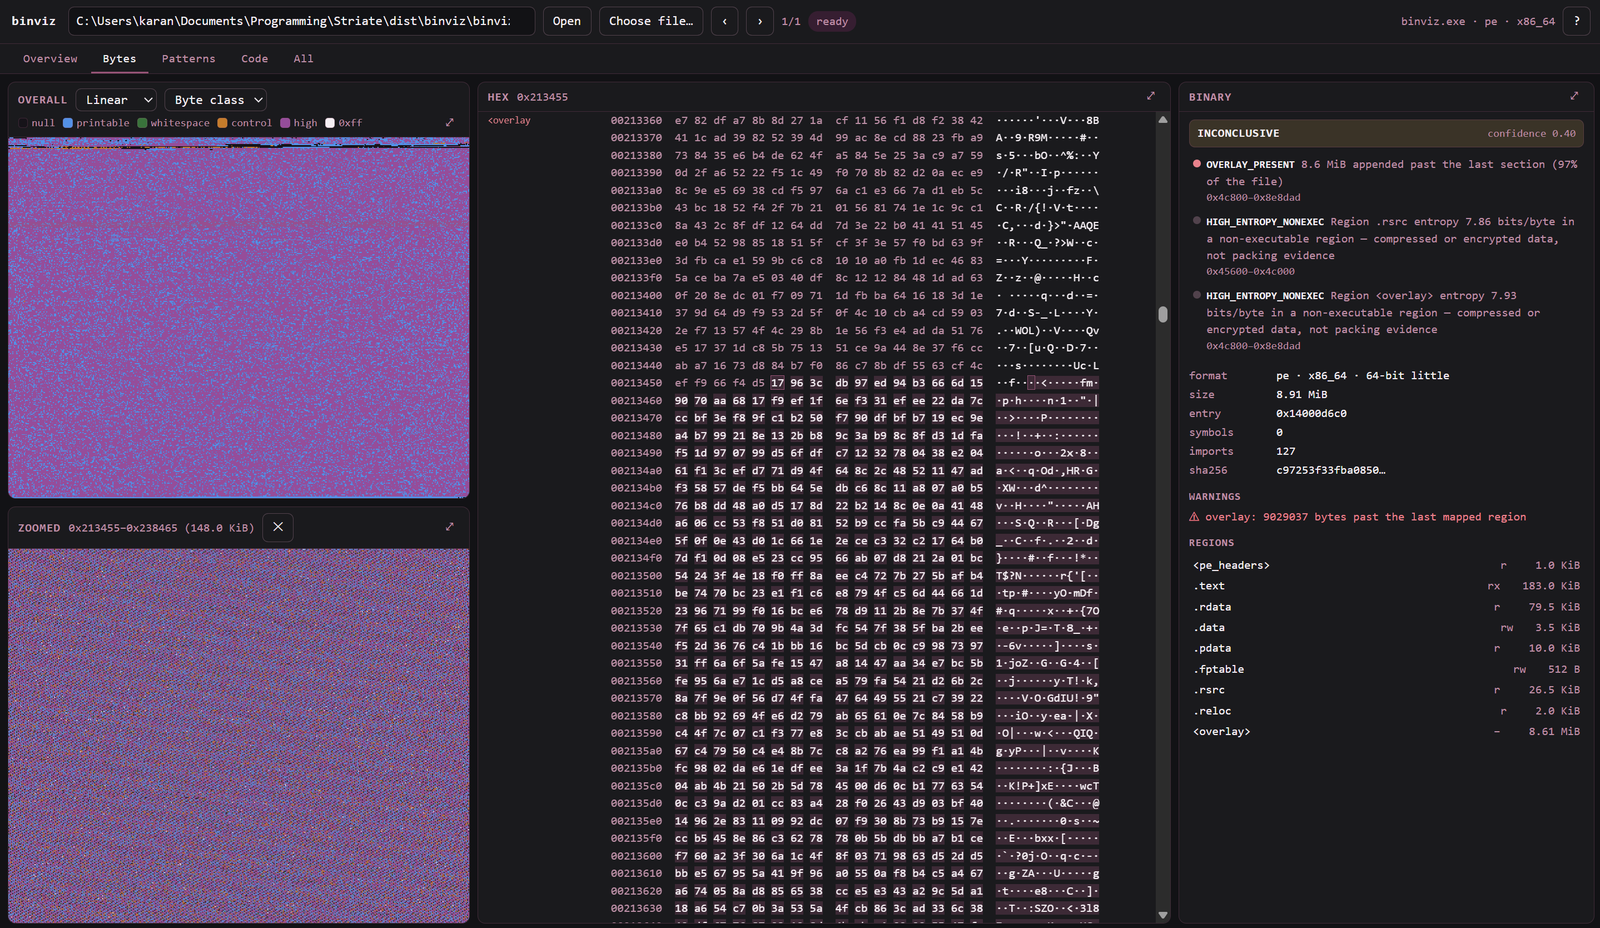 karankantaria/binviz
Binary visualiser and triage tool — entropy, byte-class and Hilbert surfaces, dot plots and control-flow graphs over one shared address-space model.
 google/timesketch
Collaborative forensic timeline analysis platform for ingesting, searching, and annotating event logs to support incident response and DFIR…
 microsoft/avml
Portable Linux RAM acquisition tool for forensics and incident response, capturing LiME-compatible images with optional compression and remote…
 dfir-orc/dfir-orc
Forensics artefact collection tool for systems running Microsoft Windows
 infobyte/wiremax
Lua-based Wireshark postdissector that decrypts and parses Ubiquiti AirMAX/RouterBoard 802.11 vendor IEs into filterable fields.
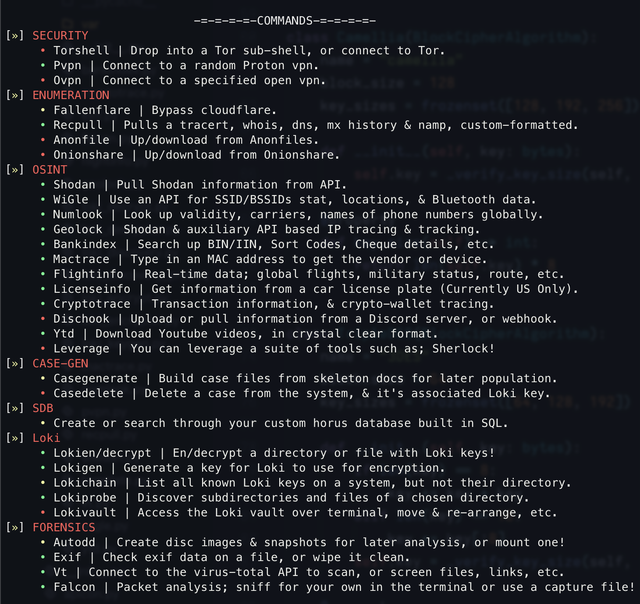 6abd/horus
An OSINT / digital forensics tool built in Python
 theevidencehunter/forensix
Digital Forensics Intelligence Framework
 nccgroup/impossibletravelloganalysis
Basic log analysis tool to detect impossible travel via IP address geographic information