
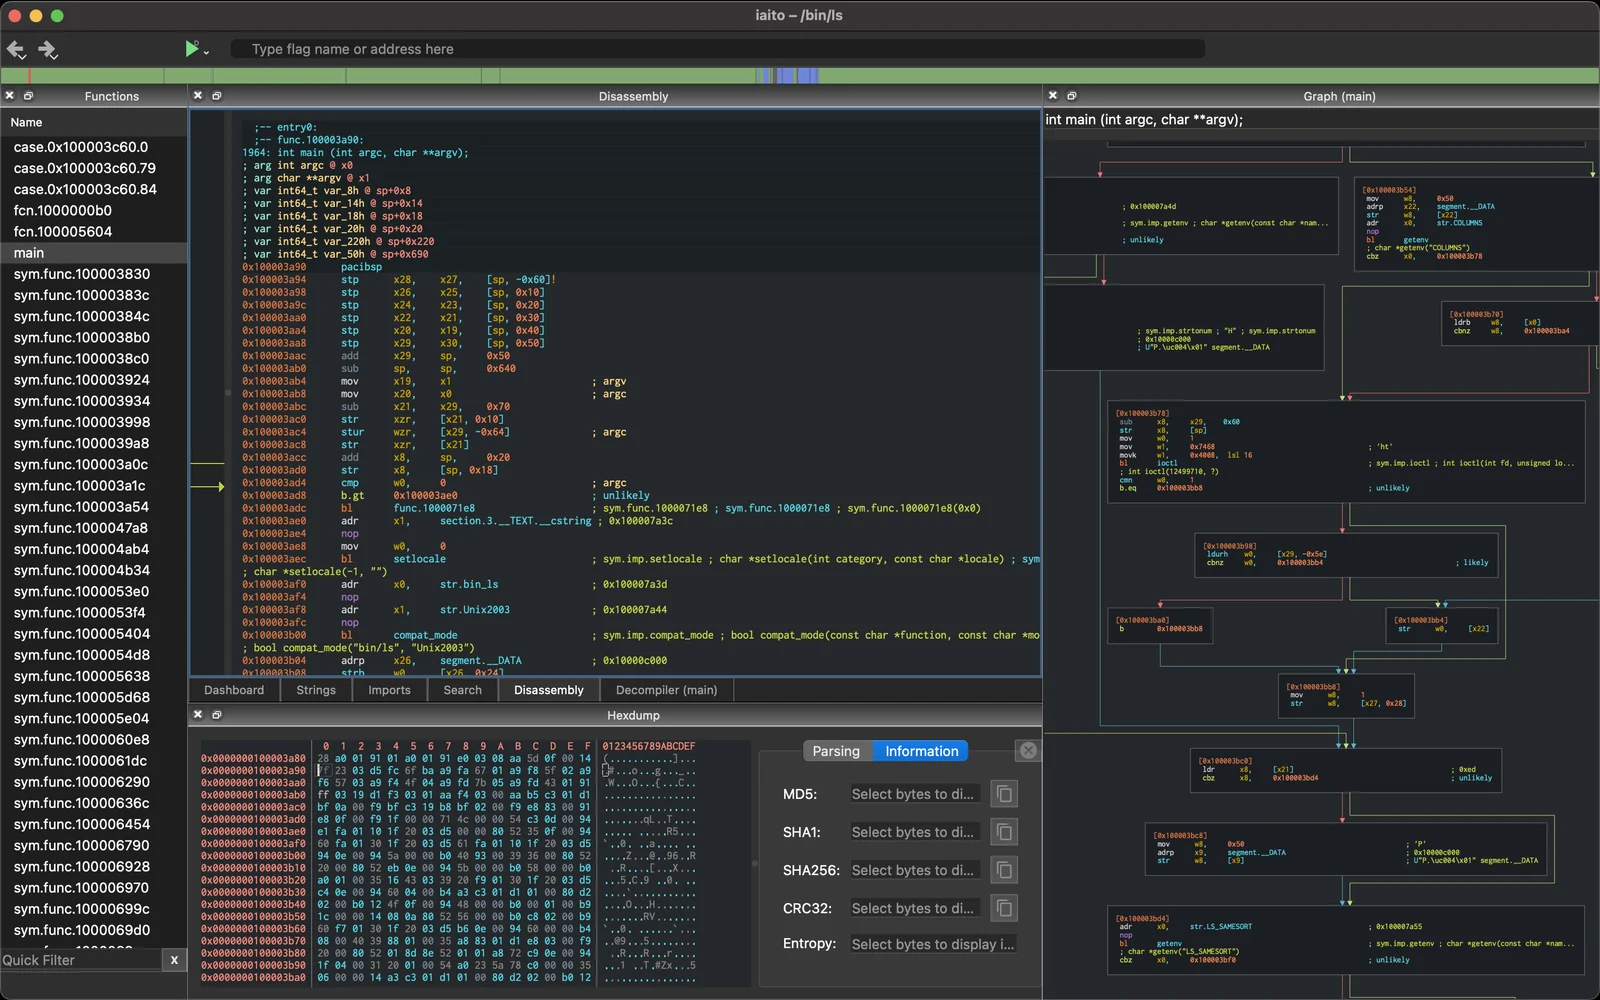
iaito
 radareorg/iaito
Qt-based graphical interface for the radare2 reverse engineering framework, providing disassembly, binary analysis, debugging, patching and forensics…
binary-analysisbinary-exploitationdebuggers+5
1.7k
radareorg/iaitoQt-based graphical interface for the radare2 reverse engineering framework, providing disassembly, binary analysis, debugging, patching and forensics…
 kowntaewook/mcptrace
Volatility 3 plugin that carves MCP/JSON-RPC message candidates from Windows and Linux memory dumps, preserving raw bytes, addresses, and SHA-256 for…
 jankammerath/bogusmips
Forensic analytics for disassembly, reassembly, reverse engineering and auditing of Android apps
 phpatch/weblogchecker
Free access-log compromise analyzer: webshell interactions, exploitation patterns and brute-force bursts in your Apache/nginx logs - severity,…
 gary23w/hodometer
A single-file native Windows tray application (C, Win32, no runtime) that shows exactly which program is sending and receiving bytes and to which…
 interplains/zero-breach-toolkit
Free, open-source, offline checks for traces of known mercenary spyware. Works on Windows, macOS and Linux, Android phones and iPhone backups.
 hunterdii/tryhackme-roadmap
Hello, aspiring hackers! 🕵️♂️ Here’s a list of 500+ Free TryHackMe rooms to kickstart your cybersecurity journey. These rooms are absolutely free,…
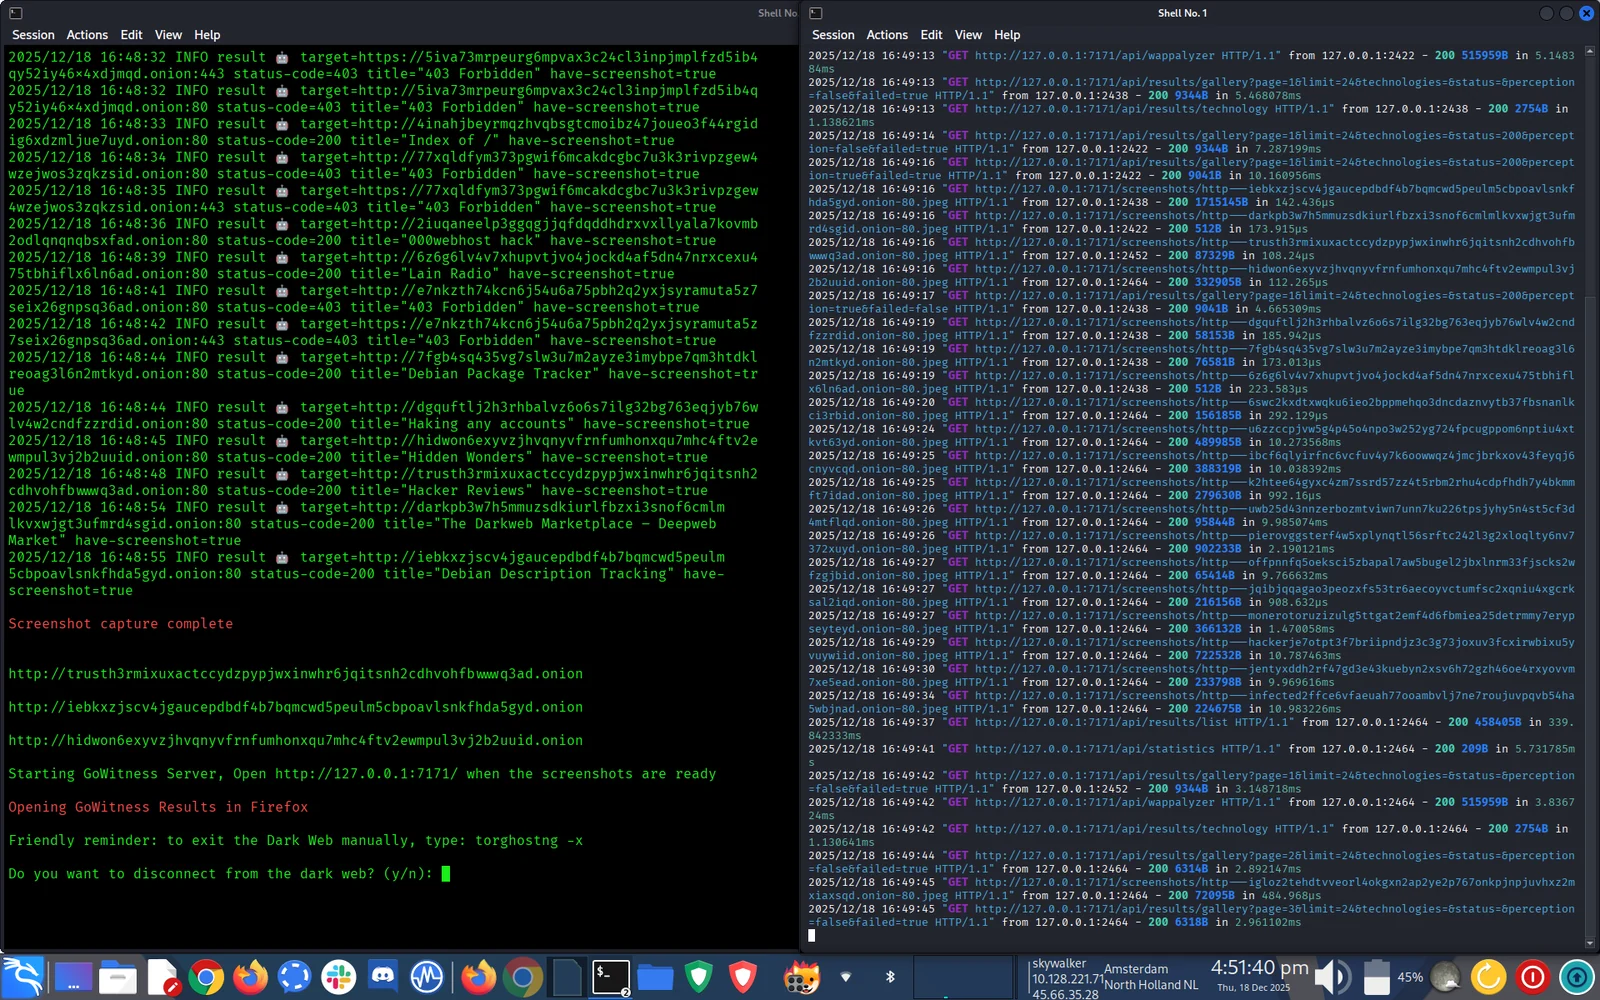 aryanguenthner/darkfox
CTI Cyber Threat Intelligence OSINT Dark Web Deep Web Research. Ransomware gang information gathering tool.
 evyatarmeged/stegextract
Bash script that extracts trailing data, embedded files, and hidden strings from PNG, JPG, and GIF images using magic numbers and hexdump analysis.
 thehackingsage/hackdroid
Curated catalog of 364 Android pentesting and security APKs organized by category, covering forensics, MITM, sniffing, OSINT, wireless, and privacy…
 giordanosconti/icloudkitextractor
Experimental .NET/WPF forensic toolkit for iCloud auth, CloudKit/MMCS backup download, and Octagon/PCS recovery (ADP, Recovery Key, Lockdown Mode).…
 doctorwebltd/malware-iocs
Curated Indicators of Compromise (IOCs) from Doctor Web malware investigations, published for threat intelligence, detection engineering, and…
 owasp/agentic-evidence
OWASP reference project for agentic AI security evidence: correlates agent execution, identity, tool calls, and authorization decisions into…
 asngs/agenttriage-open-source
Cross-agent tracing and security-diagnosis system for tool-using LLM agents: normalizes trace events, builds provenance graphs, extracts…
 seclog-open/seclog
Collects multi-source security logs from reproducible Docker attack scenarios, builds attack chains, and provides the SecLog-Bench-216 benchmark for…
 aide/aide
File integrity monitoring tool that detects unauthorized changes to monitored files and directories using attribute checks, multiple hash algorithms,…
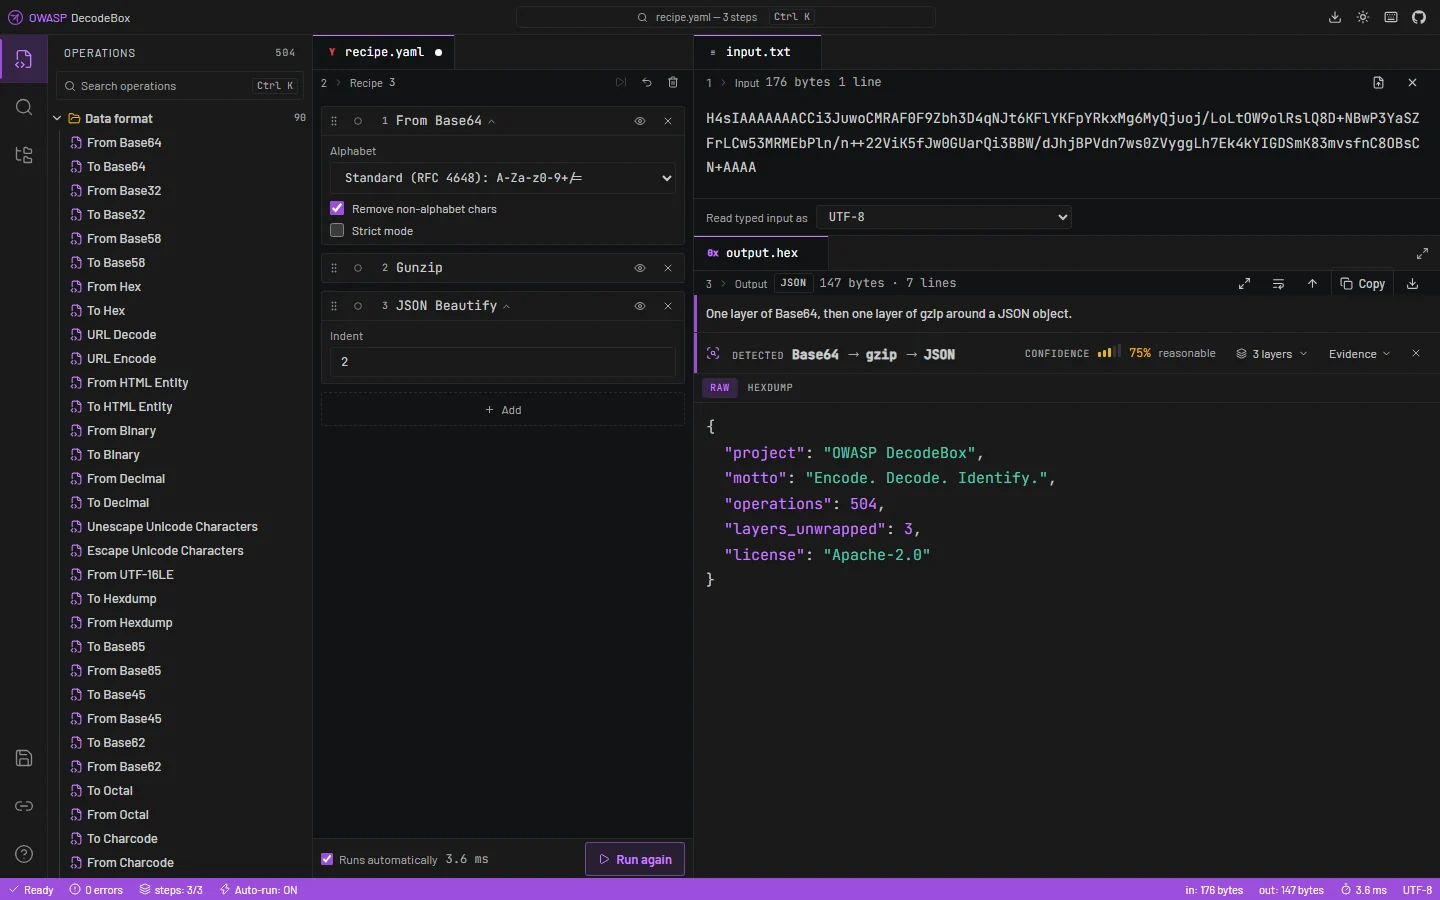 owasp/decodebox
Client-side workbench that auto-detects, recursively decodes, and analyses unknown or layered data, extracting indicators and CWE-tagged security…
 nextronsystems/iocs
Indicators of compromise from to analysis and research by Nextron Threat Research team