
CVE-2022-4510
 electr0sm0g/cve-2022-4510
Exploit for CVE-2022-4510 enabling remote command execution in Binwalk firmware analysis tool. Provides proof-of-concept code for security testing…
binary-analysisexploitationfirmware-analysis+2
electr0sm0g/cve-2022-4510Exploit for CVE-2022-4510 enabling remote command execution in Binwalk firmware analysis tool. Provides proof-of-concept code for security testing…

 ospg/binwalk
Firmware Analysis Tool
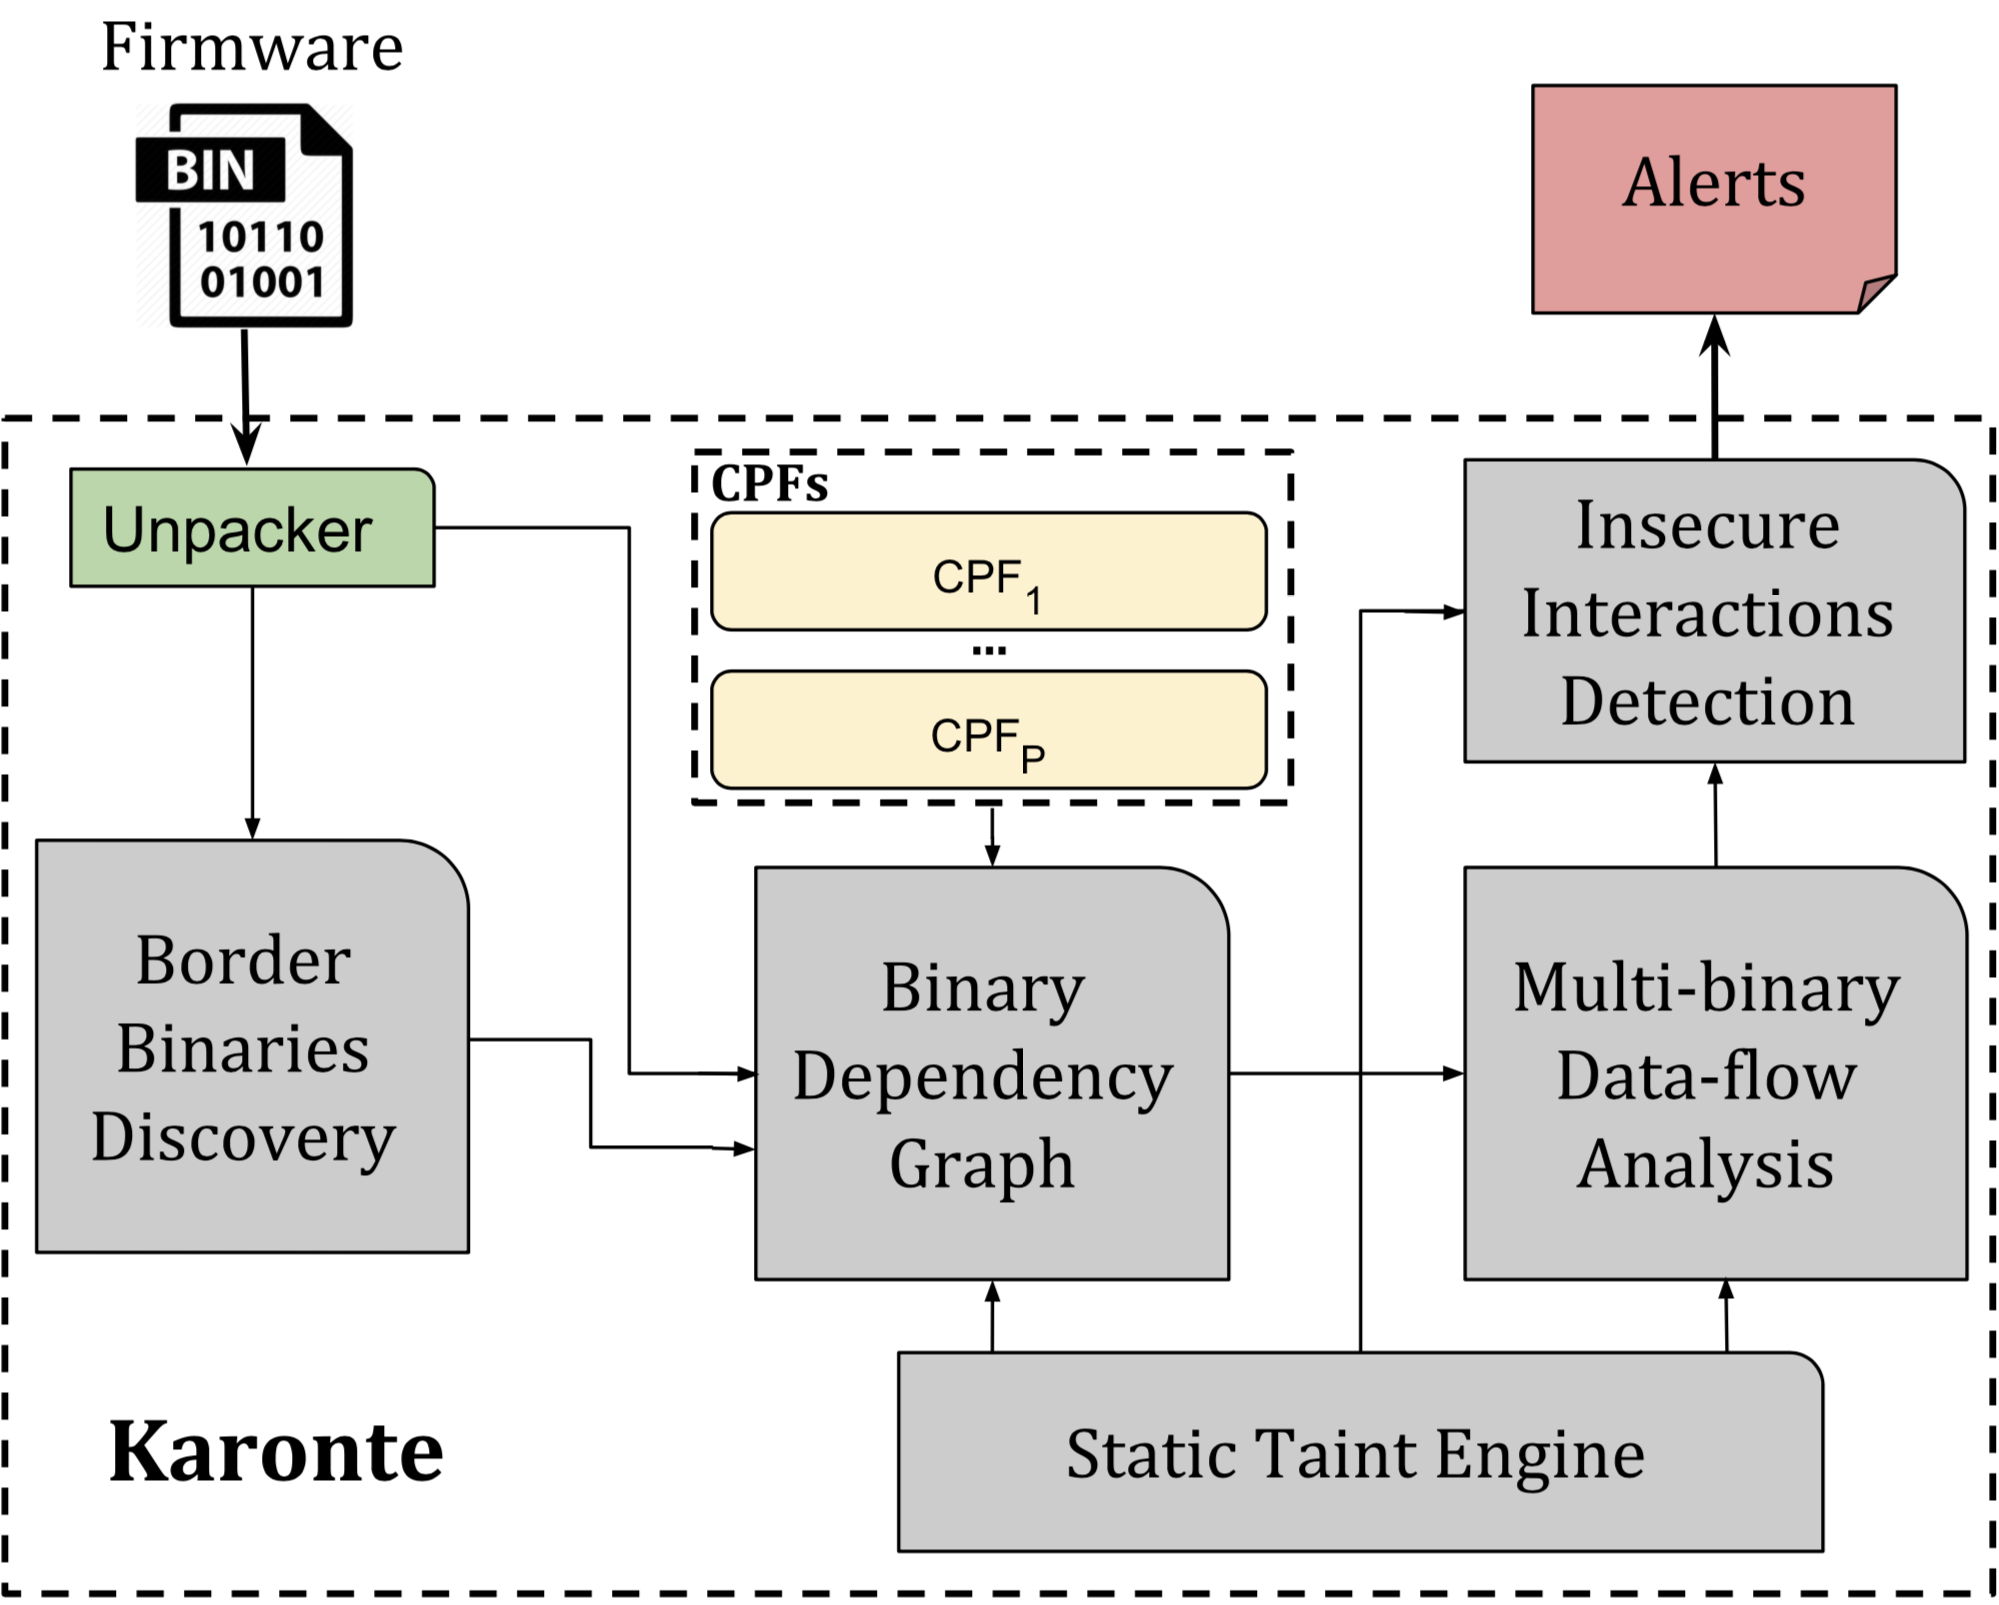 ucsb-seclab/karonte
Karonte is a static analysis tool to detect multi-binary vulnerabilities in embedded firmware
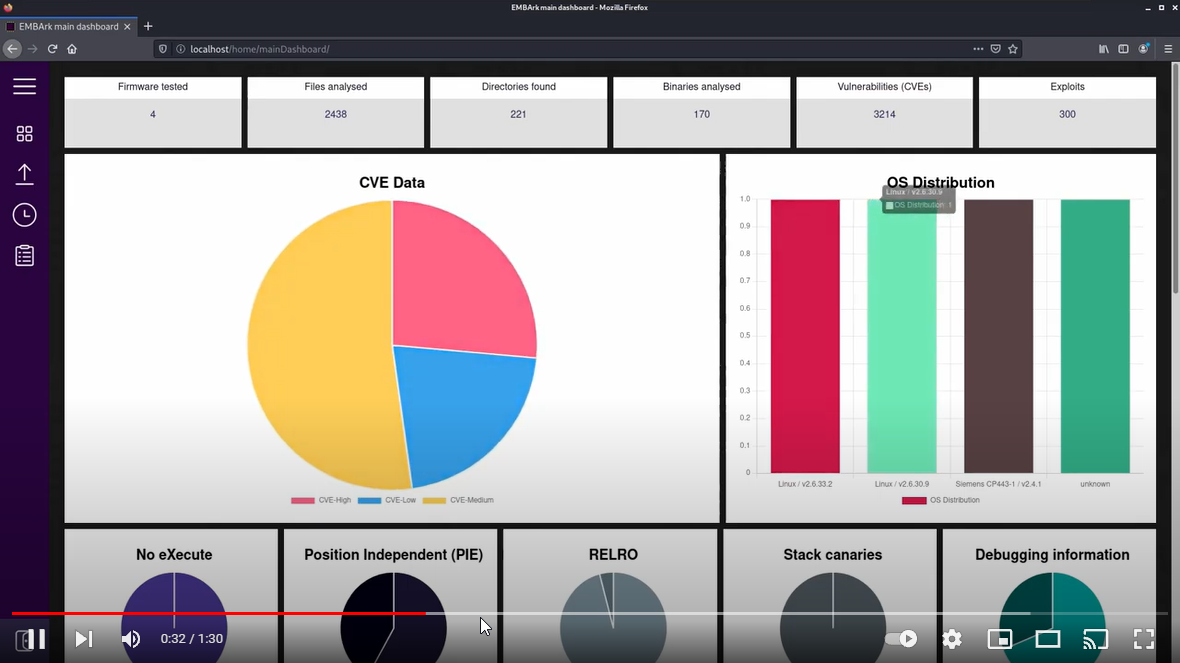 e-m-b-a/embark
Centralized firmware scanning and reporting platform with a web UI, REST API, and automated analysis workflows for securing embedded/IoT devices.
 yeggor/uefi_retool
A tool for UEFI firmware reverse engineering
 marin-m/vmlinux-to-elf
A tool to recover a fully analyzable .ELF from a raw kernel, through extracting the kernel symbol table (kallsyms)
 forescout/project-memoria-detector
Active fingerprinting tool that identifies 16 embedded TCP/IP stacks on network devices using ICMP, TCP, HTTP, SSH, and FTP probing techniques for…
 doudoudedi/hackembedded
This tool is used for encrypt backdoor,shellcode,socks5 proxy generation,Information retrieval and POC arrangement for various architecture devices
 kkamagui/napper-for-tpm
TPM vulnerability checking tool for CVE-2018-6622. This tool will be published at Black Hat Asia 2019 and Black Hat Europe 2019
 infobyte/draytek-arsenal
Reverse Engineering and Observability toolkit for Draytek firewalls
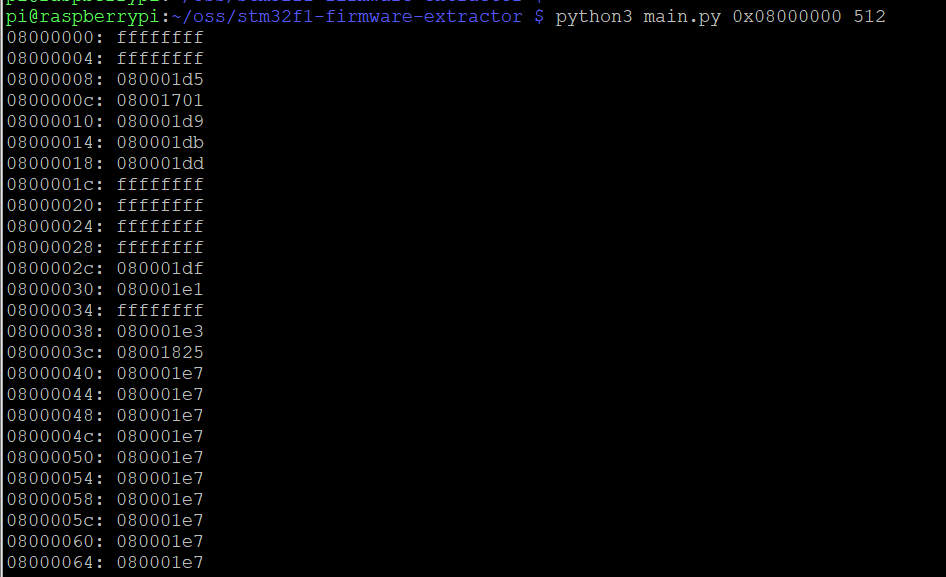 wuxx/cve-2020-8004
Exploit tool for CVE-2020-8004 targeting STM32F1 microcontrollers, enabling firmware extraction via OpenOCD and Python scripts to bypass readout…
 bishopfox/sonicrack
Decrypt encrypted SonicOSX firmware images
 jatinkapilaq1/intel-me-research
Talk to your Intel Management Engine directly — zero-dependency Python tool. Finds memory leaks, partition manifest, live MKHI probing. First public…
 synacktiv/synodecrypt
A tool to decrypt all Synology encrypted archives (SPK, PAT, ...)
 finngineering/apxutil
A tool to manipulate Schneider Electric PLC archive files
 bahaabdelwahed/st
IoT protocol threat detection tool that scans devices for vulnerabilities, searches CVEs/PoCs, analyzes firmware, and monitors MQTT/UPnP traffic to…
 nikitapbst/cve-2019-6260
Low-level hardware debugging and security assessment tool for ASPEED BMC AHB interfaces. Probes PCIe, LPC, and UART interfaces to read/write…