NGINX-CVE-2026-123007-CVE-2026-123633

Shell-based proof-of-concept material for NGINX vulnerabilities CVE-2026-123007 and CVE-2026-123633, covering reproduction and verification of the…

Shell-based proof-of-concept material for NGINX vulnerabilities CVE-2026-123007 and CVE-2026-123633, covering reproduction and verification of the…

Python PoC exploiting CVE-2026-115560, a PHP session upload-progress serialize-handler mismatch enabling unauthenticated object injection and RCE via…

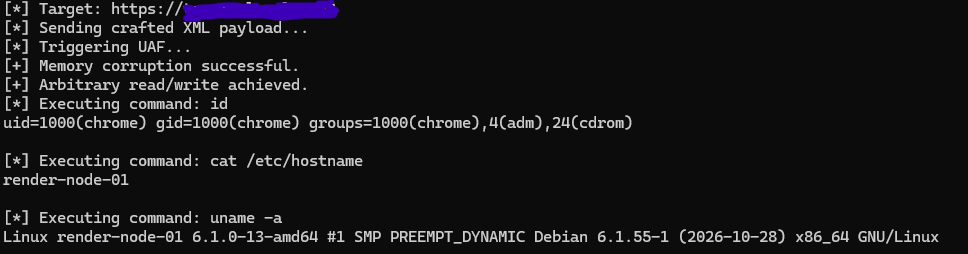
Proof-of-concept trigger and detection notes for CVE-2026-125350, a use-after-free in Chrome's XML parser (CVSS 8.8, Chrome < 157.0.8103.50, CISA…

Docker-based proof-of-concept for CVE-2026-121810, an nginx HTTP/3 (QUIC) use-after-free triggered by worker_connections exhaustion, with a Python…

Python PoC and write-up for CVE-2026-119258, an unauthenticated authentication bypass in the Swipe WordPress plugin (<=1.4) that issues admin session…

Python PoC for CVE-2026-125283, an nginx alias + try_files integer underflow triggered via map captures, with Docker lab, trigger variants, and…

Proof-of-concept scripts for CVE-2026-123007, an NGINX HTTP/2 integer underflow, including a minimal trigger and an exploit demonstrating…

PatrowlHears - Vulnerability Intelligence Center / Exploits

Archived proof-of-concept and detection rules for CVE-2026-115560, a pre-auth PHP deserialization object-injection flaw enabling remote code…

Archived pointer repository for CVE-2026-125350, a Chromium libxslt use-after-free; code, packet captures and Suricata/YARA detection rules now live…

Proof-of-concept and writeup for CVE-2026-125440, an unauthenticated shortcode injection in s2Member PayPal IPN handlers that can escalate to code…

Reflected XSS in Opixido OCMS admin/TUI/index.php (img parameter)

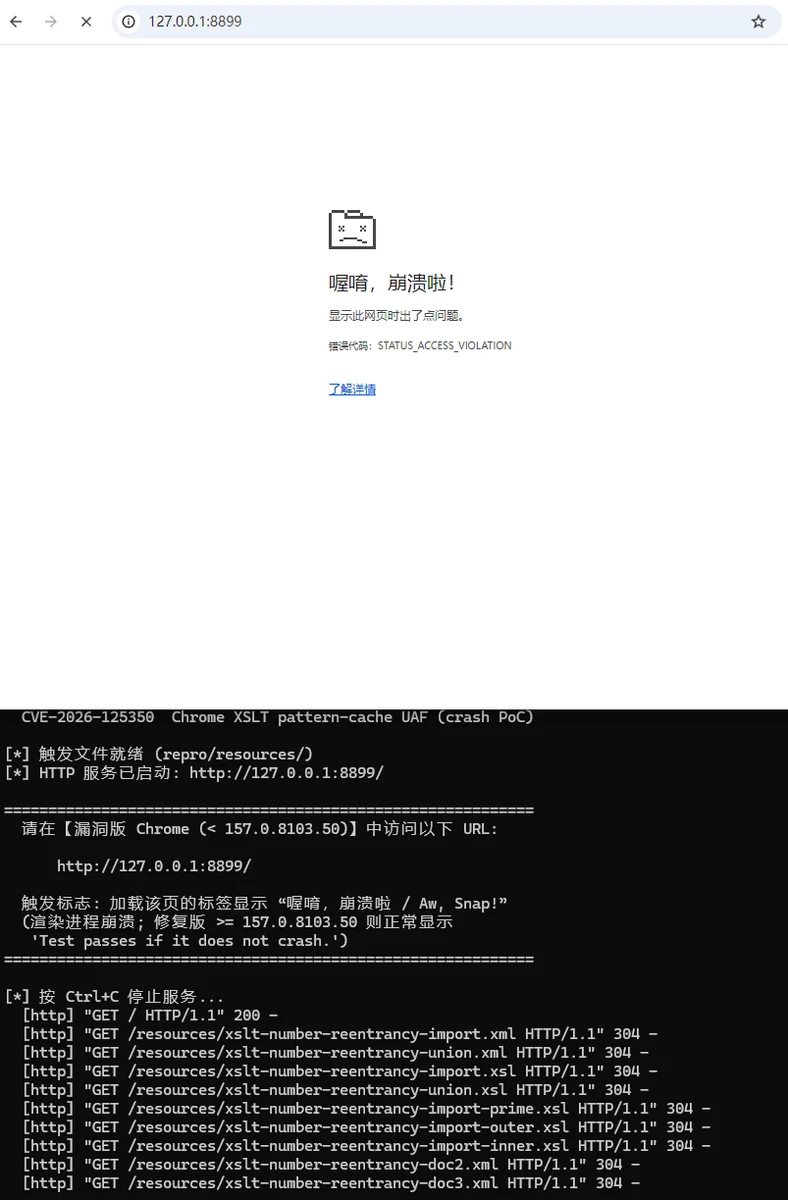
Google Chrome XSLT pattern-cache Use-After-Free (CVE-2026-125350) crash PoC — affected < 157.0.8103.50

Proof-of-concept and analysis for CVE-2026-124040, a CivetWeb HTTP/2 HPACK header-name corruption via use-after-free that bypasses literal-header…

Exploit notes and proof-of-concept material for CVE-2022-23943, a mod_sed buffer overflow in Apache HTTP Server 2.4.0-2.4.52, with prerequisites and…

Exploit and safe-check toolkit for CVE-2026-21589, an unauthenticated path traversal in Atlassian Data Center: WEB-INF file read, credential…

Printcart <= 2.13.2 Unauthenticated File Upload

Technical analysis and skeleton PoC for CVE-2026-125350 (Chrome XML UAF)