initial-access-community

Go-based exploits for unauthenticated network vulnerabilities in routers, VPNs, appliances, and IoT, bundled with PCAPs, Suricata/Snort/YARA/Sigma…

Go-based exploits for unauthenticated network vulnerabilities in routers, VPNs, appliances, and IoT, bundled with PCAPs, Suricata/Snort/YARA/Sigma…

Ring -4 to Ring 0: offense-defense firmware research platform. We build the bootkits, then we catch them. Closed-loop. Zero trust in silicon.

Working POC of Mikrotik exploit from Vault 7 CIA Leaks

Python client for the Thinkware U3000 dashcam's local WiFi control protocol, reverse-engineered from the official Android app. PoC tooling behind…

Tool for reconstructing SPI flash images via logic analyzer captures

Analysis and cleanup guide for BadBox malware on Allwinner H713 Android projectors: ADB access, infection proof, firmware backup, dropper removal,…

Security research write-up on exploiting CVE-2026-43499 on the Amazon Fire TV Stick 3rd Gen (sheldonp), from temporary root to bootloader unlock.

A collection of vulnerabilities & exploits against modern GCS

Firmware reverse engineering of the Philips PM5139 / PM5138A / PM5136 function generators: 8051 emulators used as measuring instruments, 35 sections…

Agent skills for firmware extraction, static analysis, Ghidra reverse engineering, emulation, and security reporting, packaged for Claude Code and…

Firmware-specific temporary root exploit for Toshiba/Amazon Fire TV (hazel) using CVE-2026-43499. Implements ARM32 futex-PI UAF, kernel address leak,…

Recovers cryptographic keys from MiFare Classic RFID cards using DarkSide and nested-auth attacks for security testing of NFC/RFID systems.

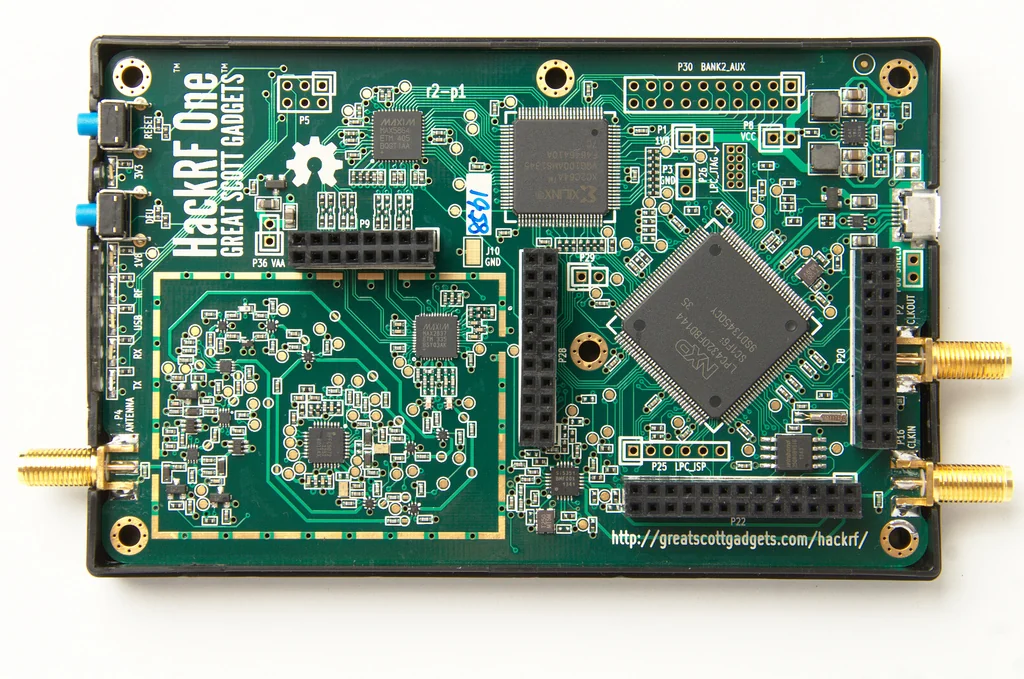
Low-cost open-source software-defined radio platform with hardware designs and firmware for RF transmission, reception, and signal analysis from 1…

C library providing a portable API for acquiring signals from logic analyzers, oscilloscopes, multimeters, and other test instruments, with…

From a bare PCB to root: hardware-hacking a ZyXEL P-870HN (BCM6368) over UART — CVE-2025-0890 + CVE-2024-40891, on my own hardware.

A tool to recover a fully analyzable .ELF from a raw kernel, through extracting the kernel symbol table (kallsyms)

Expose USB activity on the fly

This is a collection of Unisoc BootROMs dumped from various Unisoc chipsets via CVE-2022-38694