

ZTE-MF904Q-Reverse-Engineering
 faicalom/zte-mf904q-reverse-engineering
Open research documentation and source review for ZTE MF904Q bootloader, firmware extraction, and reverse engineering.
android-securitybinary-analysisembedded-systems-security+5
faicalom/zte-mf904q-reverse-engineeringOpen research documentation and source review for ZTE MF904Q bootloader, firmware extraction, and reverse engineering.
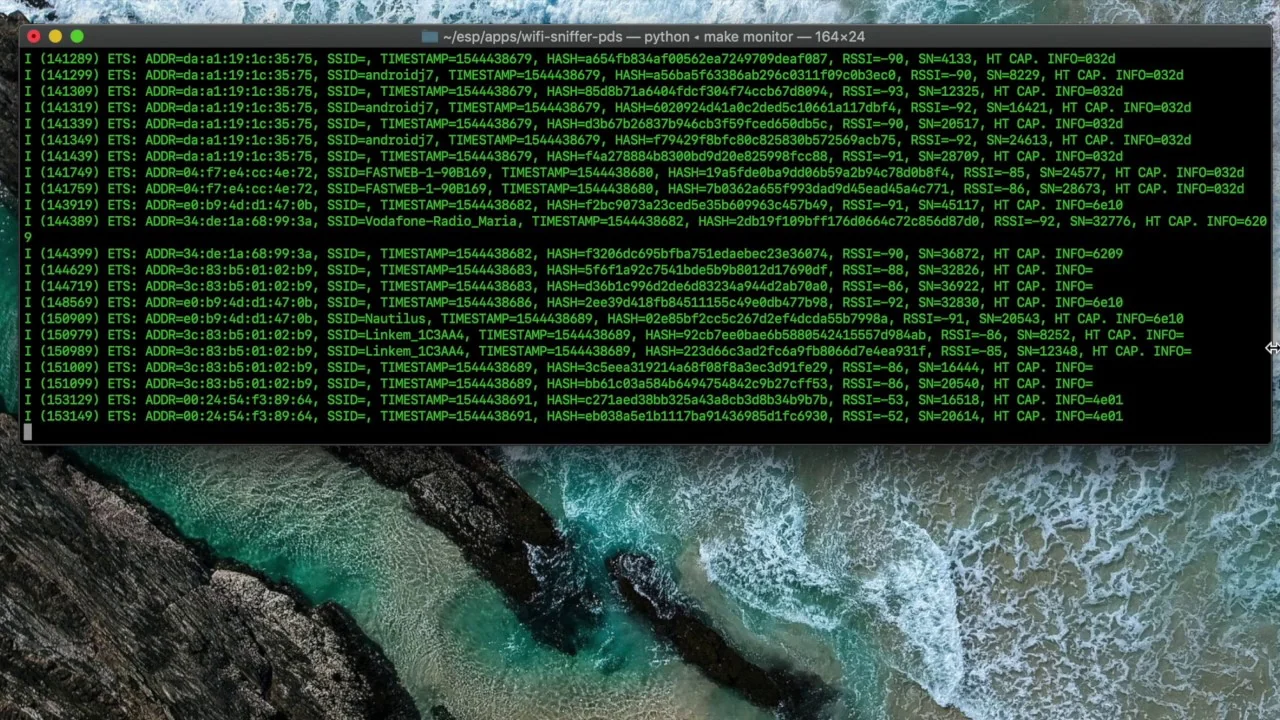 ets-polito/esp32-sniffer
ESP32 firmware that sniffs PROBE REQUEST packets sent by smartphones searching for Wi-Fi connection to extract different types of information
 lukr54/edk2-security
EDK2 BrotliCustomDecompressLib security findings — coordinated disclosure
 commit-regrets/samsung_tizen_tv_root
Research toolkit that roots a Samsung Tizen 9 TV via a Chromium WasmGC RCE and V4L2 physmap arbitrary physical memory access, with persistent on-boot…
 tylermcm/wonderlanternz7
Experimental Nikon Z7 camera firmware research lab: source patcher, QEMU emulation harness, and validation tooling for building and testing modified…
 jaredreabow/reverse-engineering-with-ai
Research methods for reverse engineering encrypted firmware and software with AI-assisted analysis, independent validation, and public-source…
 alltechdev/mtk-imei-switcheroo
Read and write IMEI records and WiFi/Bluetooth addresses in MediaTek NVRAM files or partition images. Includes interactive ADB tools for rooted…
 blasty/wake-and-break
PSP exploit for AMD navi31 (RX 7900) GPUs that disables firmware signature checks so the card loads unsigned SMU, SDMA, MEC, IMU and RLC firmware;…
 aleph-void/ghidra-rare
A repository of SLEIGH support for rare processor ISAs

 c4psu13/mali-pagecache-root
TCL 50C721 (RTD1319 / Mali-G31) root toolkit — autonomous CVE-2022-22706 exploit chain
 mr-wolf-is-me/ida-processor-modules
IDA Pro processor modules adding disassembly support for uncommon CPU, DSP, and GPU architectures including XMOS xCORE, TI C7x/PRU, MicroBlaze, and…
 pepsipu/ns2jb
Console jailbreak demo that executes native functions inside the Switch 2 filesystem process via SmileBASIC, verifies results, and restores original…
 qkaiser/broadcom-wps
Tools to fingerprint WiFi Access Points running the Broadcom SDK and a list of known affected devices.
 yasindce1998/barzakh
Ring -4 to Ring 0: offense-defense firmware research platform. We build the bootkits, then we catch them. Closed-loop. Zero trust in silicon.
 cplusplus17/deco-filepush-disclosure
Disclosure and PoC for a root file read/write flaw in the TP-Link Deco XE75 Pro V3 debug channel (tmpsvr opcodes 0xC456/0xF0), with CVSS analysis and…
 c8dhjp4tyv-bit/jbl-wave-buds2-firmware-research
Reverse-engineering notes and Python tooling for JBL Wave Buds 2 (BES1306) firmware: OTA container format, flash layout, BLE/GATT protocol, and…
 newbe3e/pwn2own-automotive-2026-alpine-ilx-f511-0-click-rce-exploit-writeup
Writeup of a 0-click remote code execution exploit chain developed for the Alpine iLX-F511 automotive head unit at Pwn2Own Automotive 2026.
 abraxas/sonic-gnmi-noauth
Documents and reproduces a fail-open authentication flaw in SONiC gNMI where an empty UserAuth map allows unauthenticated gNMI Set and gNOI writes,…