
area51
 thoropass-public/area51
The exploit server for out-of-band findings. Point a target at a domain you own. Every HTTP request and every email it sends back lands in a…
api-security-testingcloud-securityemail-security+4
6
thoropass-public/area51The exploit server for out-of-band findings. Point a target at a domain you own. Every HTTP request and every email it sends back lands in a…
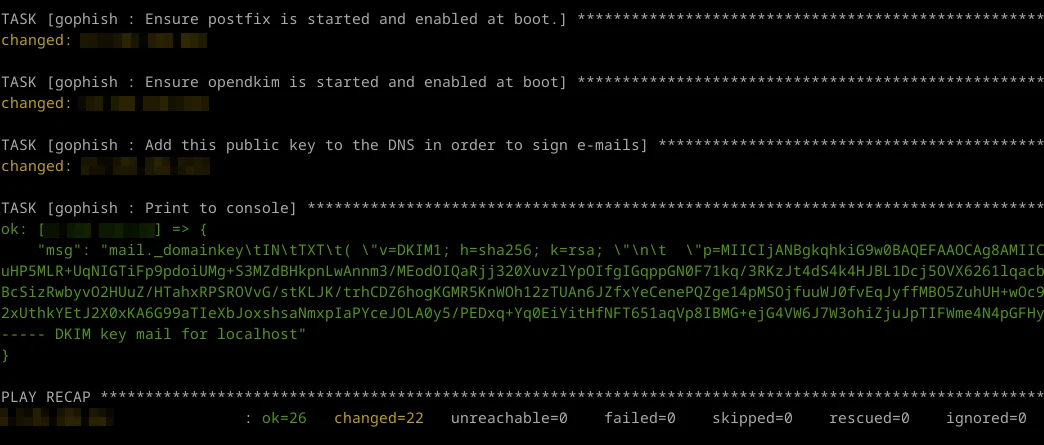 virtualsamuraii/flyphish
Deploy a phishing infrastructure on the fly.
 falcosecurity/falco
Real-time cloud-native runtime security agent for Linux that monitors syscalls and container/Kubernetes metadata to detect anomalous behavior and…
 v4d1/spoofthatmail
Bash script to check if a domain or list of domains can be spoofed based in DMARC records
 danithehack3r/cve-2024-42009-poc
CVE-2024-42009 Proof of Concept
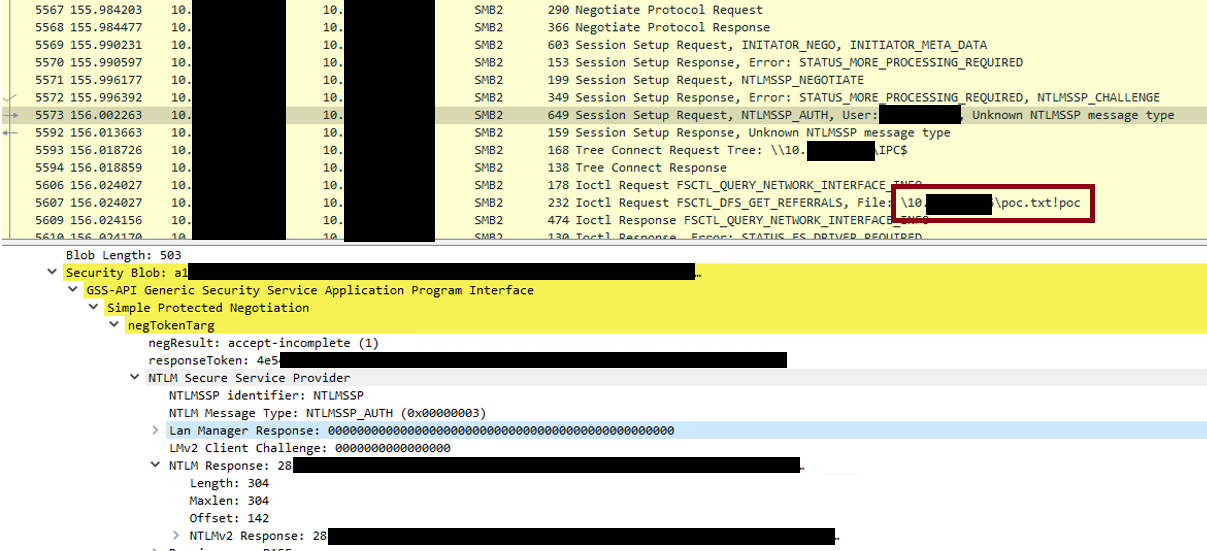 xaitax/cve-2024-21413-microsoft-outlook-remote-code-execution-vulnerability
Microsoft-Outlook-Remote-Code-Execution-Vulnerability
 0nyx-my7h/cve-2025-43920
PoC and technical write-up for CVE-2025-43920, a remote command injection in GNU Mailman 2.1.39's external archiver allowing unauthenticated code…
 yfelipecruvinel/tryhackme-moniker-link
Documentation of my hands-on lab Moniker Link (CVE-2024-21413) completed on TryHackMe.
 qsecure-labs/overlord
Python-based CLI for automated red team infrastructure deployment on AWS and Digital Ocean, with modular support for C2, email servers, HTTP…

 networksecure/cve-2020-14066
Proof-of-concept exploit for CVE-2020-14066 targeting insecure permissions in Icewarp Email Server 12.3.0.1, enabling privilege escalation or…
 jishino567/cve-2026-73570
Python PoC for CVE-2026-73570, an SMTP command injection in Zimbra. Sends malformed RCPT TO payloads to trigger shell command execution via…
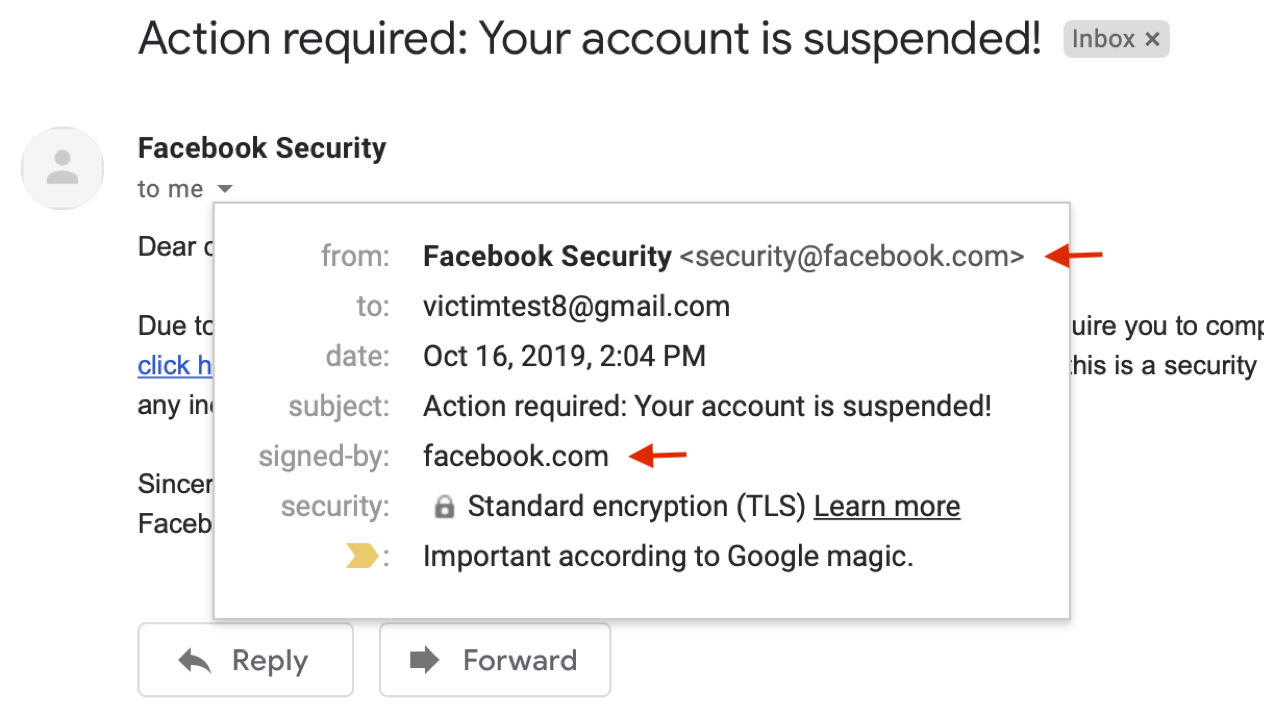 chenjj/espoofer
An email spoofing testing tool that aims to bypass SPF/DKIM/DMARC and forge DKIM signatures.🍻

 wslyvh/paperweight
Paperweight scans your inbox to map your digital footprint, then helps you take back control and delete your data. Local-first and open source.
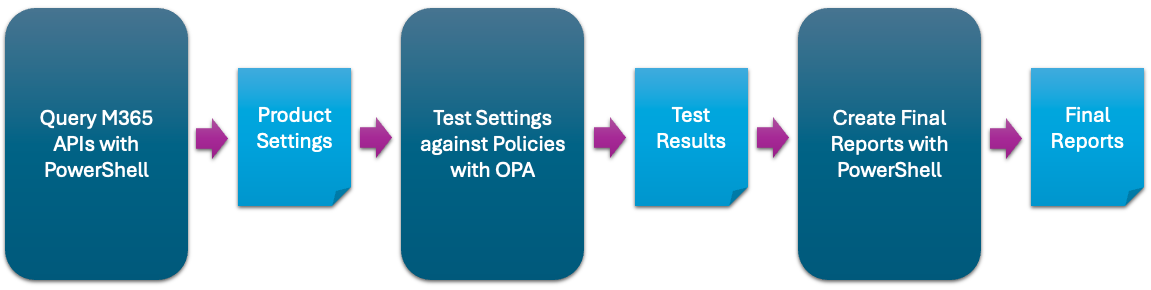 cisagov/scubagear
Automation to assess the state of your M365 tenant against CISA's baselines
 mailcow/mailcow-dockerized
Dockerized mail server suite with Postfix, Dovecot, Rspamd, and ClamAV. Provides secure email hosting with integrated spam filtering, antivirus, and…
 saykino/cve-2026-31283
Documentation of CVE-2026-31283: an email bombing vulnerability in Totara LMS's forgot password API due to missing rate limiting, allowing…