
Aegis
 antropos17/aegis
Desktop monitoring and local security reviews for AI agents, with opt-in policy-controlled execution and MCP action tools. Windows primary;…
ai-securityanomaly-detectiondefensive-tools+4
154
antropos17/aegisDesktop monitoring and local security reviews for AI agents, with opt-in policy-controlled execution and MCP action tools. Windows primary;…
 gtfobins/gtfobins.github.io
GTFOBins is a curated list of Unix-like executables that can be used to bypass local security restrictions in misconfigured systems.
 sleventyeleven/linuxprivchecker
Local Linux enumeration script that identifies privilege escalation vectors including misconfigurations, world-writable files, clear-text passwords,…
 00xcanelo/cve-2025-27591
🔥 Local Privilege Escalation Exploit for CVE-2025-27591 | Abuses world-writable log dir in Below to gain root via /etc/passwd injection
 0xblackash/cve-2026-81000
Research repository for CVE-2026-81000 (TUNderflow), a Linux kernel TUN/TAP receive headroom integer underflow enabling local privilege escalation,…
 xzx482/cve-2024-1086
Universal local privilege escalation exploit for CVE-2024-1086 targeting Linux kernels v5.14 to v6.6. Provides root shell with 99.4% success rate on…
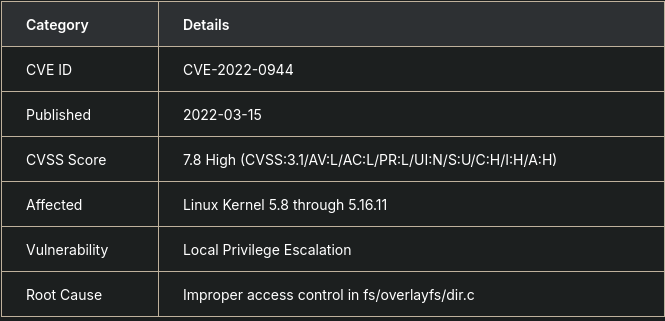 neoartemis37/overlayfs-privesc-cve-2022-0944
Educational exploit for CVE-2022-0944 OverlayFS privilege escalation with reverse shell payload delivery and kernel version detection scripts.
 curtishoughton/cve-2021-3560
Proof-of-concept exploit for CVE-2021-3560, a local privilege escalation vulnerability in Polkit (PolicyKit) on Linux systems, enabling unprivileged…
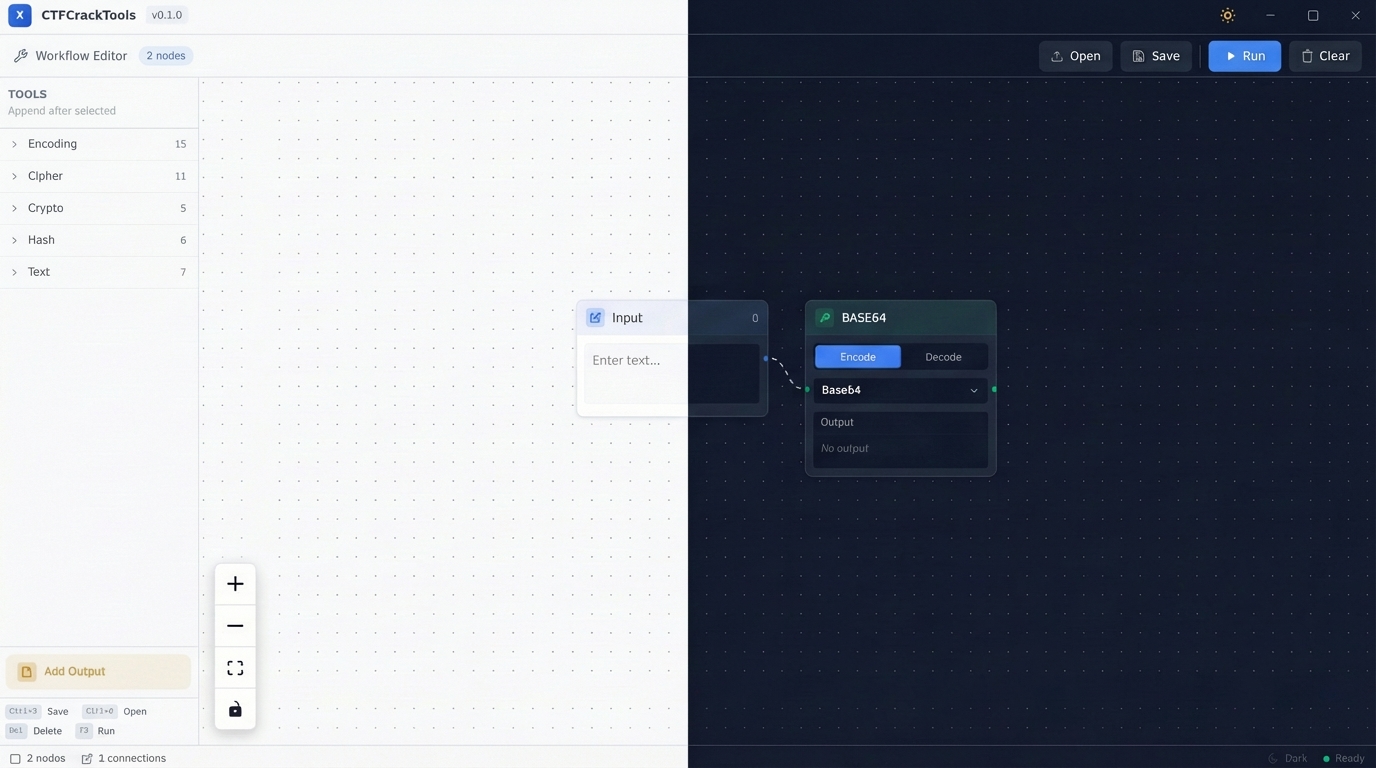 0chencc/ctfcracktools
The next-generation CTF Swiss Army Knife powered by Rust & Tauri. Features a visual node-based workflow and local AI intelligence for extreme…
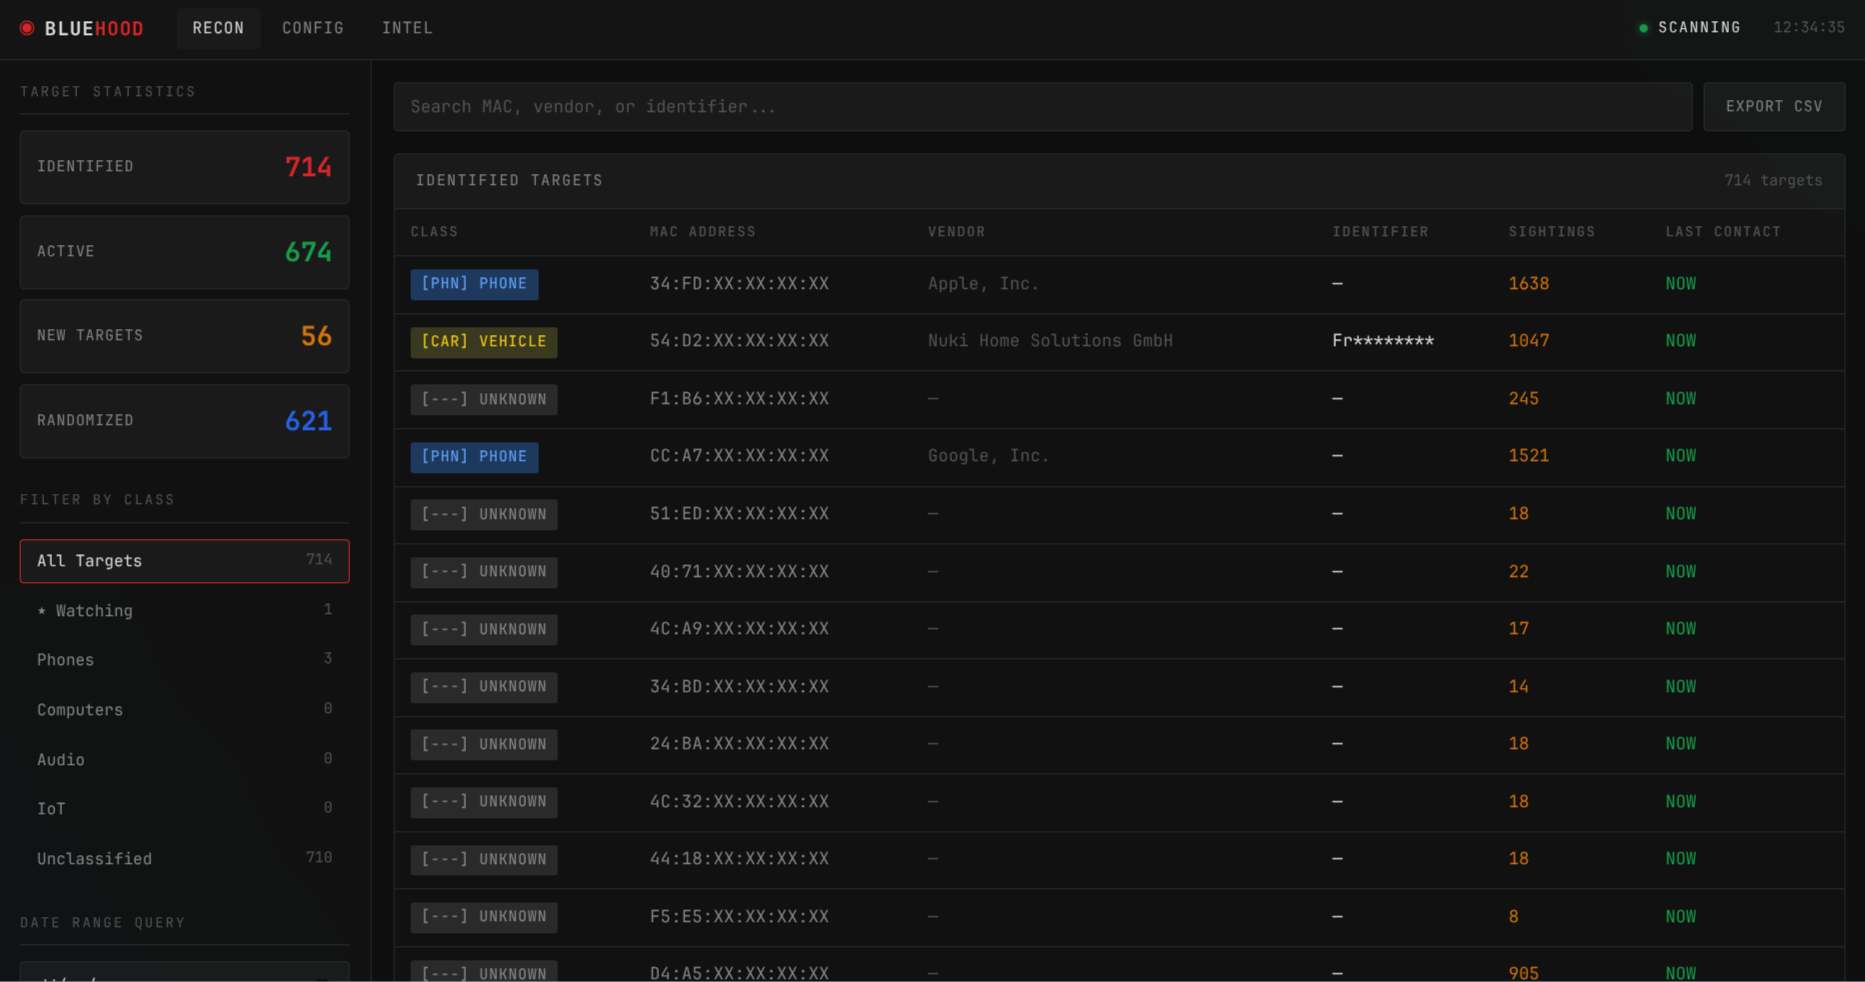 dannymcc/bluehood
Monitor your local neighbourhood's bluetooth activity
 0xblackash/cve-2026-68121
Research repository for CVE-2026-68121, a Linux kernel PPPoE use-after-free in pppoe_sendmsg() enabling local privilege escalation, with PoC,…
 sooryathejas/metatron
AI-powered penetration testing assistant using local LLM on linux (Parrot OS)
 maxime288/fragnesia-cve-2026-46300
Educational repository detailing CVE-2026-46300 (Fragnesia), a Linux kernel local privilege escalation vulnerability. Provides technical analysis,…
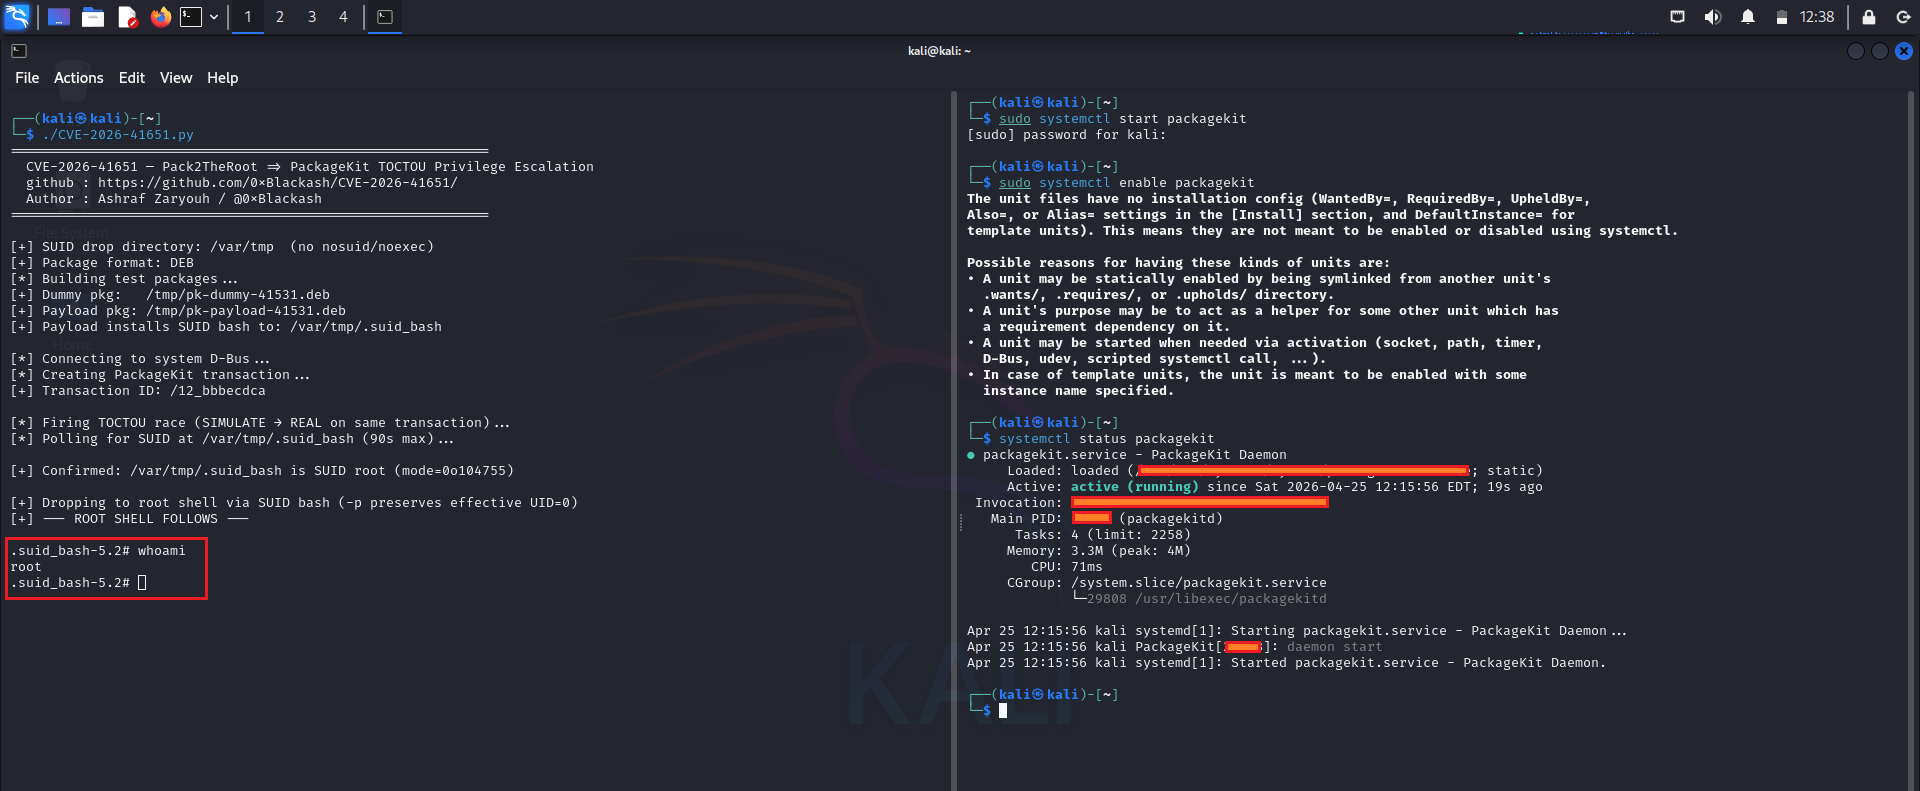
 lucastran05/cve-2026-29000
Local lab simulating CVE-2026-29000 JWT/JWE authentication bypass in pac4j-jwt. Provides login, token forging, and dashboard APIs for practicing web…
 luotian2/cve-2026-31431
Exploit for CVE-2026-31431, a Linux kernel authencesn bug enabling local privilege escalation and container escape via a 4-byte page cache write.
 nisec-eric/cve-2026-31431
Linux kernel local privilege escalation exploit for CVE-2026-31431, providing a reliable single-shot PoC with multiple language implementations,…
 adilkurtulmus/linux-copy-fail-cve-2026-31431
Proof-of-concept exploit for CVE-2026-31431 (Copy-Fail), a Linux kernel AF_ALG and splice() flaw enabling page cache poisoning and local privilege…