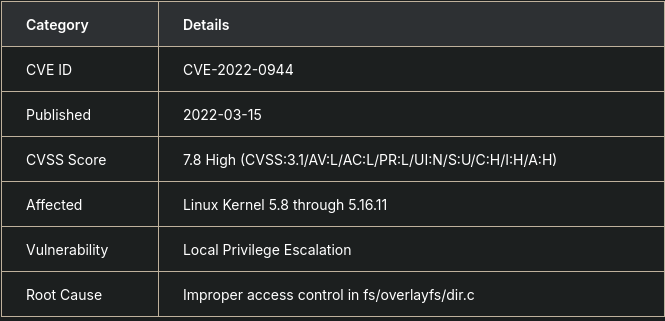
 neoartemis37/overlayfs-privesc-cve-2022-0944
Educational exploit for CVE-2022-0944 OverlayFS privilege escalation with reverse shell payload delivery and kernel version detection scripts.

Historical Linux research material with an identifier that requires verification.
The repository name contains a historical CVE identifier. This documentation refresh does not establish that the identifier matches the code or that the original vulnerability claims are accurate.
Python research artifact and existing SECURITY.md. The code and its history are retained; this README is a presentation and provenance update.
No new license or authorship claim is introduced by this documentation update. Verify the provenance and applicable permissions before reuse.
Maintained as part of Artemis’s project and learning collection.






