

hardstop
 joseluispino/hardstop
Reference implementation for "Hard Stop: Kernel-Level Preemption and Containment for Rogue Agentic Execution". Out-of-band Epistemic Andon Cord,…
ai-securityanomaly-detectioncloud-security+7
2
joseluispino/hardstopReference implementation for "Hard Stop: Kernel-Level Preemption and Containment for Rogue Agentic Execution". Out-of-band Epistemic Andon Cord,…
 akha-security/akca
Evidence-oriented DAST scanner in Go that crawls web apps and APIs, then runs adaptive SQLi, XSS, RCE, SSRF, and auth checks with replayable proof.
 fkie-cad/sandroid_dexray-intercept
A Android malware analysis tool that creates comprehensive runtime profiles by hooking into application behavior across cryptography, file systems,…
 newliver666/apk-reverse
Agent skill for Android APK reverse engineering: dex patching, unpacking, repacking, ad and paywall removal, native .so analysis, and runtime…
 githubsecuritylab/seclab-taskflows-fuzzing
An LLM-driven fuzzing pipeline powered by the GitHub Security Lab Taskflow Agent
 recurse-labs/recurse
Agentic reverse engineering IDE with a pure-Rust multi-architecture disassembler, native decompiler, debugger, and LLM agent for binary analysis and…
 navikt/cplt
Sandbox for AI coding agents. Runs Copilot CLI, Claude Code, OpenCode, Gemini CLI, Antigravity, Pi, goose or a plain shell inside a kernel-level…
 notrequiem/antidbg
A stealthy, fully syscalled C/C++ userland anti-debugging library for Windows, designed to protect software from reverse engineering
 kaandemir993/purerat-msbuild.exe--c2-extraction--net-evasion-analysis
Reverse engineering analysis of PureRAT RAT abusing msbuild.exe, extracting C2 infrastructure, .NET evasion APIs, file system manipulation, and…
 saina15/cve-2020-14343-lab
Controlled vulnerability research and reproduction lab for CVE-2020-14343 in PyYAML
 rin449/bhpai
Multi-format malware analysis platform combining a stealth Ring-3 Windows sandbox, static PE/PDF analyzers, ransomware key recovery, and an AI…
 capesandbox/capesolo
Standalone Windows VM malware sandbox running capemon, with GUI triage viewer, YARA signatures, IOC extraction, network analysis, and…
 shivammittal2403/cve-2026-80428-ctf
Containerized educational CTF lab emulating CVE-2026-80428 (CWE-502 deserialization) for safe, isolated student and researcher practice.
 off-by-1-labs/flawed
Fix-Like Artifacts With Embedded Defects
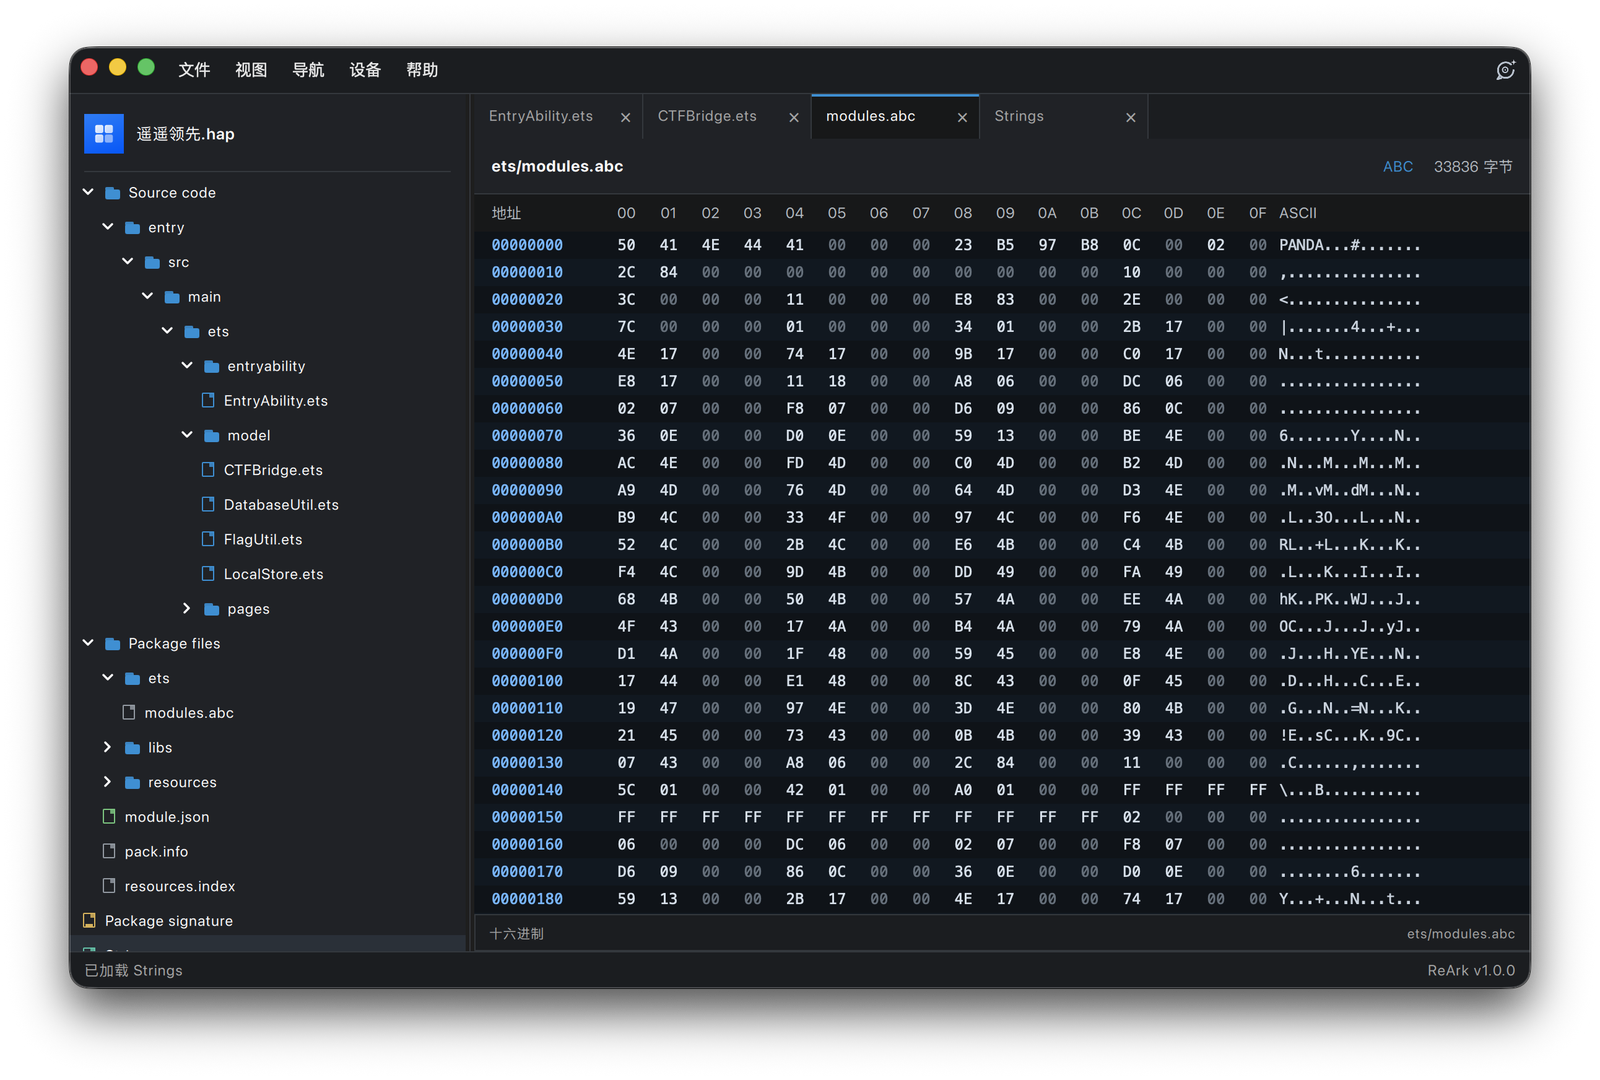 lkimuk/reark
An intelligent reverse engineering analysis tool designed for multiple target platforms, currently supporting HarmonyOS (HAP/APP/ABC) and Android…
 amd2g2zz/kunglao-agent
The reverse-engineering expert agent: plans its own analysis path, derives every fact from raw evidence, and converges under mechanical verification…
 orbitcurve/firmware-reverse-engineering
Agent skills for firmware extraction, static analysis, Ghidra reverse engineering, emulation, and security reporting, packaged for Claude Code and…
 microsoft/mxc
Policy-driven, layered isolation and containment