ReArk
English | 简体中文
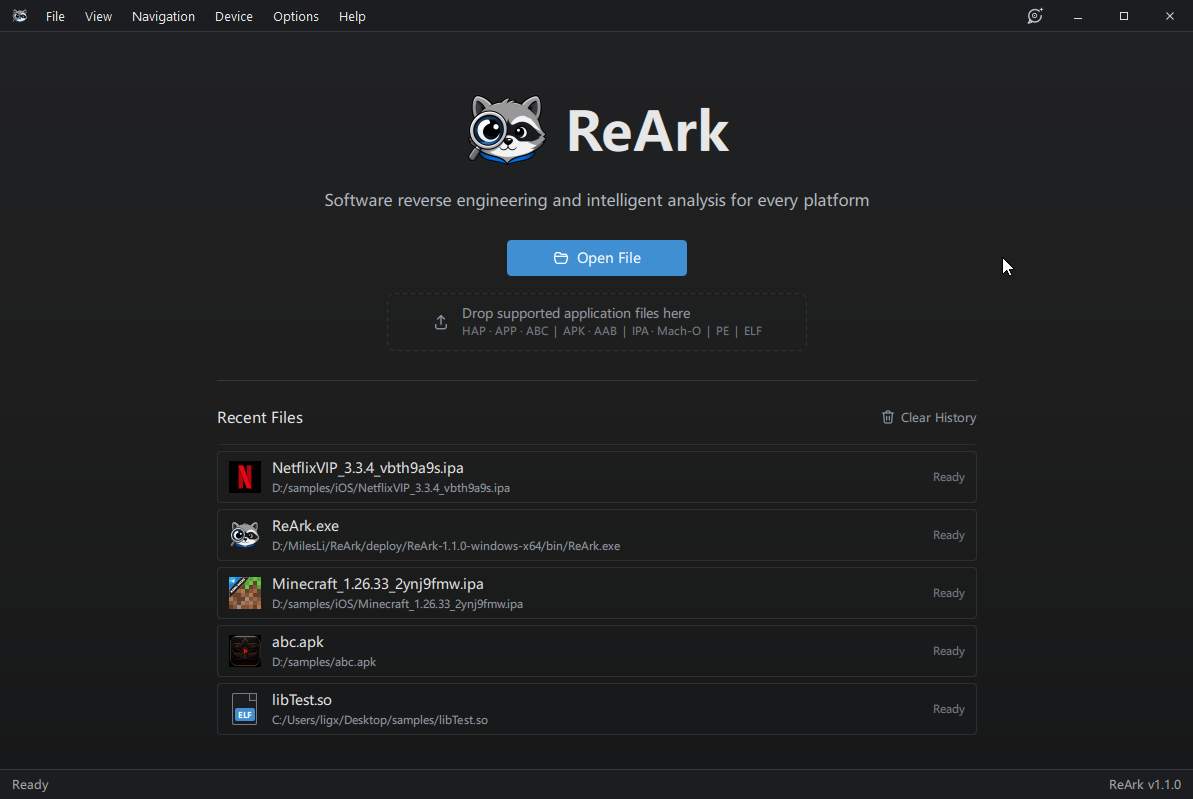
ReArk is a desktop reverse engineering and AI-assisted analysis tool for HarmonyOS NEXT, Android, and iOS applications. Open HarmonyOS .hap, .app, and .abc files, Android .apk and .aab packages, or iOS .ipa files to inspect code, resources, metadata, signatures, and application behavior in one workspace. Standalone Windows PE, ELF, and Mach-O binaries can also be opened directly for native analysis.
Combine static analysis with connected-device inspection and ReArk Agent to investigate application logic, review security, and work through CTF challenges.
Download the installer for your computer from Latest release. See All releases for version history and release notes.
| OS | Requirements | Direct links |
|---|

Windows | Windows 10+
x64 |  |

macOS | macOS 14.0+
Apple Silicon |  |

Linux | x64
System requirements to be announced | Coming in the next release |
Feature Highlights
Package and static analysis
- Supports HarmonyOS NEXT
.hap, .app, and .abc, Android .apk and .aab, and iOS .ipa files
- Browse package structure, modules, generated source output, resources, signatures, and metadata
- Disassemble and decompile ABC bytecode; explore strings, literals, cross-references, and call argument flows
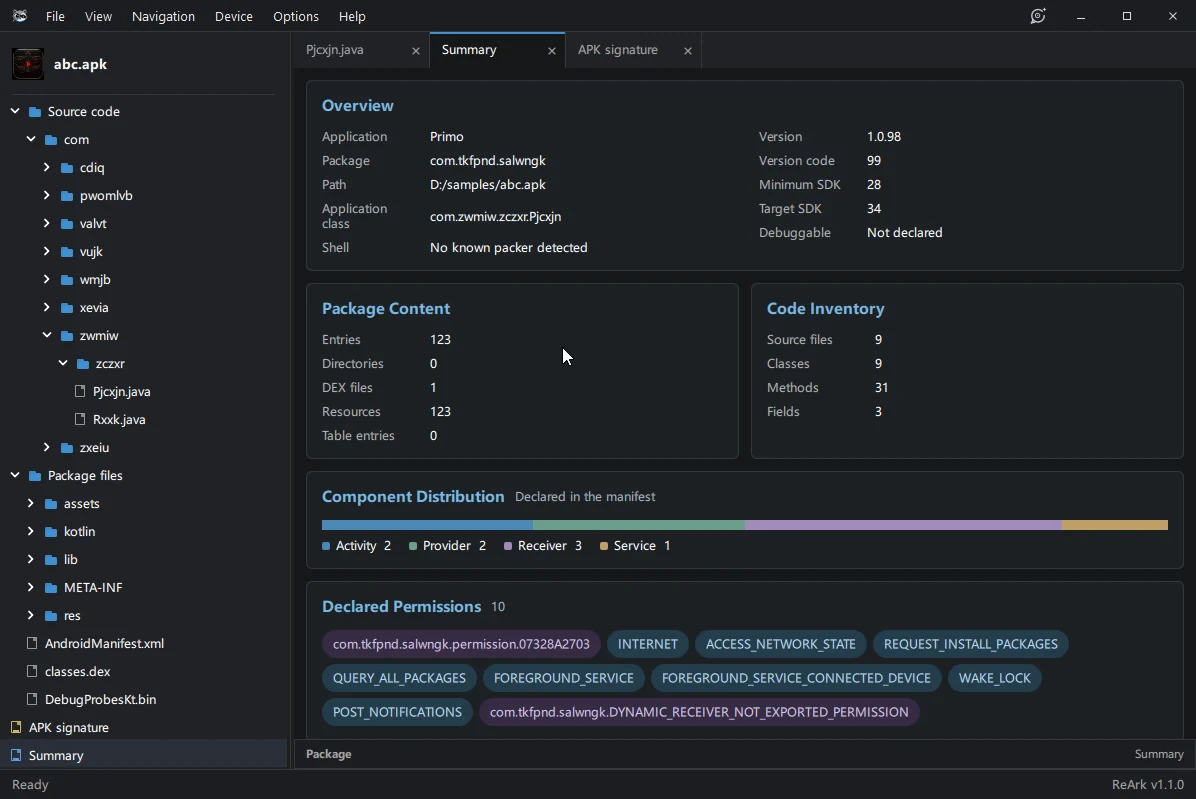
- Inspect Android manifests, permissions, components, entry points, resources, and application icons
- Read Android disassembly and Java-like decompiled output
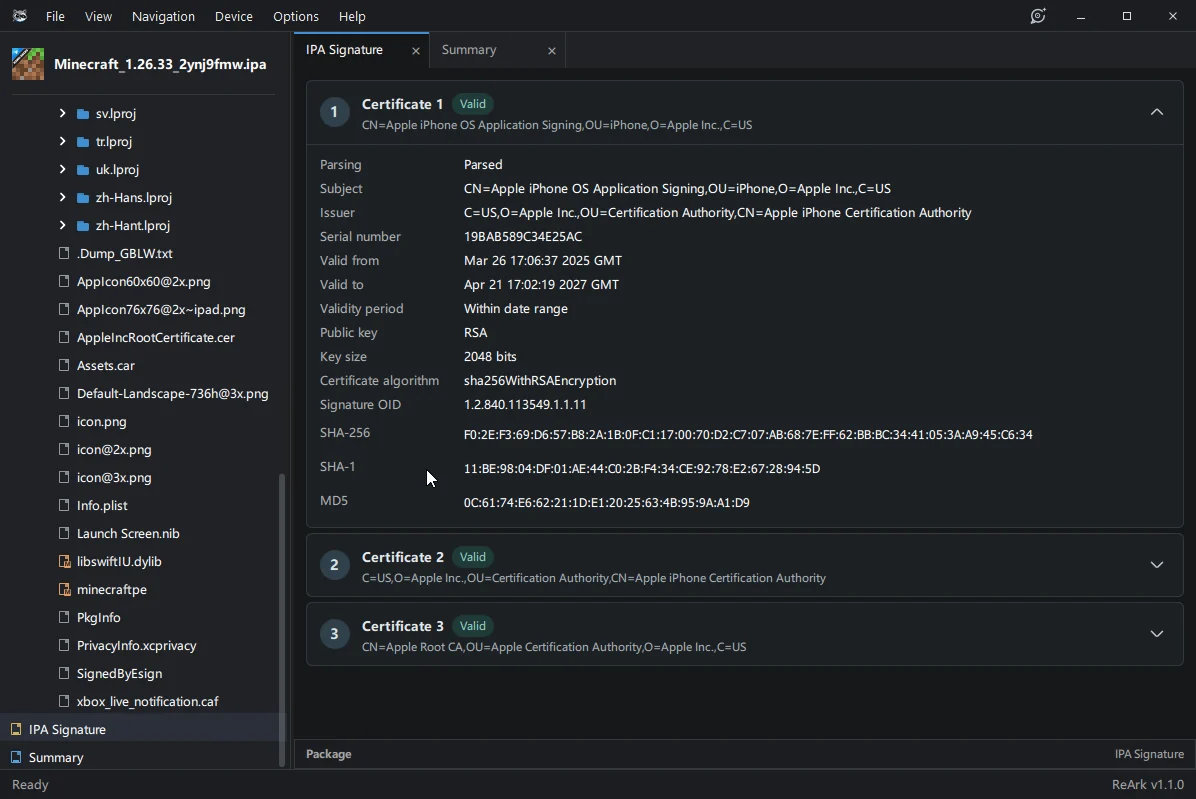
- Inspect iOS IPA signatures and certificate chains
- View hex data, formatted JSON, XML, text, images, and media resources; search files and navigate source output
Native binary analysis
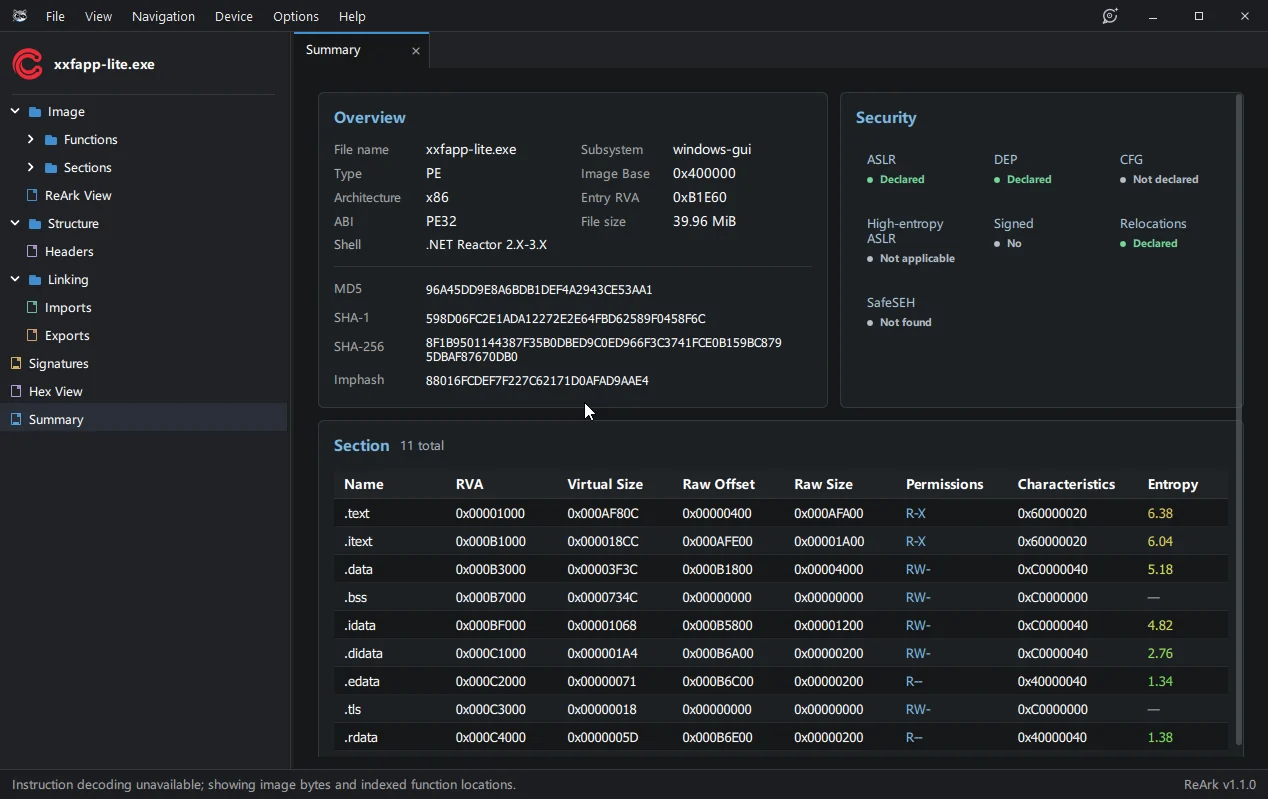
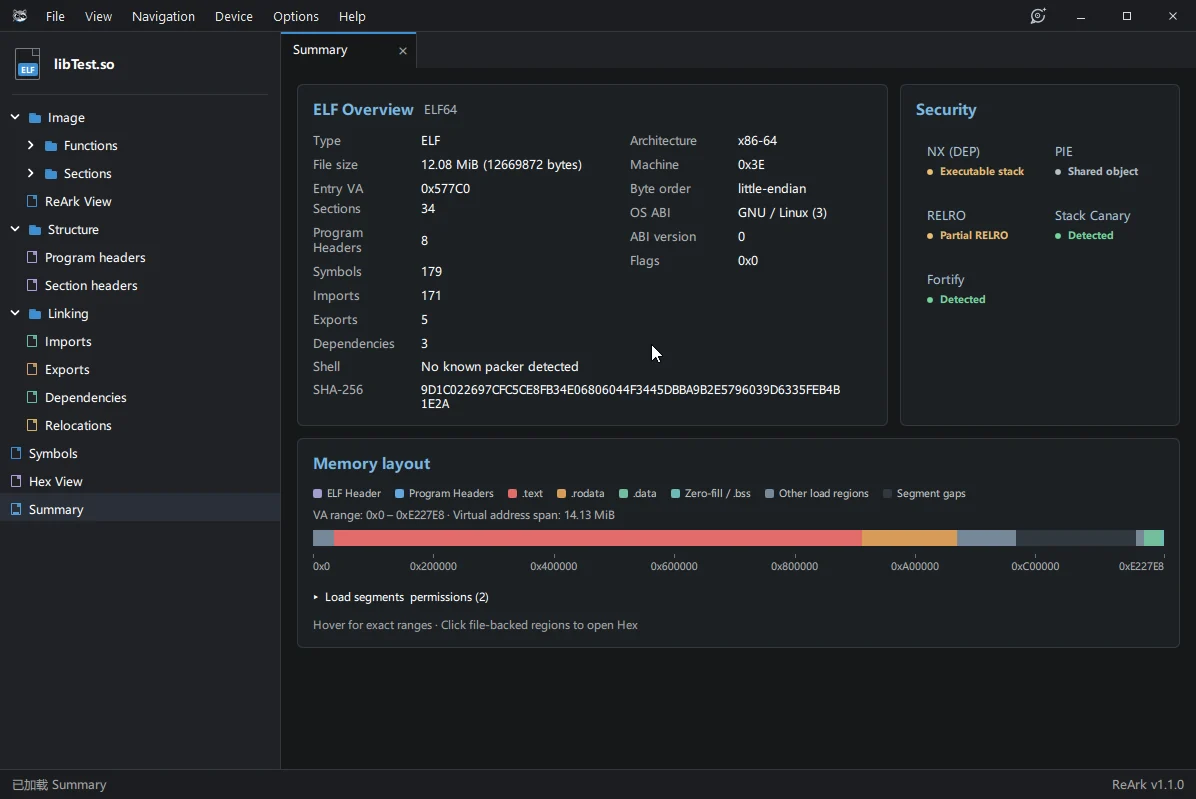
- Open Windows PE (
.exe, .dll), ELF, and Mach-O executables and libraries directly
- Browse headers, sections, imports, exports, relocations, and dependencies
- Review security mitigations such as ASLR, DEP/NX, PIE, RELRO, stack canaries, and CFG
- Navigate structure-aware listings and hex views with field-level annotations
HarmonyOS signing and packaging
- Inspect signatures, certificates, and signing validity
- Configure signing materials, re-sign, and repackage HarmonyOS applications
- Install supported application packages on connected devices; Android device installation uses APK files
ReArk Agent
- Ask contextual questions about the current HarmonyOS or Android package
- Discover analysis capabilities and retrieve package files, metadata, strings, disassembly, and decompiled output as needed
- Attach reference documents to supplement package evidence with your own materials
- Use supported model providers, including OpenAI-compatible endpoints and local Ollama models
- Combine static analysis with device workflows; host commands, Python execution, and device operations use the applicable approval flows
Connected devices
- Discover HarmonyOS devices through HDC and Android devices through ADB
- Install and launch applications, capture screenshots, inspect UI nodes, and read device logs
- Mirror device screens in real time and control devices using mouse and keyboard
- Use screen recording, audio, clipboard, and device controls where supported by the device and runtime
- Work with fullscreen or detached mirroring windows
Available analysis views and device actions depend on the package format, operating system version, and device capabilities. ABC evidence tools and HarmonyOS re-signing are specific to HarmonyOS packages.
What's new in 1.2.0
- Added dynamic analysis and runtime workflows with Frida instrumentation, CPU emulation, memory dumping, and dynamic debugging
- Added bounded APK modification, repackaging, alignment, signing, and signature verification
- Added Reproduction Mode for detecting application cracking and tampering risks
- Added permission management and dynamic model switching from the chat composer
- Added image attachments and previews,
llama-server support, and MCP Server integration for external tools such as REA
- Improved Android embedded ELF analysis and Agent access to native artifacts
- Added compatibility with legacy IPA plist formats and improved tool, runtime, and model diagnostics
Screenshots
| Welcome and supported formats | Android package summary |
|---|
 |  |
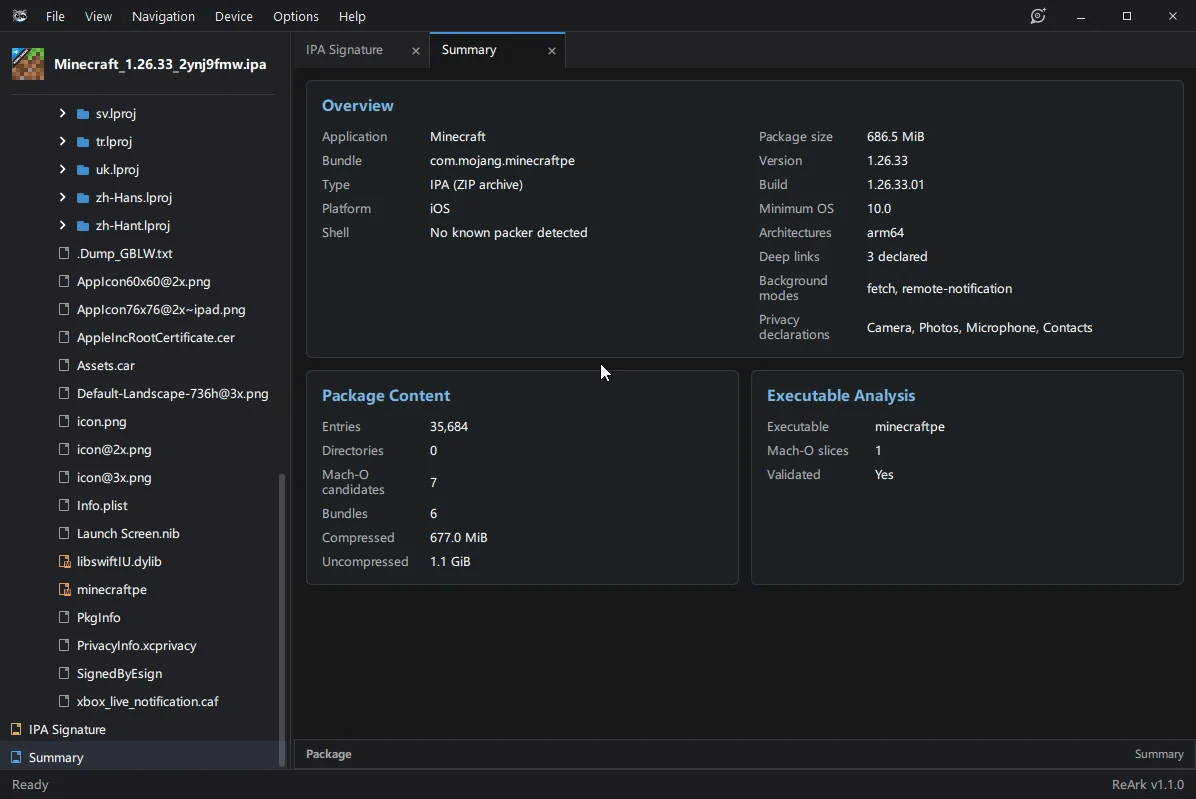
| iOS IPA summary | iOS signature chain |
|---|
 |  |
| PE analysis | ELF analysis |
|---|
 |  |

 lkimuk/reark









