Mobile-Security-Framework-MobSF

Automated mobile application security testing framework for Android, iOS, and Windows. Performs static and dynamic analysis, malware detection, and…

Automated mobile application security testing framework for Android, iOS, and Windows. Performs static and dynamic analysis, malware detection, and…

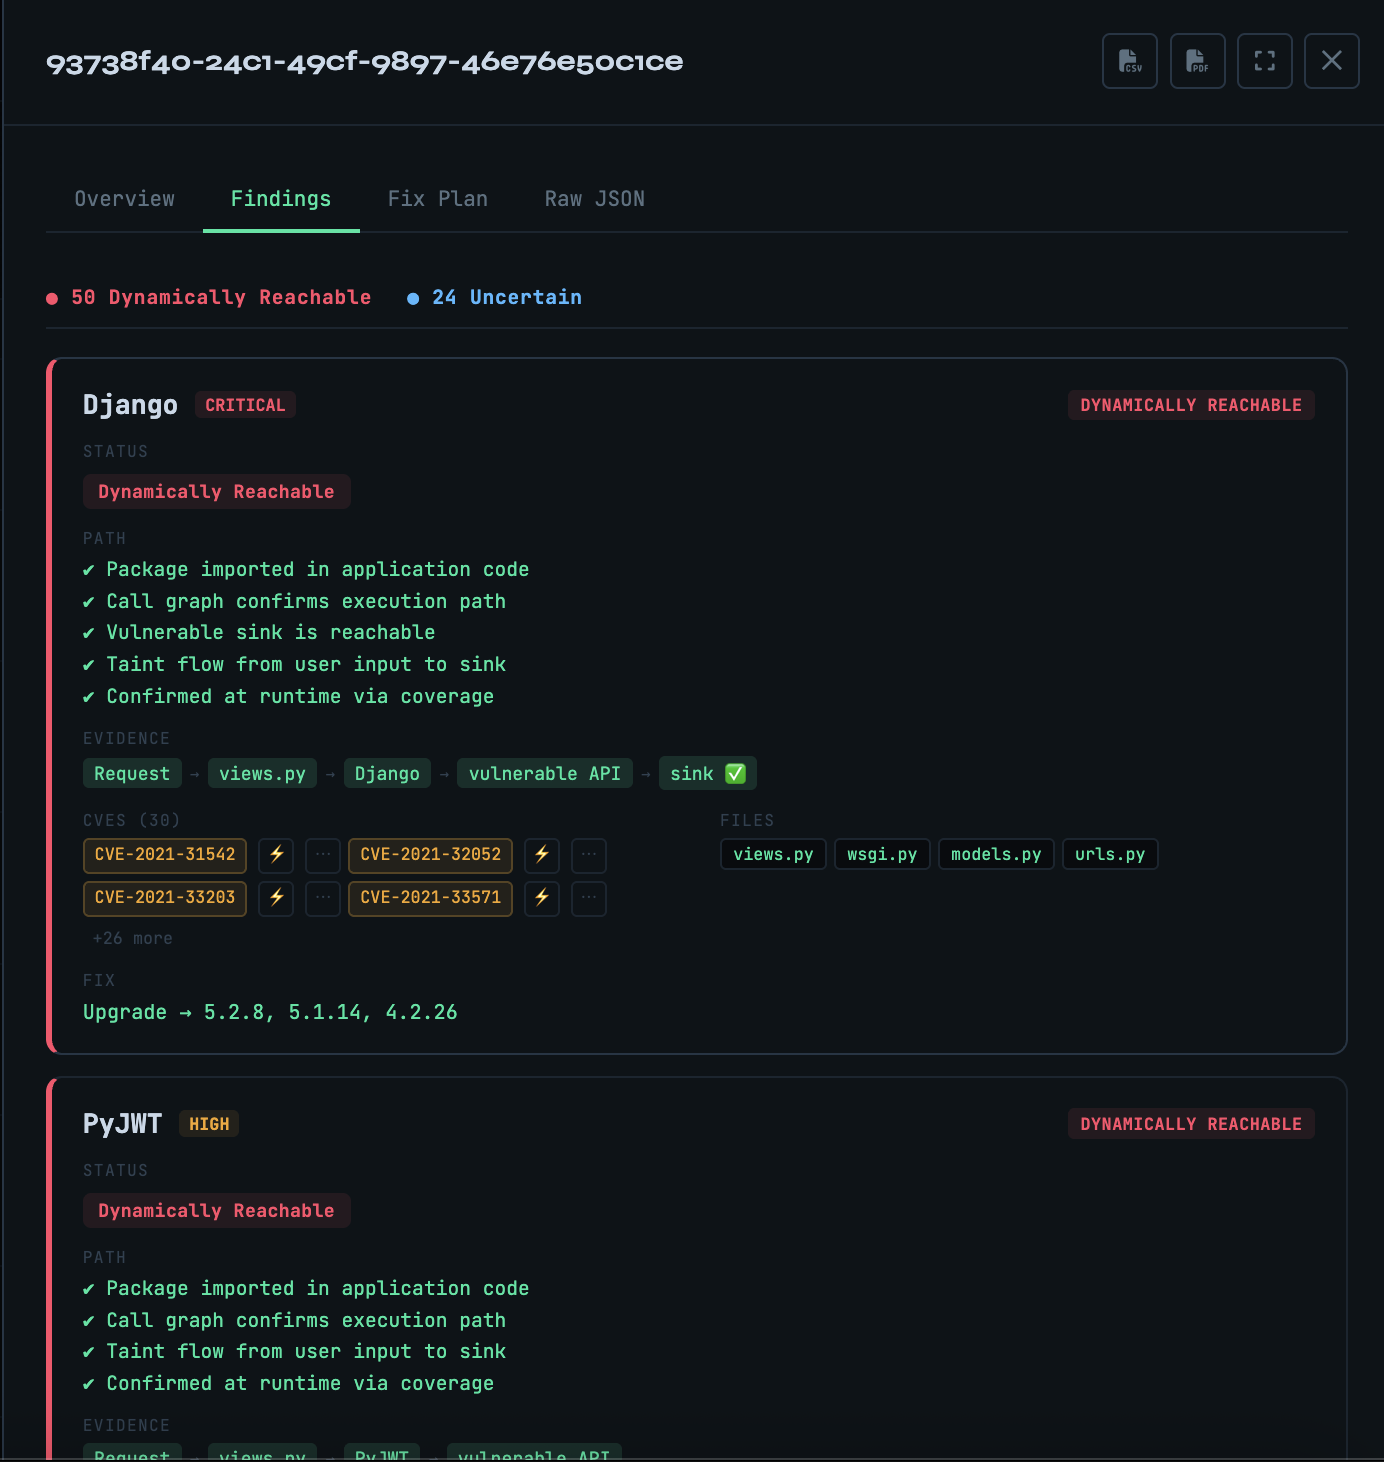
Runtime-aware SCA — proves which CVEs are actually reachable, not just installed.

AI-powered vulnerability scanner extension for Burp Suite with multi-provider support (Ollama, OpenAI, Claude, Gemini)

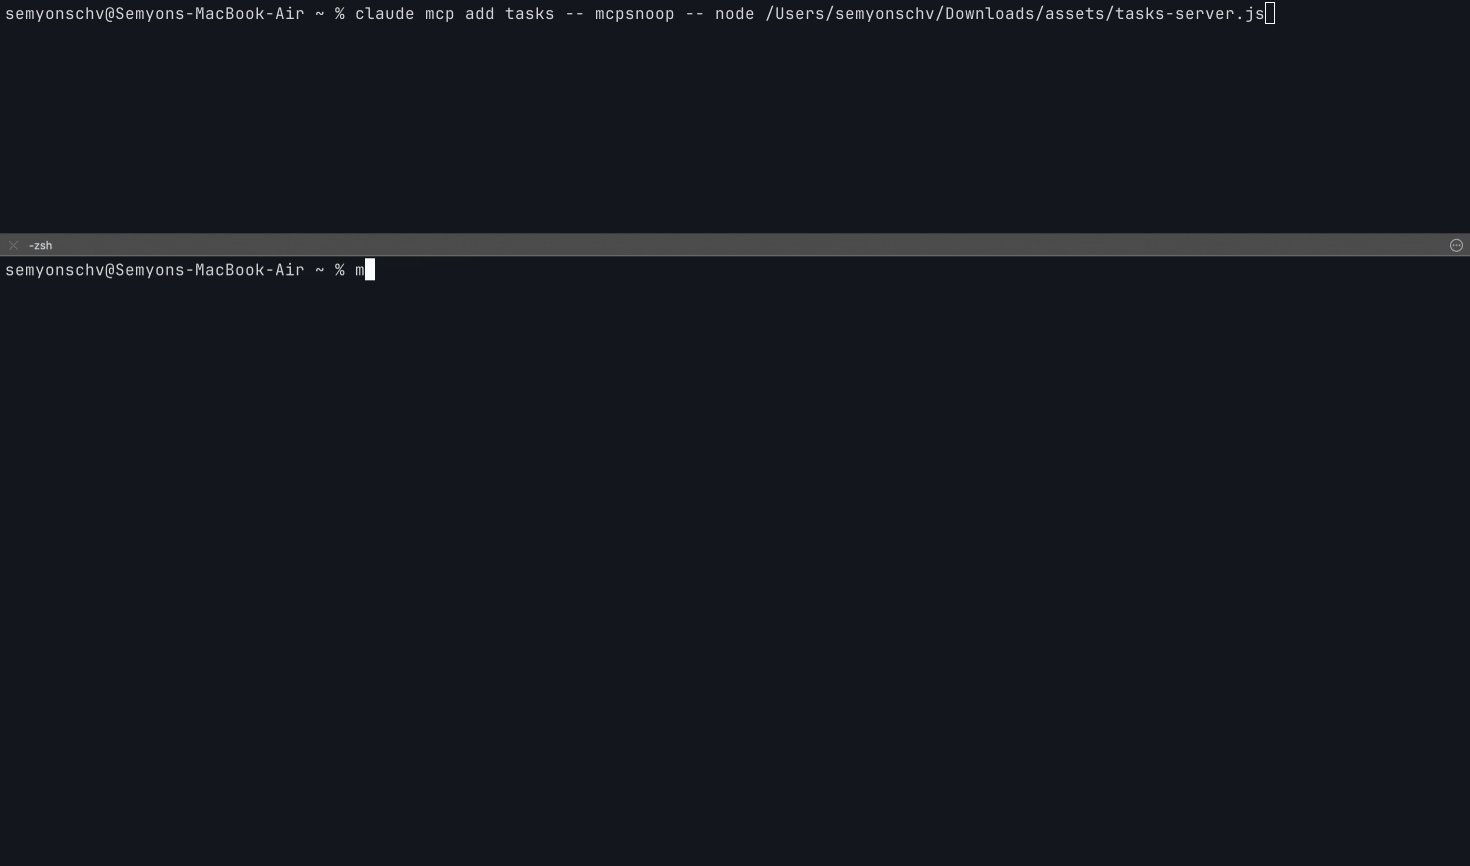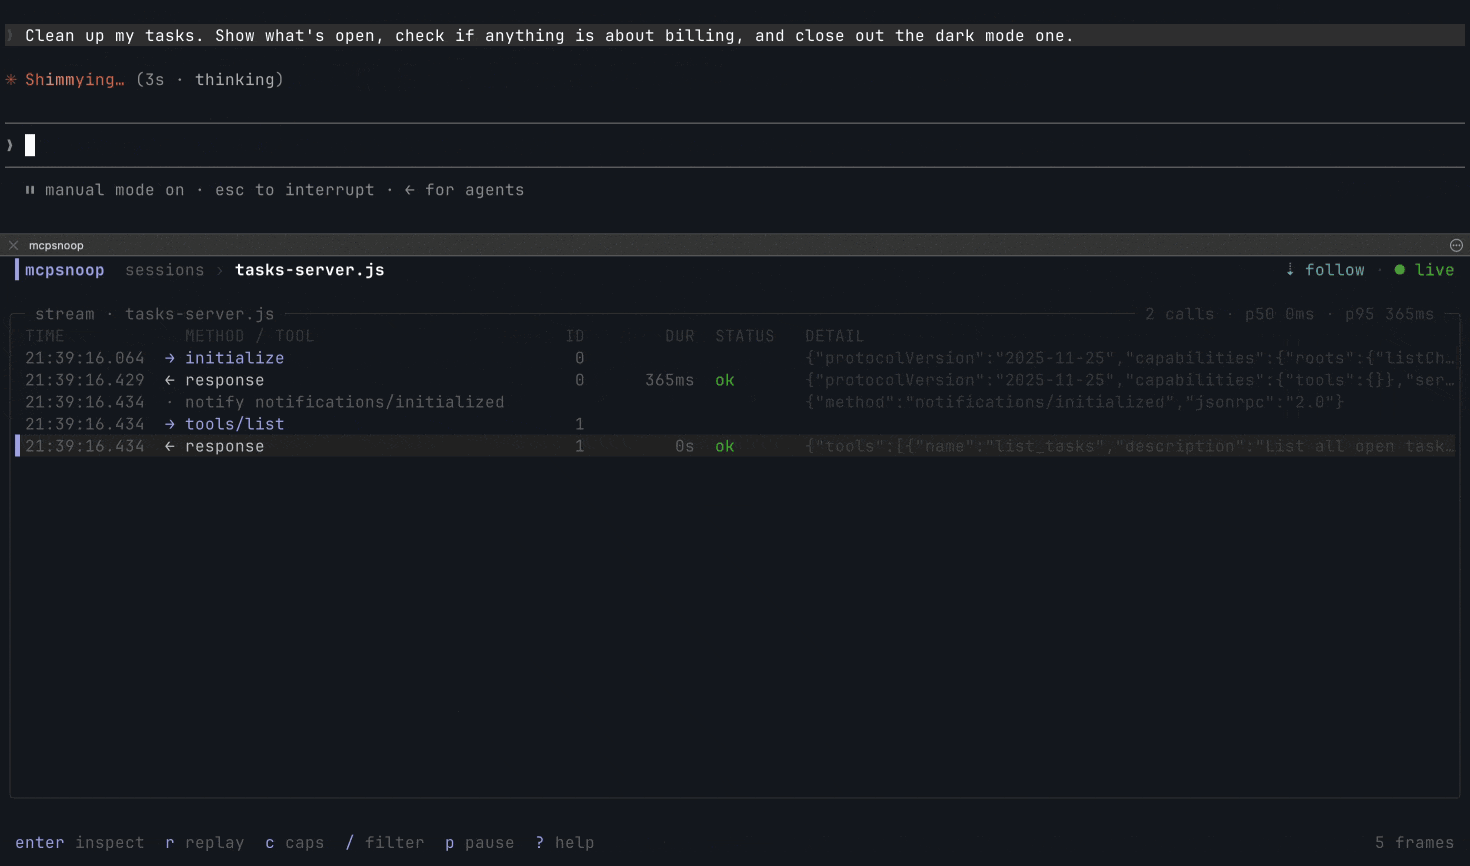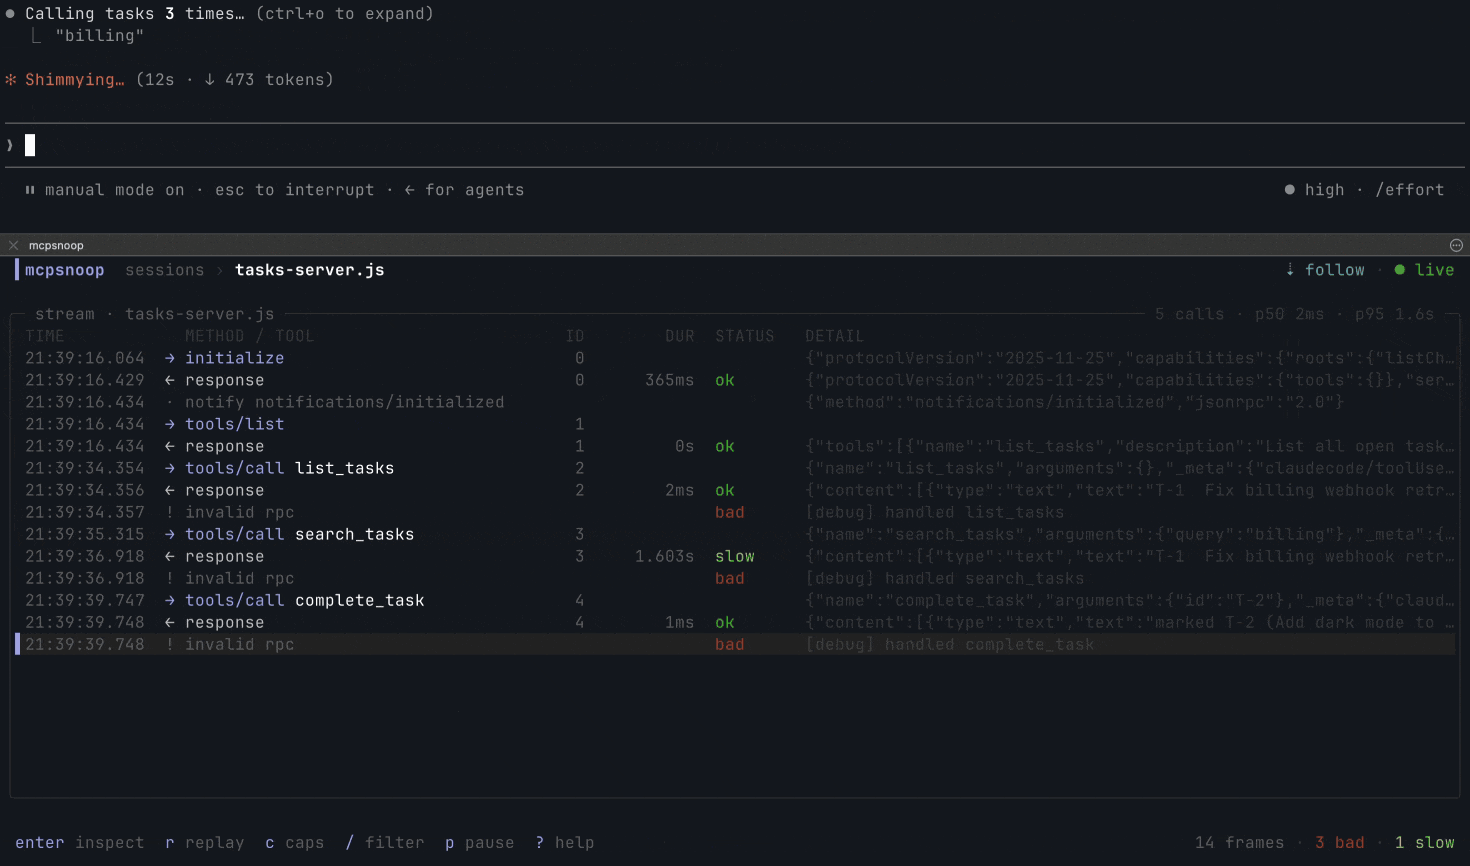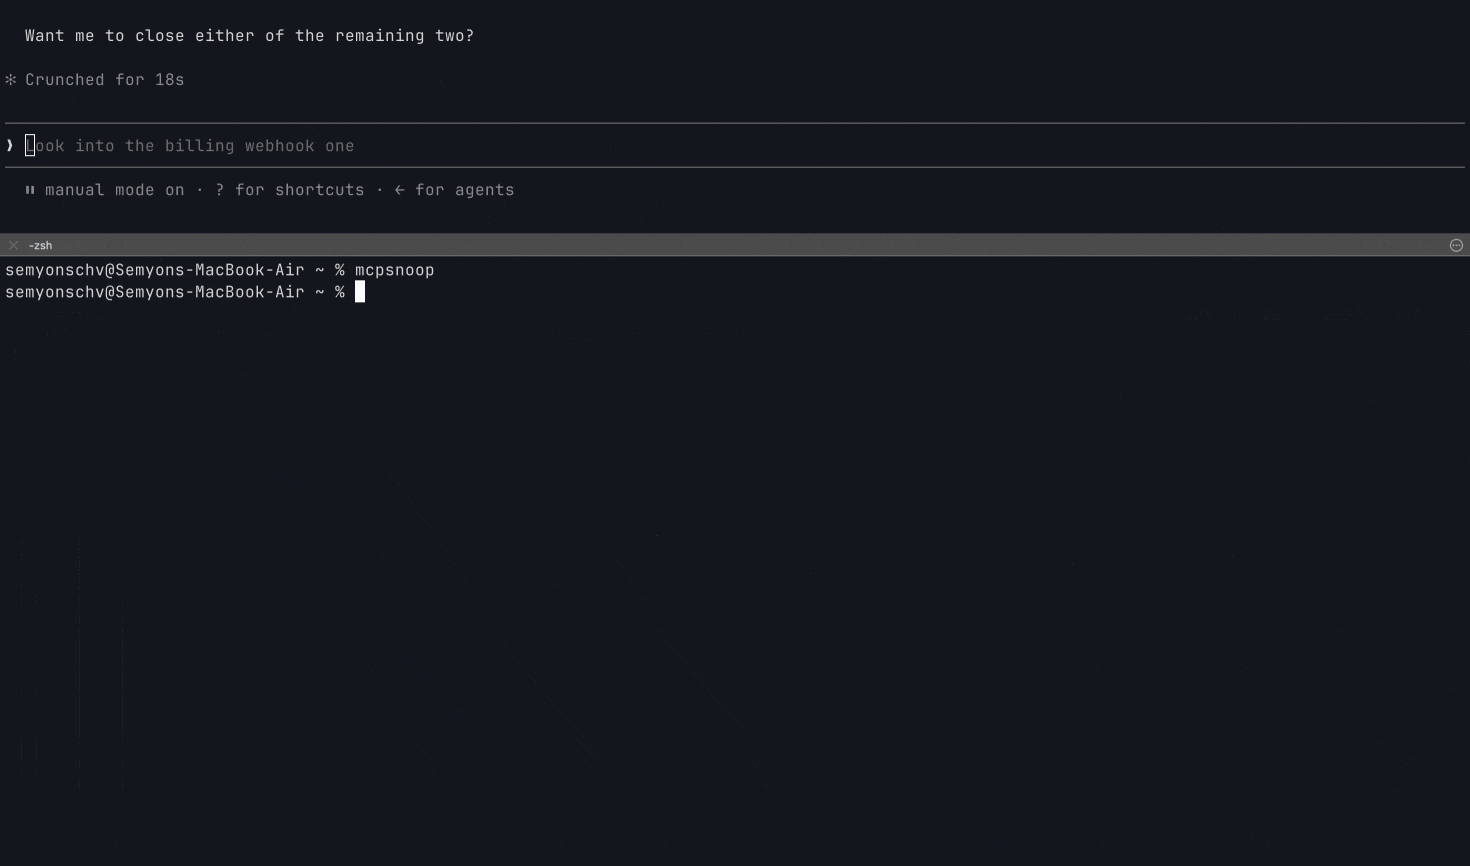
Wireshark for MCP. A transparent proxy that shows every real tool call between your AI client and your MCP servers, live in your terminal.

opensource repo for validating agentic AI applications: redteam, behavior, supply-chain, static analysis

Comprehensive OWASP guide for mobile app security testing, reverse engineering, and verifying MASVS/MASWE weaknesses through static, dynamic, and…

⚡️ Multiple target ZAP Scanning

Some good resources for getting started with application security

Automated API security testing tool that scans REST and SOAP APIs for vulnerabilities using OpenAPI/Swagger specs and WSDL files. Deploys a full …

Automated testing suite with live traffic record and replay

An API hooking framework for intercepting and monitoring Windows applications

Full-stack platform for authorized web application security scanning with a detector-based engine, async Celery workers, and a React dashboard for…

Stage two containers

This experimetal fuzzer is meant to be used for API in-memory fuzzing.


WEB SERVICE SECURITY ASSESSMENT TOOL

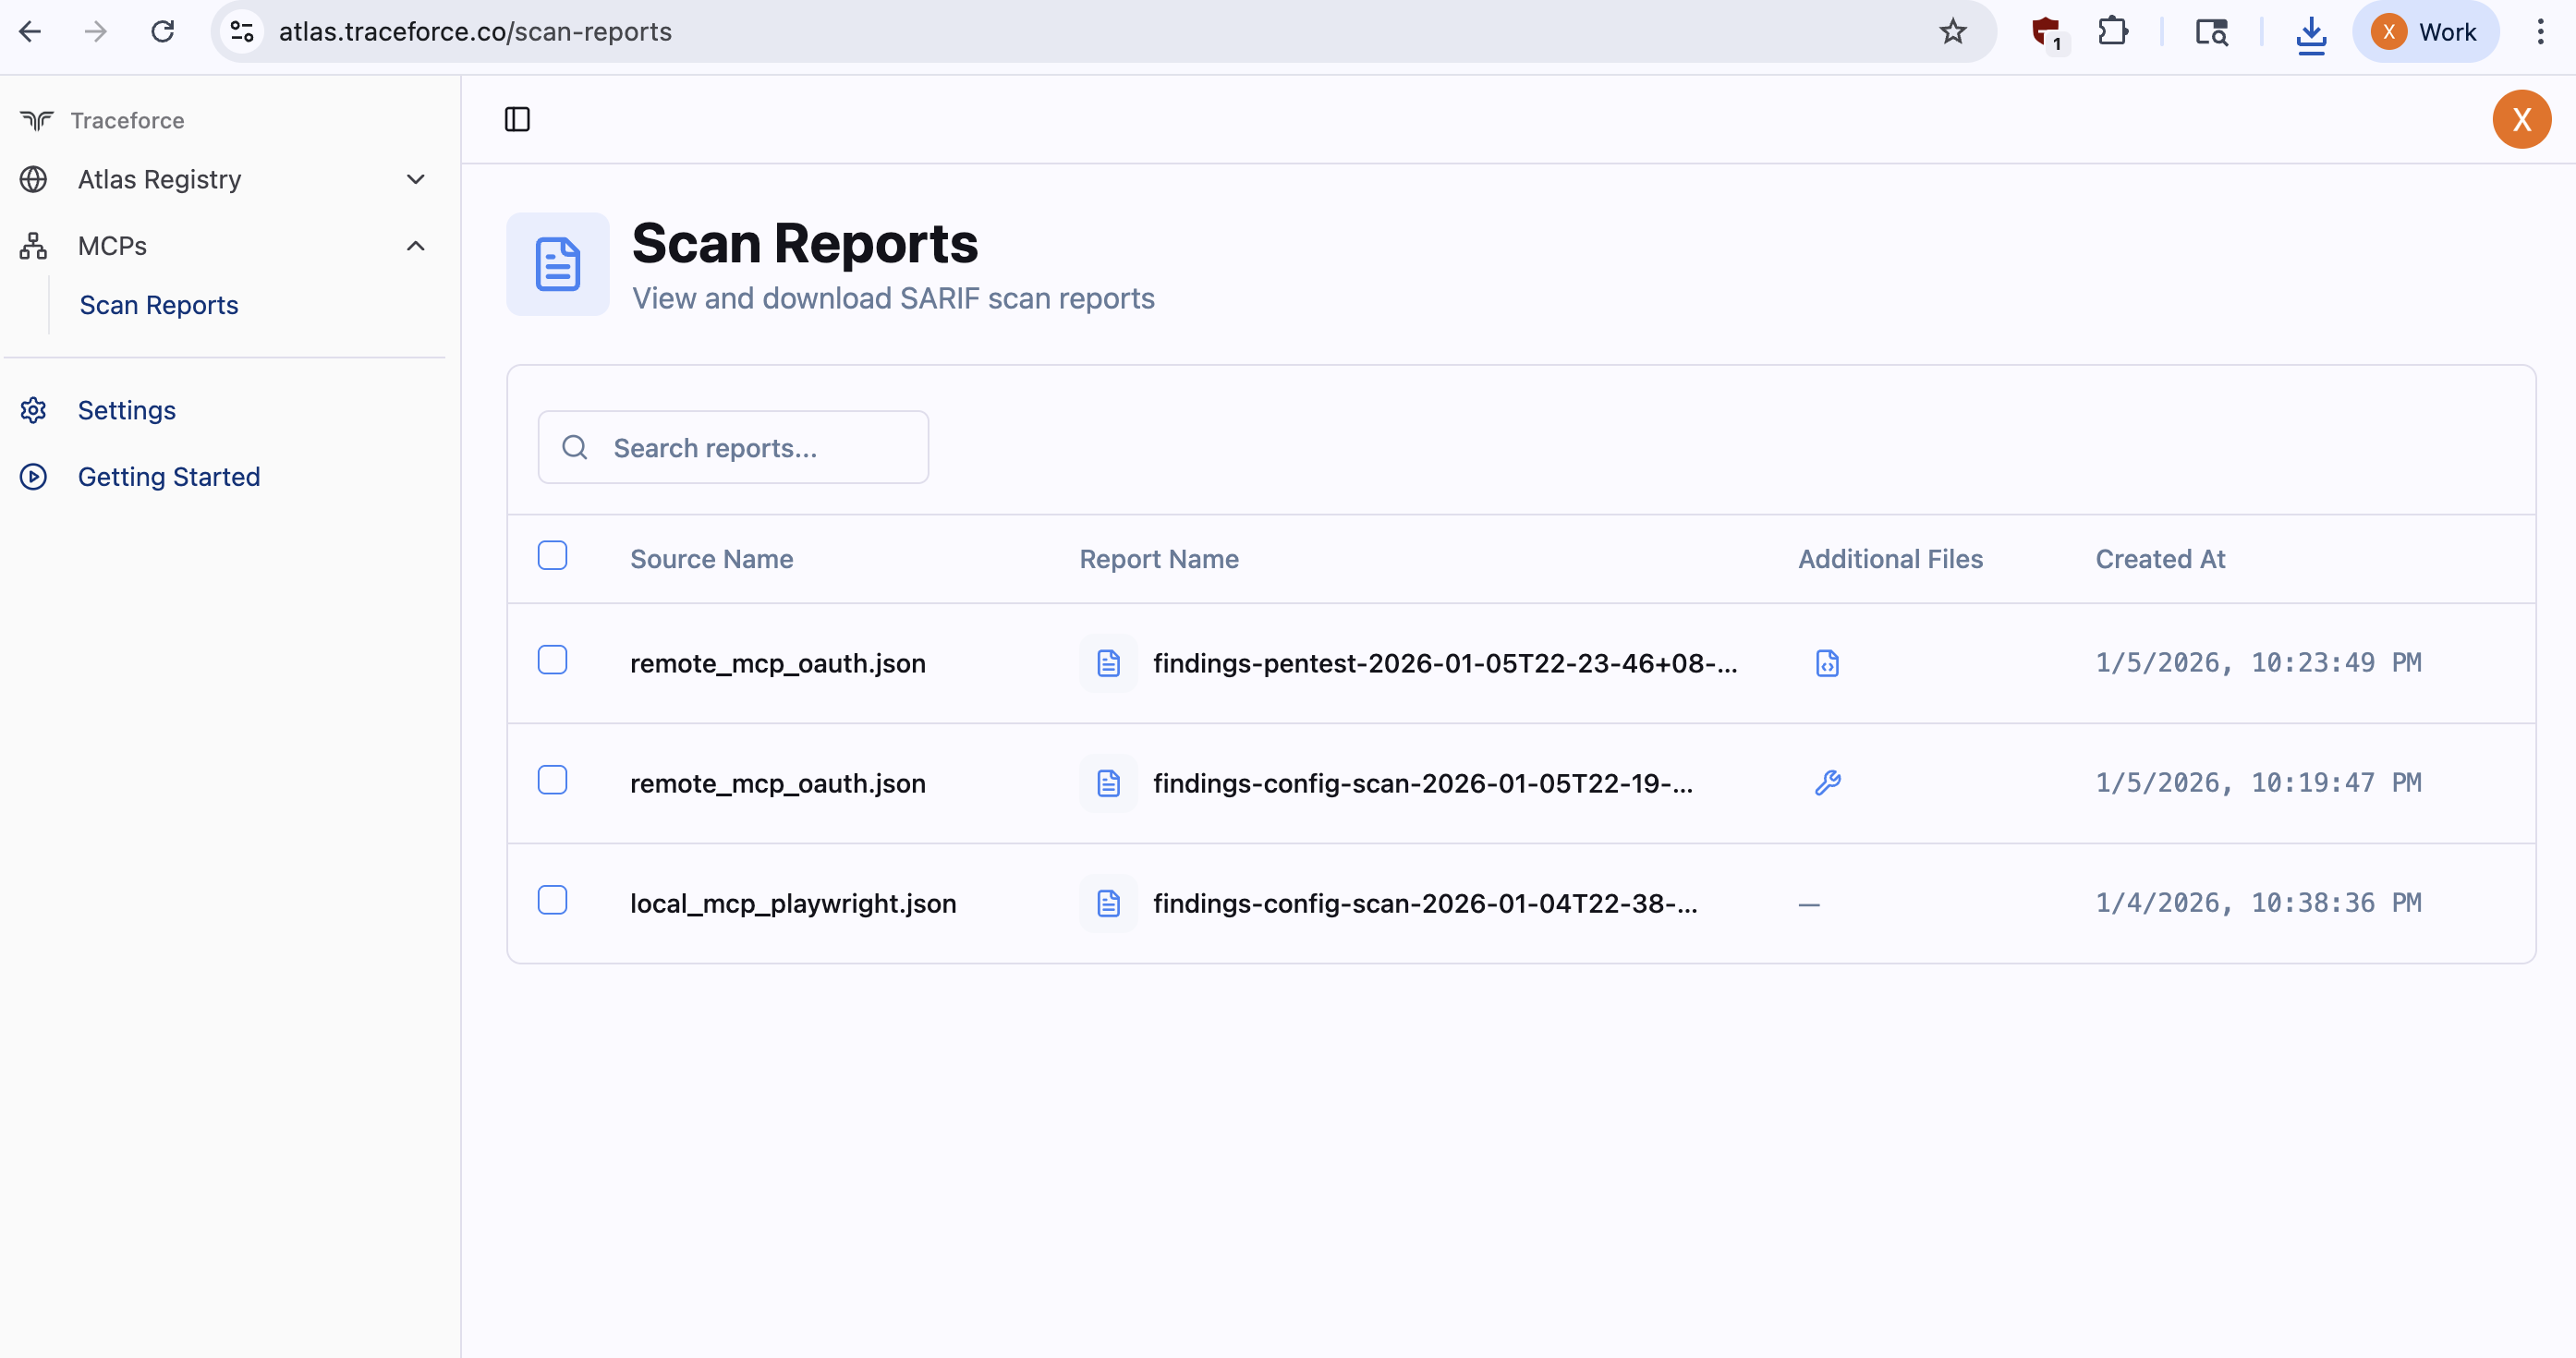
Unified security scanner for MCP servers with config, pentest, and repo-scan modes. Generates SARIF reports for CI/CD integration, detects secrets,…

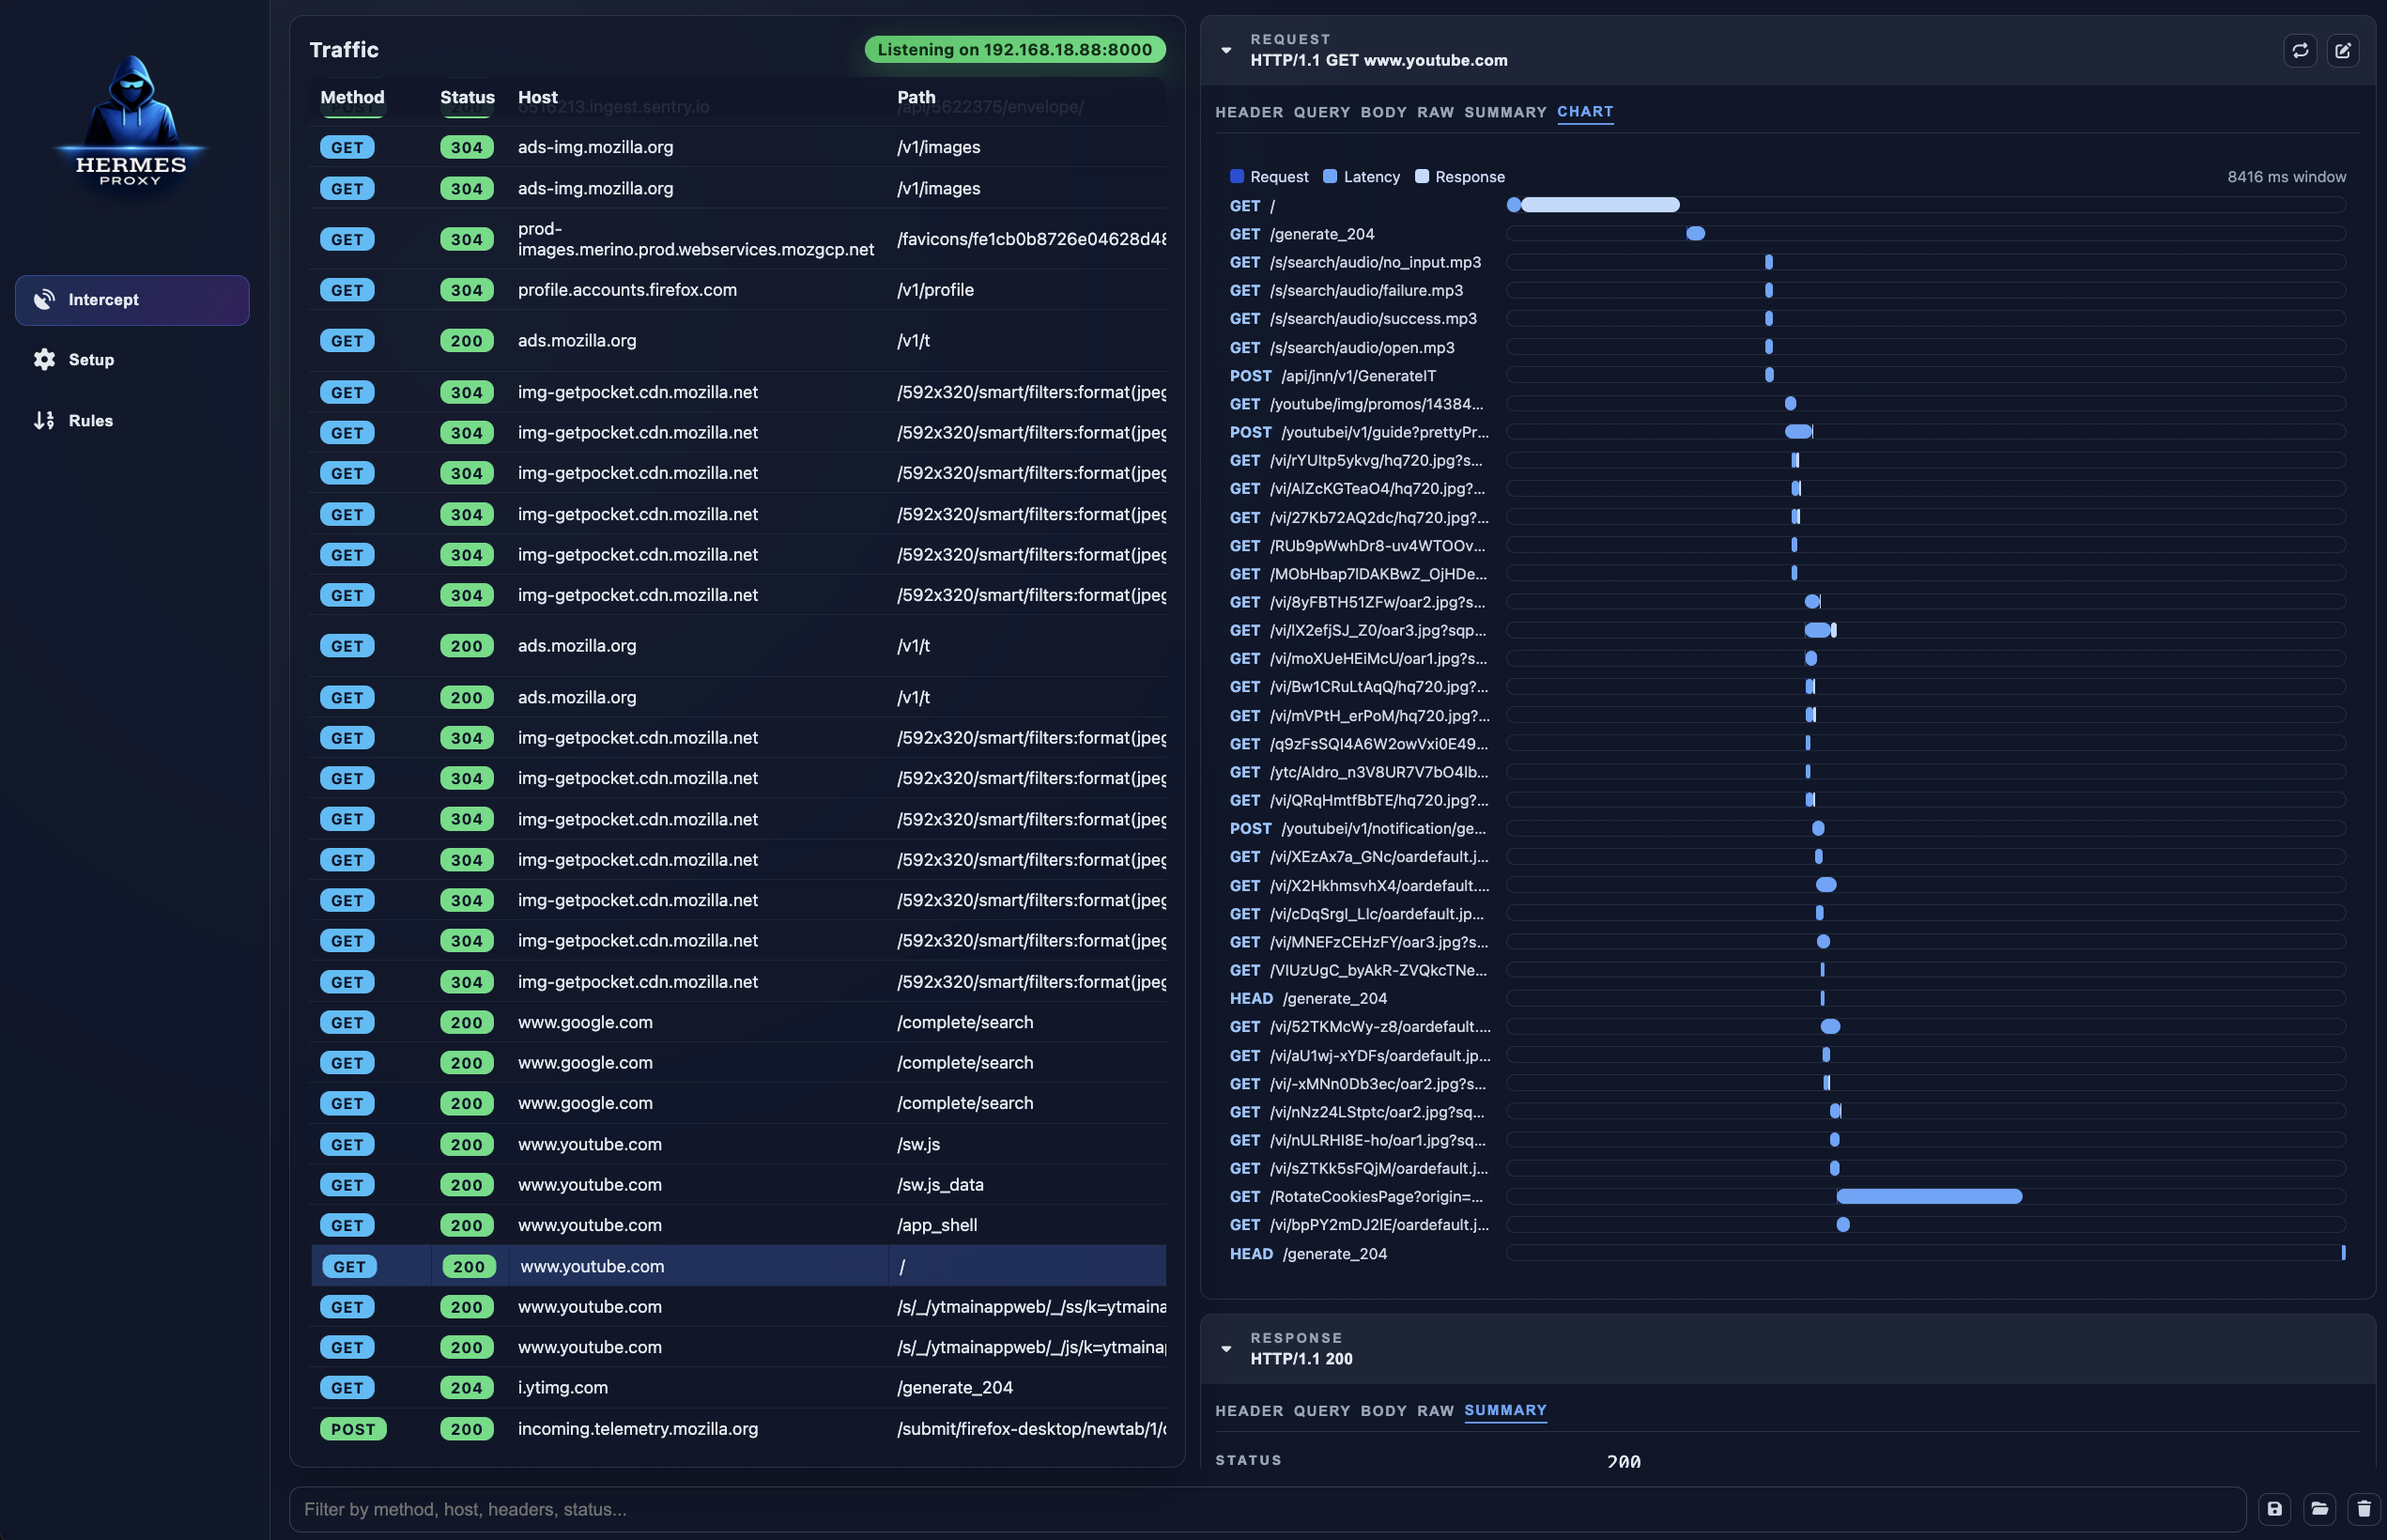
Hermes Proxy - HTTP Traffic Analyzer