
Resources-for-Application-Security
 security-prince/resources-for-application-security
Some good resources for getting started with application security
ctfcurated-resourcesdynamic-analysis-sandboxing+6
148
security-prince/resources-for-application-securitySome good resources for getting started with application security
 mobsf/mobile-security-framework-mobsf
Automated mobile application security testing framework for Android, iOS, and Windows. Performs static and dynamic analysis, malware detection, and…
 kerlenton/mcpsnoop
Wireshark for MCP. A transparent proxy that shows every real tool call between your AI client and your MCP servers, live in your terminal.
 hahwul/mzap
⚡️ Multiple target ZAP Scanning
 silentchainai/silentchain
AI-powered vulnerability scanner extension for Burp Suite with multi-provider support (Ollama, OpenAI, Claude, Gemini)
 owasp/vulnreach
Runtime-aware SCA — proves which CVEs are actually reachable, not just installed.
 nuguardai/nuguard
opensource repo for validating agentic AI applications: redteam, behavior, supply-chain, static analysis
 owasp/mastg
Comprehensive OWASP guide for mobile app security testing, reverse engineering, and verifying MASVS/MASWE weaknesses through static, dynamic, and…
 cspf-founder/api-scanner-docker
Automated API security testing tool that scans REST and SOAP APIs for vulnerabilities using OpenAPI/Swagger specs and WSDL files. Deploys a full …
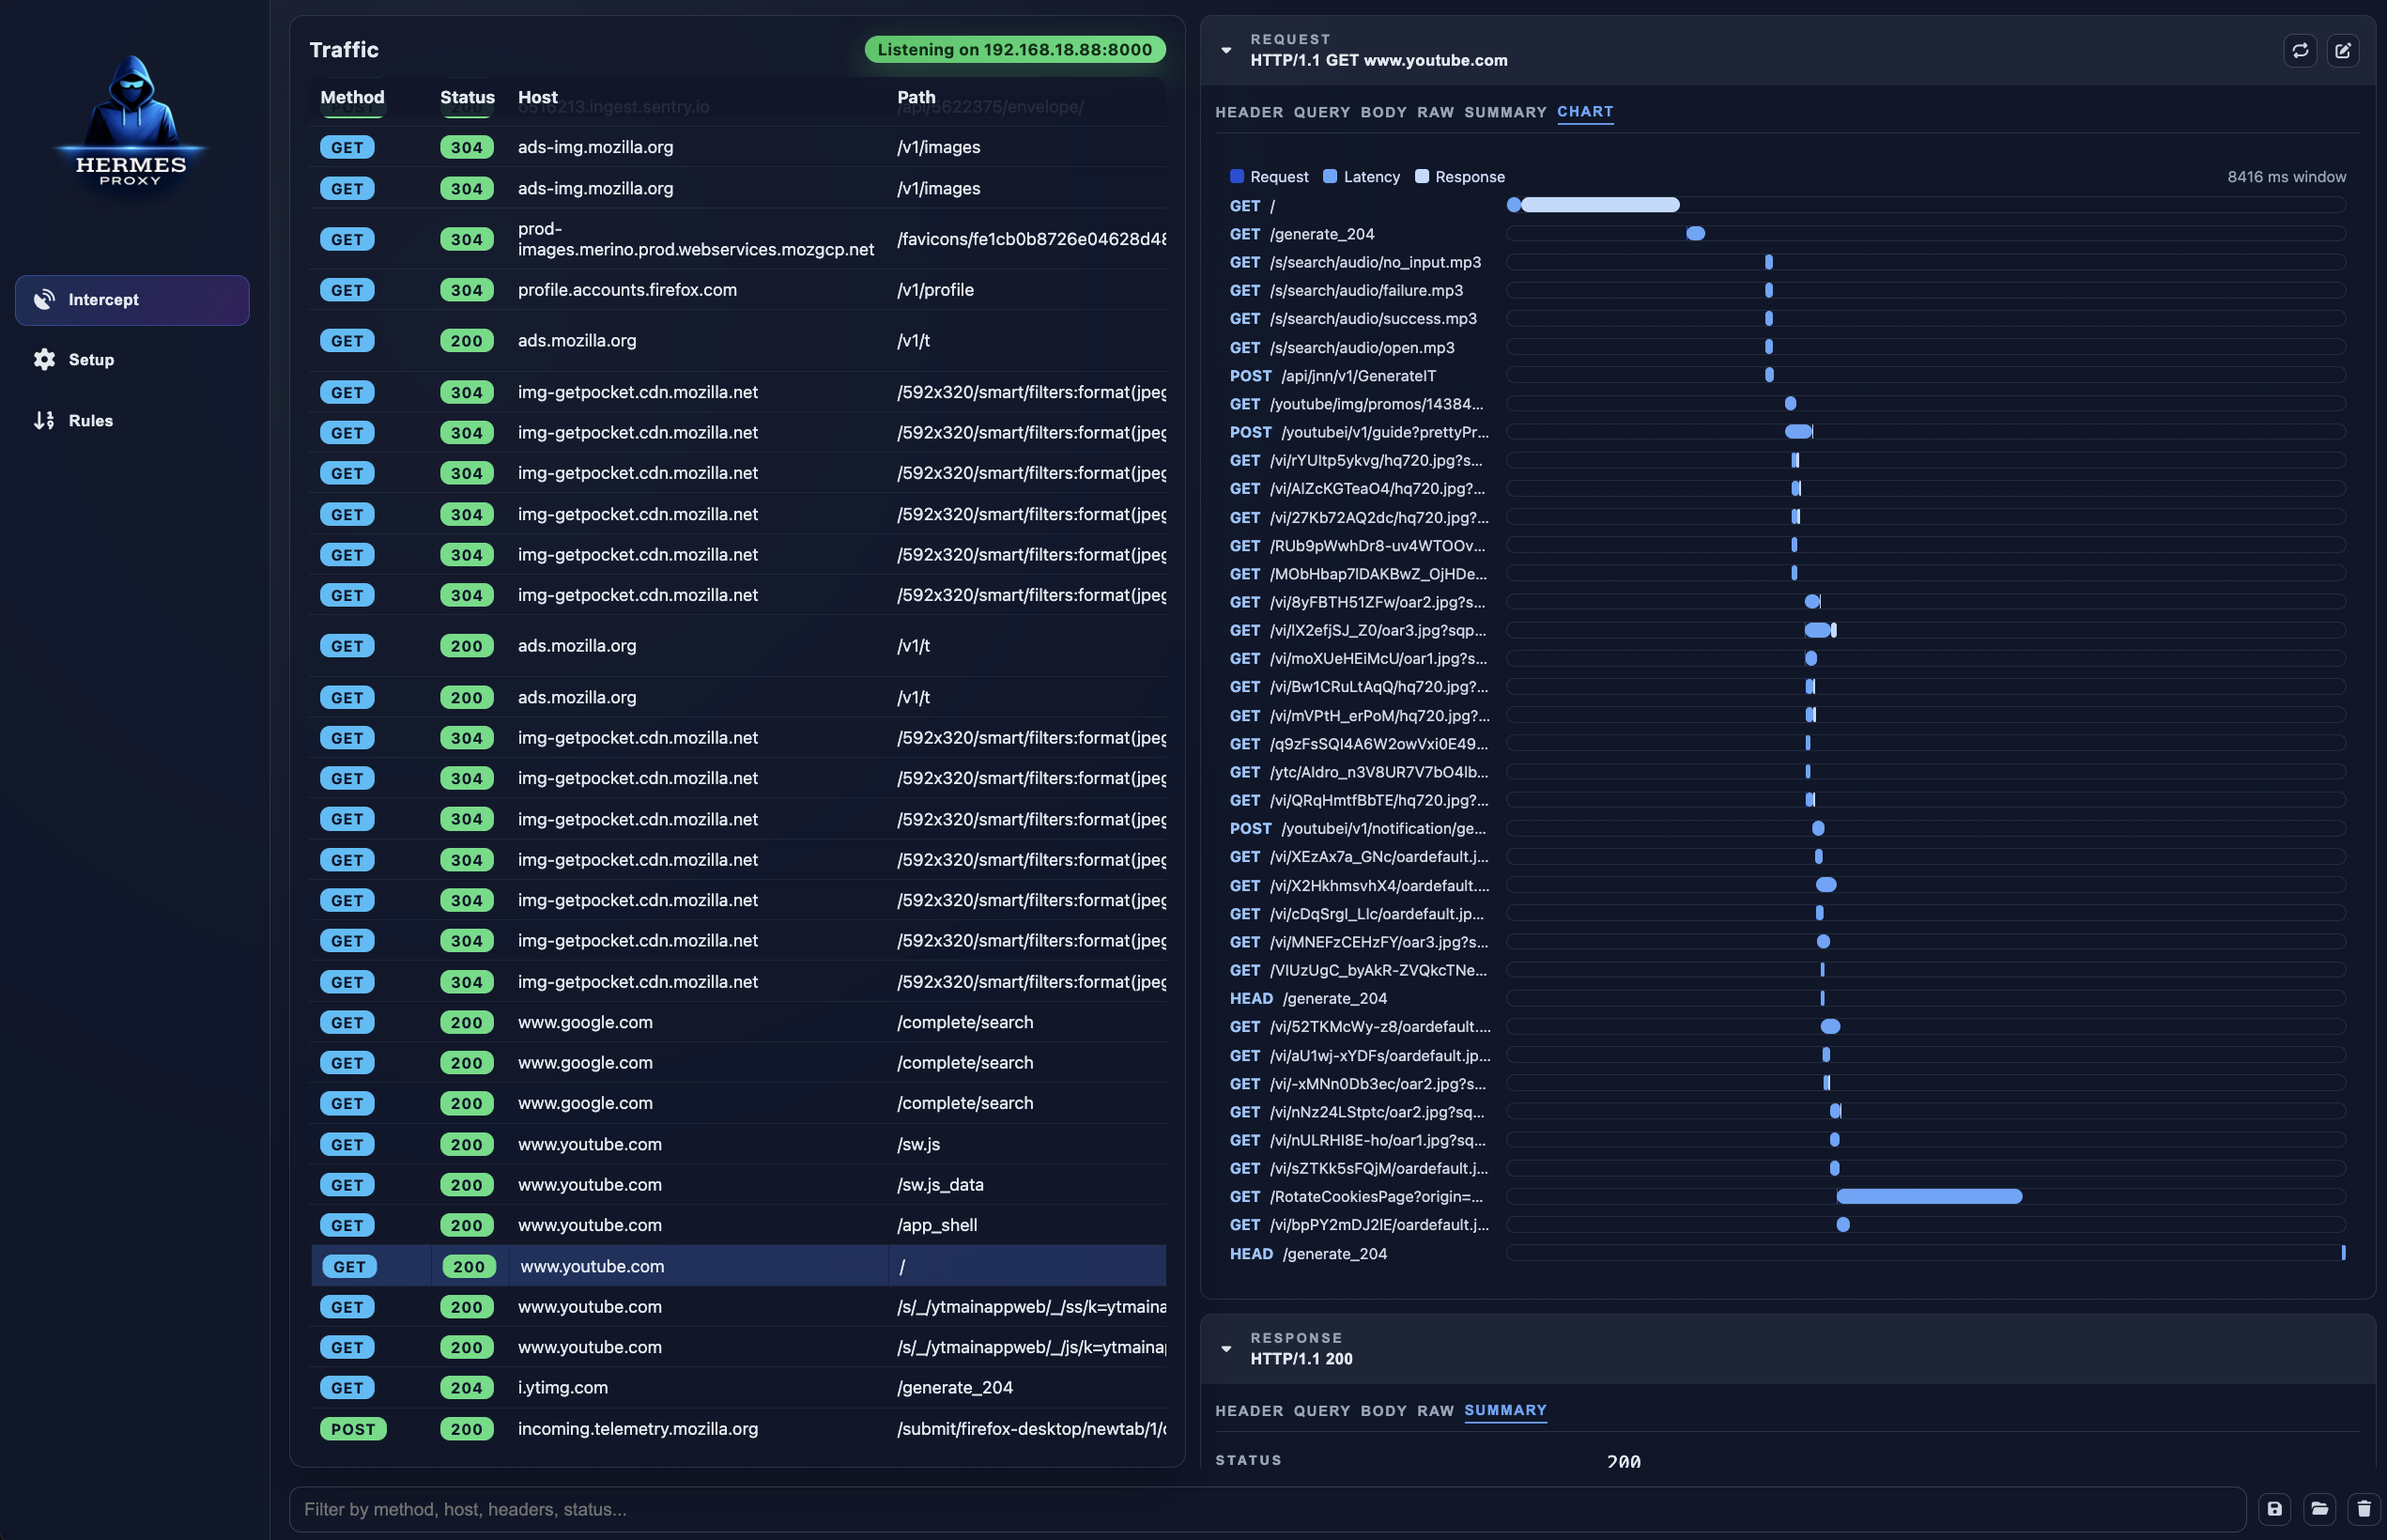 jp/hermes-proxy
Hermes Proxy - HTTP Traffic Analyzer
 hackinglz/maps_scanner
MAPS cloud scanner and response parser for Microsoft Defender research.
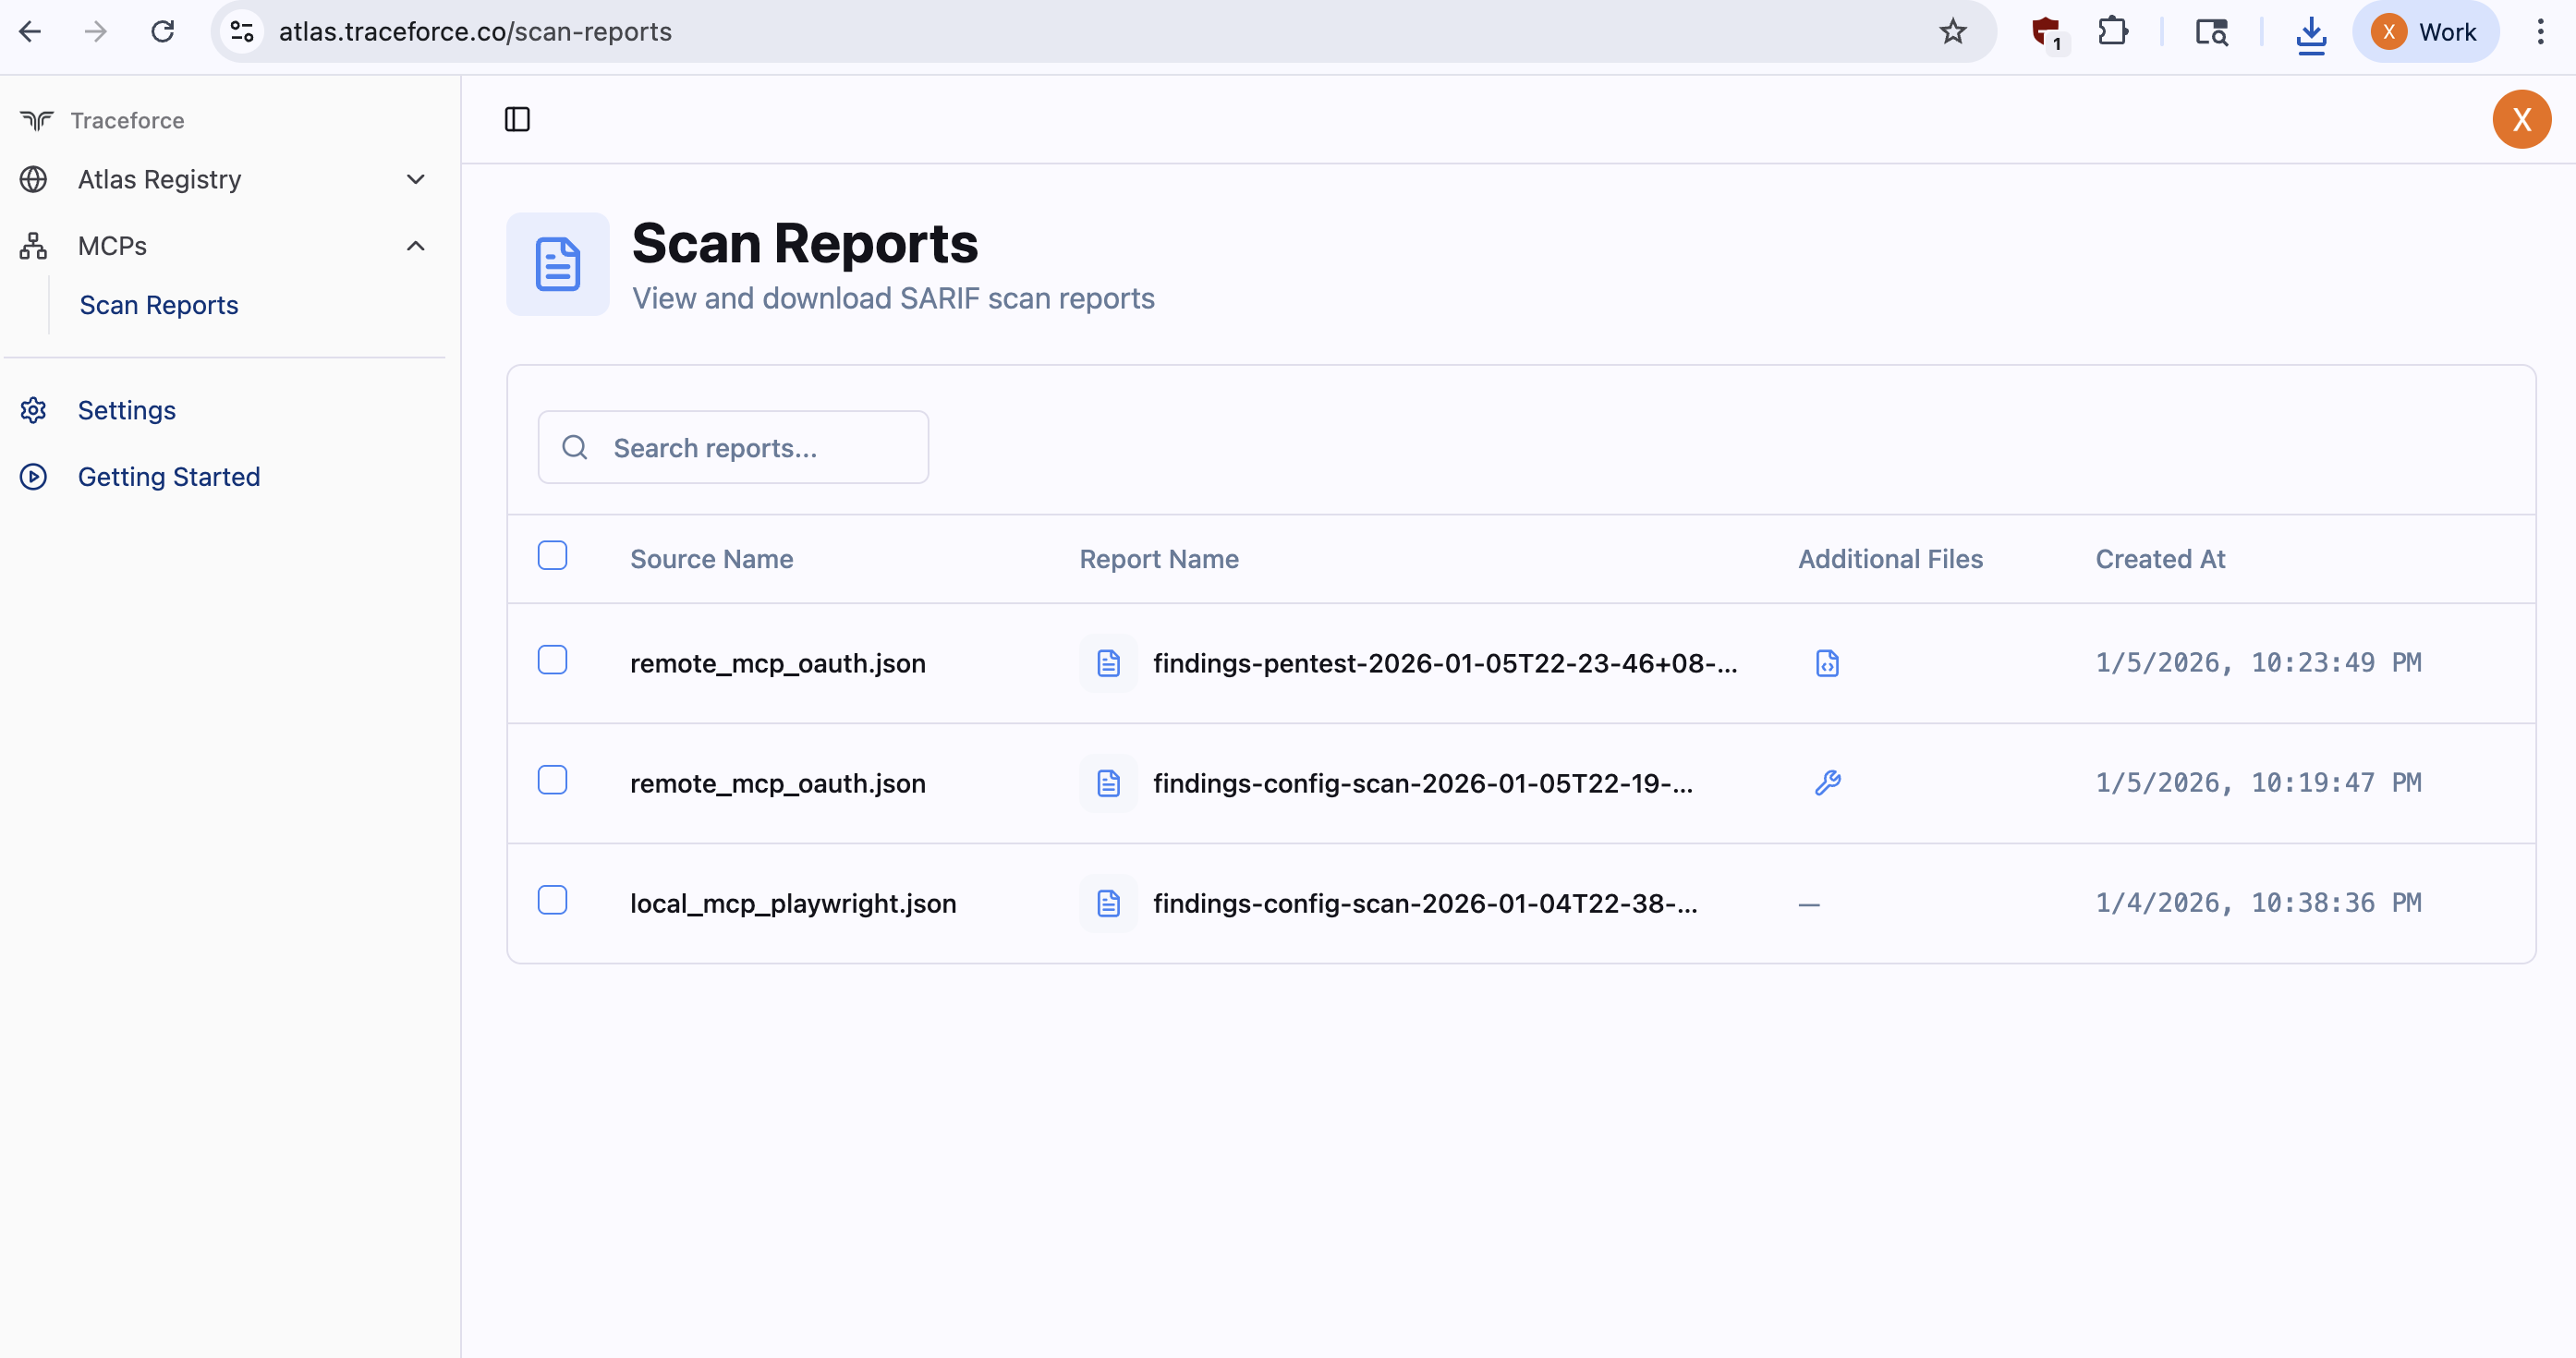 traceforce/mcp-xray
Unified security scanner for MCP servers with config, pentest, and repo-scan modes. Generates SARIF reports for CI/CD integration, detects secrets,…
 kaisonox/apiscope
An API hooking framework for intercepting and monitoring Windows applications
 andreafioraldi/frida-fuzzer
This experimetal fuzzer is meant to be used for API in-memory fuzzing.
 yalcinyolalan/wssat
WEB SERVICE SECURITY ASSESSMENT TOOL
 use-tusk/tusk-cli
Automated testing suite with live traffic record and replay
 foxvr-sudo/bug-bounty-arsenal-v.3
Full-stack platform for authorized web application security scanning with a detector-based engine, async Celery workers, and a React dashboard for…
 purpleteam-labs/purpleteam-s2-containers
Stage two containers