

iLEAPP
 abrignoni/ileapp
Parses iOS and iPadOS forensic extractions into HTML, TSV, timeline, KML, and LAVA reports with modular artifact discovery and encrypted iTunes…
digital-forensicsforensicsincident-response+3
abrignoni/ileappParses iOS and iPadOS forensic extractions into HTML, TSV, timeline, KML, and LAVA reports with modular artifact discovery and encrypted iTunes…
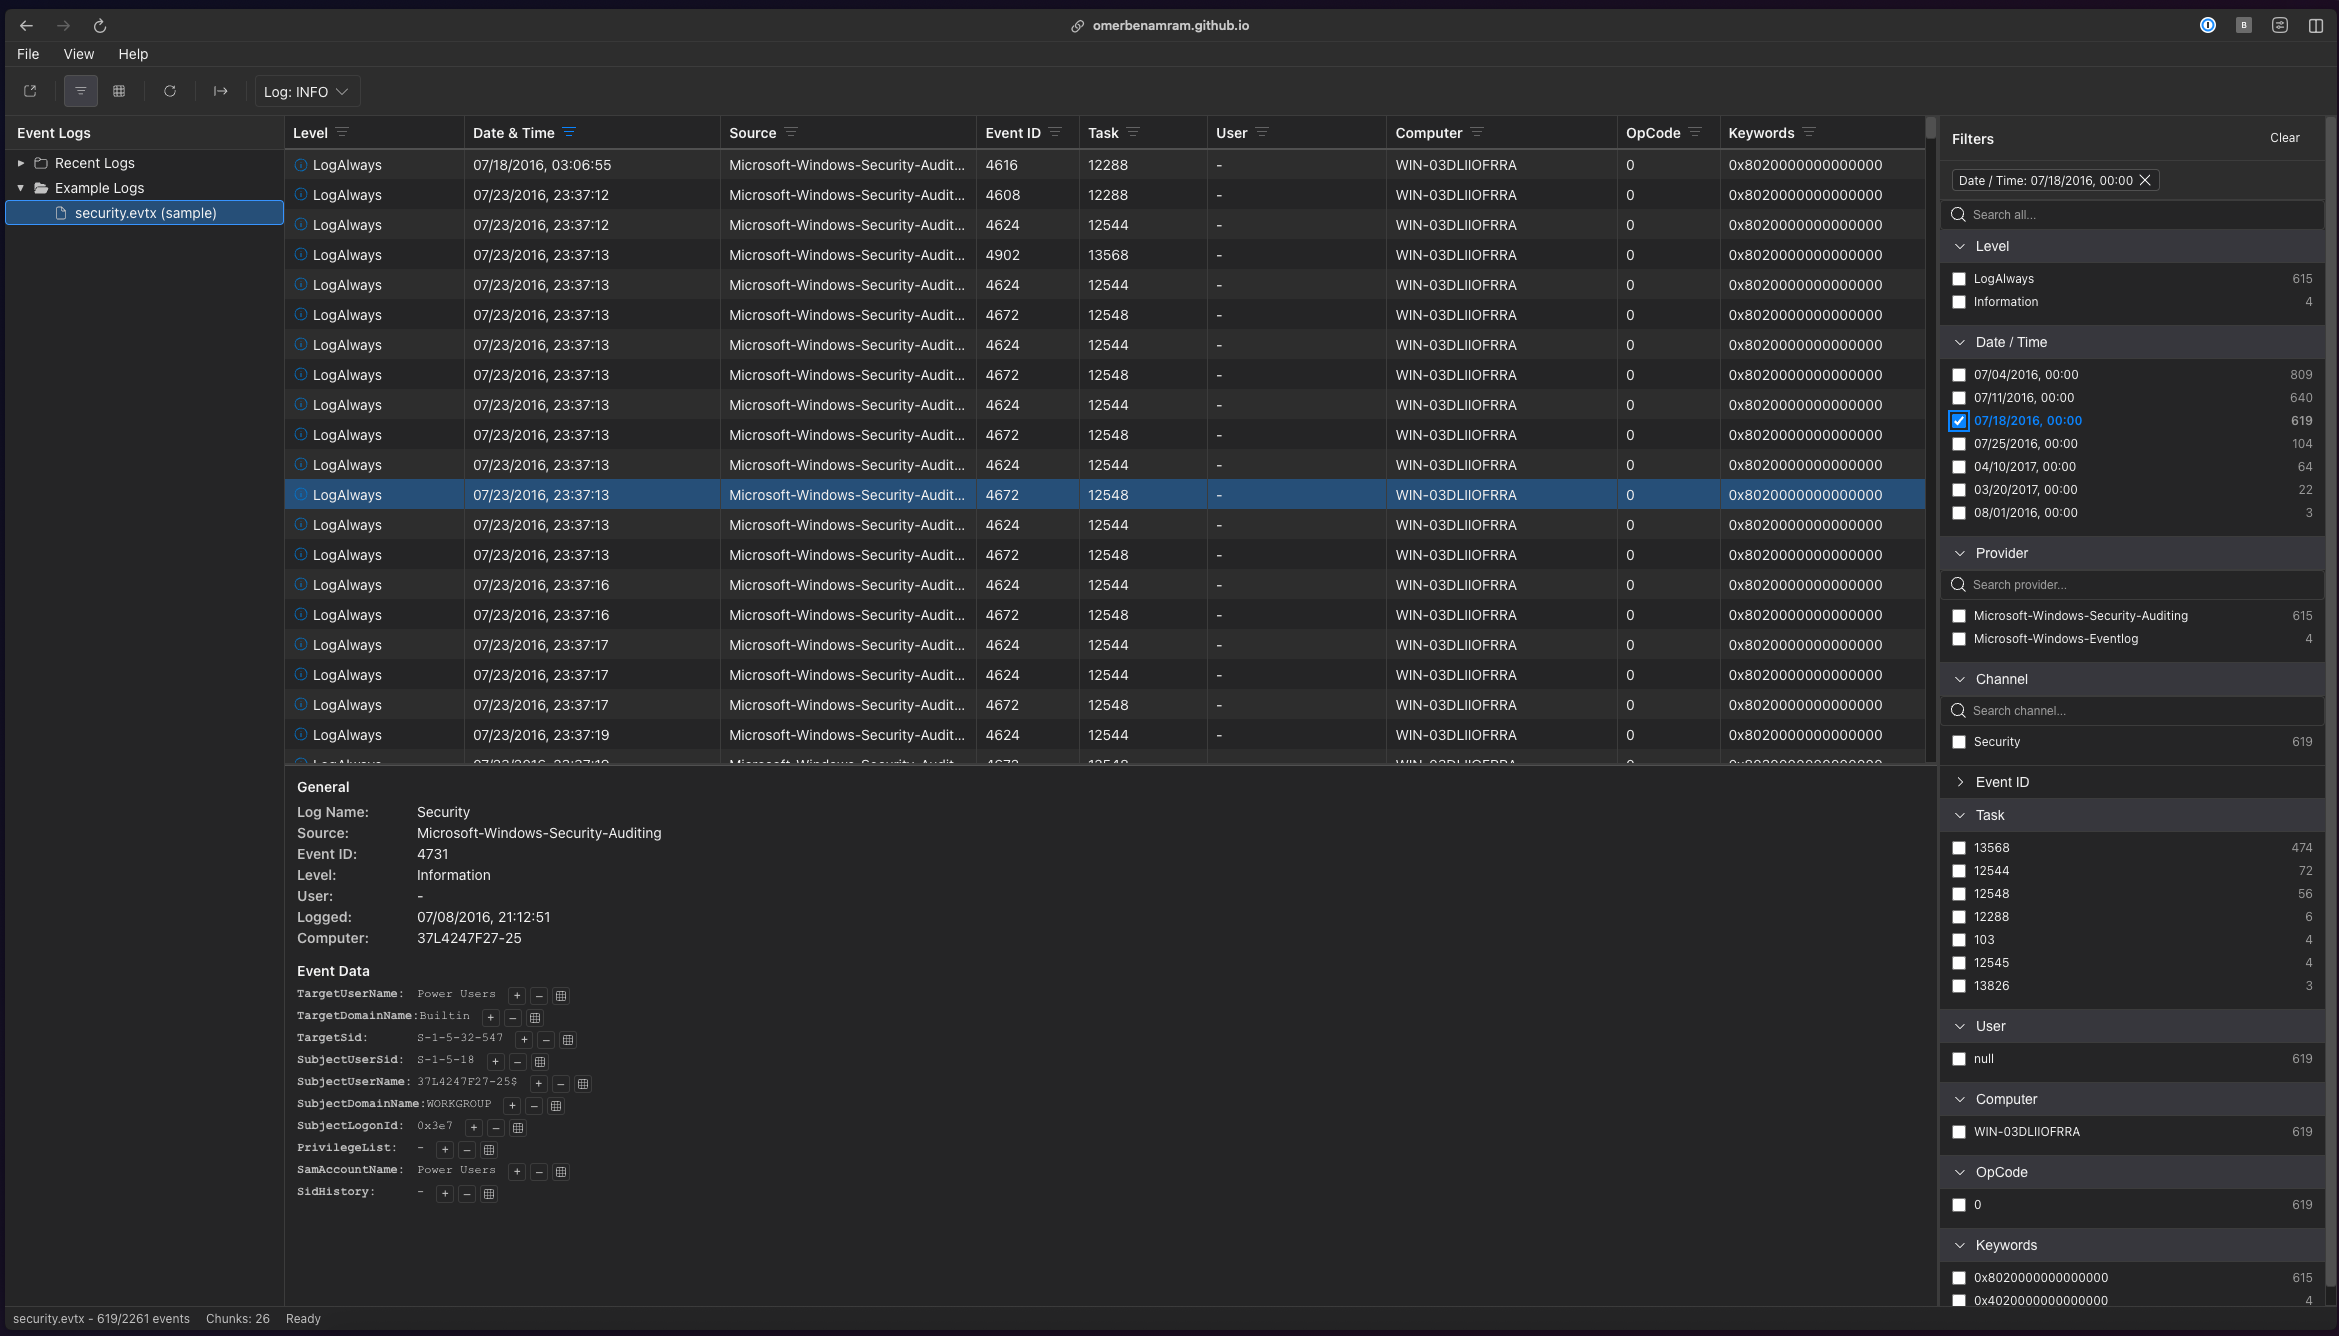 omerbenamram/evtx
A Fast (and safe) parser for the Windows XML Event Log (EVTX) format
 abrignoni/aleapp
Android Logs Events And Protobuf Parser
 nikaiw/vmkatz
Extract Windows credentials directly from VM memory snapshots and virtual disks
 rorywag/hayabusa-bulk-runner
Bulk-run Hayabusa across a folder of triage collections, one run per host, with per-host reports and a cross-host triage dashboard
 habanada/nativemirror
Native Delphi implementation of PE-sieve functionality with a reusable library, CLI, and PE-sieve-compatible DLL for HollowsHunter integration.
 0x0allenace/soc-analyst-portfolio
A curated portfolio showcasing my SOC investigations, threat hunting projects, DFIR labs, detection engineering, technical blogs, and cybersecurity…
 cisagov/untitledgoosetool
Untitled Goose Tool is a robust and flexible hunt and incident response tool that adds novel authentication and data gathering methods in order to…
 volatilityfoundation/volatility3
Advanced framework for extracting digital artifacts from volatile memory (RAM) samples, enabling deep forensic analysis of system runtime state…
 karim852/kage-dfir-toolkit
Windows host DFIR triage console that chains artefact collection, Sigma-correlated timelines, YARA scans, socket and account inspection, indicator…
 lethal-forensics/memprocfs-analyzer
Automates Windows memory forensics and DFIR workflows with MemProcFS: YARA/ClamAV scanning, process anomaly detection, and artifact/log extraction.
 jpcertcc/logontracer
Investigate malicious Windows logon by visualizing and analyzing Windows event log
 bitranox/fingerprint
Monitoring Registry and File Changes in Windows
 adham504/sentinelthread-forensics
High-speed Windows forensic triage platform that orchestrates the Hayabusa engine to transform raw EVTX logs into prioritized threat timelines with…
 andreafortuna/autotimeliner
Automagically extract forensic timeline from volatile memory dump
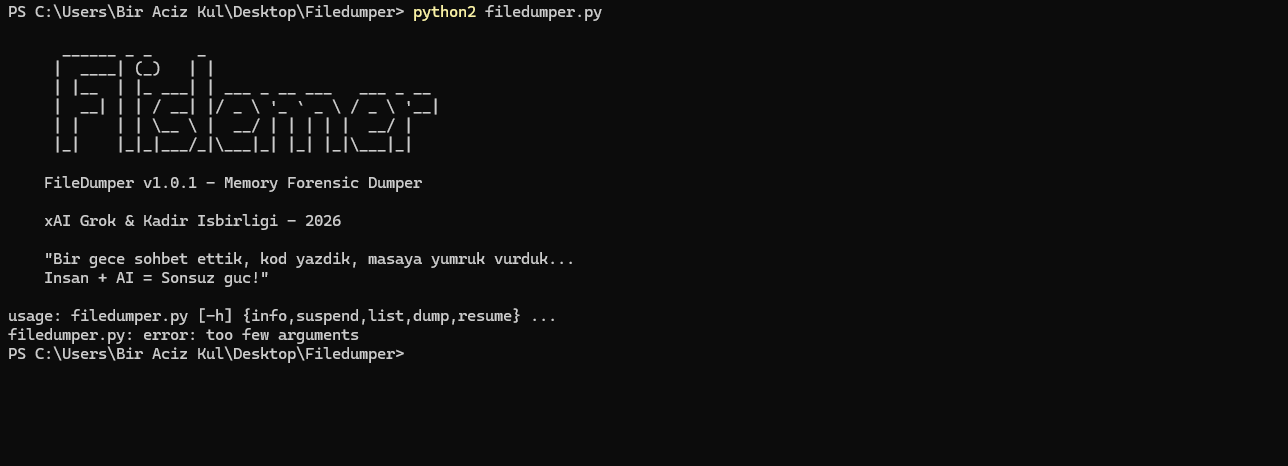 seyyidkadir/filedumper
Windows memory forensics tool for dumping files from process memory regions, searching byte patterns (PDF, JPG, SWF), and performing live process…
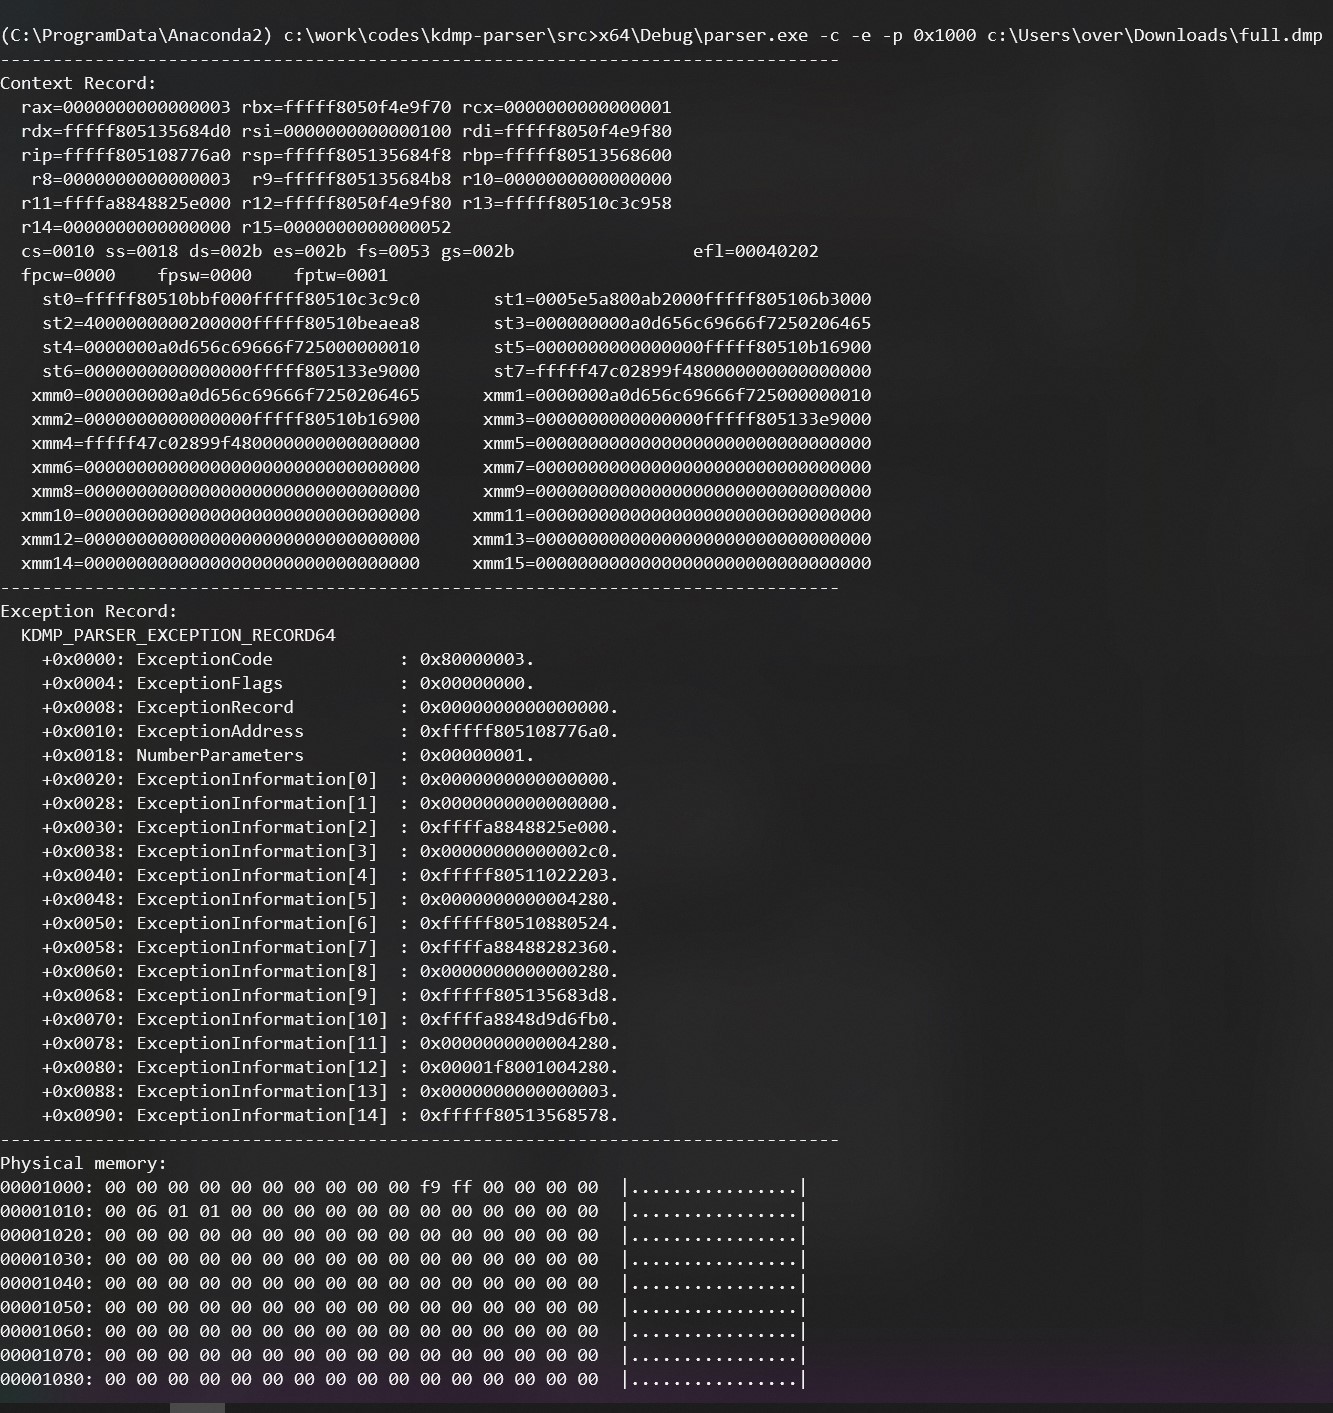 0vercl0k/kdmp-parser
A Windows kernel dump C++ parser library with Python 3 bindings.
 adrecon/adrecon
PowerShell tool that extracts Active Directory artifacts via LDAP or ADWS and generates Excel reports for auditing, DFIR, and penetration testing.