
Archived
raptor
 dpnishant/raptor
Web-based Source Code Vulnerability Scanner
android-securitycode-analysisdevsecops+6
354
 zaproxy/zaproxy
Open-source web application security scanner for automated vulnerability detection, manual penetration testing, and API security testing with a…
 0sec-labs/0
Open-source AI security harness. Includes a web UI for code analysis, pentesting, vulnerability research, reverse engineering, verification, and…
 nccgroup/cowcloud
Serverless AWS solution for distributing recon and vulnerability scanning workloads. Submit tasks via web UI; EC2 workers execute custom Python…
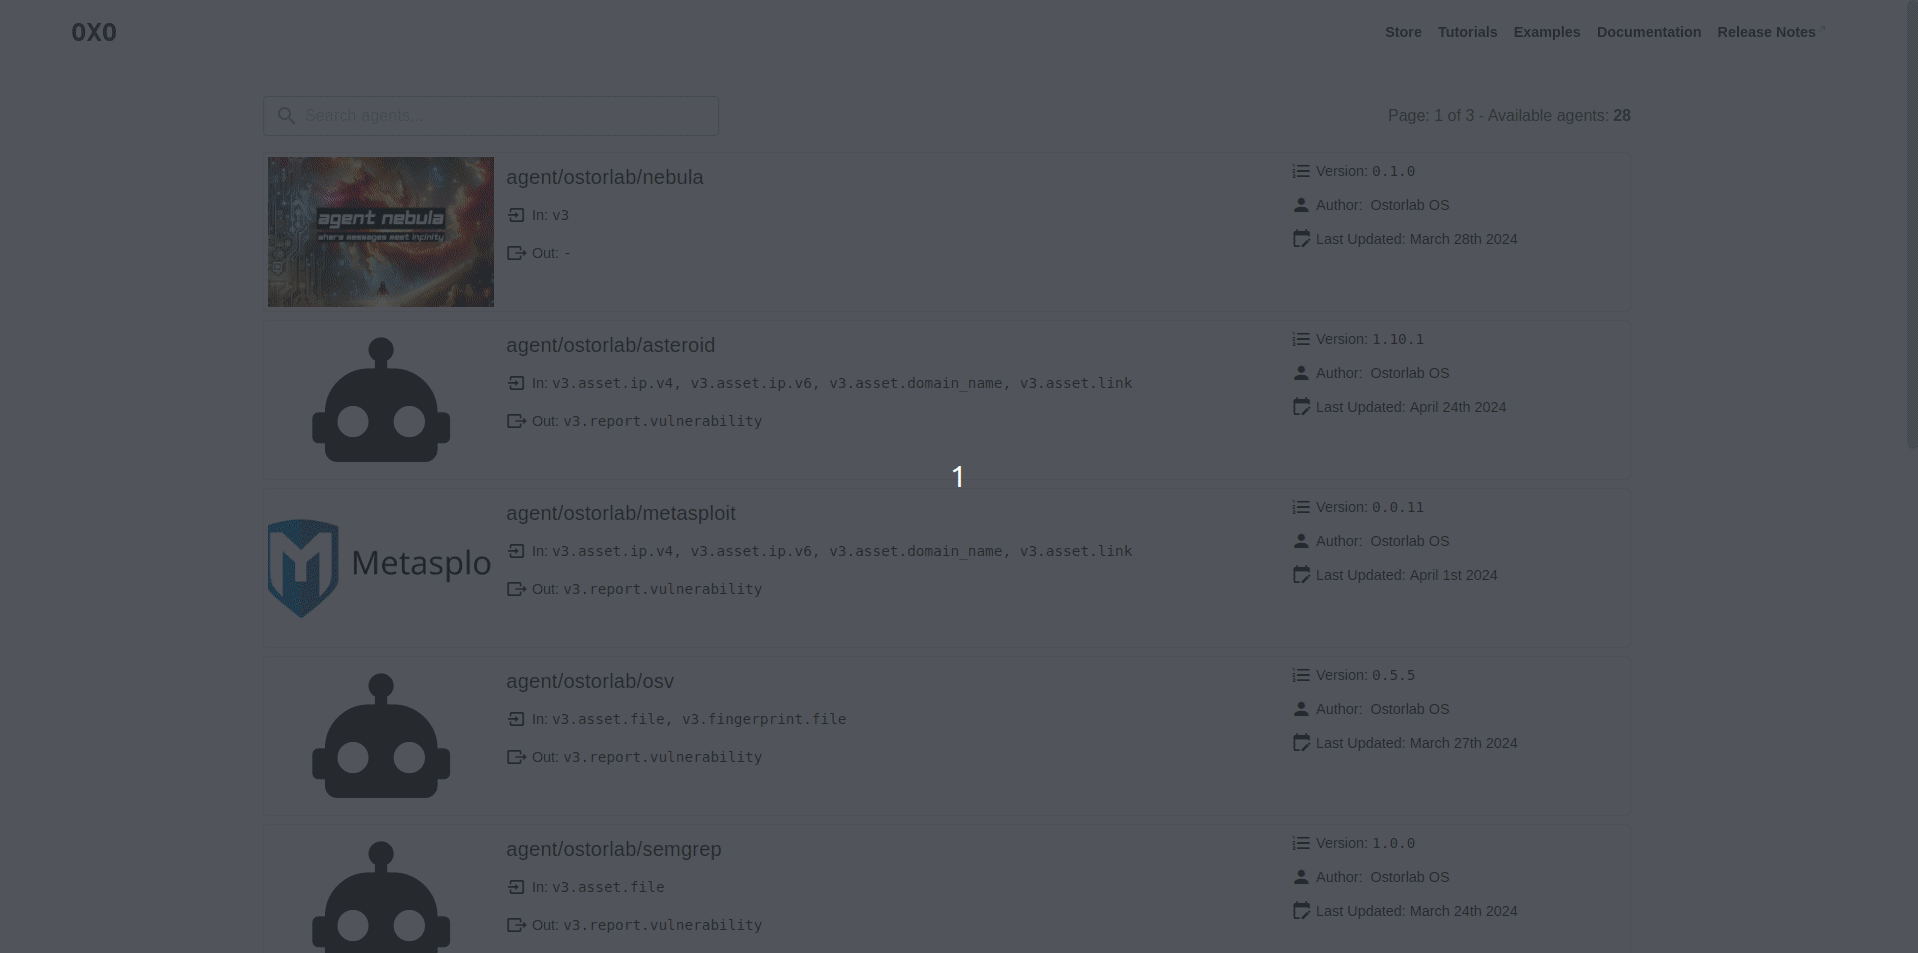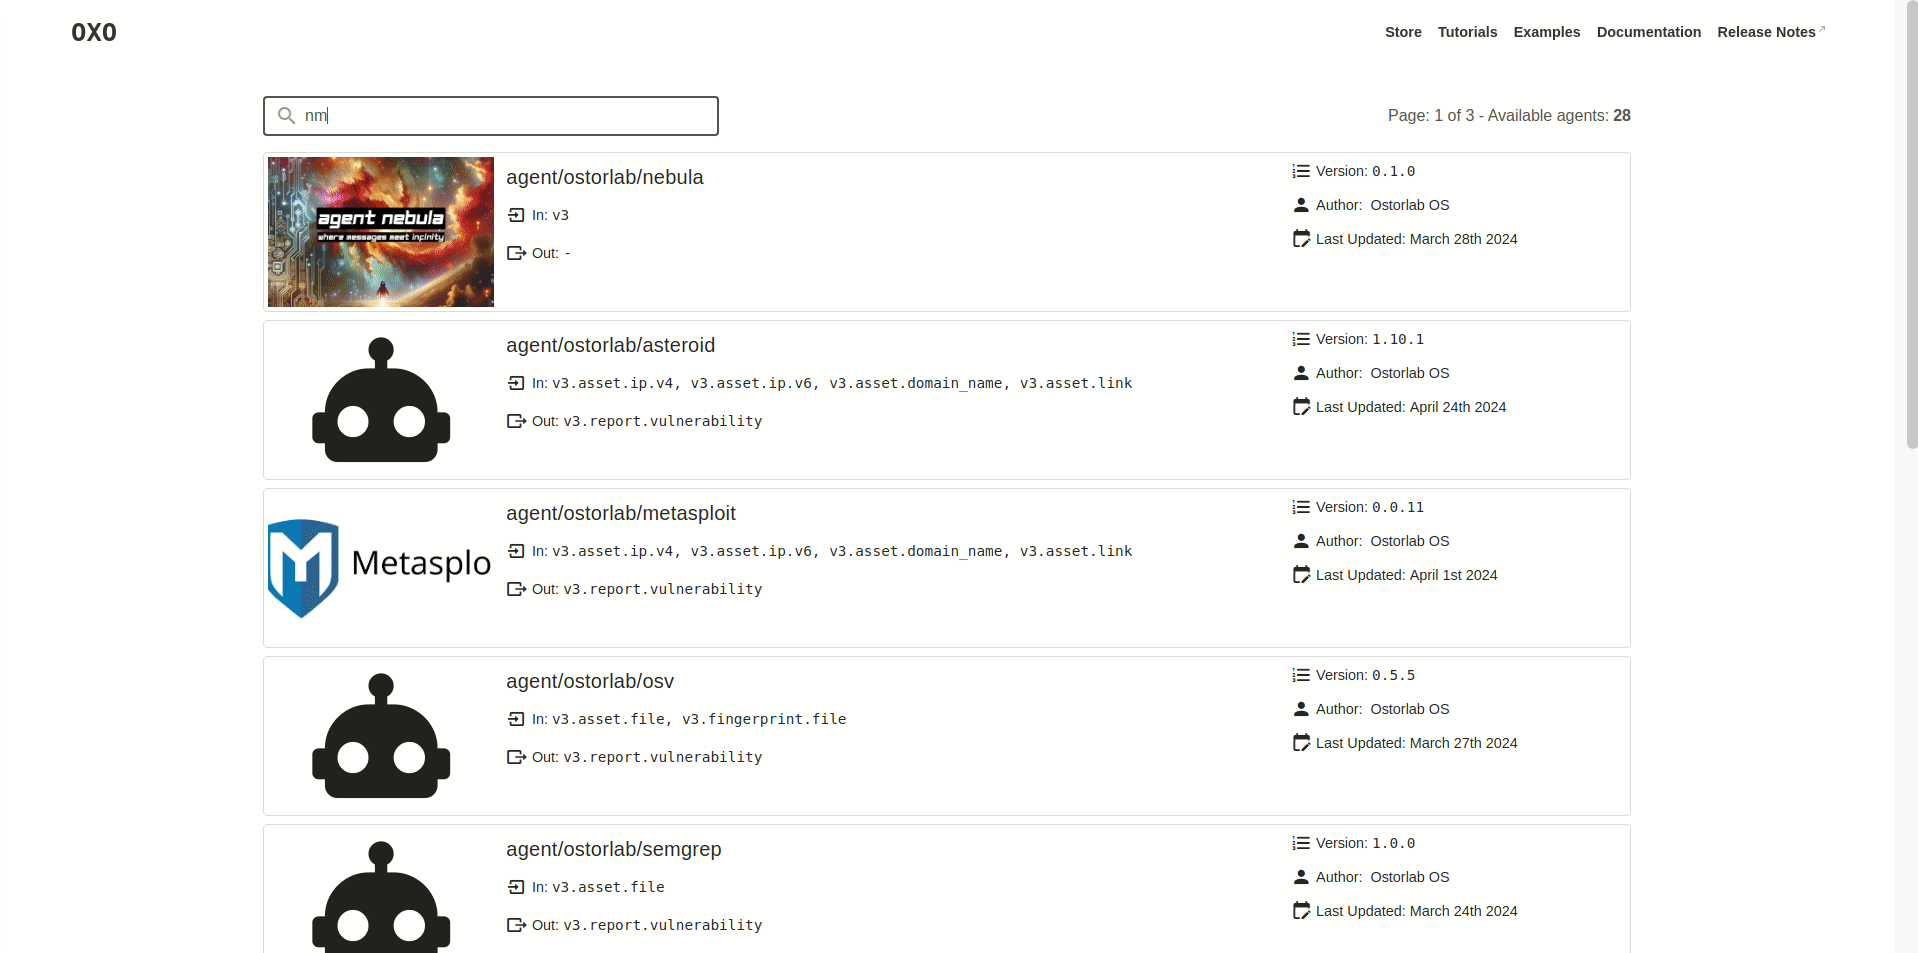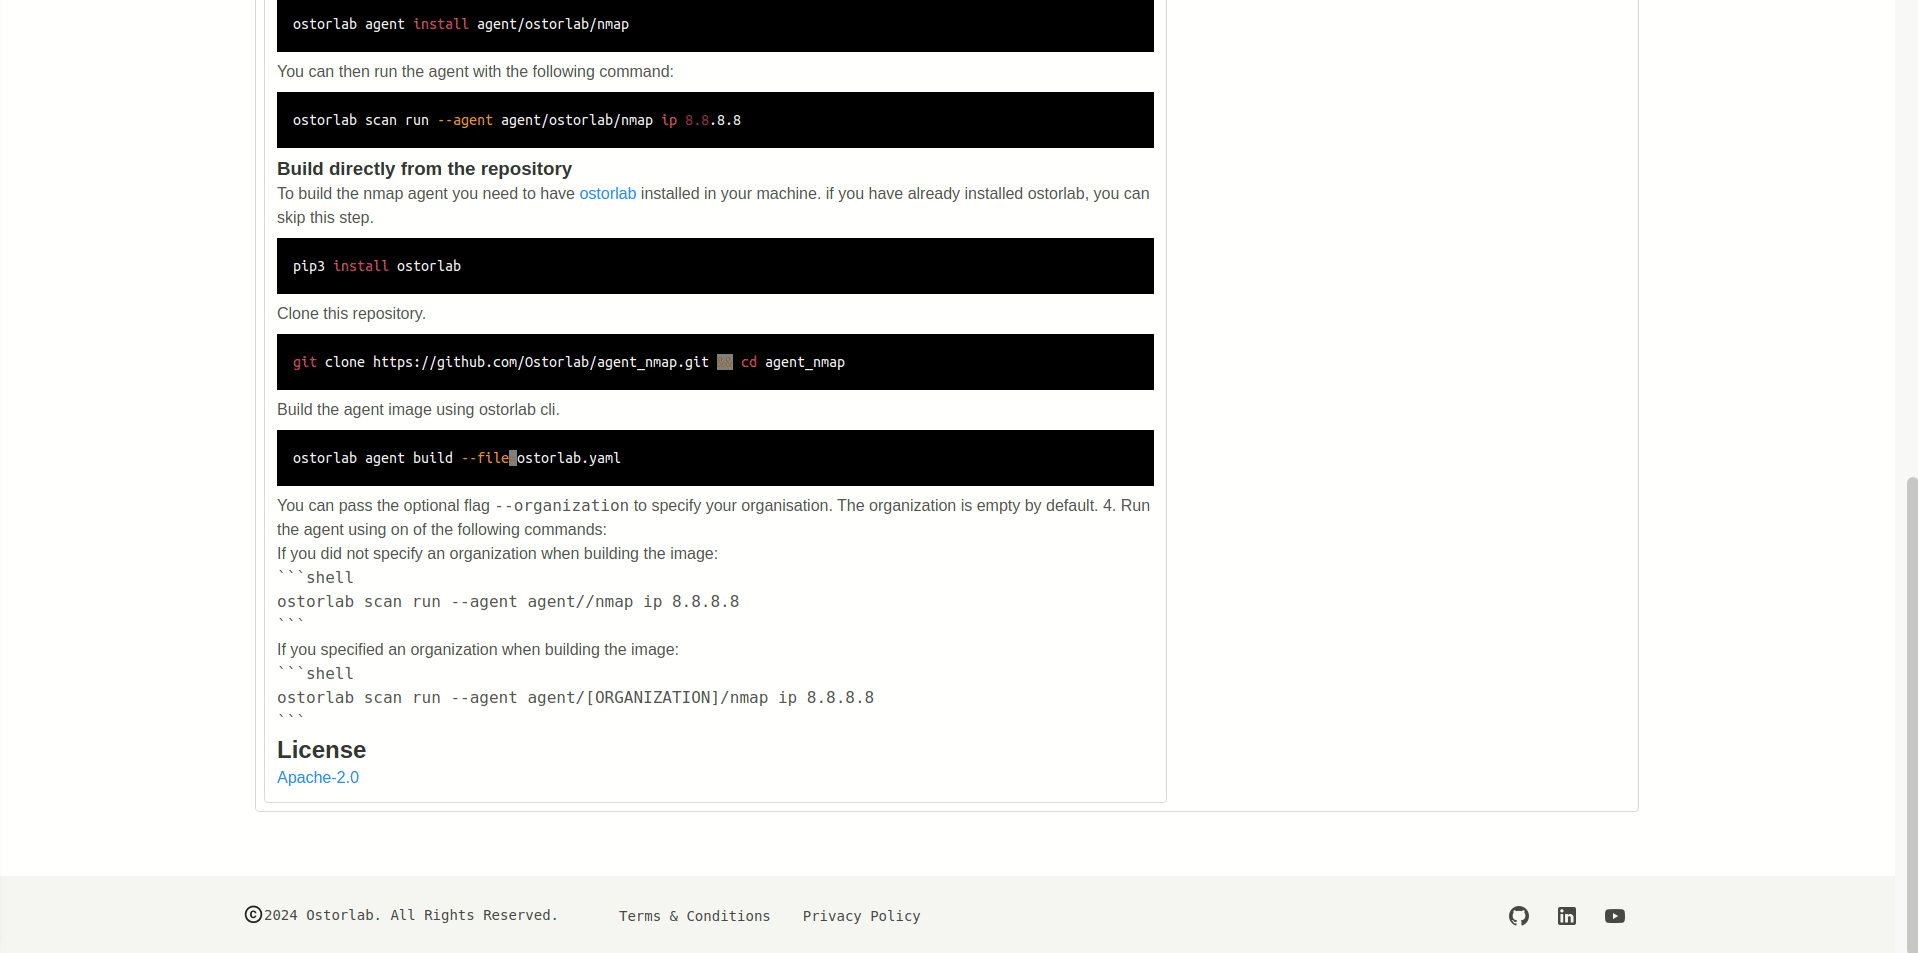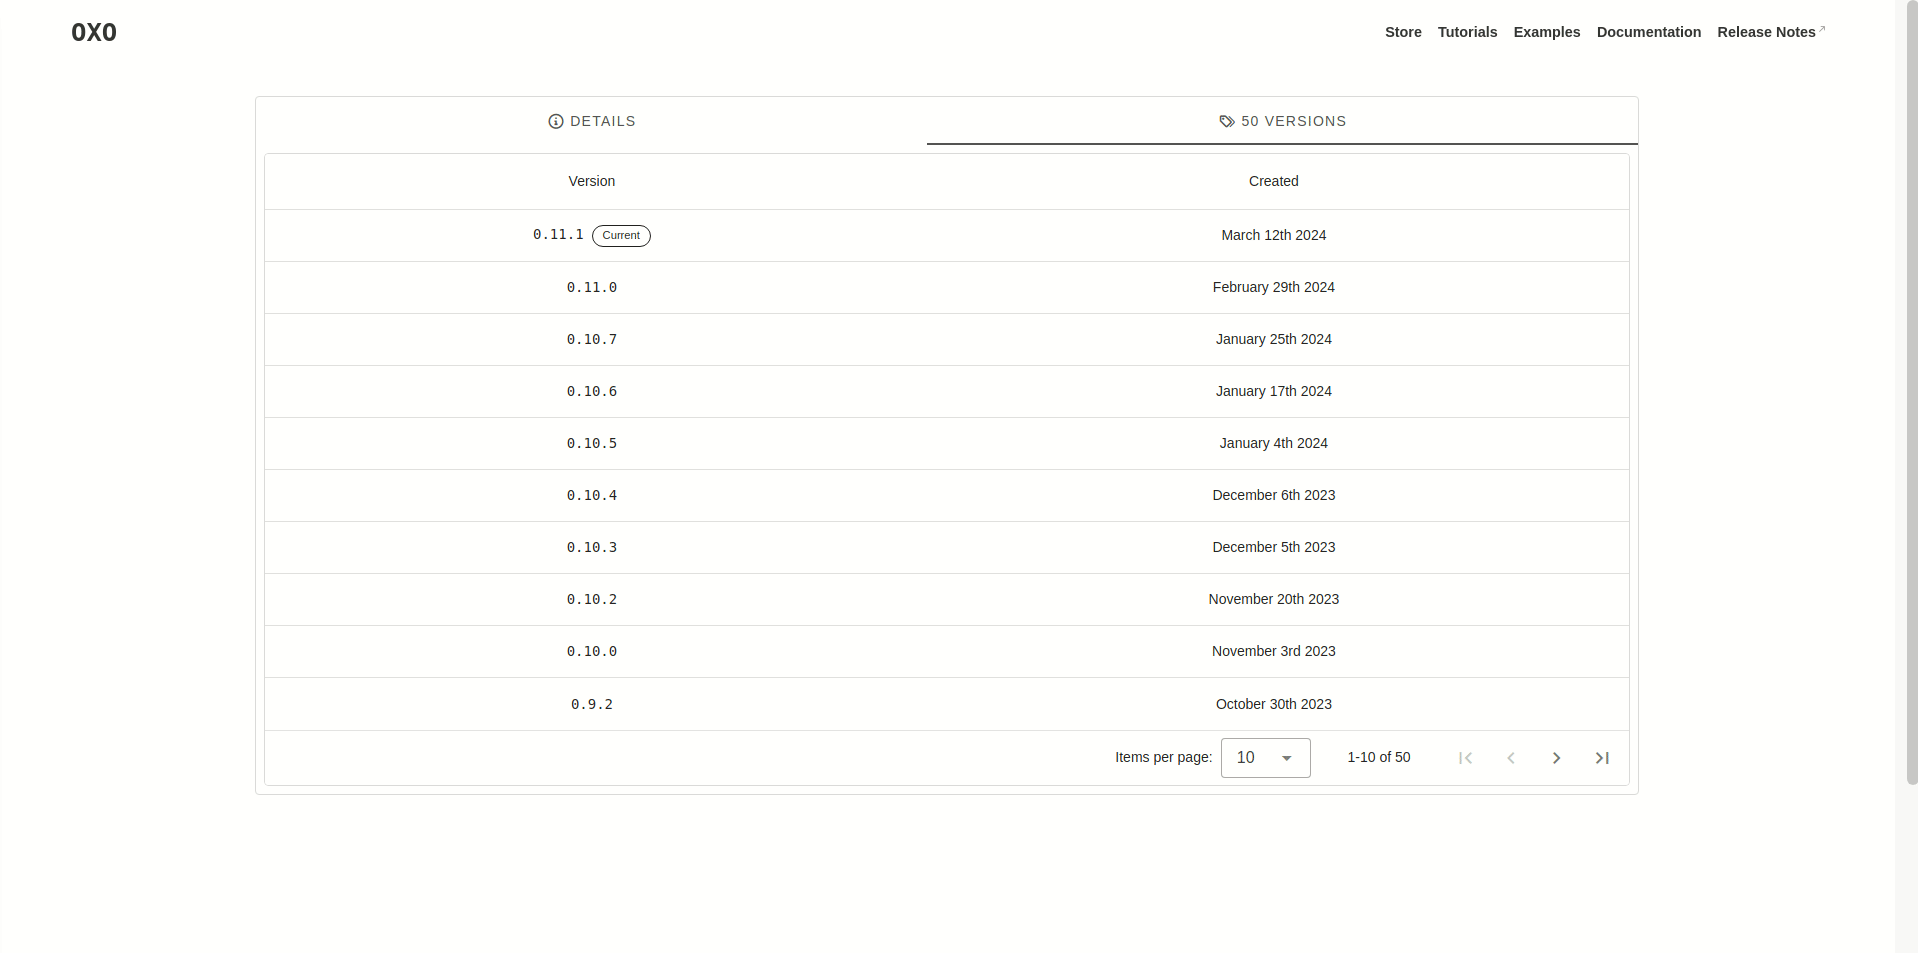 ostorlab/oxo
Modular security scanning orchestrator that combines specialized agents for vulnerability detection, reconnaissance, and fingerprinting across…
 hristiy4n/bom-view
Static web application for viewing SBOMs and performing on-demand vulnerability scanning with osv.dev. Easily deployable to GitHub/GitLab Pages.
 projectdiscovery/nuclei
Fast YAML-based vulnerability scanner with template-driven detection engine for automated security testing across web apps, APIs, networks, DNS, and…
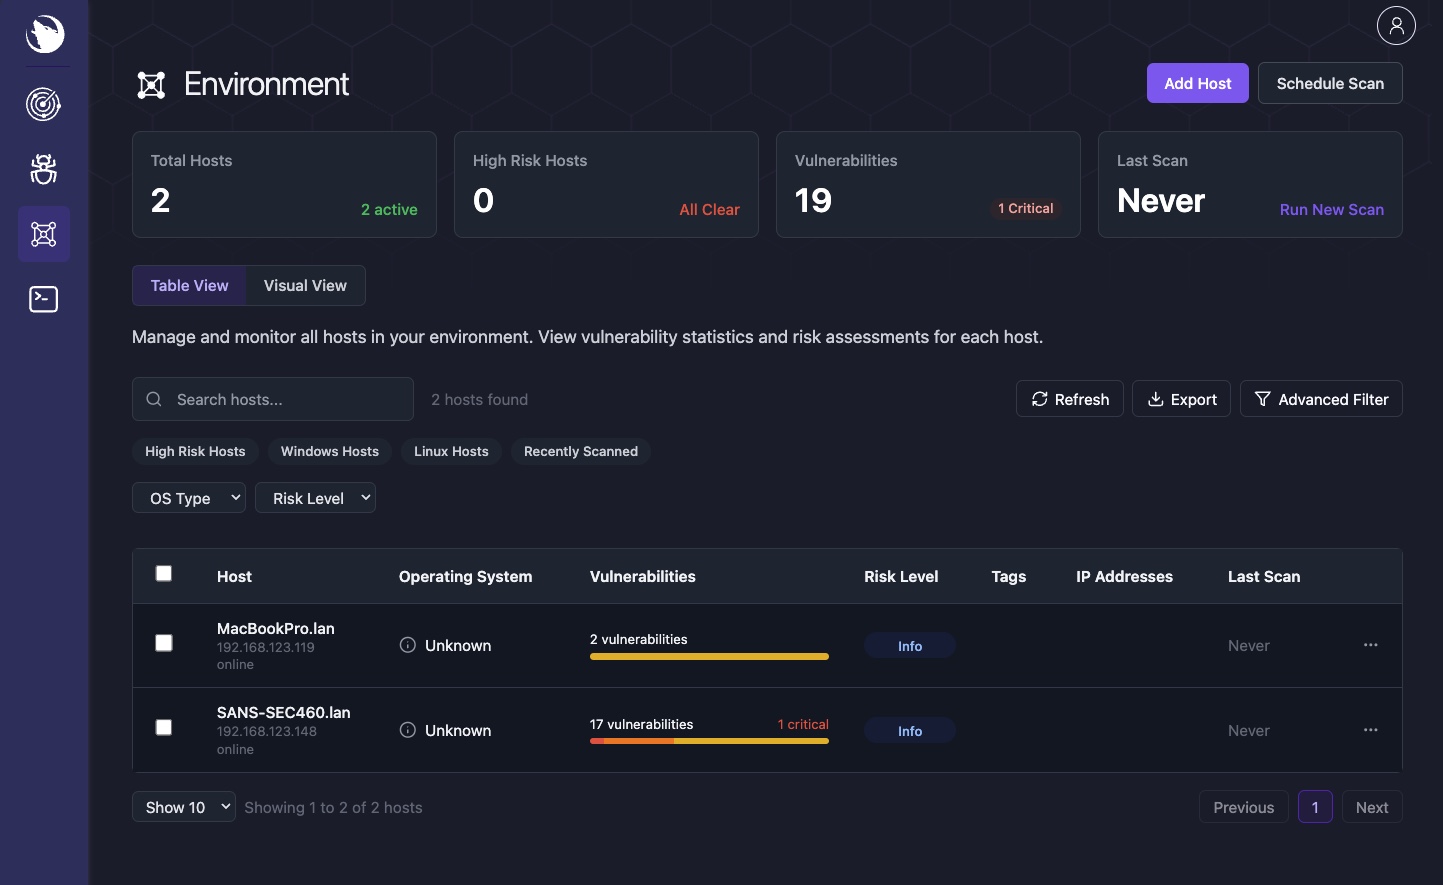 siriusscan/sirius
Open-source vulnerability scanner with automated network discovery, CVE-based detection, CVSS scoring, risk dashboards, remote agents via gRPC, and a…
 m14r41/scan4secrets
Find credentials and secret with 170+ rules covering across source code, Web URL, and CI/CD, verifies them against vendor APIs, and generates SARIF,…
 adimahluf/rapidwebrecon
A high-performance automation tool designed to bridge the gap between technical web reconnaissance and executive reporting. Developed by **Adi…
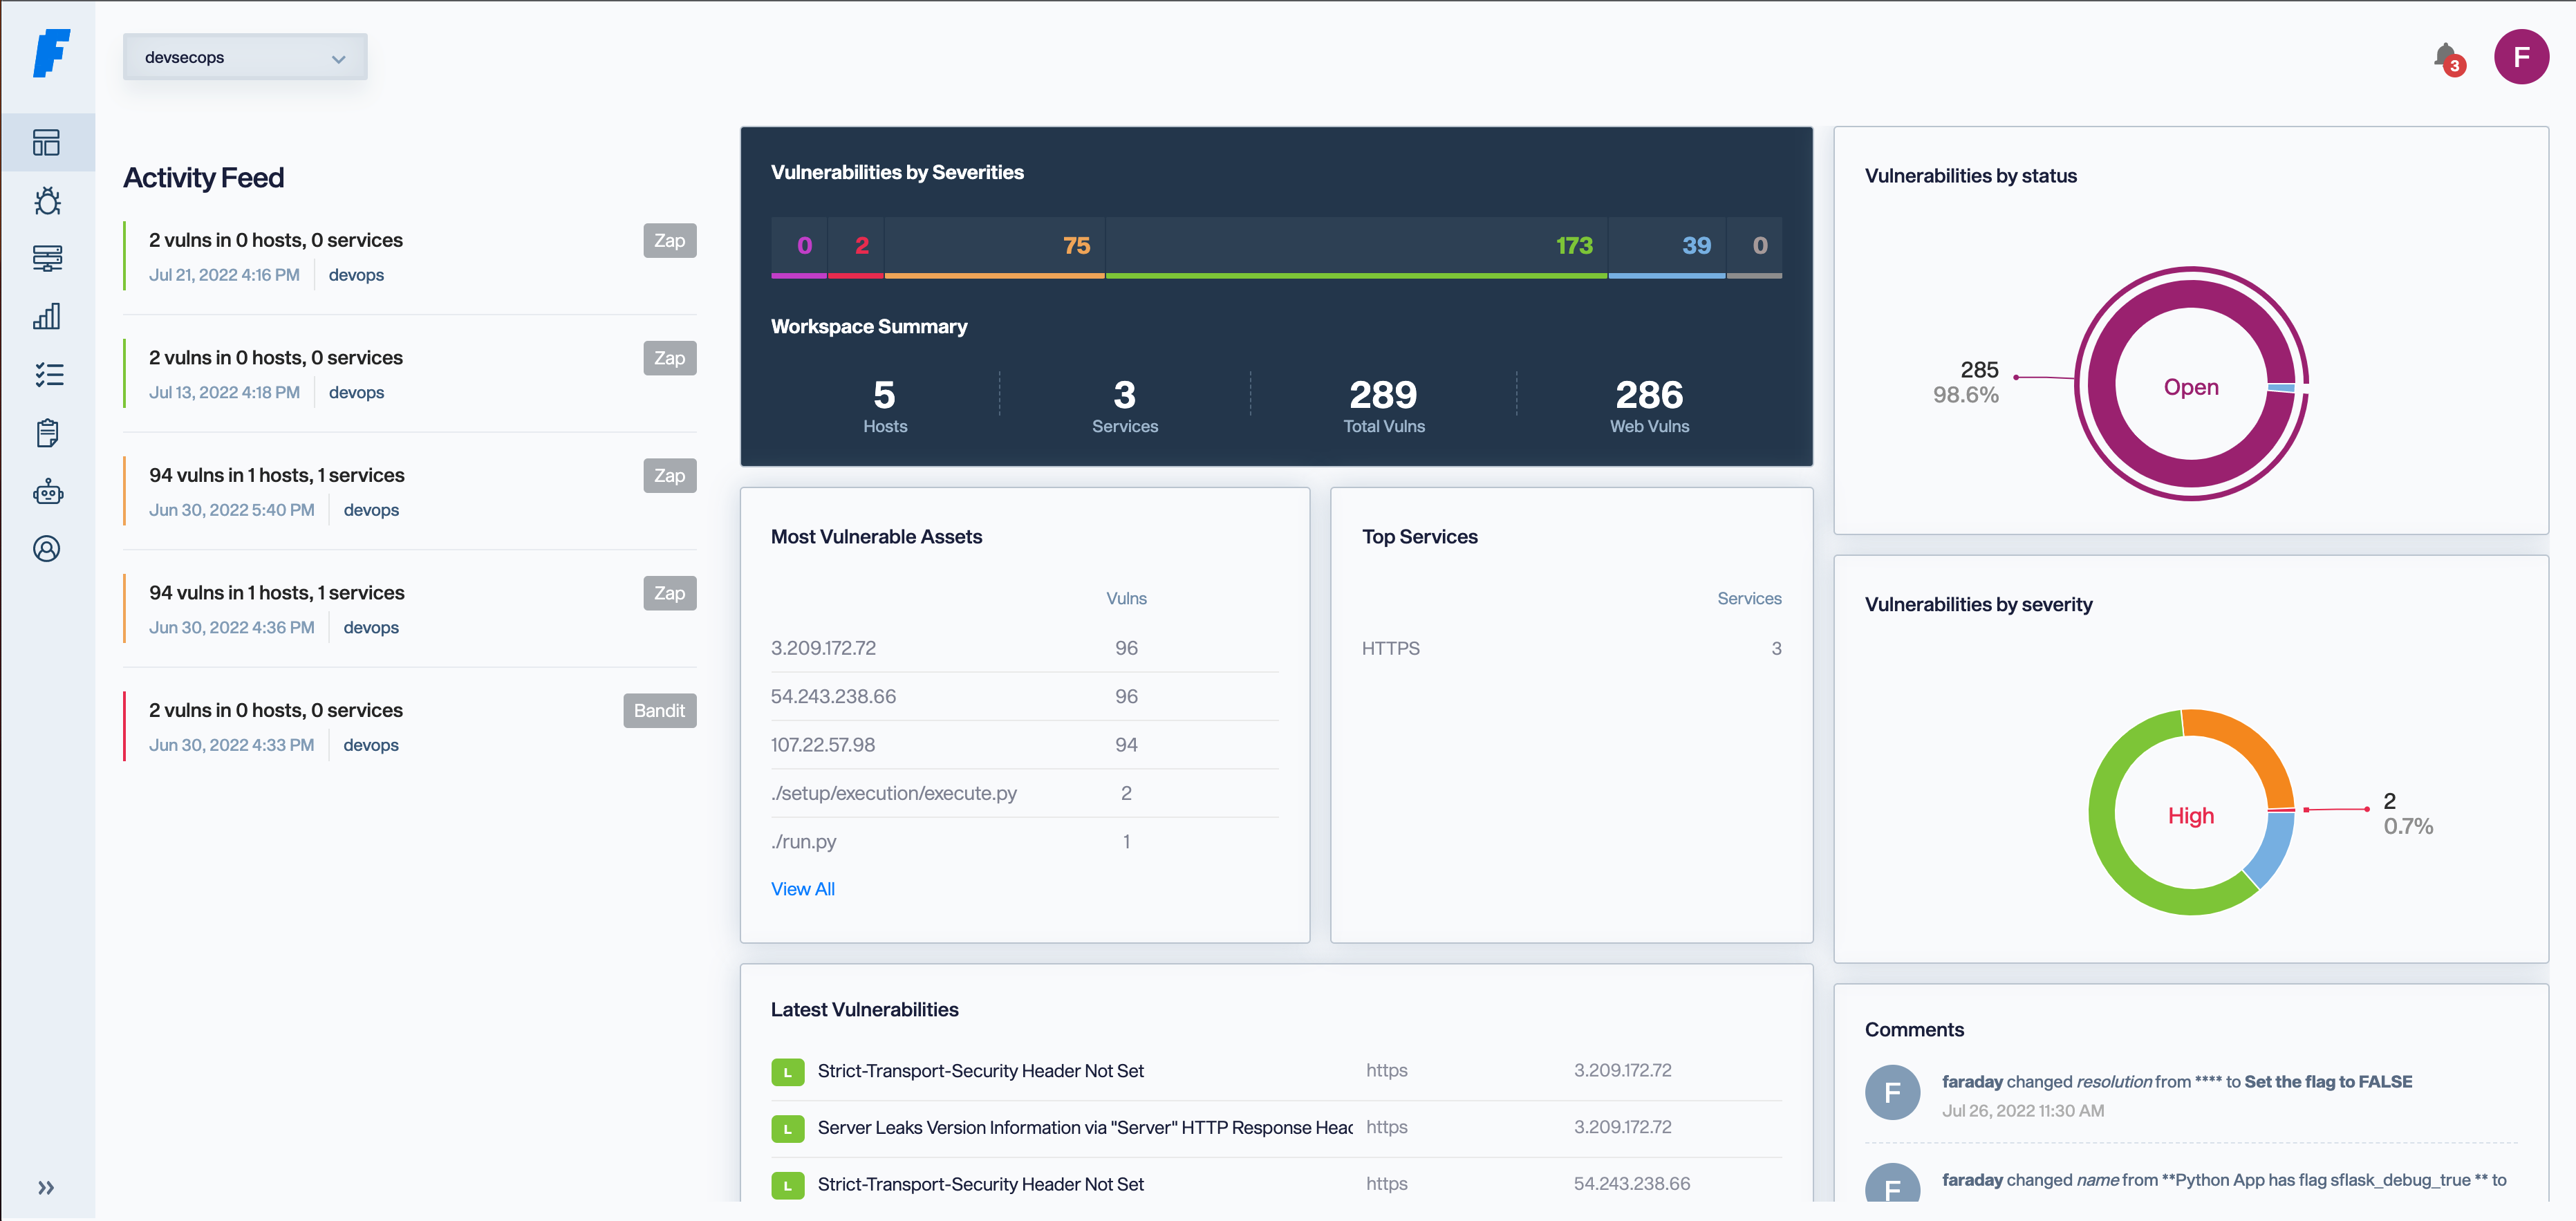 infobyte/faraday
Open-source and AI-powered cybersecurity tools for offensive security, vulnerability management, and autonomous pentesting. Built by hackers in Latin…
 hasecuritysolutions/vulnwhisperer
Create actionable data from your Vulnerability Scans
 projectdiscovery/nuclei-action
Vulnerability Scan with Nuclei
 coreruleset/ftw
YAML-driven framework for testing Web Application Firewall (WAF) rules using OWASP Core Rule Set baselines. Automates regression detection and…
 nxgn-kd01/react2shell-scanner
Detect CVE-2025-55182 (React2Shell) RCE vulnerability in React Server Components. Fast, accurate scanner with zero false positives.
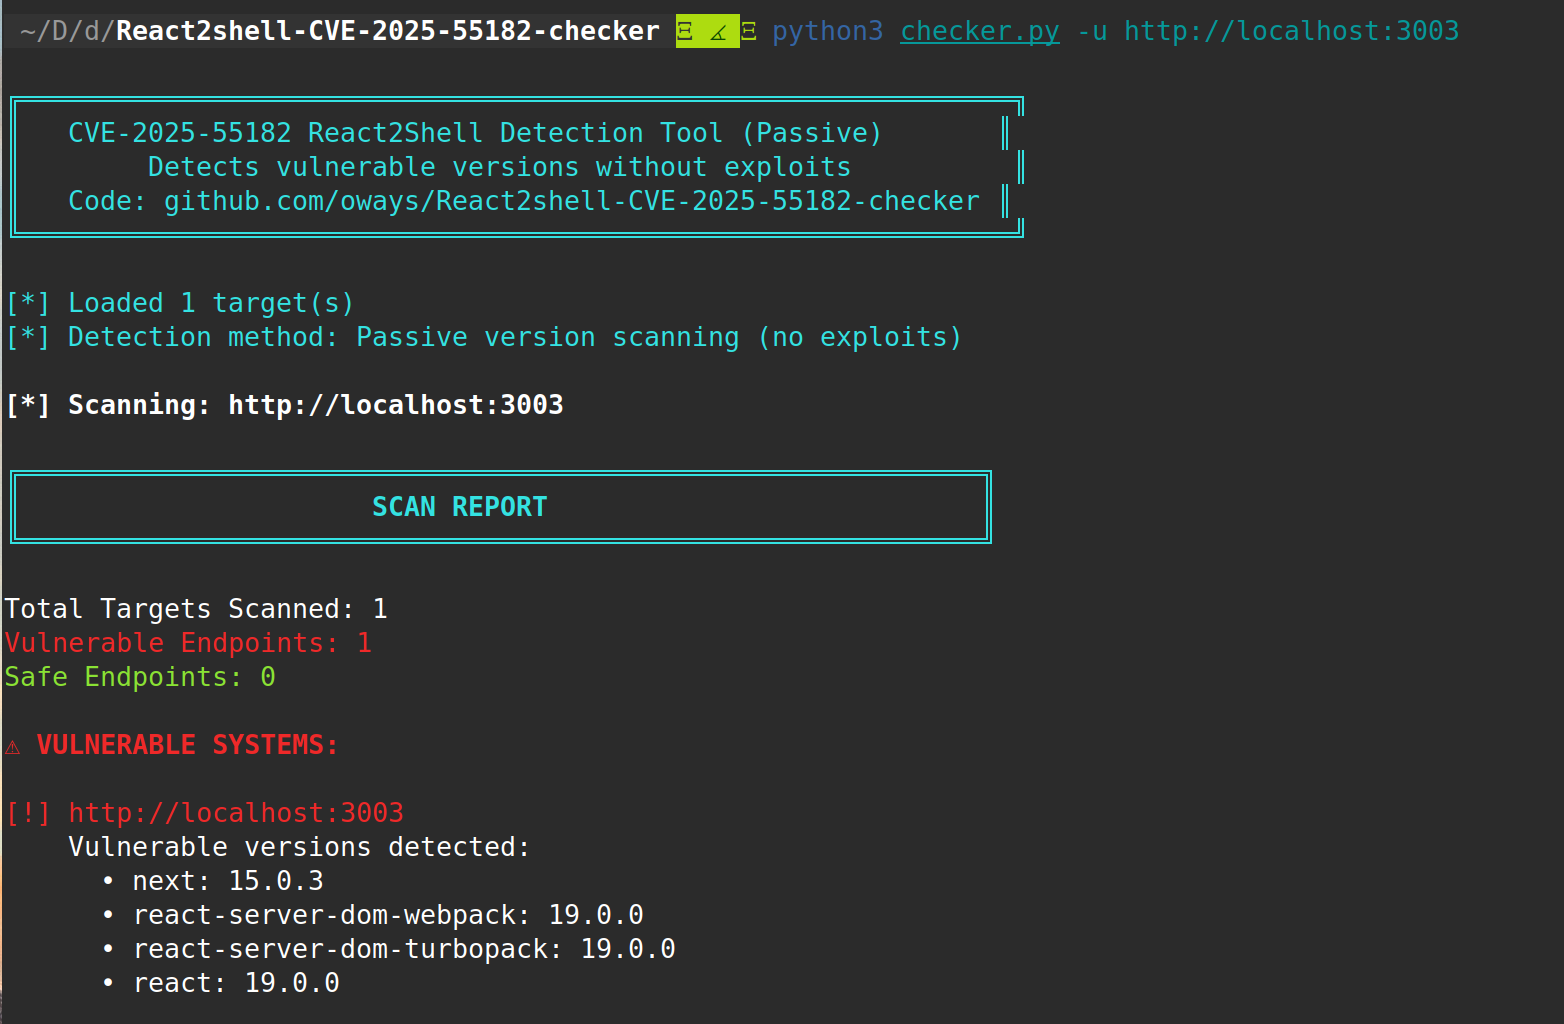 oways/react2shell-cve-2025-55182-checker
Passive CVE-2025-55182 detection tool for vulnerable React Server Components. Scans package.json, JavaScript bundles, HTTP headers, and API endpoints…
 shoucheng3/jenkinsci__workflow-multibranch-plugin_cve-2022-25175_706-vd43c65dec013
Exploit for CVE-2022-25175 targeting Jenkins Pipeline: Multibranch plugin, enabling automated exploitation of a specific vulnerability in CI/CD…
 heroku/heroku-cve-2013-0269
Inspect all of your Heroku apps for vulnerable versions of the JSON gem