

cplt
 navikt/cplt
Sandbox for AI coding agents. Runs Copilot CLI, Claude Code, OpenCode, Gemini CLI, Antigravity, Pi, goose or a plain shell inside a kernel-level…
ai-securitycommand-and-controlconfiguration-auditing+7
124
navikt/cpltSandbox for AI coding agents. Runs Copilot CLI, Claude Code, OpenCode, Gemini CLI, Antigravity, Pi, goose or a plain shell inside a kernel-level…
 trufflesecurity/trufflehog
Find, verify, and analyze leaked credentials
 awslabs/git-secrets
Prevents you from committing secrets and credentials into git repositories
 gitleaks/gitleaks
Fast, open-source static analysis tool for detecting hardcoded secrets like passwords, API keys, and tokens in git repositories, files, and stdin…
 hashicorp/vault
A tool for secrets management, encryption as a service, and privileged access management
 dionach/reposcanner
Python script to scan Git repos for interesting strings
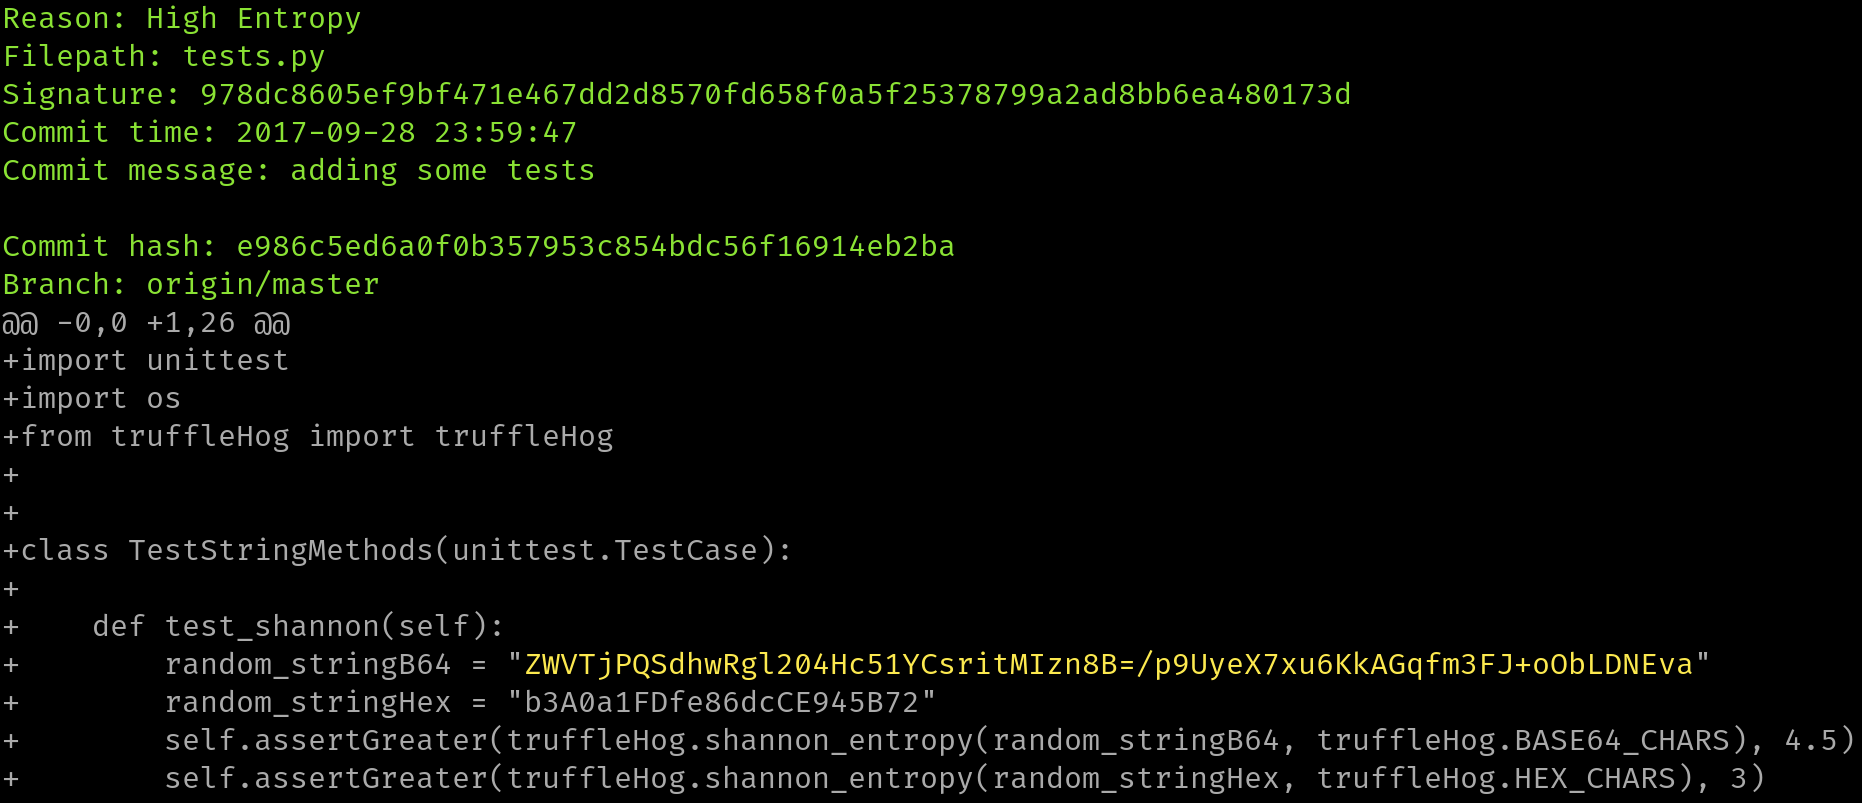 godaddy/tartufo
Searches through git repositories for high entropy strings and secrets, digging deep into commit history
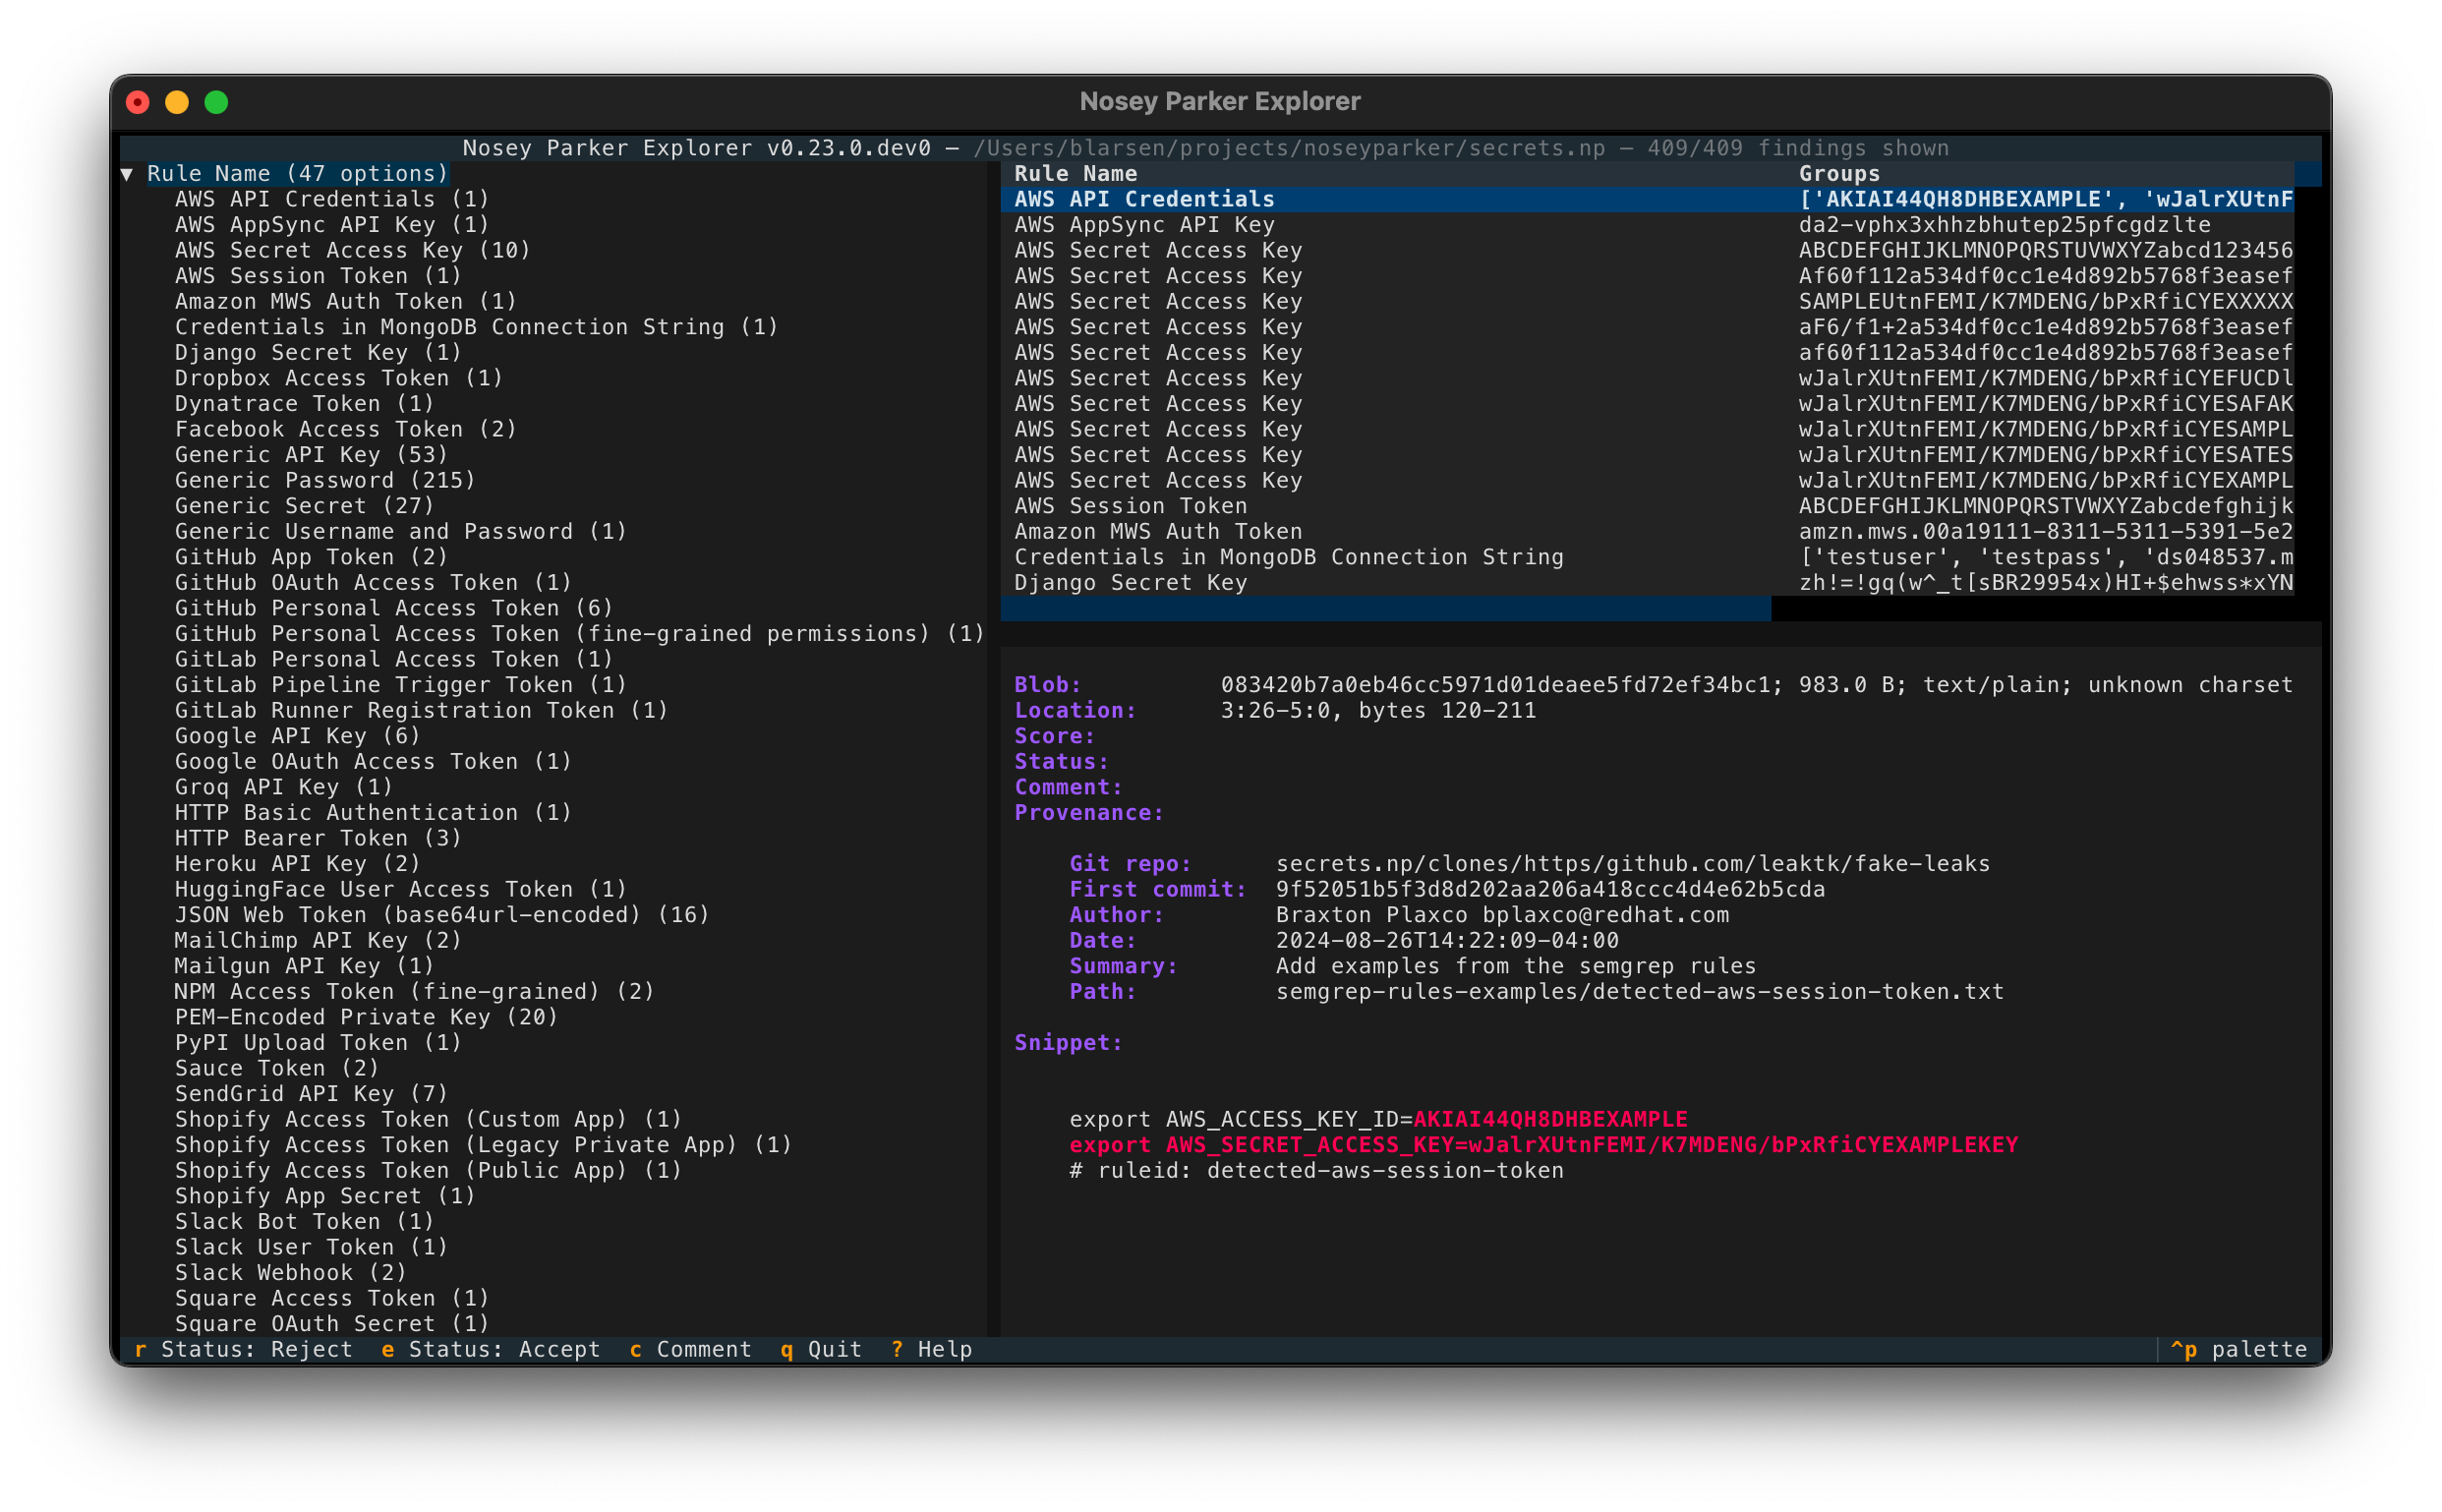 praetorian-inc/noseyparker
Nosey Parker is a command-line tool that finds secrets and sensitive information in textual data and Git history.
 praetorian-inc/titus
High-performance secrets scanner. CLI, Go library, Burp Suite extension, and Chrome extension. 487 detection rules with live credential validation.
 presidentbeef/brakeman
A static analysis security vulnerability scanner for Ruby on Rails applications
 thoughtworks/talisman
Git hook-based secret scanner that detects tokens, passwords, and private keys in outgoing changesets, preventing sensitive data from being committed…
 shoucheng3/spring-cloud__spring-cloud-config_cve-2020-5405_2-1-6-release
Centralized configuration server for distributed systems with HTTP API, encryption/decryption of properties, and support for Git, Vault, JDBC, and…
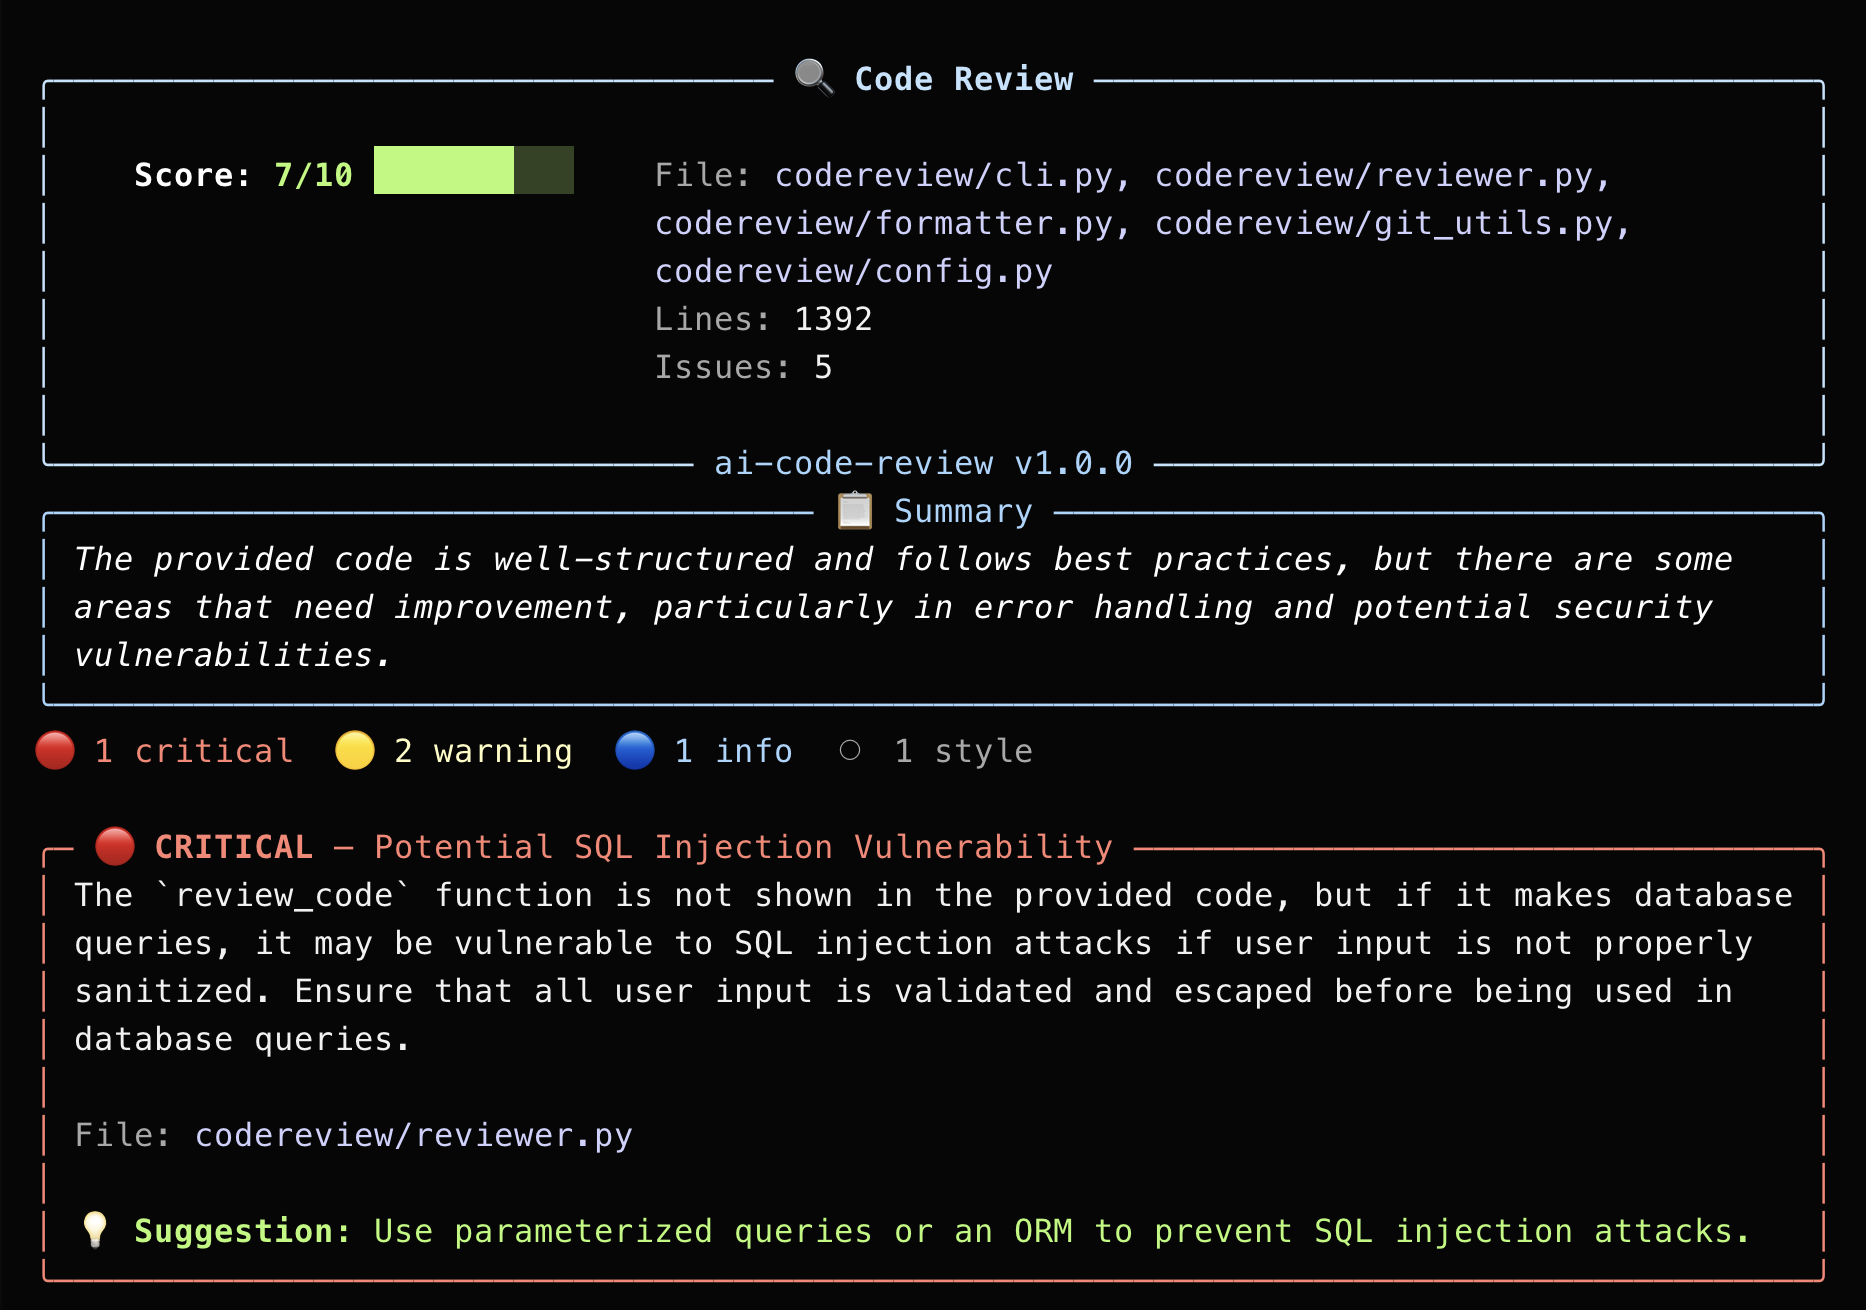 jaydendancer12/ai-code-review
AI-powered CLI tool that reviews code for security vulnerabilities, bugs, and anti-patterns using LLMs. Supports local and cloud providers, git…
 dracondev/dracon-utilities
Invisible infrastructure for Dracon developer workspaces: git sync, system guard, and warden encryption utilities.
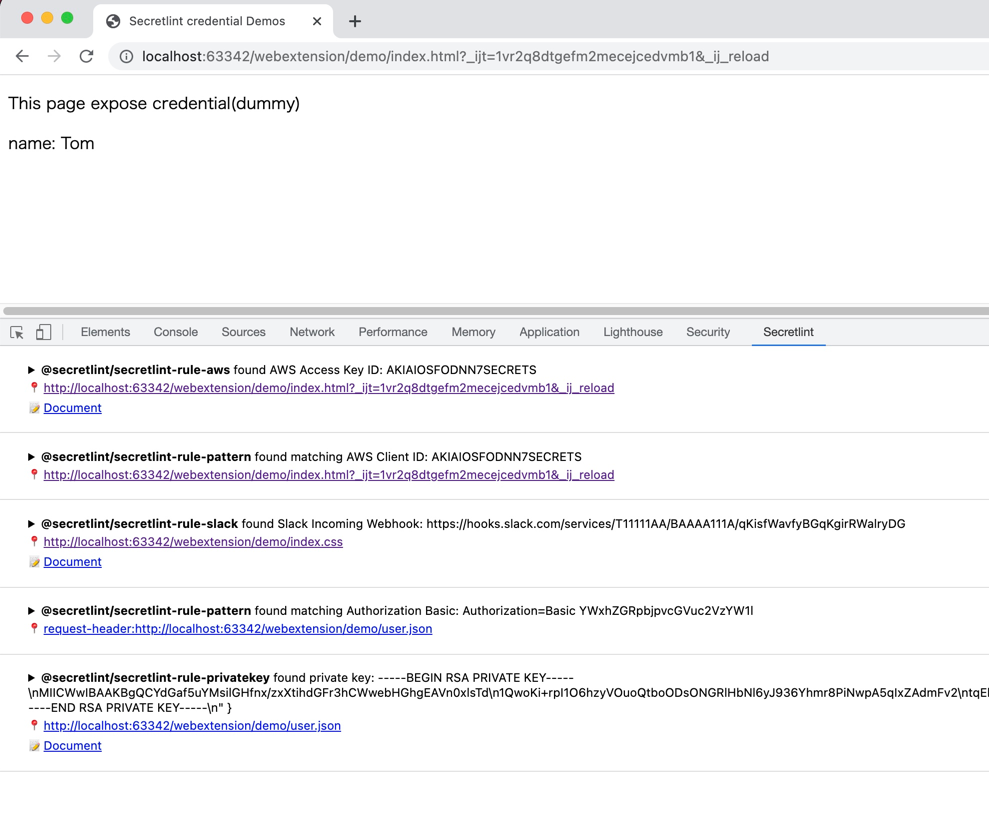 secretlint/secretlint
Pluggable linting tool to prevent committing credential.
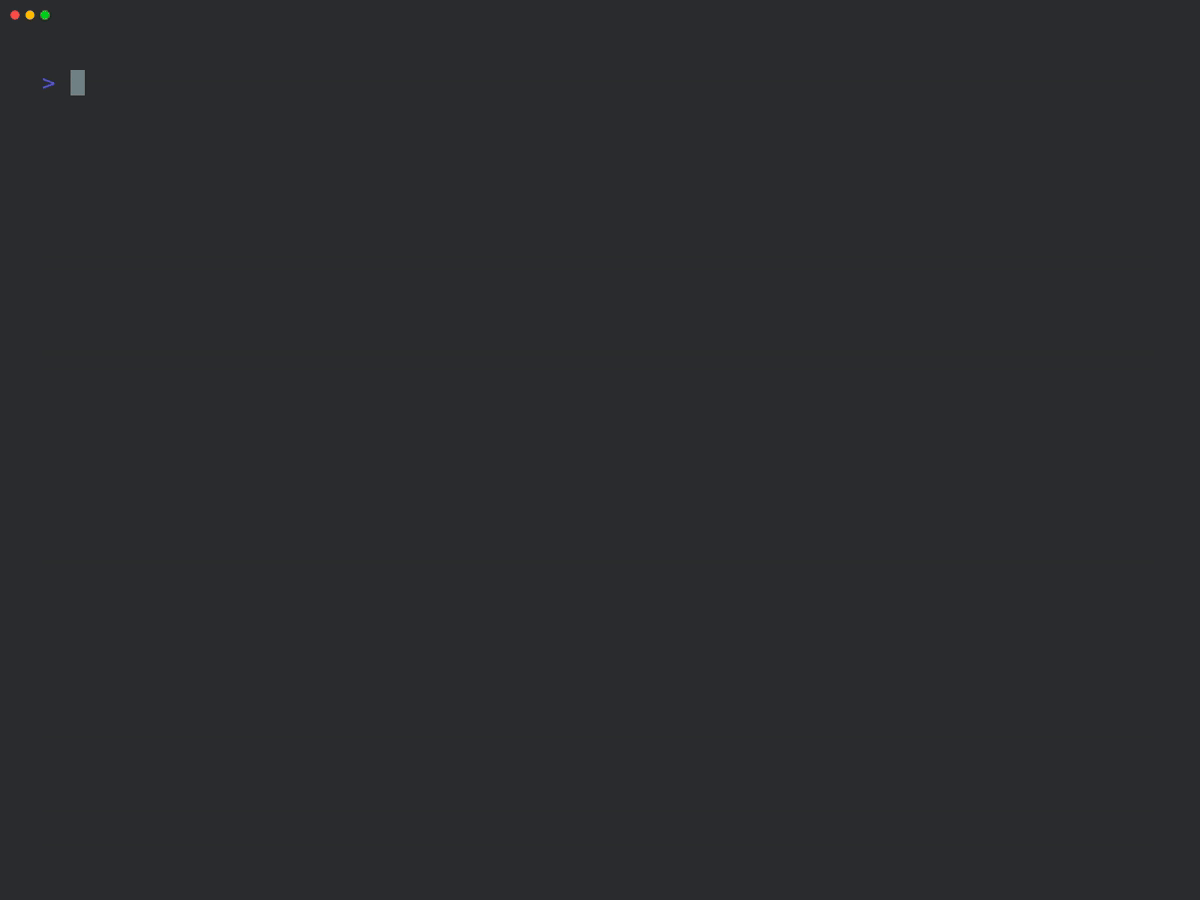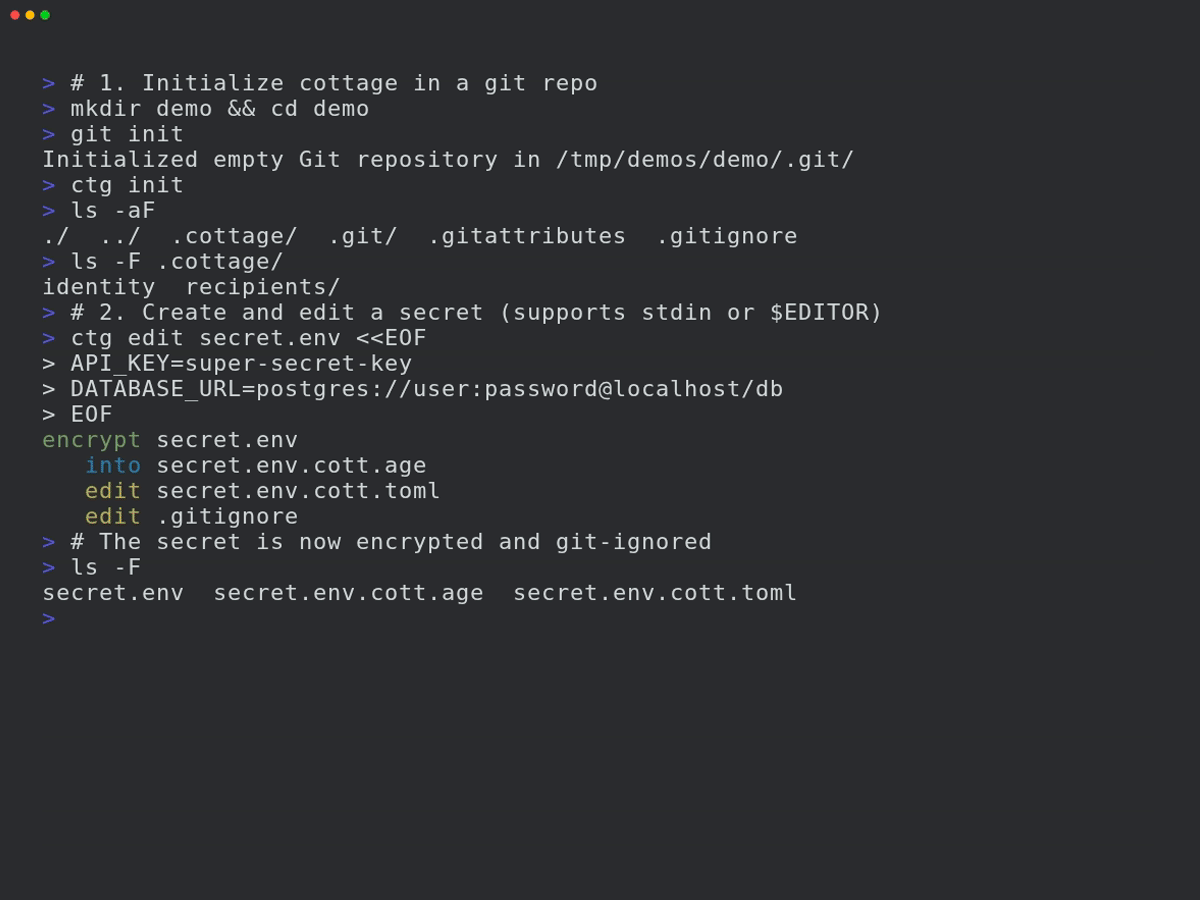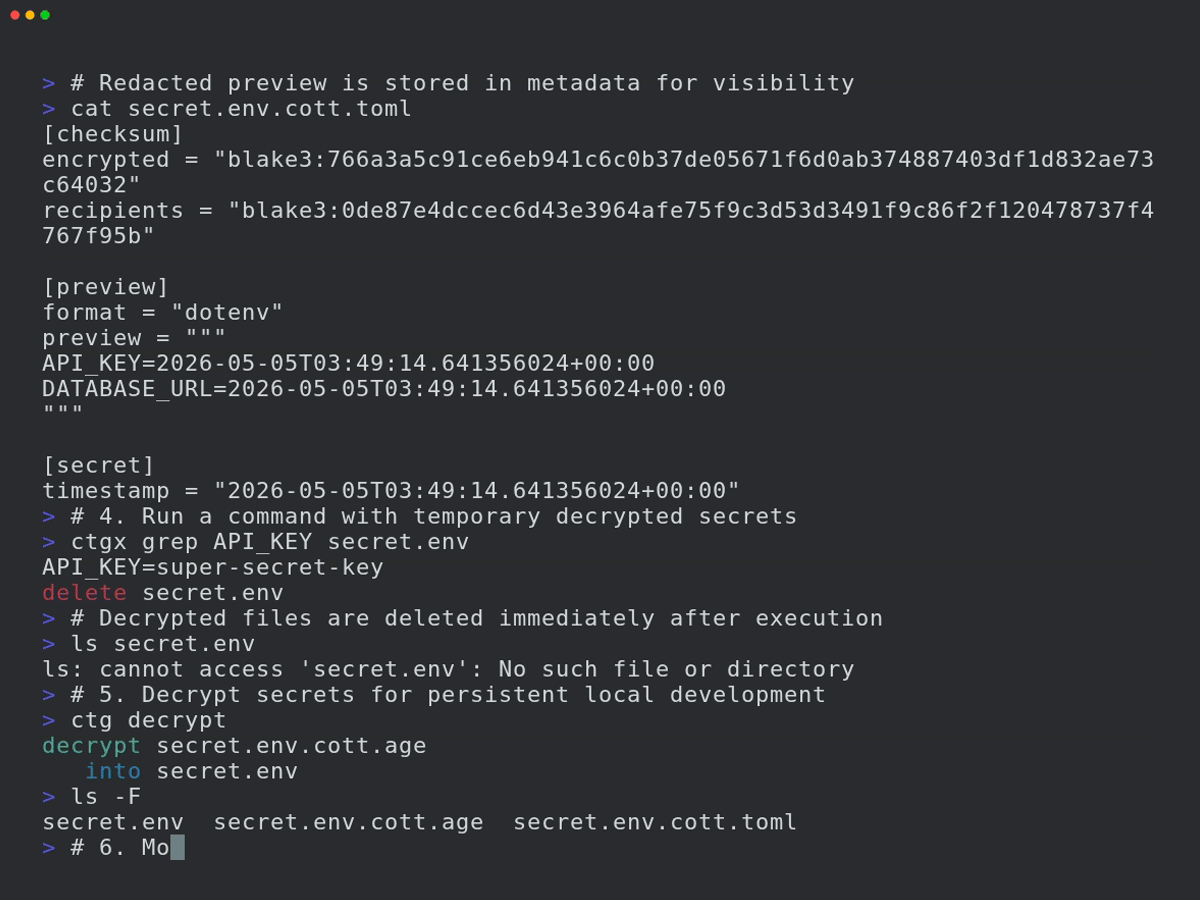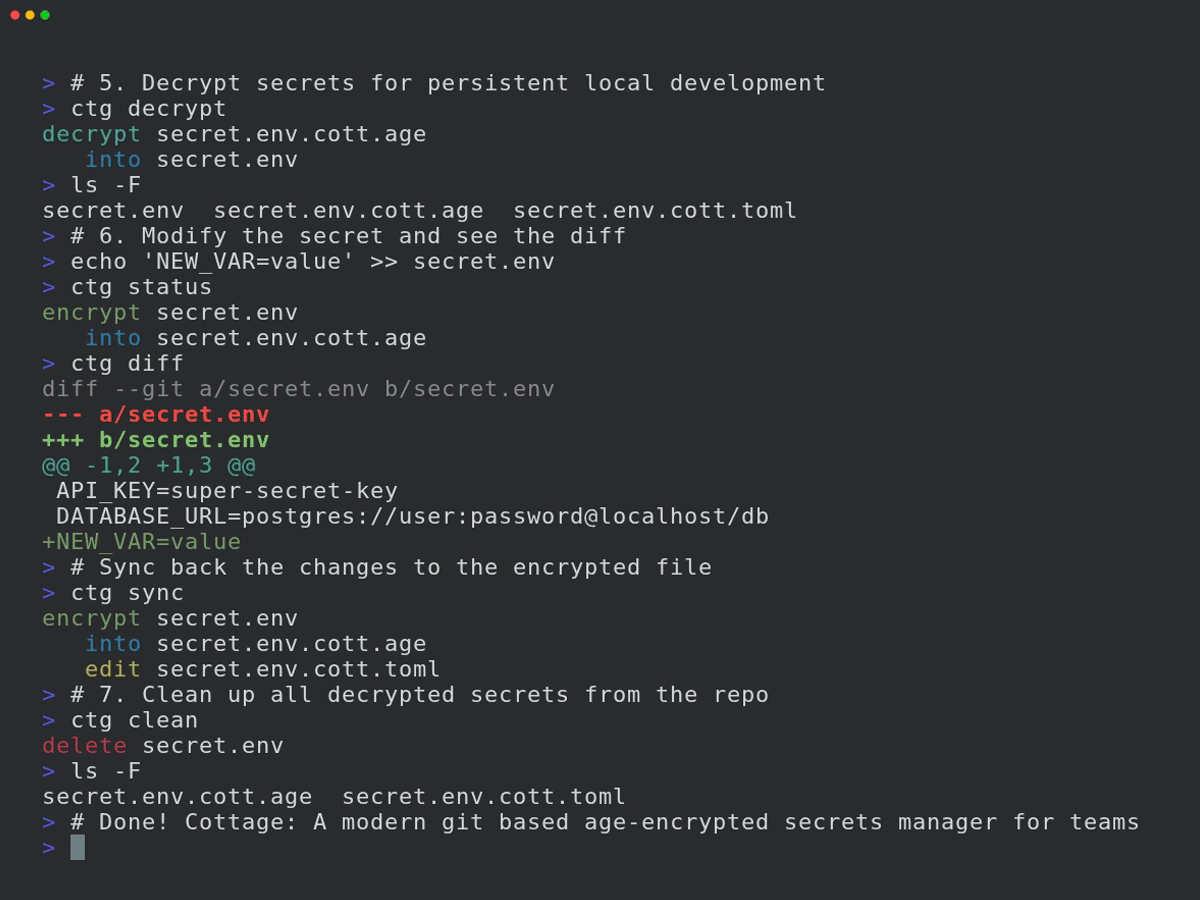 sayanarijit/cottage
A modern git based age-encrypted secrets manager for teams.
 pantheon-security/medusa
AI-first security scanner. NEW in v2026.7: Claude Code compromise detection — vet .claude/ hooks, permissions & skills before you clone — plus an…
 shubhamshubhankar/autosource
Automated static code analysis framework integrated with SonarQube for early vulnerability detection in source code by scanning Git repositories…