Skip to content
KitploitKITPLOIT
ToolsBlog
Submit
ToolsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
108 results
android-kernel-exploitation-lab preview

android-kernel-exploitation-lab

GitHub0xbinder/android-kernel-exploitation-lab

This lab guides you through setting up an environment to explore CVE-2019-2215, a critical Android kernel vulnerability in the binder subsystem.

android-securitybinary-exploitationdebuggers+6
45
1 year ago
renef-skills preview

renef-skills

GitHubvichhka-git/renef-skills

Agent Skill for operating renef.io — Android ARM64 dynamic instrumentation: hook native/Java, patch memory, trace syscalls, bypass SSL pinning/root…

android-securitybinary-analysisctf+9
153 months ago
smali preview
Archived

smali

GitHubjesusfreke/smali

smali/baksmali

android-securitybinary-analysisdebuggers+3
6.6k2 years ago
jdwp-shellifier preview

jdwp-shellifier

GitHubioactive/jdwp-shellifier

Exploitation script for exposed Java Debug Wire Protocol (JDWP) services, enabling pentesters to inject Java code and execute arbitrary OS commands…

debuggersexploitationmisconfiguration+1
9169 years ago
nCPU preview

nCPU

GitHubrobertcprice/ncpu

Research runtime for differentiable neural computers, GPU-based CPU emulation, and program synthesis. Features neural ALU, constant-time crypto, JEPA…

ai-securitybinary-analysiscryptography+8
6582 months ago
pike-agent preview

pike-agent

GitHubsynacktiv/pike-agent

Experimental Linux strace LLM agent

ai-securitydebuggersdynamic-analysis-sandboxing+5
214 months ago
lupo preview

lupo

GitHubmalienist/lupo

WinDbg plugin for automated malware dynamic analysis and IOC extraction. Executes within the debugger to collect predefined indicators and writes…

debuggersdynamic-analysis-sandboxingforensics+2
1024 years ago
CVE-2022-0853 preview

CVE-2022-0853

GitHubbytehackr/cve-2022-0853

Demonstrates a memory leak in JBoss client when using UserTransaction repeatedly, with a PoC and analysis for CVE-2022-0853.

code-analysisdebuggersexploitation+2
94 years ago
linux-4.1.15_CVE-2022-45934 preview

linux-4.1.15_CVE-2022-45934

GitHubsatheesh575555/linux-4.1.15_cve-2022-45934

Linux kernel 4.1.15 source code with a focus on CVE-2022-45934, providing a reference for vulnerability analysis and exploitation research.

binary-analysisdebuggersexploitation+2
3 years ago
CFB preview

CFB

GitHubhugsy/cfb

ProcMon-style IRP monitor for Windows drivers. Captures and logs I/O Request Packets via a kernel driver and user-land broker, outputting JSON for…

debuggersfuzzingvulnerability-analysis
3372 years ago
ida_kernelcache preview

ida_kernelcache

GitHubbazad/ida_kernelcache

An IDA Toolkit for analyzing iOS kernelcaches.

binary-analysisdebuggersembedded-systems-security+6
3057 years ago
ida_kernelcache preview

ida_kernelcache

GitHubcellebrite-labs/ida_kernelcache

An IDA Toolkit for analyzing iOS kernelcaches.

binary-analysisdebuggersexploitation+5
1511 month ago
sigwire preview

sigwire

GitHubyeet-src/sigwire

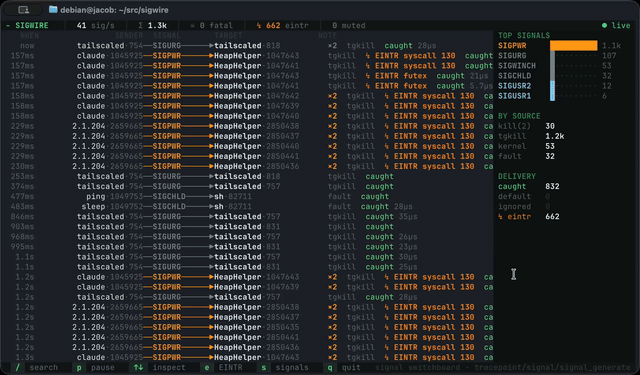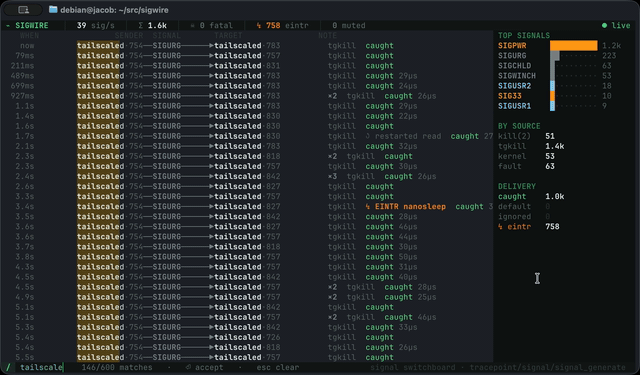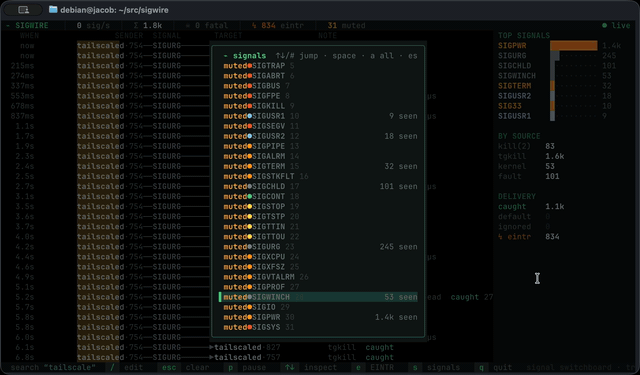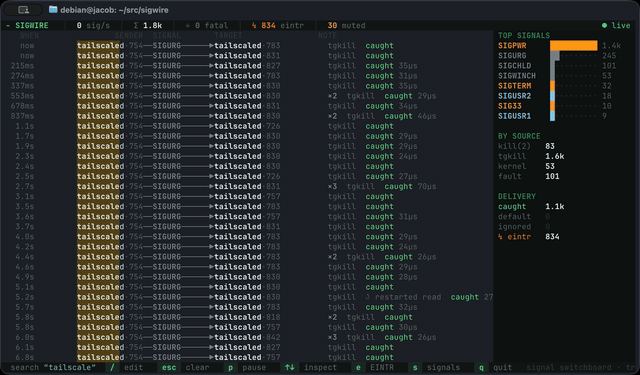
Live kernel signal observability tool using eBPF tracepoints to stream every signal raised on a Linux host, showing sender, target, disposition,…

debuggersdynamic-analysis-sandboxingforensics+2
1611 month ago
CAPE preview

CAPE

GitHubctxis/cape

Malware Configuration And Payload Extraction

debuggersdynamic-analysis-sandboxingmalware-analysis+2
7605 years ago
DriverBuddyReloaded preview

DriverBuddyReloaded

GitHubvoidsec/driverbuddyreloaded

Driver Buddy Reloaded is an IDA Pro Python plugin that helps automate some tedious Windows Kernel Drivers reverse engineering tasks

binary-analysisdebuggersreverse-engineering+2
4432 months ago
Freeloader preview

Freeloader

GitHubauthrequest/freeloader

Plex Unlocker

binary-analysiscontainer-securitydebuggers+8
952 months ago
regenerator2000 preview

regenerator2000

GitHubricardoquesada/regenerator2000

An interactive disassembler for the CPU 6502, focused on Commodore 8-bit computers. Features a TUI with modern features like x-ref, undo/redo, flow…

binary-analysisdebuggerseducation+3
16424 days ago
snoop preview

snoop

GitHubpandaadir05/snoop

A modern syscall tracer built on eBPF. Think strace, but with a real TUI, smart filters, TLS decryption, and output that's actually readable.

binary-analysisdebuggersdynamic-analysis-sandboxing+7
2245 months ago
Previous123456Next