

frida
 frida/frida
Main repo for hosting release binaries
android-securitybinary-analysiscode-analysis+9
frida/fridaMain repo for hosting release binaries
 nationalsecurityagency/ghidra
Ghidra is a software reverse engineering (SRE) framework
 radareorg/radare2
UNIX-like reverse engineering framework and command-line toolset
 momo5502/sogen
🪅 Windows & Linux userspace emulator
 mitmproxy/mitmproxy
An interactive TLS-capable intercepting HTTP proxy for penetration testers and software developers.

 dynamorio/dynamorio
Runtime instrumentation framework for building dynamic analysis tools: tracing, profiling, code coverage, memory debugging, fuzzing, and disassembly…
 mozilla/firefox-devtools-mcp
Model Context Protocol server for Firefox DevTools - enables AI assistants to inspect and control Firefox browser through WebDriver BiDi
 lief-project/lief
Cross-platform library to parse, modify, and abstract ELF, PE, and MachO executable formats. Supports C++, Python, and Rust APIs with disassembler,…
 dnspyex/dnspy
Unofficial revival of the well known .NET debugger and assembly editor, dnSpy
 ibotpeaches/apktool
A tool for reverse engineering Android apk files
 nowsecure/r2frida
Radare2 and Frida better together.
 aethervm/aethervm
LLVM-native binary analysis and emulation platform that lifts AArch64 and x86_64 machine code to LLVM IR for instrumentation, deobfuscation, and…
 crissyfield/super-trouper
MCP server exposing Frida instrumentation as tools for coding agents to connect to devices, inspect processes, manage sessions, and load JavaScript…
 openbba0/bba
Android app-cloning sandbox with a Frida-style CLI that spawns or attaches to cloned apps and injects QuickJS scripts using Gum Interceptor and…
 skylot/jadx
Command-line and GUI tool for decompiling Android Dex and APK files into readable Java source code, with resource decoding, deobfuscation, and Smali…
 xv4l3x/hermit
Inspects, decompiles and structurally patches Hermes bytecode (HBC) from React Native apps, with a GDB-style REPL, CFG, decompiler and re-serializing…
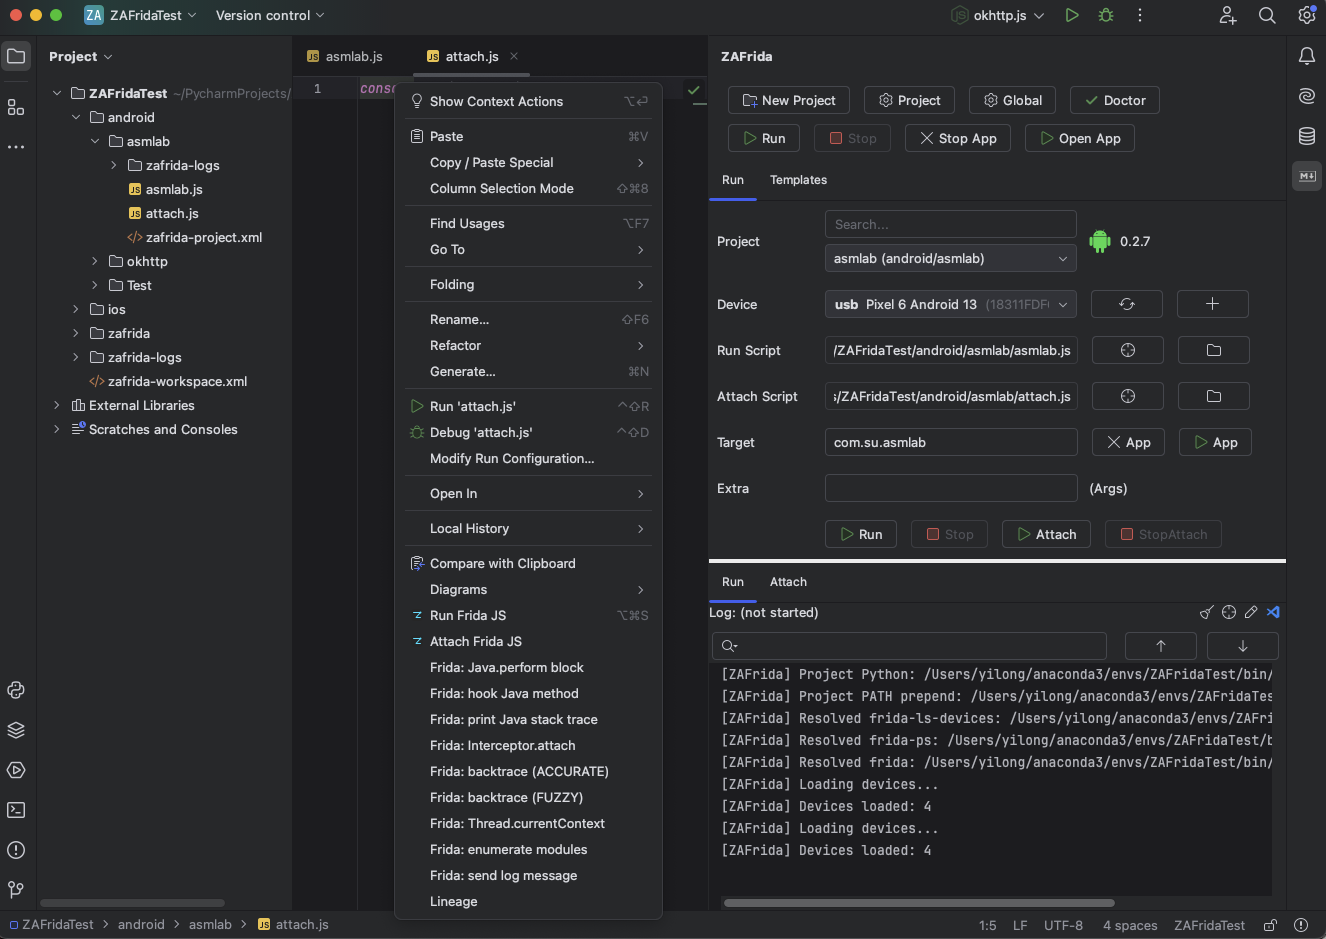 yilongmd/zafrida-ui
A Frida UI tool window inside PyCharm / JetBrains IDEs.