
GoTEE-example
 usbarmory/gotee-example
GoTEE - example application
debuggersembedded-systems-securityhardware-security+2
usbarmory/gotee-exampleGoTEE - example application
 revng/revng
Open source binary analysis framework and decompiler built on LLVM and QEMU, lifting binaries to a readable intermediate representation for reverse…
 clearbluejar/pyghidra-mcp
Python Command-Line Ghidra MCP
 vaibhavpandeyvpz/apkstudio
Open-source, cross platform Qt6 based IDE for reverse-engineering Android application packages. It features a friendly IDE-like layout including code…
 epsilon537/boxlambda
FPGA based microcomputer sandbox for software and RTL experimentation
 dovughs/mora-hwbp
Hardware Breakpoint (DR0-DR7) based patch-less user-mode hooking & telemetry instrumentation engine (AMSI, WLDP & ETW PoC).
 kaandemir993/amadey-loader-multi-stage-malware-with-keylogging-clipboard-hijack-privilege-escalation-analysis
Reverse engineering Amadey Loader with x64dbg: dynamic API resolution, token privilege escalation, keylogger hooks, clipboard capture, and…
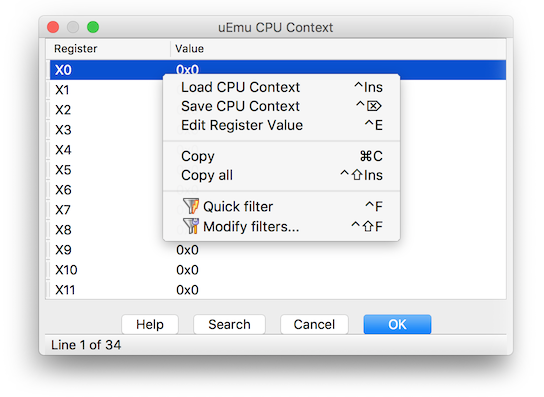 alexhude/uemu
Tiny cute emulator plugin for IDA based on unicorn.
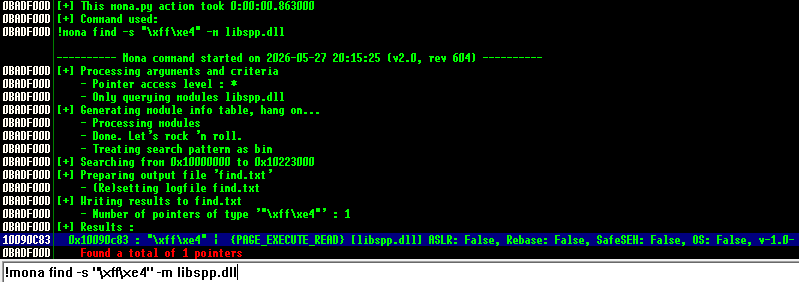 godoy-sec/cve-2017-14980
Study of a classic stack-based buffer overflow vulnerability in a controlled lab environment for educational purposes.
 liyuxuan504-byte/cve-2026-14266
7-Zip XZ Decoder Heap Buffer Overflow - Full analysis, root cause, PoC, and RCE exploitation roadmap
 benmevic/cve-2025-22457
Altay takımı haftalık sunumu için yaptığım cve-2025-22457 zafiyeti demo uygulaması
 pr0me/xtride
N-gram-based type recovery tool for binaries, recovering structures and function signatures from decompiled code with high throughput and actionable…
 umbertodellamonica/linksys-wrt54gl-exploitation
From Solder to Shell: Full Hardware Exploitation of the Linksys WRT54GL Router (CVE-2022-43973)
 colton1skees/dna
LLVM based static binary analysis framework
 asherdll/r2gopclntabparser
A radare2 script to parse the gopclntab to facilitate Reverse Engineering Go binaries.
 meckazin/chromekatz
Dump cookies and credentials directly from Chrome/Edge process memory
 themalwareguardian/cve-2018-18912
SEH-based buffer overflow in Easy File Sharing Web Server 7.2 demonstrating how an authenticated HTTP POST parameter can corrupt the exception…
 themalwareguardian/cve-2017-14980
Stack-based buffer overflow in Sync Breeze Enterprise 10.0.28 reachable through the /login handler, demonstrating how unchecked input length can…