
mcpsnoop
 kerlenton/mcpsnoop
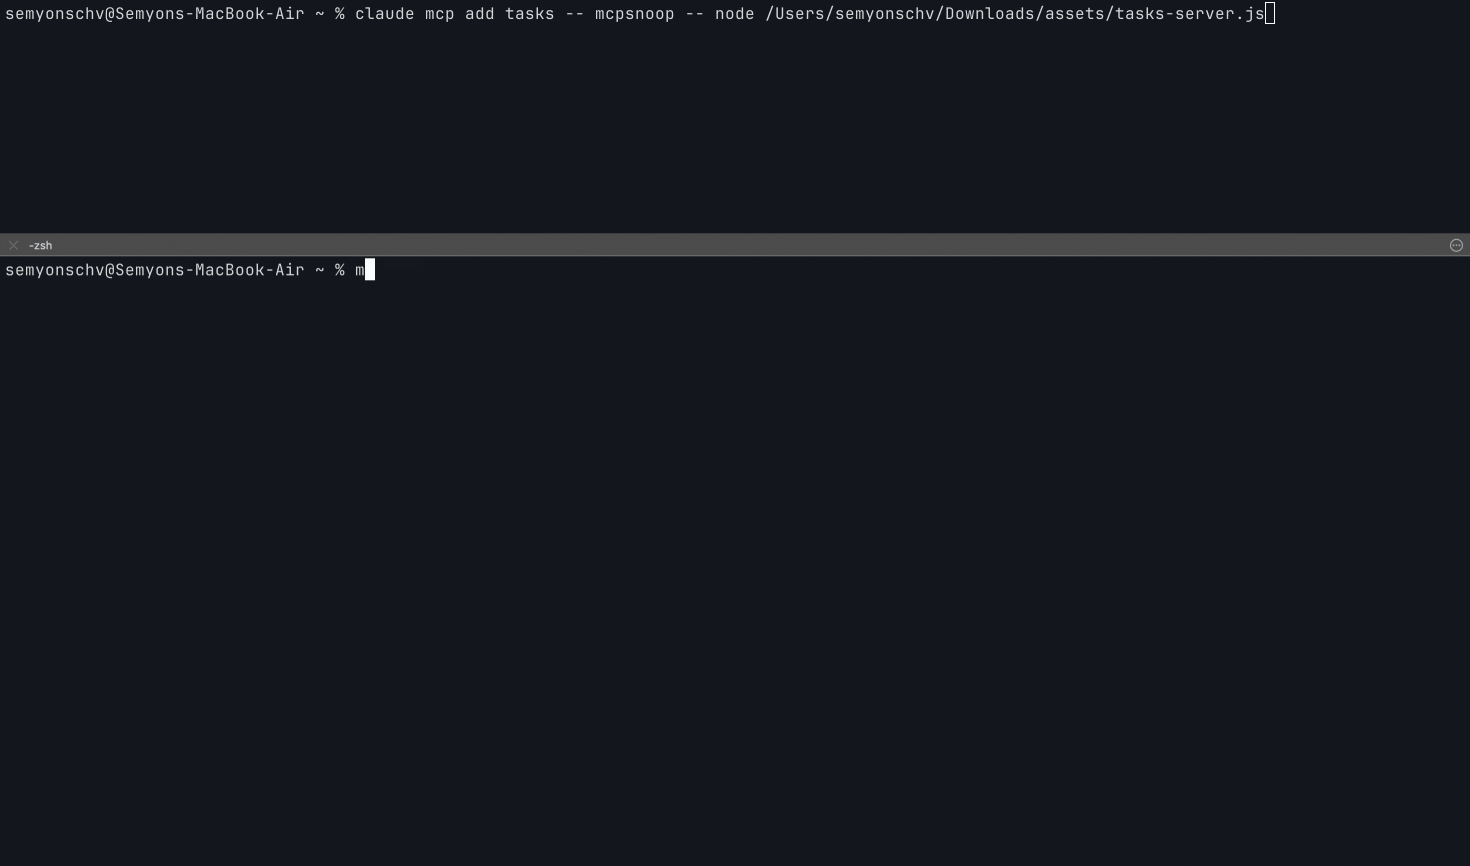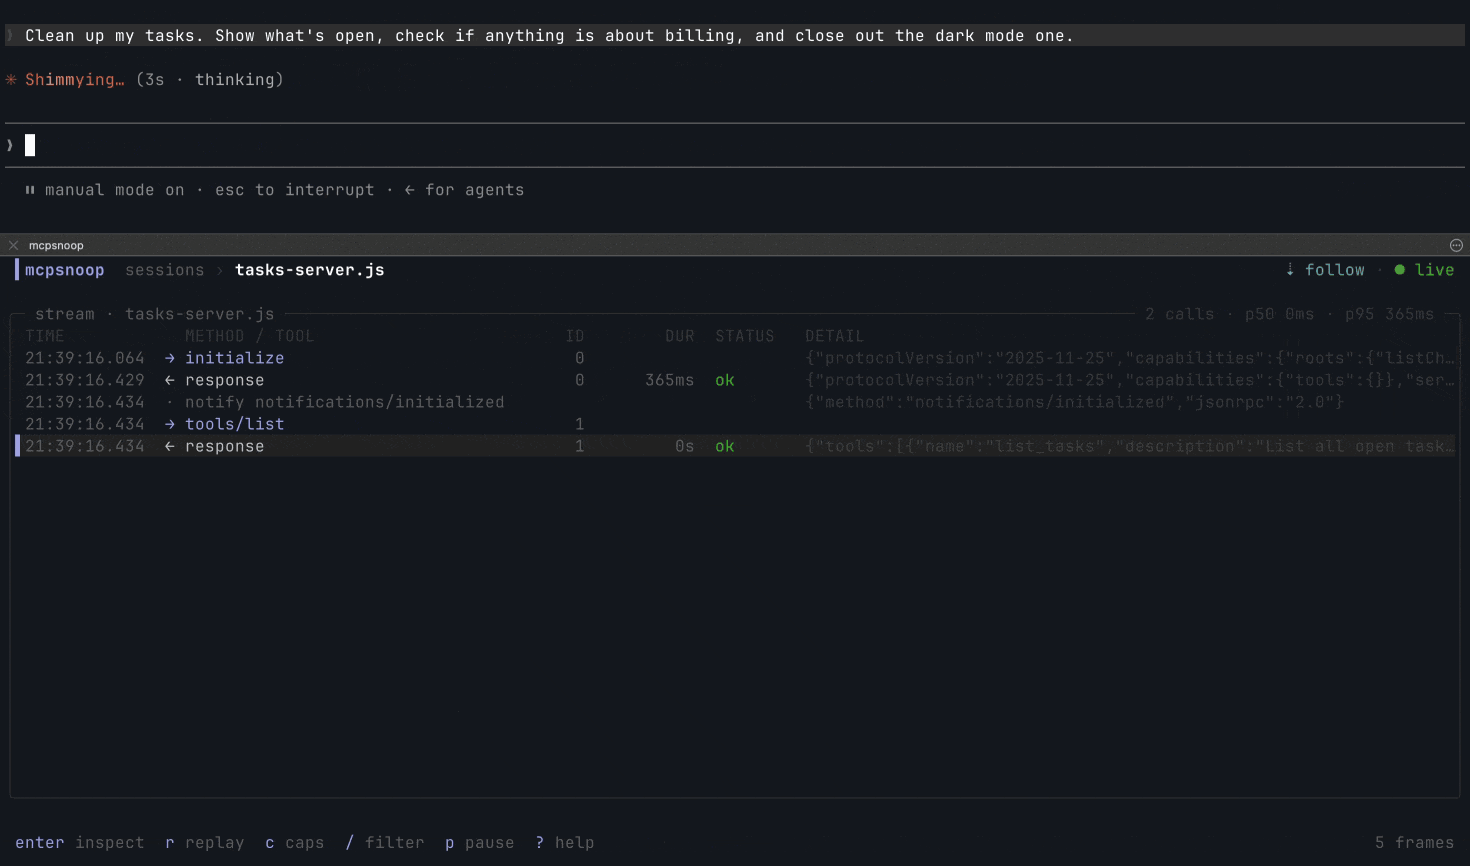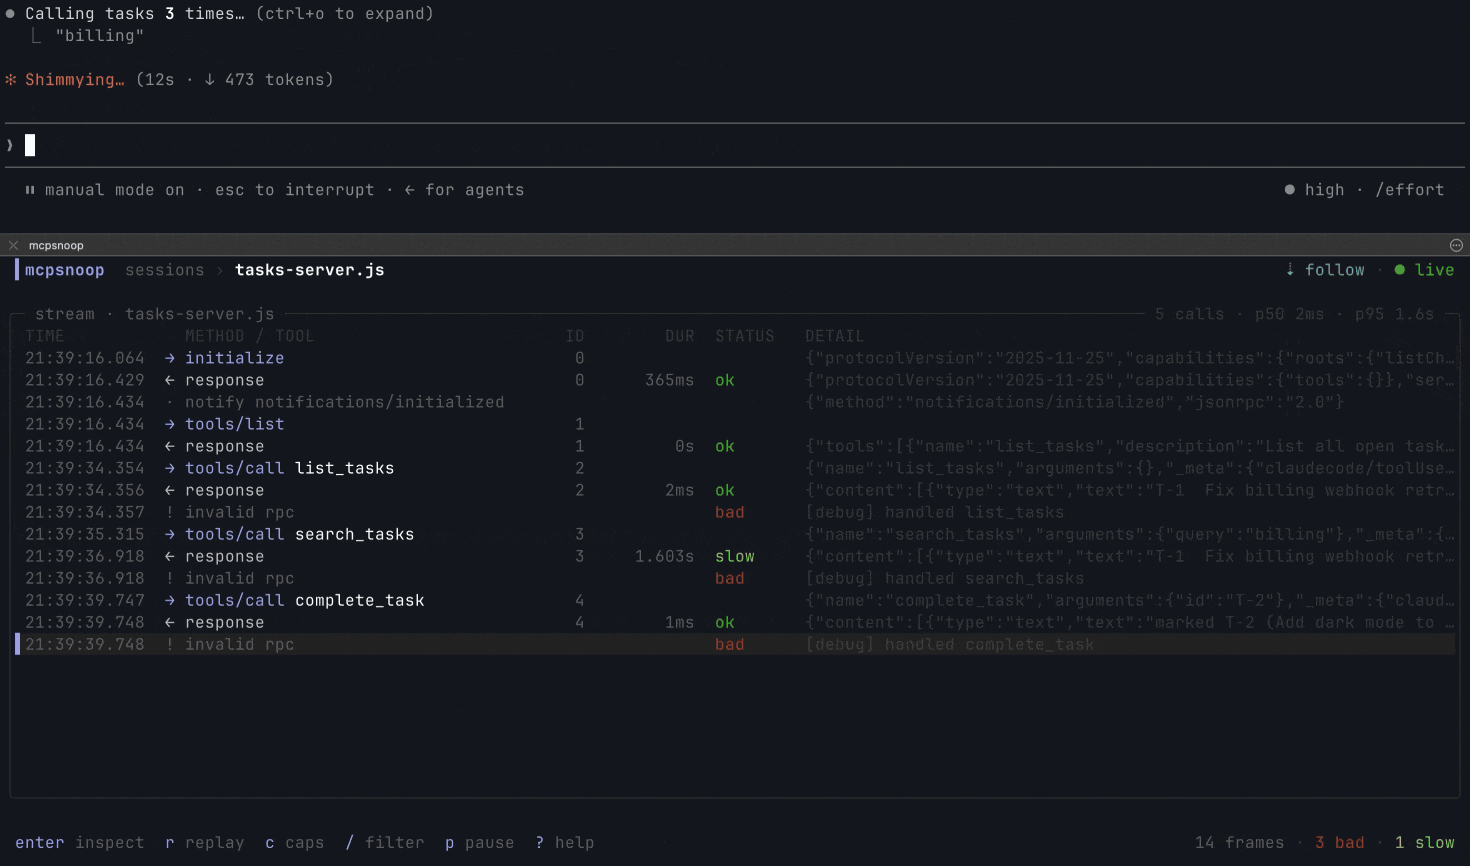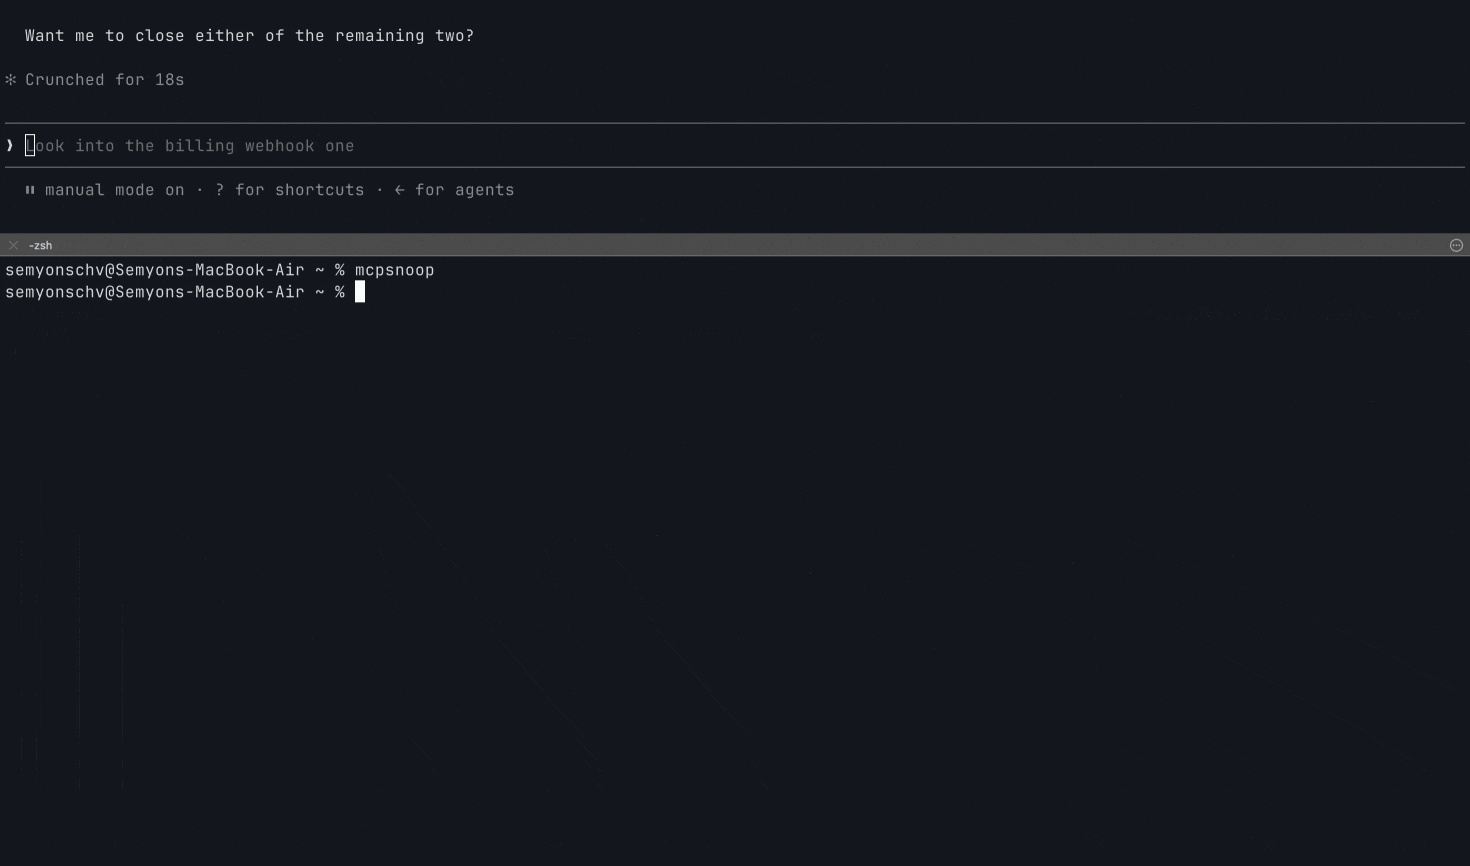
Wireshark for MCP. A transparent proxy between your AI client and MCP server. Watch every call live in your terminal, fail CI on what it finds,…
api-security-testingdebuggersdynamic-analysis-sandboxing+5
361
kerlenton/mcpsnoopWireshark for MCP. A transparent proxy between your AI client and MCP server. Watch every call live in your terminal, fail CI on what it finds,…
 kevoreilly/capev2
Malware Configuration And Payload Extraction
 pwndbg/pwndbg
Exploit Development and Reverse Engineering with GDB & LLDB Made Easy
 advdebug/brovan
User-mode x86_64 binary emulator for malware analysis and reverse engineering. Supports PE, ELF, memory dumps, and raw binaries with syscall tracing,…
 frida/frida-gum
Cross-platform instrumentation and introspection library written in C
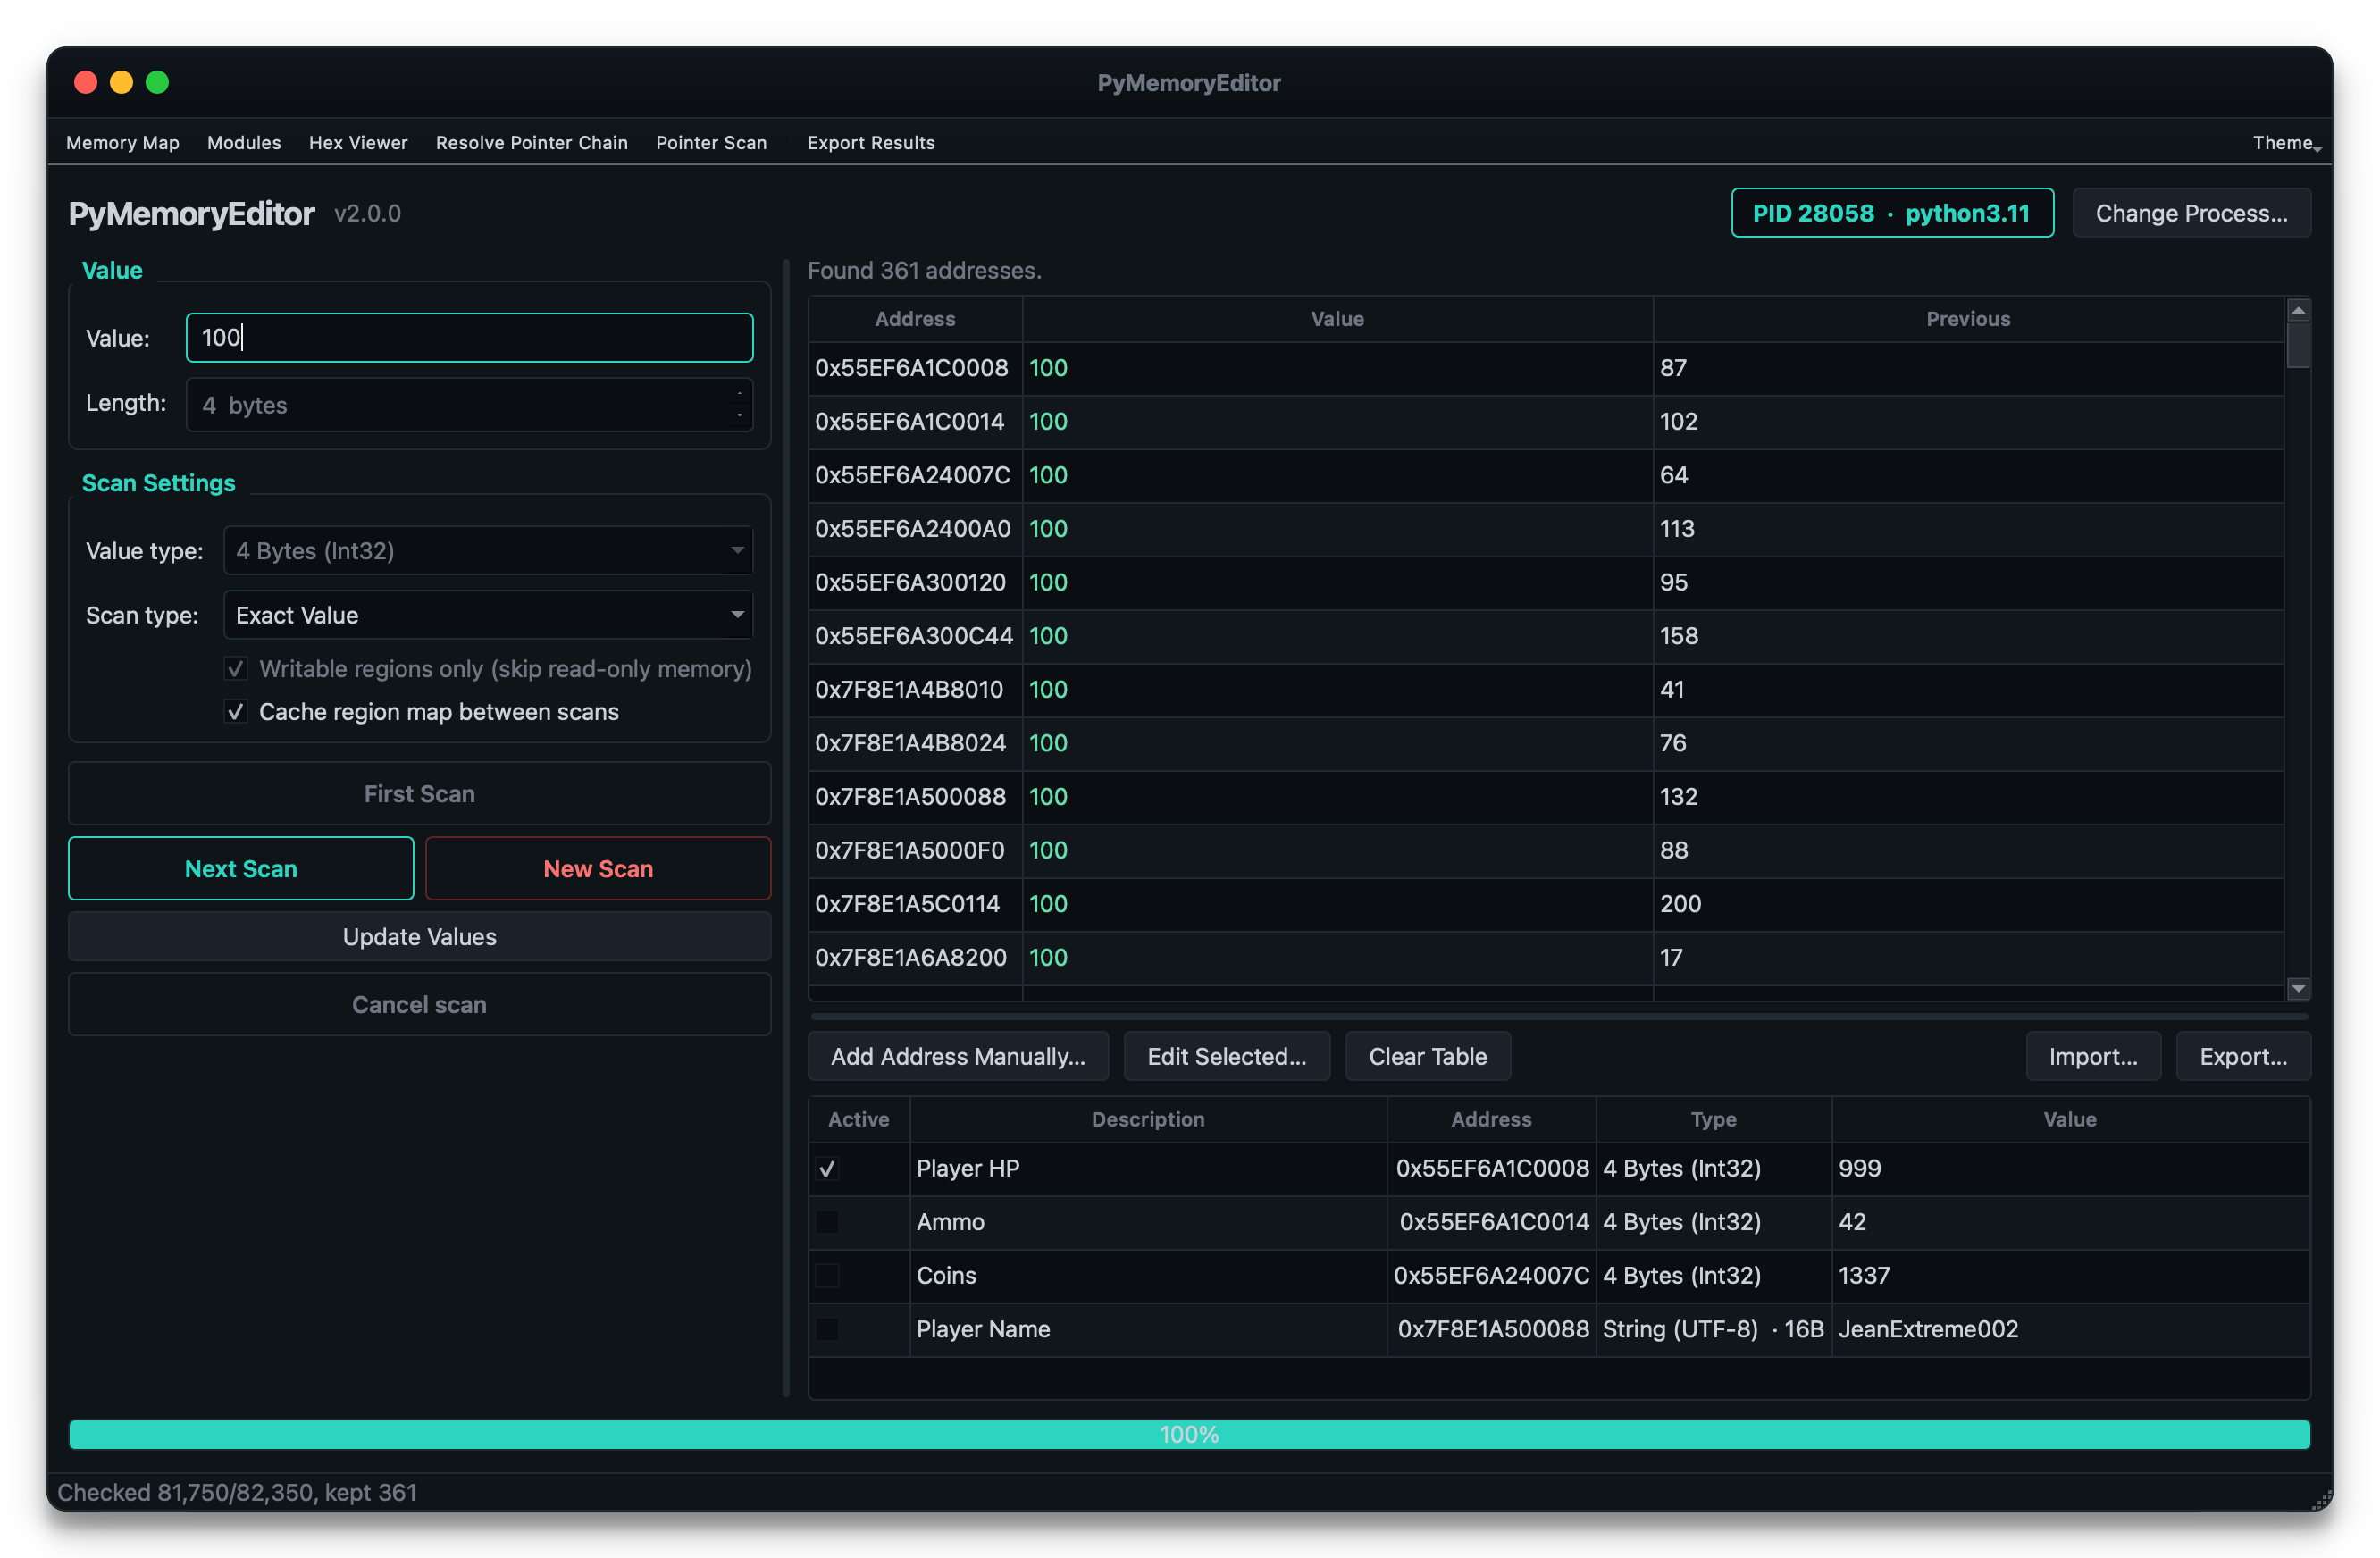 jeanextreme002/pymemoryeditor
A pure-Python library that lets you inspect, modify and search the memory of any running process in a few lines of Python :snake: .
 veridiff/veridiff
Dynamic branch-divergence finder for native code -- traces two Frida executions and finds the exact instruction where they diverge.
 idamcp/idamcp
MCP server integrating IDA Pro with AI agents, featuring a stateless gateway for multi-session management, a relational SQL query engine for binary…
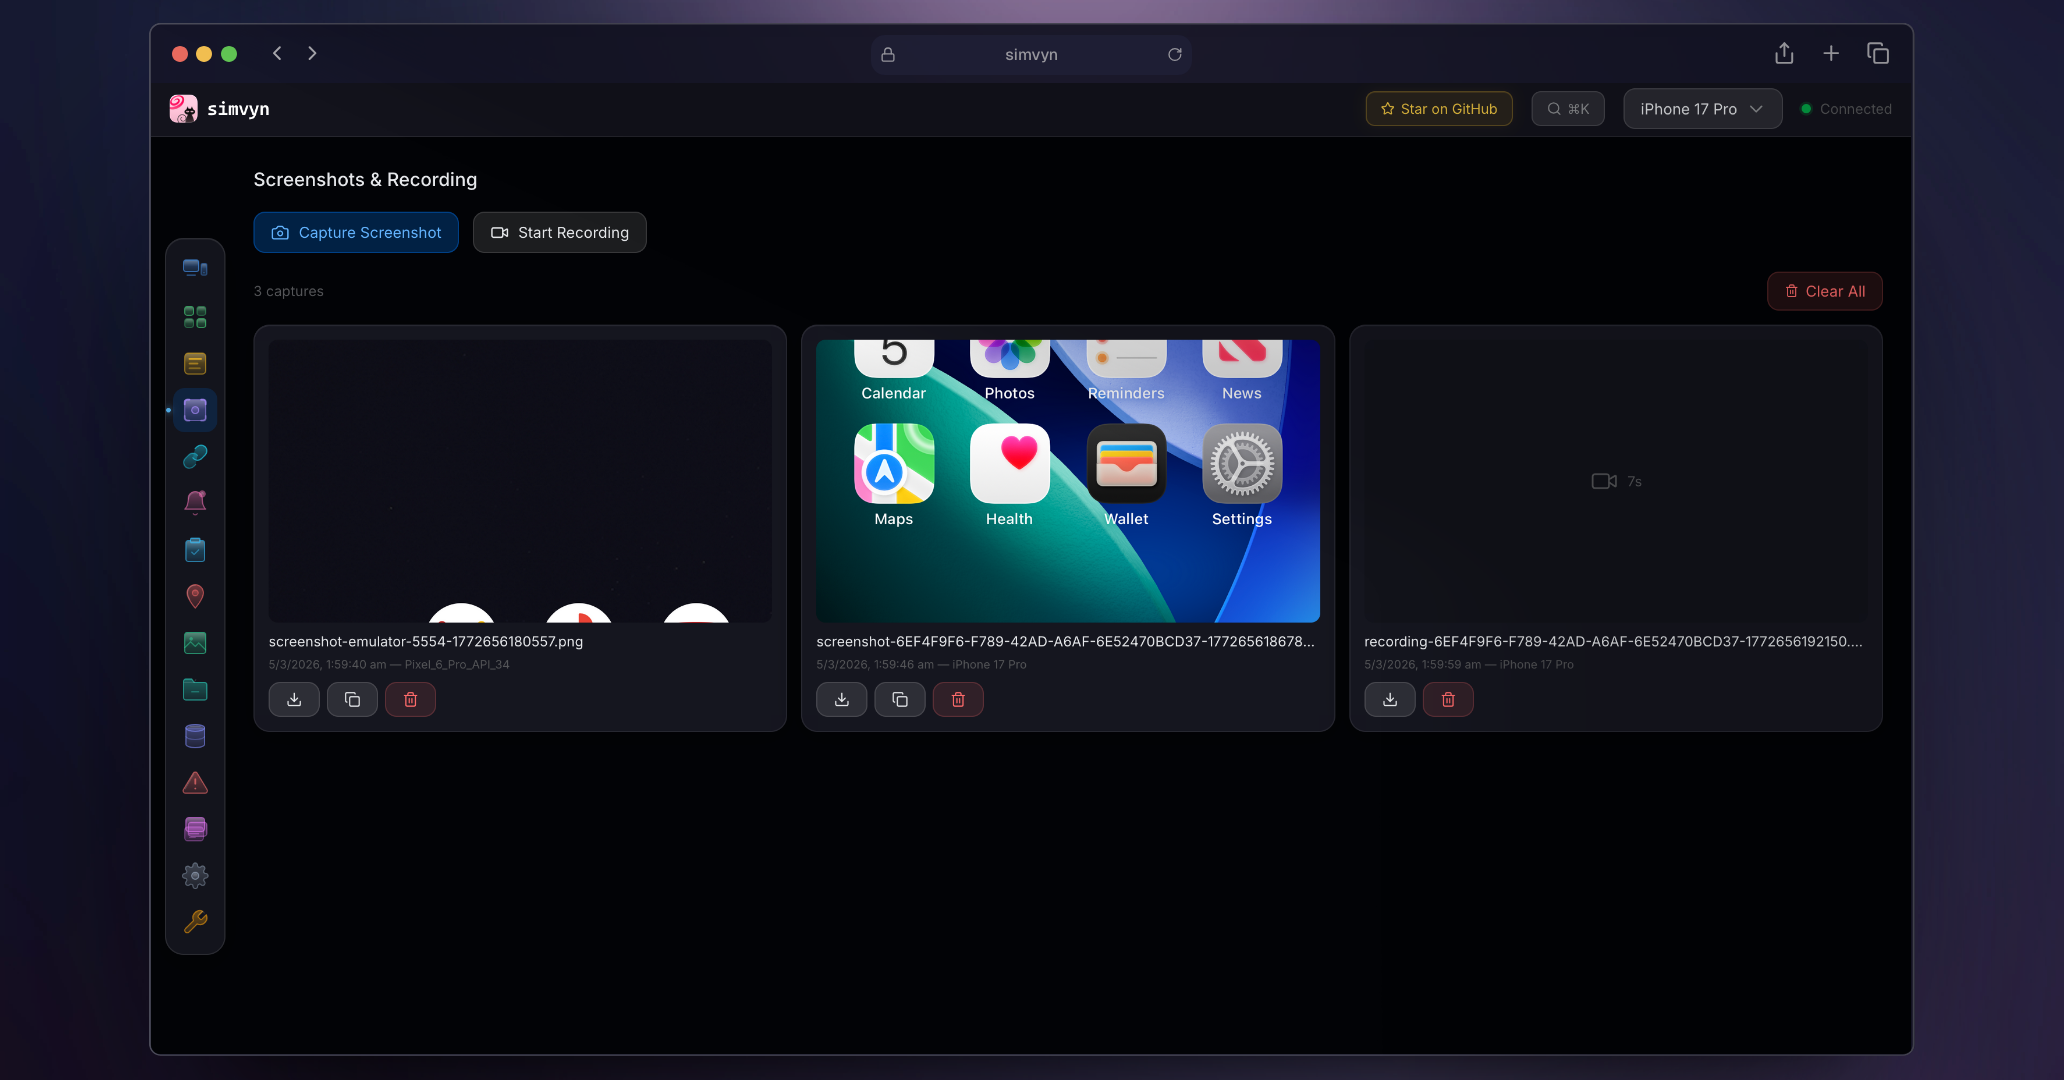 pranshuchittora/simvyn
Universal mobile devtool for Agents & Humans - control iOS Simulators, Android Emulators, and real devices from a single dashboard and CLI
 recurse-labs/recurse
Agentic reverse engineering IDE with a pure-Rust multi-architecture disassembler, native decompiler, debugger, and LLM agent for binary analysis and…
 velteyn/unbattletech
BattleTech: The Crescent Hawk's Inception reverse engeneering
 chichou/vscode-frida
Unofficial frida extension for VSCode
 kaandemir993/formbook-payload-extraction-xor-decryption-net-assembly-analysis
Reverse engineering analysis of Formbook, an info-stealer that uses .NET assembly manipulation and XOR decryption. Full payload extracted via x32dbg,…
 ngwg/ceasta
disassembler, decompiler and debugger in one, with a built-in mcp server: point an ai at a binary and it can debug it, not just read it. ida-style…
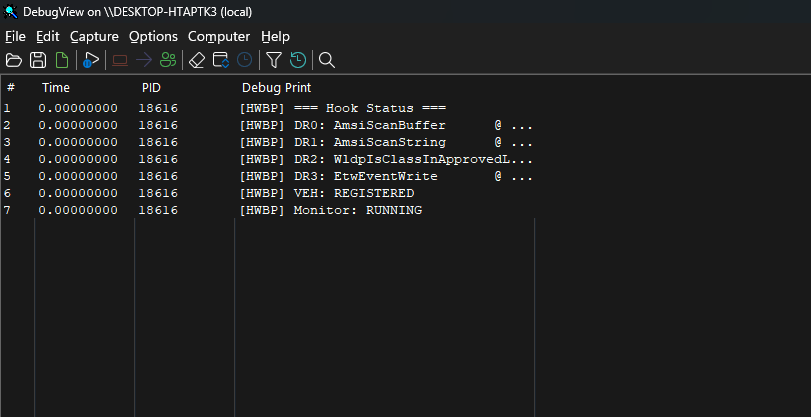 dovughs/mora-hwbp
Hardware Breakpoint (DR0-DR7) based patch-less user-mode hooking & telemetry instrumentation engine (AMSI, WLDP & ETW PoC).
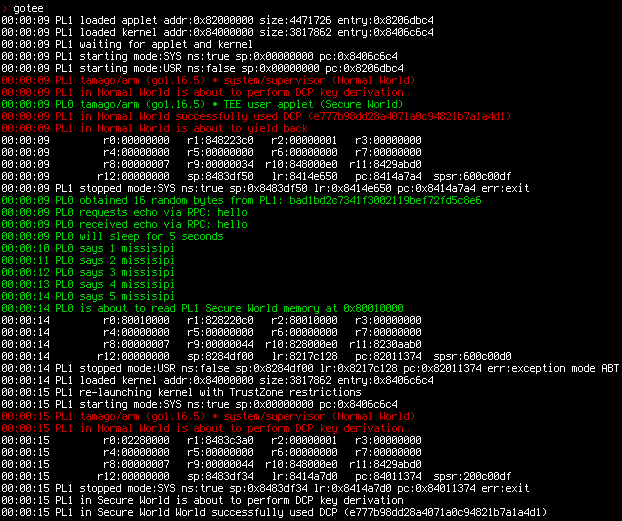 usbarmory/gotee-example
GoTEE - example application
 cea-sec/miasm
Reverse engineering framework in Python
 symgraph/ghidrassist
An LLM extension for Ghidra to enable AI assistance in RE.