
CVE-2026-37149
 pateldhyeyit/cve-2026-37149
CVE-2026-37149 - SQL Injection vulnerability in the scost parameter of search_products.php in…
database-securityeducationinformation-gathering+3
2
pateldhyeyit/cve-2026-37149CVE-2026-37149 - SQL Injection vulnerability in the scost parameter of search_products.php in…
 0xdeku/cve-2021-42670
CVE-2021-42670 - SQL Injection vulnerability in the Engineers online portal system.
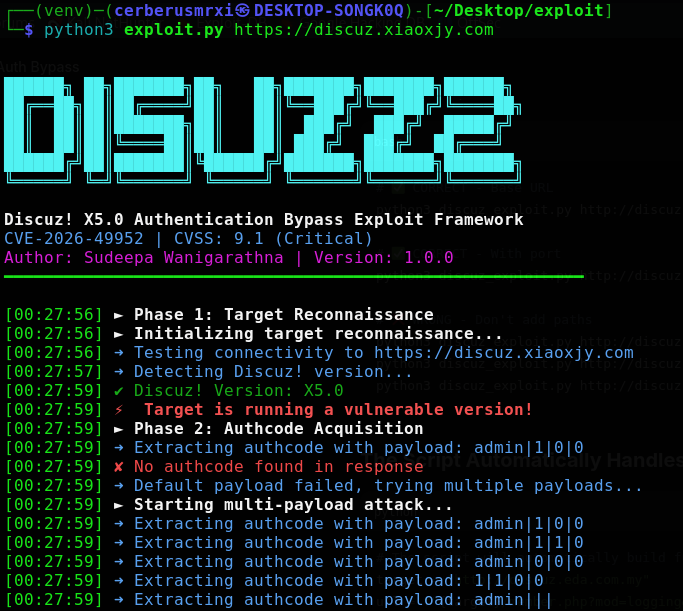 cerberusmrxi/discuz-x5.0-authentication-bypass-exploit-framework
Discuz! X5.0 Authentication Bypass Exploit Framework (CVE-2026-49952) - Critical vulnerability allowing unauthenticated database backup access via…
 cerberusmrxi/cve-2026-44680-mikroorm-sql-injection-exploit-framework
PoC tool for CVE-2026-44680 affecting MikroORM ≤7.0.13. Exploits JSON path injection to extract database contents via UNION-based attacks. Features…
 peakcyber-security/cve-2025-14847
CVE-2025-14847 | MongoBleed vulnerability proof of concept project
 0xdeku/cve-2021-42667
CVE-2021-42667 - SQL Injection vulnerability in the Online event booking and reservation system.
 nu1l0/cve-2024-46636-sqli-modaps
SQL Injection vulnerability in NASA EOSDIS MODAPS due to improper input validation in the `category` parameter. This flaw allows attackers to…
 xmyronn/cve-2026-7394-sqli
Proof-of-concept exploit for CVE-2026-7394, a SQL injection vulnerability in SourceCodester Pizzafy Ecommerce System 1.0. Demonstrates authenticated…
 shinyseam/cve-2025-64513
PoC for CVE-2025-64513 — Milvus Proxy Authentication Bypass Vulnerability Batch scanner to verify unauthorized access and gather Milvus version,…
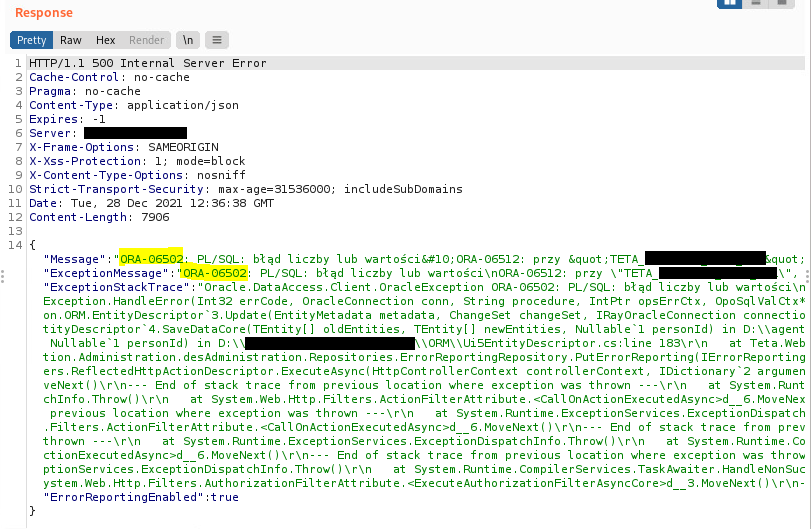 longwayhomie/cve-2022-27434
UNIT4 TETA Mobile Edition 29HF13 was discovered to contain a SQL injection vulnerability via the ProfileName parameter in the errorReporting page.
 zsy107u/cve-2025-2011-poc
Proof-of-concept exploit for CVE-2025-2011, a SQL injection vulnerability in WordPress Depicter Plugin 3.6.1, enabling database enumeration and data…
 chrissub08/cve-2026-29187_sqlinjectionvulnerabilityopenemr7.0.4
CVE-2026-29187: SQL Injection Vulnerability in OpenEMR <8.0.0.3
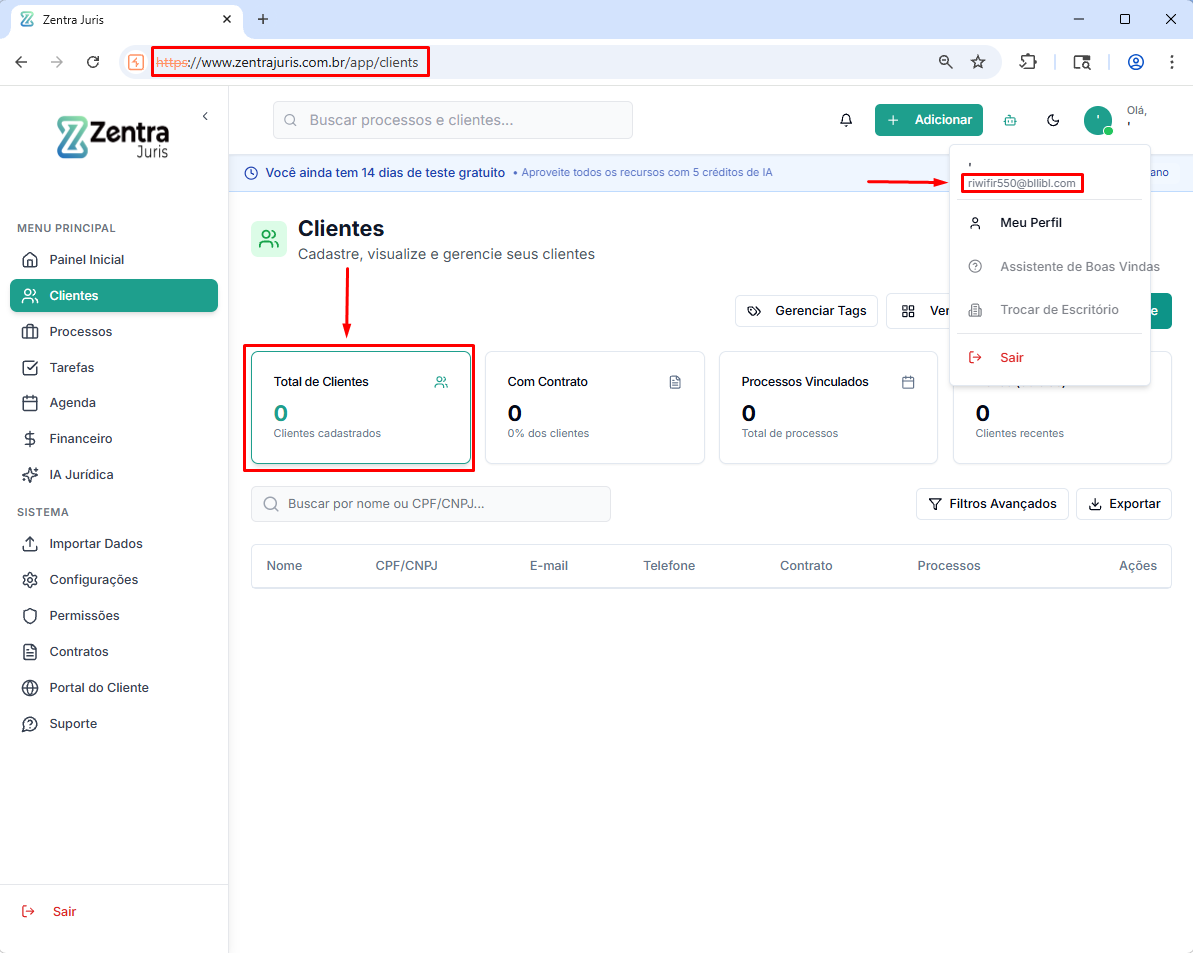 rrespxwnss/cve-2025-63572
A SQL injection vulnerability was discovered in the endpoint responsible for searching for platform clients. User input sent to the search parameter…
 systemhaus-schulz/mongobleed-cve-2025-14847
MongoBleed CVE-2025-14847 Vulnerability Checker
 sakthivel10q/sakthivel10q.github.io
🛠 Exploit the CVE-2025-14847 MongoDB vulnerability to reveal sensitive information through crafted zlib-compressed packets and real-time output.
 m0b1u3/cve-2025-50565
Proof-of-concept exploit for an SQL injection vulnerability in Doubo ERP 1.0, enabling remote attackers to extract sensitive database information.
 0xdeku/cve-2021-42666
CVE-2021-42666 - SQL Injection vulnerability in the Engineers online portal system.
 emad-almousa/cve-2023-22074
Proof-of-concept exploit for CVE-2023-22074, an Oracle Database Sharding component vulnerability enabling password hash exposure in versions 19c,…