Chrome-App-Bound-Encryption-Decryption

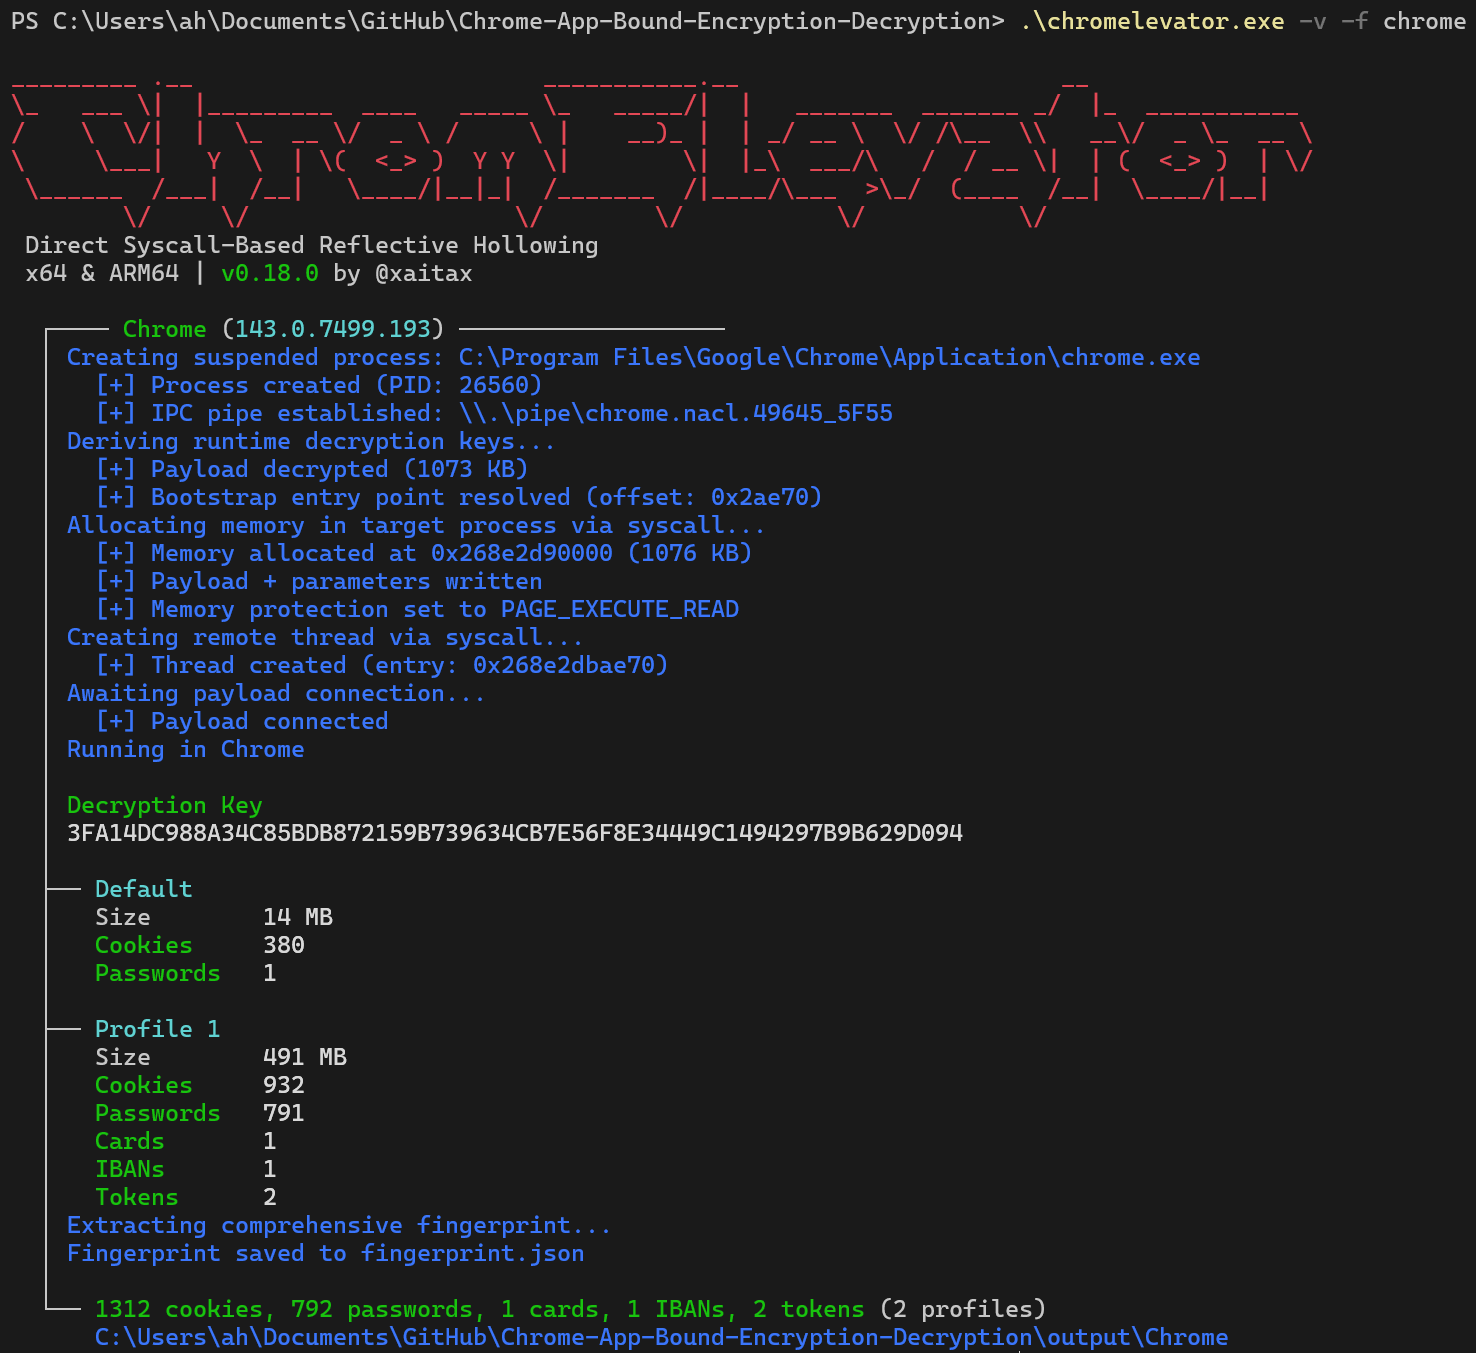
Bypass Chromium's App-Bound Encryption via Direct Syscall-based Reflective Process Hollowing. Extract cookies, passwords, payment methods & tokens…

Bypass Chromium's App-Bound Encryption via Direct Syscall-based Reflective Process Hollowing. Extract cookies, passwords, payment methods & tokens…

Dump cookies and credentials directly from Chrome/Edge process memory

Physmem2profit can be used to create a minidump of a target hosts' LSASS process by analysing physical memory remotely

Bypasses PPL protection to dump LSASS process memory, obfuscates dump files with XOR, and exfiltrates them remotely via RAW or SMB without writing to…

Solitude is a privacy analysis tool that enables anyone to conduct their own privacy investigations. Whether a curious novice or a more advanced…

LeakScraper is an efficient set of tools to process and visualize huge text files containing credentials. Theses tools are designed to help…

A standalone DLL that exports databases in cleartext once injected in the KeePass process.

Proof-of-concept exploiting an undocumented Muse dictation endpoint setting, letting a local unprivileged process redirect dictation traffic to…

Exploit for Adobe Reader DC out-of-bounds read vulnerability (CVE-2021-45067) that leaks sensitive information from the sandboxed process via…

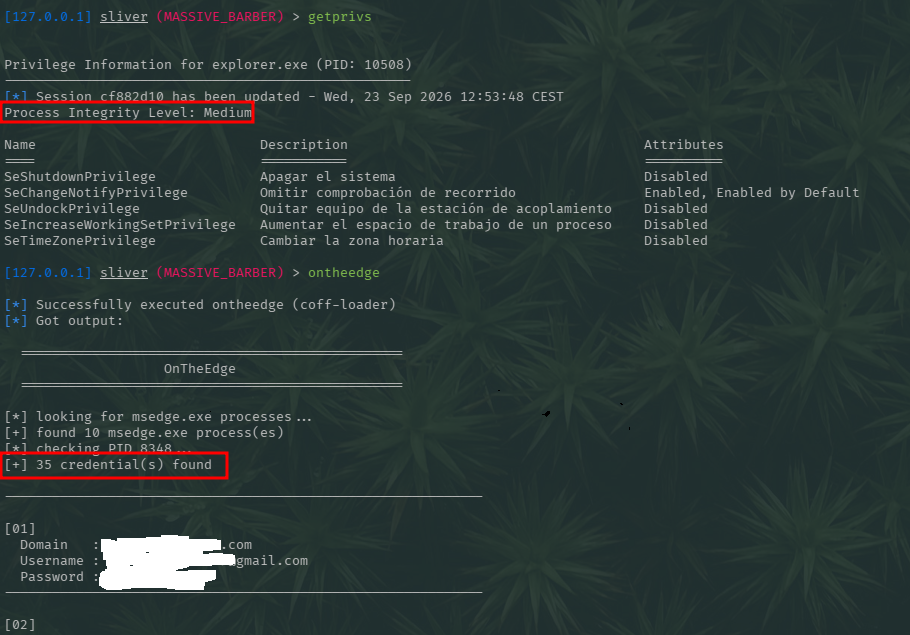
Windows research PoC in C that scans Microsoft Edge process memory for credential-related data, with a standalone executable and a BOF variant for C2…

In-depth reverse engineering analysis of Lumma Stealer, an info-stealer using process hollowing, Native API calls, and C2 communication. Includes…

Network forensics writeup + tooling for a TryHackMe DFIR challenge: reverses a hex→Base64→XOR exfiltration chain from PCAP traffic, then recovers a…

Proof-of-concept exploit for CVE-2025-12137 demonstrating local file disclosure via a WordPress plugin's REST API importer endpoint. Includes…

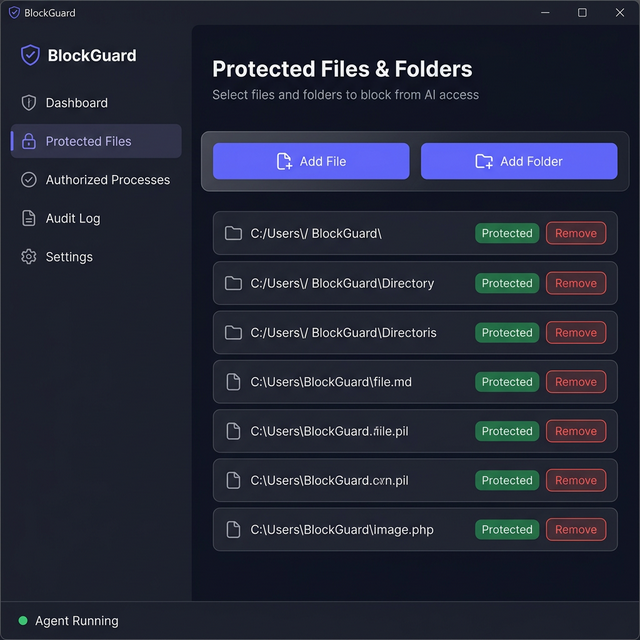
BlockGuard is a Windows Data Loss Prevention (DLP) agent that intercepts and controls file access at the process level. It ensures that only…

Simple Process Dumper using DMA over a PCIe FPGA device

My experiments in weaponizing Nim (https://nim-lang.org/)

Initial Access and Post-Exploitation Tool for Entra ID and M365 with a browser-based GUI

Kautilya - Tool for easy use of Human Interface Devices for offensive security and penetration testing.