Overlord-RAT-Reverse-Engineering-a-Go-Based-RAT-Injection-Keylogging-C2-Exfiltration-Analysis

Full static & memory analysis of Overlord RAT: Go agent architecture, HTTP/2 + WebSocket C2, reflective DLL injection, browser keylogging, and IOCs.…

Full static & memory analysis of Overlord RAT: Go agent architecture, HTTP/2 + WebSocket C2, reflective DLL injection, browser keylogging, and IOCs.…

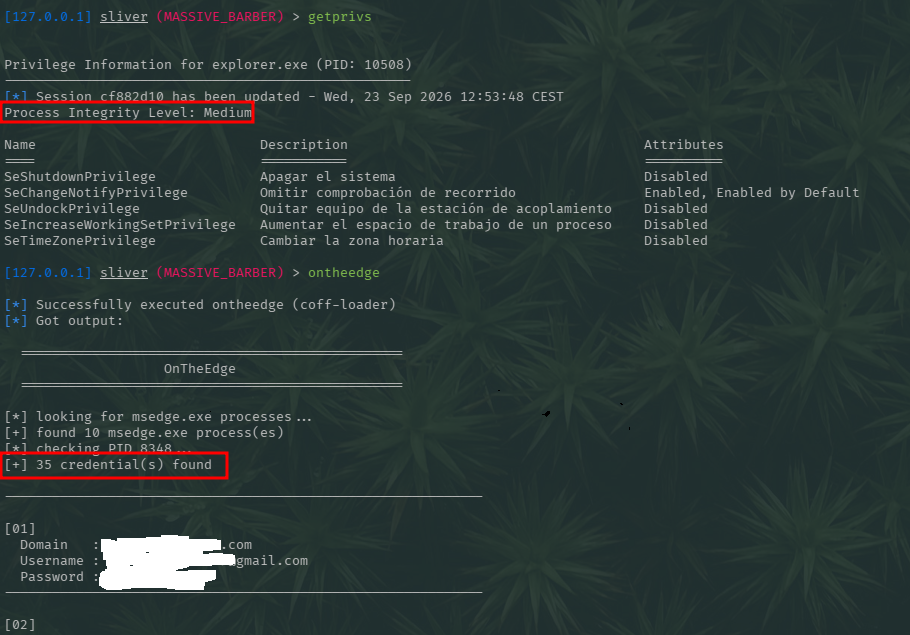
Windows research PoC in C that scans Microsoft Edge process memory for credential-related data, with a standalone executable and a BOF variant for C2…

Proof-of-concept exploiting an undocumented Muse dictation endpoint setting, letting a local unprivileged process redirect dictation traffic to…

Simple Process Dumper using DMA over a PCIe FPGA device

In-depth reverse engineering analysis of Lumma Stealer, an info-stealer using process hollowing, Native API calls, and C2 communication. Includes…

Network forensics writeup + tooling for a TryHackMe DFIR challenge: reverses a hex→Base64→XOR exfiltration chain from PCAP traffic, then recovers a…

Physmem2profit can be used to create a minidump of a target hosts' LSASS process by analysing physical memory remotely

A standalone DLL that exports databases in cleartext once injected in the KeePass process.

Initial Access and Post-Exploitation Tool for Entra ID and M365 with a browser-based GUI

Dump cookies and credentials directly from Chrome/Edge process memory

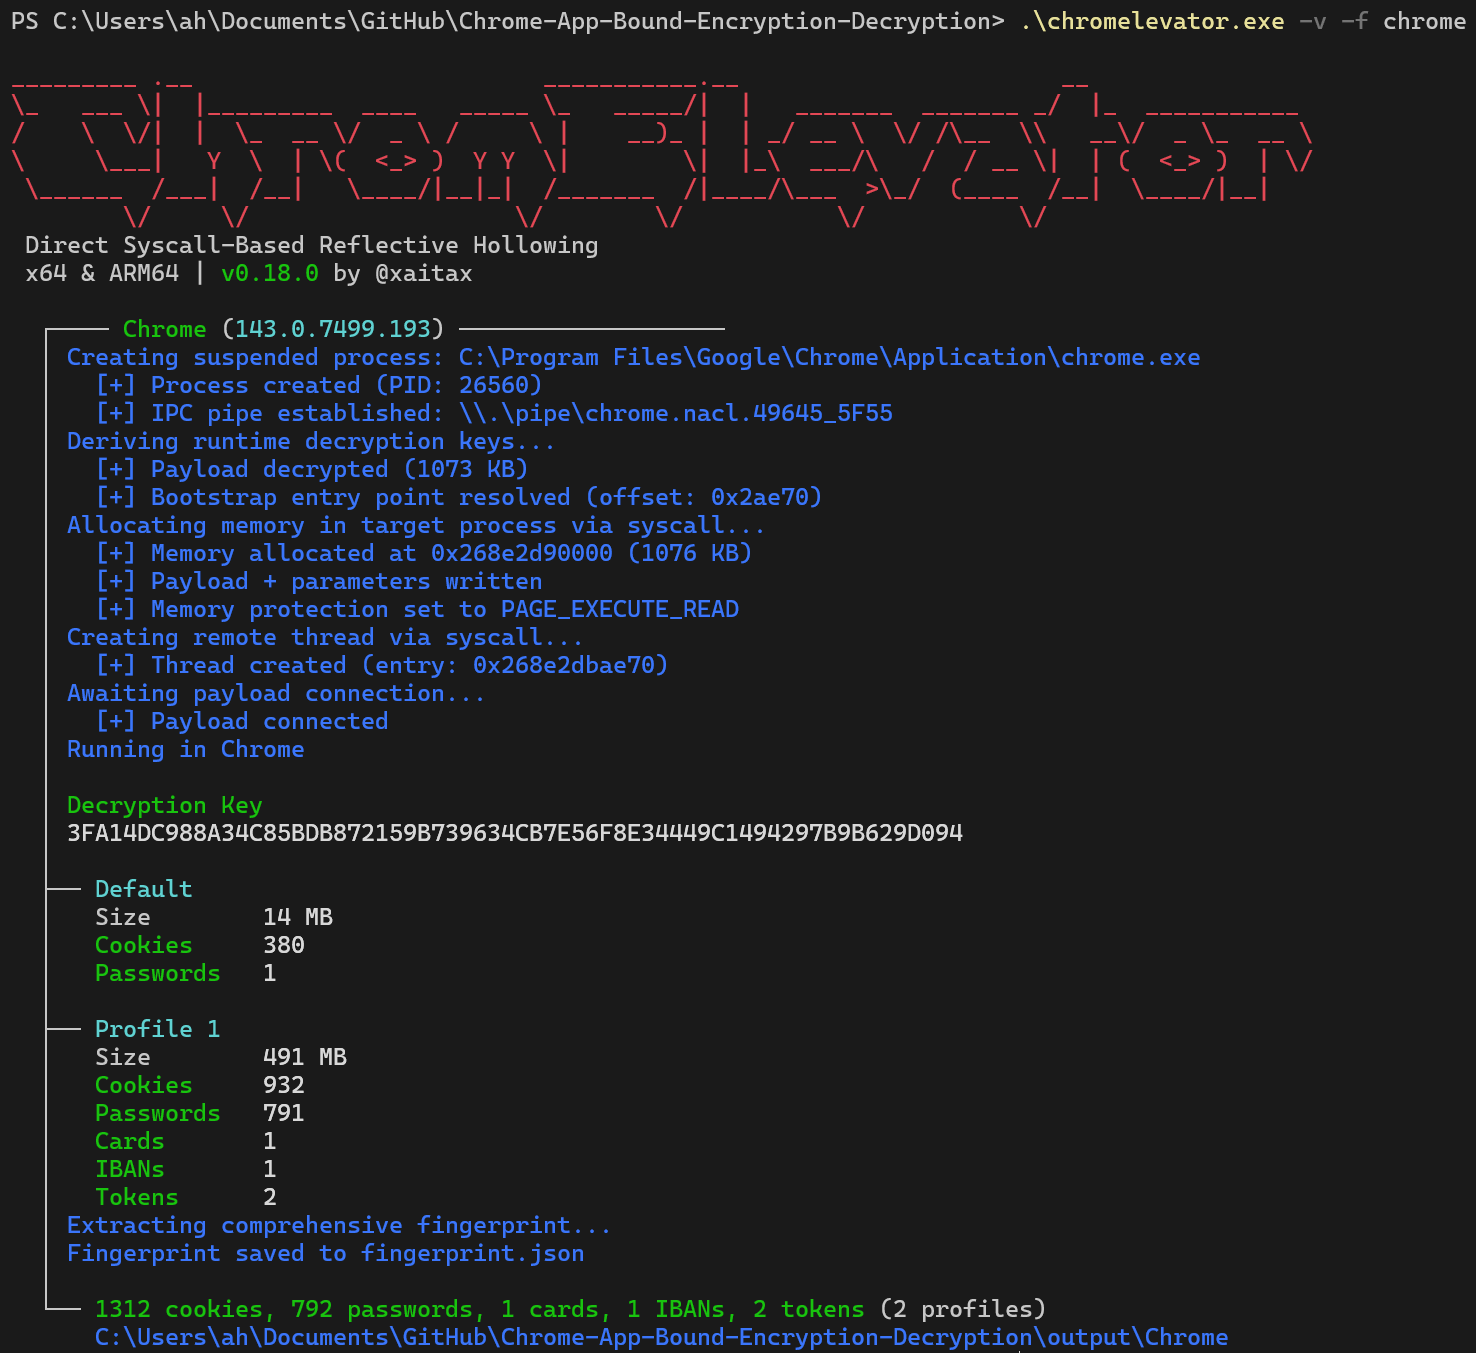
Bypass Chromium's App-Bound Encryption via Direct Syscall-based Reflective Process Hollowing. Extract cookies, passwords, payment methods & tokens…

Solitude is a privacy analysis tool that enables anyone to conduct their own privacy investigations. Whether a curious novice or a more advanced…

Scan LLM outputs and AI-generated content for data exfiltration signals (EchoLeak, CVE-2025-32711) before they reach users or downstream systems

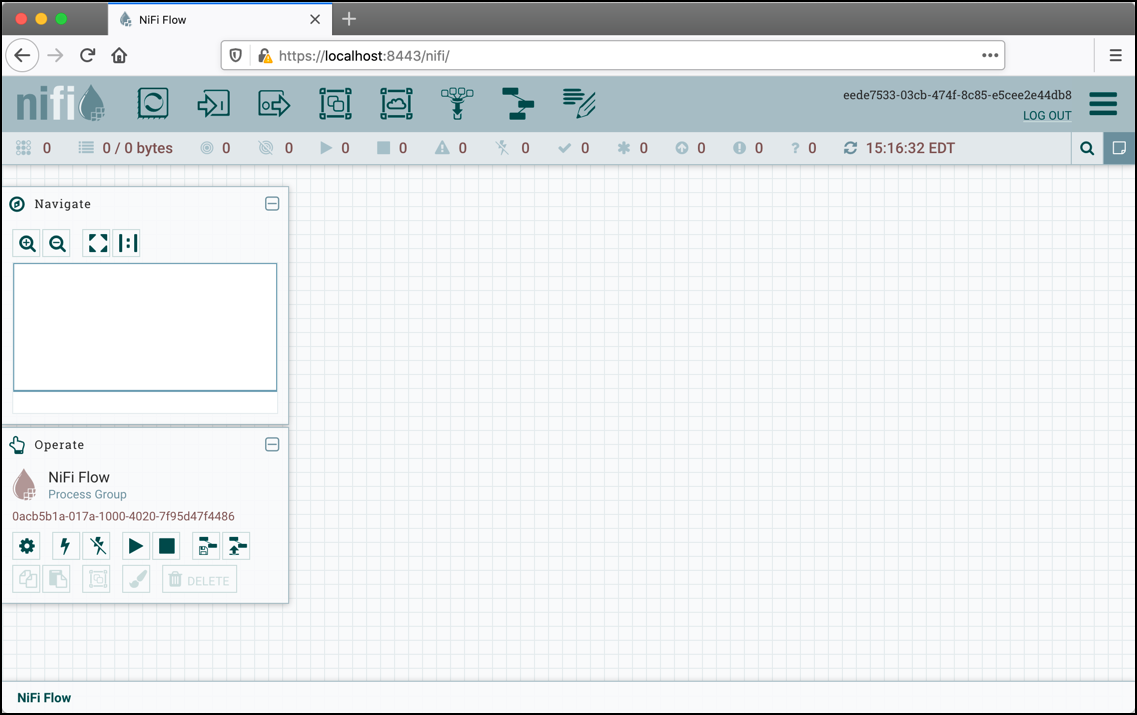
Automated data flow processing and distribution system with secure configuration, provenance tracking, and extensible plugin architecture for…

Automated data flow platform for processing and distributing data with built-in provenance tracking, secure configuration, and scalable pipeline…

Exploit for Apache NiFi CVE-2023-34468, targeting a vulnerability in versions 1.21.0 and earlier to demonstrate data access and system compromise.

Exploit for Adobe Reader DC out-of-bounds read vulnerability (CVE-2021-45067) that leaks sensitive information from the sandboxed process via…

CitrixBleed2 poc