

GateX
 abraxas/gatex
FortinetHunter (@YogSoth0) binary cracking application. Part of CTF for FortinetHunter. ELF door: a stripped Nuitka onefile, an XOR-scrambled…
binary-analysisbinary-exploitationcryptography+8
1
abraxas/gatexFortinetHunter (@YogSoth0) binary cracking application. Part of CTF for FortinetHunter. ELF door: a stripped Nuitka onefile, an XOR-scrambled…
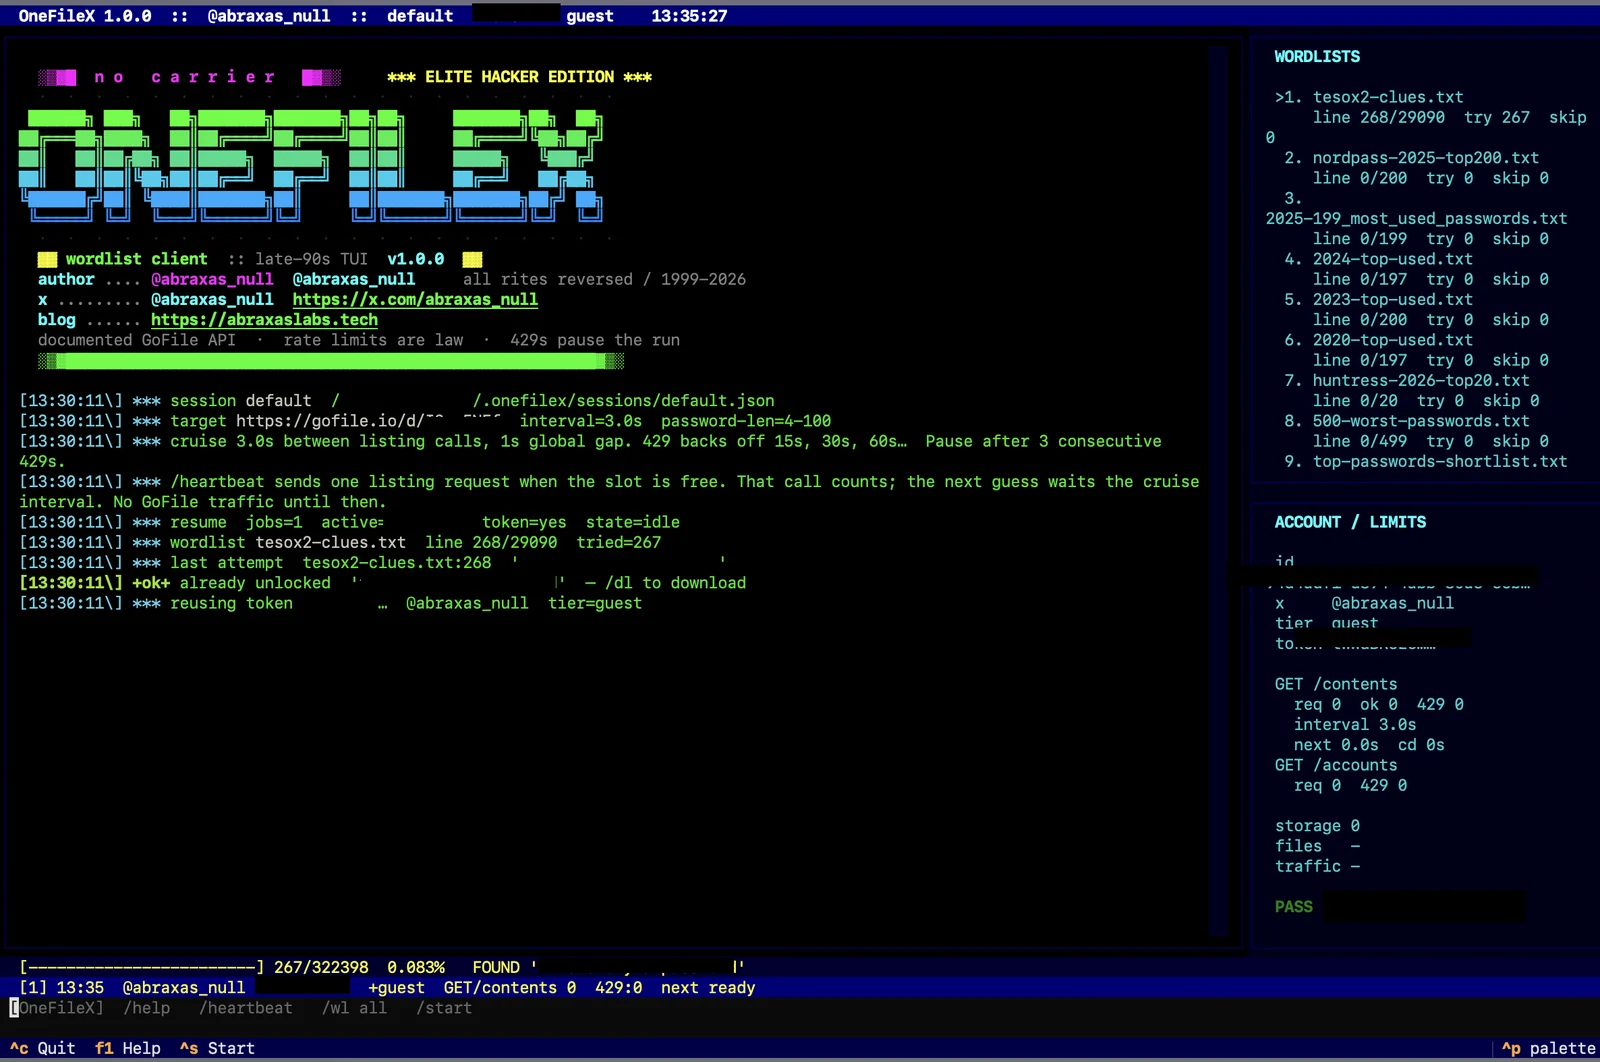 abraxas/gofilex
Wordlist Bruteforcer for GoFile (gofile.io) Download Passwords
 gmh5225/kernel-ctf
Collection of Linux kernel exploitation CTF challenges covering buffer overflow, use-after-free, and race condition vulnerabilities for hands-on…
 portswigger/splitting-the-email-atom
Research materials and tooling for exploiting email address parser discrepancies to bypass access controls, including fuzzers, Hackvertor tags, CSS…
 b4sith-sec/gu3ssweak
Deliberately vulnerable Android app for mobile security research and bug bounty practice - OWASP Mobile Top 10
 harry178945/cve-2026-38526
Python PoC exploiting CVE-2026-38526 in Krayin CRM <= 2.2.x: authenticated PHP webshell upload via /admin/tinymce/upload leading to remote code…
 mrdark-ops/cve-2026-38526
Python PoC exploiting CVE-2026-38526 in Krayin CRM <= 2.2.x: authenticates, uploads a PHP webshell via /admin/tinymce/upload, and executes commands…
 mister-iks/pcybox-attackgraph
Open source browser lab to build a simulated infrastructure, watch an attack move through it, and check whether your defense works.
 abdelhakimgafernetworksec/enigm-writeup
Comprehensive penetration testing write-up and exploit details for Hack The Box - Enigma machine, covering local enumeration, OliveTin CVE-2026-27626…
 1833ravikumar-max/cve-2021-41773-apache-path-traversal-lab
Docker-based cybersecurity lab for studying and reproducing CVE-2021-41773 in an isolated environment.
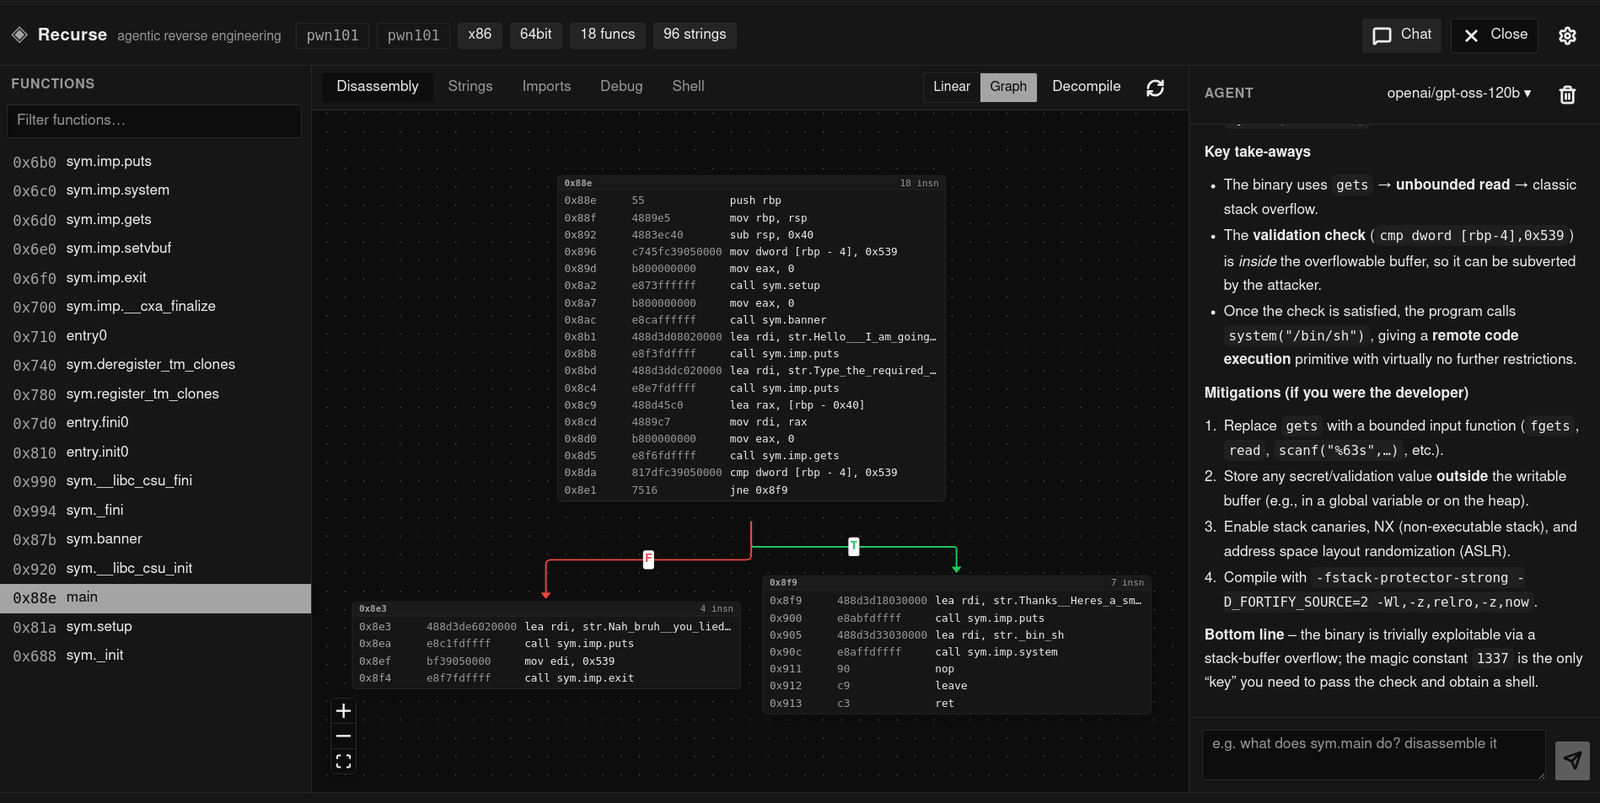 recurse-labs/recurse
Agentic reverse engineering IDE with a pure-Rust multi-architecture disassembler, native decompiler, debugger, and LLM agent for binary analysis and…
 w4r10ck423/envvisualizer
Parse and visualize /proc/self/environ on compromised Linux boxes — categorizes env vars by tech stack (AWS, Django, Rails, NodeJS, MySQL, K8s,…
 s1n6h/pentest-harness
Self-hosted AI agent harness for authorized pentests, bug bounty, security labs, and CTFs. Plugin-based, multi-provider LLM support with local…
 mubix/ai-ctf
Local AI Capture-the-Flag platform with guided lessons on prompt injection, tool-call abuse, and OSINT against six simulated chatbot personas.
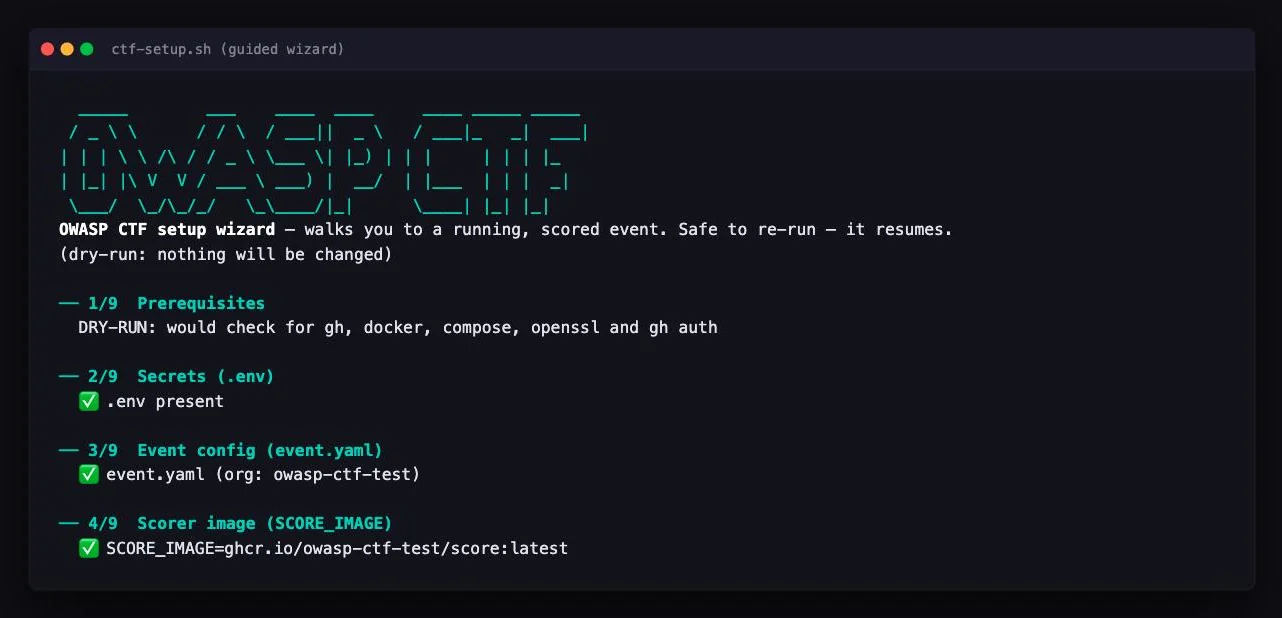 owasp/owasp-ctf-in-a-box
Self-hosted OWASP CTF kit: one box, one free GitHub org, no cloud dependencies
 horkimhab/cve-2026-74469
Proof-of-concept and educational research repository for CVE-2026-74469 (DiagSpill), providing vulnerability analysis material for authorized lab…
 whgojp/javaseclab
Comprehensive Java vulnerability lab with vulnerable and fixed code, attack scenarios, source/sink audit notes, and secure coding guidance for…
 veridiff/veridiff
Dynamic branch-divergence finder for native code -- traces two Frida executions and finds the exact instruction where they diverge.