
certbot
 certbot/certbot
Certbot is EFF's tool to obtain certs from Let's Encrypt and (optionally) auto-enable HTTPS on your server. It can also act as a client for any…
authentication-authorizationcloud-securityconfiguration-auditing+3
33.2k
certbot/certbotCertbot is EFF's tool to obtain certs from Let's Encrypt and (optionally) auto-enable HTTPS on your server. It can also act as a client for any…
 gravitational/teleport
The easiest, and most secure way to access and protect all of your infrastructure.
 prowler-cloud/prowler
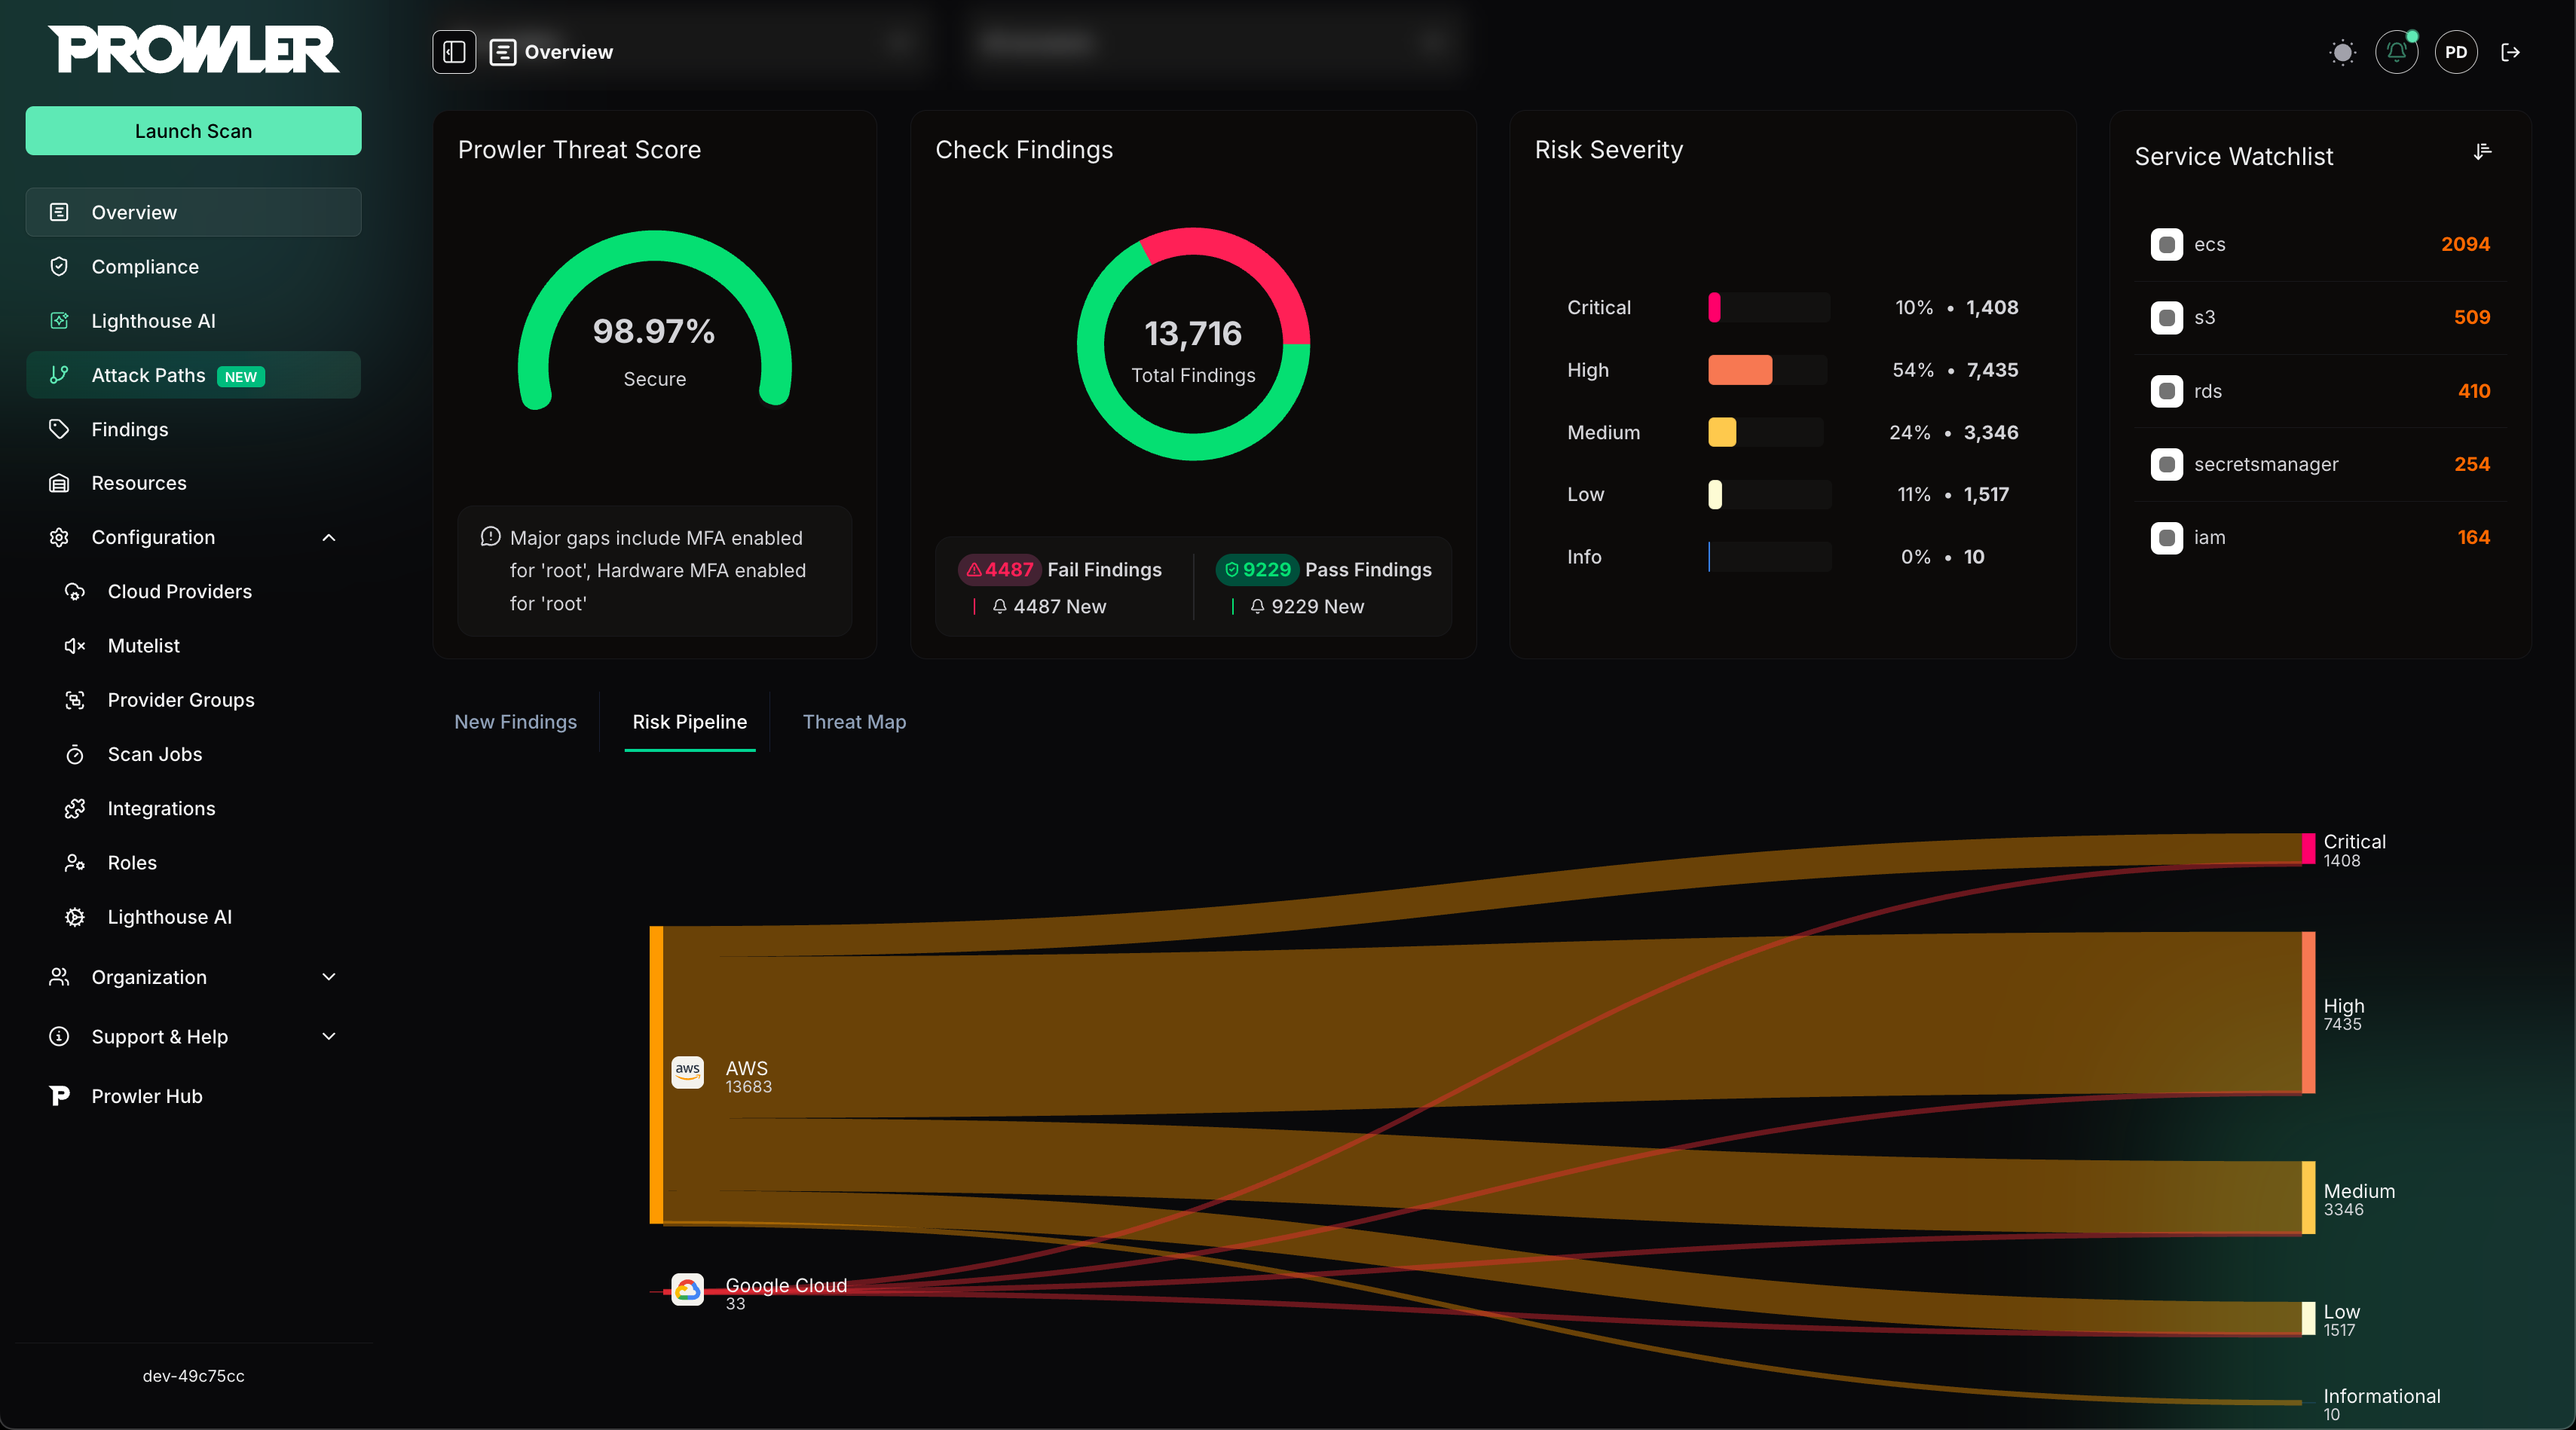
Prowler is the world’s most widely used open-source cloud security platform that automates security and compliance across any cloud environment.…
 cisagov/scubagear
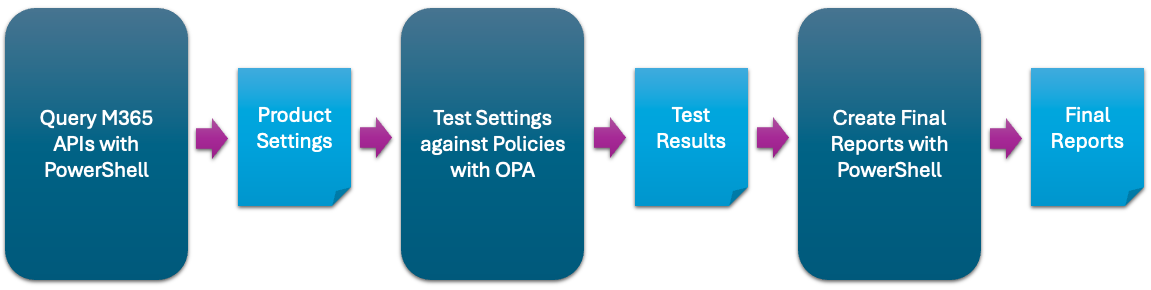
Automation to assess the state of your M365 tenant against CISA's baselines
 duo-labs/cloudmapper
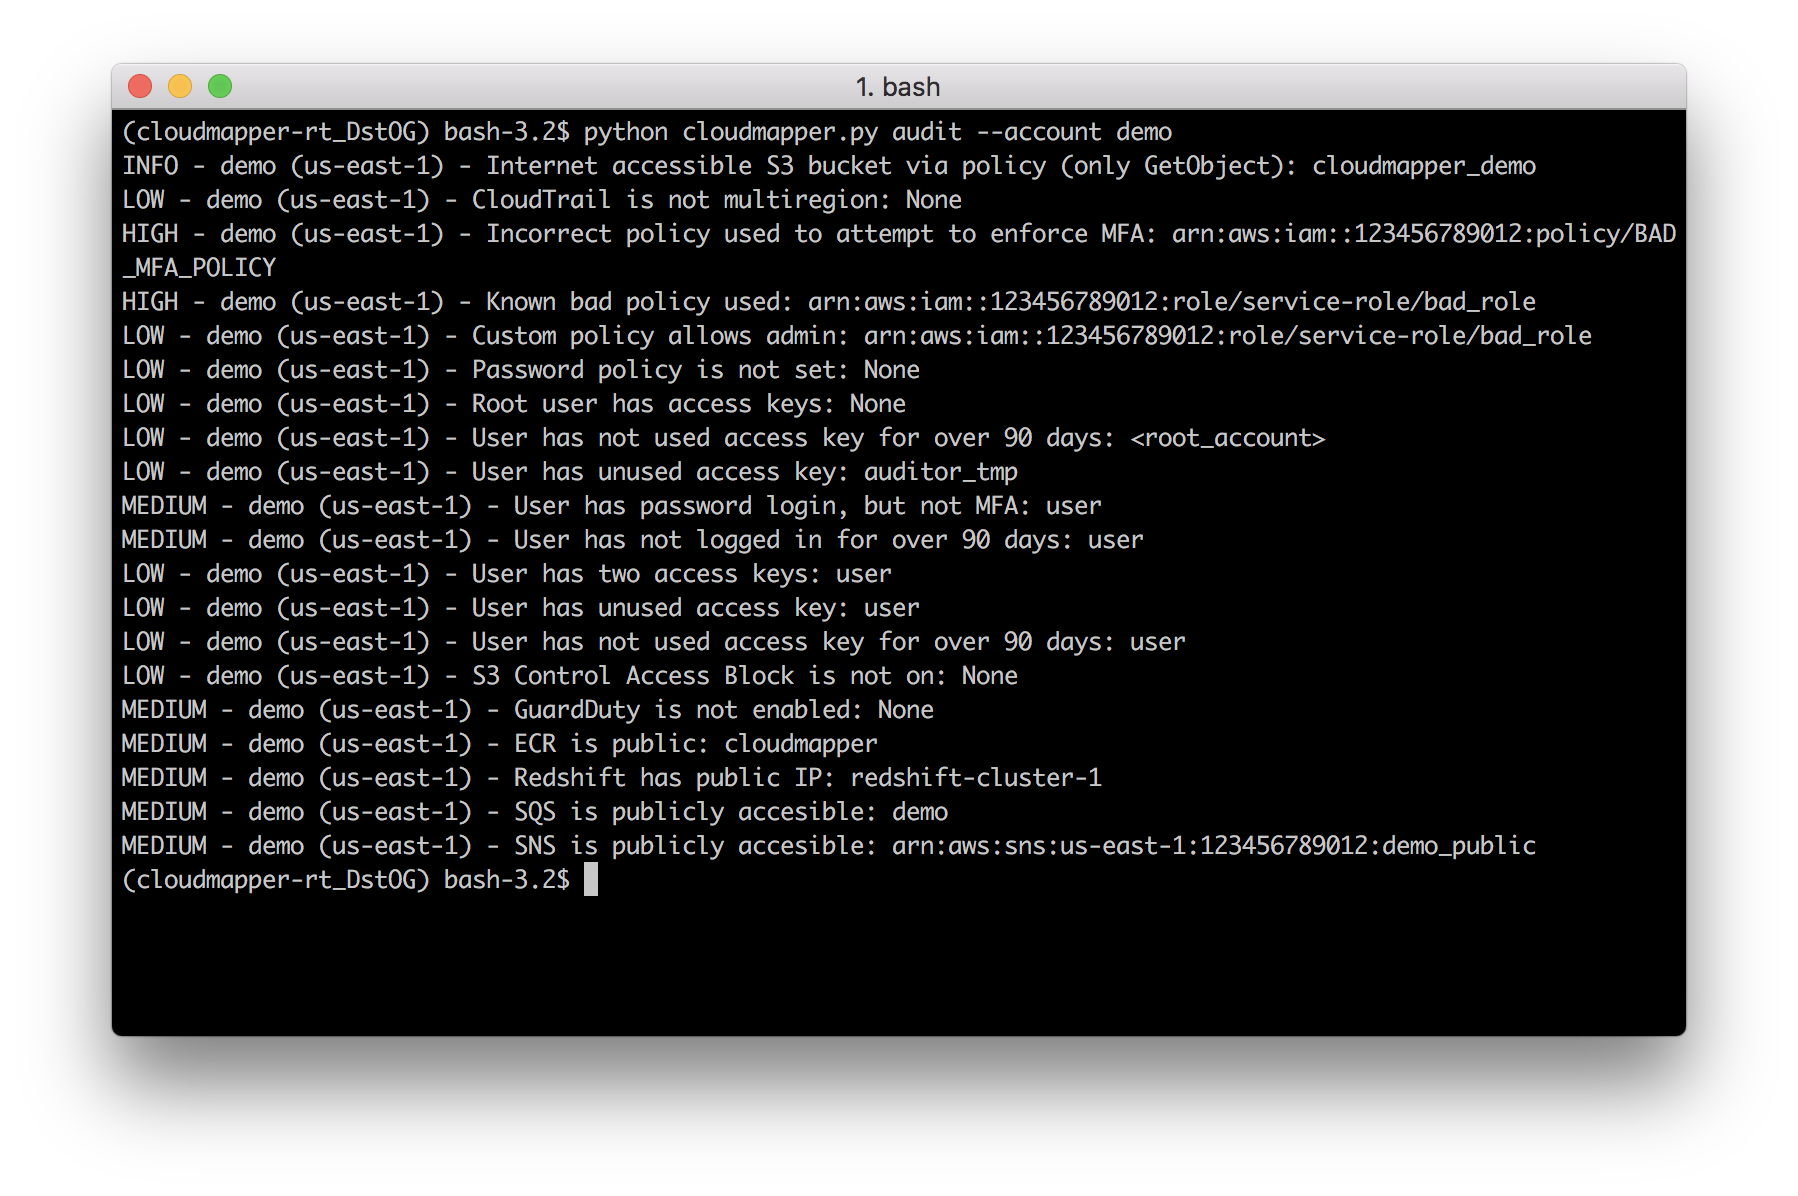
CloudMapper helps you analyze your Amazon Web Services (AWS) environments.
 fairwindsops/polaris
Validation of best practices in your Kubernetes clusters
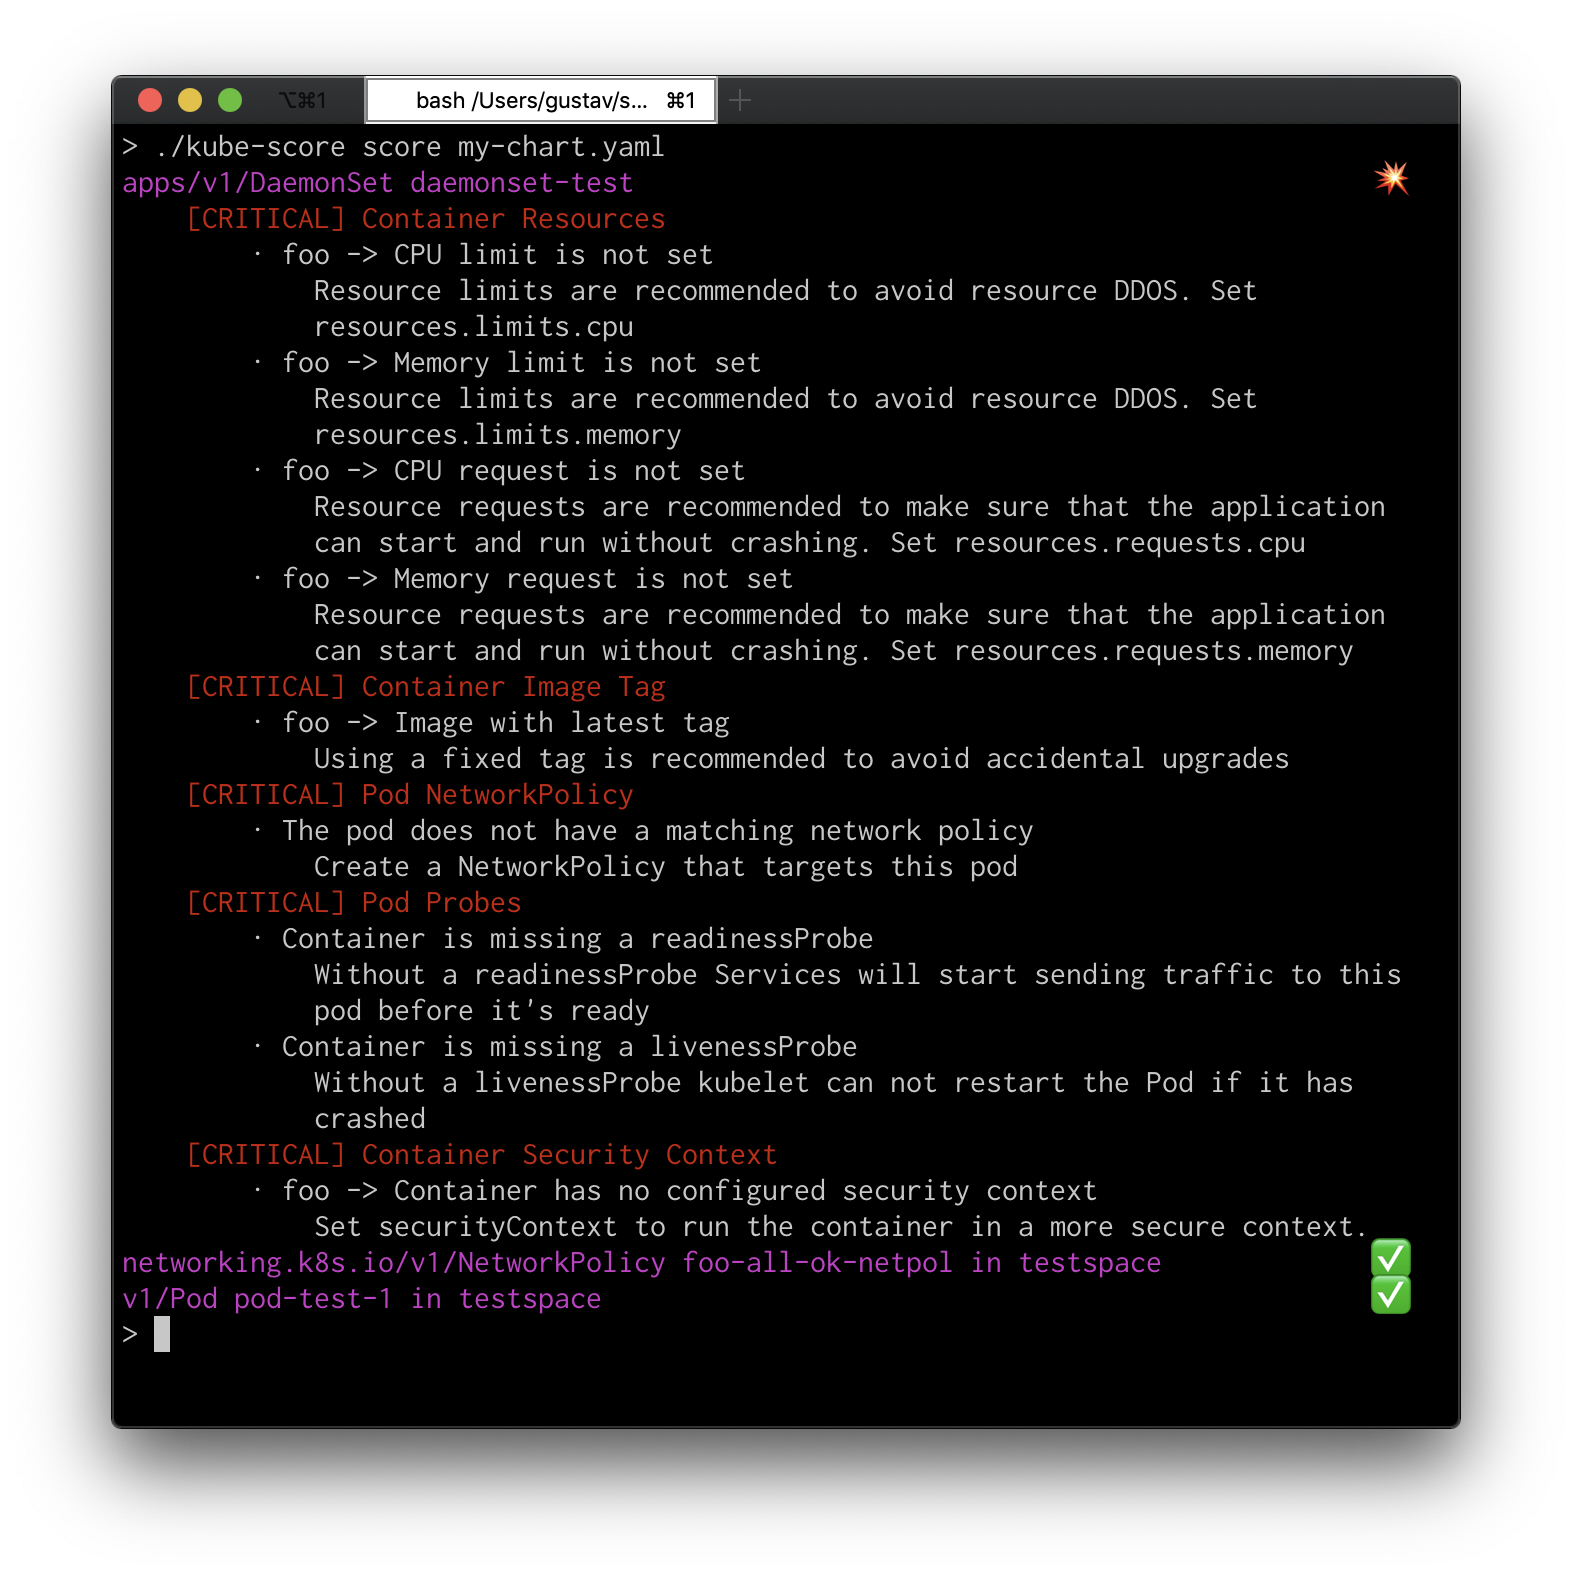 zegl/kube-score
Kubernetes object analysis with recommendations for improved reliability and security. kube-score actively prevents downtime and bugs in your…
 scipag/hardeningkitty
HardeningKitty - Checks and hardens your Windows configuration
 nozaq/terraform-aws-secure-baseline
Terraform module to set up your AWS account with the secure baseline configuration based on CIS Amazon Web Services Foundations and AWS Foundational…
 securitytemplates/sectemplates
Open source templates you can use to bootstrap your security programs
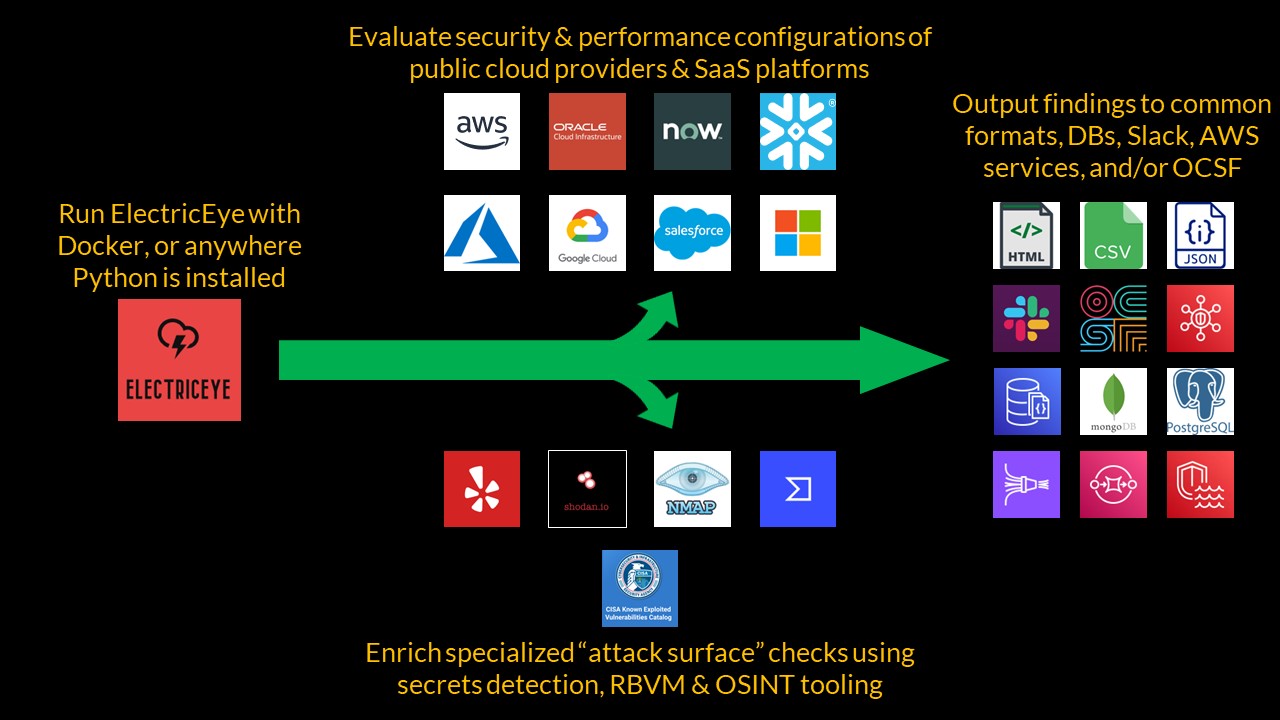 jonrau1/electriceye
ElectricEye is a multi-cloud, multi-SaaS Python CLI tool for Asset Management, Security Posture Management & Attack Surface Monitoring supporting…
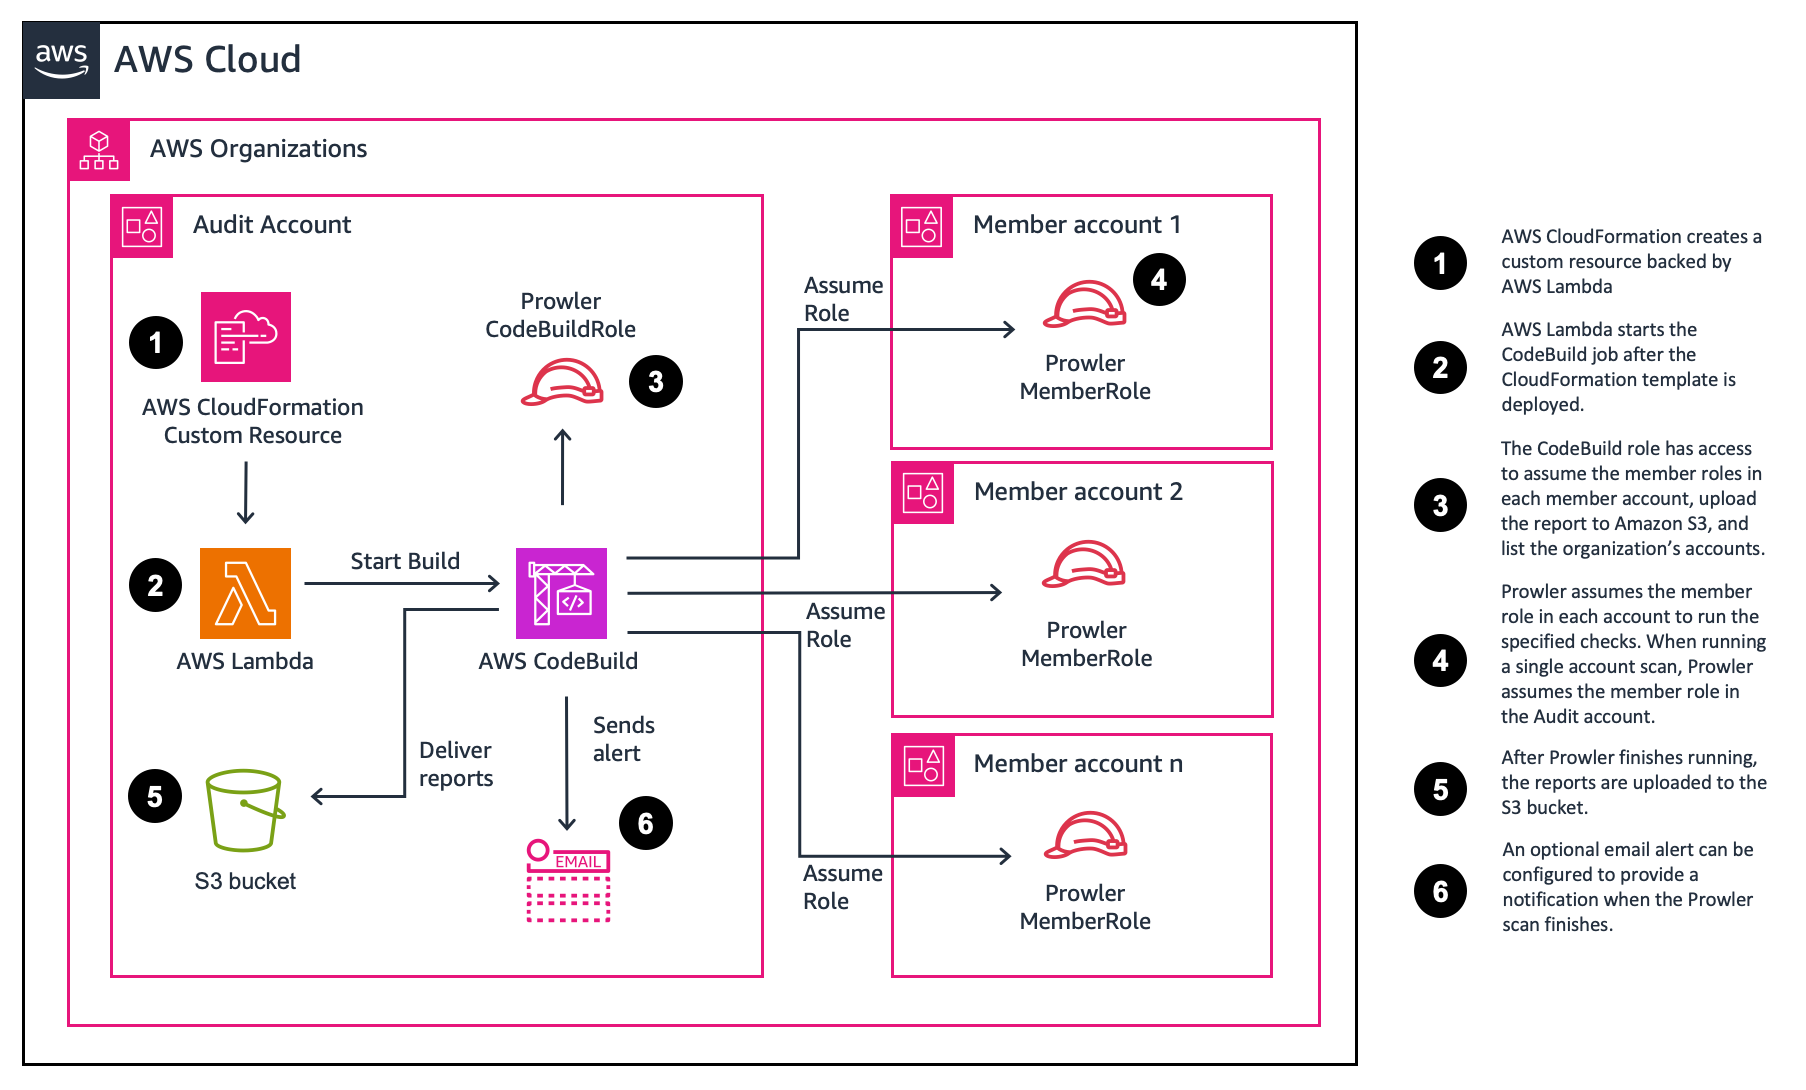 awslabs/aws-security-assessment-solution
An AWS tool to help you create a point in time assessment of your AWS account using Prowler.
 adversis/tailsnitch
A security auditor for Tailscale configurations. Scans your tailnet for misconfigurations, overly permissive access controls, and security best…
 weaveworks/weave-gitops
Weave GitOps is transitioning to a community driven project! It provides insights into your application deployments, and makes continuous delivery…
 shiftleftsecurity/sast-scan
Scan is a free & Open Source DevSecOps tool for performing static analysis based security testing of your applications and its dependencies. CI and…
 legit-labs/legitify
Detect and remediate misconfigurations and security risks across all your GitHub and GitLab assets
 arnica/depsguard
Harden your package manager configs against supply chain attacks.
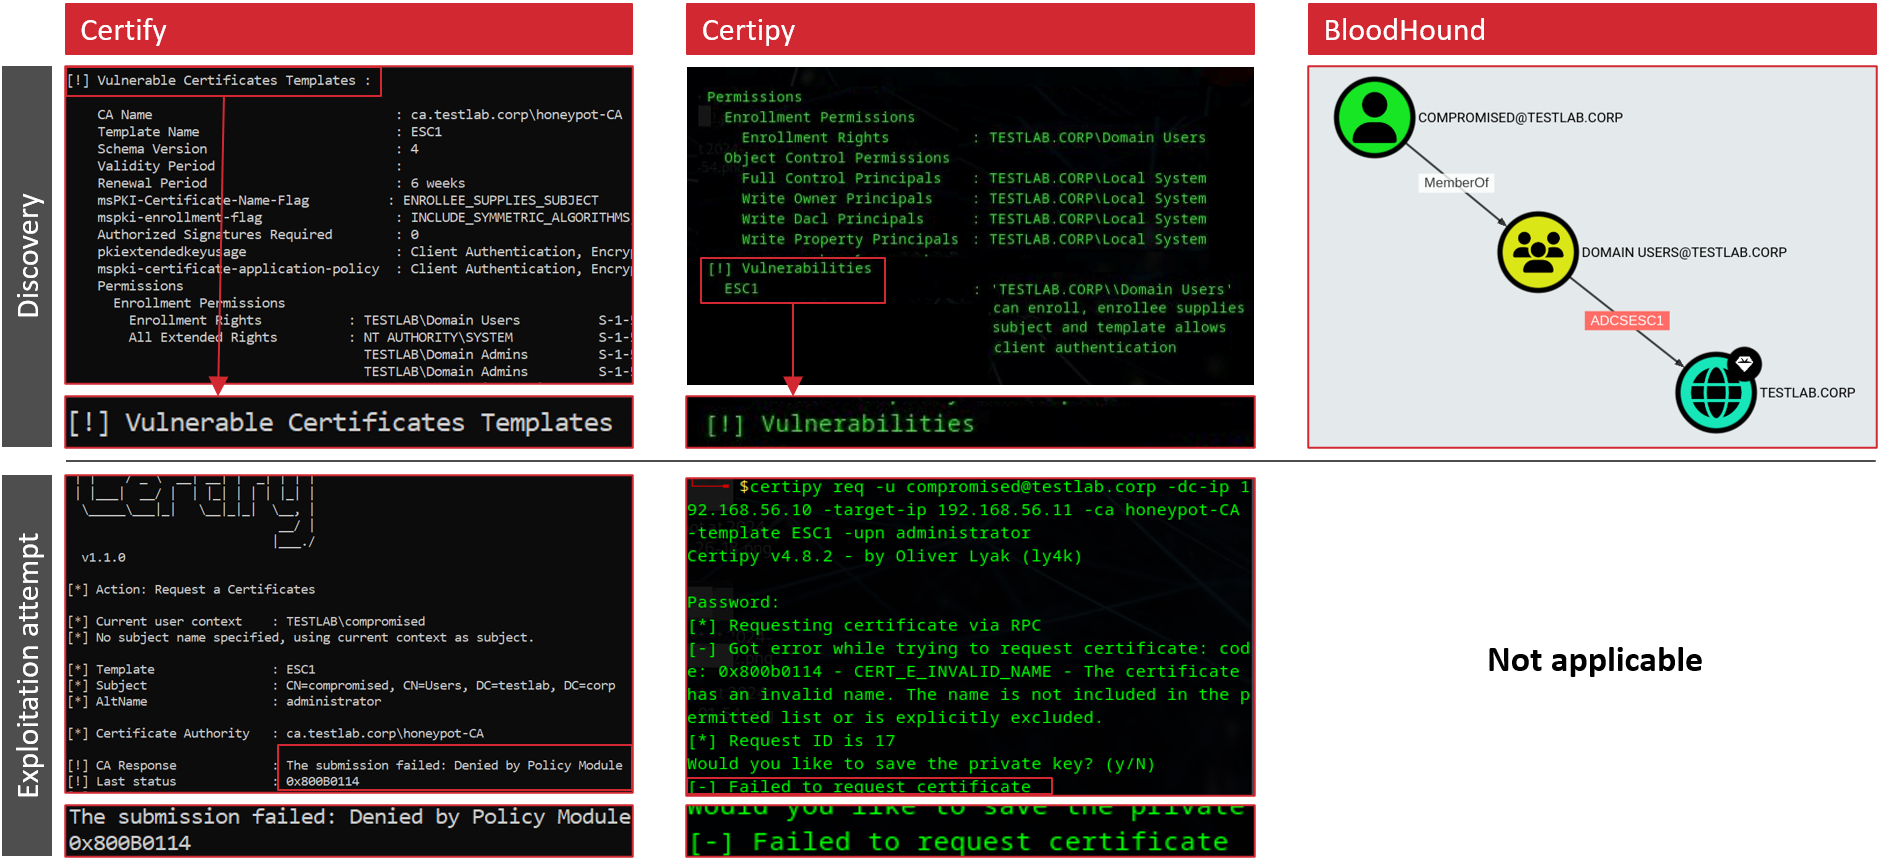 srlabs/certiception
An ADCS honeypot to catch attackers in your internal network.