

 bishopfox/sliver
Adversary Emulation Framework
 ghostmanager/ghostwriter
The SpecterOps project management and reporting engine
 kamalx06/tornadorevc2
Modular post-exploitation framework managing reverse-shell sessions over TCP/TLS/mTLS with plugins for enumeration, in-memory execution, SOCKS5…
 pennyw0rth/netexec
Post-exploitation framework for automated network authentication testing, credential harvesting, and lateral movement across Windows/AD environments…
 nccgroup/steppingstones
Web-based red team activity logging, reporting, and situational awareness tool with Cobalt Strike and BloodHound integration.
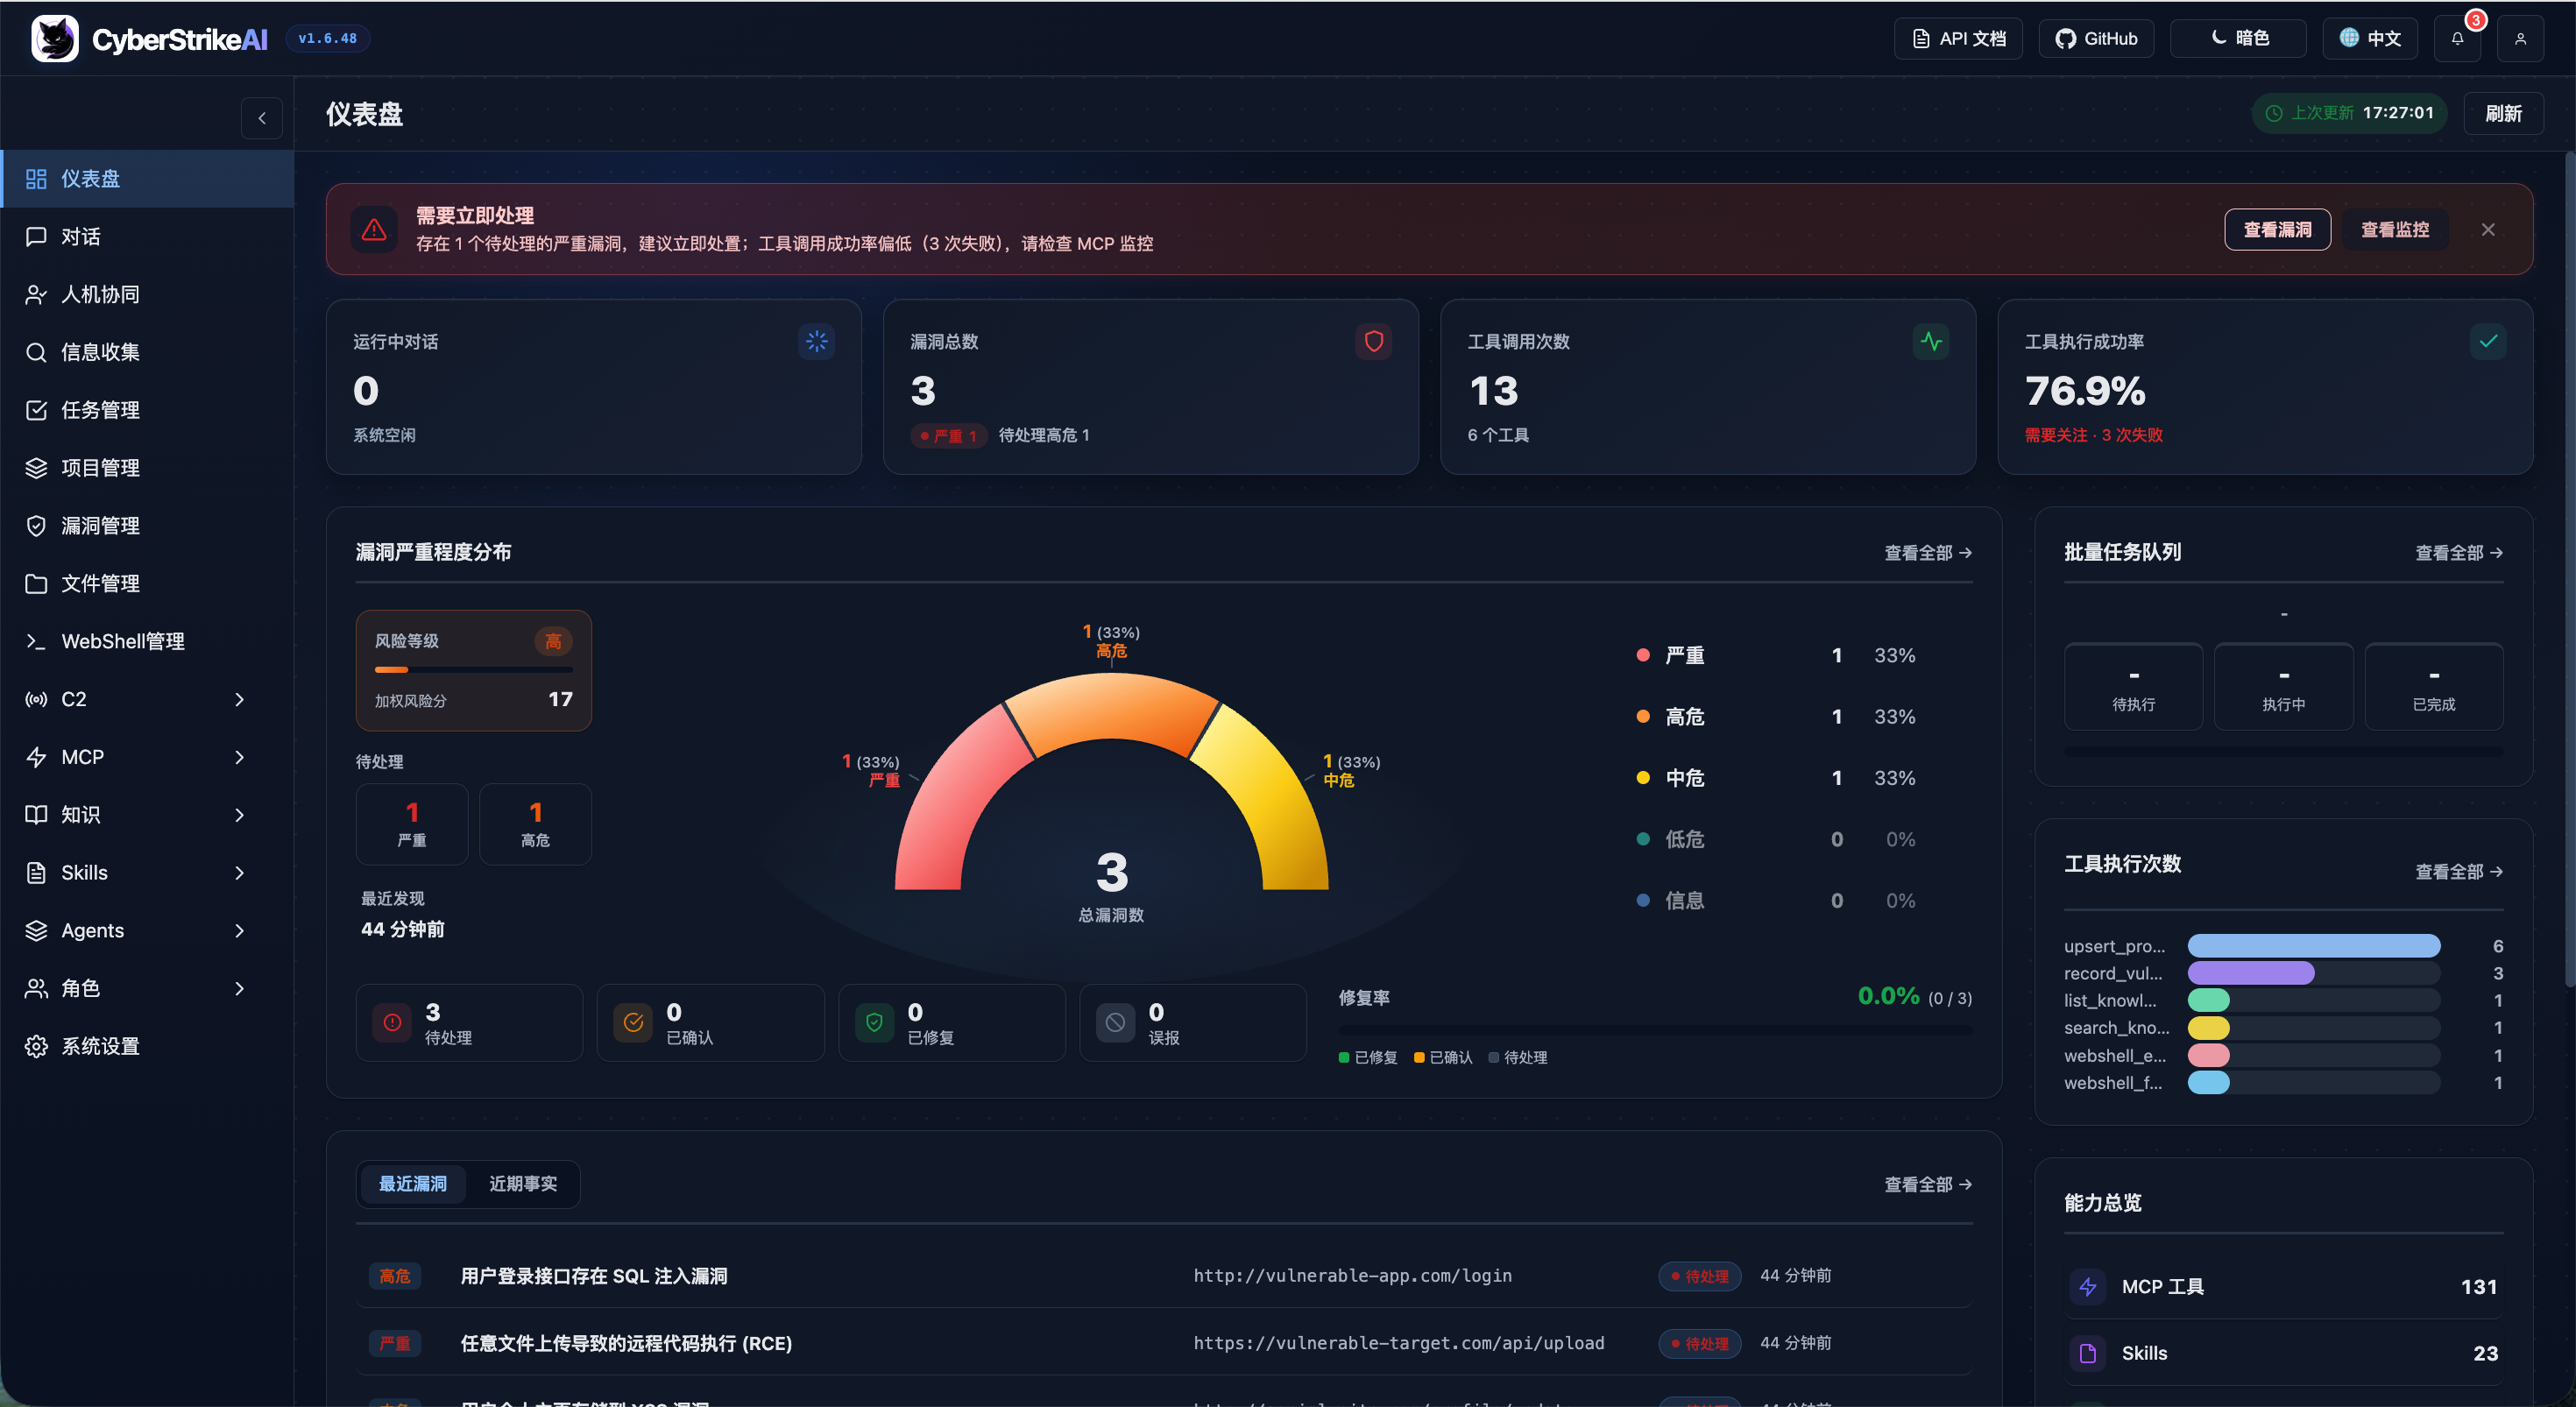 ed1s0nz/cyberstrikeai
The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation…
 joshuagodwin7929/purple-team-automation
Automated adversary emulation (Caldera) against an AD lab to validate Sigma detection coverage and map results to MITRE ATT&CK.
 bigbodycobain/shadowbroker
Real-time geospatial OSINT platform aggregating 60+ public telemetry feeds (ADS-B, AIS, satellites, CCTV) into a unified map with server-side recon…
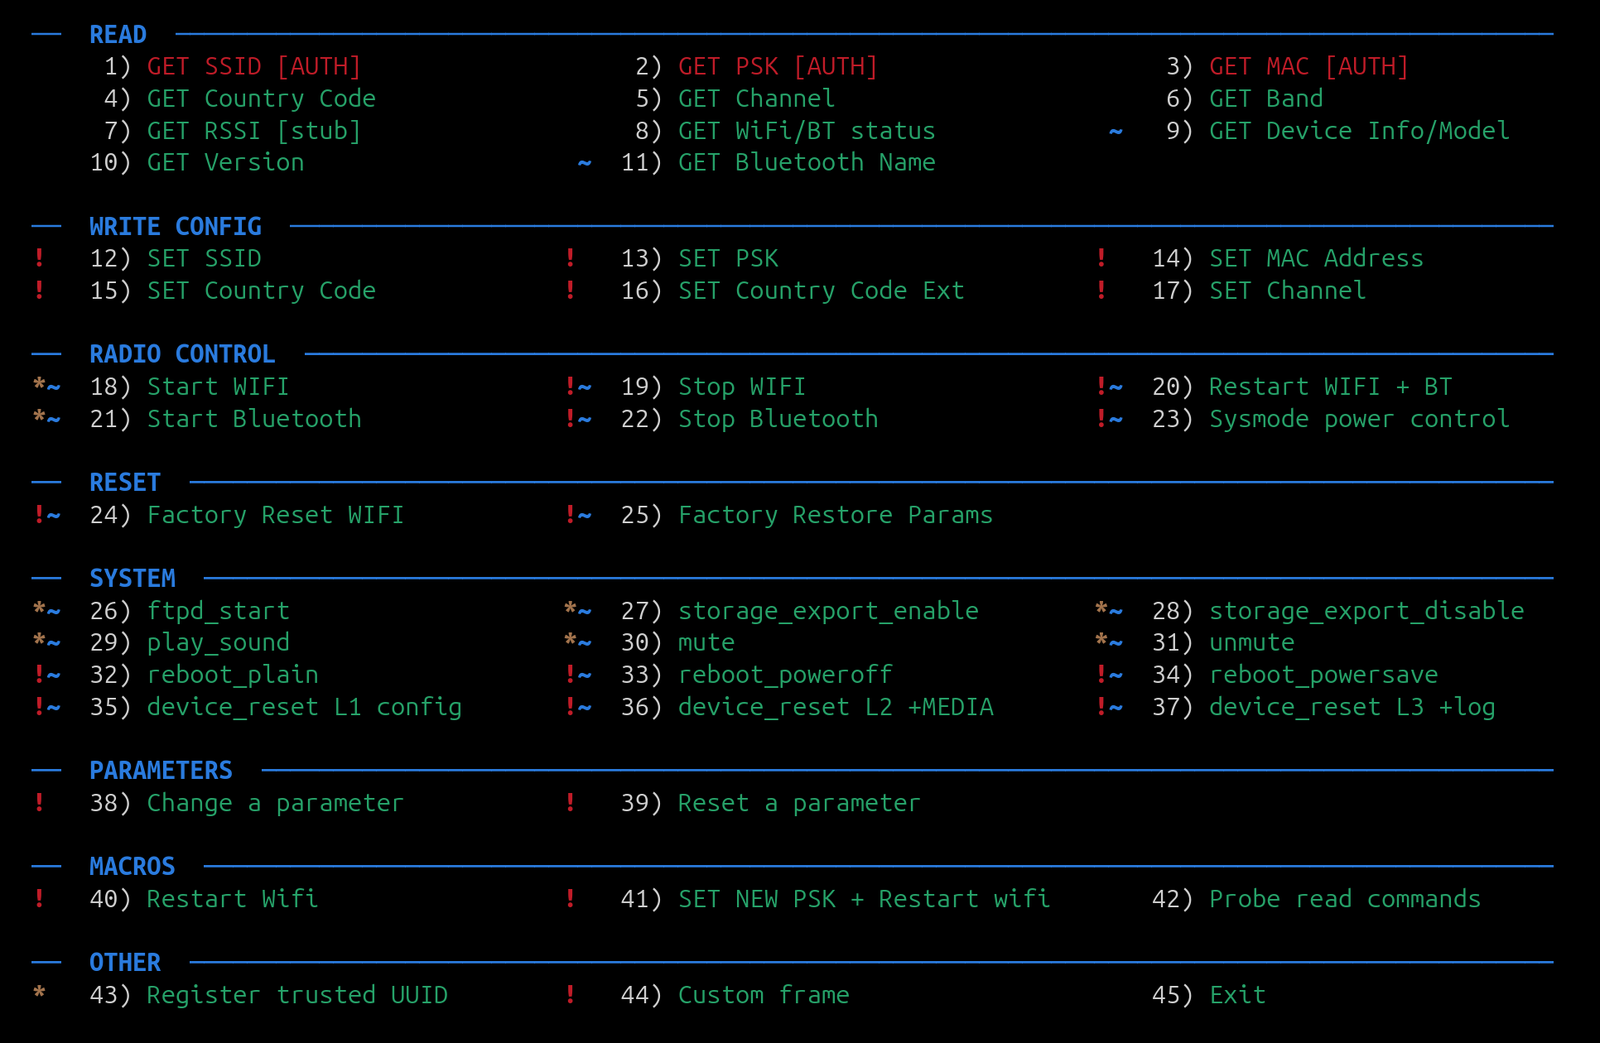 feedbeef/dji_ble_vuln
DJI Drone DUML Command Injection over Bluetooth — Proof of Concept for CVE-2026-78306
 jssngc/ontheedge
Windows research PoC in C that scans Microsoft Edge process memory for credential-related data, with a standalone executable and a BOF variant for C2…
 onyks-os/transparenttorproxy
A Linux CLI utility that transparently routes all system traffic through the Tor network using nftables. It enables rapid IP rotation and easy…
 rmhowe425/poc-cve-2026-93674
Python proof-of-concept exploit for CVE-2026-93674, an authenticated blind command injection in Langflow, enabling remote shell command execution via…
 studiomeyer-io/mcp-server-attestation
Layer-2 supply-chain hardening for MCP servers — Ed25519-signed tool manifests, runtime spawn-attestation, default-deny argument sanitizer. Defends…
 kaandemir993/purerat-msbuild.exe--c2-extraction--net-evasion-analysis
Reverse engineering analysis of PureRAT RAT abusing msbuild.exe, extracting C2 infrastructure, .NET evasion APIs, file system manipulation, and…
 mr-in4inci3le/sliver-gui
A desktop operator console for Sliver C2, built with Wails. Provides a native, lightweight GUI interface for Sliver by directly interfacing with its…
 yarrick/iodine
Tunnel IPv4 data through DNS servers to bypass firewall restrictions and provide covert network access for penetration testing.
 buter-chkalova/rvbbit-arsenal
Offensive & defensive Linux kernel security research focused on rootkit behavior, observable artifacts and detection.