

CyberStrikeAI
 ed1s0nz/cyberstrikeai
The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation…
ai-securitybinary-analysiscloud-security+9
8.2k
ed1s0nz/cyberstrikeaiThe system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation…
 stillbigjosh/adaptix-serverless-c2
Serverless C2 transport plugin for AdaptixC2 v1.2 using AWS Lambda + DynamoDB as the relay infrastructure.
 kaandemir993/nwh-stealer-analysis-fileless-bun-runtime-execution-clipboard-image-theft-cloud-c2-aws-r2-
Static analysis and payload extraction of NWH Stealer. Features deep dive into fileless execution via Bun JavaScript Runtime, in-memory clipboard…
 aipentest/cyberstrikeai
The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation…
 node9-ai/node9-proxy
Access control for AI agents. Set what Claude Code, Codex, Gemini, Cursor and any MCP server are allowed to do, review risky actions before they run,…
 mafifrizi/ares
Autonomous red-team engagement platform with MITRE ATT&CK module orchestration, DAG attack-path solving, OPSEC controls, encrypted credential vault,…
 sliverarmory/sliver-gui
Cross-platform Electron GUI for the Sliver C2 framework, providing session and beacon dashboards, payload generation, listeners, loot, and cloud…
 lame-projects/stratum-c2
Cloud dead-drop C2 framework — RSA-4096 + AES-256-GCM, 5 cloud providers, Rust-only agents, P2P mesh, persistence engine, credential harvesting
 devzero-security/redstackpro
A canvas for red team infrastructure and cyber ranges. Compose a topology, export runnable Terraform and Ansible, and deploy it yourself. Your cloud…
 nccgroup/steppingstones
Web-based red team activity logging, reporting, and situational awareness tool with Cobalt Strike and BloodHound integration.
 devzero-security/redstack
Terraform-deployed red team operator lab on AWS: Mythic, Sliver, and Adaptix C2 behind a production-style Apache redirector, with Kali/Windows hosts…
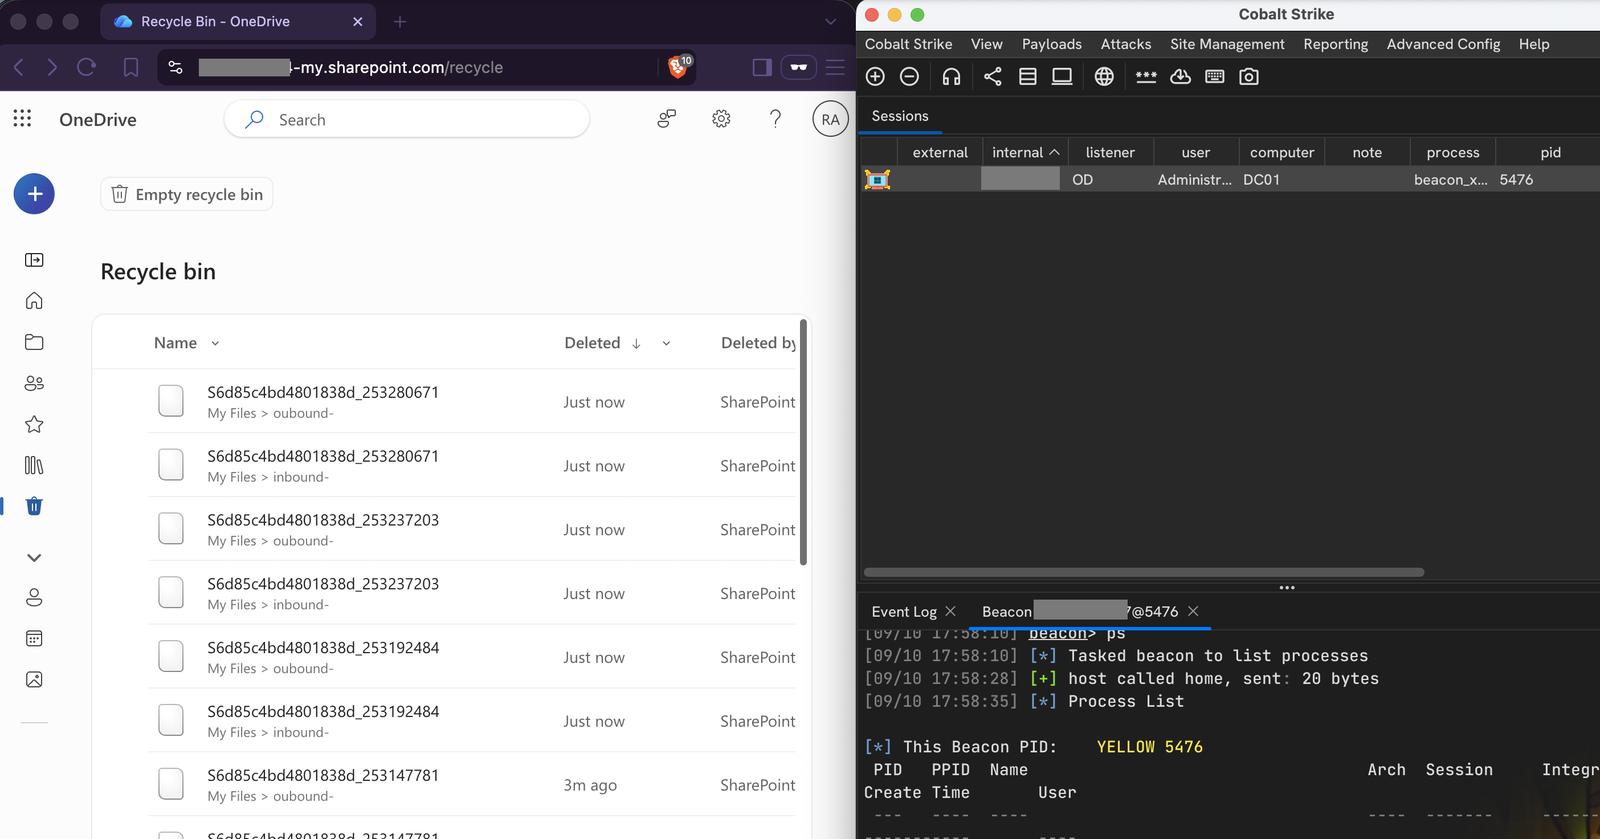 nmht3t/onedrive-udc2
OneDrive as a covert C2 transport for Cobalt Strike
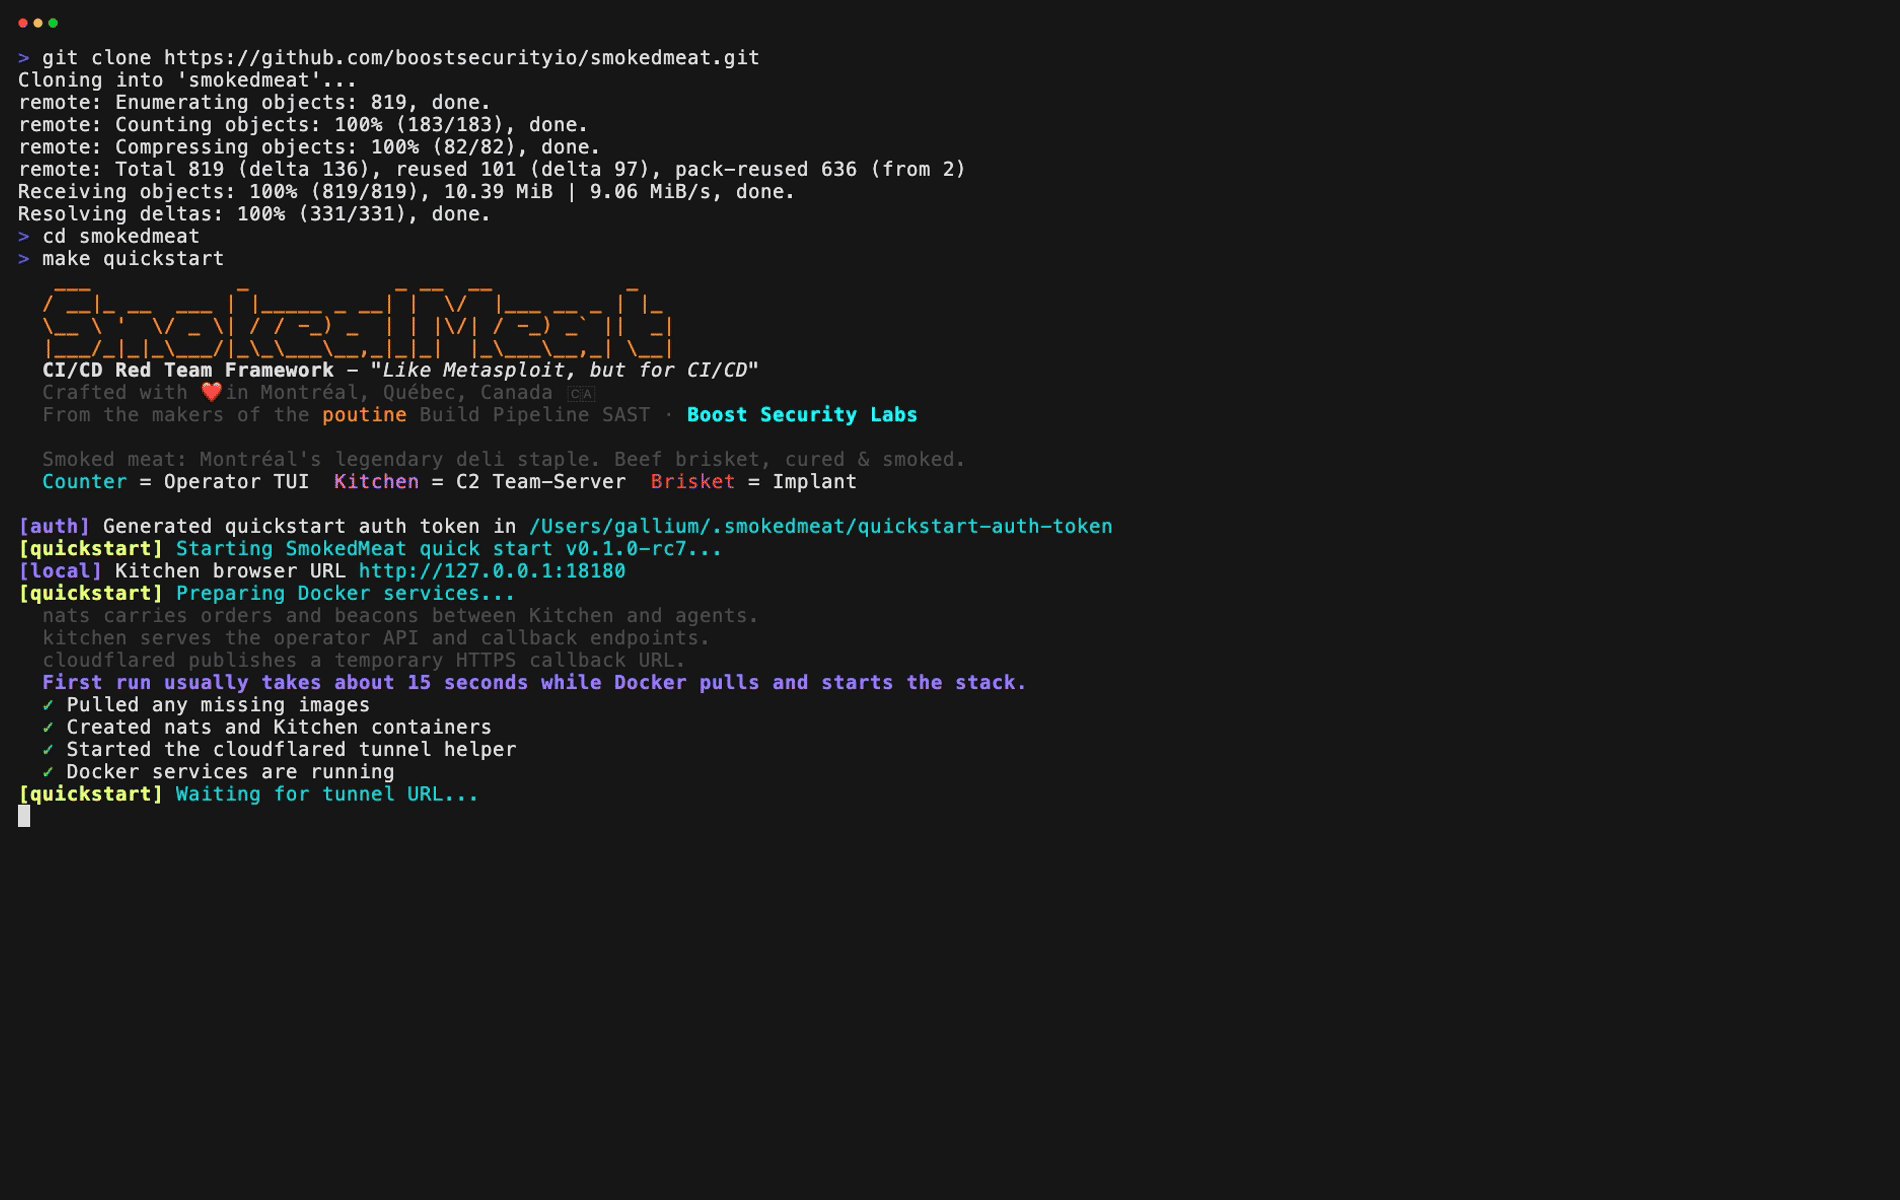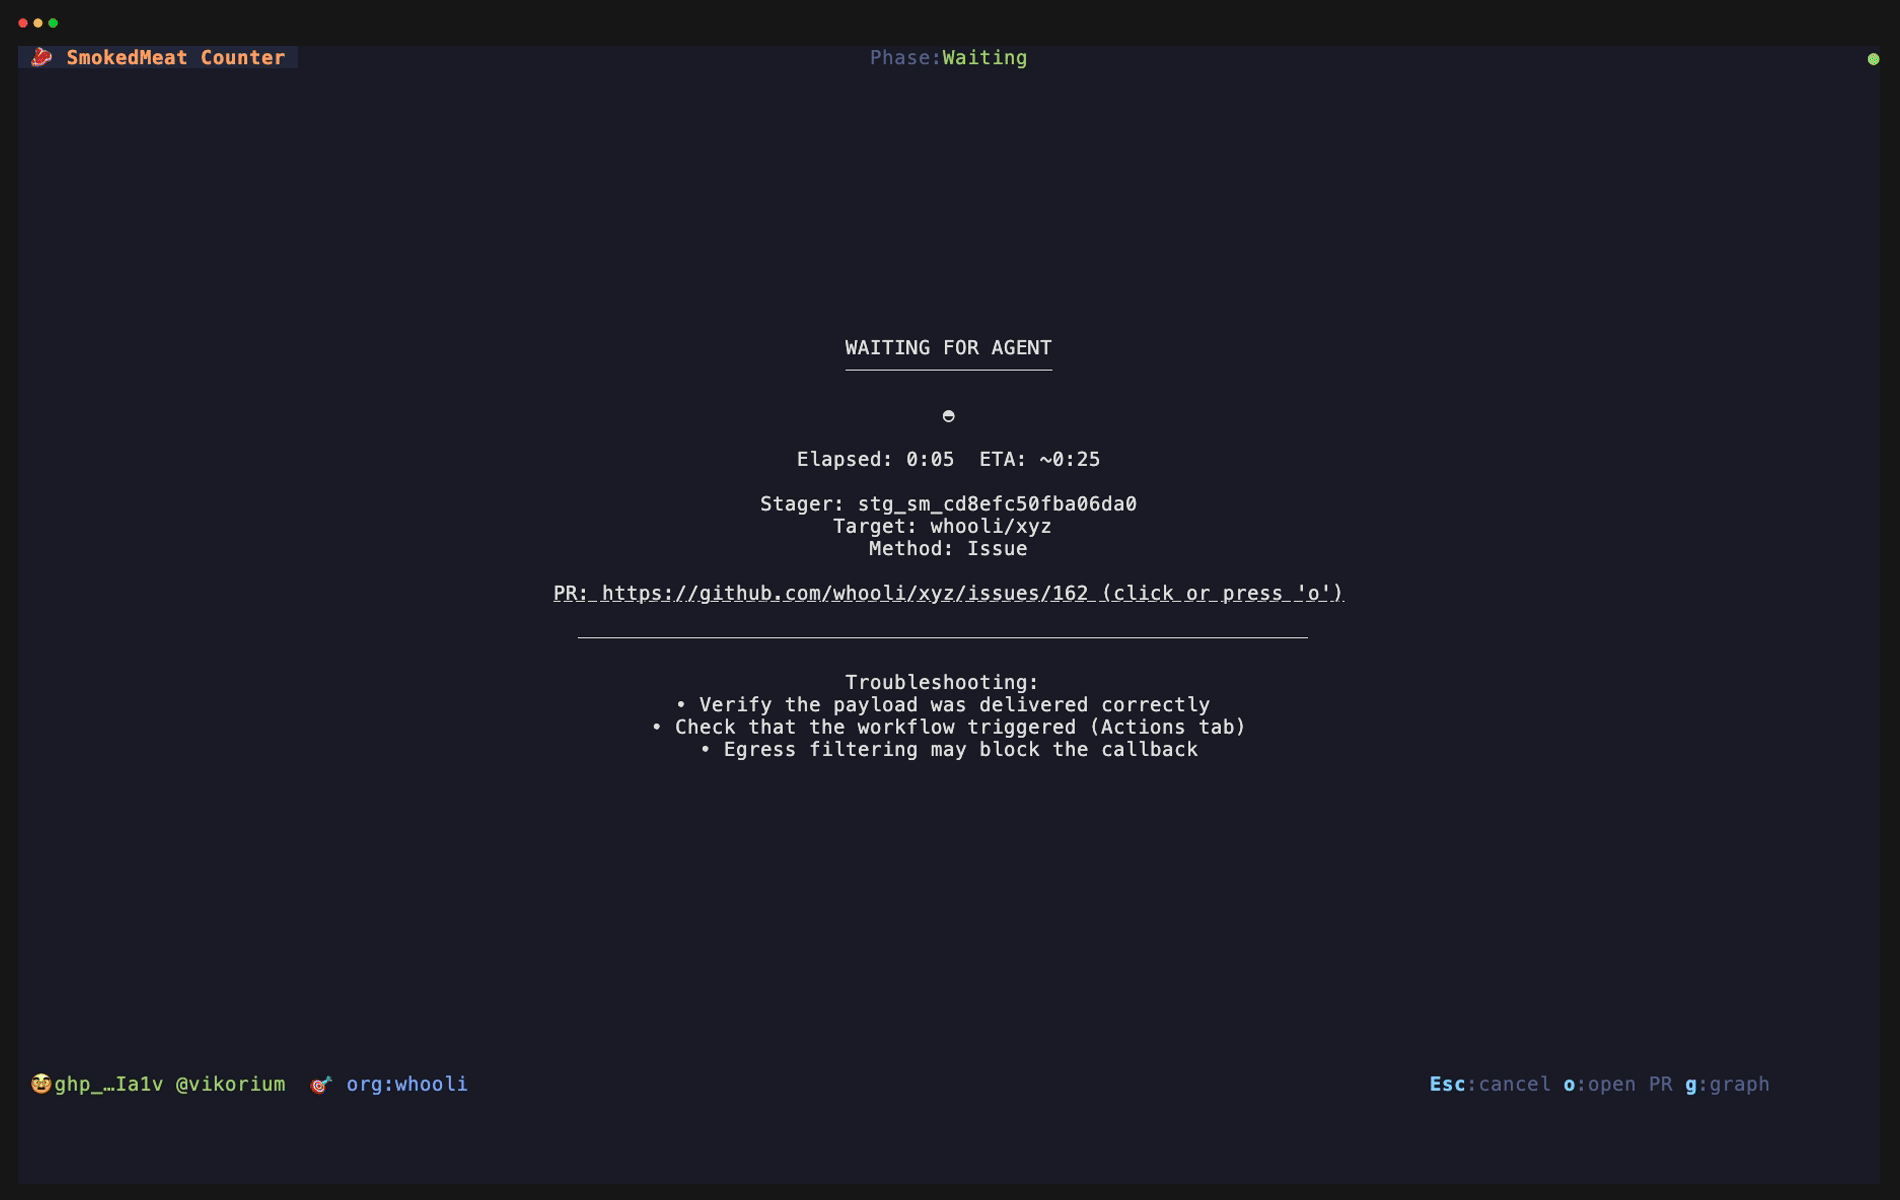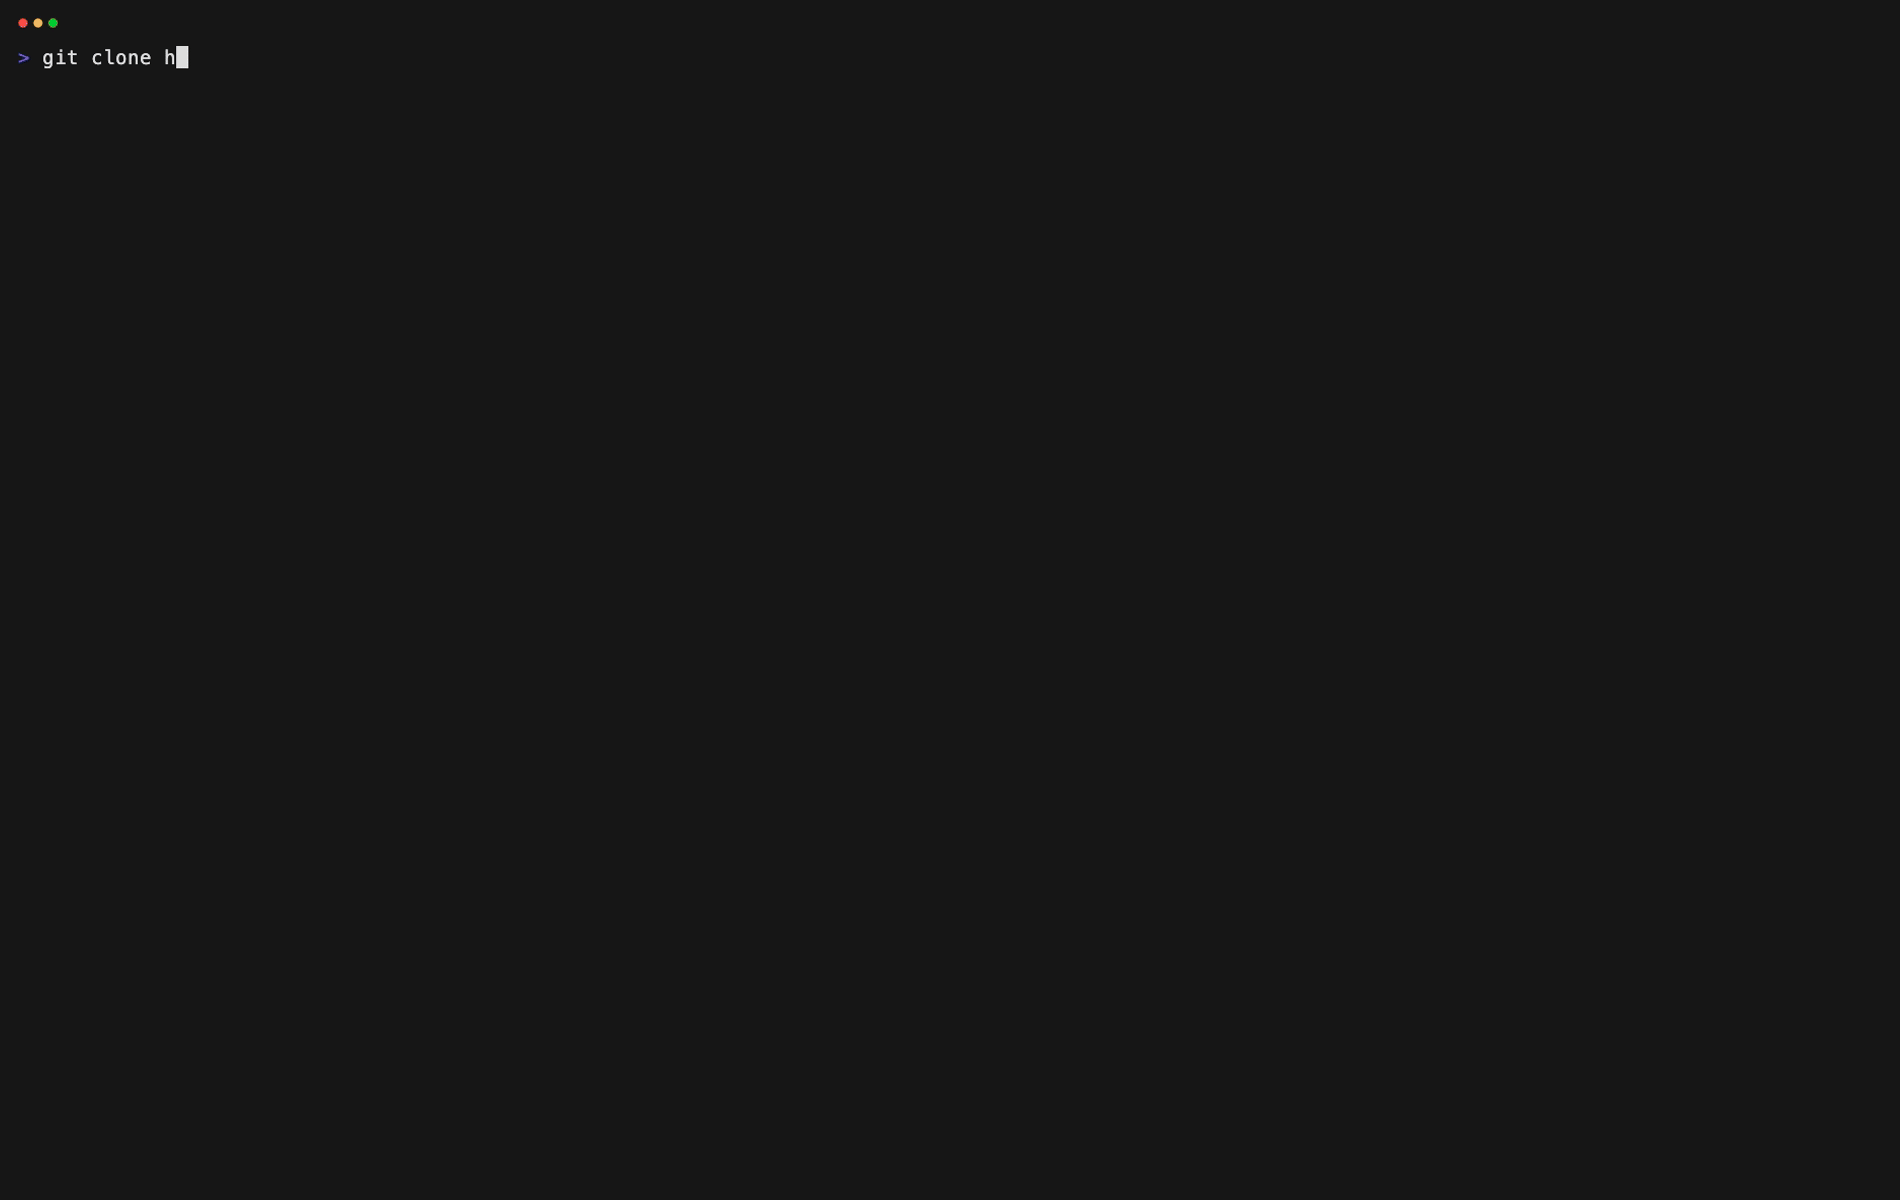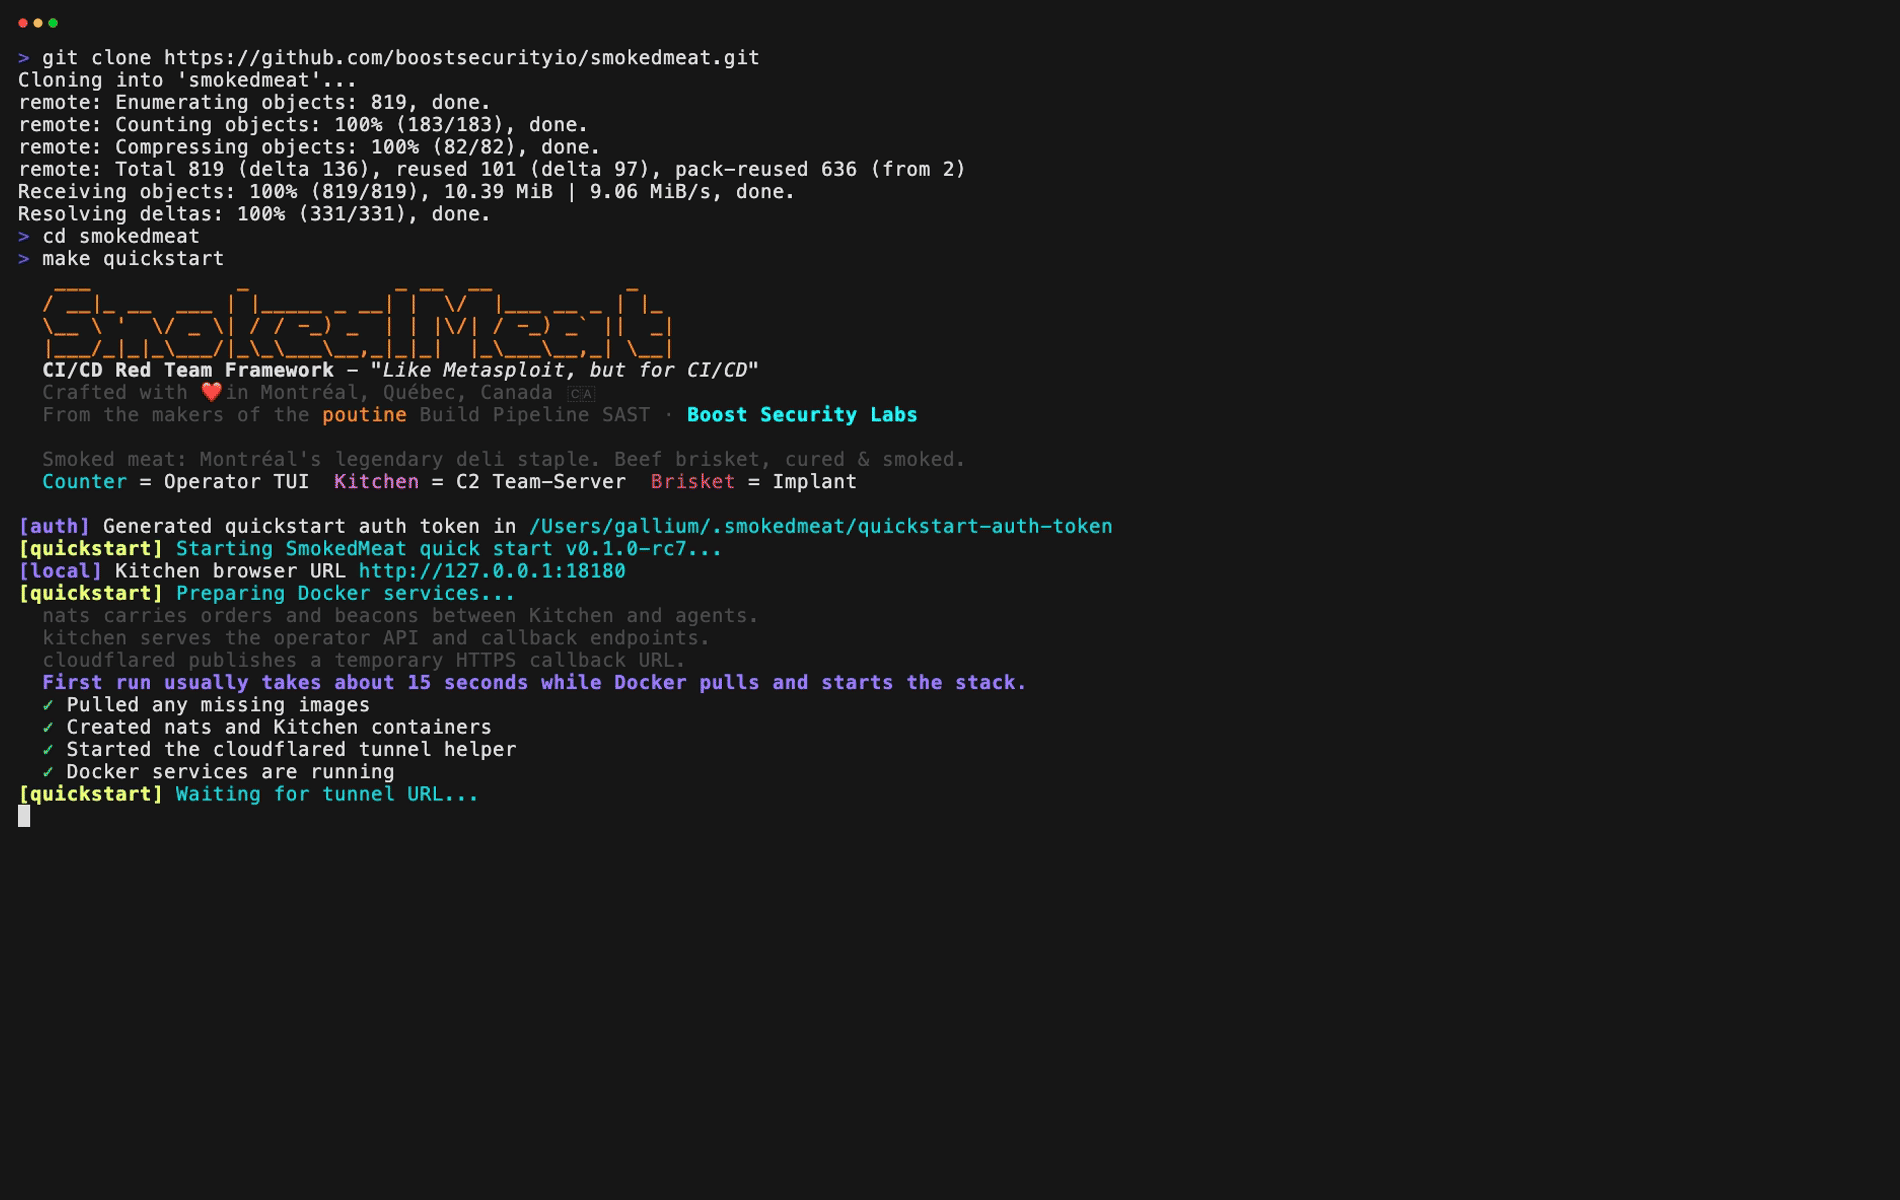 boostsecurityio/smokedmeat
A CI/CD Red Team Framework for demonstrating Build Pipeline security risks.
 cenobyte-vincit/slot2
UEFI GRUB2 bootkit that installs a pre-boot networked implant via NVRAM boot option, chainloads a UKI, executes a dracut payload, and kexecs the…
 galoryber/fawkes
Fawkes is a golang Mythic C2 Agent exclusively written by AI.
 astraljays/traditionaljay
Intentionally vulnerable VM-hosted Java shop — Log4Shell (CVE-2021-44228) workshop lab (EC2 / Azure VM / GCE)
 0xmrma/cve-2026-34048
Admin-only terminal bootstrap routes checked only for login state, which let a normal team member drive Coolify's realtime terminal backend and…
 j4ck3lsyn-gen2/cve-2026-13768
Azure IoT Hub where exposure of an owner-level Shared Access Key enables unauthenticated remote code execution (RCE) against connected IoT devices.…