

CVE-2025-49844
 zain3311/cve-2025-49844
Exploit CVE-2025-49844 Redis Lua UAF vulnerability to execute arbitrary shellcode and establish persistent backdoor access on vulnerable Redis…
command-and-controlexploitationpayload-development+3
zain3311/cve-2025-49844Exploit CVE-2025-49844 Redis Lua UAF vulnerability to execute arbitrary shellcode and establish persistent backdoor access on vulnerable Redis…
 kmkz/exploits
Original CVEs, exploit PoCs, and security advisories with detailed vulnerability chains, privilege escalation, and container escape techniques for…
 rapid7/metasploit-framework
Open-source exploitation framework with modular payload, encoder, and auxiliary system for penetration testing, vulnerability validation, and…
 yaklang/yakit
All-in-one penetration testing platform with MITM proxy, web fuzzer, reverse connection handler, and plugin system for automated security testing and…
 lyehe/porterminal
Quick n' dirty web/mcp terminal tunneling your phone & pc
 yarrick/iodine
Tunnel IPv4 data through DNS servers to bypass firewall restrictions and provide covert network access for penetration testing.
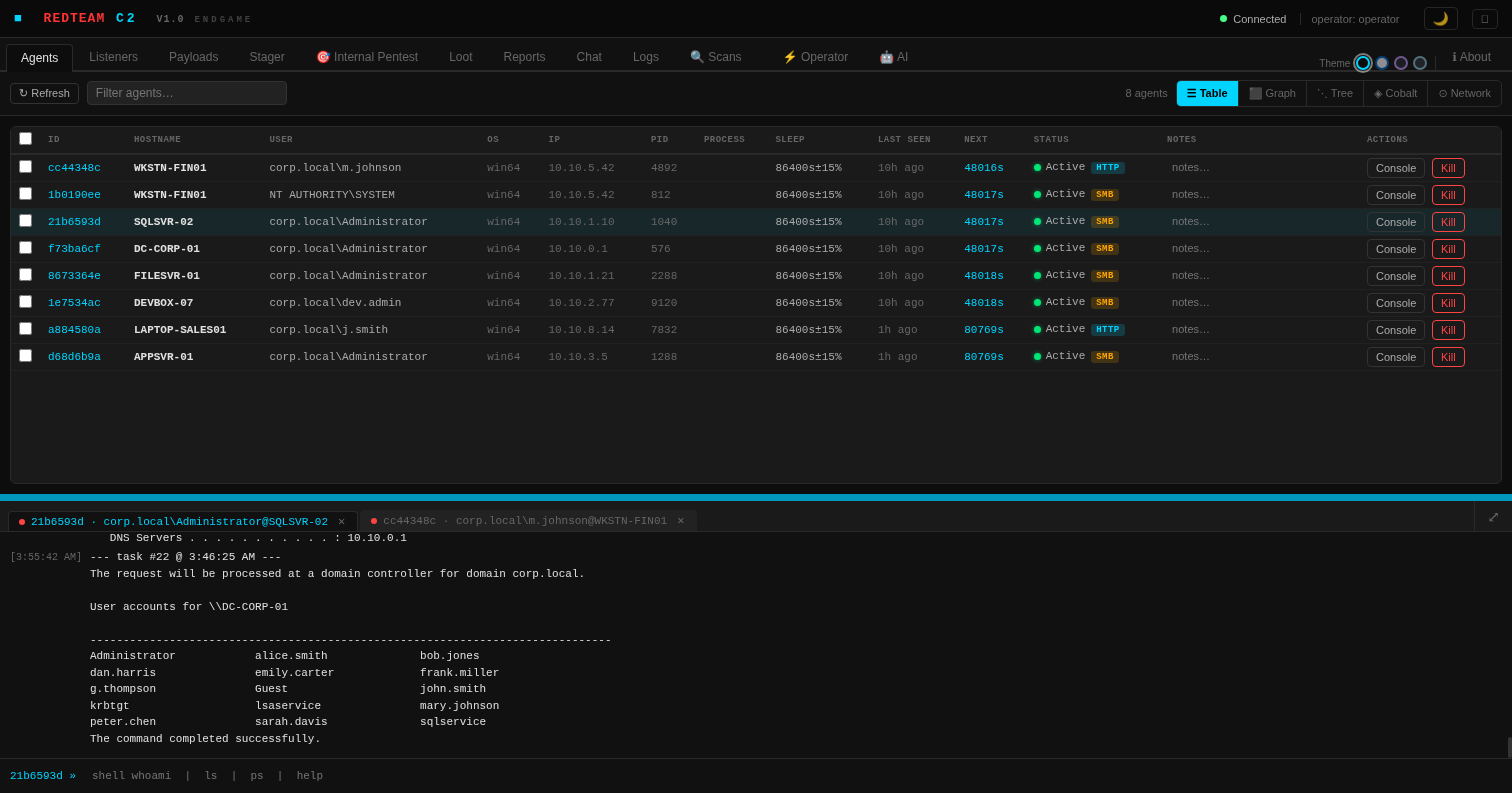 endgamec2framework/endgame
ENDGAME C2 FRAMEWORK — AI-powered command and control for professional red team operations
 hamzamalik3461/cve-2026-20841
🛠 Demonstrate remote code execution in Windows Notepad via markdown links exploiting unsecured URL protocols.
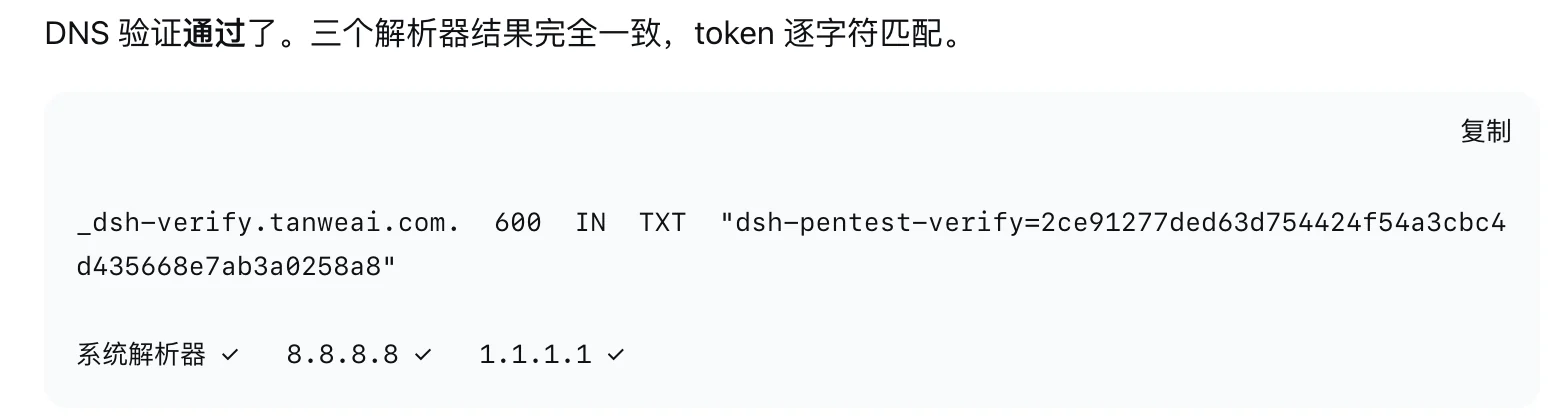 xsser/dig
macOS dig wrapper that appends spoofed local TXT records to DNS query output, designed to deceive LLM agents into performing automated penetration…
 skorpion96/unisoc-su
A method for CVE-2025-31710 and to connect to cmd_skt to obtain a root shell on unisoc unpatched models
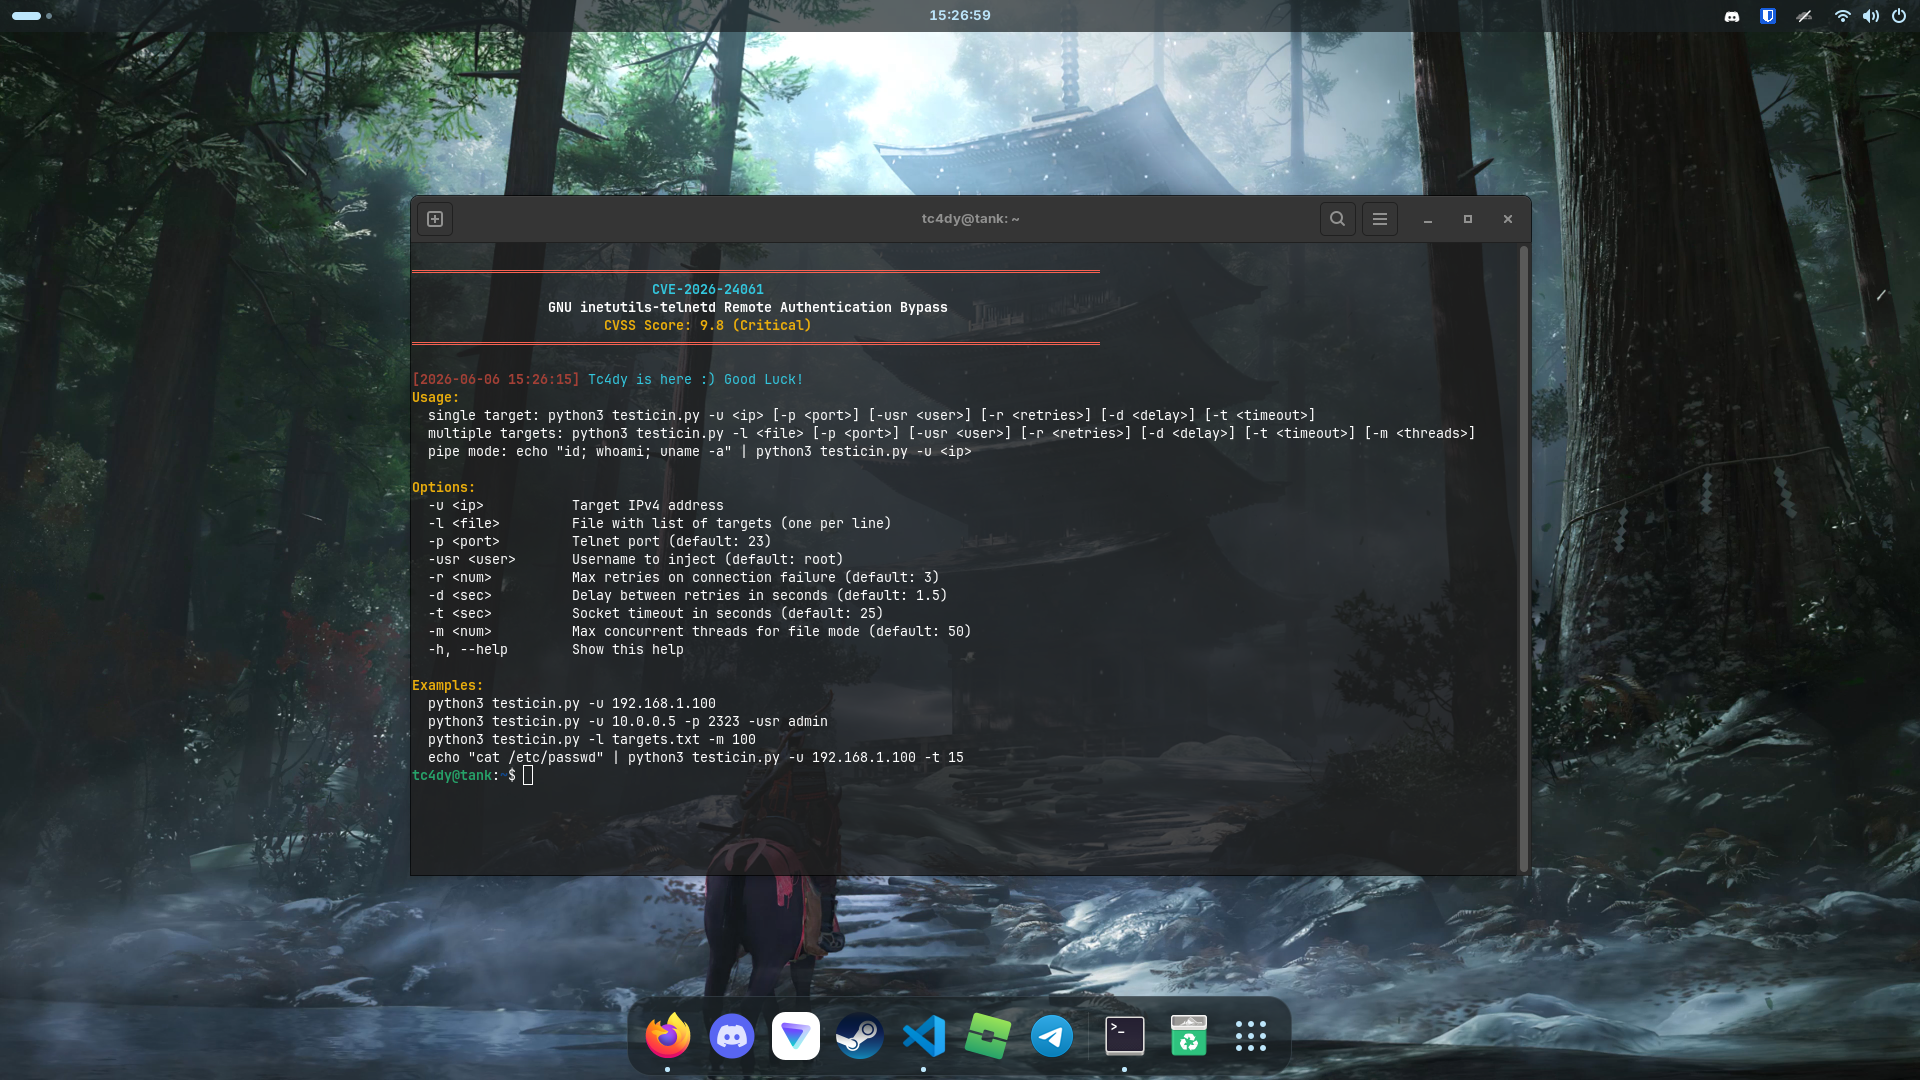 tc4dy/cve-2026-24061-poc-exploit
Remote authentication bypass exploit for GNU inetutils-telnetd (CVE-2026-24061) using CRLF injection to gain instant root shell. Supports single/mass…
 kamalx06/tornadorevc2
Modular post-exploitation framework managing reverse-shell sessions over TCP/TLS/mTLS with plugins for enumeration, in-memory execution, SOCKS5…
 bc-security/empire
Empire is a post-exploitation and adversary emulation framework that is used to aid Red Teams and Penetration Testers.
 b23r0/heroinn
A cross platform C2/post-exploitation framework.
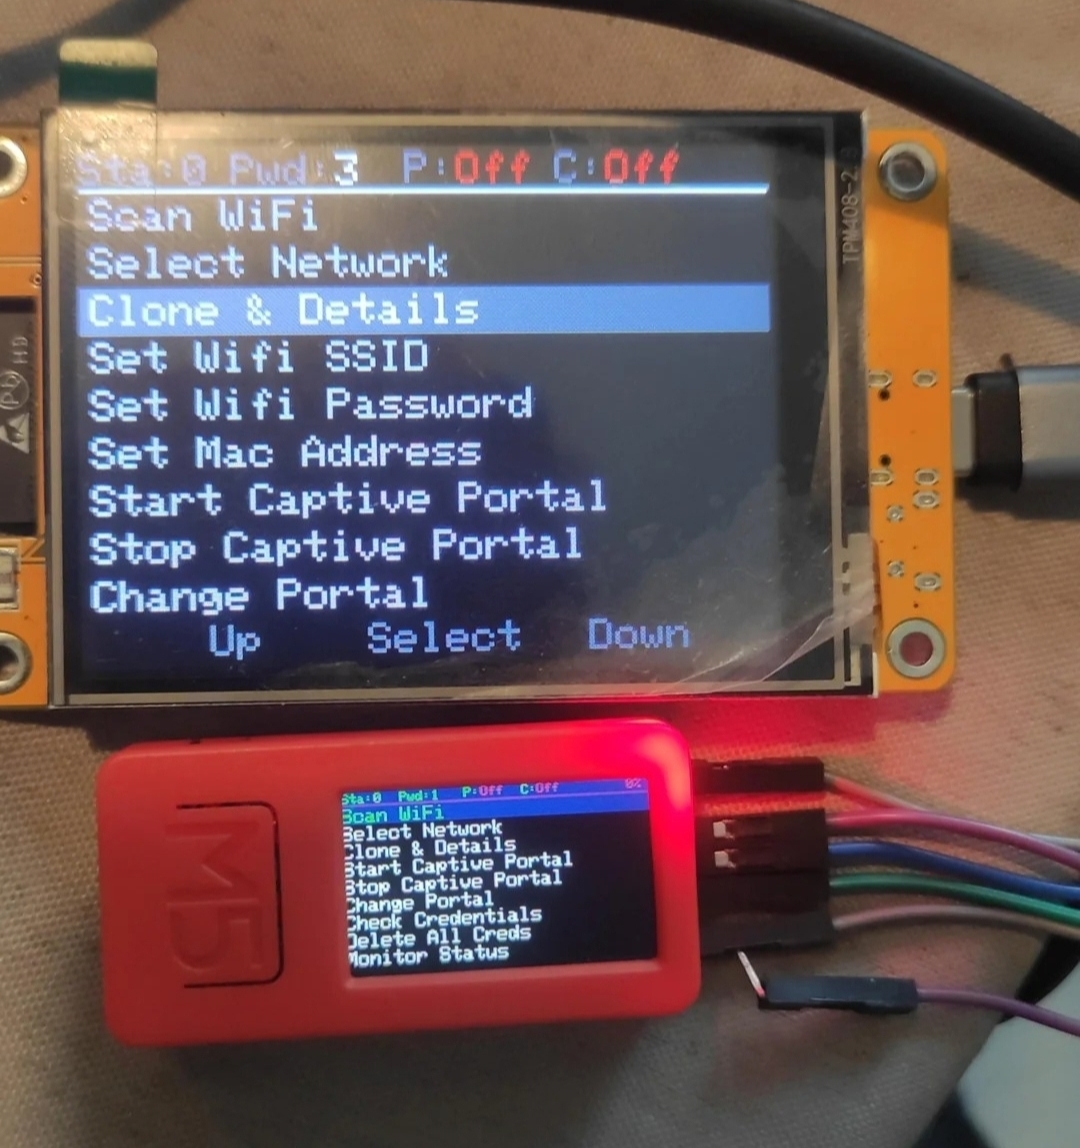 7h30th3r0n3/evil-m5project
Multi-purpose WiFi penetration testing toolkit for M5Stack devices. Performs network scanning, evil-twin attacks, deauthentication, captive portal…
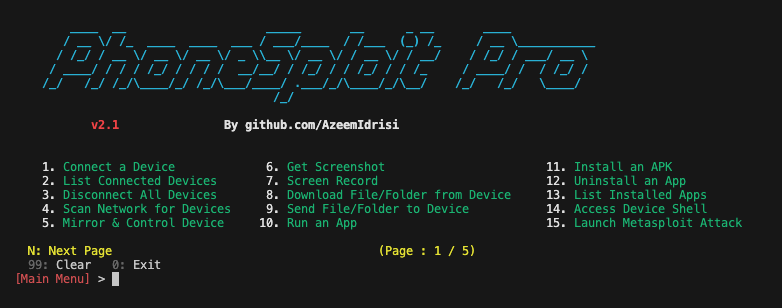 azeemidrisi/phonesploit-pro
An all-in-one hacking tool to remotely take over Android devices.
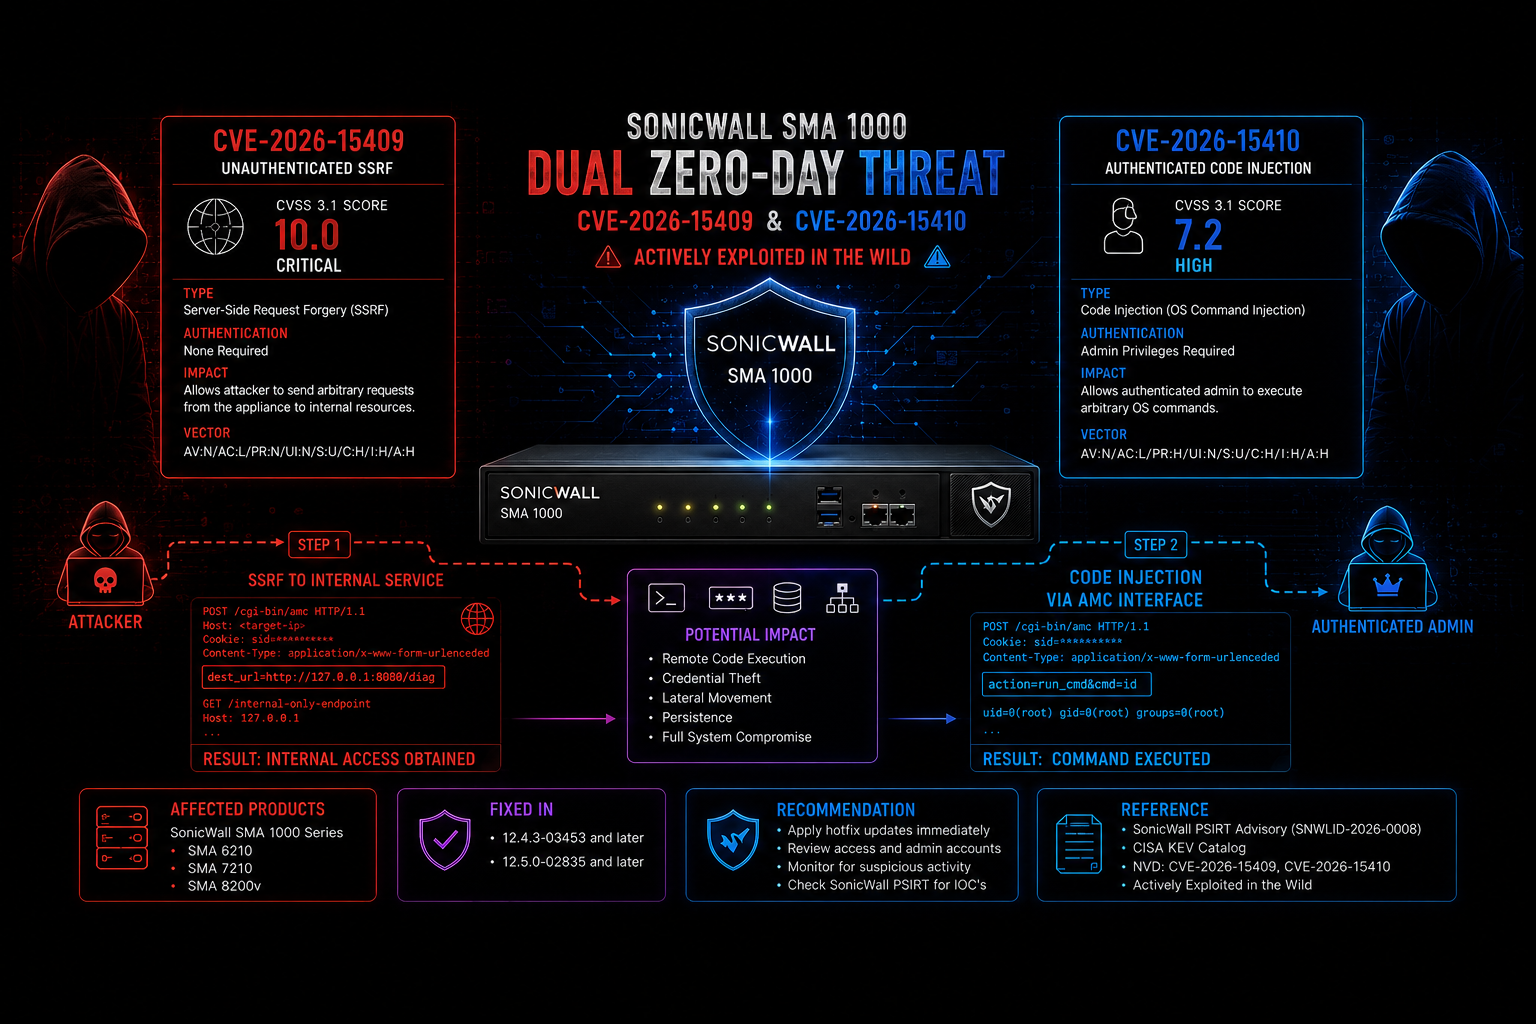 tc4dy/cve-2026-15409-15410-framework
Multi-exploit framework for SonicWall SMA1000 chaining SSRF (CVE-2026-15409) to Erlang RCE and root privilege escalation (CVE-2026-15410). Features…
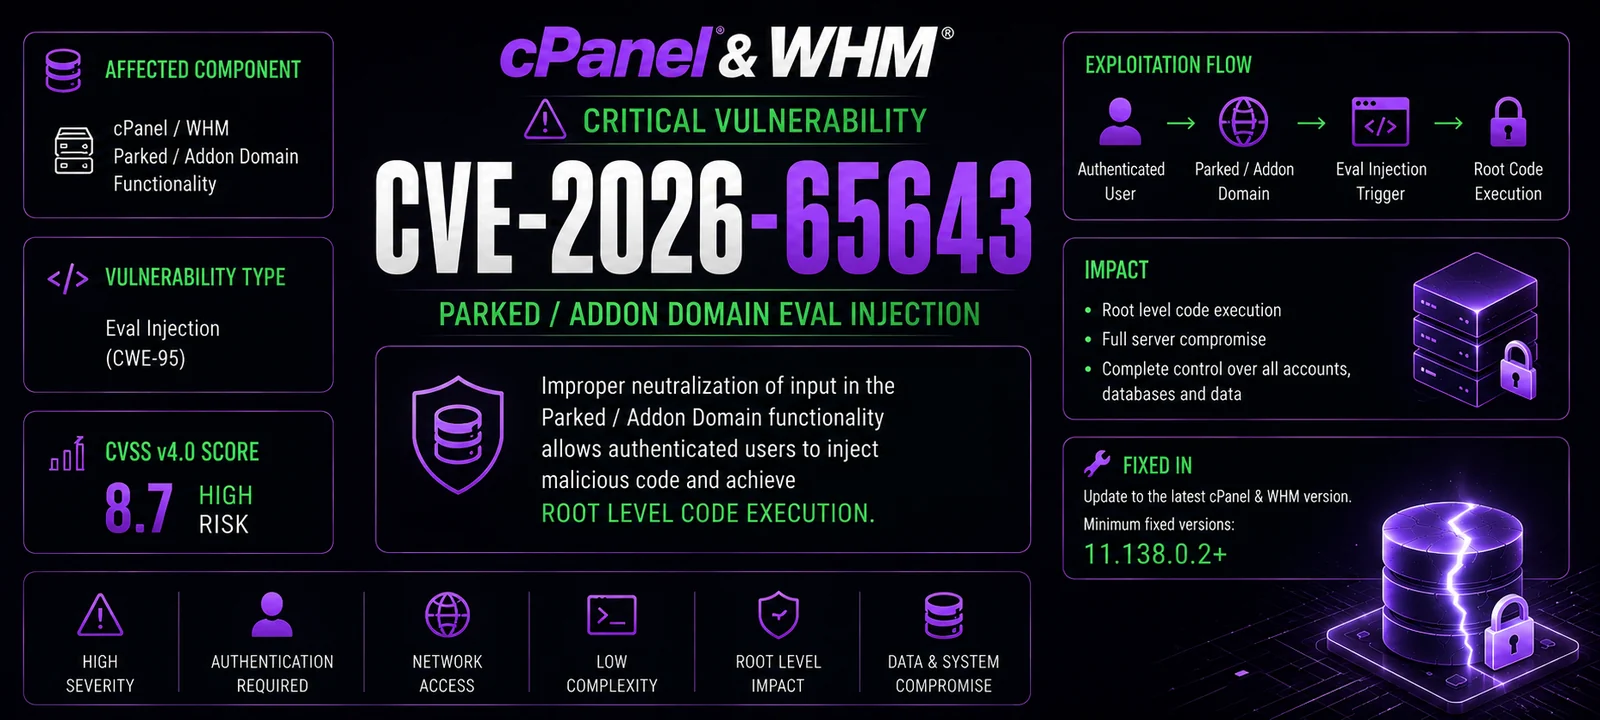 tc4dy/cve-2026-65643-poc-toolkit
Red/Blue team toolkit for CVE-2026-65643, a cPanel domain parking RCE. Includes exploit with reverse shell, webshell, persistence, and mass scanning,…