

Lab-RATS-v1.6
 k4n3co/lab-rats-v1.6
Lab-RATS is a powerful and lightweight Android Remote Administration Tool full of features that enables remote monitoring, management and interaction…
android-securitycommand-and-controldata-exfiltration+8
80
k4n3co/lab-rats-v1.6Lab-RATS is a powerful and lightweight Android Remote Administration Tool full of features that enables remote monitoring, management and interaction…
 karma9874/androrat
A Simple android remote administration tool using sockets. It uses java on the client side and python on the server side
 a-d-team/sharpmemshell
.NET in-memory webshell (memshell) payloads implemented via HttpListener and VirtualPath, compatible with the Godzilla 4.01 post-exploitation…
 abraxas/pfsense-l2tp-radius-mpd
pfSense CE 2.9.0-DEVELOPMENT - High - Remote - RCE - L2TP RADIUS mpd.conf
 abraxas/pfsense-sshguard-crlf
pfSense CE 2.9.0-DEVELOPMENT - High - Remote - RCE - sshguard THRESHOLD CRLF
 capture0x/adstrike
AI-powered modular Active Directory red-team framework for authorized penetration testing, AD enumeration, attack-path analysis, Kerberos/ADCS…
 abraxas/pfsense-wireless-clone
pfSense CE 2.9.0-DEVELOPMENT - High - Remote - RCE - wireless clone ifconfig
 abraxas/pfsense-qinq-parent-if
pfSense CE 2.9.0-DEVELOPMENT - High - Remote - RCE - QinQ parent-if ifconfig
 vqkro/ddossnake
Go load and stress testing tool with L7 HTTP and L4 raw TCP/UDP modes, multi-threaded workers, live rate graph, and a Windows GUI plus cross-platform…
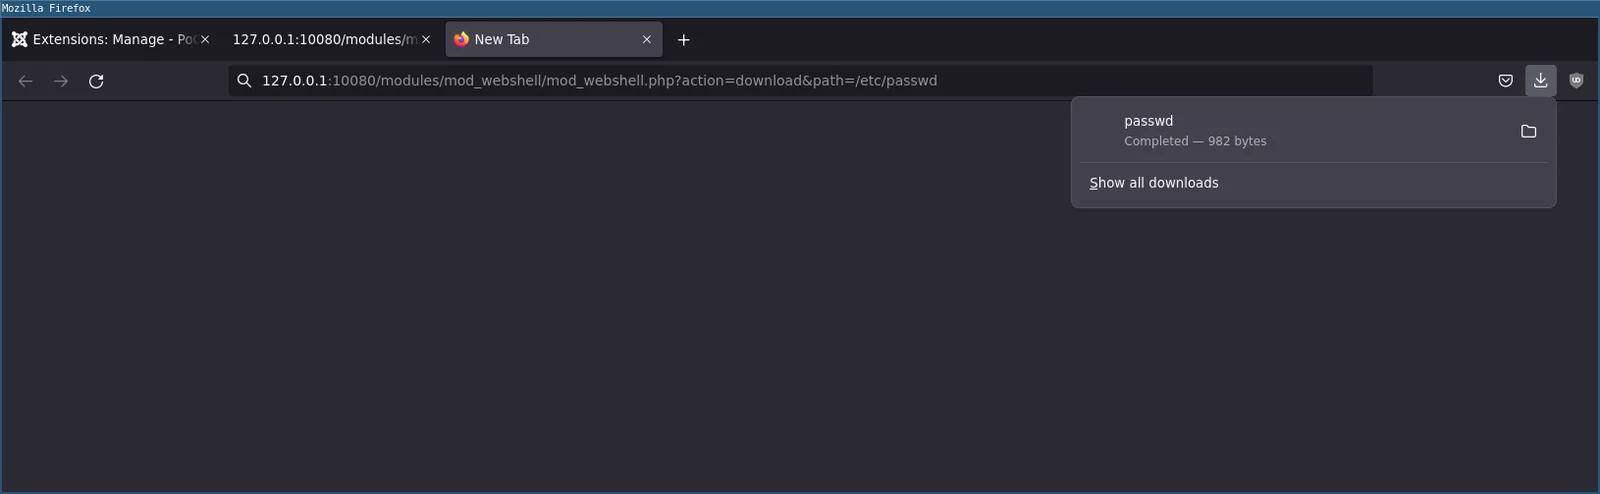 p0dalirius/joomla-webshell-plugin
A webshell plugin and interactive shell for pentesting a Joomla website.
 d4kw1n/cve-2026-102607-zoneminder
Python PoC exploiting CVE-2026-102607, an authenticated OS command injection in ZoneMinder <= 1.38.1 exportEvents() enabling RCE, command output…
 si13nttt/cve-2026-22777
Proof-of-concept exploit chaining CRLF injection in ComfyUI-Manager's config endpoint with an arbitrary git install to achieve unauthenticated remote…
 0asylum/cve-2026-31857
CraftCMS has an RCE vulnerability via relational conditionals in the control panel
 4xura/cve-2026-44011-craftcms-auth-rce
The PoC of CVE-2026-44011: Craft CMS RCE with an authenticated user.
 dennisdgr/cve-2026-44011-poc
Authenticated Craft CMS RCE PoC for CVE-2026-44011
 langz337/cve-2026-63030
Python exploit tool chaining CVE-2026-63030 REST batch-route confusion with CVE-2026-60137 SQL injection to achieve unauthenticated WordPress RCE,…
 hitechcloud-vietnam/cve-2026-41940-poc
Exploits CVE-2026-41940, a cPanel & WHM authentication bypass, to gain root WHM access and run post-exploitation commands, file reads, and account…
 absllk/hexestra
AI-native penetration testing IDE where operators and an AI agent share browser, terminals, traffic capture, shells, asset graph, tasks, and evidence…