threat-modeling-mcp-server

MCP server for structured STRIDE-based threat modeling with automatic code validation, business context analysis, and comprehensive report generation…

MCP server for structured STRIDE-based threat modeling with automatic code validation, business context analysis, and comprehensive report generation…

Formal inter-procedural taint analysis engine for application security. Tracks untrusted data across function boundaries, persistence layers, and…

Threadless Module Stomping In Rust with some features (In memory of those murdered in the Nova party massacre)

Dependency analysis and optimization toolkit for modern JavaScript and TypeScript codebases. Enforce dependency graph hygiene and remove unused code…

IDA Pro plugin for filtering functions by assembly patterns, byte sequences, string/name references, and size constraints, with rule-based search and…

Sandbox untrusted code with safe access to the host.

Scala-based static analysis framework for Android and Java bytecode with flow analysis, decompilation, and native code analysis via symbolic…

Offline secrets scanner combining regex rules, lexer-based semantic analysis, and hashed-value matching to detect exposed credentials in code with…

Laravel RCE Exploit PoC - CVE-2021-3129 (user-friendly with automatic log path detection)

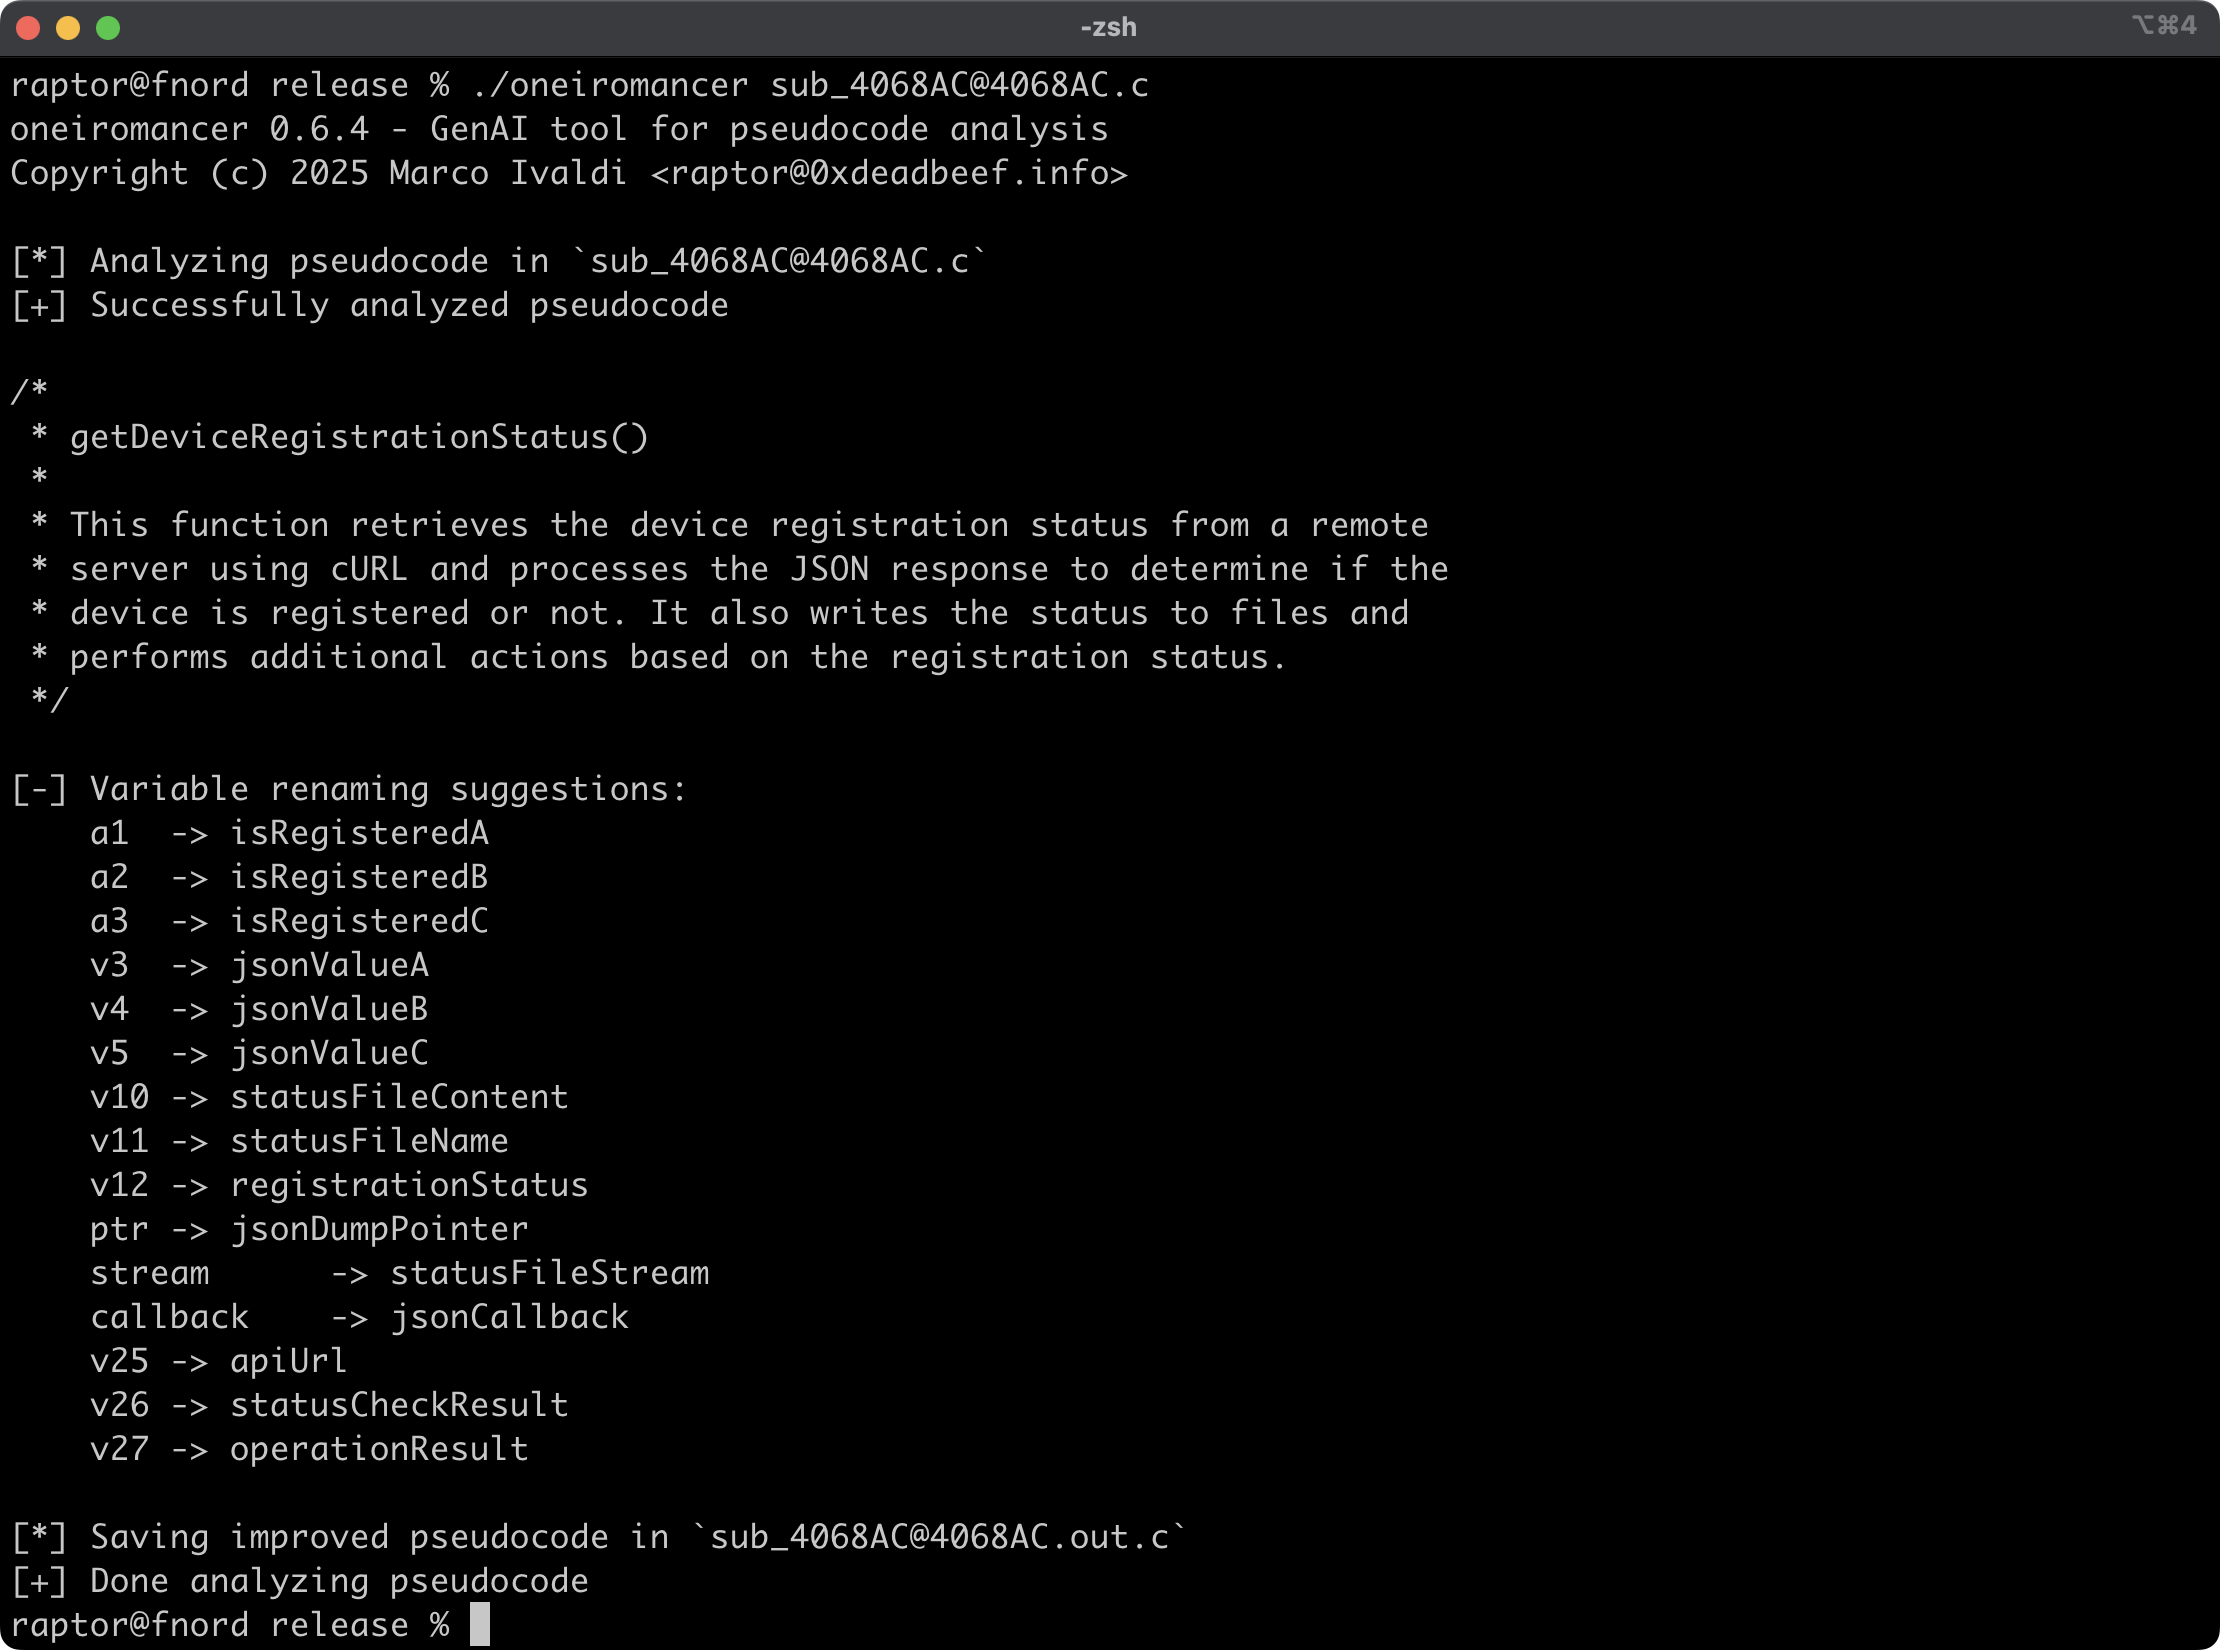
Reverse engineering assistant that uses a locally running LLM to aid with pseudocode analysis.

Unified security scanner for MCP servers with config, pentest, and repo-scan modes. Generates SARIF reports for CI/CD integration, detects secrets,…

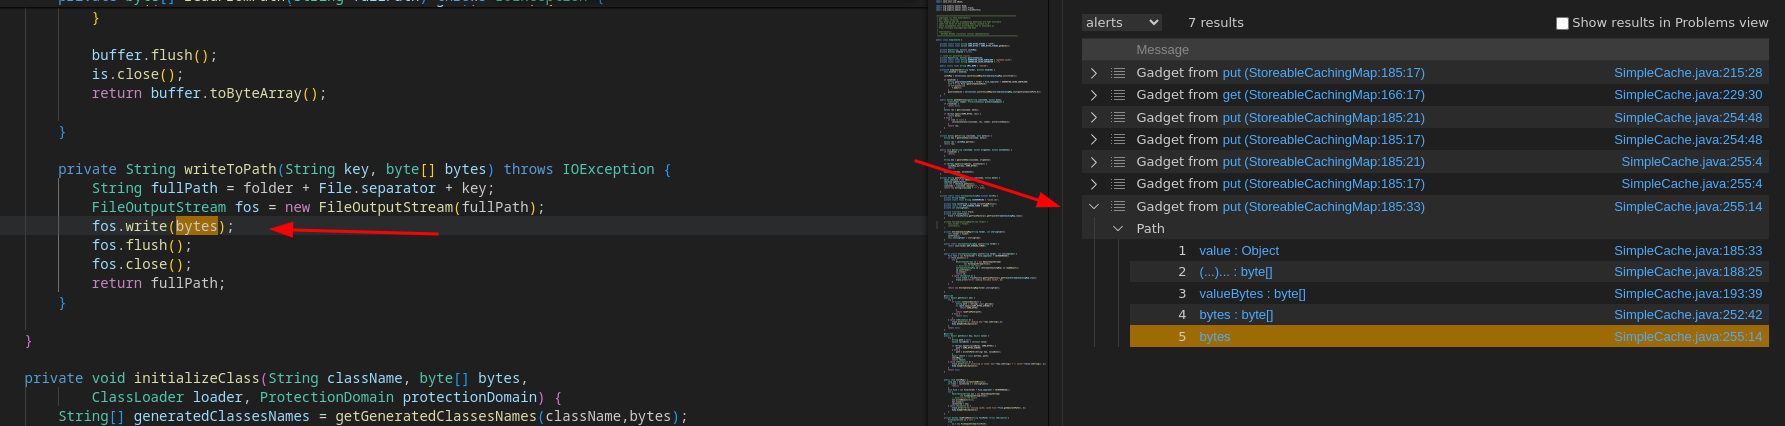
Finding Java/C# gadget chains with CodeQL

Find credentials and secret with 170+ rules covering across source code, Web URL, and CI/CD, verifies them against vendor APIs, and generates SARIF,…

Object-oriented Python API to simplify interaction with IDA for reverse engineering, enabling plugin development and automation of disassembly…

Automated static code analysis framework integrated with SonarQube for early vulnerability detection in source code by scanning Git repositories…

End-to-end security audit framework for LLM agents: static AST and taint modeling, attack synthesis, Docker sandbox replay, and deterministic verdict…

Command-line static analysis scanner that detects critical vulnerabilities in PHP and YAML source code using custom semgrep rules, with Jira and…

CVE-2022-25845 (fastjson 1.2.80) exploit for Spring environments with step-by-step PoC, file read, and arbitrary file write via Jackson/commons-io…