

-LogicSentry-AI
 vighnesh91/-logicsentry-ai
Offline SAST/DAST triage engine that parses source code and replays HAR traffic to detect business-logic flaws, BOLA, race conditions, and privilege…
ai-securityapi-security-testingcode-analysis+9
1
vighnesh91/-logicsentry-aiOffline SAST/DAST triage engine that parses source code and replays HAR traffic to detect business-logic flaws, BOLA, race conditions, and privilege…
 lolcaken/javascript-deobfuscator
Deobfuscator for javascript-obfuscator 5.x output (string arrays, control-flow flattening, self-defending, RC4/base64)
 tomnomnom/gf
A wrapper around grep, to help you grep for things
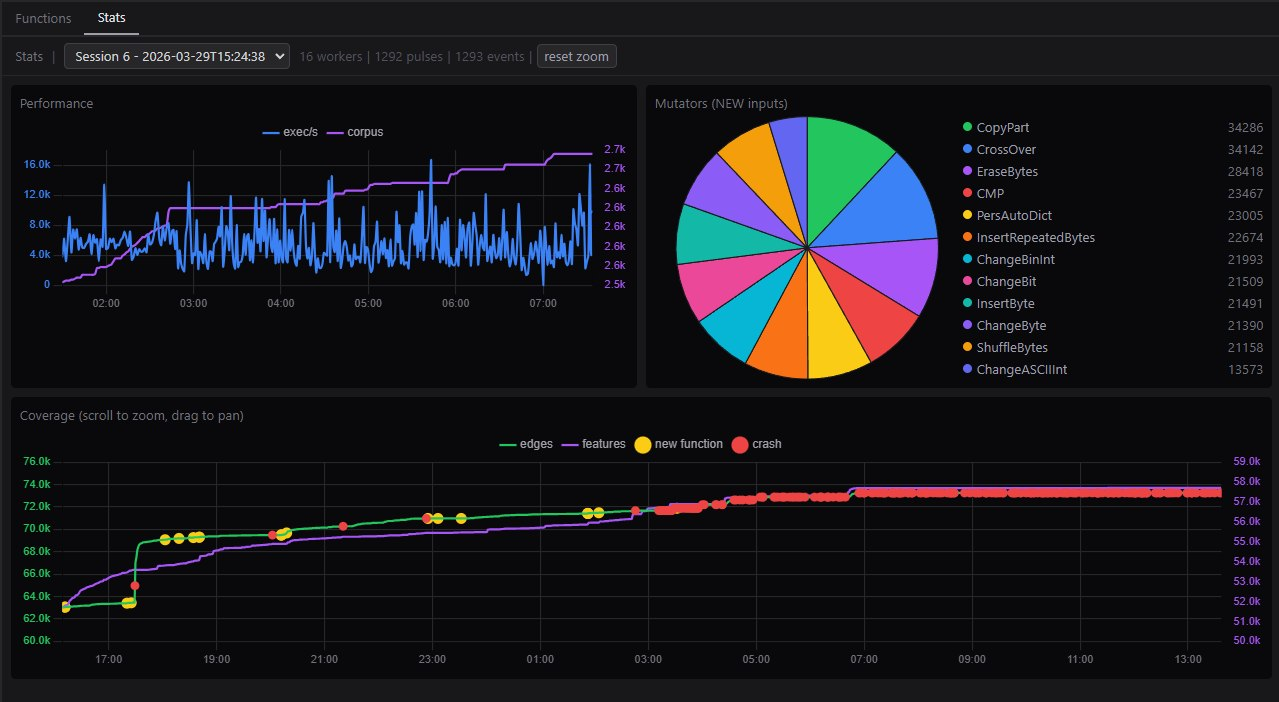 0xbigshaq/apatchy
Fuzzing Framework for Modules in Apache HTTPD Server
 skysliently/cve-2022-22947-pb-ai
一个由AI生成的漏洞验证应用
 csinexus/mcpshield
Drop-in fix for the unpatched MCP STDIO command-injection flaw (CVE-2026-30623 family)
 owasp/agent-security-regression-harness
Executable security regression testing for agentic applications and MCP-integrated systems.
 silentchainai/silentchain
AI-powered vulnerability scanner extension for Burp Suite with multi-provider support (Ollama, OpenAI, Claude, Gemini)
 shoucheng3/x-stream__xstream_cve-2021-21345_1-4-15
Java XML serialization library with a focus on CVE-2021-21345 exploit analysis and deserialization vulnerability testing for web applications.
 ananay/wp2shell-lab
Validation target: minimal WordPress core slice reproducing the wp2shell (CVE-2026-63030 + CVE-2026-60137) REST-to-SQLi chain
 usestrix/strix
Open-source AI penetration testing tool to find and fix your app’s vulnerabilities.
 vigolium/vigolium
Vigolium - High-fidelity vulnerability scanner fusing agentic AI with native speed, modularity, and precision
 cloudflare/security-audit-skill
A coding-agent skill for multi-phase security audits with independently verified, machine-readable findings
 jpiechowka/jenkins-cve-2016-0792
Exploit for Jenkins serialization vulnerability - CVE-2016-0792
 hupe1980/cve-2021-3129
Laravel debug mode - Remote Code Execution (RCE)
 clemfavre/cve-2023-45612_exploit
Reproduction of a high severty security problem that allows XXE (XML eXternal Entity) attacks on Ktor's XML serialization.
 ronf98/cve-2024-11972-poc
CVE-2024-11972 in Hunk Companion <1.9.0 allows unauthenticated attackers to exploit insecure REST API endpoints and install vulnerable plugins,…
 traceforce/mcp-xray
Unified security scanner for MCP servers with config, pentest, and repo-scan modes. Generates SARIF reports for CI/CD integration, detects secrets,…