CVE-2026-54917-SeaweedFS-Cross-Bucket-Traversal

PoC + analysis for CVE-2026-54917 — SeaweedFS S3 gateway cross-bucket path traversal (CVSS 10.0, <4.30). Read/write any bucket via .. in the object…

PoC + analysis for CVE-2026-54917 — SeaweedFS S3 gateway cross-bucket path traversal (CVSS 10.0, <4.30). Read/write any bucket via .. in the object…

a Damn Vulnerable Serverless Application

End to End testing of Web, API, Cloud, Events and Security

Application scanning component of purpleteam

CLI component of purpleteam

Server scanning component of purpleteam

Custom Bash and Python scripts used to automate various penetration testing tasks including recon, scanning, enumeration, and malicious payload…

RESTler is the first stateful REST API fuzzing tool for automatically testing cloud services through their REST APIs and finding security and…

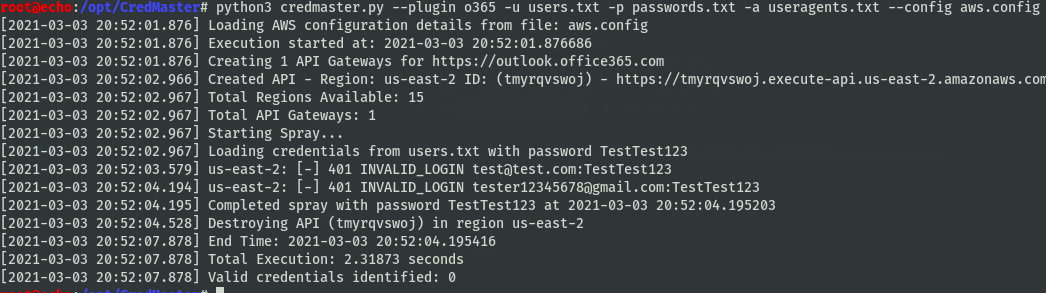
Refactored & improved CredKing password spraying tool, uses FireProx APIs to rotate IP addresses, stay anonymous, and beat throttling

Terminal API client for HTTP, GraphQL and gRPC. Plain .http files you can diff and version, with workflows, mocks, profiling, tracing, OpenAPI…

Opensource, cross-platform and portable toolkit for automating routine processes when carrying out various works for testing!

Automated security testing tool for Salesforce Experience Cloud that discovers misconfigured Aura applications, accessible records, and unauthorized…

Validates Google Maps API keys against 21 endpoints, revealing exposed services with PoC URLs, proxy support, and quiet mode for focused auditing.

CyberArk Security Audit

Vulnerability Assessment Scanner with Report Generation

find sensitive data leaking from ServiceNow instances.

The exploit server for out-of-band findings. Point a target at a domain you own. Every HTTP request and every email it sends back lands in a…

Detects unauthenticated MLflow webhook SSRF (CVE-2026-64849) that accesses internal or cloud metadata services and leaks response details via…