
IATelligence
 fr0gger/iatelligence
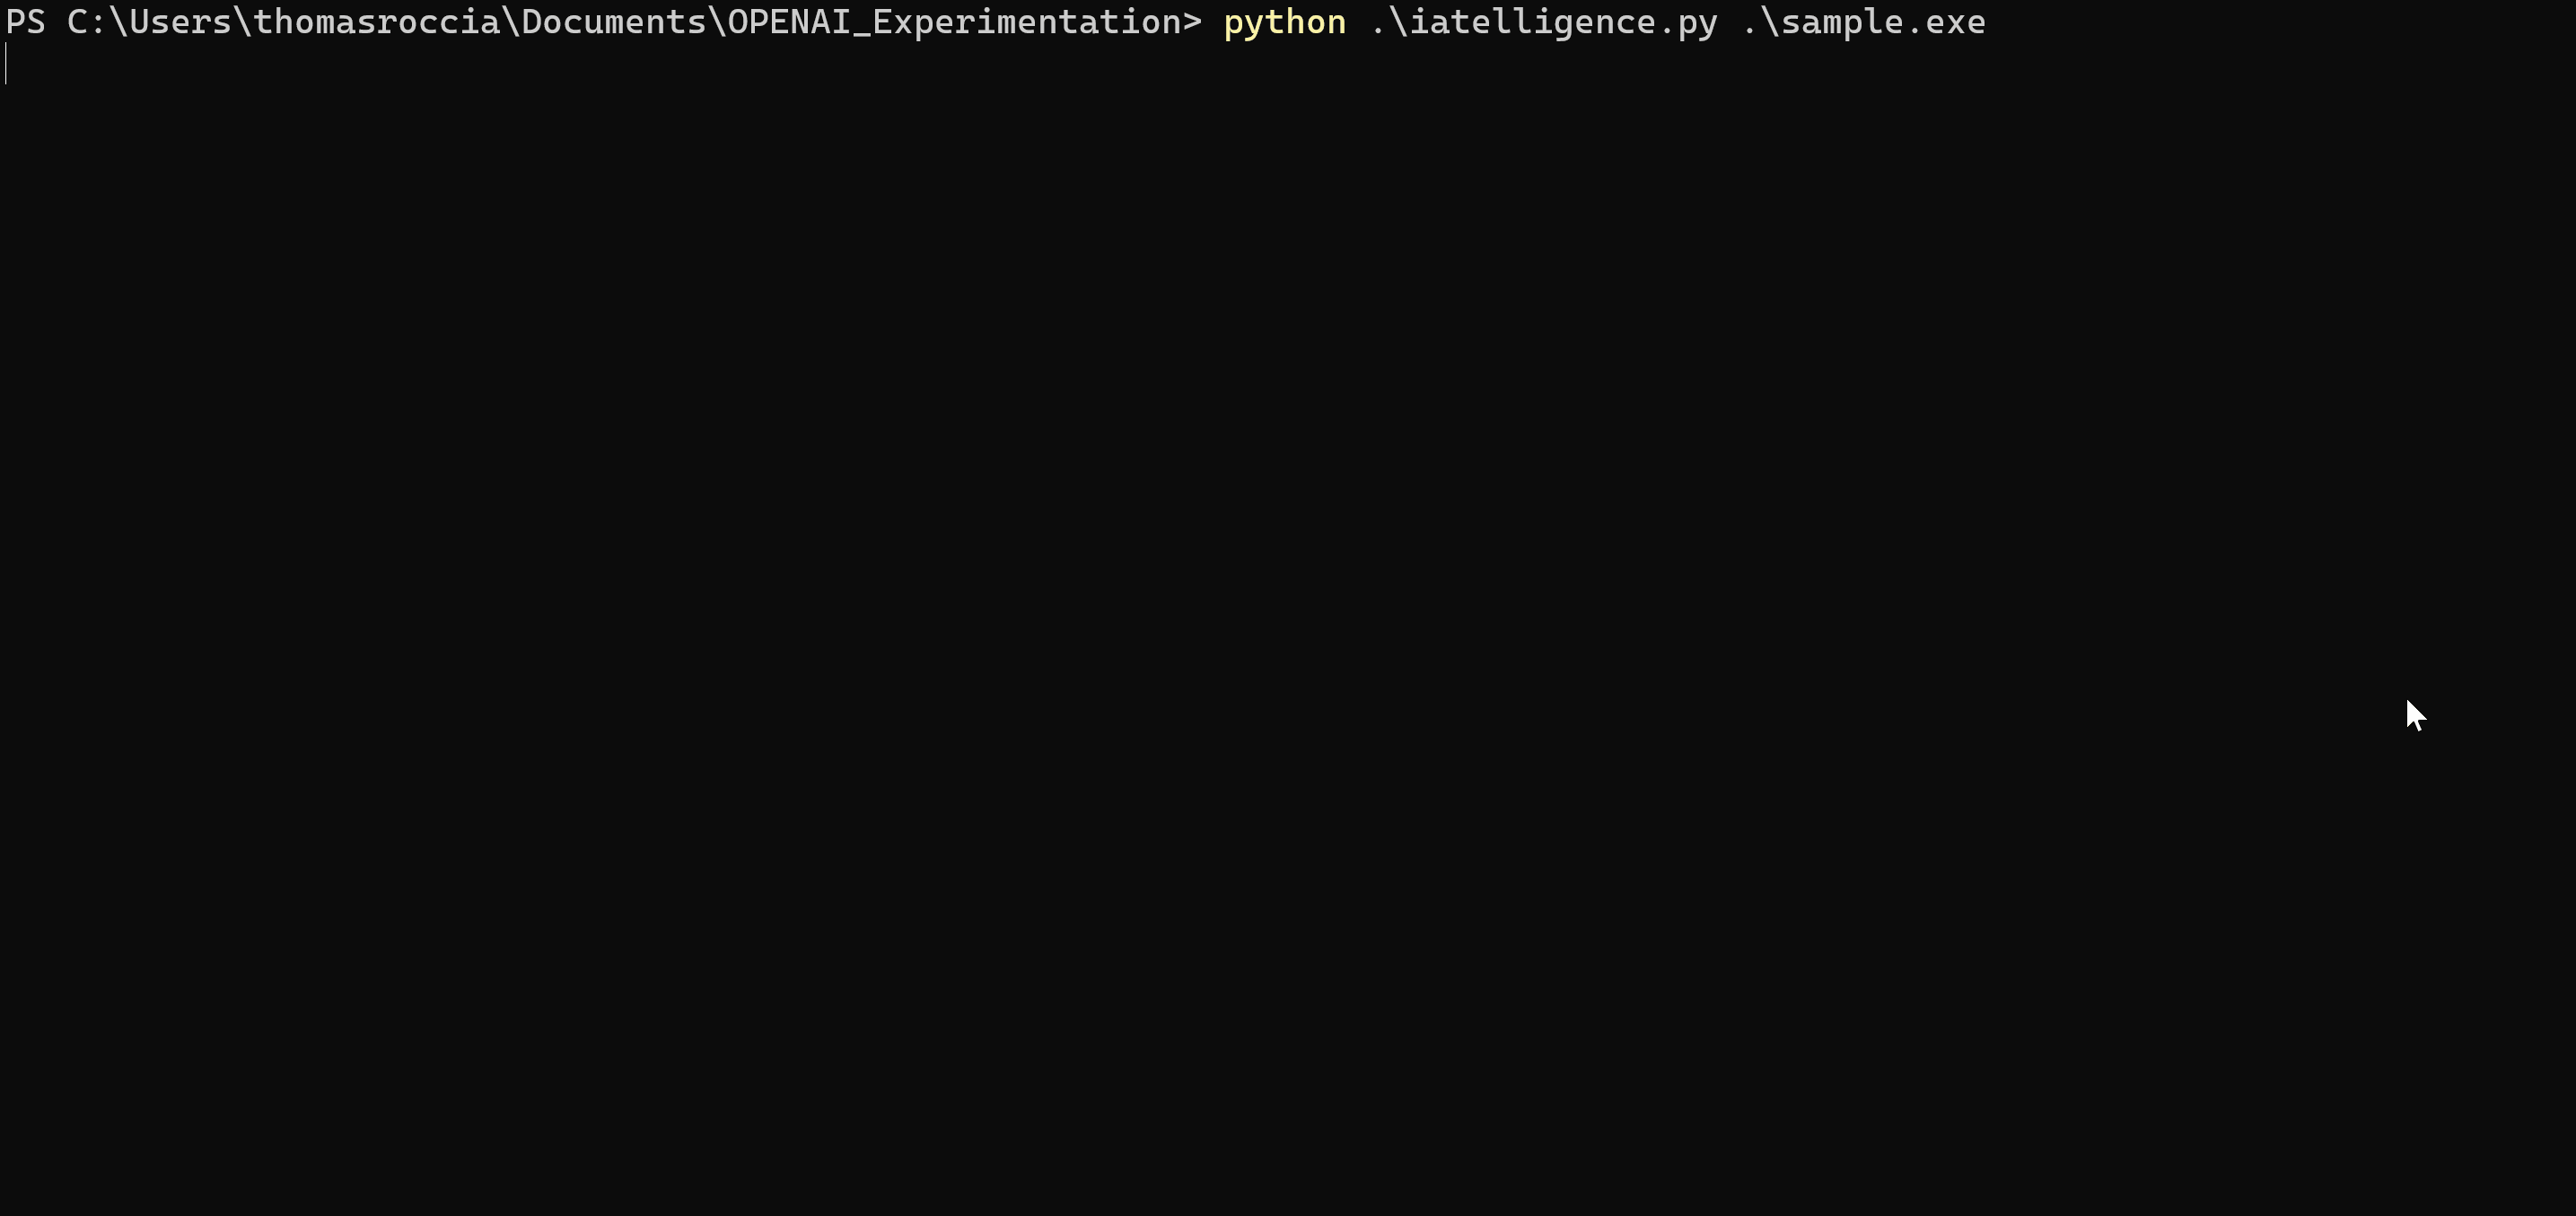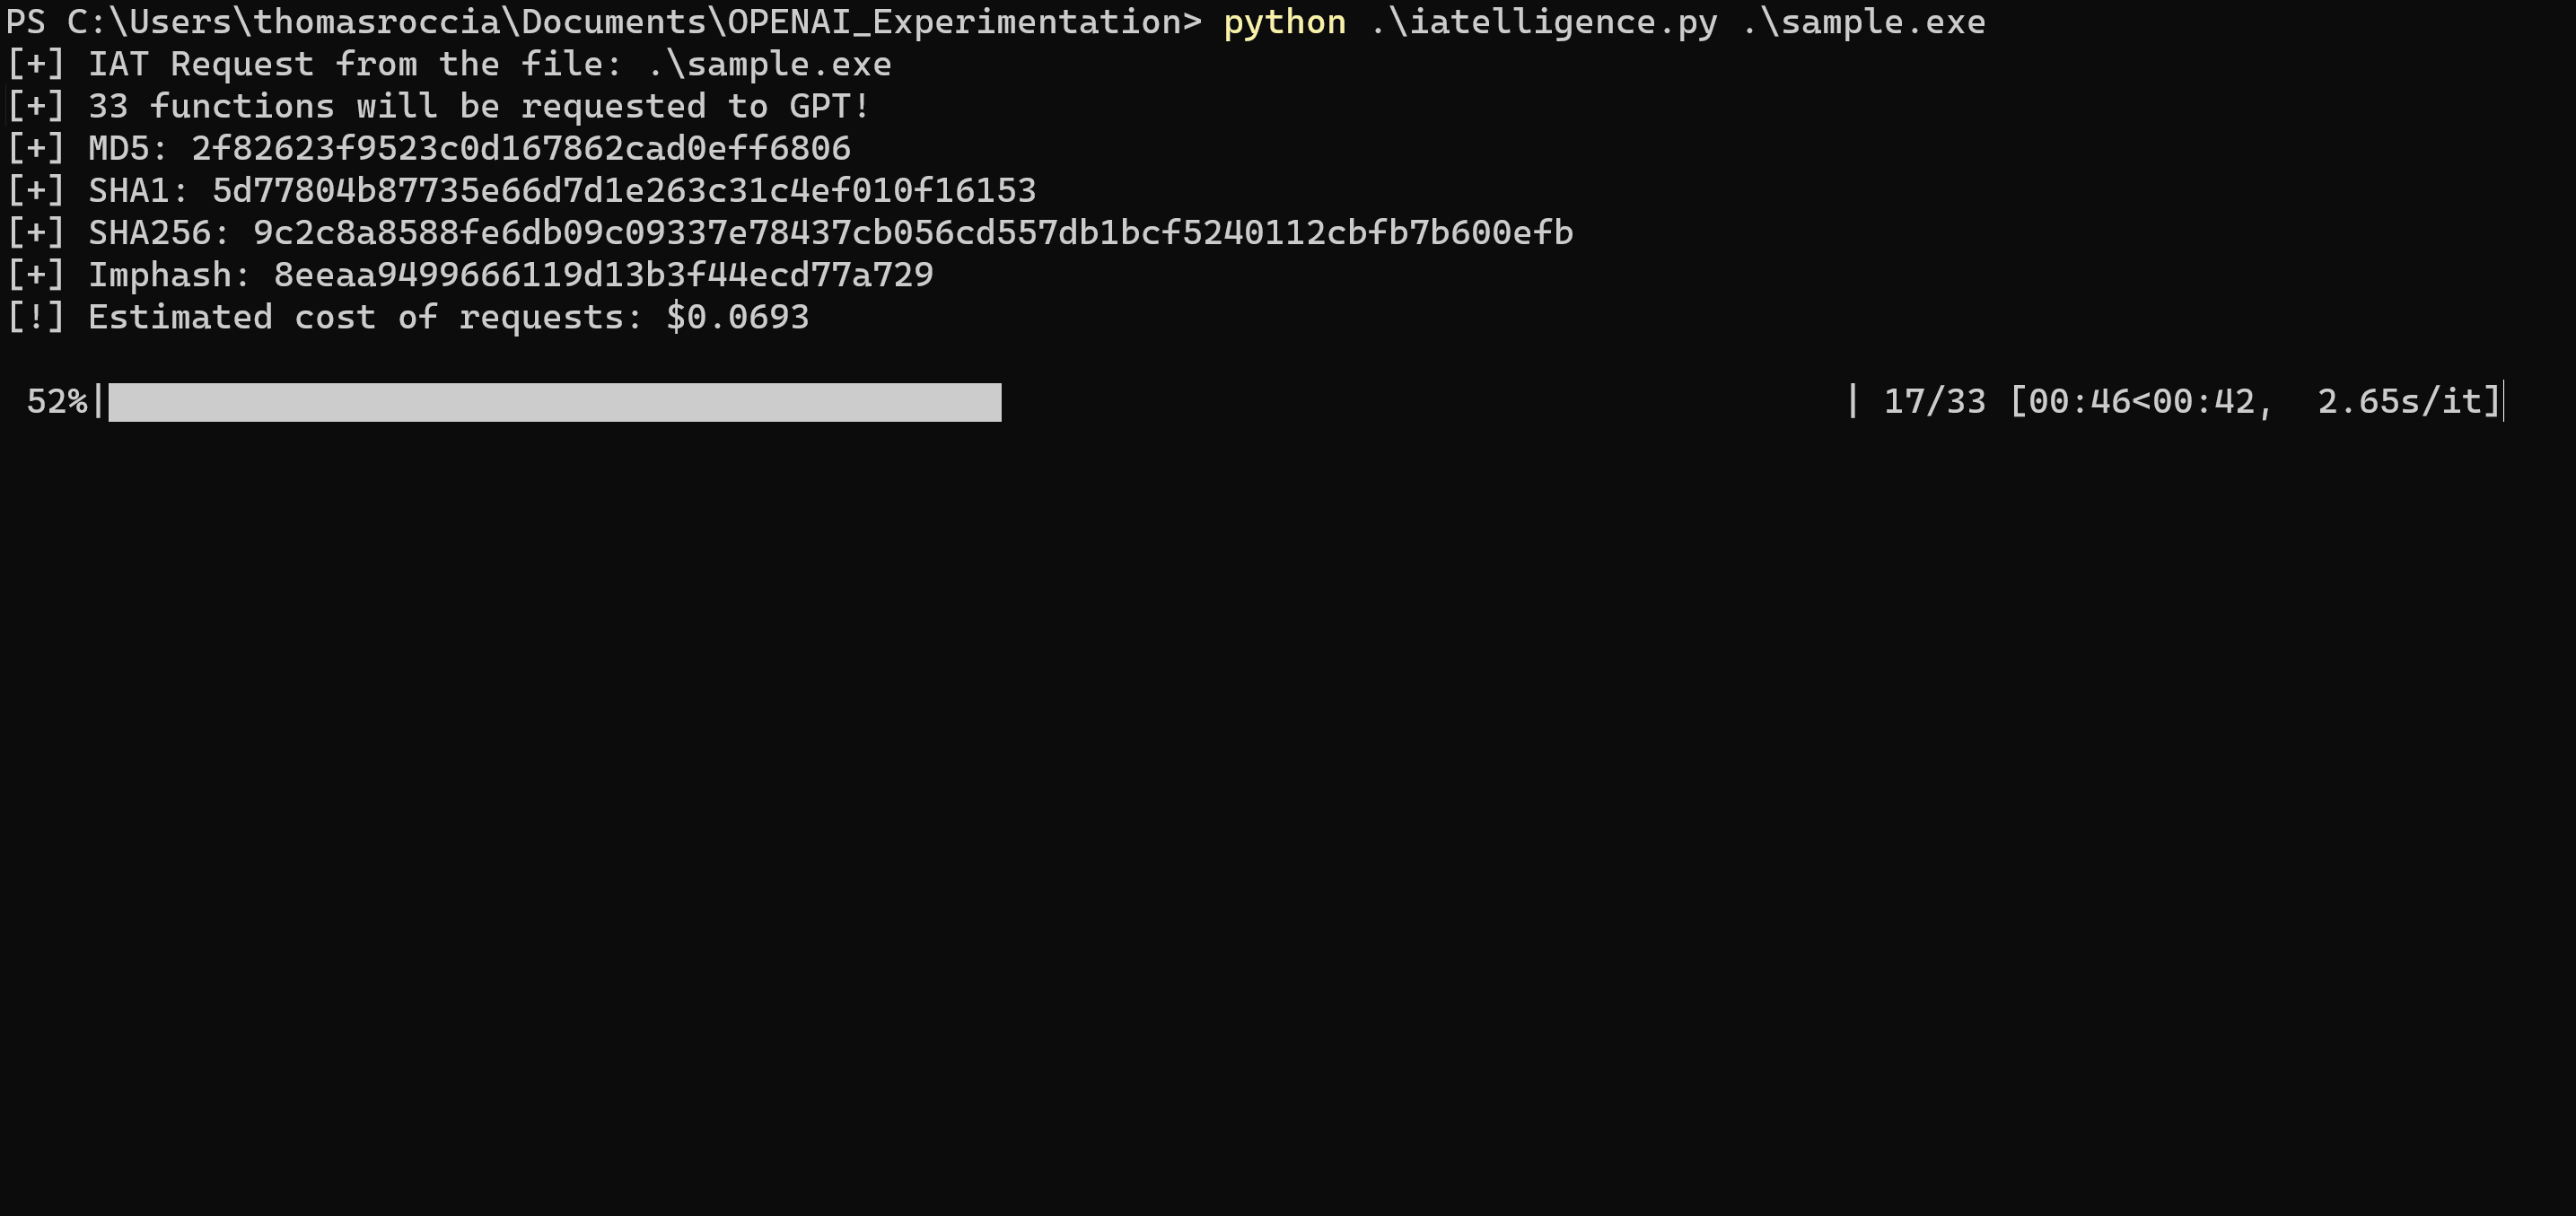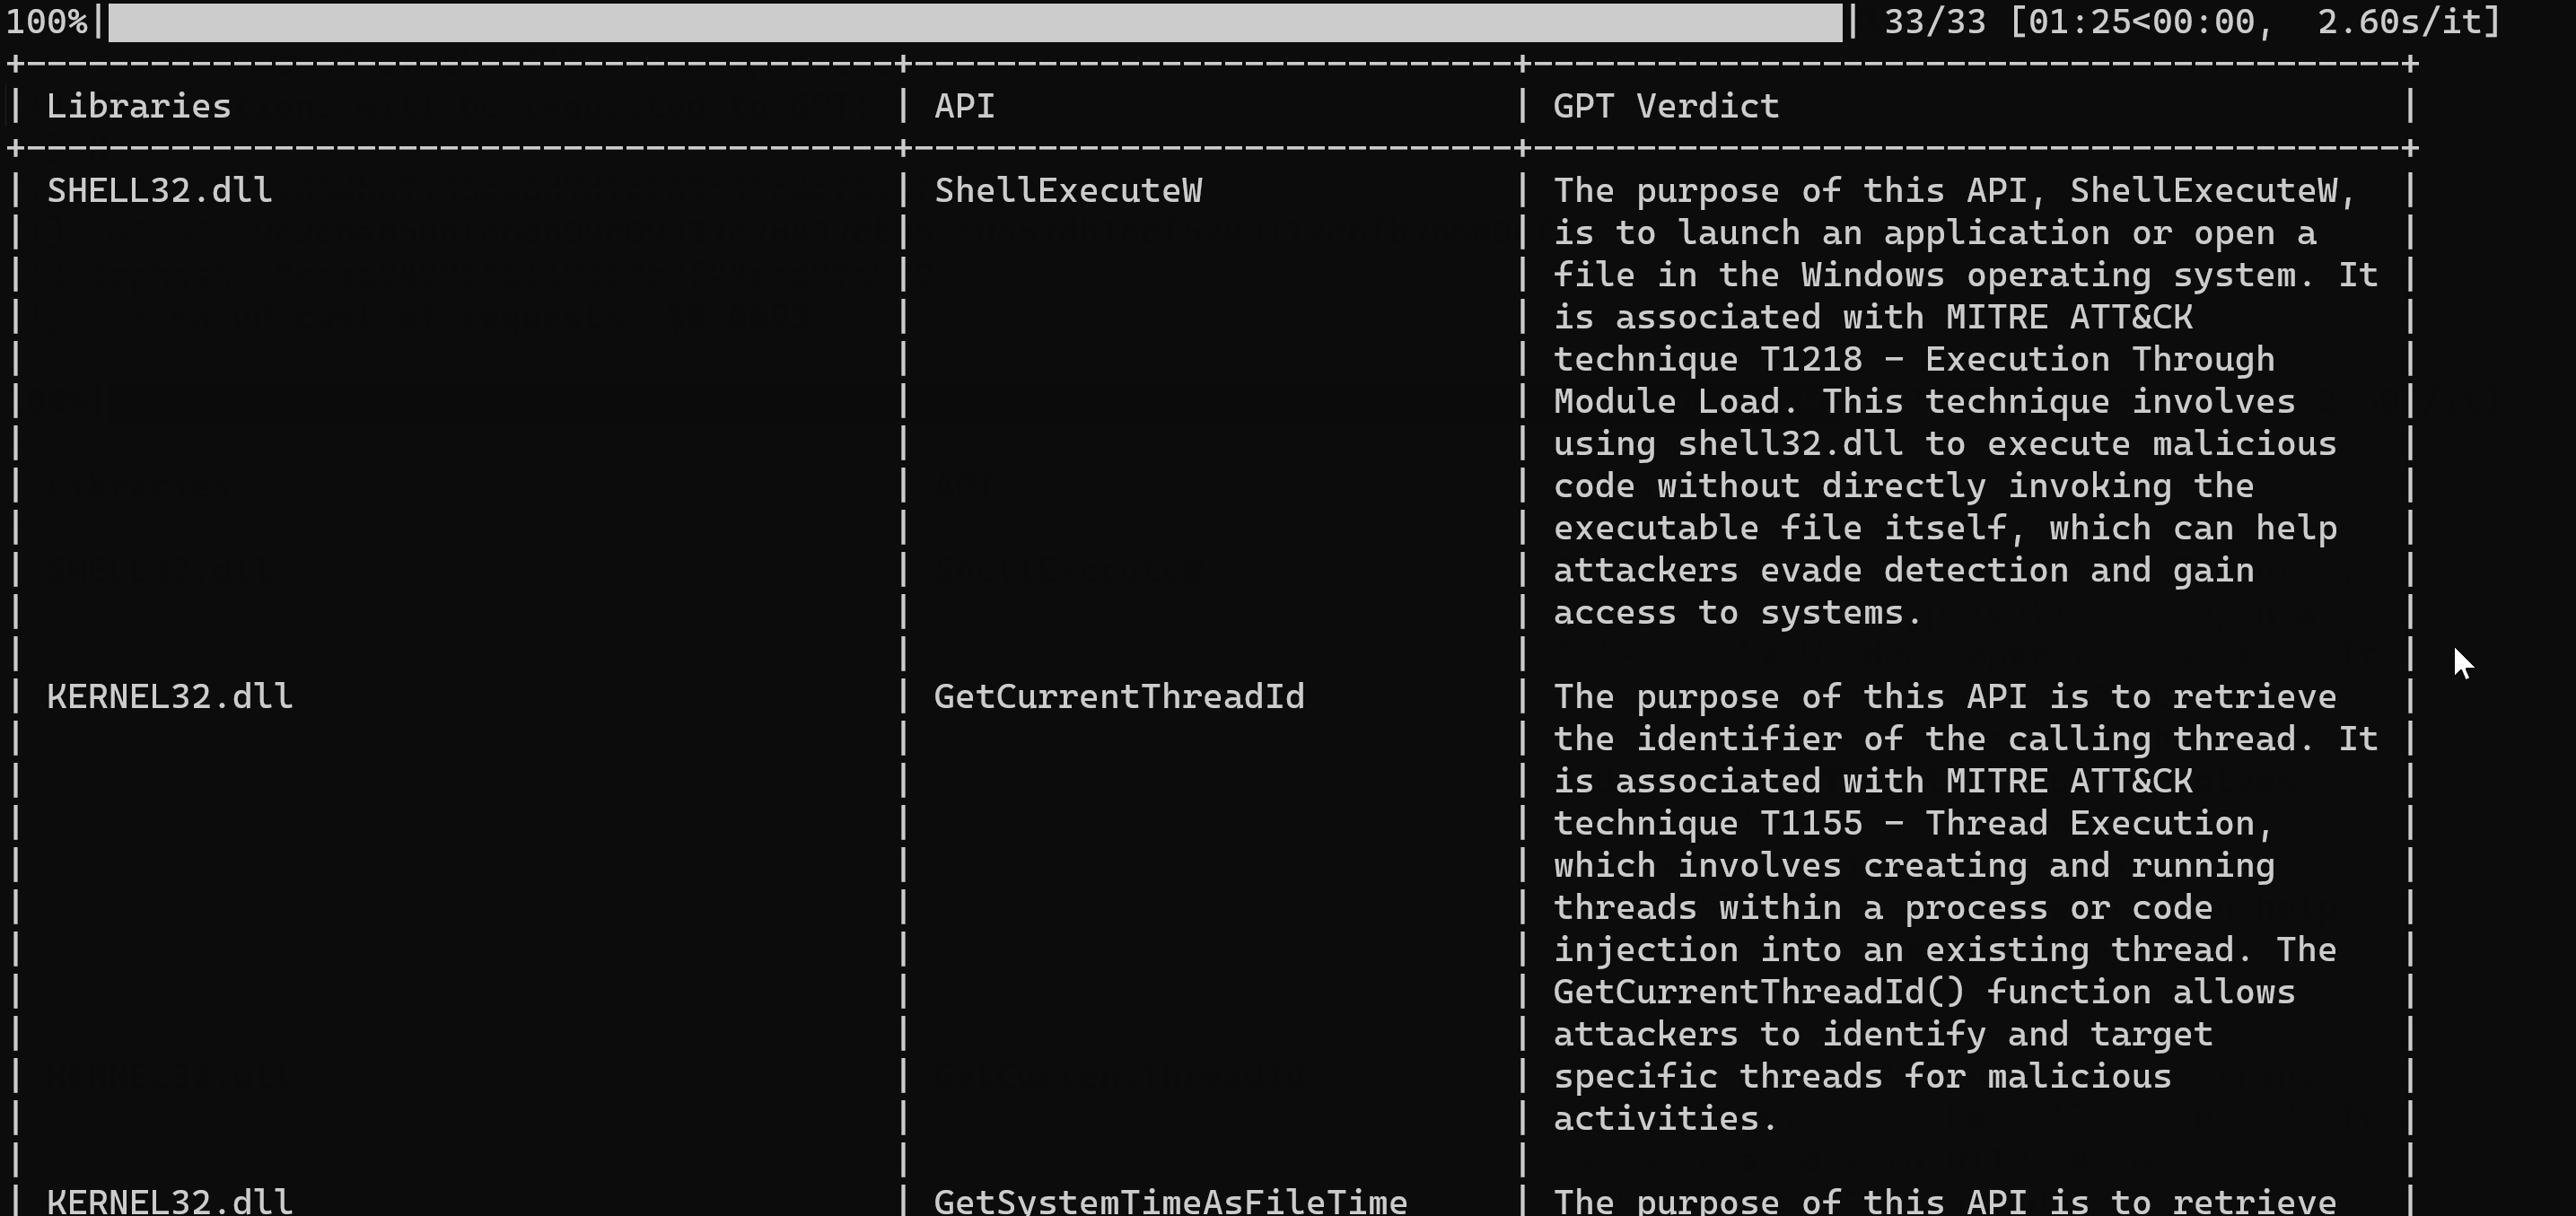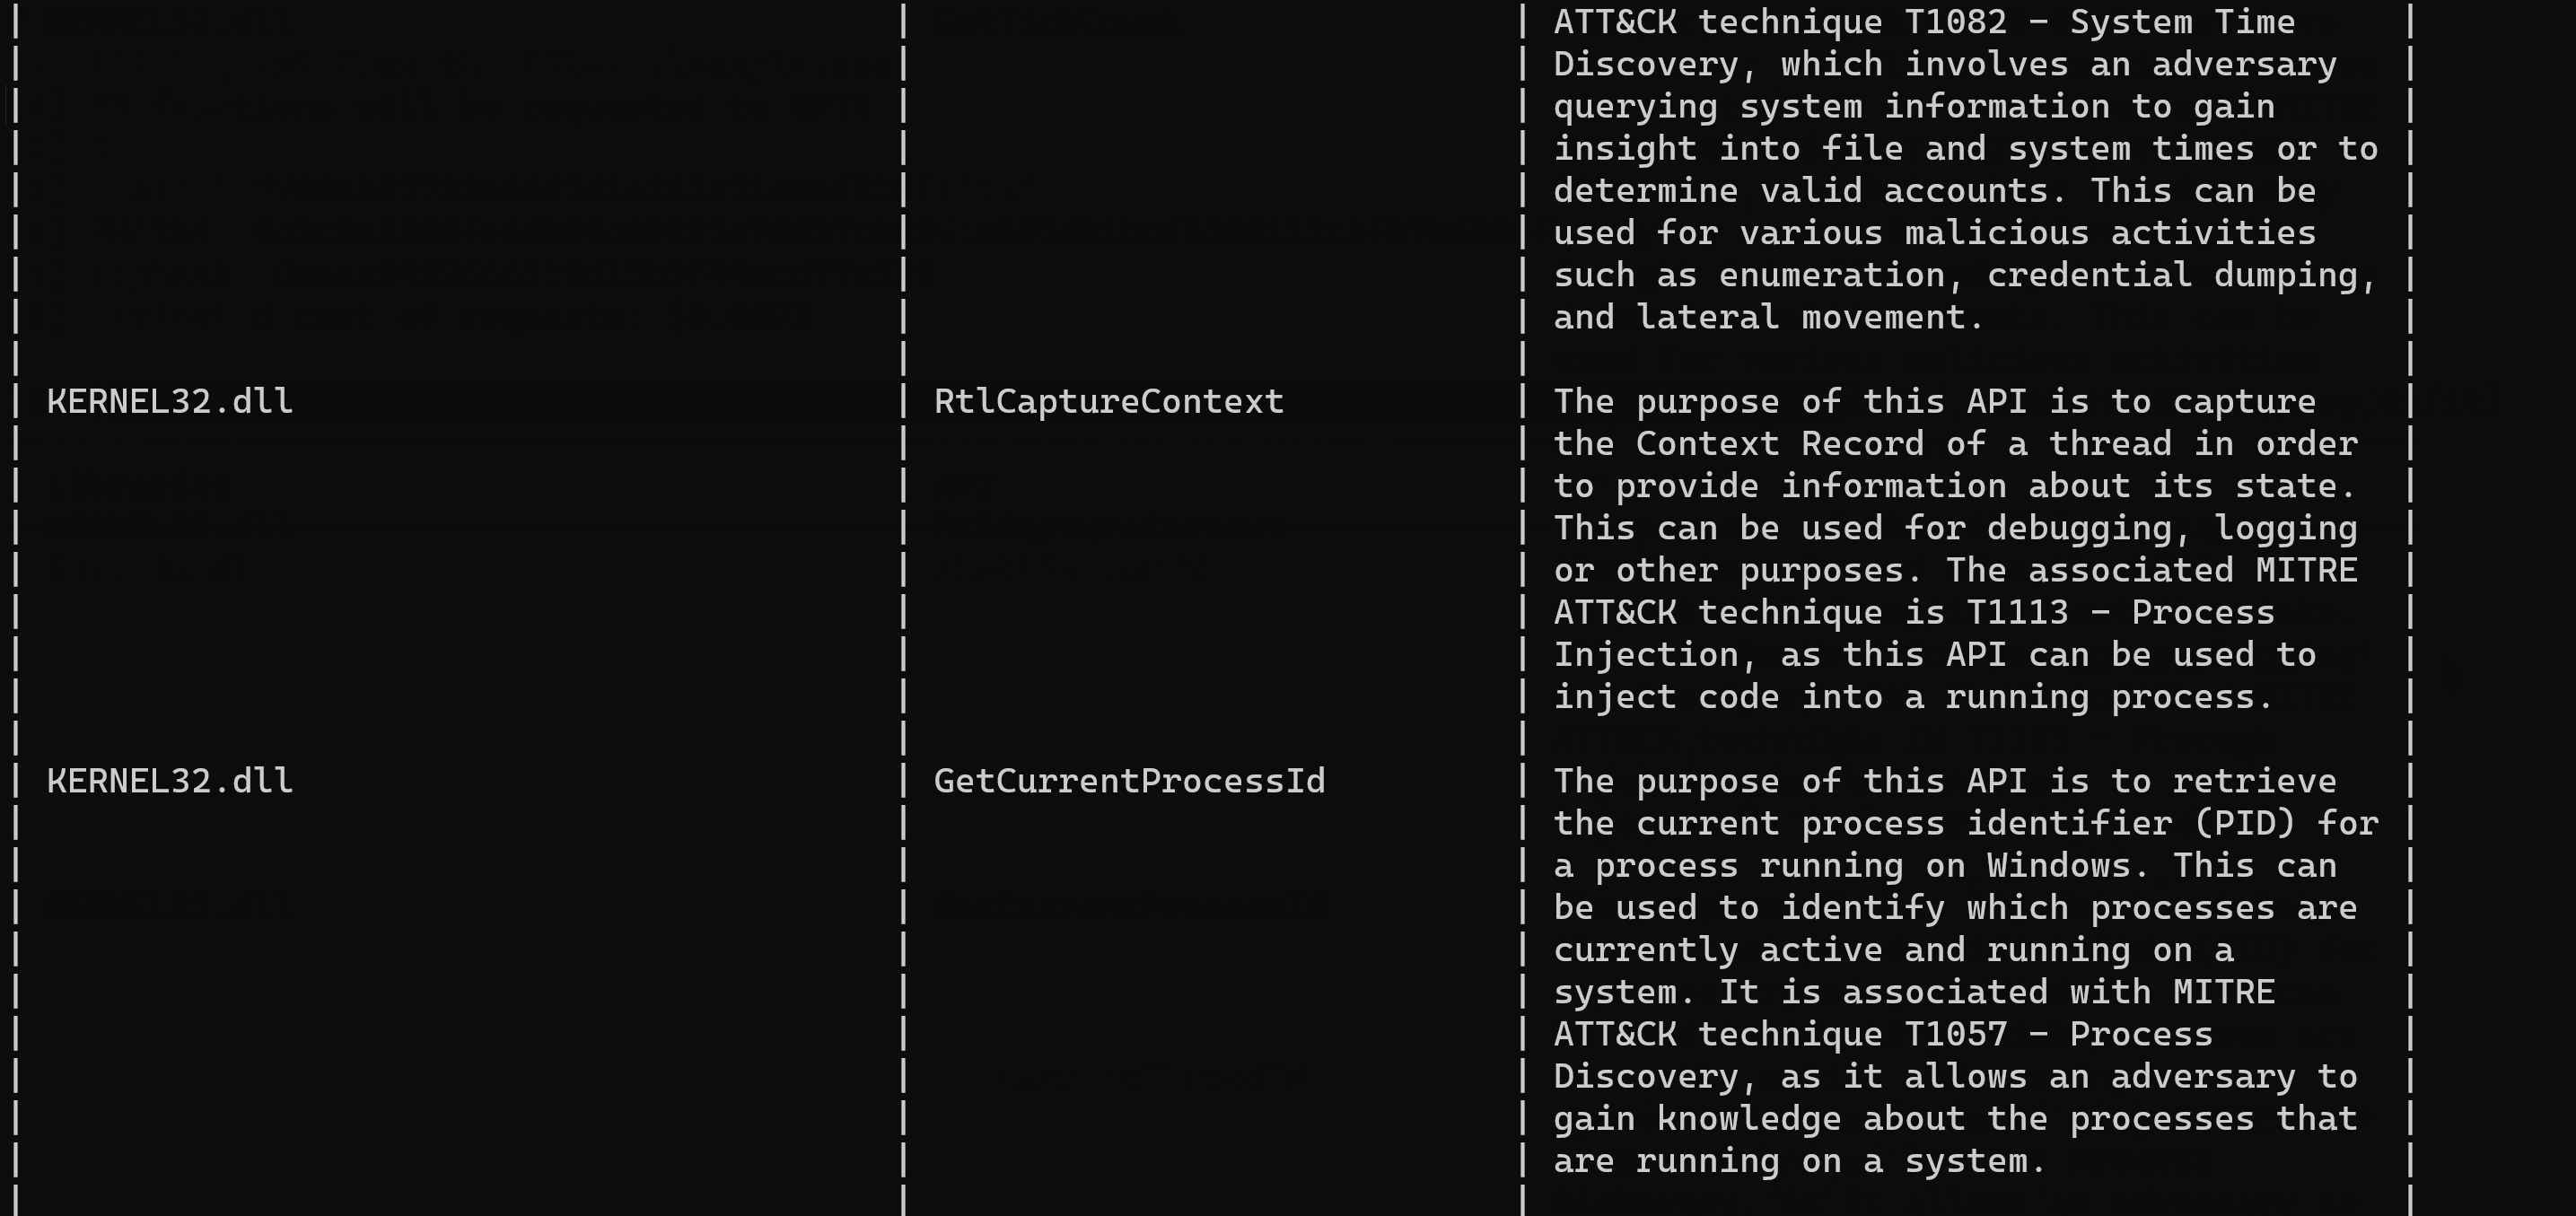
IATelligence is a Python script that will extract the IAT of a PE file and request GPT to get more information about the API and the ATT&CK matrix…
ai-assisted-reversingbinary-analysismalware-analysis+3
384
fr0gger/iatelligenceIATelligence is a Python script that will extract the IAT of a PE file and request GPT to get more information about the API and the ATT&CK matrix…
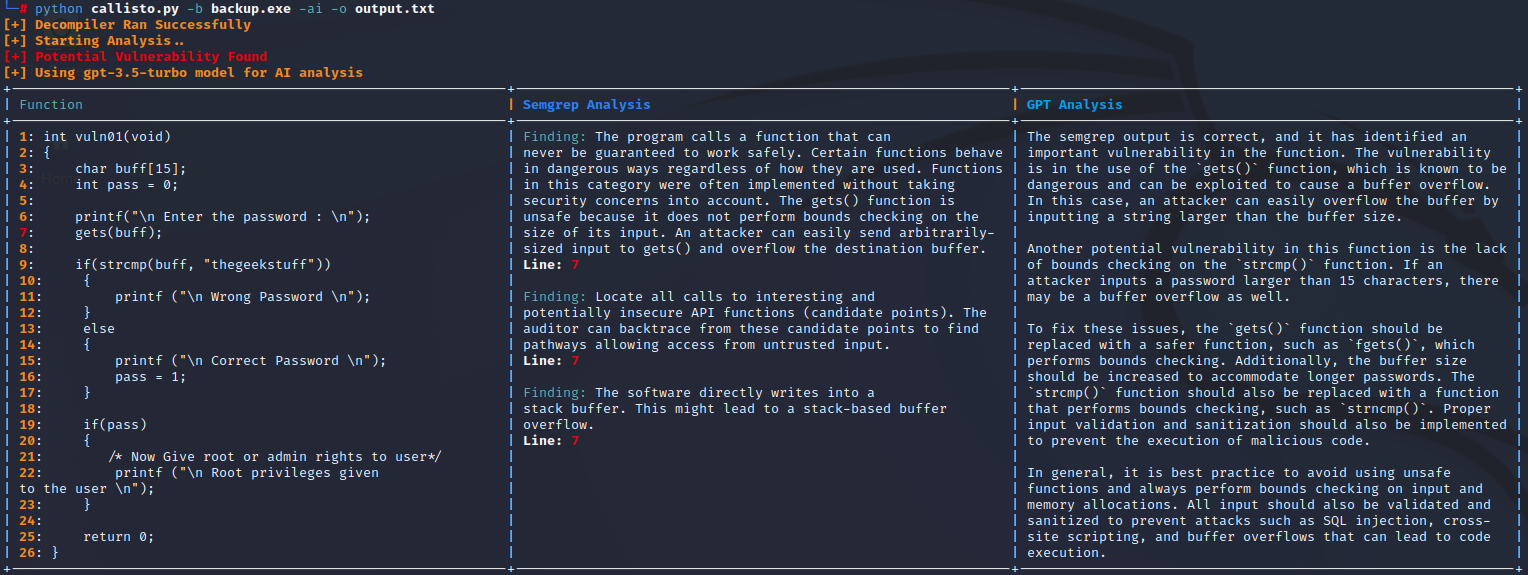 jetp1ane/callisto
Automated binary vulnerability analysis tool that decompiles executables via Ghidra, scans pseudo-C code with Semgrep, and validates findings using…
 sjkim1127/reversecore_mcp
A security-first MCP server that empowers AI agents to perform automated reverse engineering, malware analysis, forensics, vulnerability research,…
 httpvoid/cve-reverse
Curated list of CVEs that have been reverse-engineered and analyzed, serving as a resource for vulnerability research, exploitation understanding,…
 reb311ion/replica
Ghidra plugin that enhances reverse engineering by fixing missed disassembly, detecting functions, labeling crypto constants, and renaming functions…
 uds-se/formatfuzzer
Template-driven binary format fuzzer that generates and parses valid test inputs at high speed, with AFL++ integration for coverage-guided fuzzing.
 kudelskisecurity/cdf
Automated differential fuzzing tool for cryptographic software that detects implementation errors, compliance failures, and side-channel leaks…
 atomdrift-project/scan
0-day malware detection for binaries, source & scripts (that doesn't suck)
 seemoo-lab/polypyus
Binary-only firmware historian that learns to locate functions in raw binaries by extracting known functions from similar binaries, enabling fast…
 1-3-7/disrobe
Rust CLI suite that statically decompiles, deobfuscates, and unpacks native code, bytecode, scripts, firmware, and app packages across 15+ ecosystems…
 nevesnunes/z80-sans
OpenType font that disassembles Z80 instructions
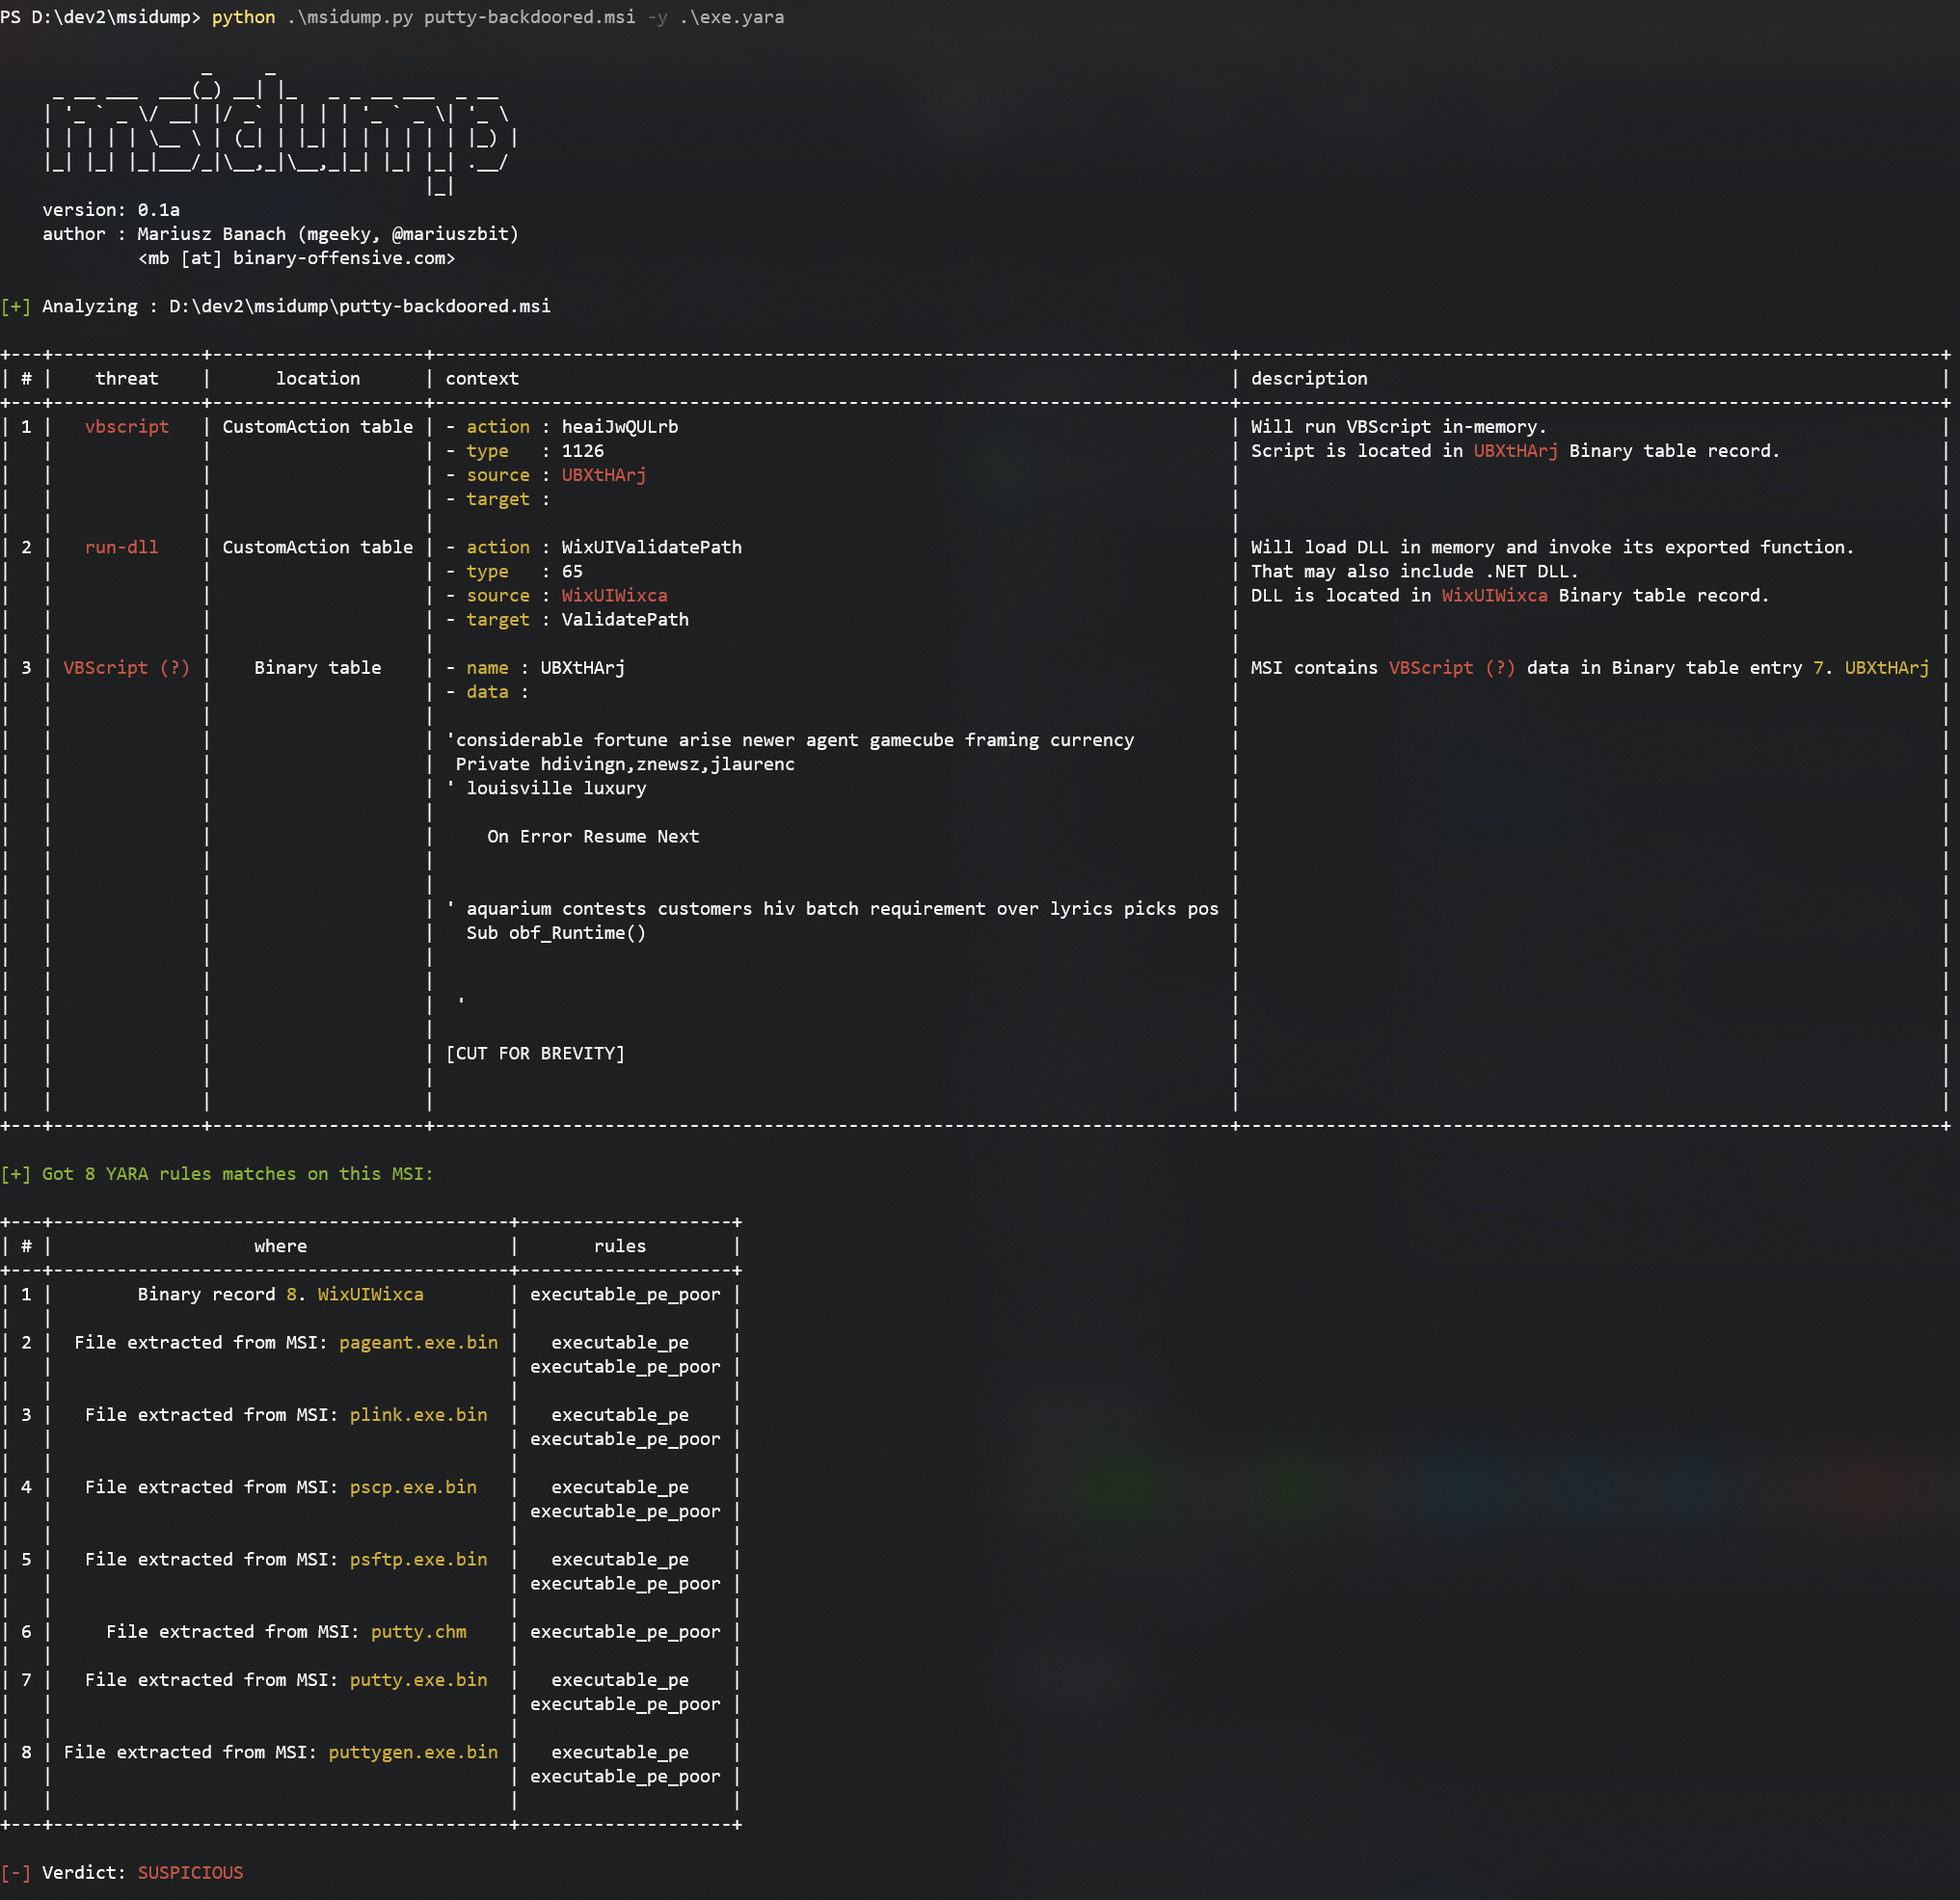 mgeeky/msidump
MSI Dump - a tool that analyzes malicious MSI installation packages, extracts files, streams, binary data and incorporates YARA scanner.
 concollmic/concollmic
LLM-agent-powered concolic execution engine that instruments source code, summarizes path constraints in natural language, and generates test cases…
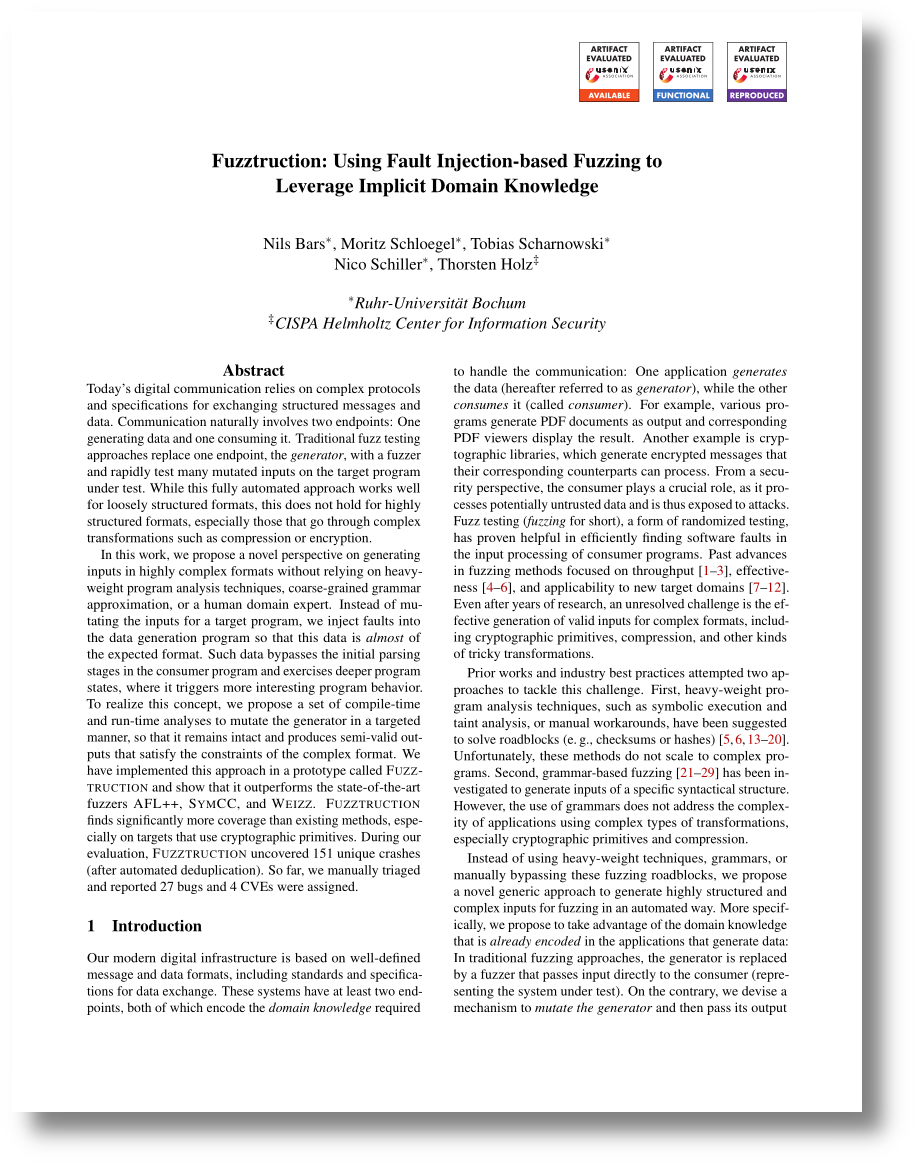 fuzztruction/fuzztruction
Fault-injection-based fuzzer that mutates generator programs to produce almost-valid inputs for targets, enabling fuzzing of complex formats and…
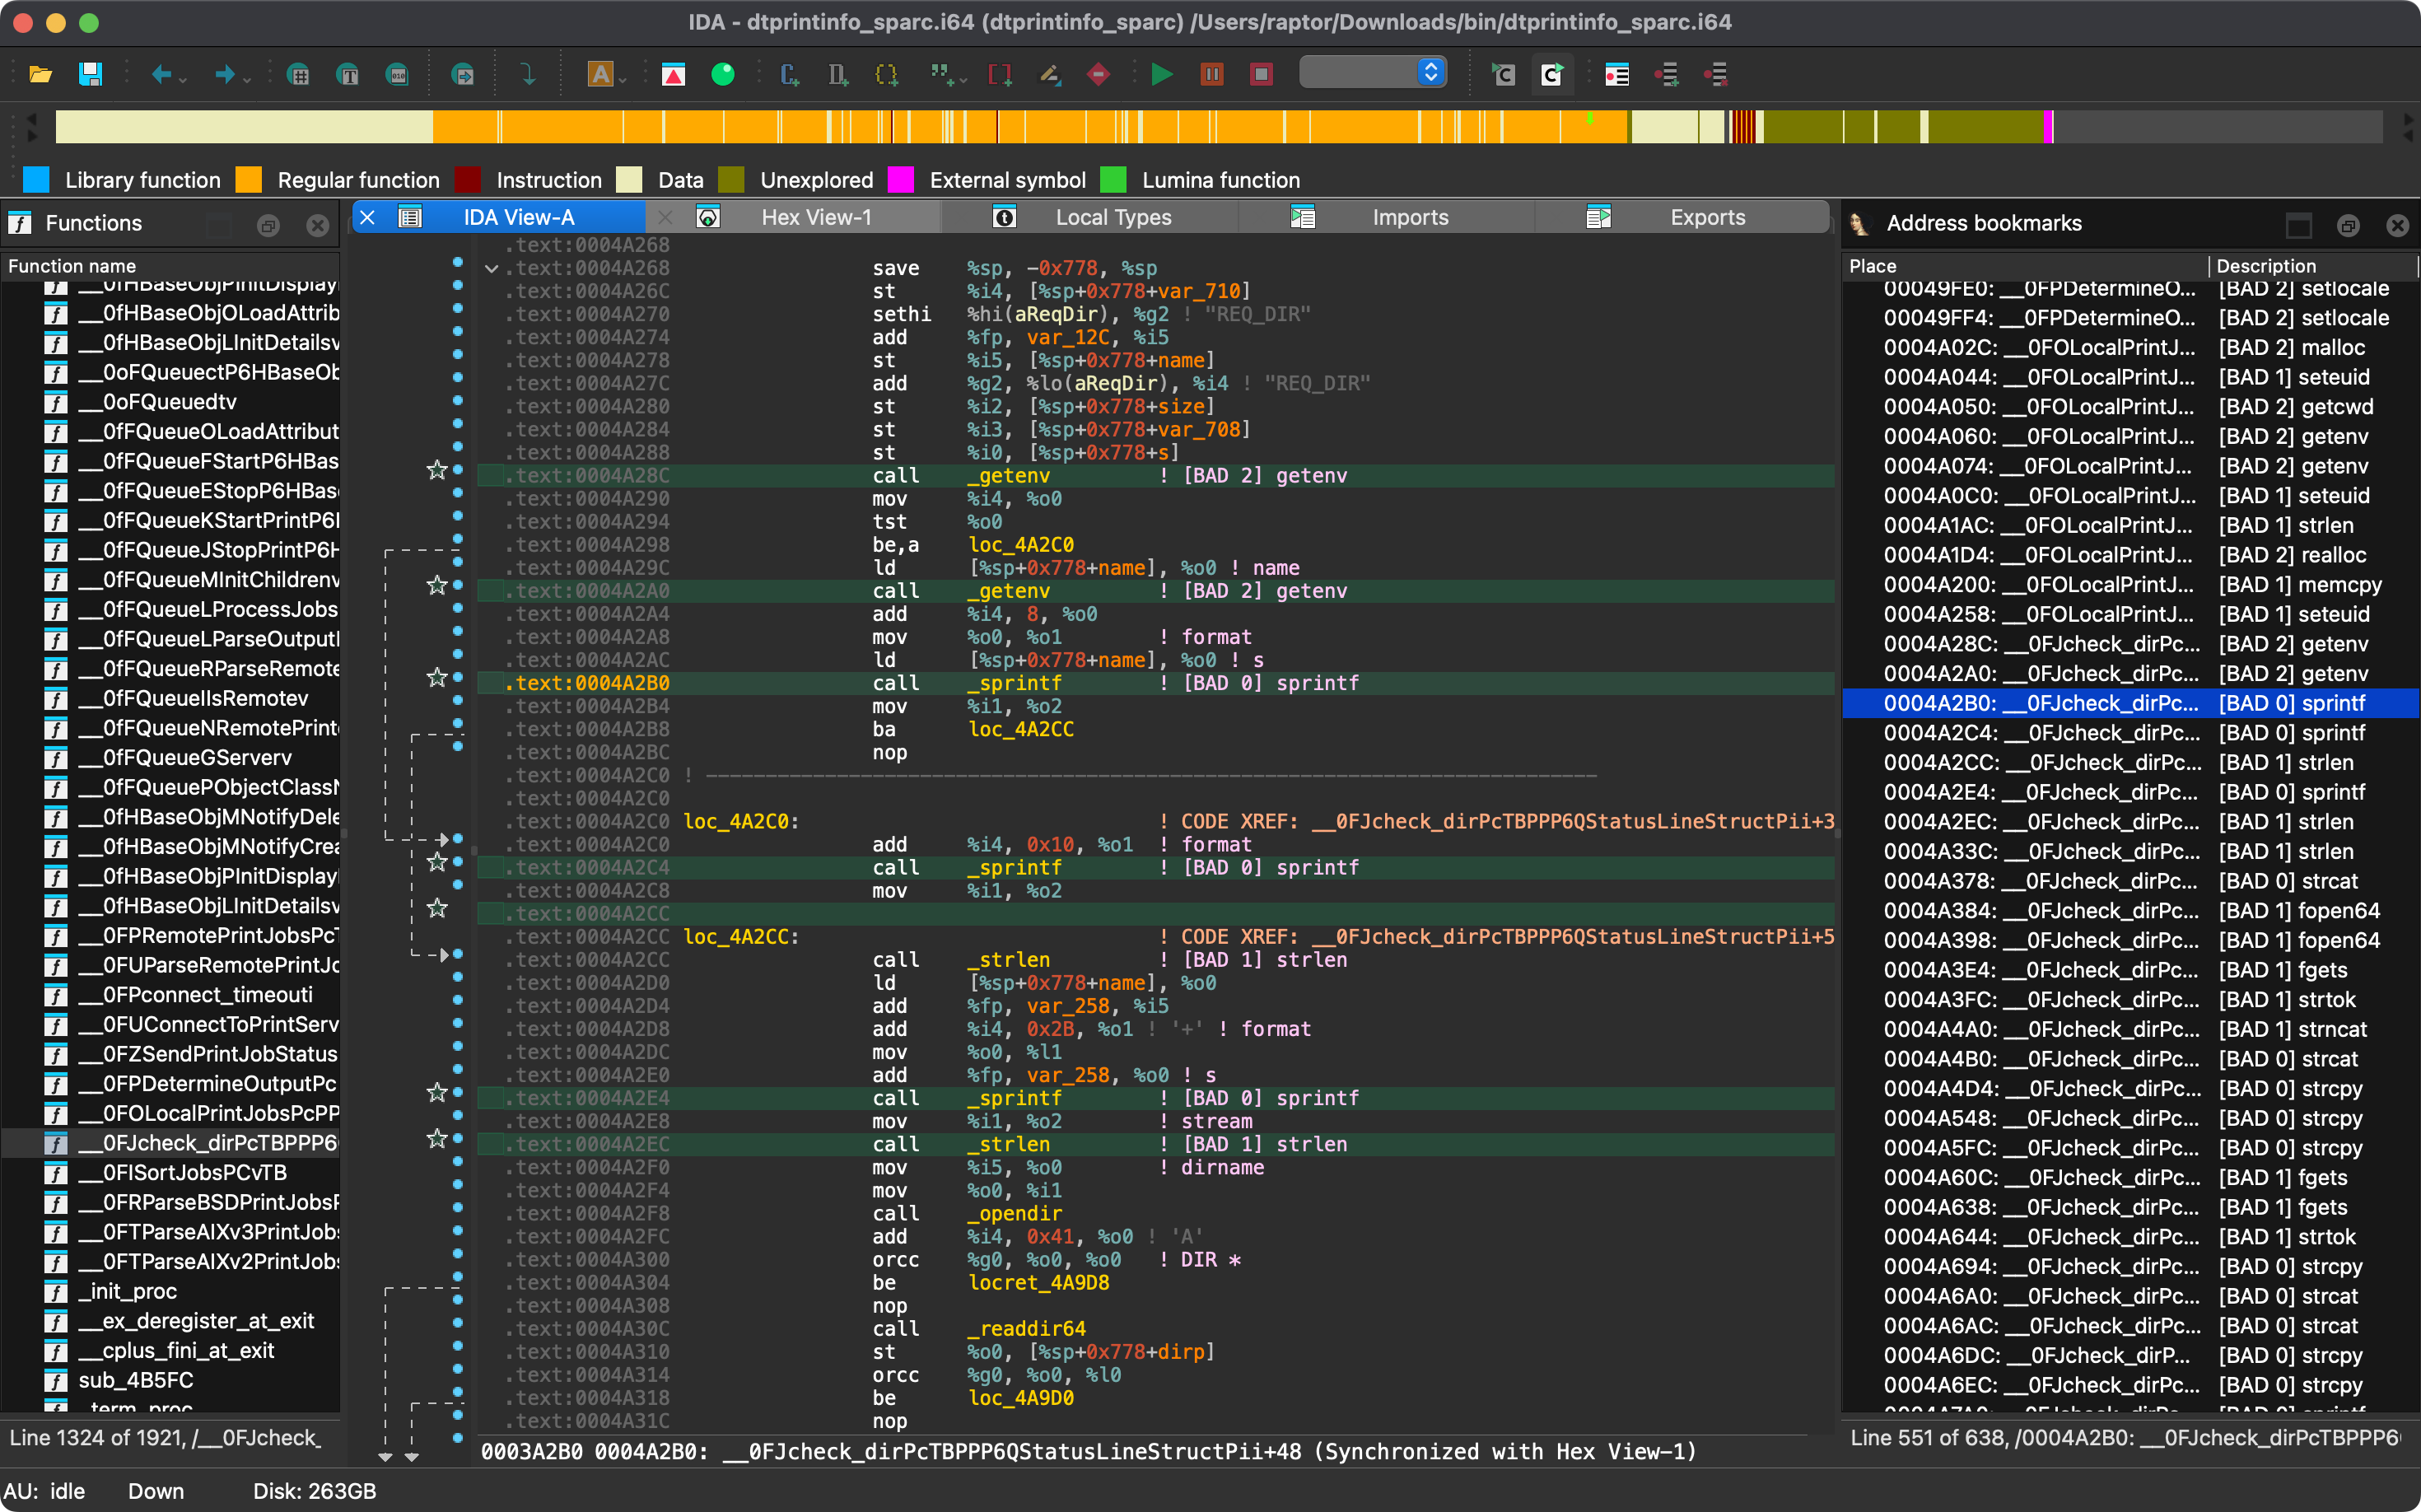 0xdea/rhabdomancer
Vulnerability research assistant that locates calls to potentially insecure API functions in a binary file.
 xoreaxeaxeax/schrodingers-toctou
Detect compiler-invented memory loads that turn secure C into TOCTOU vulnerabilities. Includes automated source audits, Unicorn-based binary…
 0xdea/haruspex
Vulnerability research assistant that extracts pseudocode from the IDA Hex-Rays decompiler.
 parikhakshat/autoharness
A tool that automatically creates fuzzing harnesses based on a library