
Frida-Labs
 dere-ad2001/frida-labs
The repo contains a series of challenges for learning Frida for Android Exploitation.
android-securitybinary-analysisctf+6
1.3k8 months ago
dere-ad2001/frida-labsThe repo contains a series of challenges for learning Frida for Android Exploitation.
 pelock/crackmez3s-ctf-crackme-tutorial
How to write a CrackMe for a CTF competition. Source code, technical explanation, anti-debugging and anti reverse-engineering tricks.
 0xm3r/cgpwn
A lightweight VM for hardware hacking, RE (fuzzing, symEx, exploiting etc) and wargaming tasks
 binarly-io/fwhunt-scan
Tools for analyzing UEFI firmware and checking UEFI modules with FwHunt rules
 nccgroup/mtk_bp
Tools for analyzing and reverse engineering MediaTek baseband firmware, including file extraction, symbol parsing, and Ghidra integration for modem…
 synacktiv/canon-tools
Tools used for decrypting Canon printers firmwares
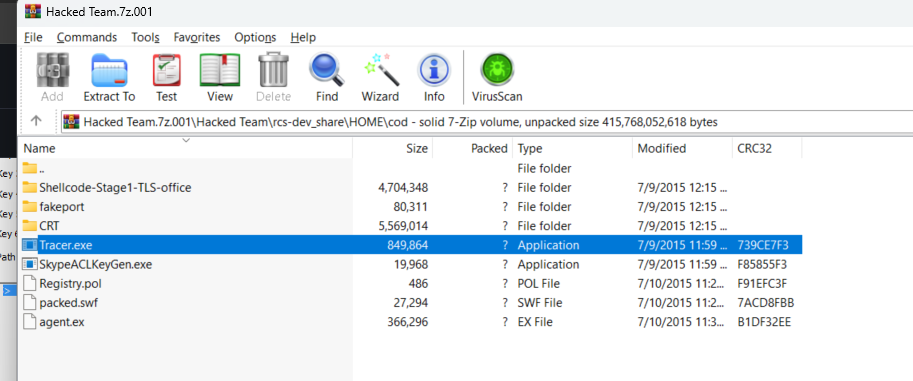 spiralbl0ck/skypeaclkeygen.exe-analysis-for-hacking-team
SkypeACLKeyGen.exe analysis for hacking team
 wtsxdev/reverse-engineering
List of awesome reverse engineering resources
 marin-m/vmlinux-to-elf
A tool to recover a fully analyzable .ELF from a raw kernel, through extracting the kernel symbol table (kallsyms)
 theopolis/uefi-firmware-parser
Parse BIOS/Intel ME/UEFI firmware related structures: Volumes, FileSystems, Files, etc
 boku7/bokuloader
A proof-of-concept Cobalt Strike Reflective Loader which aims to recreate, integrate, and enhance Cobalt Strike's evasion features!
 rehints/efixplorer
IDA plugin and loader for UEFI firmware analysis and reverse engineering automation
 jackofmosttrades/gadgetinspector
A byte code analyzer for finding deserialization gadget chains in Java applications
 mgeeky/protectmytooling
Multi-Packer wrapper letting us daisy-chain various packers, obfuscators and other Red Team oriented weaponry. Featured with artifacts watermarking,…
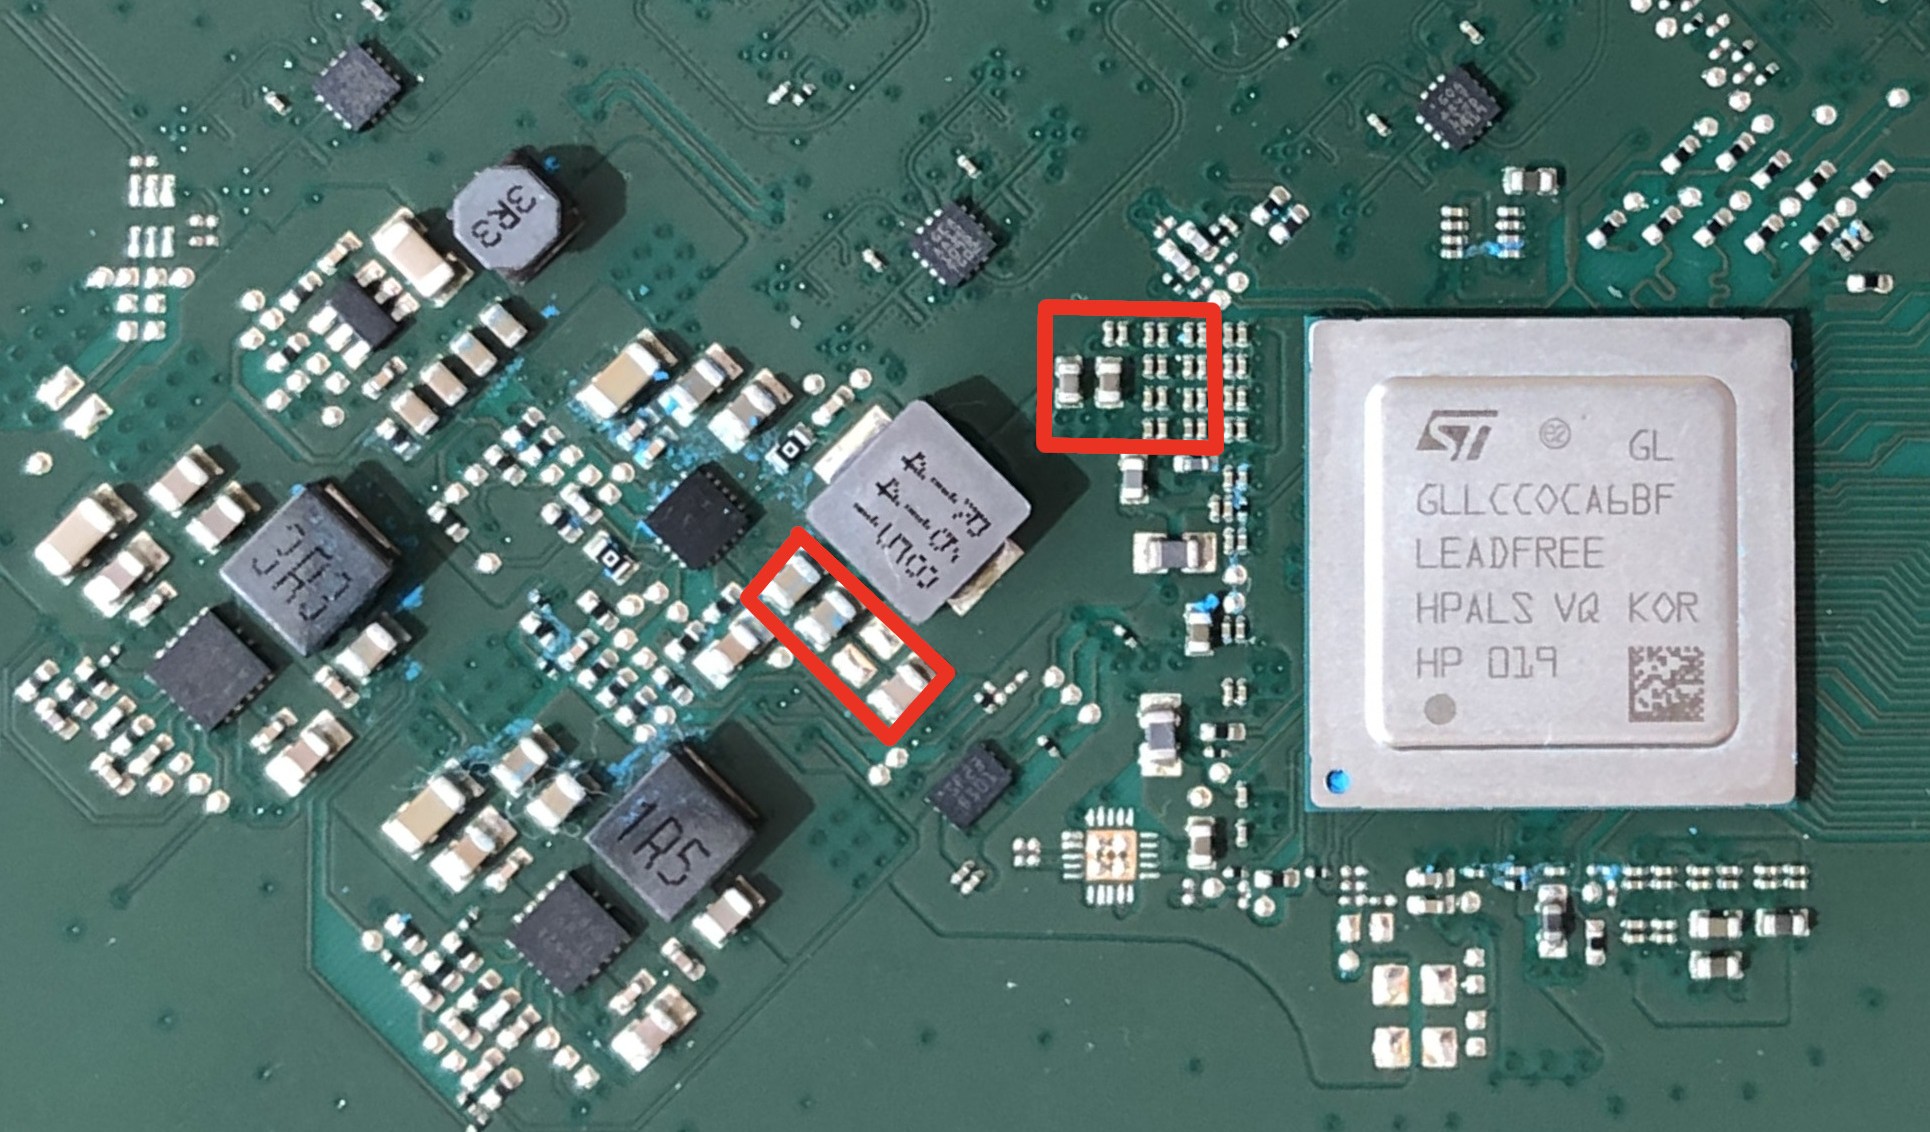 kuleuven-cosic/starlink-fi
Voltage fault-injection modchip for black-box security evaluation of Starlink terminals, bypassing bootloader signature verification to execute…
 frkngksl/shoggoth
Polymorphic encryptor that transforms shellcode, PE, and COFF files into obfuscated, position-independent payloads with RC4 and random block cipher…
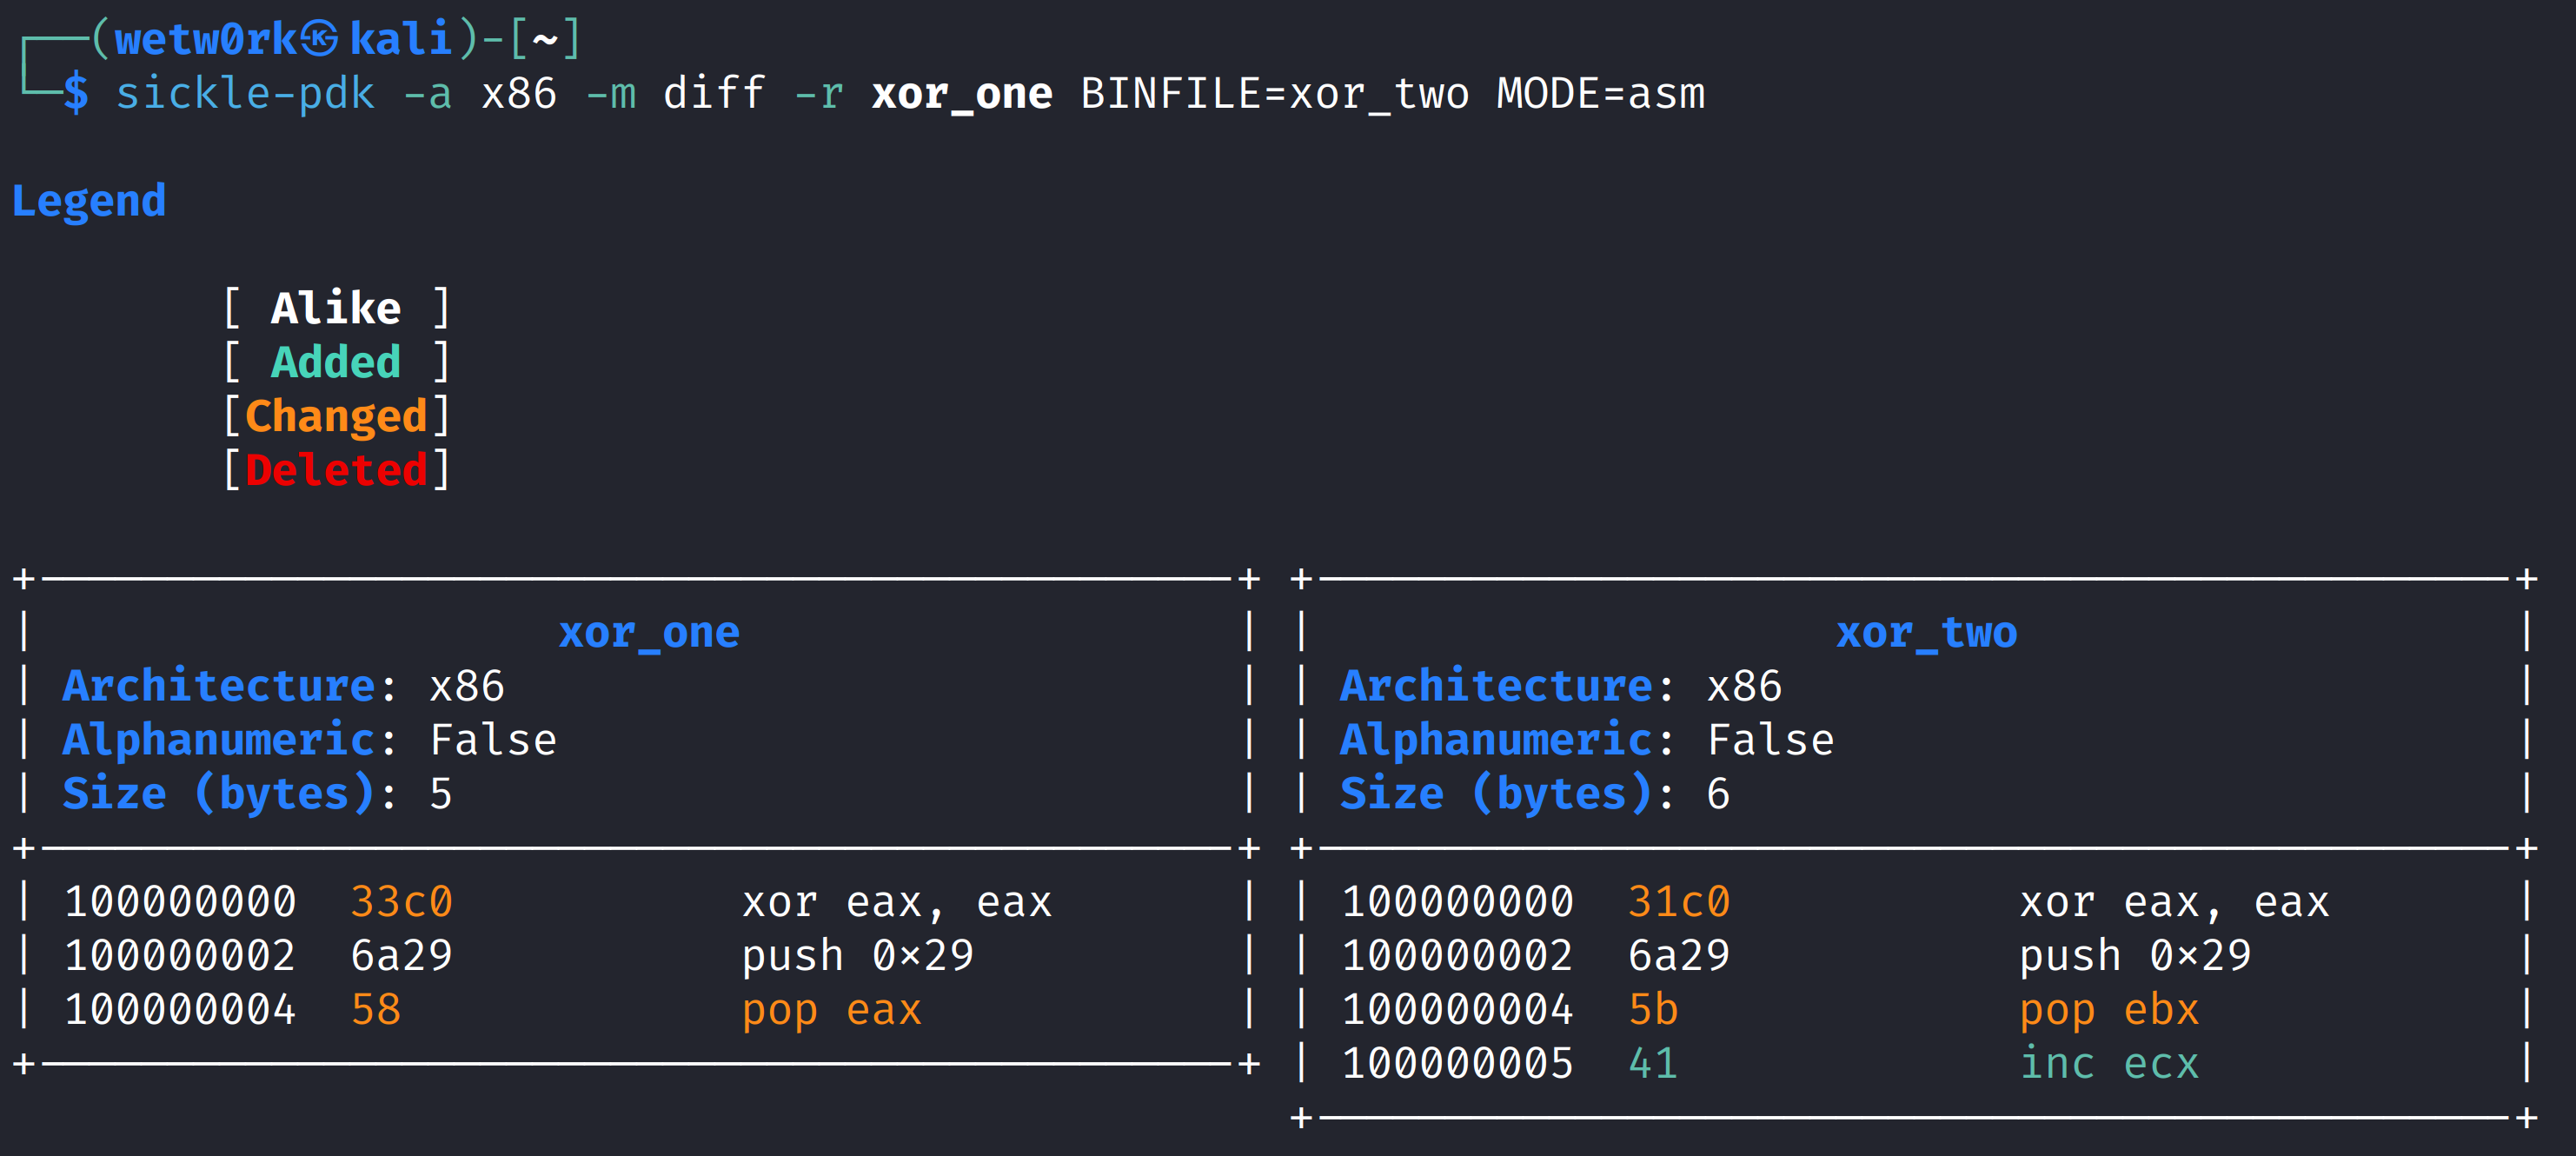 wetw0rk/sickle-pdk
Sickle - Payload Development Kit
 al3xtjames/ghidra-firmware-utils
Ghidra extension for PC firmware reverse engineering, providing loaders for PCI option ROMs, Intel Flash Descriptor, coreboot CBFS, and UEFI firmware…