SkypeACLKeyGen.exe analysis for hacking team

So...
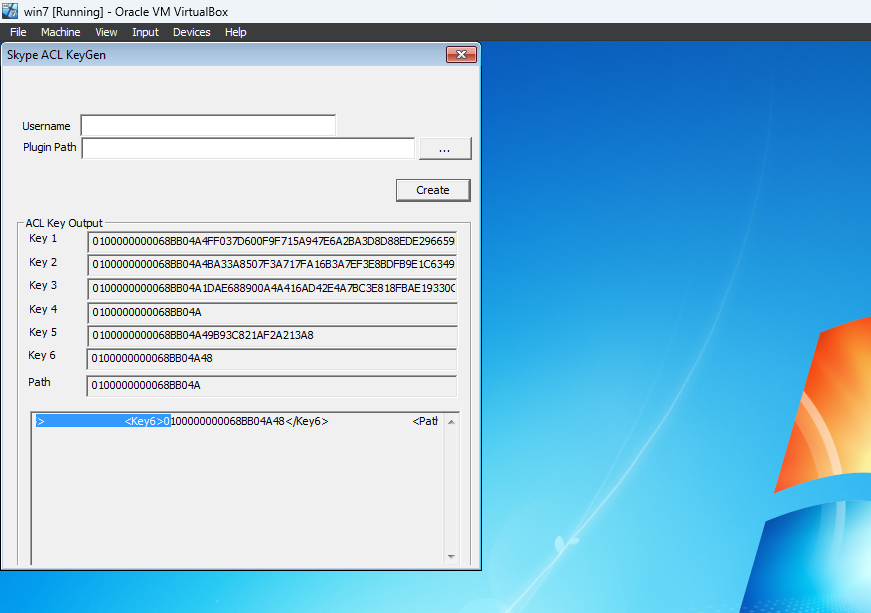
what do we analyse today ? well today we analyse a piece of software from hacking team. It's about skype? why do we do this ? idk i find it interesting.
So anyway we start by inspecting runtime behaviour. As you can see it requires a username and a plugin path and it outputs an acl ? sooo whatt is thissszz about ? Well inspecting this https://airbus-seclab.github.io/skype/vskype-part2.pdf , tells us that - "Skype implements an ACL-like system to allow or disallow plugins to attach themselves to a runnning instance A plugin ”signature” is added to the configuration file based on the user reply to a warning dialog" - . So ok what's in the folder of that software ?

So amm ok... still dont tells us anything . right so we see a stage 1 shellcode with office ending on that folder which may indicate an office exploit(still not yet confidirmed) fakeport which is a c# app tracer.exe and other stuff. Cool my hunch is that the actuall plugin will be register is tracer.exe . why is that ? Well from same pdf - "Skype voice engine can generate encrypted trace files if Logging and Logging2 are set Encryption is much simpler, a basic XOR with a 31 byte key" - . So let's give an analysis of the actuall generator of the acl , and next let's go over tracer, and maybe in other post over shellcode ;)
We start with this

Than move to this

And finally flow into these

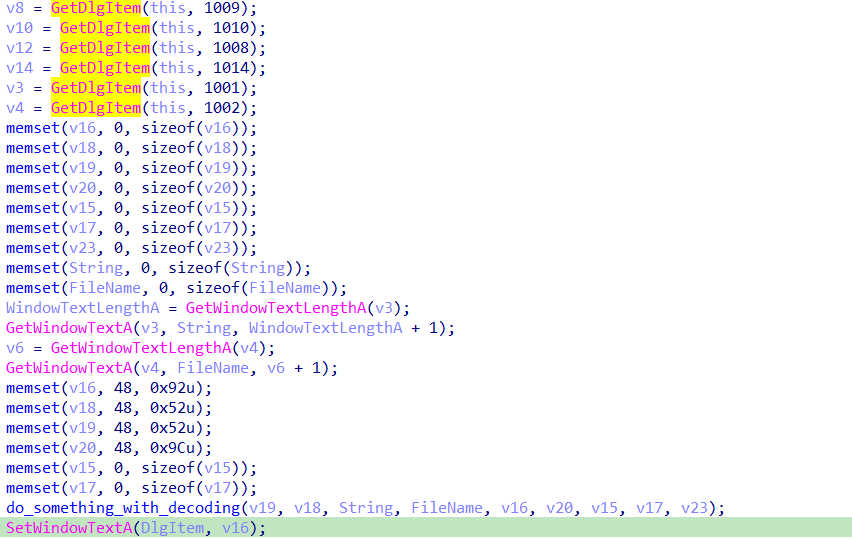
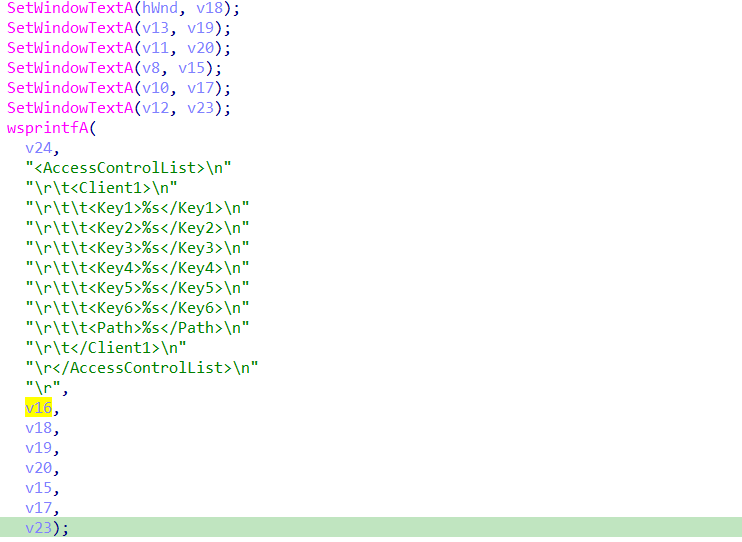
From there flow into this




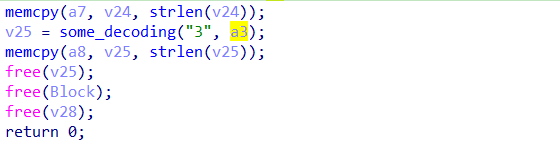
Cool another dynamic easteregg behaviour is this when you input user and plugin to be run you get 
Anyway so we go further and analyse


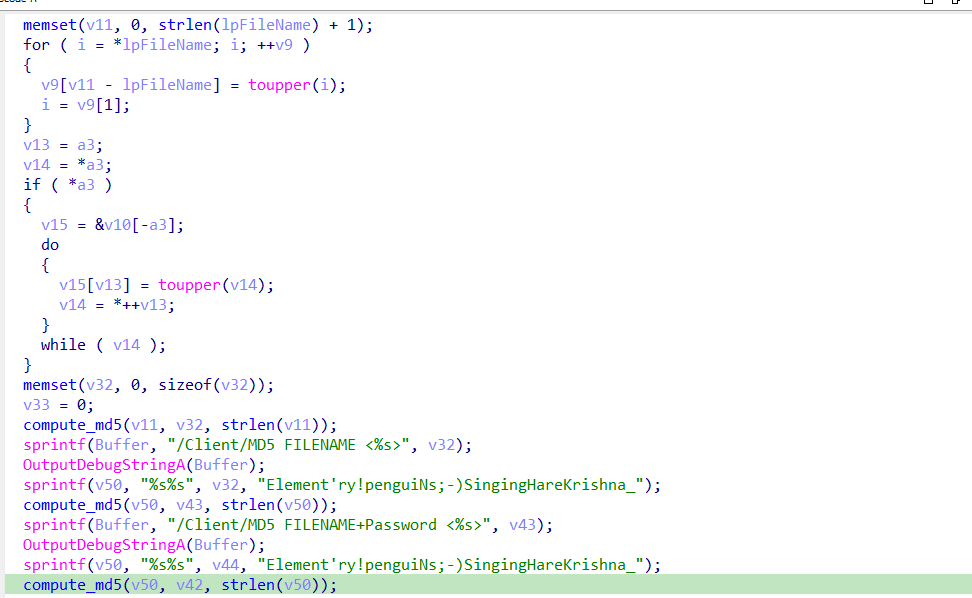
So from a topdown view it compute sha2 of content of file and it also maps it's contents in memory. Unfortunatelly for me dynamically it failed and so it didn't do anything :/\ what can we do . We move further. We go in probably_do_hash_based_function_function_recovery.

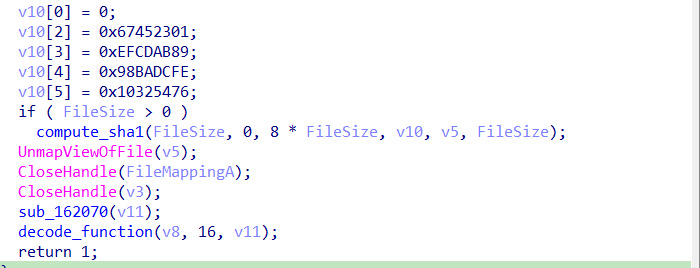
Unf it's the same case as previous case where we fail to map it in memory and exit from the function. non of the less we only compute md5 and probably do some function retrival based on md5 comparison.
We than go ahead and do some malloc and memset

We than convert the filename to uppercase
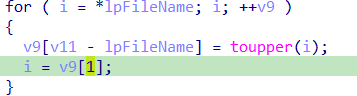
Same thing for username
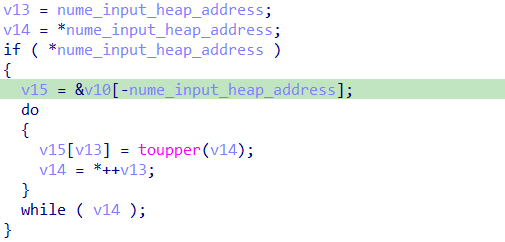
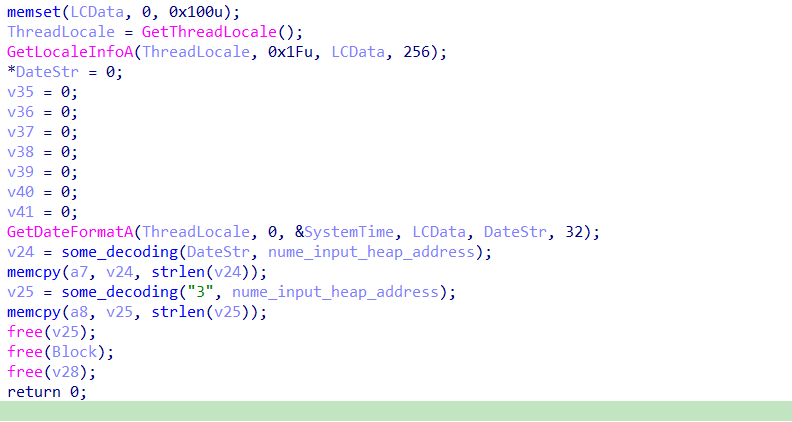
Cool and next we do this:

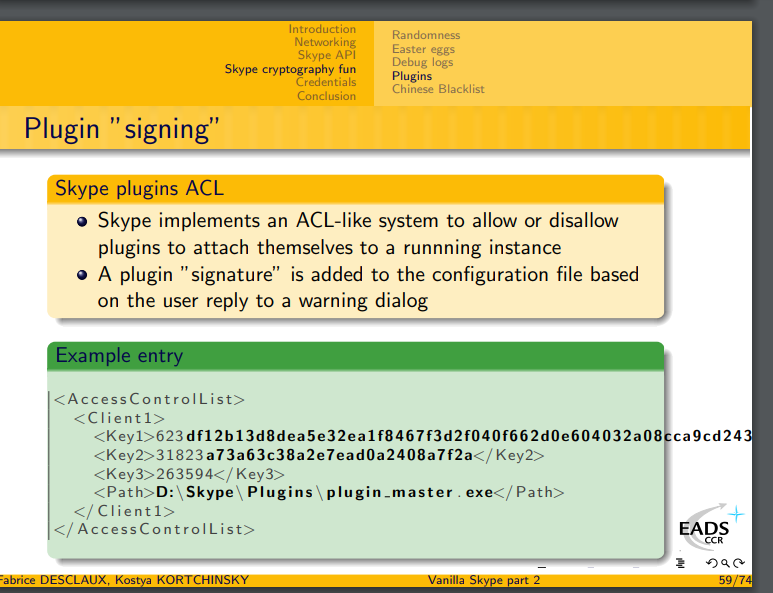
Basically create out own acl to allow us to run our plugin. In this case, now i assume it will be Tracer.exe which theoretically i suppose will log trace files generated by Skype voice engine.

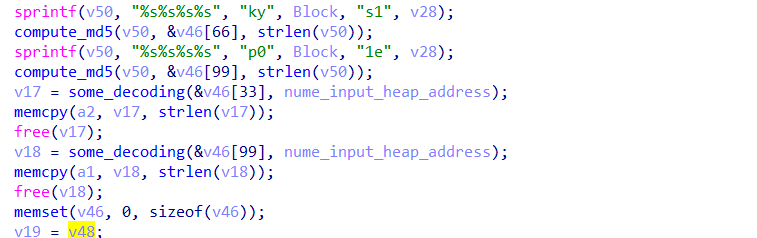
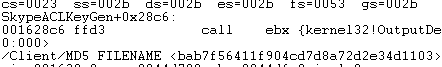
Output Result of mentioned upper images function

Output Result of mentioned upper images function
That's about it for now. Later today i will come back and update this . For now what's left is to analyse this half on function only