

angr
 angr/angr
A powerful and user-friendly binary analysis platform!
ai-assisted-reversingbinary-analysisbinary-exploitation+12
angr/angrA powerful and user-friendly binary analysis platform!
 capstone-engine/capstone
Multi-architecture disassembly framework providing a lightweight, thread-safe API for binary analysis, reverse engineering, and malware research…
 horsicq/detect-it-easy
Program for determining types of files for Windows, Linux and MacOS.
 0xor0ne/awesome-list
Cybersecurity oriented awesome list
 pwndbg/pwndbg
Exploit Development and Reverse Engineering with GDB & LLDB Made Easy
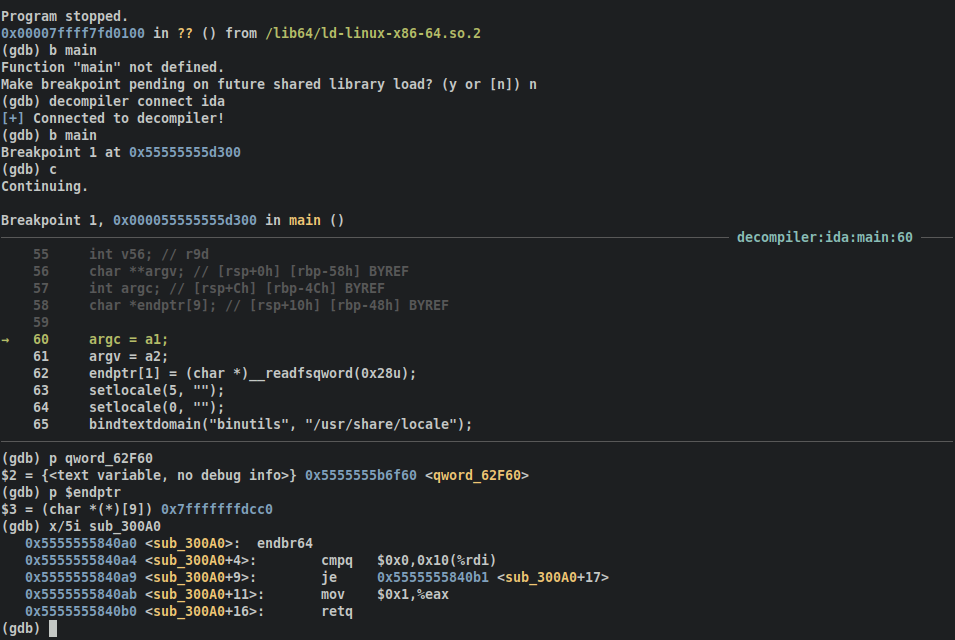 mahaloz/decomp2dbg
A plugin to introduce interactive symbols into your debugger from your decompiler
 neurosaki987/tvm-recover
Devirtualizes Tencent VM .tvm0 sections: lifts VM handlers to guest-level listings and LLVM IR, recovers CFG and dispatch, and patches recovered code…
 x64dbg/x64dbg
An open-source user mode debugger for Windows. Optimized for reverse engineering and malware analysis.
 dnspyex/dnspy
Unofficial revival of the well known .NET debugger and assembly editor, dnSpy
 gallopsled/pwntools
CTF framework and exploit development library

 abdelkabirouadoukou/cve-2026-31431-analysis-and-fix
In-depth technical analysis of Linux kernel CVE-2026-31431 (Copy Fail), a local privilege escalation via AF_ALG in-place scatterlist bug, including…
 jaime64net/debuggerj-
Debugger de aplicaciones x86 y x64 con intgracion de AI
 x86rc/vmp-lazy-unpack
Emulation-based unpacker and import resolver for Windows x86/x64 VMProtect 3.x binaries, using Unicorn to emulate syscalls and rebuild the IAT…
 aethervm/aethervm
LLVM-native binary analysis and emulation platform that lifts AArch64 and x86_64 machine code to LLVM IR for instrumentation, deobfuscation, and…
 structio-labs/n0xis
AI-first reverse-engineering toolkit: static analysis, SSA decompiler, live memory, provenance. Source-available (PolyForm Noncommercial).
 rizinorg/rizin
UNIX-like reverse engineering framework and command-line toolset.
 kikiuuw/cve-2025-68921
Analyze and demonstrate the local privilege escalation vulnerability (CVE-2025-68921) in Nahimic audio software on gaming laptops, with automated…