
cve-2026-98432-kernel-upgrade
 bigbiuewhale/cve-2026-98432-kernel-upgrade
Safe kernel upgrade for CVE-2026-98432 on Ubuntu 24.04 with NVIDIA, and an analysis of the bug
binary-analysisconfiguration-auditingdefensive-tools+4
bigbiuewhale/cve-2026-98432-kernel-upgradeSafe kernel upgrade for CVE-2026-98432 on Ubuntu 24.04 with NVIDIA, and an analysis of the bug
 4onurdemir/tcl-androidtv-root-attempts
Documents reverse engineering of a TCL Android TV factory layer: 56 kHz IR protocol, tclfactoryos daemon, kernel IR driver, and evidence that…
 j0wii/cve-2026-97798_lpe_windows
CVE-2026-97798 PoC — WER Time Travel Debugging argument injection to SYSTEM (Windows 11 LPE), with an adaptive faultrep.dll resolver.
 suffixing/apkscope
Android reverse engineering for humans and AI agents: typed Java in milliseconds, xrefs, API and secret recon, APK diff, re-signing, a native viewer…
 jankammerath/bogusmips
Forensic analytics for disassembly, reassembly, reverse engineering and auditing of Android apps
 fare9/dragon-tales
Binary analysis library built on LLVM for disassembling, lifting, and symbolically executing machine code across x86, ARM, and RISC-V, with CFG…
 s12cybersecurity/whatpatchguardprotects
Reference of all kernel structures, routines, and MSRs monitored by PatchGuard (KPP) on Windows.
 faicalom/zte-mf904q-reverse-engineering
Open research documentation and source review for ZTE MF904Q bootloader, firmware extraction, and reverse engineering.
 nighthawkk/jnisleuth-mcp
Automated Android JNI RegisterNatives recovery, stripped ARM64 .so type reconstruction, OLLVM BR X8 deobfuscator, and universal LLM/MCP bridge for…
 exporx/idachef
CyberChef-style recipe toolkit for IDA Pro: chain 289 encoding, cipher, compression, and hashing operations on database bytes, then patch results…
 0xade1a1de/mastik
C toolkit implementing micro-architectural side-channel attacks on Intel x86-64, including Prime+Probe, Flush+Reload, Flush+Flush, CacheBleed and…
 gmh5225/packer-kitsupe
Some PE hackery I'm working on (shellcode loader, packer, all WIP)
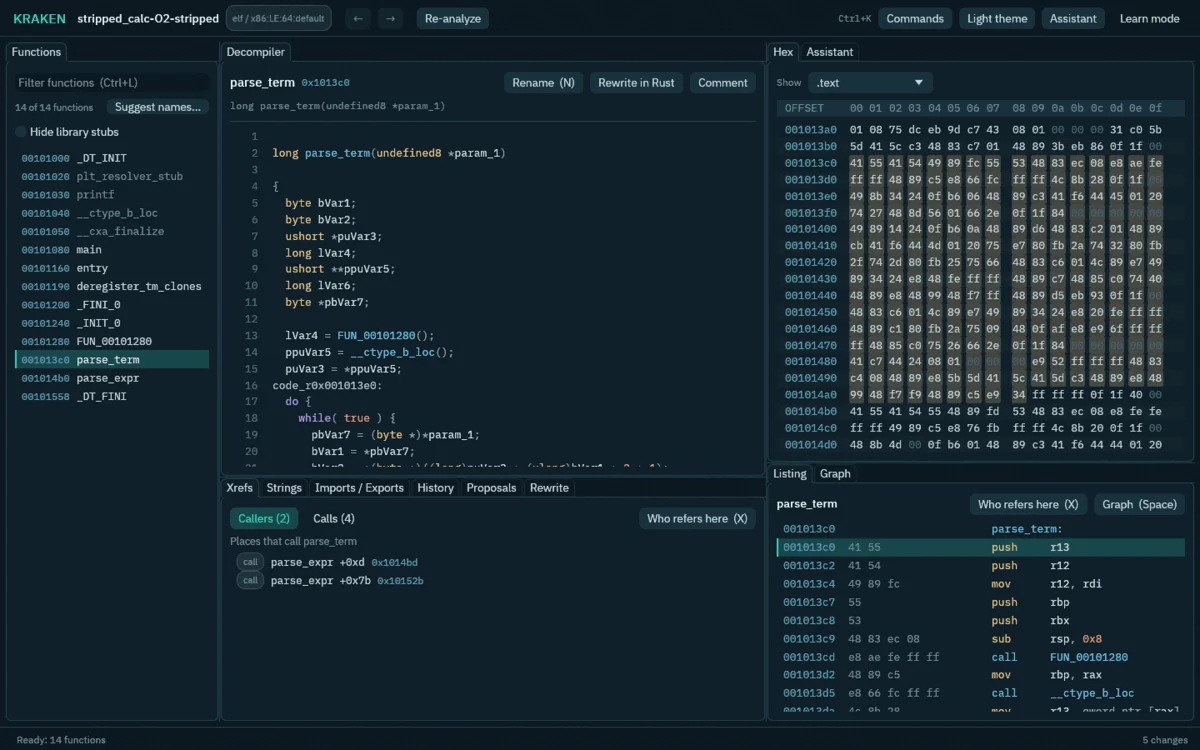 adam-atlassoftware/kraken
Reverse-engineering workbench built on Ghidra's decompiler with a native Java-free engine, AI-assisted function analysis, byte patching, sandboxed…
 kaandemir993/vidar-stealer-chrome-injection-malicious-js-targeting-google-reddit-sessions-analysis
Reverse engineering Vidar Stealer: From obfuscated memory strings to Chrome process injection, malicious JS execution, and active session hijacking…
 yuatemycat/superghidra
Python toolkit accelerating Ghidra with a cached daemon, ARM64 P-code lifting, Z3 equivalence proofs, GPU-accelerated scanning, binary diffing, and…
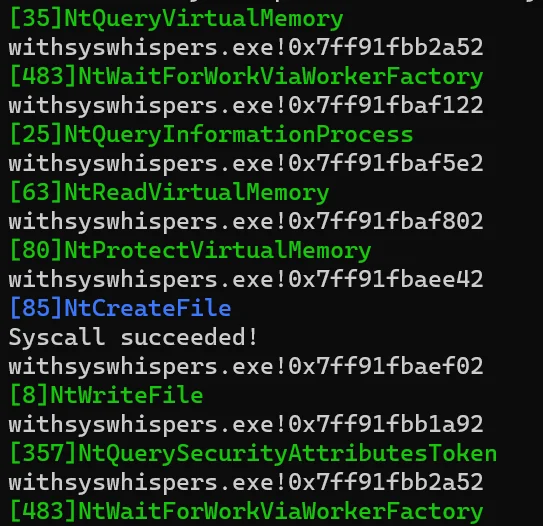 gmh5225/ntstrace
frida-stalker based system call tracer on windows(x64).
 giveen/decomp.anything
decomp.wtf fork: Windows PE matching, MinGW/clang-cl toolchains, and an optional REA MCP bridge
 maoabc/nmmp
dex-vm used to protect the android classes.dex file