CVE-2026-21155-SVE-2026-3546

Technical writeup and PoC for CVE-2026-21155 (SVE-2026-3546): fail-open signature checks and an unbounded boot-logo JPEG decode in Samsung Exynos…

Technical writeup and PoC for CVE-2026-21155 (SVE-2026-3546): fail-open signature checks and an unbounded boot-logo JPEG decode in Samsung Exynos…

Static S-Boot/LK probe for Samsung Exynos 1380 (s5e8835): SVE-2026-3546 / CVE-2026-21155 resolver patch, four-device coverage, and safety notes.

Crash-only proof-of-concept for CVE-2026-21096, a 32-bit integer overflow leading to heap overflow in Samsung's Quram JPEG decoder, with reversing…

Deterministic offline Chromium LevelDB .log carver, PNG/JPEG ICC provenance inspector, financial checksum validator & StarShield-Bench-24

Packs a runtime into built APK, AAB or IPA files to detect root, jailbreak, debuggers, Frida hooks, emulators, VPN/proxy interception and repackaging…

Fortinet Firmware decryption and analysis tools

Orchestrates JADX, CFR, Procyon and Vineflower to decompile Android APK/AAB/XAPK/APKS files, with hidden DEX extraction, deobfuscation, signed APK…

Make your own app expensive to reverse. A build-time audit, harden and verify harness for native binaries and mobile apps, built to counter…

Domain-organized library of reverse engineering playbooks, guides, and research notes for analyzing software and recreating patches, with repeatable…

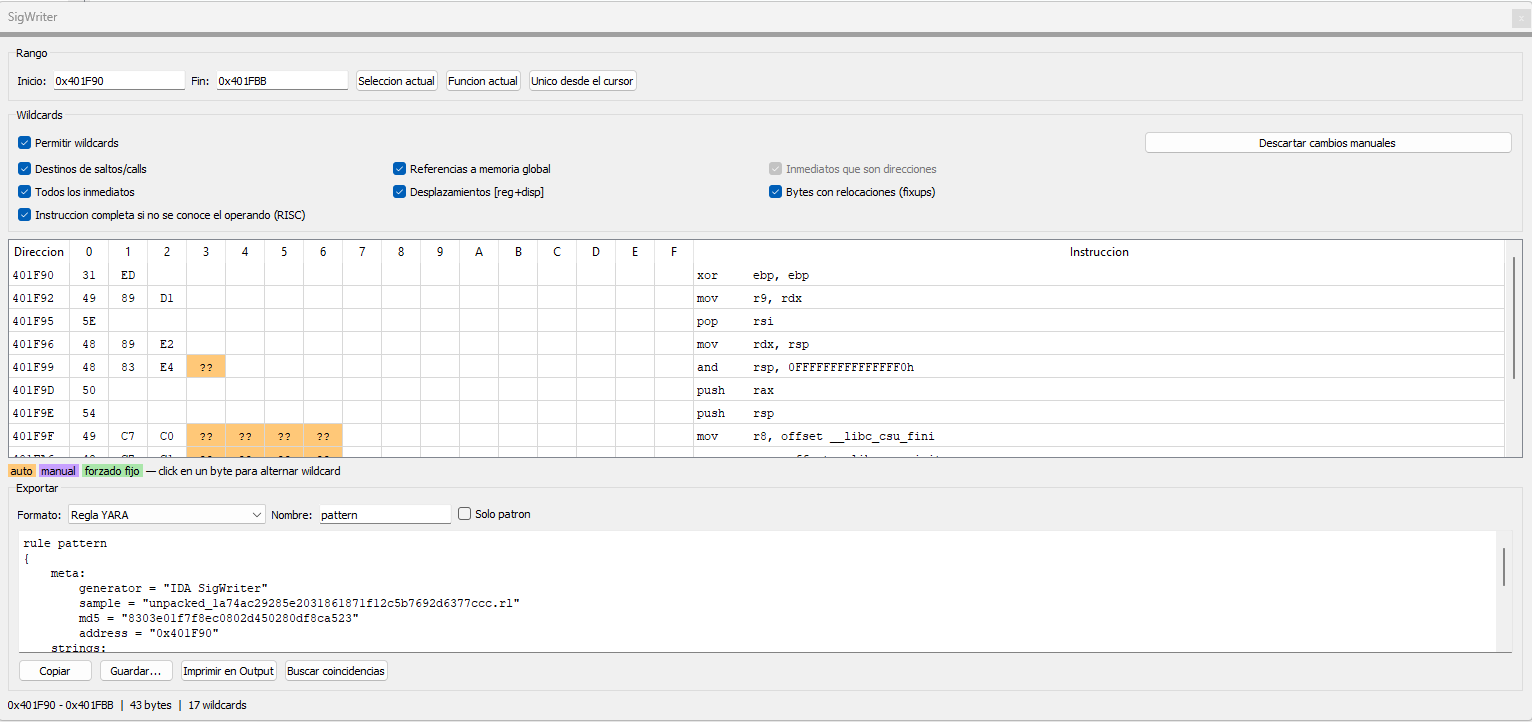
IDA Pro plugin that generates byte signatures from disassembly selections, with automatic and manual wildcards, match search, and export to YARA,…

Specialized Windows Reverse Engineering & Binary Analysis Toolkit | API Deobfuscation, Call Graphs, Kernel Driver & IOCTL Analysis

C tool that silences Microsoft Defender for Endpoint telemetry on Linux by writing syscall IDs into the exposed disabled_syscal eBPF map, suppressing…

CVE-2026-126915 - Google Chrome - High - Remote - Uninitialized variable - Skia Ganesh Vulkan fCurrentRenderPass. Chrome on Android < 157.0.8103.78.

Clean-room execution environment and research harness for Sony BIONZ X camera firmware, with ARM emulation, hardware contracts, and…

In-vitro static malware dissection pipeline for Telegram, AI agents (Antigravity / Local Ollama / OpenCode), and IDA Pro 9.5 via ph4ntom-ida-bridge

Open-source, bare-metal desktop malware triage and static threat intelligence workbench for Windows (MapViewOfFile PE parsing, Capstone disassembly,…

Let AI agents explore a running game from the inside. Live, safe, instant.

Free online disassembler and binary analysis tool. Reverse engineer PE, ELF and Mach-O files in your browser. Nothing is uploaded.