
vimana-framework
 s4dhulabs/vimana-framework
Vimana is a modular security framework for auditing Python APIs and Web applications. The plugin-based architecture enables security professionals to…
api-securityapi-security-testingcrawler+9
66
s4dhulabs/vimana-frameworkVimana is a modular security framework for auditing Python APIs and Web applications. The plugin-based architecture enables security professionals to…
 rushi9/zimaos-cve-2026-28286-arbitrary-file-write
PoC and verification toolkit for CVE-2026-28286, an arbitrary file write vulnerability in ZimaOS, exploiting API misconfiguration to write files…
 oscerd/cve-2026-46592
Reproducer for CVE-2026-46592: Apache Camel camel-cxf operationName header injection redirecting the invoked SOAP operation (confused deputy) from a…
 filipegaudard/cve-2026-24134-poc
Proof-of-concept exploit for CVE-2026-24134, a Broken Object Level Authorization vulnerability in StudioCMS, demonstrating unauthorized access to…
 shoucheng3/vert-x3__vertx-web_cve-2018-12542_3-5-3-cr1
Exploit for CVE-2018-12542 in Vert.x-Web, a Java web framework. Demonstrates a path traversal vulnerability allowing unauthorized access to static…
 cetinpy/cve-2024-50633
Proof-of-concept exploit for CVE-2024-50633, a Broken Object Level Authorization (BOLA) vulnerability in Indico v3.2.9–v3.3.2, enabling unauthorized…
 androidhooker/hooker
Hooker is an opensource project for dynamic analyses of Android applications. This project provides various tools and applications that can be use to…
 owasp/crapi
Deliberately vulnerable microservices API designed for hands-on training in the OWASP API Security Top 10 risks, with built-in challenges and a…
 microsoft/restler-fuzzer
RESTler is the first stateful REST API fuzzing tool for automatically testing cloud services through their REST APIs and finding security and…
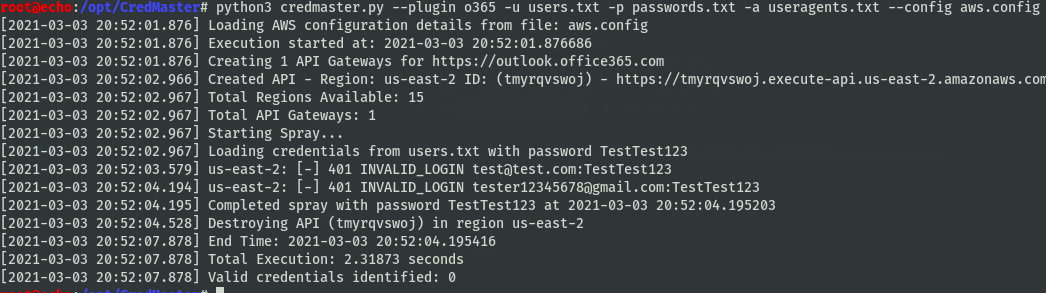 knavesec/credmaster
Refactored & improved CredKing password spraying tool, uses FireProx APIs to rotate IP addresses, stay anonymous, and beat throttling
 dolevf/damn-vulnerable-graphql-application
Damn Vulnerable GraphQL Application is an intentionally vulnerable GraphQL service implementation designed for learning about and practising GraphQL…
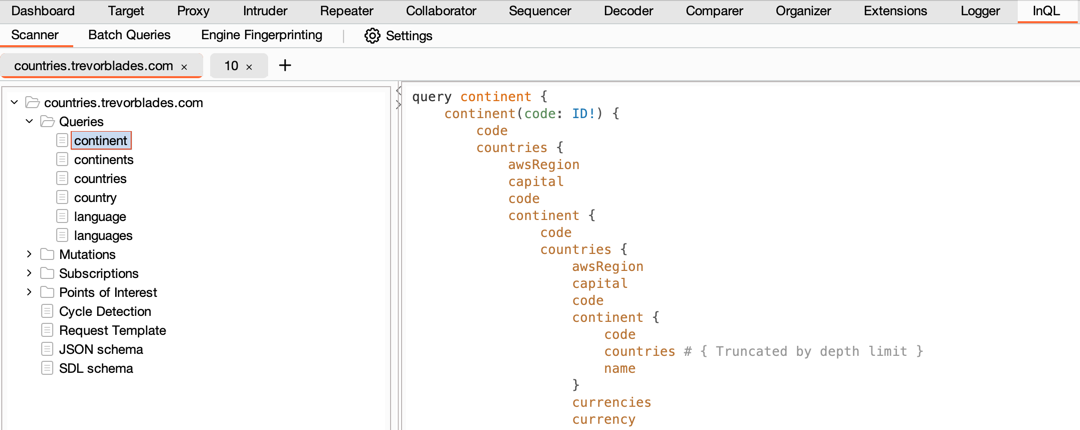 doyensec/inql
InQL is a robust, open-source Burp Suite extension for advanced GraphQL testing, offering intuitive vulnerability detection, customizable scans, and…
 bishopfox/sj
A tool for auditing endpoints defined in exposed (Swagger/OpenAPI) definition files.
 mitmproxy/mitmproxy_rs
Rust components for traffic interception and redirection, enabling WireGuard device proxying and local app redirection across macOS, Windows, and…
 silentchainai/silentchain
AI-powered vulnerability scanner extension for Burp Suite with multi-provider support (Ollama, OpenAI, Claude, Gemini)
 dolevf/graphw00f
GraphQL server engine fingerprinting tool that sends benign and malformed queries to identify backend technology and assess security defenses via the…
 dolevf/graphql-cop
Lightweight Python utility for automated security auditing of GraphQL APIs. Detects misconfigurations, information leaks, and denial-of-service…
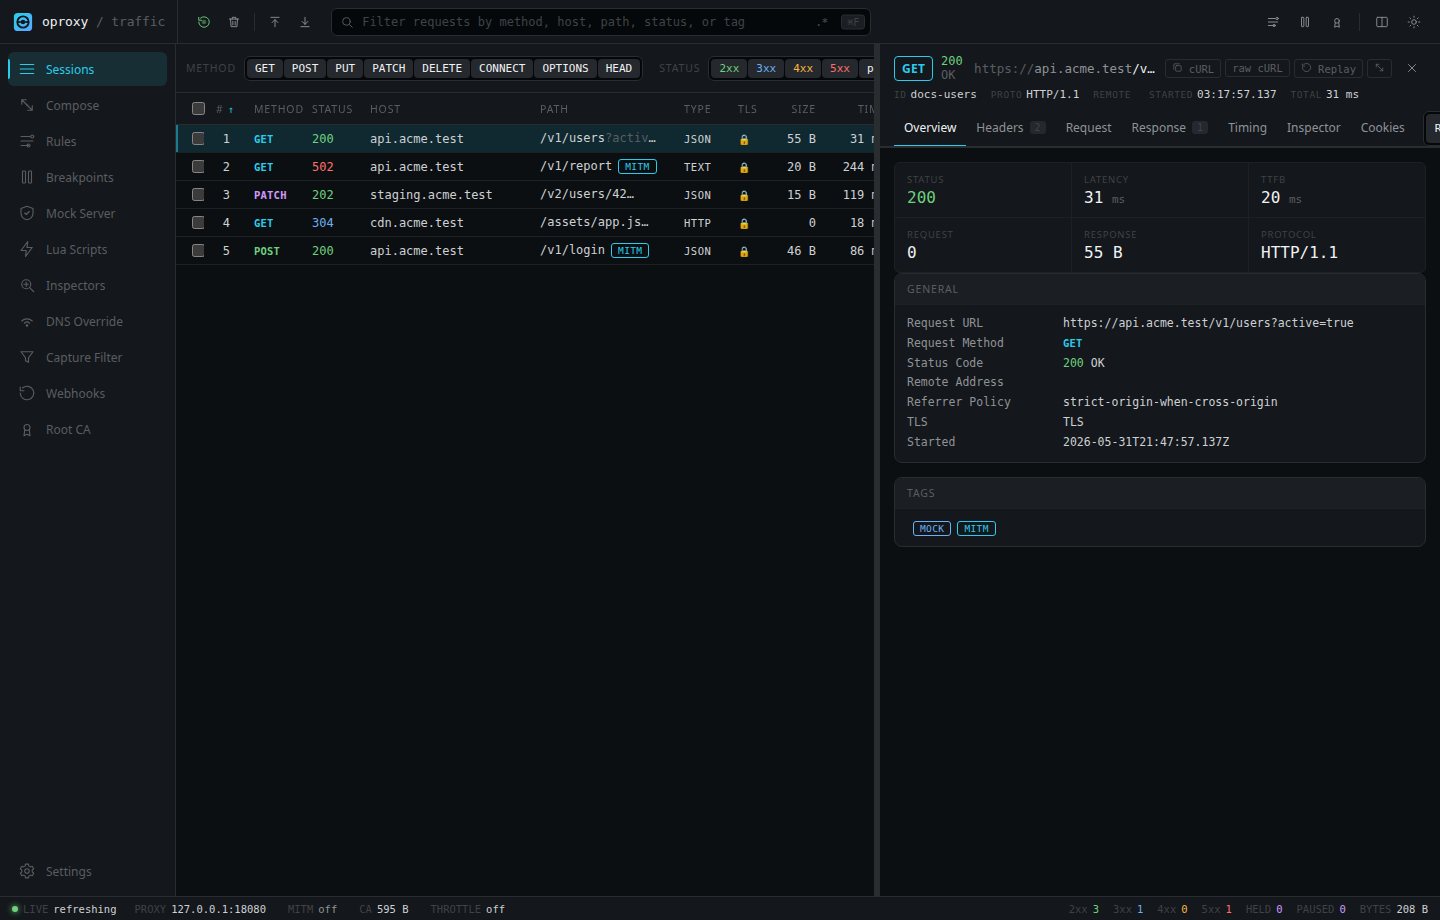 sauravrao637/oproxy
Open-source MITM proxy to intercept, inspect, and mock network traffic.